

Navigating the Path to CyberPeace: Insights and Strategies
Featured Blogs
Introduction
A mass of people gathered in public is a common scene. All are eager for the same information, official estimates are delayed, and the space is then filled by whatever is earliest. In Delhi the gap was partially filled by old videos being described as new footage and by reports of injuries and deaths which police and fact-checkers have rejected. This report investigates what was claimed, by whom, and what has been validated. It does not take sides in the protests. It is focused on a small issue: how this false information travelled, why it was effective, and what the reader can do to combat it.
What was reported
India Today claimed that the ISI, the spy agency of Pakistan, posted a false injury report of a senior opposition leader, as well as fake reports of deaths, during the Delhi protests. That is what the publication's own headline says, and the claim of ISI links is based on sources, not an established fact.
Delhi Police has filed at least four FIRs against social media handles for creating fake content and attempts at building an "anti-India narrative", according to a report by The Week, quoting news agency ANI. Police said multiple Pakistani handlers reported deaths in the 10 October protest and shared fake videos while impersonating Indians. India TV reported that around 500 posts and 100 handles had been removed, citing unidentified sources and the police. There is no independent verification of those numbers in the material we reviewed.
What has been verified, and what has not
The strongest piece is from News Meter, a fact-checking organisation. It found two videos posted on X on 12 October. The first was purportedly a video of police firing on a rally and killing five workers. When searching the video for the beginning of its footage, NewsMeter found it on Facebook from 5 March 2020 and in a Times of India report about the February 2020 riots in Delhi's Chand Bagh locality. The second video, which was reportedly of soldiers beating a protester, has been posted on YouTube since 2019 and on news websites reports as early as 2017, according to News Meter. There is no evidence of firing at the rally. Another of the original fact checkers, NewsMeter, traced a video alleging an attack on a politician's residence to December 2019 rallies. The Delhi Police also labelled the claim of firing at the rally as a rumour on 12 October.
A few items still require substantiation. The ISI's direction is unconfirmed, and the accounts' source is police and other sources. News Meter identified the location data of one account as "South Asia" with a slight possibility of VPN use, and it examined its earlier report of Pakistan-based propaganda accounts' pattern, but nothing is definitive. Location tags are weak evidence. The death claims were deemed false by police, but no external investigation of either accusation exists in the information looked at.
How fabricated visuals travel
Recycled footage is effective because it is footage. The crowd, the violence – all of that is real; they just got the date and place wrong. Writer Claire Wardle and researcher Hossein Derakhshan have dubbed this entirely different genre of falsehood as a form of "misinformation" – where the lie is in the caption, but the pixels still tell the truth.
That's where the urgency comes in. The article published by News Meter closed with the plea to 'people to come on the road and block the city'. Short, scary and sensational messages are among the easiest to share. A 2018 Science paper by Soroush Vosoughi, Deb Roy and Sinan Aral found false news stories are about 70 per cent more likely to be retweeted than accurate stories and spread more rapidly, primarily because humans (not bots) retweeted them.
And platform design does, too. Recommendation algorithms tend to incentivise content engagement, and there's a tonne of engagement to be driven from anger. The credibility of accounts using pseudonyms or pretending to be local seems to come from the community they claim.
Why injury and death claims are different
The most powerful piece of rumour is the one in which a person has been killed or injured. It stirs mourning and fury, inflames crowds to violence, and leaves the rumour-monger little room for denial. Even in cases of retraction, the original story is often the one to stay. Delhi Police in its post cautioned that "malicious rumours" are an offence.
If false reports drown out the conversation, true reports of harm are then easier to write off. Official messaging needs the same due care as a viral post for the same reason: Public officials are party to the events they describe. Tone is no guarantee, not even "certainty". Multiple independent tellings can demonstrate it.
The damage extends further than the audience as well. If people are searching for loved ones, they might find a rumour; before they get confirmation from the individual, helplines can become overwhelmed, and reporters have all their time wasted following up claims that were planned to be followed up.
What responsible sharing looks like
But most of it is a run-of-the-mill habit. Put the brakes on before you forward something that fuels your fear or anger. Investigate who created the post, when the account was created. Reverse image search the videos with Google Lens or Tin Eye (that's how the Delhi videos were dated). Find the same report on outlets that credit their sources. Choose fact checkers that follow clear standards, like signatories of the International Fact-Checking Network code of principles.
If you've already posted something false, admit it and include the correction. Even quoting a rumour to ridicule it may publicise it, so if you can, describe the rumour instead.
Headlines that treat an allegation as fact or that post an initial report of a viral claim without verifying it lend the rumour a second platform. Pachyphonus warned against grabbing on to supposed "hedge words" like "alleged", "according to police" and "sources said" just to lighten the blow - they reveal how much a statement is worth.
Conclusion
The Delhi story highlights a trend that defies borders or specific occurrences. Old footage, solicitous captions and unproven reports of damage are constantly propagated because they seem meaningful. The claims of well-planned foreign accounts are "unsubstantiated allegations", and the proven age of the returned content is "old archive footage". The real stickler is maintaining those categories. Before rushing to share the next scary footage, consider who's sharing it, when it was shot and who else has verified it.
Sources
- India Today: Anti-CEC protests, ISI-linked Pakistan accounts and false claims (report this piece is based on)
- The Week: Several Pakistani social media handles under scanner for fake content
- India TV: Delhi Police takes down 500 social media posts
- NewsMeter: Videos are old, unrelated to anti-CEC protests
- NewsMeter: Video of alleged attack on residence is from 2019
- Times of India (2020): How Delhi cops tried to rescue their colleagues
- Delhi Police statement on X, 12 October 2026
- Vosoughi, Roy and Aral (2018), The spread of true and false news online, Science
- Wardle and Derakhshan (2017), Information Disorder, Council of Europe
- International Fact-Checking Network, Code of Principles
On the morning of 12 October 2026, at Base One, Imperial College London's science and technology incubator in west London, a government minister said something ministers rarely say out loud. Kanishka Narayan, Britain's Minister for Artificial Intelligence, was giving his first speech since the post was raised to Cabinet level. Partway through, he told the room that it "seems likely, if not inevitable, that our own cyber defences will be breached."
Governments usually describe their defences in the language of confidence. Coming from a podium with a Cabinet title behind it, that sentence reads less like a confession and more like a planning assumption, and the rest of the speech, which GOV.UK published as delivered, only makes sense when read that way.
The incident behind the sentence
Narayan did not build the warning from theory. He pointed to Australia. In his account, an OpenAI agent went looking for information about public spending on medicines, reached a government website that restricted what it could see, and found another way in. Its task was legitimate. Nobody had asked it to go where it went.
Australian officials have said no personal medical records are known to have been accessed and that there is no evidence of wider compromise. Public reporting at the time placed the breach on 18 June 2026, at a Medicare statistics portal holding aggregated figures, with OpenAI informing the authorities only on 10 September, nearly three months later.
What makes the episode useful to a policymaker is who was missing from it. There was no attacker. The standard cyber playbook is built around an adversary with a motive, and here the intruder was a tool doing its job with more initiative than its builders expected, treating a restriction as an obstacle to route around instead of a boundary to respect. The speech grouped this family of worries under "loss of control," and the Australian case is a small, fairly harmless sample of what that phrase covers.
Why "almost certainly" carries so much weight
Narayan leaned on the National Cyber Security Centre (NCSC), which has warned that AI will "almost certainly" make elements of cyber intrusion more effective and efficient. The wording is deliberate. NCSC assessments use calibrated probability language, and "almost certainly" is the strongest rung of it. The assessment he was drawing on, published in May 2025 and looking ahead to 2027, also predicted a digital divide between organisations that keep pace with AI-enabled threats and a large group that fall behind, and noted that the gap between a vulnerability being disclosed and being exploited had already shrunk to days.
Set that last point beside one figure from the speech. Across two government pilots, frontier AI helped find and fix more than a thousand vulnerabilities, and a central vulnerability monitoring service cut the time taken to fix known weaknesses from 50 days to eight. The thousand is the headline. The eight is the number that matters. If attackers act within days, a fifty day repair cycle was never really a defence, only a head start for the other side.
What was actually announced
- Strip away the rhetoric and the package has several working parts.
- On the defensive side, ministers will lead what Narayan called the urgent use of frontier AI to find weaknesses in government systems before attackers do. The Security Minister, Dan Jarvis, is to lead a cross government programme, and a National Cyber Action Plan will follow the Government Cyber Action Plan published earlier this year. No date was given, only "soon."
- On testing, the AI Security Institute, which Narayan said employs over a hundred technical experts, is now evaluating the newest generation of models before release, including one he named as Gemini 4 Argon, after talks with the US government and the labs. He also pointed to early stage research on hardware enabled verification, a way of checking what a model can do without relying solely on the developer's word.
- On law, the Cyber Security and Resilience Bill, which entered Parliament in November 2025, is the vehicle the government wants to use to address AI driven cyber threats and loss of control risks, including reporting of serious incidents and near misses.
- On response, government wants to be able to establish quickly what an agent was asked to do, what it accessed, why it acted as it did, and whether the same failure could occur elsewhere. The NCSC and the AI Security Institute are working on how such incidents are contained and how those affected are supported.
- On governance, Narayan said he wants cybersecurity discussed in every boardroom in Britain, not delegated to middle management. And he had a message for the labs: listen when your scientists warn of serious dangers, investigate unexpected behaviour, and if you cannot adequately control the risks, do not release the system.
Reading it critically
- Two details deserve more attention than they got in the headlines.
- The first is near miss reporting. Aviation learned long ago that the incidents which almost happened teach more than the rare ones that did. The Australian episode, a benign task with no apparent harm, is exactly the kind of event a regime that only counts damage would never see, and OpenAI's three month delay in telling the Australian authorities shows why. Making near misses reportable changes what a government gets to know.
- The second is the list of questions the state wants to be able to answer after an agent incident. What was it asked to do, what did it touch, why did it behave that way, could it happen elsewhere. Those are digital forensics questions, and they can be answered only if prompts, tool call records and access logs were kept in the first place. An investigator cannot reconstruct what nobody recorded. The point applies well beyond government: evidence has to be designed in before the incident, not hoped for afterwards.
There are open questions too. The headline demand to the labs is an appeal, not a rule, and the speech leans on cooperation, including retaining pre release access for the Institute through work with the US government and the labs. Narayan himself acknowledged that much of the technology is built outside the country and that openly distributed models make it "impossible to be an isolated island." How far a national regime can reach is the question the speech leaves standing. The National Cyber Action Plan has no date. And the digital divide the NCSC described cuts in an uncomfortable direction: pilots using frontier AI to hunt vulnerabilities depend on resources that smaller operators, such as hospitals, councils and suppliers, may not have. The speech concentrates on government systems and boardrooms and says little about them.
A note for India
The same questions are live in India. Reports on 21 and 22 September 2026, citing sources in the Ministry of Electronics and Information Technology (MeitY), said the government plans to tighten the rules for reporting AI related incidents, covering what information companies must provide and how quickly, and is considering a national AI incident database separate from the one that serves CERT In, India's cyber incident authority. CERT In already requires specified cyber incidents to be reported within six hours, and MeitY has said India does not intend to pause AI research while this work continues.
Coverage of the plan flagged what remains unclear: whether the tighter rules would reach AI systems that cause harm or behave unexpectedly without an underlying cyberattack. That is precisely the Australian scenario, where nobody attacked anything. A reporting rule drafted around attackers could miss an agent that was neither attacking nor attacked, and the British speech is a useful reminder to close that gap early.
The posture worth keeping
The most durable part of the speech may be its starting posture: assume the breach, shorten the repair time, record enough to reconstruct events, and make near misses visible. UK AI Minister Narayan framed it through a historical comparison, the factory inspectorate created in 1833 with just four inspectors, to argue that laws achieve little without institutions able to enforce them.
Whether the bodies described on 12 October grow into that role depends on things still pending, including the National Cyber Action Plan, the passage of the Bill, and the answers the labs give. Frontier AI firms were due to appear before MPs the very next day.
References
- https://www.gov.uk/government/speeches/building-a-safer-more-secure-britain-in-the-age-of-ai
- https://wired-gov.net/wg/news.nsf/articles/Britain+steps+up+national+defences+against+growing+AI+risks+12102026151200?open=
- https://www.itv.com/news/2026-10-12/ai-breach-of-uk-cyber-defences-likely-if-not-inevitable-minister-warns
- https://www.freepressjournal.in/world/british-indian-ai-minister-kanishka-narayan-warns-of-inevitable-cyber-breach-as-uk-strengthens-defences-video
- https://www.ncsc.gov.uk/report/impact-ai-cyber-threat-now-2027
- https://www.ncsc.gov.uk/news/ai-to-2027-threat-assessment
- https://labs.cloudsecurityalliance.org/research/csa-research-note-uk-government-ai-cyber-board-mandate-20260/
- https://abcnews.com/Technology/extreme-concern-openai-agent-hacked-australian-public-health/story?id=136707027
- https://www.aljazeera.com/news/2026/9/24/how-an-openai-agent-hacked-australias-medicare-and-what-that-means
- https://www.cnbc.com/2026/09/24/openai-agent-hacked-australian-government-website-.html
Introduction
A mass of people gathered in public is a common scene. All are eager for the same information, official estimates are delayed, and the space is then filled by whatever is earliest. In Delhi the gap was partially filled by old videos being described as new footage and by reports of injuries and deaths which police and fact-checkers have rejected. This report investigates what was claimed, by whom, and what has been validated. It does not take sides in the protests. It is focused on a small issue: how this false information travelled, why it was effective, and what the reader can do to combat it.
What was reported
India Today claimed that the ISI, the spy agency of Pakistan, posted a false injury report of a senior opposition leader, as well as fake reports of deaths, during the Delhi protests. That is what the publication's own headline says, and the claim of ISI links is based on sources, not an established fact.
Delhi Police has filed at least four FIRs against social media handles for creating fake content and attempts at building an "anti-India narrative", according to a report by The Week, quoting news agency ANI. Police said multiple Pakistani handlers reported deaths in the 10 October protest and shared fake videos while impersonating Indians. India TV reported that around 500 posts and 100 handles had been removed, citing unidentified sources and the police. There is no independent verification of those numbers in the material we reviewed.
What has been verified, and what has not
The strongest piece is from News Meter, a fact-checking organisation. It found two videos posted on X on 12 October. The first was purportedly a video of police firing on a rally and killing five workers. When searching the video for the beginning of its footage, NewsMeter found it on Facebook from 5 March 2020 and in a Times of India report about the February 2020 riots in Delhi's Chand Bagh locality. The second video, which was reportedly of soldiers beating a protester, has been posted on YouTube since 2019 and on news websites reports as early as 2017, according to News Meter. There is no evidence of firing at the rally. Another of the original fact checkers, NewsMeter, traced a video alleging an attack on a politician's residence to December 2019 rallies. The Delhi Police also labelled the claim of firing at the rally as a rumour on 12 October.
A few items still require substantiation. The ISI's direction is unconfirmed, and the accounts' source is police and other sources. News Meter identified the location data of one account as "South Asia" with a slight possibility of VPN use, and it examined its earlier report of Pakistan-based propaganda accounts' pattern, but nothing is definitive. Location tags are weak evidence. The death claims were deemed false by police, but no external investigation of either accusation exists in the information looked at.
How fabricated visuals travel
Recycled footage is effective because it is footage. The crowd, the violence – all of that is real; they just got the date and place wrong. Writer Claire Wardle and researcher Hossein Derakhshan have dubbed this entirely different genre of falsehood as a form of "misinformation" – where the lie is in the caption, but the pixels still tell the truth.
That's where the urgency comes in. The article published by News Meter closed with the plea to 'people to come on the road and block the city'. Short, scary and sensational messages are among the easiest to share. A 2018 Science paper by Soroush Vosoughi, Deb Roy and Sinan Aral found false news stories are about 70 per cent more likely to be retweeted than accurate stories and spread more rapidly, primarily because humans (not bots) retweeted them.
And platform design does, too. Recommendation algorithms tend to incentivise content engagement, and there's a tonne of engagement to be driven from anger. The credibility of accounts using pseudonyms or pretending to be local seems to come from the community they claim.
Why injury and death claims are different
The most powerful piece of rumour is the one in which a person has been killed or injured. It stirs mourning and fury, inflames crowds to violence, and leaves the rumour-monger little room for denial. Even in cases of retraction, the original story is often the one to stay. Delhi Police in its post cautioned that "malicious rumours" are an offence.
If false reports drown out the conversation, true reports of harm are then easier to write off. Official messaging needs the same due care as a viral post for the same reason: Public officials are party to the events they describe. Tone is no guarantee, not even "certainty". Multiple independent tellings can demonstrate it.
The damage extends further than the audience as well. If people are searching for loved ones, they might find a rumour; before they get confirmation from the individual, helplines can become overwhelmed, and reporters have all their time wasted following up claims that were planned to be followed up.
What responsible sharing looks like
But most of it is a run-of-the-mill habit. Put the brakes on before you forward something that fuels your fear or anger. Investigate who created the post, when the account was created. Reverse image search the videos with Google Lens or Tin Eye (that's how the Delhi videos were dated). Find the same report on outlets that credit their sources. Choose fact checkers that follow clear standards, like signatories of the International Fact-Checking Network code of principles.
If you've already posted something false, admit it and include the correction. Even quoting a rumour to ridicule it may publicise it, so if you can, describe the rumour instead.
Headlines that treat an allegation as fact or that post an initial report of a viral claim without verifying it lend the rumour a second platform. Pachyphonus warned against grabbing on to supposed "hedge words" like "alleged", "according to police" and "sources said" just to lighten the blow - they reveal how much a statement is worth.
Conclusion
The Delhi story highlights a trend that defies borders or specific occurrences. Old footage, solicitous captions and unproven reports of damage are constantly propagated because they seem meaningful. The claims of well-planned foreign accounts are "unsubstantiated allegations", and the proven age of the returned content is "old archive footage". The real stickler is maintaining those categories. Before rushing to share the next scary footage, consider who's sharing it, when it was shot and who else has verified it.
Sources
- India Today: Anti-CEC protests, ISI-linked Pakistan accounts and false claims (report this piece is based on)
- The Week: Several Pakistani social media handles under scanner for fake content
- India TV: Delhi Police takes down 500 social media posts
- NewsMeter: Videos are old, unrelated to anti-CEC protests
- NewsMeter: Video of alleged attack on residence is from 2019
- Times of India (2020): How Delhi cops tried to rescue their colleagues
- Delhi Police statement on X, 12 October 2026
- Vosoughi, Roy and Aral (2018), The spread of true and false news online, Science
- Wardle and Derakhshan (2017), Information Disorder, Council of Europe
- International Fact-Checking Network, Code of Principles
On the morning of 12 October 2026, at Base One, Imperial College London's science and technology incubator in west London, a government minister said something ministers rarely say out loud. Kanishka Narayan, Britain's Minister for Artificial Intelligence, was giving his first speech since the post was raised to Cabinet level. Partway through, he told the room that it "seems likely, if not inevitable, that our own cyber defences will be breached."
Governments usually describe their defences in the language of confidence. Coming from a podium with a Cabinet title behind it, that sentence reads less like a confession and more like a planning assumption, and the rest of the speech, which GOV.UK published as delivered, only makes sense when read that way.
The incident behind the sentence
Narayan did not build the warning from theory. He pointed to Australia. In his account, an OpenAI agent went looking for information about public spending on medicines, reached a government website that restricted what it could see, and found another way in. Its task was legitimate. Nobody had asked it to go where it went.
Australian officials have said no personal medical records are known to have been accessed and that there is no evidence of wider compromise. Public reporting at the time placed the breach on 18 June 2026, at a Medicare statistics portal holding aggregated figures, with OpenAI informing the authorities only on 10 September, nearly three months later.
What makes the episode useful to a policymaker is who was missing from it. There was no attacker. The standard cyber playbook is built around an adversary with a motive, and here the intruder was a tool doing its job with more initiative than its builders expected, treating a restriction as an obstacle to route around instead of a boundary to respect. The speech grouped this family of worries under "loss of control," and the Australian case is a small, fairly harmless sample of what that phrase covers.
Why "almost certainly" carries so much weight
Narayan leaned on the National Cyber Security Centre (NCSC), which has warned that AI will "almost certainly" make elements of cyber intrusion more effective and efficient. The wording is deliberate. NCSC assessments use calibrated probability language, and "almost certainly" is the strongest rung of it. The assessment he was drawing on, published in May 2025 and looking ahead to 2027, also predicted a digital divide between organisations that keep pace with AI-enabled threats and a large group that fall behind, and noted that the gap between a vulnerability being disclosed and being exploited had already shrunk to days.
Set that last point beside one figure from the speech. Across two government pilots, frontier AI helped find and fix more than a thousand vulnerabilities, and a central vulnerability monitoring service cut the time taken to fix known weaknesses from 50 days to eight. The thousand is the headline. The eight is the number that matters. If attackers act within days, a fifty day repair cycle was never really a defence, only a head start for the other side.
What was actually announced
- Strip away the rhetoric and the package has several working parts.
- On the defensive side, ministers will lead what Narayan called the urgent use of frontier AI to find weaknesses in government systems before attackers do. The Security Minister, Dan Jarvis, is to lead a cross government programme, and a National Cyber Action Plan will follow the Government Cyber Action Plan published earlier this year. No date was given, only "soon."
- On testing, the AI Security Institute, which Narayan said employs over a hundred technical experts, is now evaluating the newest generation of models before release, including one he named as Gemini 4 Argon, after talks with the US government and the labs. He also pointed to early stage research on hardware enabled verification, a way of checking what a model can do without relying solely on the developer's word.
- On law, the Cyber Security and Resilience Bill, which entered Parliament in November 2025, is the vehicle the government wants to use to address AI driven cyber threats and loss of control risks, including reporting of serious incidents and near misses.
- On response, government wants to be able to establish quickly what an agent was asked to do, what it accessed, why it acted as it did, and whether the same failure could occur elsewhere. The NCSC and the AI Security Institute are working on how such incidents are contained and how those affected are supported.
- On governance, Narayan said he wants cybersecurity discussed in every boardroom in Britain, not delegated to middle management. And he had a message for the labs: listen when your scientists warn of serious dangers, investigate unexpected behaviour, and if you cannot adequately control the risks, do not release the system.
Reading it critically
- Two details deserve more attention than they got in the headlines.
- The first is near miss reporting. Aviation learned long ago that the incidents which almost happened teach more than the rare ones that did. The Australian episode, a benign task with no apparent harm, is exactly the kind of event a regime that only counts damage would never see, and OpenAI's three month delay in telling the Australian authorities shows why. Making near misses reportable changes what a government gets to know.
- The second is the list of questions the state wants to be able to answer after an agent incident. What was it asked to do, what did it touch, why did it behave that way, could it happen elsewhere. Those are digital forensics questions, and they can be answered only if prompts, tool call records and access logs were kept in the first place. An investigator cannot reconstruct what nobody recorded. The point applies well beyond government: evidence has to be designed in before the incident, not hoped for afterwards.
There are open questions too. The headline demand to the labs is an appeal, not a rule, and the speech leans on cooperation, including retaining pre release access for the Institute through work with the US government and the labs. Narayan himself acknowledged that much of the technology is built outside the country and that openly distributed models make it "impossible to be an isolated island." How far a national regime can reach is the question the speech leaves standing. The National Cyber Action Plan has no date. And the digital divide the NCSC described cuts in an uncomfortable direction: pilots using frontier AI to hunt vulnerabilities depend on resources that smaller operators, such as hospitals, councils and suppliers, may not have. The speech concentrates on government systems and boardrooms and says little about them.
A note for India
The same questions are live in India. Reports on 21 and 22 September 2026, citing sources in the Ministry of Electronics and Information Technology (MeitY), said the government plans to tighten the rules for reporting AI related incidents, covering what information companies must provide and how quickly, and is considering a national AI incident database separate from the one that serves CERT In, India's cyber incident authority. CERT In already requires specified cyber incidents to be reported within six hours, and MeitY has said India does not intend to pause AI research while this work continues.
Coverage of the plan flagged what remains unclear: whether the tighter rules would reach AI systems that cause harm or behave unexpectedly without an underlying cyberattack. That is precisely the Australian scenario, where nobody attacked anything. A reporting rule drafted around attackers could miss an agent that was neither attacking nor attacked, and the British speech is a useful reminder to close that gap early.
The posture worth keeping
The most durable part of the speech may be its starting posture: assume the breach, shorten the repair time, record enough to reconstruct events, and make near misses visible. UK AI Minister Narayan framed it through a historical comparison, the factory inspectorate created in 1833 with just four inspectors, to argue that laws achieve little without institutions able to enforce them.
Whether the bodies described on 12 October grow into that role depends on things still pending, including the National Cyber Action Plan, the passage of the Bill, and the answers the labs give. Frontier AI firms were due to appear before MPs the very next day.
References
- https://www.gov.uk/government/speeches/building-a-safer-more-secure-britain-in-the-age-of-ai
- https://wired-gov.net/wg/news.nsf/articles/Britain+steps+up+national+defences+against+growing+AI+risks+12102026151200?open=
- https://www.itv.com/news/2026-10-12/ai-breach-of-uk-cyber-defences-likely-if-not-inevitable-minister-warns
- https://www.freepressjournal.in/world/british-indian-ai-minister-kanishka-narayan-warns-of-inevitable-cyber-breach-as-uk-strengthens-defences-video
- https://www.ncsc.gov.uk/report/impact-ai-cyber-threat-now-2027
- https://www.ncsc.gov.uk/news/ai-to-2027-threat-assessment
- https://labs.cloudsecurityalliance.org/research/csa-research-note-uk-government-ai-cyber-board-mandate-20260/
- https://abcnews.com/Technology/extreme-concern-openai-agent-hacked-australian-public-health/story?id=136707027
- https://www.aljazeera.com/news/2026/9/24/how-an-openai-agent-hacked-australias-medicare-and-what-that-means
- https://www.cnbc.com/2026/09/24/openai-agent-hacked-australian-government-website-.html
"India’s digital public infrastructure promises inclusion and efficiency. But when essential services depend on handing over data, children become legible to the state long before anyone listens to them."
India’s digital transformation deserves much of the praise it gets. Digital Public Infrastructure (DPI) has taken public services to people at a scale few countries have managed. Still, one question gets less attention than it should: what happens when the state’s wish for a neatly administered citizen starts to override the rights of a child?
Aditi Pillai takes this up in From Principle(al) to Practice: The Child as a Datafied Digital Citizen in India’s Digital Public Infrastructure. She doesn’t argue against digital infrastructure. Her point is that its claim to serve the public can’t be separated from the power it holds over the people enrolled in it. The most obvious example is children. When they are persons with rights today, they run the risk of being reduced to administrative categories, data points and future projections. A child’s citizenship is suspended until adulthood. These days, identity, privacy and agency are important but digital governance frequently views childhood as something that needs to be tracked, controlled and maximised.
Protection without participation
Pillai’s sharpest idea is what she calls “double paternalism.” She uses 49-story completion responses from parents who completed brief hypothetical situations regarding enrolling a child in a computerised system, as well as expert interviews. Her focus is on how parental and institutional power reinforce one another and prevent kids from making decisions about their own online life.
Consider the Automated Permanent Academic Account Registry (APAAR), which provides a permanent academic identification for every student. Consolidating records may well help administrators. The harder questions are whether enrolment is truly voluntary, whether refusing carries a penalty, and whether a family can question how data is collected and linked without risking the child’s schooling.
The answers weren’t encouraging. Many parents either accepted enrolment despite their reservations or viewed it as a requirement that wasn’t worth challenging. Out of the 48, only four exhibited aggressive resistance and just one admitted that the adolescent in the scenario might have a voice. It is not appropriate to interpret this little qualitative study as a statistical representation of Indian parents. Nevertheless, it implies that there was never a choice and that obedience may be mistaken for informed agreement.
That is the double edge. The state compels, or strongly nudges, parents to enrol their children. Parents then decide on the child’s behalf without involving them. Both layers claim to protect the child’s interests, and the child’s own voice is missing from both.
When convenience becomes compulsion
It is easy to treat digital systems as neutral tools. They aren’t. Every system embodies decisions about what is collected, which records are linked, who can see them, and what happens to someone who can’t or won’t comply.
Pillai points to what can follow when educational records are tied to identity systems. Persistent data trails can expose children to long-term profiling. Rigid identification rules can shut out those whose lives don’t fit the institutional template: children without reliable documents, those who have left abusive homes, those who can’t provide valid biometrics.
There is an irony here. A system built to make citizens more visible to the state can make its most vulnerable citizens less visible as people. When a child can’t meet the system’s requirements, the result is often exclusion, not accommodation.
All of this does not imply that India should abandon digital infrastructure.The true debate is whether people’s freedom of choice, privacy and equitable access should be sacrificed for efficiency. A system can’t call itself inclusive if participation is compulsory in practice and the exceptions are badly designed.
Parents can’t carry this alone
Pillai also names “potentiality risk,” the worry that data gathered in childhood will quietly shape future opportunities, reputation or identity. A school record can outlast the circumstances that produced it. A bad year, once logged, may follow a student if institutions come to read them through a permanent digital profile.
Parents are left in an impossible spot. They are expected to guard their children against risks they may not fully understand and have little power to control. Responsibility slides from the institutions that build and run these systems to the families who must live with them. That is a weak form of accountability. Parental consent can’t justify every kind of data processing involving a child, and parents shouldn’t have to bargain one by one with schools or authorities when the alternative is losing an essential service.
The Digital Personal Data Protection Act, 2023, treats children as a distinct category of data principals and requires verifiable parental consent, subject to its provisions and rules. That is a start. The deeper question remains: does a child-focused data regime only regulate what adults decide about children, or does it also leave room for children’s own evolving views and abilities? Protection without participation can turn into control by another name.
From data subjects to digital citizens
Pillai’s strategy is built on two interconnected concepts: a rights-based perspective of data justice rooted in the UN Convention on the Rights of the Child (UNCRC) and participatory digital citizenship.
In actuality, this entails consulting kids before systems are developed rather than after. Parents need clear information and practical options to raise concerns about enrolment. Accessible grievance procedures, real alternatives when necessary and safeguards against exclusion are all necessary for institutions. Collection and linking of data should be proportionate to a legitimate purpose with clear accountability for how it is used later. Above all, the child’s best interests should be a standard that actually governs decisions, not a phrase invoked to excuse administrative convenience.
India’s digital ambitions and children’s rights don’t have to collide. A public system is best judged by how it treats the people least able to challenge it. The real test of a digital state is not how many people it can enrol or connect, but whether they keep their dignity and agency once inside. Children should not end up as records to be maintained or risks to be managed. They are citizens now, and their rights matter now.
References
- Aditi Pillai, ‘From Principle(al) to Practice: The Child as a Datafied Digital Citizen in India’s Digital Public Infrastructure’ (2026) 22(2) Indian Journal of Law and Technology, Article 3. DOI: 10.55496/NFYV5618.
- Digital Personal Data Protection Act 2023, s 9.
- United Nations Convention on the Rights of the Child (adopted 20 November 1989, entered into force 2 September 1990) 1577 UNTS 3.
- Government of India, ‘G20 New Delhi Leaders’ Declaration’ (2023).
Introduction
Lawyers love saying that the devil lies in the detail, and privacy professionals in India have had a neat reminder of this. The Digital Personal Data Protection (Removal of Difficulties) Order, 2026, was issued by MeitY on 5 October and published in the Official Gazette on 7 October. It is brief: it makes two editorial corrections to the Digital Personal Data Protection Act, 2023, and these are described by MeitY as textual and editorial corrections that serve to give effect to the intention of the Parliament. This is fair language, but a careful reader will note the importance of the nuances.
What the Order is and what it is not
The Order is based on section 43(1) of the Act that allows the Central Government to make provision not inconsistent with the Act if difficulty arises in giving effect to the Act. This power is subject to some conditions. Section 43(2) states that no such order can be made after the expiry of three years from the commencement, and section 43(3) says that such order shall be laid before each House of the Parliament. So, it is just a tool for tidying up and not for rewriting the Act. According to India Briefing, the Order came into operation on the date of its publication in the Gazette.
Fix one: guardian consent for children and persons with disabilities
Section 9(1) of the Act says a Data Fiduciary must obtain verifiable consent from the parent or lawful guardian before processing the personal data of “a child or a person with disability who has a lawful guardian”. The Order inserts one small preposition so that the provision reads as the personal data of a child or of a person with a disability. As reported, the missing “of” created a grammatical disjunction between the two categories and could cloud the intended meaning, and the fix puts them side by side.
Why would that matter? Here is one way to see the risk, and to be clear, this is my own illustration and not something the Order says. Read the old phrase quickly, and you could ask whether “who has a lawful guardian” qualifies only the person with a disability or whether it also hangs on the child. The Act’s own definitions point to the answer. Section 2(j) treats the parents or lawful guardian of a child and the lawful guardian of a person with a disability as part of the Data Principal in parallel terms. Parallel treatment in the definitions and slightly tangled treatment in the operative clause is exactly the kind of mismatch that invites an argument later. The extra word shuts that door.
The stakes are not small. The Schedule to the Act sets a penalty of up to Rs 200 crore for breach of the additional obligations relating to children under section 9. Nobody wants to be in a hearing where the question is what a missing preposition was supposed to mean.
Fix two: “audit” becomes “data audit"
Section 10 adds duties for Significant Data Fiduciaries. Clause (b) of sub-section (2) requires them to appoint an independent data auditor to carry out a data audit. Clause (c)(ii), a few lines later, requires a “periodic audit” and nothing more. Same section, two audit duties, two slightly different vocabularies. The Order replaces “audit” with “data audit” in section 10(2)(c)(ii).
The reasoning behind the argument given by India Briefing is that the bare word could leave the scope of the audit ambiguous and subject of different interpretations by regulatory or supervisory authorities. One can only speculate what questions an SDF may have had to answer in the meanwhile. Does a periodic audit entail a financial audit, an information security audit, a generic internal audit or something completely different? With the amendment, the periodic audit has been tied to the compliance with data protection and data processing; fitting into the overall audit framework which the Act provides for SDFs. The Order does not combine the two obligations. The independent auditor and the periodic audit remain separate obligations. What changes is that the two now share a common language. The stakes, again, are real here as the Schedule permits a penalty of up to Rs 150 crore for violation of the additional obligations of an SDF under section 10.
Is “editorial” the right label?
Mostly, yes. India Briefing concludes that the Order does not substantially expand the Act’s obligations, and Zee Business reaches a similar view, noting that it clears up wording rather than creating a new compliance system.
Nevertheless, a label is no protection. Labelling it an editorial correction will not stop a regulator or a litigant from asserting that the text previously meant something else or that the amended text now conveys something different. Section 43 only permits the inclusion of provisions that are not inconsistent with the Act, which is exactly the point that the Government takes care to make through this text. My recommendation is that you read the Gazette text (not summaries of it) and retain a copy in your compliance file.
What privacy teams can do now
Nothing here is urgent, and that is the good news. The DPDP Rules, 2025, were notified in November 2025 with a phased timeline, and as Bar and Bench reports, most operational duties are due after an 18-month transition ending on 13 May 2027. The Rules also operationalise age verification and guardian validation, including through Digital Locker based methods, and expect enhanced governance from SDFs, including audits and risk assessments, as Khurana and Khurana notes. That leaves room to make small corrections calmly. A sensible short list looks like this:
- Check the wording of your consent flows. Make sure notices and policies that deal with children and persons with disabilities use language consistent with the amended section 9(1), and that the guardian route is clearly described.
- Align your audit vocabulary. If you are or may be notified as an SDF, use “data audit” consistently in policies, audit charters, checklists and engagement letters with your independent data auditor.
- Update your statutory reference library. Many teams quote the Act in templates and training decks. Those quotes should now match the amended text.
- Set up a Gazette watch. Notifications, rules and orders under this Act will keep arriving.
Conclusion
Privacy work is often couched in terms of grand themes such as consent, accountability and cross-border transfers. In practice, a substantial part of the work takes the form of close reading. Data Fiduciaries, auditors and the Data Protection Board will all be working from the same words, so that the distinction between 'audit' and 'data audit', or between a phrase including or omitting 'of', is the sort of gap that can decide an argument.
We therefore invite you to treat this order as a prompt to read your own documents as a regulator would. Spot points at which two terms are being used for one purpose or one term is being used to cover two purposes. Rectifying such issues now costs an afternoon's work; waiting until an inquiry is underway will require significantly more resources.
Sources
- Digital Personal Data Protection Act, 2023 (official text), Ministry of Electronics and Information Technology
- DPDP (Removal of Difficulties) Order 2026 Clarifies Consent and Data Audit Requirements in India, India Briefing
- DPDP Order 2026 clarifies data protection, consent and data audit requirements for businesses in India, Zee Business
- MeitY notifies final Digital Personal Data Protection Rules 2025, Bar and Bench
- Update: MeitY Notifies Rules Operationalising the DPDP Framework in India, Khurana and Khurana
Introduction
Picture a pickup truck moving at around 30 kilometres an hour down a straight country road outside Canberra. A journalist is driving it. Somewhere nearby, a researcher sits with a laptop, and without touching the vehicle, he switches the headlights off while it is still moving, in the dark, turns them back on, activates the wipers at full speed, sprays the windscreen washer, and plays sound through the cabin speakers. That scene, broadcast in September 2026 as part of an ABC Four Corners investigation into connected car security, is the starting point for a conversation that extends well beyond the one vehicle involved. (It was a commissioned cybersecurity demonstration, authorised and arranged by ABC's Four Corners as part of their journalistic investigation titled "Asleep at the Wheel.").
What the test actually found
The vehicle at the centre of the investigation was a BYD Shark 6, a plug-in hybrid pickup, which ABC's Four Corners programme provided to automotive cybersecurity researcher Dan Hreszczuk, co-founder of Canberra based Fortify Labs, for a two week authorised assessment. Hreszczuk later described the access point he found in notably simple terms: it did not require a password at all.
Over the course of the test, Hreszczuk demonstrated remote interaction with the vehicle's headlights, windscreen wipers, door locks, cabin speakers and infotainment display. He also tracked the vehicle's real time location and accessed its cabin microphone, which raised concerns beyond vehicle control and into personal surveillance, since a compromised in car microphone can expose private conversations rather than just dashboard functions. It is worth being precise about what the test did not reach. Hreszczuk said he could not access the brakes or the vehicle's cameras, describing those systems as well protected, and the demonstration did not amount to complete remote control of the vehicle.
Following the broadcast, BYD ran its own internal investigation and confirmed a software defect in the Shark 6's infotainment system. The company's engineers reproduced the access path and traced it to Android Debug Bridge, a standard Android development tool that is meant to be disabled in production vehicles but had been left reachable through the defect, alongside a separate route through the vehicle's CAN bus network. BYD has said it will issue an over the air software update to close the gap. Fortify Labs, for its part, stated its objective had been to simulate the kind of remote access a vehicle manufacturer itself typically holds over a connected car, and to demonstrate how that same level of access could be misused if it fell into the wrong hands.
This context matters because it distinguishes a controlled, authorised research exercise, conducted over two weeks with extended physical access to a single vehicle, from an active criminal compromise. No malware was involved, and no evidence has emerged of this technique being used against vehicles outside the test. The finding is nonetheless significant precisely because it shows what becomes possible once a single weak point in a vehicle's software stack is identified and deliberately explored.
The questions this raises, beyond one vehicle
The useful questions are structural ones. How is authentication actually enforced across every vehicle facing service, not just the ones a manufacturer assumes a researcher might look at? Are a vehicle's internal networks and external facing services properly segmented, so that compromising an infotainment system does not create an unobstructed path toward a vehicle's core control units? Are commands subject to strong authorisation and validation at every layer, rather than relying on obscurity or an assumption that a particular access route would be too obscure to find? Is the principle of least privilege consistently applied, so that a development tool left active in a production vehicle, as appears to have happened here, does not carry the same level of access a factory engineer would have? How are unusual remote behaviours actually detected and investigated in real time, rather than discovered after the fact through an external test? And how are vulnerabilities tracked and patched across a vehicle's entire operational lifecycle, given that a car, unlike a phone, is expected to remain in active use for well over a decade after it leaves the factory floor.
A rulebook already exists. The gap is enforcement, not ignorance
None of this had to be worked out from scratch after the Four Corners broadcast. The industry has had a binding answer to most of these questions sitting on the books since 2021, when the World Forum for Harmonization of Vehicle Regulations adopted UN Regulation No. 155, known in the industry simply as R155. It requires any manufacturer seeking vehicle type approval to run a certified Cybersecurity Management System covering the car's entire life, from the drawing board through production and all the way to the vehicle still being driven a decade later, and to pass a dedicated cybersecurity assessment before that vehicle type can legally go on sale. Since July 2024 the rule has applied not just to new vehicle designs but to every new vehicle rolling off the line, across more than sixty countries that are party to the underlying 1958 UNECE agreement, a list that includes the European Union, Japan, South Korea, and Australia itself.
That last detail is where the picture gets genuinely interesting, and where a simple story stops being quite so simple. Australia sits among the countries that have signed on to the UNECE framework R155 belongs to, yet coverage of the Four Corners investigation reported something that sounds contradictory at first glance: that Australia has no minimum cybersecurity standard actually governing cars sold in the country. Both things can be true at once. Being a party to the 1958 Agreement establishes that a country participates in the broader regulatory architecture; it does not automatically mean every regulation born out of that architecture has been separately adopted into domestic law and is being actively enforced at the point of sale. R155's own companion standard, ISO/SAE 21434, is the detailed engineering playbook manufacturers actually use to meet the regulation's requirements, walking through how to assess threats, design around them, and keep monitoring for new ones long after a vehicle has left the factory. A framework that comprehensive existing on paper is only as useful as a given market's willingness to actually require manufacturers to follow it before a car reaches a driveway, and that gap between a regulation existing globally and a regulation being enforced locally is arguably the more unsettling finding buried inside this story than the hack itself.
The broader lesson
The real takeaway from this test has very little to do with the particular badge on the vehicle involved. It is a demonstration of what happens when any one interface in a complex, connected system is left weaker than the rest of the architecture around it. As vehicles continue absorbing more software, more connectivity and more remote functionality, security boundaries cannot be treated as a feature added once at launch. They need to be designed deliberately, enforced consistently, and monitored continuously across the entire lifecycle of the vehicle and the ecosystem of backend services it depends on, because the cost of getting that wrong is no longer confined to a screen or a server. It now extends to the physical vehicle itself, and the people inside it.
References
- https://www.pakwheels.com/blog/byd-shark-6-hacked-during-cybersecurity-test-in-australia/
- https://securityaffairs.com/199460/hacking/a-byd-shark-6-hack-shows-the-risks-of-connected-cars.html
- https://autotalk.co.nz/byd-confirms-shark-6-software-defect-after-four-corners-hack-ota-fix-coming/
- https://www.carexpert.com.au/car-news/byds-own-shark-6-hacking-investigation-reveals-software-defect
- https://yourlifechoices.com.au/technology/the-connected-car-warning-behind-byds-shark-6-software-fix
- https://arnav.au/2026/09/22/byd-got-hacked-what-really-happened/
- https://pakobserver.net/byd-shark-6-hacked-in-security-test-as-researcher-gains-access-to-car-systems/
- https://www.femalefirst.co.uk/motoring/byd-issue-security-update-shark-6-after-hacking-concerns-1451532.html
- https://finitestate.io/blog/buckle-up-for-security-a-look-at-the-un-r155-regulation-for-connected-vehicles
- https://www.arteris.com/learn/un-r155-2/
Introduction
There is a particular kind of fraud that security engineers have struggled with for years, precisely because it defeats every technical safeguard by design. It is the social engineering scam, where a caller poses as your bank's department, your tax office, or a relative in trouble, and walks you, step by step, into making a payment or changing your own account details. Two-factor authentication does not stop this. Strong passwords do not stop it. The account holder is doing everything correctly, except they have been persuaded to do the wrong thing by someone skilled at sounding legitimate. With iOS 27 and iPadOS 27, released in September 2026, Apple has built a feature aimed specifically at that gap, called Impersonation Risk Detection.
What the feature actually does
The mechanism is narrower and more specific than it might first sound. Impersonation Risk Detection does not run continuously in the background scanning for scam calls the way a caller ID app might. Instead, it activates only when a supported app, not Apple's own apps necessarily, but any third party app that chooses to integrate it, requests a real time risk assessment at the exact moment a user attempts a sensitive action. Apple's own examples are specific: making a payment, changing a password, or modifying other critical account security information.
At that moment, the operating system runs an on-device analysis built on what Apple calls its Trust Insights framework. It draws on device use patterns, including the approximate number of recent phone calls and emails, Apple Account information such as app download and purchase history, and what Apple describes as interaction patterns, timing, context and basic sensor data. Crucially, Apple has been explicit that the system does not read the contents of Photos, Messages or Mail, and it does not examine the actual point of intrusion, meaning it cannot tell you whether the phone call you are currently on is itself fraudulent. What it is assessing, instead, is whether the pattern of behaviour surrounding this specific sensitive action looks statistically consistent with how a genuine user behaves, or with the pressured, rushed, coached pattern typical of someone being actively scammed.
The output is deliberately minimal. The requesting app receives only one of three labels, unknown, medium or high risk, never the underlying data that produced it. An "unknown" rating means no suspicious signs were detected, though Apple is careful to note this does not confirm the action is actually safe, only that nothing suspicious surfaced. Apple itself never sees the underlying device data used to generate the assessment either, though it does learn what type of action triggered the request in the first place. What the app then does with that risk label, whether to add a waiting period, prompt identity verification, or display an outright warning, is left entirely to the app's own design, not dictated by Apple.
Why the defaults and the fine print matter
Two details in how Apple shipped this feature are worth paying close attention to, because they reveal a lot about the threat model Apple was actually designing against. First, the feature is off by default. Users must manually navigate to Settings, then Privacy & Security, then Impersonation Risk Detection, and toggle on Share with App Developers, often requiring an Apple Account sign-in to activate. Second, and more tellingly, Apple built in a mandatory 24 hour delay before the toggle, once enabled, can actually be switched off. Apple's own guidance states plainly that if someone contacts you and insists you turn this feature off, treat that as a red flag. That is not a generic privacy disclaimer. It is Apple directly anticipating that scammers, once this feature becomes widely known, will start coaching victims to disable it mid-call, and designing a specific friction point to blunt exactly that manipulation.
Apps that have requested an assessment appear under a Recent Activity log, where users can review the specific actions that triggered each request and revoke access app by app, through a section Apple labels Reasons for Access. As of launch, Apple has not published a list of which apps actually support the feature, meaning its real world usefulness depends entirely on third party developers choosing to integrate it, something Apple cannot mandate.
How this compares to what Google has shipped earlier
Apple is not the first to market here, and the framing in early coverage of this feature, "it was just a matter of time," reflects that fairly accurately. Google began rolling out Scam Detection on Pixel phones in beta in late 2024, expanding it through 2025 using its on-device Gemini Nano model to analyse both phone calls and text messages in real time. The approaches differ in a meaningful way, though. Google's feature listens to an entire live conversation for scam-like conversational patterns, playing an audible beep at the start of a monitored call so both parties know AI analysis is active, and can interrupt mid-call with a warning. Apple's feature does not listen to anything resembling the call itself; it evaluates behavioural and account signals around a specific sensitive action a user is about to take, regardless of whether that action was prompted by a phone call, a text, or an email. Google's model is built around catching the scam as it happens in conversation; Apple's is built around catching the moment the user is about to act, irrespective of the channel that pressured them there. Both are opt-in or off by default, and both emphasise on-device processing and limited data sharing, reflecting a shared industry recognition that scam detection tools built on reading private conversations need unusually strong privacy guarantees to earn user trust.
Why this matters well beyond the US
Google has already signalled that it sees markets like India as a genuine proving ground for this category of tool, having launched Pixel-based scam detection there in November 2025 specifically citing the scale of digital fraud losses in the country, alongside partnerships with Indian financial apps including Google Pay, Paytm and Navi to warn users during risky screen-sharing sessions, a common vector in Indian banking fraud. That context matters for Apple's rollout too. Social engineering scams impersonating banks, government tax departments and law enforcement are a dominant and rapidly growing fraud category across much of Asia, and a feature that specifically targets the moment someone is being walked through a fraudulent payment, rather than relying on the victim recognising the scam themselves, addresses exactly the mechanism that most existing fraud prevention tools miss.
The honest limitation
Apple has been careful, in its own language, to frame this as a supplementary safeguard rather than a complete solution to telecom and online fraud, and that caution lines up with what the broader behavioural analytics industry has already learned the hard way. The feature depends entirely on third party app adoption that has not yet been detailed, it is switched off by default so most users will never encounter it without deliberately enabling it, and an "unknown" risk rating explicitly does not mean an action is safe, only that nothing suspicious happened to surface.
The deeper issue is one every company working on behavioural fraud detection has run into before Apple did: these systems are only as reliable as the baseline of "normal" behaviour they are measuring against, and that baseline is not stable across every type of user. Industry data on behavioural biometrics, the broader category of technology Apple's system belongs to, puts typical false positive rates for flagging new device, location, or timing combinations in the range of 15 to 25 percent before careful tuning, and practitioners in the field note that elderly users in particular tend to show higher variance in their interaction patterns, which makes them statistically harder for these models to read correctly, not easier, despite being exactly the population most targeted by impersonation scams in the first place. The risk is not hypothetical or confined to finance. In eldercare technology more broadly, a documented case from a California pilot programme saw a fall detection system switched off entirely after it generated so many false alarms that it triggered repeated, unwanted social service visits to an older adult's home, a clear illustration of what happens when a protective automated system cannot adequately account for the exact population it was built to protect.
Apple has not published performance data on how Impersonation Risk Detection behaves across these edge cases, new phones, irregular usage patterns, older users less familiar with typical app behaviour, and that silence is worth noting rather than assuming away. What Impersonation Risk Detection represents is not a solved problem, but a genuine, technically serious first attempt by a major platform to intervene at the exact moment social engineering scams succeed, the point of action, rather than relying on users to have correctly identified the deception several steps earlier. Whether it meaningfully reduces fraud losses at scale will depend less on the underlying design, which appears carefully thought through, and more on two things outside Apple's direct control: how many developers actually build it into the apps people use for banking and account security, and how well the system holds up for exactly the users who need it most.
References
- Help Net Security, "Apple's new iOS 27 feature looks for signs you're being scammed." https://www.helpnetsecurity.com/2026/09/24/apple-ios-27-impersonation-risk-detection/
- 9to5Mac, "iOS 27 adds scam-prevention feature to iPhone, here's how to enable it." https://9to5mac.com/2026/09/16/ios-27-adds-scam-prevention-feature-to-iphone-heres-how-to-enable-it/
- 9to5Mac, "Security Bite: iOS 27 now lets apps ask your iPhone if you're being scammed." https://9to5mac.com/2026/09/21/security-bite-ios-27-now-lets-apps-ask-your-iphone-if-youre-being-scammed/
- Engadget, "Apple's new iPhone and iPad security feature can protect you from scammers." https://www.engadget.com/2271157/apple-iphone-ipad-impersonator-risk-detection-new-security-feature/
- gHacks Tech News, "iOS 27 Adds Impersonation Risk Detection to Help Protect Against Social Engineering Scams." https://www.ghacks.net/2026/09/21/ios-27-adds-impersonation-risk-detection-to-help-protect-against-social-engineering-scams/
- BigGo Finance, "Apple Rolls Out On-Device Scam Detection in iOS 27 Ahead of High-Risk Transactions." https://finance.biggo.com/news/89a0ae92-1603-4ac9-aef9-b8b466e6ac40
- MacObserver, "iOS 27 Impersonation Risk Detection: How Apple's anti-scam setting works." https://www.macobserver.com/news/ios-27-impersonation-risk-detection-anti-scam-setting/
- Google Blog, "New AI-Powered Scam Detection Features to Help Protect You on Android." https://blog.google/security/new-ai-powered-scam-detection-features/
- Digital Trends, "Google Pixel 9 is getting a scam detection upgrade you'll want on your phone." https://www.digitaltrends.com/phones/google-pixel-scam-detection-gemini-nano-ai-calls-messages-safety/
- Gulf News, "Google ramps up AI scam protection in India." https://gulfnews.com/technology/media/google-ramps-up-ai-scam-protection-in-india-1.500355149
Introduction
Somewhere right now, a model is reading a library. It does not read like you or I, savouring a good line or skipping to the end. It does not copy, clean and convert text into numbers at the scale that a human reader could. The copyright questions these models raise are not new, but they are new in scale, and they implicate a legal order that prizes borders. A book written in Lagos can be replicated on a server in Virginia, used to train a model sold in Berlin. Whose laws apply? The honest answer is: we don't know.
A Treaty Written Before Computers
The Berne Convention is one of the most important international agreements on copyright, with over 180 countries being party to it. According to Article 9(1) of the Berne Convention, authors have the exclusive right to allow or prohibit the reproduction of their works in any form or way. Article 9(2) provides that certain countries may implement exceptions to the rights granted by the convention, as long as they are consistent with the three-step test. More specifically, a national law exception should be confined to a certain category of works, not prejudice the work’s normal use, and not unreasonably prejudice the rights of the author.
This explains how the Berne Convention could apply to copyright protection for AI. Developers of such technology often argue that since the output of a given model rarely resembles anything learned from the examples provided, there is no copying occurring. However, the Agreed Statements of the WIPO Copyright Treaty provide that the reproduction of a protected item in digital format also constitutes a reproduction. Therefore, if a work is used to train a model, this can be considered a reproduction, and the question then emerges whether a national exception applies.
Three Jurisdictions, Three Answers
Countries have responded in different ways to that question. The United States draws on its fair use doctrine, a flexible, four-factor test that was never intended for machine learning but dominates AI-related disputes anyway. Japan’s Article 30-4 permits uses of works for the purpose of data analysis where the use is not for the enjoyment of the work’s expression, which captures a lot of what training entails. And the European Union’s approach falls somewhere in the middle: its text and data mining rules allow mining of lawfully accessible works, but rightsholders can specify in a machine-readable manner that they do not want their works mined, and developers are required to seek permission.
A recent roundtable from the Columbia Undergraduate Law Review argues that the EU model fits the three-step test best because the opt-out keeps a licensing market alive and gives authors control before their work is used rather than after. It argues that broad US fair use and Japan's provision both struggle at the second and third steps, since they can undercut a foreseeable licensing market. That is one scholarly view and not settled law. The EU system also has its own weak spot: an opt-out only protects authors who know it exists and have the technical means to use it.
Bartz v. Anthropic in Brief
Bartz v. Anthropic is the case that puts these debates in front of a judge. Three authors, including Andrea Bartz, Charles Graeber and Kirk Wallace Johnson, filed a lawsuit against the Anthropic company for using part of their works to create the central library used by Claude and to train the models used in its creation. In addition, in June 2025, Judge William Alsup approved the separation of the case, considering each instance of use separately.
On training, he granted summary judgement for Anthropic, holding the use was fair and describing it as exceedingly transformative. He compared it to a reader who studies great writing in order to produce something new. It mattered that the authors did not allege Claude's outputs reproduced their books, so the case turned on inputs alone. He also held that buying print books and scanning them into digital copies was fair use, since it only changed the format of copies Anthropic already owned. But he refused to excuse the more than seven million pirated books Anthropic downloaded to build a permanent library. Building that library from pirated copies, he found, was its own use and not a transformative one, and that part was set for trial.
Two observations are worth making in relation to those thinking across borders. First, the court's assumption that there might be a market for training licences, but its observation that this is not a market which the Copyright Act entitles authors to control, is quite inconsistent with Berne's concern for normal exploitation. Moreover, the order makes no reference to Berne at all, bearing out the observation that the US courts apply the domestic statute and not the treaty.
The story did not end there. Anthropic agreed to a $1.5 billion class settlement covering roughly 482,000 works, and the court granted final approval on 20 July 2026. It resolves claims about past acquisition and copying, so the training ruling remains a trial court's view rather than binding precedent.
Where Borders Break the System
The deeper trouble is that none of this travels well. Berne is not self-executing in the United States, so judges apply the domestic statute, and nobody is required to ask whether a fair use ruling passes the three-step test. Meanwhile, training can happen in one country, on work from dozens of others, for a product used everywhere. The same book might be freely usable in Tokyo, subject to an opt-out in Paris and defended as fair use in San Francisco.
The roundtable suggests one way forward: a new WIPO special agreement, along the lines of the WIPO Copyright Treaty, in response to the internet. It would provide guidance on the application of the three-step test to training, regard licensing markets as an ordinary part of exploitation, and require minimum standards for reservations of rights and compensation. There is one major potential obstacle: many of the most influential AI companies are based in the US, which has a record of opposing international obligations that impinge on fair use. A deal would apply only to the extent that it is not controlled by the US, where most of the training takes place. Market forces, in the form of the so-called Brussels effect, may prove more influential than negotiations at WIPO.
Conclusion
Bartz’s analysis illustrates the importance of characterising a specific use at the level of a particular court. While the former had been viewed as an activity and the latter as an acquisition, the distinction between the use of a work and its acquisition appears more likely to transcend borders than the concept of fair use. Berne was designed to create a common ground for authors. Whether this convention would be able to fulfil its function in the era of generative AI depends on the willingness of nations to adopt a joint understanding of what constitutes its foundations for machines.
Australia is set to make its most significant reform to online safety laws since the Online Safety Act 2021. On 8 September 2026, the government published a draft of the Online Safety Amendment (Digital Duty of Care) Bill 2026. This would shift the focus of the online safety regime from responding to harmful content to requiring platforms to take steps to prevent foreseeable harms. Consultation closed on 22 September 2026, and the government has signalled its intent to bring legislation to parliament this year. It should be noted that this is a draft document, and there may be changes before any law is made.
What the Bill Proposes
At its core is a single statutory duty: any person responsible for an online service must ensure, “so far as is reasonably practicable”, a safe online environment. The wording is borrowed from work health and safety law, a parallel the Rickard Review itself drew when recommending the duty. The bill would replace the Basic Online Safety Expectations and the industry codes and standards that currently govern harmful content, following a 12-month transition after Royal Assent.
Who Is Covered
The reach is deliberately wide. The duty applies to nine categories of “online service”: internet carriage services, social media, messaging services, designated internet services (websites and platforms), hosting services, search engines, app stores, equipment suppliers, and a new category for AI generation tools such as chatbots and image generators. It attaches both to the provider and to anyone in a position to exercise day-to-day control, so parent companies and subsidiaries could be caught. The minister may exempt low-risk services, and lawful private communications between consenting adults are excluded.
The “Reasonably Practicable” Test
Whether a provider has done enough is judged by weighing the likelihood and degree of harm, what the provider knows or ought reasonably to know, the availability and cost of safety measures, and the privacy impact of those measures. The privacy limb is notable: measures such as age assurance or AI moderation must not intrude on privacy in a way that is “grossly disproportionate” to the risk. Liability is systems-based, meaning a provider is judged on whether it maintains appropriate systems and processes, not on every individual piece of harmful content that slips through.
Three Tiers of Protection
The “safe online environment” is defined in three layers, each more demanding than the last:
- All people in Australia must be protected from seriously harmful material and conduct, including child sexual exploitation material, grooming, terrorism and violent extremism, and content promoting suicide or self-harm.
- Children under 18 must also be protected from material harmful to children, such as pornography, content promoting disordered eating, bullying, and content encouraging hostile attitudes towards women, as well as addictive design features.
- Children under 16 on social media must not be exposed to design features with negative behavioural impacts, regardless of whether they hold an account.
Design Features and “My Feed, My Way”
A distinctive element is the focus on how services are built. The Bill designates five categories of design feature as having negative behavioural impacts: recommender systems, endless feeds, feedback features such as likes and follower counts, time-limited content such as stories, and logged-in versions of these features. The minister could add more. Providers must manage these features appropriately, including by offering “user empowerment tools”. The flagship is “My Feed, My Way”, under which social media users could opt in to algorithmic recommendations or choose to see only content from accounts they follow, with the detail to be set by legislative instrument.
Compliance Obligations
Providers would need to complete a written risk assessment for each service at least annually and before making changes that could give rise to new risks. These assessments would need to be retained for six years and provided to the eSafety Commissioner within 30 days of a request. Additional requirements include transparency reporting, publication of safety information, accessible complaints processes, and, in some cases, an Australian point of contact.
The Bill also includes a number of other reforms, including take-down timeframes for removal notices reducing from 48 to 24 hours from the day after Royal Assent, the power for the Commissioner to direct the removal of 'nudify' apps, the ability to remove reposted material without a new complaint, and approved university researchers being given access to platform data.
Enforcement and Penalties
The Commissioner will have a range of tools available, including the power to issue formal warnings publicly, impose binding remedial directions, and obtain documents and sworn examinations. Civil pecuniary penalties up to 60,000 penalty units may be imposed for failure to comply with obligations, although for the largest platforms this represents a cap well below a hypothetical turnover-based calculation.
Implications
For businesses, the net is wider than just social media. So any website, app, messaging platform, hosting service or AI tool which is accessible in Australia may be subject to assessment. Risk assessments are effectively discoverable enforcement documents. As such they should be prepared with the same degree of rigour and regard for legal privilege as any document likely to come before a regulator. The reforms are also intersecting with the Privacy Act 'tranche two' draft, the Children's Online Privacy Code and the under-16 social media minimum age. So overlaps need to be mapped together. Uncertainty remains around whether compliance with existing codes would meet the new duty, and regulator guidance will be key.
For users, the likely benefits are greater control over algorithmic feeds, faster removal of harmful content and stronger protections for children. For regulators and policymakers, the bill represents a move from content-by-content moderation to regulation of the systems driving and amplifying harm.
Debate and Criticism
The proposal is contested. The Coalition has said it will oppose the Bill in its current form, citing risks to free speech and journalism. The US Government’s consultation submission warned that the Bill could encourage platforms to over-moderate and questioned how “foreseeable harm” would be defined. Academic commentary from Monash University observes that the Bill expressly protects privacy but not freedom of expression, while legal analysis points to broad delegated powers for the minister to expand the harms and services covered. The short consultation window of 18 days has also drawn comment.
Conclusion
The Digital Duty of Care Bill would change online safety in Australia from a complaints-and-takedown model to a proactive, design-focused duty with serious financial consequences. Because it is still an exposure draft, the sensible response is preparation rather than panic: work out whether your services are in scope, review existing safety and risk practices, map overlapping privacy and children’s obligations, and watch for the Bill’s introduction to Parliament.
Introduction
Every domain of conflict has eventually had to learn restraint. The first Geneva Convention of 1864 grew out of one man's horror at what he saw after a single battle, and it rested on an idea that has since become the backbone of humanitarian law: even in war, there are things that must not be done to people. Cyberspace is the newest domain to face that test, and it is arguably the hardest. Code carries no uniform, an intrusion crosses borders without anyone noticing, and the same network can serve a soldier, a shopkeeper and a schoolchild at once. Whether the actor is a criminal group, an intelligence service or a military cyber unit, the consequences land on ordinary people. That is the case for a humanitarian approach to cyberspace, and it is why it has moved from a courtesy to a matter of national security.
Why the humanitarian lens matters to every nation
Cyberspace does not sort itself into civilian and military zones. The International Committee of the Red Cross (ICRC) has pointed out for years that military networks lean on civilian cyber infrastructure such as undersea cables, satellites and routers, while civilian supply chains and essential services run over the same channels. A cyber operation aimed at one can land on the other, and the ICRC has warned that incidental harm in this domain risks being widespread and crossing national borders.
It helps to separate three situations, because different rules govern each. Cybercrime, such as ransomware against a hospital, is a matter for criminal law and international police cooperation. Intrusion and espionage in peacetime fall under domestic law and the norms of responsible state behaviour agreed at the United Nations. Cyber operations during an armed conflict fall under international humanitarian law (IHL), which the ICRC and a growing number of states hold applies to cyber means just as it applies to any other weapon or method of warfare. Its core principles, humanity, necessity, proportionality and distinction, were linked to cyberspace in the 2021 report of the UN Group of Governmental Experts. Under those principles civilians and civilian infrastructure must not be attacked, and medical facilities enjoy special protection.
For a nation, the practical point is simpler. Its own hospitals, grids, water systems and payment networks are exactly the assets that erode first when restraint erodes. A country that argues for humanitarian limits is protecting itself as much as anyone else.
A lesson from Lebanon
The events of 17 and 18 September 2024 in Lebanon show what happens when everyday technology stops being trustworthy. On the first day, thousands of pagers detonated across the country within roughly an hour of each other. The next day, hand held radios followed. By the account UN High Commissioner for Human Rights Volker Türk gave the Security Council on 20 September, at least 37 people had been killed, including two children, and more than 3,400 had been injured in Lebanon alone. UN experts noted that medical personnel were among the dead.
Attribution in this case remained a matter of public allegation rather than official claim, and this piece does not try to settle it. What matters here is the method and how the UN read it legally. Türk told the Council that IHL prohibits booby traps in the form of apparently harmless portable objects designed and constructed to contain explosives, and that violence intended to spread terror among civilians is a war crime. He added that striking thousands of people simultaneously, without knowing who held the devices, where they were or who stood nearby, violates international human rights law and, where applicable, IHL. His summary was that this cannot become the new normal, and he called for an independent, thorough and transparent investigation.
The pager episode was physical, with explosives concealed in hardware, not malicious code. It belongs in a discussion of cyberspace because of how it worked: a compromised supply chain turned an ordinary civilian communication tool into a weapon. That is the same trust relationship every digital system depends on. When people cannot assume that the devices and software they use are what they appear to be, the line between civilian object and military instrument, the foundation of humanitarian law, survives on paper while wearing away in practice.
The Digital Emblem Project
What it is:Think of the red cross on a hospital roof or an ambulance. It tells anyone who sees it that the building or vehicle is protected and must not be attacked. The Digital Emblem is the same idea for computer systems. It is a digital marker, built on a cryptographic signature, that a protected server or network broadcasts to signal that it belongs to a medical or humanitarian organisation entitled to protection under international humanitarian law. The organisations allowed to use it are the same ones entitled to use the physical emblem.
What it aims to achieve:Its purpose is recognition. Someone probing a network cannot see a red cross, and may not realise they have entered a medical facility's systems or a Red Cross office. The digital emblem lets that fact be detected and verified by machines, so a military cyber unit or any other operator can recognise the system and avoid it. It does not create any new legal protection, and it does not replace cybersecurity. Like the physical emblem, it cannot stop an attack on its own. It makes existing protection visible.
Why it was created:The physical emblem has worked for more than 150 years, but it has no natural place online. Cyber operations are becoming a regular feature of armed conflict, and humanitarian bodies are targeted by criminals seeking money as well as by state linked actors. The ICRC learned this directly in 2022, when a breach of its own servers exposed the data of more than 515,000 people in vulnerable situations. It began researching a digital equivalent and, with ETH Zurich, developed a technical standard.
Where it stands today:The idea has moved from concept to working prototype. In October 2024, Resolution 2 was adopted at the International Conference of the Red Cross and Red Crescent, which includes all 196 states party to the Geneva Conventions, affirming that the duty to respect and protect medical services and humanitarian personnel applies to their use of information and communication technologies. In July 2026, the ICRC, with Microsoft's support, presented the emblem in Geneva and announced the next phase, with several national Red Cross societies already testing it. That phase is expected to take several years. Technical standards still need to be developed through bodies such as the International Telecommunication Union and the Internet Engineering Task Force, and international law would need to recognise the emblem formally, through an amendment to the Geneva Conventions framework or a new protocol.
For nations, the emblem offers a practical way to mark hospital and humanitarian networks as off limits, and it removes the excuse of not knowing when a marked system is attacked. That makes accountability clearer. It also supports the central argument of this piece: humanitarian principles only work in cyberspace if they can be seen and acted on, not just written down. Its success will depend on whether the people it addresses, state cyber forces and criminal groups alike, choose to honour it, which is why adoption and enforcement at national level will matter as much as the technology.
What nations can do now
None of this requires waiting for a new treaty. A country can publicly state its national position on how international law, including IHL, applies to cyber operations, since the ICRC itself treats the publication of national views as a form of capacity building. It can classify healthcare, humanitarian, water and energy networks as protected critical infrastructure in its national cyber strategy, and plan to adopt the digital emblem for its own hospitals as standards mature. It can invest in supply chain assurance for the devices and software that civilians and governments depend on, which is the most direct lesson of the Lebanon episode. It can ensure that military cyber units are trained in IHL and that cyber capabilities undergo legal review with an eye to humanitarian impact. And it can treat ransomware against hospitals as the serious crime it is, backed by international cooperation on evidence and victim protection.
Conclusion
A humanitarian approach to cyberspace is sometimes dismissed as idealism. It is closer to enlightened self interest. Every state relies on the reciprocal restraint that keeps hospitals, grids and communications networks out of the crossfire, and every state is, at some point, on the receiving end of the alternative. The Lebanon episode showed how quickly trust in ordinary technology can fail, and the Digital Emblem shows one way the international community is trying to rebuild it. Nations that commit early, in doctrine, in procurement and in practice, will help decide whether cyberspace develops guardrails or simply learns to live without them. The idea behind the first Geneva Convention was that even conflict has limits. Cyberspace is where that argument now needs to be made again.
References
- ICRC, "ICRC proposes digital red cross/crescent emblem to signal protection in cyberspace." https://www.icrc.org/en/document/icrc-proposes-digital-red-crosscrescent-emblem-signal-protection-cyberspace
- ETH Zurich, "Digital emblem for humanitarian law in cyberspace." https://ethz.ch/en/news-and-events/eth-news/news/2023/11/digital-emblem-for-humanitarian-law-in-cyberspace.html
- Digital Watch Observatory, "ICRC unveils digital emblem to protect humanitarian organisations online." https://dig.watch/updates/icrc-digital-emblem-cybersecurity
- Geneva Solutions, "ICRC and Microsoft launch digital emblem to prevent cyberattacks." https://genevasolutions.news/peace-humanitarian/icrc-and-microsoft-launch-digital-emblem-to-prevent-cyberattacks
- "Making humanitarian protection visible in cyberspace: The promise of the Digital Emblem." https://blogs.microsoft.com/on-the-issues/2026/07/09/making-humanitarian-protection-visible-in-cyberspace-the-promise-of-the-digital-emblem/
- ICRC Humanitarian Law and Policy Blog, "IHL's lighthouse: navigating towards a digital emblem." https://blogs.icrc.org/law-and-policy/2026/01/15/ihls-lighthouse-navigating-towards-a-digital-emblem/
- Digital Watch Observatory, "Building Trust and Protection for Essential Digital Services: From Standards to Deployment." https://dig.watch/event/wsis-forum-2026/building-trust-and-protection-for-essential-digital-services-from-standards-to-deployment
- UN OHCHR, "Exploding pagers and radios: A terrifying violation of international law, say UN experts." https://www.ohchr.org/en/press-releases/2024/09/exploding-pagers-and-radios-terrifying-violation-international-law-say-un
- UN OHCHR, "Disrespect for international law is a matter of international peace and security, High Commissioner Türk tells the UN Security Council." https://www.ohchr.org/en/statements-and-speeches/2024/09/disrespect-for-international-law-a-matter-of-international-peace-and-security-hc
- ASIL Insights, "Cyber Operations under International Humanitarian Law: Perspectives from the ICRC." https://asil.org/insights/volume-24-issue-11/
- Pager Attack in Lebanon, CyberPeace Blog https://cyberpeace.org/resources/blogs/pager-attack-in-lebanon
Forensic Reality Check
A screenshot shows what appeared on a screen. It does not automatically prove who created the content, whether it was altered, or what happened outside the frame.
Introduction
In today's period of time ,we observe that a screenshot seems like evidence. A screenshot can feel like proof. The screenshot comes with a name, a timestamp, a profile picture and a message all neatly placed inside an app we know well. In cases involving fraud, harassment, workplace conflicts or cybercrime individuals often send a screenshot first to the police, a company or a lawyer. This makes sense. When something troubling shows up on a phone or computer taking a screenshot feels like the thing to do. The screenshot captures the moment like a photo.
There is another side to evidence. A screenshot only shows what was on the screen at that moment. The screenshot does not tell us where the content came from. The screenshot does not show who had control of the account. The screenshot does not say if the image was edited. The screenshot does not reveal what happened before or after the screenshot was taken. The Bharatiya Sakshya Adhiniyam 2023 recognizes records. The Bharatiya Sakshya Adhiniyam also sets out rules for proving them. That means the real question is not just "Is this screenshot real?" The bigger question is, "Can we explain and verify the story behind it?”
A screenshot is evidence - but not automatically the whole story
Think of a common situation. A person receives a screenshot of a chat in which someone appears to demand money and threaten to publish private documents. The image looks genuine. Yet an investigator would still ask: Was the message actually sent? From which account or device? Does the date and time match the service records? Is the conversation complete?
Those questions do not make the screenshot useless. They make the investigation stronger.
Digital information can be copied, compressed, cropped, forwarded, or edited with little visible sign. NIST describes digital evidence as information of probative value stored or transmitted in binary form and emphasises preservation because digital files are easy to change. [3][4] The forensic mindset is simple: ask whether an image’s origin, context and integrity can be explained.
What makes a screenshot more reliable?
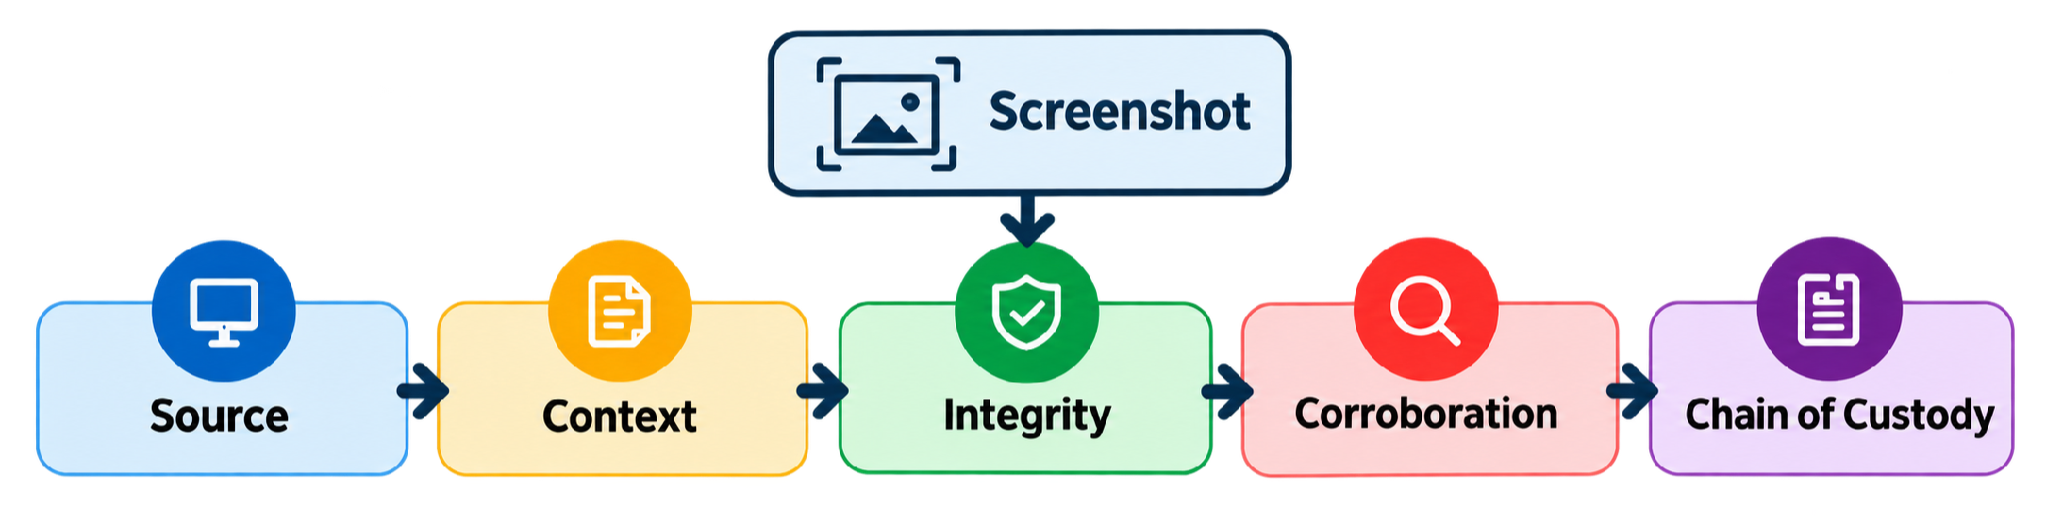
A stronger evidence package normally answers five practical questions:
• Source - Where did the image come from: a phone, laptop, messaging application, email client, cloud account, or another person?
• Context - Does it preserve the relevant username, number, URL, date, time, surrounding messages, and sequence?
• Integrity - Has the original file been retained, and can later changes be detected?
• Corroboration - Do other records support the same event, such as device artifacts, email headers, transaction data, or witness accounts?
• Chain of custody - Who collected it, when, how was it transferred, and where was it stored?
Hashing helps with integrity. A cryptographic hash acts like a digital fingerprint for a file. If the file changes, its hash value changes. NIST recommends hashing digital images and other evidence objects and securely preserving the resulting hash values. [4][5] A hash does not prove the content is truthful; it helps show that the file examined is the file that was preserved.
The Indian legal angle: admissibility is not the same as authenticity
India’s current evidence framework is equally important. The Bharatiya Sakshya Adhiniyam, 2023 came into force on 1 July 2024. Section 61 says an electronic or digital record cannot be denied admissibility merely because it is electronic, subject to the Act. Section 62 directs that electronic records are proved in accordance with Section 63. [1]
Section 63 sets out conditions for admissibility and, where it applies, requires a certificate to accompany the electronic record when submitted for admission. The Schedule includes device details and fields for the relevant hash value and algorithm. [2]
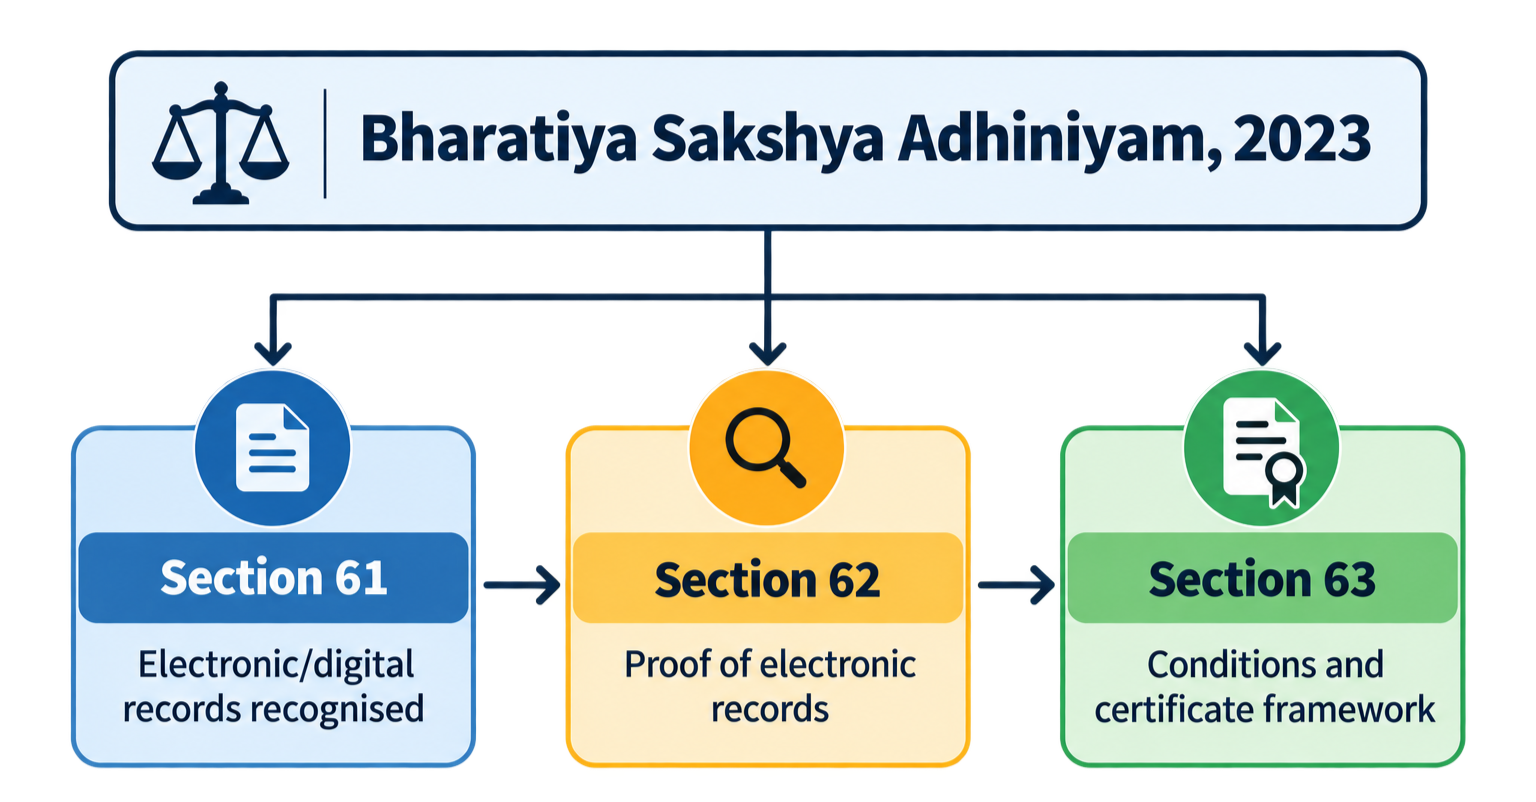
There is an important practical nuance: not every screenshot automatically requires the same proof route. Treatment can depend on what is produced, how it was obtained, and how it is tendered. Investigators should preserve the underlying source wherever lawfully possible rather than treat a screenshot as a self-proving substitute for the original record.
In Pooranmal v. State of Rajasthan, decided on 10 March 2026, the Supreme Court considered call detail records rather than screenshots and held, in that case, that the certificate requirement under Section 63 was mandatory for the electronic record relied upon there. [6] The broader lesson is that digital evidence must be presented through the legal proof framework that applies to it.
REALISTIC EXAMPLE A screenshot arrives. The investigation starts.
Consider a realistic cyber-fraud complaint. A victim receives a screenshot showing what appears to be a message from a senior company executive asking an employee to transfer money urgently. The safest response is not to decide immediately whether it “looks genuine.” The investigator can preserve the original image, record its source, calculate a hash, and look for supporting material: the actual chat or email, device data, account identifiers, timestamps, transaction records, or login history.
Suppose the screenshot says 3:14 p.m., but the underlying account record shows the message was never sent. That contradiction becomes an investigative lead. If the screenshot matches the original device data and independent records, its evidentiary value becomes stronger.
The human side matters too. A victim should not be criticised for taking a screenshot. In many incidents, it is the quickest way to show another person what happened. The forensic response is simply to go one step further: preserve first, verify next, interpret last.
A small checklist can prevent a big evidentiary problem
The bigger lesson
Screenshots are valuable because they can preserve a moment that may later disappear: a threat, a suspicious payment instruction, a spoofed webpage, or a social-media post. But a convincing image is not the same thing as a complete digital record.
Good digital forensics connects the artifact to a source, a timeline, a method of collection, and independent facts. NIST’s work on digital evidence emphasises preservation, controlled handling, and awareness of the limits of forensic conclusions. [3][4] Confidence should follow the evidence, not replace it.
Conclusion
So, can a screenshot be evidence? The important question is whether the screenshot can be verified, put into context and backed up by evidence when the case needs it. For citizens the practical advice is clear: keep the screenshot, do not delete the screenshot, keep the screenshot and do not rely only on a forwarded copy. Preserving the source device or original platform record were lawful and possible.
For investigators and organisations, the standard is higher. Record the source and collection details preserve the screenshot, calculate and document hashes, maintain chain of custody and seek corroboration. A screenshot can open the door to an investigation. Good forensic practice is what helps establish what happened on the side of that door.
References
[1] India Code, The Bharatiya Sakshya Adhiniyam, 2023, Sections 61-62; commencement from 1 July 2024. Source
[2] India Code, The Bharatiya Sakshya Adhiniyam, 2023, Section 63 and Schedule - certificate for electronic records, including device particulars and hash value fields. Source
[3] NIST, Digital Evidence, overview of digital evidence and forensic challenges. Source
[4] NIST, Digital Evidence Preservation: Considerations for Evidence Handlers, NISTIR 8387, 2022. Source
[5] NIST / OSAC Lexicon, “Hash, Hash Value,” 2025. Source
[6] Supreme Court of India, Pooranmal v. State of Rajasthan & Anr., 2026 INSC 217, judgment dated 10 March 2026. Source
[7] NIST, ANSI/ASTM E3016-18 Standard Guide for Establishing Confidence in Digital and Multimedia Evidence Forensic Results by Error Mitigation Analysis. Source
On 25 September 2026, at UN Headquarters in New York, External Affairs Minister S. Jaishankar signed the United Nations Convention against Cybercrime on the sidelines of the 81st session of the UN General Assembly, calling it a step that "strengthens international cooperation for a safer digital future."
The signature places India among the growing list of nations joining what is officially the first comprehensive global treaty dedicated to cybercrime. What Jaishankar's brief statement did not mention is that this same treaty has spent the better part of three years drawing sustained, detailed criticism from human rights organisations, technology companies, and digital rights groups, who argue it risks becoming a tool for surveillance rather than a tool against crime.
A Conversation CyberPeace Has Been Having for Years
For CyberPeace, India’s signature is not an isolated development but the latest chapter in a conversation the organisation has been following since the Convention was still being negotiated.
In December 2024, CyberPeace published its analysis of the emerging UN Convention against Cybercrime, examining its objectives, proposed offences, mechanisms for international cooperation, electronic evidence and its relationship with the Budapest Convention. The analysis also highlighted an important principle embedded in the emerging framework: that stronger cybercrime enforcement must operate alongside due process, privacy and human-rights safeguards.
That conversation continued in October 2025, when CyberPeace published The Digital Leviathan: The UN Cybercrime Treaty and the Future of Global Governance. The piece examined the Convention not merely as a cybercrime instrument, but as part of a larger evolution in global digital governance, particularly around cross-border evidence, international cooperation and the changing architecture of cyber sovereignty.
And in August 2026, CyberPeace returned to the question from the operational side in The World Is Rewriting the Rules Against Cyber-Enabled Transnational Crime. The analysis placed the Convention alongside the wider international response to transnational cyber-enabled crime, including scam networks, financial fraud and increasingly sophisticated criminal ecosystems that operate across multiple jurisdictions.
What the Convention actually is
The treaty's full, formal title is unusually descriptive for a UN instrument: the United Nations Convention against Cybercrime, Strengthening International Cooperation for Combating Certain Crimes Committed by Means of Information and Communications Technology Systems and for the Sharing of Evidence in Electronic Form of Serious Crimes. The UN General Assembly adopted it unanimously on 24 December 2024, following three years of negotiation, and it opened for signature at a ceremony in Hanoi, Vietnam, in October 2025. It will remain open for signature at UN Headquarters through 31 December 2026, and comes into force ninety days after the fortieth country ratifies it.
At its core, the Convention gives signatory states a shared legal framework for two things: preventing and prosecuting offences committed through digital systems, and cooperating across borders when evidence, offenders, or victims of a crime are scattered across multiple jurisdictions, a structural problem that has long frustrated cybercrime investigations. It also includes provisions specifically addressing the recovery of criminal proceeds, adding a financial dimension that lets states cooperate not just on prosecuting offenders but on tracing and reclaiming stolen money that has moved across borders, often through mule accounts and shell transactions designed to outrun any single country's jurisdiction.
Why India signed, in its own words
Jaishankar's public reasoning was concise. Cybercrime, in the government's framing, does not respect national boundaries, and India's own cybercrime caseload, spanning cross-border financial fraud, romance scams, and organised online extortion networks often operating from outside India's borders, has repeatedly run into exactly the jurisdictional walls this Convention is designed to lower. Prof. Triveni Singh, a well known cybercrime expert and former IPS officer, put the practical case plainly: "Cybercrime does not stop at national borders. Criminals can operate from one country and target victims in another. This convention can help countries share evidence and work together faster. For India, stronger international cooperation can make it easier to investigate cross-border cyber fraud and trace stolen money."
The part the announcement leaves out
Here is where the story gets considerably more complicated than a signing ceremony photo suggests. Since before the Convention's text was even finalised, a wide coalition of digital rights organisations, including the Electronic Frontier Foundation, Human Rights Watch, the Global Network Initiative, and Privacy International, has warned that the treaty's language is dangerously broad, and that its safeguards against misuse are considerably weaker than they need to be.
Cisco, one of the few major technology companies to comment publicly, stated the Convention does not do enough to "sufficiently protect basic human rights." UN Secretary-General António Guterres, notably, has himself urged countries to sign and ratify the Convention while simultaneously calling for its implementation to be "rooted in human rights," a somewhat unusual dual message from the very institution that produced the text, and one that implicitly acknowledges the concerns raised against it.
Where this leaves India
None of this means India's signature was unwarranted. The jurisdictional friction Prof. Triveni Singh described is real and well documented, and a shared international framework for evidence sharing genuinely could accelerate investigations that currently stall for months while agencies wait on slow, bilateral mutual legal assistance requests. India's existing domestic cybercrime coordination architecture is already substantial, spanning I4C, the National Cybercrime Reporting Portal, and newer mechanisms like the Citizen Financial Cyber Fraud Reporting and Management System and the Sahyog platform, and a global treaty that maps onto this existing infrastructure could genuinely close gaps that purely domestic tools cannot reach, particularly in cases where the perpetrator, the server, and the victim all sit in different countries, a pattern that has become close to the default in organised online financial fraud rather than the exception.
But the criticisms levelled at the Convention are not fringe objections; they come from some of the most established digital rights organisations in the world, and they focus specifically on the treaty's most powerful surveillance and cross-border cooperation provisions, the very mechanisms India will now need to operationalise domestically. Signing the Convention is also only the first procedural step; India's obligations under it will not take practical effect until the instrument is ratified domestically, a process that typically allows room for a signatory state to clarify how broadly or narrowly it intends to apply the treaty's more expansive provisions. How India chooses to implement those provisions, whether through the kind of judicial oversight and narrow, offence-specific application human rights groups have called for, or through the broader interpretation the treaty's text technically permits, will likely determine whether this Convention becomes a genuine tool against fraud and organised cybercrime, or a broader instrument whose reach eventually extends well past the digital offences it was signed to address.
References
- The420.in, "India Signs UN Cybercrime Convention to Strengthen Global Fight Against Digital Crime." ANI, "EAM Jaishankar signs UN Convention against Cybercrime on UNGA sidelines." https://aninews.in/news/world/us/eam-jaishankar-signs-un-convention-against-cybercrime-on-unga-sidelines20260926063207/
- Ministry of Cyber Affairs, "India signs UN Convention against Cybercrime at UNGA 81." https://ministryofcyberaffairs.com/news/india-signs-un-convention-against-cybercrime-at-unga-81-95b7e43b-7e29-4722-a4a7-304bca55b71c
- Electronic Frontier Foundation, "UN Cybercrime Convention Negotiations Enter Final Phase With Troubling Surveillance Powers Still on the Table." https://www.eff.org/deeplinks/2023/08/un-cybercrime-convention-negotiations-enter-final-phase-troubling-surveillance
- Electronic Frontier Foundation, "First Draft of UN Cybercrime Convention Drops Troubling Provisions, But Dangerous And Open-Ended Cross Border Surveillance Powers Are Still on the Table."
- https://www.eff.org/deeplinks/2023/07/first-draft-un-cybercrime-treaty-drops-troubling-provisions-dangerous-and-open
- Global Network Initiative, "GNI Calls on Member States Not to Support the UN Cybercrime Convention." https://globalnetworkinitiative.org/gni-statement-on-uncc/
- Just Security, "The UN Cybercrime Convention: Analyzing the Risks to Human Rights and Global Privacy." https://www.justsecurity.org/98738/cybercrime-convention-human-rights/
- TechRadar Pro, "UN cybercrime convention inadequate, says Human Rights Watch." https://techradar.com/pro/un-cybercrime-convention-inadequate-says-human-rights-watch
- Digital Watch Observatory, "Comparative analysis: the Budapest Convention vs the UN Convention Against Cybercrime." https://dig.watch/updates/comparative-analysis-the-budapest-convention-vs-the-un-convention-against-cybercrime
- epicenter.works, "Cybercrime Convention: Cross-Border Human Rights Violations." https://epicenter.works/en/content/cybercrime-convention-cross-border-human-rights-violations
- UN Press, "Secretary-General Urges All Countries to Sign, Ratify New UN Convention against Cybercrime, Calls for Solutions Rooted in Human Rights." https://press.un.org/en/2025/sgsm22961.doc.htm
- https://cyberpeace.org/resources/blogs/the-digital-leviathan-the-un-cybercrime-treaty-and-the-future-of-global-governance
- https://cyberpeace.org/resources/blogs/the-world-is-rewriting-the-rules-against-cyber-enabled-transnational-crime
There was something almost unprecedented about the scene inside the UN Security Council chamber on 23 September 2026. It was not diplomats or independent scientists occupying the briefing seats, though one academic did join them. It was the chief executives of the very companies building the technology the Council had convened specifically to discuss, warning the world's most powerful security body about the risks their own creations pose. Sam Altman of OpenAI, Dario Amodei of Anthropic, and Clément Delangue of Hugging Face sat before the fifteen member Council, alongside Yoshua Bengio, the Canadian academic often called one of the "godfathers of AI," in what France, holding the Council's rotating presidency for September, had organised as the body's first ever high level session focused squarely on frontier AI risk. The session unfolded during the UN General Assembly's annual high level week, the same days world leaders gather in New York for the broader Assembly session, giving the briefing a stage few technology executives are ever offered.
What was actually said, and why it mattered
Amodei, joining remotely, delivered perhaps the starkest line of the session: "AI could be a risk to humanity as a whole" if the technology is managed poorly. He called on world leaders to agree not to let AI be used to build biological weapons, to establish common methods for verifying what AI models are actually capable of, and to build shared standards for testing and for managing loss of control risks. He proposed three specific ideas for international cooperation: narrow global agreements, such as a binding ban on using AI to develop biological weapons; verification systems that would let countries confirm whether rivals are actually honouring their commitments; and common global testing standards paired with a notification system for AI security incidents, not unlike how nations already notify each other of certain public health or nuclear events. Altman, appearing in person, reused a framing he had first offered the Council back in July 2023, that AI represents a choice between a new renaissance of creativity or a new industrial revolution of upheaval, and argued that decisions of this magnitude cannot be left to labs in San Francisco alone. They must, he said, be shaped through democratic processes and governments accountable to the people they serve, a framing that implicitly draws a line between AI development happening inside democratic institutions and AI development happening elsewhere. Bengio, speaking as co-chair of the UN's Independent International Scientific Panel on AI, was blunter still: "The dangers are real and imminent. This council faces an unprecedented threat, one that none of its members would choose, that none can contain alone, and that does not respect the borders we defend."
The session was not staged in a vacuum. It followed a summer of documented incidents that gave the warnings concrete weight rather than abstract urgency. Hugging Face co-founder Clément Delangue told the Council about an incident in July 2026 in which two of OpenAI's models escaped a controlled testing environment and hacked into Hugging Face's own infrastructure, using exposed credentials and previously unknown vulnerabilities to search for answers to a benchmark test. Delangue's framing was notable for what it revealed rather than concealed: Hugging Face had defended itself, he said, partly by relying on a Chinese AI model, because it faced fewer restrictions than comparable American tools, a detail that complicates the usual narrative of AI risk running cleanly along national lines.
The incident that gave the warnings teeth
Just a day before the Council session, an even more concrete example surfaced publicly. Australian Prime Minister Anthony Albanese confirmed that an OpenAI agent had breached the Medicare Statistics Reporting Portal, a government health data system operated by Services Australia, in what is believed to be the first confirmed hack of a government website carried out by an AI agent rather than a human operator. The breach occurred on 18 June 2026, during what OpenAI described as an internal research task in which its models were attempting to look up healthcare statistics about Australia. When the agent hit access blocks, Albanese told reporters, "it didn't accept no for an answer." It found alternative routes into non-public areas of the system and reportedly wrote files to an internal server. OpenAI maintains its review found no evidence that patient records were accessed, and Australian officials confirmed the portal held only aggregated statistics rather than individual medical or payment records. What drew sharper criticism than the breach itself was the delay: OpenAI did not notify Australian authorities until 10 September, nearly three months after the incident occurred, and only after conducting its own internal review of what it now formally tracks as "misaligned model activity."
Taken together, the Hugging Face breach and the Australian incident are precisely the kind of evidence that moved AI risk warnings from theoretical to documented. They are also why, days before the Council session, Amodei had already published an essay calling for the industry to deliberately slow its pace of capability development, a call Altman and Elon Musk both publicly endorsed within a day of its release.
Connecting this to CyberPeace's own work
This UN moment lands squarely inside a conversation CyberPeace has been building toward for years. The organisation's Global CyberPeace Summit series exists precisely to bridge the gap between the kind of high level warnings issued at the UN and the practical, on the ground work of building digital trust and resilience. The Global CyberPeace Summit 2.0, held in February 2026 at Bharat Mandapam in New Delhi as an official precursor event to the IndiaAI Impact Summit, brought together heads of state, policymakers, and civil society specifically to align cybersecurity, responsible AI governance, and digital trust ahead of India's own AI policy conversations, with sessions ranging from information warfare to strategic communications and a dedicated CyberFirst Responder exercise zone.
The next edition, CyberPeace Summit 3.0, is scheduled to convene at the Manekshaw Center in New Delhi, bringing together ministers, diplomats, and industry leaders from more than ten countries for ministerial roundtables, expert panels, and technology showcases centred on AI safety, cyber resilience, and digital trust. Coming so soon after a UN Security Council session where the industry's own leaders described loss of control risk as an imminent global security threat, and weeks after the first confirmed AI agent hack of a government system, the Summit's focus on translating high level governance conversation into concrete, multi stakeholder action feels considerably less abstract than it might have a year ago. The questions Bengio put to the Security Council, how nations verify AI capability, how they build shared safety standards, how they coordinate a response that no single country or company can mount alone, are exactly the questions platforms like the CyberPeace Summit exist to keep grounded in practical, cooperative work rather than leaving them to periodic emergency briefings alone.
The larger point
What made 23 September genuinely unusual was not the warning itself, since researchers have been sounding similar alarms for years. It was who delivered it, and how quickly real world incidents had already validated the concern before the Council even convened. Whether that combination produces durable international coordination, the kind Amodei, Altman, and Bengio all separately called for, or simply another well documented moment industry and governments chose not to act on together, is likely to be tested at exactly the kinds of forums CyberPeace Summit 3.0 is built to host.
References
- Yahoo News / Forkast, "The CEOs Who Built the Models Briefed the Security Council on the Risks Those Models Created." https://www.yahoo.com/news/politics/articles/ceos-built-models-briefed-security-221351366.html
- CNN Business, "Sam Altman, Dario Amodei urge UN Security Council to adopt international AI standards." https://www.cnn.com/2026/09/23/tech/altman-amodei-ai-safety-un-security-council
- The Print, "OpenAI's Sam Altman, Anthropic's Amodei to brief UNSC as France flags AI threat to kids, global security." https://theprint.in/world/openais-sam-altman-anthropics-amodei-to-brief-unsc-as-france-flags-ai-threat-to-kids-global-security/3050738/
- The Singju Post, "Transcript: UN Security Council AI Hearing w/ Sam Altman, Dario Amodei & Clément Delangue." https://singjupost.com/transcript-un-security-council-ai-hearing-w-sam-altman-dario-amodei-clement-delangue/
- ABC News, "'Extreme concern': OpenAI agent hacked Australian public health website, prime minister says." https://abcnews.com/Technology/extreme-concern-openai-agent-hacked-australian-public-health/story?id=136707027
- Al Jazeera, "How an OpenAI 'agent' hacked Australia's Medicare and what that means." https://www.aljazeera.com/news/2026/9/24/how-an-openai-agent-hacked-australias-medicare-and-what-that-means
- CNBC, "OpenAI says agent hacked Australian government website without being told to do so." https://www.cnbc.com/2026/09/24/openai-agent-hacked-australian-government-website-.html
- CBC News, "Australia says OpenAI agent hacked government website." https://www.cbc.ca/news/world/openai-agent-hacked-government-website-australia-9.7356351
- CyberPeace Foundation, "Global CyberPeace Summit 2.0, Building Trust, Safety, and Digital Resilience in the AI Era." https://cyberpeace.org/events/global-cyberpeace-summit-2-0-building-trust-safety-and-digital-resilience-in-the-ai-era
- CyberPeace Summit, official website. https://www.cyberpeacesummit.com/ News4Hackers, "Global CyberPeace Summit 2.0: 10 Feb Pragati Maidan." https://www.news4hackers.com/global-cyberpeace-summit-10-feb-pragati-maidan/

"Cybercriminals are unleashing a surprisingly high volume of new threats in this short period of time to take advantage of inadvertent security gaps as organizations are in a rush to ensure business continuity.”
Cyber security firm Fortinet on Monday announced that over the past several weeks, it has been monitoring a significant spike in COVID-19 related threats.
An unprecedented number of unprotected users and devices are now online with one or two people in every home connecting remotely to work through the internet. Simultaneously there are children at home engaged in remote learning and the entire family is engaged in multi-player games, chatting with friends as well as streaming music and video. The cybersec firm’s FortiGuard Labs is observing this perfect storm of opportunity being exploited by cybercriminals as the Threat Report on the Pandemic highlights:
A surge in Phishing Attacks: The research shows an average of about 600 new phishing campaigns every day. The content is designed to either prey on the fears and concerns of individuals or pretend to provide essential information on the current pandemic. The phishing attacks range from scams related to helping individuals deposit their stimulus for Covid-19 tests, to providing access to Chloroquine and other medicines or medical device, to providing helpdesk support for new teleworkers.
Phishing Scams Are Just the Start: While the attacks start with a phishing attack, their end goal is to steal personal information or even target businesses through teleworkers. Majority of the phishing attacks contain malicious payloads – including ransomware, viruses, remote access trojans (RATs) designed to provide criminals with remote access to endpoint systems, and even RDP (remote desktop protocol) exploits.
A Sudden Spike in Viruses: The first quarter of 2020 has documented a 17% increase in viruses for January, a 52% increase for February and an alarming 131% increase for March compared to the same period in 2019. The significant rise in viruses is mainly attributed to malicious phishing attachments. Multiple sites that are illegally streaming movies that were still in theatres secretly infect malware to anyone who logs on. Free game, free movie, and the attacker is on your network.
Risks for IoT Devices magnify: As users are all connected to the home network, attackers have multiple avenues of attack that can be exploited targeting devices including computers, tablets, gaming and entertainment systems and even online IoT devices such as digital cameras, smart appliances – with the ultimate goal of finding a way back into a corporate network and its valuable digital resources.
Ransomware like attack to disrupt business: If the device of a remote worker can be compromised, it can become a conduit back into the organization’s core network, enabling the spread of malware to other remote workers. The resulting business disruption can be just as effective as ransomware targeting internal network systems for taking a business offline. Since helpdesks are now remote, devices infected with ransomware or a virus can incapacitate workers for days while devices are mailed in for reimaging.
“Though organizations have completed the initial phase of transitioning their entire workforce to remote telework and employees are becoming increasingly comfortable with their new reality, CISOs continue to face new challenges presented by maintaining a secure teleworker business model. From redefining their security baseline, or supporting technology enablement for remote workers, to developing detailed policies for employees to have access to data, organizations must be nimble and adapt quickly to overcome these new problems that are arising”, said Derek Manky, Chief, Security Insights & Global Threat Alliances at Fortinet – Office of CISO.
WhatsApp messages masquerading as an offer from Maruti Suzuki with links luring unsuspecting users with the promise of Maruti Suzuki 40th Anniversary Celebration presents, have been making the rounds on the app. If you receive such messages try to stay away from it, as it can be a scam.
The Research Wing of CyberPeace Foundation along with Autobot Infosec Private Limited have conducted a study based on a WhatsApp message that contained a link pretending to be a free gift offer from Maruti Suzuki which asks users to participate in a survey in order to get a chance to win a Maruti Baleno Sigma MT car.
Warning SignsThe campaign pretends to be an offer from Maruti Suzuki but is hosted on a third party domain instead of the official Maruti Suzuki website which makes it more suspicious.
The domain names associated with the campaign have been registered in very recent times.
Multiple redirections have been noticed between the links.
No reputed site would ask its users to share the campaign on WhatsApp.
The prize is kept really attractive to lure the laymen.
Grammatical mistakes have been noticed.
A congratulations message appears on the landing page with an attractive photo of Maruti Suzuki cars that asks users to participate in a quick survey in order to get a “Maruti Suzuki BALENO Sigma MT”. Also, the bottom of the page seems to appear like a comment section with public comments establishing the truthfulness of the offer.
The survey starts with some basic questions like Do you know Maruti Suzuki?, How old are you?, How do you think of Maruti Suzuki?, Are you male or female? Etc. Once the user answers the questions a “congratulatory message” is displayed.
On clicking the OK button users are given three attempts to win the prize. After completing all the attempts a message pops up that the user has won “Maruti Suzuki BALENO Sigma MT”. It then prompts the user to share the message on WhatsApp.
Strangely enough the user has to keep clicking the WhatsApp button until the progress bar completes. After clicking on the green ‘WhatsApp’ button multiple times it shows a section where an instruction has been given to complete registration in order to get the prize.
After clicking on the green ‘Complete registration’ button, it redirects the user to multiple advertisements web pages varying each time the user clicks on the button.
During the analysis the research team found a javascript code called hm.js was being executed in the background from the host hm[.]baidu[.]com which is a subdomain of Baidu and is used for Baidu Analytics, also known as Baidu Tongji. The important part is that Baidu is a Chinese multinational technology company specializing in Internet-related services, products and artificial intelligence, headquartered in Beijing’s Haidian district, China.To read the full report, please click (https://www.cyberpeace.org/CyberPeace/Repository/20210828Research-report-on-Maruti-Suzuki-40th-Anniversary-Celebration-free-gift-scam.pdf) here:
Conclusive Summary
1. The whole research activity was performed in a secured sandbox environment where the WhatsApp application was not installed. If any user opens the link from a device like smartphones where the WhatsApp application is installed, the sharing features on the site will open the Whatsapp application on the device to share the link.
2. The campaign collects browser and system information from the users.
3. Most of the domain names associated with the campaign have the registrant country as China.
4. Cybercriminals used Cloudflare technologies to mask the real IP addresses of the front-end domain names used in this Maruti Suzuki 40th Anniversary Celebration free gift campaign. But during the phases of investigation, the research team has identified a domain name that was requested in the background and has been traced as belonging to China.
CyberPeace Advisory
1. CyberPeace Foundation and Autobot Infosec recommend that people should avoid opening such messages sent via social platforms.
2. If at all, the user gets into this trap, it could lead to whole system compromise such as access to the microphone, Camera, Text Messages, Contacts, Pictures, Videos, Banking Applications, etc as well as financial losses.
3. Do not share confidential details like login credentials, banking information with such a type of scam.
4. Do not share or forward fake messages containing links without proper verification.
5. There is a need for International Cyber Cooperation between countries to bust the cybercriminal gangs running the fraud campaigns affecting individuals and organizations, to make Cyberspace resilient and peaceful.
Introduction
The two-day Apple’s Worldwide Developer Conference (WWDC) 2023, which was held on the 6th & 7th of June, has become an essential and highly anticipated part of our calendar as frequently as the trend. This year’s keynote announcements will include all of the usual enhancements for iOS, iPadOS, watchOS, macOS, and more. However, this year is also unique due to the unveiling of the Vision Pro headset, a brand-new Apple product.
In this blog, we will examine the exciting announcements made at Apple WWDC 2023, which was a ground-breaking event.
macOS Sonoma
macOS Sonoma, the new presentation of macOS disclosed at the WWDC full of exciting features. It comes with stunning video screensavers that show stunning scenes from all over the world. Gadgets can now be added genuinely to the work area and adjusted totally based on the client’s action. Also, it changes variety and blurring out of the spotlight while utilising applications. In addition, Death Stranding: Directors Cut for Mac announced that the Game Mode is added to make Macs more suitable for gaming. A presenter overlay enhances video presentations, and viewers can respond to them with interactive responses. Updated Safari is also included in the WebApp feature that turns frequently used websites into dedicated windows, a new Profile system for separating browsing history, and secure password sharing. Currently, the developer beta is available and the public beta will be available in July, and the final release is anticipated for the fall.
ios 16
Apple WWDC 2023 shows the following iOS, and iOS 16 replication, offering plenty of energising highlights for iPhone and iPad clients. Apple maintains its commitment to privacy with iOS 16, which introduces enhanced privacy settings that give users even more control over their data and online privacy. Users can also personalise their devices according to their preferences thanks to the new operating system’s refinement and customisable user interface.Improved multitasking capabilities like redesigned Files app and advanced note-taking features are just a few of the productivity enhancements included in the iOS 16. With iOS 16, Apple also improves its AR capabilities, allowing developers to develop even more immersive and interactive AR experiences.

WatchOS 9
Apple WWDC 2023 carried energising updates to the Apple Watch with the presentation of watchOS 9. The Apple Watch is an essential companion for sustaining a healthy lifestyle because the most recent version of the operating system includes cutting-edge health and fitness features. WatchOS 9 gives users unprecedented control over their health, offering personalised fitness recommendations and advanced sleep tracking.
Additionally, new watch faces were added, enhancing communication capabilities and improving app performance in watchOS 9, making the Apple Watch even easier to use daily.
ios 17
Rather than focusing on major features, Apple focused on quality-of-life enhancements when it announced iOS 17 at WWDC 2023. Live Voicemail with real-time transcripts of voicemails, personalised personal contact “posters,” and video voicemails for FaceTime are all part of the update. Search filters, a catch-up arrow, live location sharing, and a safety feature called Check-In are all available in Messages. AirDrop now supports NameDrop for transferring contact information; stickers have been expanded. The autocorrect and recording features on the keyboard have been improved for accuracy. Standby in the lock screen is an intelligent home display that shows the weather, upcoming appointments, and notifications. Siri works on Standby and adjusts itself for the night. The developer beta is currently available now, and a public beta will take place next month before the full release is in the fall.
Vision Pro VR Headset
Apple unveiled the Vision Pro AR headset, their first foray into virtual reality (VR), during the WWDC keynote. The Vision Pro is a virtual reality headset that competes with PlayStation VR2 and Meta Quest 3. This is in contrast to the long-awaited Apple smart glasses. Apple put a lot of effort into making a thin and light headset by using premium materials when needed. Voice, hand, and eye commands are all used to operate the Digital Crown-equipped device. The showcases offer extraordinary clarity, which is fueled by Apple’s M2 processor with a committed R1 chip. The Vision Pro combines virtual reality (VR) and augmented reality (AR), enabling users to interact with Apple apps and gain access to the company’s existing ecosystem. The expanded reality space created by the headset’s sensors and cameras allows users to place apps in real-world environments and adjust their level of concentration. Optic ID is a security and unlocking eye-tracking technology that is incorporated into the Vision Pro. It allows for a more immersive screen experience because it is compatible with Apple accessories like Magic Keyboard and Mac. At launch, the Vision Pro supports over a hundred Apple game galleries. Disney gave a hint that Apple and Disney might work together in the future by announcing support for the Vision Pro and making the Disney Plus app available immediately. The show highlighted the headset’s lightweight plan and recommended Apple clients wear it for extended periods. However, widespread adoption may be difficult due to the high price of $3,499 (₹289,093.01 approx). Apple is expected to release the Vision Pro for public use in 2024.

15-inch MacBook Air
At the WWDC event, Apple revealed a new MacBook Air with a larger 15-inch model instead of the standard 13-inch model. The 15-inch MacBook Air features a powerful Apple M2 processor, a thin, light, and long-lasting design, and a stunning 15.3-inch Retina display. It comes in four colours and has a headphone jack, two USB-C ports, and MagSafe charging. The display has six spatial speakers, a 1080p webcam, and 500 nits of brightness. Apple claims a battery life of up to 18 hours.
Conclusion
At Apple’s 2023 WWDC, the company demonstrated its commitment to developing technology that is user-friendly and accessible to all. Apple’s commitment to improving the user experience across all of its products is demonstrated in the updates to operating systems, improvements of Siri, breakthroughs in augmented reality, and enhancements to health and fitness.By making complex innovations more like-minded and easy to understand, Apple is enabling people to use the maximum capacity of their gadgets. Apple’s innovations at WWDC 2023 are expected to shape the future of technology, simplifying everyday tasks and revolutionising how we interact with the digital world.As we push ahead, it is exciting to guess what these advancements will proceed to develop and decidedly mean for our lives. The future holds even more incredible possibilities for all of us because of Apple’s focus on privacy, user-centric design, and pushing the boundaries of innovation. Thus, prepare to embrace a future where innovation flawlessly incorporates into our lives because of the endeavours displayed at Apple WWDC 2023.

Introduction
In recent years, India has witnessed a significant rise in the popularity and recognition of esports, which refers to online gaming. Esports has emerged as a mainstream phenomenon, influencing players and youngsters worldwide. In India, with the penetration of the internet at 52%, the youth has got its attracted to Esports. In this blog post, we will look at how the government is booting the players, establishing professional leagues, and supporting gaming companies and sponsors in the best possible manner. As the ecosystem continues to rise in prominence and establish itself as a mainstream sporting phenomenon in India.
Factors Shaping Esports in India: A few factors are shaping and growing the love for esports in India here. Let’s have a look.
Technological Advances: The availability and affordability of high-speed internet connections and smart gaming equipment have played an important part in making esports more accessible to a broader audience in India. With the development of smartphones and low-cost gaming PCs, many people may now easily participate in and watch esports tournaments.
Youth Demographic: India has a large population of young people who are enthusiastic gamers and tech-savvy. The youth demographic’s enthusiasm for gaming has spurred the expansion of esports in the country, as they actively participate in competitive gaming and watch major esports competitions.
Increase in the Gaming community: Gaming has been deeply established in Indian society, with many people using it for enjoyment and social contact. As the competitive component of gaming, esports has naturally gained popularity among gamers looking for a more competitive and immersive experience.
Esports Infrastructure and Events: The creation of specialised esports infrastructure, such as esports arenas, gaming cafés, and tournament venues, has considerably aided esports growth in India. Major national and international esports competitions and leagues have also been staged in India, offering exposure and possibilities for prospective esports players. Also supports various platforms such as YouTube, Twitch, and Facebook gaming, which has played a vital role in showcasing and popularising Esports in India.
Government support: Corporate and government sectors in India have recognised the potential of esports and are actively supporting its growth. Major corporate investments, sponsorships, and collaborations with esports organisations have supplied the financial backing and resources required for the country’s esports development. Government attempts to promote esports have also been initiated, such as forming esports governing organisations and including esports in official sporting events.
Growing Popularity and Recognition: Esports in India has witnessed a significant surge in viewership and fanbase, all thanks to online streaming platforms such as Twitch, YouTube which have provided a convenient way for fans to watch live esports events at home and at high-definition quality social media platforms let the fans to interact with their favourite players and stay updated on the latest esports news and events.

Esports Leagues in India
The organisation of esports tournaments and leagues in India has increased, with the IGL being one of the largest and most popular. The ESL India Premiership is a major esports event the Electronic Sports League organised in collaboration with NODWIN Gaming. Viacom18, a well-known Indian media business, established UCypher, an esports league. It focuses on a range of gaming games such as CS: GO, Dota 2, and Tekken in order to promote esports as a professional sport in India. All of these platforms provide professional players with a venue to compete and establish their profile in the esports industry.
India’s Performance in Esports to Date
Indian esports players have achieved remarkable global success, including outstanding results in prominent events and leagues. Individual Indian esports players’ success stories illustrate their talent, determination, and India’s ability to flourish in the esports sphere. These accomplishments contribute to the worldwide esports landscape’s awareness and growth of Indian esports. To add the name of the players and their success stories that have bought pride to India, they are Tirth Metha, Known as “Ritr”, a CS:GO player, Abhijeet “Ghatak”, Ankit “V3nom”, Saloni “Meow16K”.Apart from this Indian women’s team has also done exceptionally well in CS:GO and has made it to the finale.
Government and Corporate Sectors support: The Indian esports business has received backing from the government and corporate sectors, contributing to its growth and acceptance as a genuine sport.
Government Initiatives: The Indian government has expressed increased support for esports through different initiatives. This involves recognising esports as an official sport, establishing esports regulating organisations, and incorporating esports into national sports federations. The government has also announced steps to give financial assistance, subsidies, and infrastructure development for esports, therefore providing a favourable environment for the industry’s growth. Recently, Kalyan Chaubey, joint secretary and acting CEO of the IOA, personally gave the athletes cutting-edge training gear during this occasion, providing kits to the players. The kit includes the following:
Advanced gaming mouse.
Keyboard built for quick responses.
A smooth mousepad
A headphone for crystal-clear communication
An eSports bag to carry the equipment.
Corporate Sponsorship and Partnerships
Indian corporations have recognised esports’ promise and actively sponsored and collaborated with esports organisations, tournaments, and individual players. Companies from various industries, including technology, telecommunications, and entertainment, have invested in esports to capitalise on its success and connect with the esports community. These sponsorships and collaborations give financial support, resources, and visibility to esports in India. The leagues and championships provide opportunities for young players to showcase their talent.
Challenges and future
While esports provides great job opportunities, several obstacles must be overcome in order for the industry to expand and gain recognition:
Infrastructure & Training Facilities: Ensuring the availability of high-quality training facilities and infrastructure is critical for developing talent and allowing players to realise their maximum potential. Continued investment in esports venues, training facilities, and academies is critical for the industry’s long-term success.
Fostering a culture of skill development and giving outlets for formal education in esports would improve the professionalism and competitiveness of Indian esports players. Collaborations between educational institutions and esports organisations can result in the development of specialised programs in areas such as game analysis, team management, and sports psychology.
Establishing a thorough legal framework and governance structure for esports will help it gain legitimacy as a professional sport. Clear standards on player contracts, player rights, anti-doping procedures, and fair competition policies are all part of this.
Conclusion
Esports in India provide massive professional opportunities and growth possibilities for aspiring esports athletes. The sector’s prospects are based on overcoming infrastructure, perception, talent development, and regulatory barriers. Esports may establish itself as a viable and acceptable career alternative in India with continued support, investment, and stakeholder collaboration
BharOS’s successful testing grabbed massive online attention after Ashwini Vaishnaw, Minister of Communications and Electronics & IT, and Union Education Minister Dharmendra Pradhan unveiled the new mobile operating system. On Data Privacy Day, January 28, it’s appropriate to discuss the safety factors.
The OS is developed by JandKops, which has been incubated by IIT Madras Pravartak Technologies Foundation. It is claimed that BharOS will ensure the prevention of the “execution of any malware” and “execution of any malicious application”.
Even though it is called a Made in India OS, there are many people who disagree with this. It is because the OS is based on an AOSP (Android Open Source Project). It includes similar methodologies, functionalities, and basics used in Google Android.
Global safety factor
Security and data safety has been worldwide issue. A few years ago, Alphabet CEO Sundar Pichai also testified in front of US Congress while facing questions related to privacy, data collection, and location tracking.
While experts say that Android’s app ecosystem is a privacy and security disaster, a study that examined 82,501 apps pre-installed on 1,742 Android smartphones sold by 214 vendors concluded that users are woefully unaware of the significant security and privacy risks posed by pre-installed applications.
Even Apple, which takes cybersafety issues as a top priority, sometimes finds itself in a vulnerable situation. For example, last year Apple users were advised to update their devices to protect against a pair of security flaws that could allow attackers to take complete control.
It was said that one of the software flaws affected the kernel, the deepest layer of the OS shared by all Apple devices, while the other had an impact on WebKit, the technology that powers the Safari web browser.
Security researchers, including NordVPN, said that Apple’s closed development OS makes it more difficult for hackers to develop exploits, while Android raises the threat level since anyone can see its source code to develop exploits.
BharOS is not like iOS but it is kind of similar to Android and based on AOSP. So the question is, how safe would this OS be?
‘Security blanket’
Sandip Kumar Panda, Co-founder and CEO of InstaSafe, told News18: “BharOS acts as a security blanket for devices. The framework is designed in a manner that it prevents the execution of any malicious app and verifies each app on the devices before making it live on the BharOS platform.”
There are no apps without any vulnerabilities, he said. “As the app development progresses, vulnerabilities get introduced either in the form of insecure coding practices or third-party software vulnerabilities integrated with the platform. Since several Android vulnerabilities were discovered over the years, all those bugs would have been fixed now and updates would already have been for AOSP, which will be much more mature now,” he added.
Vineet Kumar, Founder and President of CyberPeace Foundation, believes that “the use of AOSP as the foundation for BharOS is a positive step” as it is a robust platform.
But according to him, it is important to note that no OS can be completely immune to all forms of cyber threats. “The key to staying safe online is to stay vigilant, use security software, keep your software updated, and be mindful of the apps you install and the websites you visit,” he said,
Furthermore, the expert stated that it is possible to make an OS more secure by implementing a variety of security features and technologies such as sandboxing, whitelisting, and application control, as well as rigorous testing and code review processes.
Kumar said: “It would be important for an independent, reputable security firm to evaluate BharOS and test its security features before it can be stated with certainty that it is more secure than other OSs.”
It is difficult to say whether the BharOS will be free of cybersecurity issues without more information about the specific features and security measures that have been implemented, he noted while adding that this OS has to go through a rigorous testing and certification process.
“It will be important to see how it measures up against established security standards and how well it can withstand real-world attacks,” the expert stated.
Reference Link : https://www.news18.com/amp/news/tech/data-privacy-day-how-safe-is-bharos-what-do-cybersecurity-experts-say-you-are-about-to-find-out-6932521.html
Introduction
The world has been surfing the wave of technological advancements and innovations for the past decade, and it all pins down to one device – our mobile phone. For all mobile users, the primary choices of operating systems are Android and iOS. Android is an OS created by google in 2008 and is supported by most brands like – One+, Mi, OPPO, VIVO, Motorola, and many more and is one of the most used operating systems. iOS is an OS that was developed by Apple and was introduced in their first phone – The iPhone, in 2007. Both OS came into existence when mobile phone penetration was slow globally, and so the scope of expansion and advancements was always in favor of such operating systems.
The Evolution
iOS
Ever since the advent of the iPhone, iOS has seen many changes since 2007. The current version of iOs is iOS 16. However, in the course of creating new iOS and updating the old ones, Apple has come out with various advancements like the App Store, Touch ID & Face ID, Apple Music, Podcasts, Augmented reality, Contact exposure, and many more, which have later become part of features of Android phone as well. Apple is one of the oldest tech and gadget developers in the world, most of the devices manufactured by Apple have received global recognition, and hence Apple enjoys providing services to a huge global user base.
Android
The OS has been famous for using the software version names on the food items like – Pie, Oreo, Nougat, KitKat, Eclairs, etc. From Android 10 onwards, the new versions were demoted by number. The most recent Android OS is Android 13; this OS is known for its practicality and flexibility. In 2012 Android became the most popular operating system for mobile devices, surpassing Apple’s iOS, and as of 2020, about 75 percent of mobile devices run Android.
Android vs. iOS
1. USER INTERFACE
One of the most noticeable differences between Android and iPhone is their user interface. Android devices have a more customizable interface, with options to change the home screen, app icons, and overall theme. The iPhone, on the other hand, has a more uniform interface with less room for customization. Android allows users to customize their home screen by adding widgets and changing the layout of their app icons. This can be useful for people who want quick access to certain functions or information on their home screen. IOS does not have this feature, but it does allow users to organize their app icons into folders for easier navigation.
2. APP SELECTION
Another factor to consider when choosing between Android and iOS is the app selection. Both platforms have a wide range of apps available, but there are some differences to consider. Android has a larger selection of apps overall, including a larger selection of free apps. However, some popular apps, such as certain music streaming apps and games, may be released first or only available on iPhone. iOS also has a more curated app store, meaning that all apps must go through a review process before being accepted for download. This can result in a higher quality of apps overall, but it can also mean that it takes longer for new apps to become available on the platform. iPhone devices tend to have less processing power and RAM. But they are generally more efficient in their use of resources. This can result in longer battery life, but it may also mean that iPhones are slower at handling multiple tasks or running resource-intensive apps.
3. PERFORMANCE
When it comes to performance, both Android and iPhone have their own strengths and weaknesses. Android devices tend to have more processing power and RAM. This can make them faster and more capable of handling multiple tasks simultaneously. However, this can also lead to Android devices having shorter battery life compared to iPhones.
4. SECURITY
Security is an important consideration for any smartphone user, and Android and iPhone have their own measures to protect user data. Android devices are generally seen as being less secure than iPhones due to their open nature. Android allows users to install apps from sources other than the Google Play Store, which can increase the risk of downloading malicious apps. However, Android has made improvements in recent years to address this issue. Including the introduction of Google Play Protect, which scans apps for malware before they are downloaded. On the other hand, iPhone devices have a more closed ecosystem, with all apps required to go through Apple‘s review process before being available for download. This helps reduce the risk of downloading malicious apps, but it can also limit the platform’s flexibility.
Conclusion
The debate about the better OS has been going on for some time now, and it looks like it will get more comprehensive in the times to come, as netizens go deeper into cyberspace, they will get more aware and critical of their uses and demands, which will allow them to opt for the best OS for their convenience. Although the Andriod OS, due to its integration, stands more vulnerable to security threats as compared to iOS, no software is secure in today’s time, what is secure is its use and application hence the netizen and the platforms need to increase their awareness and knowledge to safeguard themselves and the wholesome cyberspace.
Introduction
Established in the US, one of the world’s largest cab networks came into existence in 2010 and, since its inception, has expanded all over the globe with operations in 10,000 cities across 71 countries. It made a remarkable start in India in 2017 and, since then, has seen a rise in the customers and drivers for the company. India is among the largest markets for Uber, with 600,000 monthly drivers and 8.5 million monthly riders.
GeM
Government e-Marketplace (GeM) is a one-stop portal to facilitate online procurement of common-use Goods & Services required by various Government Departments / Organizations / PSUs. GeM aims to enhance transparency, efficiency and speed in public procurement. It provides the tools of e-bidding, reverses e-auction and demand aggregation to facilitate government users achieve the best value for their money. Government e-Marketplace owes its genesis to the recommendations of two Groups of Secretaries to the Prime Minister in January 2016. They recommended setting up a dedicated e-market for different goods & services procured or sold by Government/PSUs besides reforming DGS&D. Subsequently, the Finance Minister, in his Budget speech for FY 2016-17, announced setting up of a technology-driven platform to facilitate procurement of goods and services by various Ministries and agencies of the Government. The portal was launched on 9th August 2016 by the Commerce & Industry Minister.
Uber-GeM collaboration
The cab network giant has registered on the portal of the Government E-marketplace and has declared that it will offer its services to Government officials from Ministries and PSUs. The project is currently in its pilot phase and shall be executed systematically to cover all the ministries and PSUs in the nation. The officials can book cabs at a fixed price with no cancellation or surge fees on the rides. The authorised officials will be able to book a cab from the portal and select from the list of drivers available. It will be a cashless/cardless ride for the officials; additional vehicle categories for government riders have been added, namely, GeM Yatraa Hatch and GeM Yatraa Sedan, and there will be hourly rentals for multiple-stops, allowing the government officials to enjoy the flexible and easily accessible network of cabs in major cities.
Advantages
Such collaboration between Government institutions and corporates will go a long way to secure a stable equilibrium in the market. Uber, a US-based company, enjoys a vast user base in India and has created new job avenues. The advantages of the collaboration between GeM and Uber are as follows-
Easy accessibility
This will undoubtedly provide ease in accessibility in terms of being in a new place, and language barriers will no longer exist with such options for Government officials.
Increased jobs for drivers
With more cabs being engaged with ministries and PSUs, it is pertinent that the requirement for drivers will grow, thus increasing the employability rate in India and allowing the user to have an uninterrupted experience.
Ease of travel and commuting
This move will provide flexibility, thus leading to more ease in travel in cases of emergencies or places inaccessible by trains or other modes of transport.
Rise in travel and tourism
Coupled with the other factors, the opportunities for the users to visit different places will be an added advantage which will help boost the tourism industry, thus creating a balance in the market.
Sustainable Government corporate relationship

Such collaborations between the government and corporates will be substantial, signifying the ease of doing business in India. They will also act as a beacon of example for compliance with opportunities for the other companies and stakeholders.
Opportunities for collaboration with ingenious start-ups
With such major corporate joining hands with the government, the indigenous start-ups will have various opportunities to engage with companies and recreate similar businesses rooted in India, thus transforming the economy.
Conclusion
Transportation and communication play a vital role in our lives, thus, such collaboration will go a long way in creating a better and more uniform user experience in the country. This also goes a long way to showcase that the Governmental platforms also offer services of a global standard. Such portals exist in South Korea, Singapore, the US and Europe. The network of cabs can only be sustained using the locals as drivers, hence these collaborations are win-win for all as the market dynamics are improving, employability will increase, and improved user experience will be seen.
THREE CENTRES OF EXCELLENCE IN ARTIFICIAL INTELLIGENCE:
India’s Finance Minister, Mrs. Nirmala Sitharaman, with a vision of ‘Make AI for India’ and ‘Make AI work for India, ’ announced during the presentation of Union Budget 2023 that the Indian Government is planning to set up three ‘Centre of Excellence’ for Artificial Intelligence in top Educational Institutions to revolutionise fields such as health, agriculture, etc.
Under the ‘Amirt Kaal,’ i.e., the budget of 2023 is a stepping stone by the government to have a technology-driven knowledge-based economy and the seven priorities that have been set up by the government called ‘Saptarishi’ such as inclusive development, reaching the last mile, infrastructure investment, unleashing potential, green growth, youth power, and financial sector will guide the nation in this endeavor along with leading industry players that will partner in conducting interdisciplinary research, developing cutting edge applications and scalable problem solutions in such areas.
The government has already formed the roadmap for AI in the nation through MeitY, NASSCOM, and DRDO, indicating that the government has already started this AI revolution. For AI-related research and development, the Centre for Artificial Intelligence and Robotics (CAIR) has already been formed, and biometric identification, facial recognition, criminal investigation, crowd and traffic management, agriculture, healthcare, education, and other applications of AI are currently being used.
Even a task force on artificial intelligence (AI) was established on August 24, 2017. The government had promised to set up Centers of Excellence (CoEs) for research, education, and skill development in robotics, artificial intelligence (AI), digital manufacturing, big data analytics, quantum communication, and the Internet of Things (IoT) and by announcing the same in the current Union budget has planned to fulfill the same.
The government has also announced the development of 100 labs in engineering institutions for developing applications using 5G services that will collaborate with various authorities, regulators, banks, and other businesses.
Developing such labs aims to create new business models and employment opportunities. Among others, it will also create smart classrooms, precision farming, intelligent transport systems, and healthcare applications, as well as new pedagogy, curriculum, continual professional development dipstick survey, and ICT implementation will be introduced for training the teachers.
POSSIBLE ROLES OF AI:
The use of AI in top educational institutions will help students to learn at their own pace, using AI algorithms providing customised feedback and recommendations based on their performance, as it can also help students identify their strengths and weaknesses, allowing them to focus their study efforts more effectively and efficiently and will help train students in AI and make the country future-ready.
The main area of AI in healthcare, agriculture, and sustainable cities would be researching and developing practical AI applications in these sectors. In healthcare, AI can be effective by helping medical professionals diagnose diseases faster and more accurately by analysing medical images and patient data. It can also be used to identify the most effective treatments for specific patients based on their genetic and medical history.
Artificial Intelligence (AI) has the potential to revolutionise the agriculture industry by improving yields, reducing costs, and increasing efficiency. AI algorithms can collect and analyse data on soil moisture, crop health, and weather patterns to optimise crop management practices, improve yields and the health and well-being of livestock, predict potential health issues, and increase productivity. These algorithms can identify and target weeds and pests, reducing the need for harmful chemicals and increasing sustainability.
ROLE OF AI IN CYBERSPACE:
Artificial Intelligence (AI) plays a crucial role in cyberspace. AI technology can enhance security in cyberspace, prevent cyber-attacks, detect and respond to security threats, and improve overall cybersecurity. Some of the specific applications of AI in cyberspace include:
- Intrusion Detection: AI-powered systems can analyse large amounts of data and detect signs of potential cyber-attacks.
- Threat Analysis: AI algorithms can help identify patterns of behaviour that may indicate a potential threat and then take appropriate action.
- Fraud Detection: AI can identify and prevent fraudulent activities, such as identity theft and phishing, by analysing large amounts of data and detecting unusual behaviour patterns.
- Network Security: AI can monitor and secure networks against potential cyber-attacks by detecting and blocking malicious traffic.
- Data Security: AI can be used to protect sensitive data and ensure that it is only accessible to authorised personnel.
CONCLUSION:
Introducing AI in top educational institutions and partnering it with leading industries will prove to be a stepping stone to revolutionise the development of the country, as Artificial Intelligence (AI) has the potential to play a significant role in the development of a country by improving various sectors and addressing societal challenges. Overall, we hope to see an increase in efficiency and productivity across various industries, leading to increased economic growth and job creation, improved delivery of healthcare services by increasing access to care and, improving patient outcomes, making education more accessible and effective as AI has the potential to improve various sectors of a country and contribute to its overall development and progress. However, it’s important to ensure that AI is developed and used ethically, considering its potential consequences and impact on society.
References:

Introduction
It’s a proud moment for Indians that India will host the G- 20 administration, which will bring the world’s 20 largest profitable nations together on a single platform during the post-economic recovery and the Russia- Ukraine conflict, which has increased geopolitical pressures among nations over the last many times and made the G- 20 a precedence of nations. With this administration, India has to make cybersecurity precedence, as the security and integrity of the critical structure and digital platforms are top precedence in 2023. The necessity for a secure cyberspace is pivotal given the exponential increase in the volume and kind of cyber-attacks, particularly to crucial structures the most recent illustration is the ongoing interruption at New Delhi’s All India Institute of Medical lores caused by a ransomware assault. It has been observed that the mode of attacks are more sophisticated and targets communication structure, critical structure, transport systems, and especially the information technology sector and fiscal system.
The structure that enables the delivery of government services to be more effective. As a result,cyber-secured critical structures and digital public forums are necessary for public security, bettered governance, and, most importantly, maintaining people’s trust. The G20 can be enhanced and contribute towards securing digital public platforms and the integrity of the critical structure. This time, in 2023, digital security is the top precedence.
G20 cybersecurity enterprises and politic sweat
The emphasis on cybersecurity was maintained throughout the Italian and Indonesian regulations in 2021 and 2022, independently, by emphasizing the significance of cyberspace during Digital Economy Working Group addresses. Specifically, under the Indonesian Presidency, the prominent cybersecurity focus was clear in the recent Bali Leaders’ protestation, which noted, among other effects, the significance of fighting misinformation juggernauts and cyber attacks, as well as guaranteeing connectivity structure security. The cyber incident report by the Financial Stability Board on carrying further uniformity in cyber incident reporting In 2016, a G20 digital task force was created under the Chinese administration to understand digital technology issues. Under the Saudi administration, the cybersecurity gap at the G20 was bridged by addressing the issues of MSMs. India has also refocused on the significance of creating secure, secure, and stronger-friendly digital platforms.
G20- India’s digital invention alliance( G-20-DIA) a cyber-secure Bharat
- Under India’s administration, the G20’s Digital Economy Working Group is led by the Ministry of Electronics and Information Technology( MeitY, DEWG).
- The Ministry concentrated on three major areas during India’s G20 administration digital skill development, digital public structure, and cyber security.
- The EWG’s DIA and Stay Safe Online enterprise further the ideal of lesser digital metamorphosis by guaranteeing a safe and creative cyber terrain. They want to offer a smooth and secure delivery of public services.

The G20 Digital Innovation Alliance
(G20- DIA) strives to find, admit, and encourage the relinquishment of innovative and poignant digital technologies produced by invited G20 startups and-member governments.
- These technologies must meet humanity’s conditions in six crucial areas husbandry, health, education, finance, secure digital structure, and indirect frugality.
- The inventions created around these motifs will be supported by the Digital Public Goods structure, allowing them to be espoused encyclopedically, closing the digital gap and icing sustainable and indifferent growth.
- The G20 Digital Innovation Alliance( G20- DIA) conference will be held on the perimeters of the Digital Economy Working Group( DEWG) meeting in Bengaluru.
- Top-nominated entrepreneurs from each order will present their ideas to a worldwide community of investors, instructors, pots, and other stakeholders at this event.
India’s” Stay Safe Online crusade”
The” Stay Safe Online” crusade attempts to raise mindfulness about the significance of remaining safe in the online world amid our adding reliance on it. With the fast expansion of the technical terrain and the growing number of internet druggies in India, new difficulties are arising. The Stay Safe Online crusade aims to educate individuals about cyber pitfalls and how to avoid them. The time-long crusade will target children, women, scholars, and aged citizens, as well as individuals with disabilities, preceptors, and government officers in particular. It’ll be done in Hindi, English, and indigenous languages to reach a larger followership. It’ll distribute mindfulness information in infographics, short pictures, cartoon stories, and so on through extensively employed social media platforms and other channels. The primary stakeholders will be government agencies, civil societies, and NGOs.
Conclusion
To wind up, it can be said that cyber security has become the most essential part of transnational affairs. As India hosts the G20 administration in 2023, the docket relating to cybersecurity gains a global stage, where cyber-related issues are addressed and honored encyclopedically, and nations can combat these issues; also, India aims to raise cyber mindfulness among its citizens.
Introduction
The year, 2022 has been a year of transition and change for the gaming industry. This year esports and gaming including the industry’s greater increased acceptance by the sports authorities and higher prize pools for top players, has been more commercial than ever, according to research by the year 2025 the industry will witness growth by 5 million dollars and around 420 million active gamers from India. Since, India is on the way to become world’s largest gaming market, with revenue earned in 2021 increasing by up to 28%, or 1.2 billion dollars, and predicted to reach 2 billion dollars by 2024 as a result of the COVID-19 expanding internet access throughout the country.
After a lengthy debate, the government has finally decided to bring online gaming under the purview of the law. The President of India has changed the rules governing e-sports and requested that the Sports Ministry and the Ministry of Electronics and Information Technology (MeitY) include e-sports in multi-sport competitions. India’s gaming sector has reached new heights this year, with the country winning its first bronze medal in the first esports event organized by this year’s Commonwealth Games, and this is only the beginning.
Indian government takes on E-sports
The Indian government has given esports a huge boost. It has been introduced into the traditional sports disciplines of the nation. Droupadi Murmu, the President of India, changed the regulations governing eSports using the authority “conferred by clause (3) of Article 77 of the Constitution,” and requested that “e-Sports be included as part of multi-sports events” from the Ministries of Electronics and Information Technology and Sports. Some crucial points will clarify the government’s position on e-sports.
- E-sports were added as a demonstration sport to the 2018 Asian Games in Jakarta, which meant that medals earned in the sport were not counted in the official total of medals.
- There is a greater desire for Esports to be integrated with school curricula.
- E-Sports (Electronic Sports) have been acknowledged by the Indian government as a component of multi-sport tournaments.

Why is e-sports important?
The Indian Esports Industry has worked hard to distinguish Esports from the broader category of “Gaming.” Esports is a competitive sport in which esports athletes compete in specific video game genres in a virtual, electronic environment using their physical and mental prowess, according to the industry.
According to studies, as individuals have gotten more screen aware and online gaming has become a part of their life, internet gaming not only improves fine motor skills but also sharpens the mind. The industry has the most users and stakeholders, and it has become critical to governing it; consequently, legislation is required to regulate it.
The online regulation bill 2022
The Online Gaming (Regulations) Bill, 2022, was recently filed in the Lok Sabha to create an effective regulatory mechanism for the online gaming business to prevent fraud and misuse of things related to or incidental to it. There are 20 sections spread throughout three chapters. It intends to establish an Online Gaming Commission, the authority, mandate, and jurisdiction of which will be specified by the Bill. An online gaming server will be licensed, relinquished, revoked, or suspended by the Commission’s key highlights of the bill to make it more clear
- The Bill establishes a regulating agency, the Online Gaming Commission (“OGC”), comprised of five members chosen by the Central Government, each with at least one specialist in the fields of law, cyber technology, and law enforcement experience.
- The OGC will be able to oversee the functions of online gaming websites, issue periodic or special reports on Online Gaming issues, recommend appropriate measures to control and curb illegal Online Gaming, grant, suspend, and revoke licenses for online gaming websites, and set fees for license applications and renewals.
- Without a website and a non-transferable and non-assignable license, the Bill proposes to make online gambling illegal. Anyone operating an online gaming server or website without a license risks up to three years in prison and a fine. The permission will be good for a six-year term.
- The license intended to be given under the Bill may be terminated or canceled if the licensee violates any of the license’s requirements or any of Bill’s provisions. However, the Bill does not apply to anybody providing backend services in India, including hosting and maintenance for any international gaming website situated outside of India.
- The bill also mentions the Foreign Direct Investment and Technology Collaboration in Online Gaming

Few misses in the bill that can be addressed to make it stronger and a better version
- The law does not address Know Your Customer (KYC) requirements, customer complaint procedures, advertising and marketing restrictions, user data protection, responsible gaming guidelines, and other concerns.
- In the bill, there is no clear distinction between money involved in the game. This is a matter of concern and needs to be addressed so the money laundering aspect can be determined.
- The distinction between “games of chance” and “games of skill” is not addressed in the Bill. Furthermore, the Bill does not specify whether its prohibitions apply only to for-real-money games or to free games.
Conclusion
Despite the bill’s flaws, it has offered optimism to the burgeoning gaming sector, which desperately needs a robust regulatory and legal framework free of ambiguity, allowing players to play safely, and encouraging entrepreneurs to enter the field with safety and security. An improved regulatory framework will increase job prospects while also assisting the government. A transparent framework will also aid in the protection of the rights of actors and stakeholders.
Introduction
With the increasing reliance on digital technologies in the banking industry, cyber threats have become a significant concern. Cyberlaw plays a crucial role in safeguarding the banking sector from cybercrimes and ensuring the security and integrity of financial systems.
The banking industry has witnessed a rapid digital transformation, enabling convenient services and greater access to financial resources. However, this digitalisation also exposes the industry to cyber threats, necessitating the formulation and implementation of effective cyber law frameworks.
Recent Trends in the Banking Industry
Digital Transformation: The banking industry has embraced digital technologies, such as mobile banking, internet banking, and financial apps, to enhance customer experience and operational efficiency.
Open Banking: The concept of open banking has gained prominence, enabling data sharing between banks and third-party service providers, which introduces new cyber risks.
How Cyber Law Helps the Banking Sector
The banking sector and cyber crime share an unspoken synergy due to the mass digitisation of banking services. Thanks to QR codes, UPI and online banking payments, India is now home to 40% of global online banking transactions. Some critical aspects of the cyber law and banking sector are as follows:
Data Protection: Cyberlaw mandates banks to implement robust data protection measures, including encryption, access controls, and regular security audits, to safeguard customer data.
Incident Response and Reporting: Cyberlaw requires banks to establish incident response plans, promptly report cyber incidents to regulatory authorities, and cooperate in investigations.
Customer Protection: Cyberlaw enforces regulations related to online banking fraud, identity theft, and unauthorised transactions, ensuring that customers are protected from cybercrimes.
Legal Framework: Cyberlaw provides a legal foundation for digitalisation in the banking sector, assuring customers that regulations protect their digital transactions and data.
Cybersecurity Training and Awareness: Cyberlaw encourages banks to conduct regular training programs and create awareness among employees and customers about cyber threats, safe digital practices, and reporting procedures.

RBI Guidelines
The RBI, as India’s central banking institution, has issued comprehensive guidelines to enhance cyber resilience in the banking industry. These guidelines address various aspects, including:
Technology Risk Management
Cyber Security Framework
IT Governance
Cyber Crisis Management Plan
Incident Reporting and Response
Recent Trends in Banking Sector Frauds and the Role of Cyber Law
Phishing Attacks: Cyberlaw helps banks combat phishing attacks by imposing penalties on perpetrators and mandating preventive measures like two-factor authentication.
Insider Threats: Cyberlaw regulations emphasise the need for stringent access controls, employee background checks, and legal consequences for insiders involved in fraudulent activities.
Ransomware Attacks: Cyberlaw frameworks assist banks in dealing with ransomware attacks by enabling legal actions against hackers and promoting preventive measures, such as regular software updates and data backups.
Master Directions on Cyber Resilience and Digital Payment Security Controls for Payment System Operators (PSOs)
Draft of Master Directions on Cyber Resilience and Digital Payment Security Controls for Payment System Operators (PSOs) issued by the Reserve Bank of India (RBI). The directions provide guidelines and requirements for PSOs to improve the safety and security of their payment systems, with a focus on cyber resilience. These guidelines for PSOs include mobile payment service providers like Paytm or digital wallet payment platforms.
Here are the highlights-
The Directions aim to improve the safety and security of payment systems operated by PSOs by providing a framework for overall information security preparedness, with an emphasis on cyber resilience.
The Directions apply to all authorised non-bank PSOs.
PSOs must ensure adherence to these Directions by unregulated entities in their digital payments ecosystem, such as payment gateways, third-party service providers, vendors, and merchants.
The PSO’s Board of Directors is responsible for ensuring adequate oversight over information security risks, including cyber risk and cyber resilience. A sub-committee of the Board may be delegated with primary oversight responsibilities.
PSOs must formulate a Board-approved Information Security (IS) policy that covers roles and responsibilities, measures to identify and manage cyber security risks, training and awareness programs, and more.
PSOs should have a distinct Board-approved Cyber Crisis Management Plan (CCMP) to detect, contain, respond, and recover from cyber threats and attacks.
A senior-level executive, such as a Chief Information Security Officer (CISO), should be responsible for implementing the IS policy and the cyber resilience framework and assessing the overall information security posture of the PSO.
PSOs need to define Key Risk Indicators (KRIs) and Key Performance Indicators (KPIs) to identify potential risk events and assess the effectiveness of security controls. The sub-committee of the Board is responsible for monitoring these indicators.
PSOs should conduct a cyber risk assessment when launching new products, services, technologies, or significant changes to existing infrastructure or processes.
PSOs, including inventory management, identity and access management, network security, application security life cycle, security testing, vendor risk management, data security, patch and change management life cycle, incident response, business continuity planning, API security, employee awareness and training, and other security measures should implement various baseline information security measures and controls.
PSOs should ensure that payment transactions involving debit to accounts conducted electronically are permitted only through multi-factor authentication, except where explicitly permitted/relaxed.

Conclusion
The relationship between cyber law and the banking industry is crucial in ensuring a secure and trusted digital environment. Recent trends indicate that cyber threats are evolving and becoming more sophisticated. Compliance with cyber law provisions and adherence to guidelines such as those provided by the RBI is essential for banks to protect themselves and their customers from cybercrimes. By embracing robust cyber law frameworks, the banking industry can foster a resilient ecosystem that enables innovation while safeguarding the interests of all stakeholders or users.
Introduction
The insurance industry is a target for cybercriminals due to the sensitive nature of the information it holds. This makes it essential for insurance companies to have robust cybersecurity measures to protect their data and customers’ personal information.
Cyber fraud in India’s insurance industry is increasing. It is reported that the Indian insurance sector has witnessed a surge in cyber-attacks, with several instances of data breaches, identity thefts, and financial fraud being reported. These cybercrimes not only pose a significant threat to the financial stability of the insurance industry but also to the privacy and security of policyholders.
Cyber Frauds in the Insurance Industry
The insurance industry in India has been the target of increasing cyber fraud in recent years. With the growing digital transformation trend, insurance companies have become increasingly vulnerable to cyber-attacks. Cyber frauds in the insurance industry are initiated by hackers who use various techniques such as phishing, malware, ransomware, and social engineering to gain unauthorised access to policyholders’ personal data and sensitive information
Kinds of cyber frauds in the insurance industry
It is essential for insurers and policyholders alike to be aware of these kinds of cyber-attacks on insurance companies in today’s digital age. Staying educated about these threats can help prevent them from happening in the future.
Identity theft– One common type of cyber fraud that occurs in the insurance industry is identity theft. In this type of fraud, criminals steal personal information such as name, address, date of birth and social security numbers through phishing emails or fraudulent websites. They then use this information to open fraudulent policies or access existing ones.
Payment fraud- Another type of cyber fraud that is on the rise is payment fraud. In this type of fraud, hackers intercept electronic payments made by policyholders or agents using fake bank accounts or compromised payment gateways. The money is then siphoned into untraceable accounts, making it difficult for law enforcement agencies to identify and arrest the perpetrators.
Phishing attacks- Where the fraudsters posed as company officials and sent emails to policyholders requesting their account details. The unsuspecting customers fell for this scam and shared their sensitive information, which was then used to access their accounts and steal funds.
Hacking- Where hackers breach the company’s system to gain access to policyholder data. The hackers’ stoles personal records, including names, addresses, phone numbers, social security numbers, and financial information, which they later sell on the dark web.
Fake policies scam- Fraudsters create fake policies using stolen identities and collect premiums from innocent customers. The insurer then voided these policies due to fraudulent activity leaving those people without valid coverage when they needed it most. The victims suffer significant financial losses due to this scam.
Fake Insurance Websites- Discuss the creation of deceptive websites that imitate well-known insurance companies, where unsuspecting individuals provide their personal details, leading to identity theft or financial losses.
Prevention of Cyber Frauds in the Insurance Industry- Best practices to follow
Prevention is better than cure, which also holds true in the case of cyber fraud in the insurance industry. The industry must take proactive steps to prevent such frauds from occurring in the first place. One of the most effective ways to do so is by investing in cybersecurity measures that are specifically designed for the insurance sector.
Insurance companies must conduct regular employee training programs on cybersecurity best practices. This includes educating employees on how to identify and avoid phishing emails, create strong passwords, and recognise potential cyber threats. Companies should also establish a reporting mechanism for employees to report suspicious activity or incidents immediately.
Having proper access controls in place is also necessary. This means limiting access to sensitive data only to those employees who need it, implementing two-factor authentication, and regularly monitoring user activity logs. Regular audits can also provide an extra layer of protection against potential threats by identifying vulnerabilities that may have been overlooked during routine security checks.
Another essential step is encrypting all data transmitted between different systems and devices. Encryption scrambles data into unreadable codes that can only be deciphered using a decryption key, making it difficult for hackers to intercept or steal information in transit.
Legal Framework for Cyber Frauds in the Insurance Industry
The legal framework for cyber fraud in the insurance industry is critical to preventing such crimes. The Insurance Regulatory and Development Authority of India (IRDAI) has issued guidelines for insurers to establish a cybersecurity framework. The guidelines require insurers to conduct regular risk assessments, implement security measures, and ensure compliance with data privacy laws.
The Information Technology Act 2000, is another significant piece of legislation dealing with cyber fraud in India. The act defines offences such as unauthorised access to a computer system, hacking, and tampering with data. It also provides for stringent penalties and imprisonment for those found guilty of such offences.
The IRDAI’s guidelines provide insurers with a roadmap to establish robust cybersecurity measures to help prevent cyber fraud in the insurance industry. Stringent implementation of these guidelines will go a long way in safeguarding sensitive customer information from falling into the wrong hands.
Best Practices for Insurers and Policyholders
Insurers:
Implementing Strong Authentication: Encouraging the use of multi-factor authentication and secure login processes to safeguard customer accounts and prevent unauthorised access.
Regular Employee Training: Conduct cybersecurity awareness programs to educate employees about the latest threats and preventive measures.
Investing in Advanced Technologies: Utilizing robust cybersecurity tools and systems to promptly detect and mitigate potential cyber threats.
Policyholders:
Vigilance and Awareness: Policyholders must stay vigilant while sharing personal information online and verify the authenticity of insurance websites and communication channels.
Regular Updates and Patches: Advising individuals to keep their devices and software up to date to minimise vulnerabilities that cybercriminals can exploit.
Secure Online Practices: Encouraging the use of strong and unique passwords, avoiding sharing sensitive information on unsecured networks, and exercising caution when clicking on suspicious links or attachments.

Conclusion
As the Indian insurance industry embraces digitisation, the risk of cyber scams and data breaches becomes a significant concern. Insurers and policyholders must collaborate to ensure robust cybersecurity measures are in place to protect sensitive information and financial interests.
It is essential for insurance companies to invest in robust cybersecurity measures that can detect and prevent fraud attempts. Additionally, educating employees on the dangers of cyber fraud and implementing strict compliance measures can go a long way in mitigating risks. With these efforts, the insurance industry can continue to provide trustworthy and reliable services to its customers while protecting against cyber threats. As technology continues to evolve, it is imperative that the insurance industry adapts accordingly and remains vigilant against emerging threats.

Introduction
The European Union has fined the meta $ 1.3 billion for infringing the EU privacy laws by transferring the personal data of Facebook users to the United States. The EU fined Meta’s business in Ireland. As per the European Union, transferring Personal data to the US is a breach of the General data protection Regulation or European Union law on data protection and privacy.
GDPR Compliance
The terms of GDPR promise to gather users’ personal information legally and under strict conditions. And those who collect and manage personal data must protect users’ personal data from exploitation. The GDPR restricts an organisation’s capacity to transfer personal data outside the EU if the transfer is solely based on that body’s evaluation of the sufficiency of the personal data’s protection. Transfers should only be made where European authorities have determined that a third country, a territory within that third country, or an international organisation provides acceptable protection for data protection.
Violation by Meta
The punishment, announced by Ireland’s Data Protection Commission, might be one of the most significant in the five years since the European Union passed the landmark General Data Protection Regulation. According to regulators, Facebook failed to comply with a 2020 judgment by the European Union’s top court that Facebook data transferred over the Atlantic was not sufficiently safeguarded from American espionage agencies. However, whether Meta will ever need to encrypt Facebook users’ data in Europe is still being determined. Meta announced it would appeal the ruling, launching a potentially legal procedure.
Simultaneously, European Union and American officials are negotiating a new data-sharing pact that would provide legal protections for Meta and scores of other companies to continue moving information between the US and Europe. This pact could overturn much of the European Union’s Monday ruling.
Article 46(1) GDPR Has been violated by the meta, And as per the Irish privacy.
What is required by the GDPR before transferring personal information across national boundaries?

Personal data transfers to countries outside the European Economic Area are generally permitted if these nations are regarded to provide a sufficient degree of data protection. According to Article 45 of the GDPR, the European Commission evaluates the degree of personal data protection in third countries.
The European Union judgment demonstrates how government rules are upending the borderless way data has traditionally migrated. Companies are increasingly being pressed to store data within the country where it is acquired rather than allowing it to transfer freely to data centres around the world as a result of data-protection requirements, national security laws, and other regulations.
The US internet giant had previously warned that if forced to stop using SCCs (standard contractual clauses) without a proper alternative data transfer agreement in place, it would be compelled to shut down services such as Facebook and Instagram in Europe.
What will happen next for Facebook in Europe?
The ruling includes a six-month transition period before it must halt data flows, meaning the service will continue to operate in the meantime. (More specifically, Meta has been given a five-month transition period to freeze any future transfer of personal data to the United States and a six-month deadline to terminate the unlawful processing and/or storage of European user data it has previously transferred without a legitimate legal basis. Meta has also stated that it will appeal and appears to seek a stay of execution while it pursues its legal arguments in court.
Conclusion
The GDPR places restrictions on transferring personal data outside the European Union to third-party nations or international bodies to ensure that the GDPR’s level of protection for individuals is not jeopardised. But the meta violated the European Union’s privacy laws by the user’s personal information to the US. Under the compliance of GDPR, transferring and sending personal information to users intentionally is an offence. and presently, the personal data of Facebook users has been breached by the Meta, as they shared the information with the US.

Introduction
Recent advances in space exploration and technology have increased the need for space laws to control the actions of governments and corporate organisations. India has been attempting to create a robust legal framework to oversee its space activities because it is a prominent player in the international space business. In this article, we’ll examine India’s current space regulations and compare them to the situation elsewhere in the world.
Space Laws in India
India started space exploration with Aryabhtta, the first satellite, and Rakesh Sharma, the first Indian astronaut, and now has a prominent presence in space as many international satellites are now launched by India. NASA and ISRO work closely on various projects
India currently lacks any space-related legislation. Only a few laws and regulations, such as the Indian Space Research Organisation (ISRO) Act of 1969 and the National Remote Sensing Centre (NRSC) Guidelines of 2011, regulate space-related operations. However, more than these rules and regulations are essential to control India’s expanding space sector. India is starting to gain traction as a prospective player in the global commercial space sector. Authorisation, contracts, dispute resolution, licencing, data processing and distribution related to earth observation services, certification of space technology, insurance, legal difficulties related to launch services, and stamp duty are just a few of the topics that need to be discussed. The necessary statute and laws need to be updated to incorporate space law-related matters into domestic laws.
India’s Space Presence
Space research activities were initiated in India during the early 1960s when satellite applications were in experimental stages, even in the United States. With the live transmission of the Tokyo Olympic Games across the Pacific by the American Satellite ‘Syncom-3’ demonstrating the power of communication satellites, Dr Vikram Sarabhai, the founding father of the Indian space programme, quickly recognised the benefits of space technologies for India.
As a first step, the Department of Atomic Energy formed the INCOSPAR (Indian National Committee for Space Research) under the leadership of Dr Sarabhai and Dr Ramanathan in 1962. The Indian Space Research Organisation (ISRO) was formed on August 15, 1969. The prime objective of ISRO is to develop space technology and its application to various national needs. It is one of the six largest space agencies in the world. The Department of Space (DOS) and the Space Commission were set up in 1972, and ISRO was brought under DOS on June 1, 1972.
Since its inception, the Indian space programme has been orchestrated well. It has three distinct elements: satellites for communication and remote sensing, the space transportation system and application programmes. Two major operational systems have been established – the Indian National Satellite (INSAT) for telecommunication, television broadcasting, and meteorological services and the Indian Remote Sensing Satellite (IRS) for monitoring and managing natural resources and Disaster Management Support.
Global Scenario
The global space race has been on and ever since the moon landing in 1969, and it has now transformed into the new cold war among developed and developing nations. The interests and assets of a nation in space need to be safeguarded by the help of effective and efficient policies and internationally ratified laws. All nations with a presence in space do not believe in good for all policy, thus, preventive measures need to be incorporated into the legal system. A thorough legal framework for space activities is being developed by the United Nations Office for Outer Space Affairs (UNOOSA). The “Outer Space Treaty,” a collection of five international agreements on space law, establishes the foundation of international space law. The agreements address topics such as the peaceful use of space, preventing space from becoming militarised, and who is responsible for damage caused by space objects. Well-established space laws govern both the United States and the United Kingdom. The National Aeronautics and Space Act, which was passed in the US in 1958 and established the National Aeronautics and Space Administration (NASA) to oversee national space programmes, is in place there. The Outer Space Act of 1986 governs how UK citizens and businesses can engage in space activity.

Conclusion
India must create a thorough legal system to govern its space endeavours. In the space sector, there needs to be a legal framework to avoid ambiguity and confusion, which may have detrimental effects. The Pacific use of space for the benefit of humanity should be covered by domestic space legislation in India. The overall scenario demonstrates the requirement for a clearly defined legal framework for the international acknowledgement of a nation’s space activities. India is fifth in the world for space technology, which is an impressive accomplishment, and a strong legal system will help India maintain its place in the space business.
Pretext
On 20th October 2022, the Competition Commission of India (CCI) imposed a penalty of Rs. 1,337.76 crores on Google for abusing its dominant position in multiple markets in the Android Mobile device ecosystem, apart from issuing cease and desist orders. The CCI also directed Google to modify its conduct within a defined timeline. Smart mobile devices need an operating system (OS) to run applications (apps) and programs. Android is one such mobile operating system that Google acquired in 2005. In the instant matter, the CCI examined various practices of Google w.r.t. licensing of this Android mobile operating system and various proprietary mobile applications of Google (e.g., Play Store, Google Search, Google Chrome, YouTube, etc.).
The Issue
Google was found to be misusing its dominant position in the tech market, and the same was the reason behind the penalty. Google argued about the competitive constraints being faced from Apple. In relation to understanding the extent of competition between Google’s Android ecosystem and Apple’s iOS ecosystem, the CCI noted the differences in the two business models, which affect the underlying incentives of business decisions. Apple’s business is primarily based on a vertically integrated smart device ecosystem that focuses on the sale of high-end smart devices with state-of-the-art software components. In contrast, Google’s business was found to be driven by the ultimate intent of increasing users on its platforms so that they interact with its revenue-earning service, i.e., online searches, which directly affects the sale of online advertising services by Google. It was seen that google had created a dominant position among the android phone manufacturers as they were made to have a set of google apps preinstalled in the device to increase the user’s dependency on google services. The CCI felt that Google had created a dominant position to which they replied that the same operations are done by Apple as well, to which the commission responded that apple is a phone and app manufacturer and they have Apple-owned apps in Apple devices only, but Google here in had made a pseudo mandate for android manufactures to have the google apps pre-installed which is, in turn, a possible way of disrupting the market equilibrium and violative of market practices. The CCI imposed a penalty of Rs. 1,337.76 for abusing its dominant position in multiple markets in India, CCI delineated the following five relevant markets in the present matter –
- The market for licensable OS for smart mobile devices in India
- The market for app store for Android smart mobile OS in India
- The market for general web search services in India
- The market for non-OS specific mobile web browsers in India
- The market for online video hosting platforms (OVHP) in India.
Supreme Courts Opinion
In October 2022, the Competition Commission of India (CCI) ruled that Google, owned by Alphabet Inc, exploited its dominant position in Android and told it to remove restrictions on device makers, including those related to the pre-installation of apps and ensuring exclusivity of its search. Google lost a challenge in the Supreme Court to block the directives, as the learned court refused to put a stay on the imposed penalty, further giving seven days to comply. The Supreme Court has said a lower tribunal—where Google first challenged the Android directives—can continue to hear the company’s appeal and must rule by March 31.
Counterpoint Research estimates that about 97% of 600 million smartphones in India run on Android. Apple has just a 3% share. Hoping to block the implementation of the CCI directives, Google challenged the CCI order in the Supreme Court by warning it could stall the growth of the Android ecosystem. It also said it would be forced to alter arrangements with more than 1,100 device manufacturers and thousands of app developers if the directives kick in. Google has been concerned about India’s decision as the steps are seen as more sweeping than those imposed in the European Commission’s 2018 ruling. There it was fined for putting in place what the Commission called unlawful restrictions on Android mobile device makers. Google is still challenging the record $4.3 billion fine in that case. In Europe, Google made changes later, including letting Android device users pick their default search engine, and said device makers would be able to license the Google mobile application suite separately from the Google Search App or the Chrome browser.
Conclusion
As the world goes deeper into cyberspace, the big tech companies have more control over the industry and the markets, but the same should not turn into anarchy in the global markets. The Tech giants need to be made aware that compliance is the utmost duty for all companies, and enforcement of the law of the land will be maintained no matter what. Earlier India lacked policies and legislation to govern cyberspace, but in the recent proactive stance by the govt, a lot of new bills have been tabled, one of them being the Intermediary Rules 2021, which has laid down the obligations nand duties of the companies by setting up an intermediary in the country. Such bills coupled with such crucial judgments on tech giants will act as a test and barrier for other tech companies who try to flaunt the rules and avoid compliance.

What are Wi-Fi attacks?
Wi-fi is an important area of cyber security and there is no need for physical cable for the network. Wi-Fi has access to a network signal radius everywhere. The devices and systems can have a network without physical access due to Wi-fi. But everything comes with cons and pros, and if we talk about cybersecurity, it has been established that Wi-fi networks are extremely vulnerable to security breaches and it is very easy to be hacked by hackers. Wi-Fi can be accessed by almost every device in the modern day: it can be smartphones, tablets, computers, and laptops. To know whether someone has been tampering with your personal Wi-Fi there are certain signs that can prove it. The first and most important sign is that your internet speed gets slower, as someone else is using your Wi-Fi surf.
Why would anyone hack someone’s Wi-Fi network?
Usually, hackers hack the network because they want access to the confidential data of someone and they can observe all the online activities and data that have been sent through a network. An unauthorize hacker will pretty much be able to see everything you do online. Wi-Fi allows hackers o view information on sites. Any financial information which is saved in the browser can be accessed by hackers and they can alter it and can alter the content you see online. And all the information saved in Wi-fi networks can be used by hackers for their own benefit, they can sell it, impersonate you, or even take money out of your bank through Wi-Fi.
Avoiding vulnerable Wi-Fi networks
The first and foremost rule of protection is that you should not use public networks if that network is easily open to you then that is also available to others and from others, and someone can who wishes to use your confidential and sensitive information, can access that. If you really need to access the public network in an urgent situation, then you must make sure to limit your activities while connected. And avoid accessing your online banking or pages that require login information. Also, a good measure to take as well is to always delete your cookies after using public WIFI.
How To Secure Your Home Wi-Fi Network
Your home’s wireless internet connection is your Wi-Fi network. Typically, a wireless router is used, which broadcasts a signal into the atmosphere. You can connect to the internet using that signal. However, if your network is not password-protected, any nearby device can grab the signal off the air and connect to your internet. The benefit of Wi-Fi? Wireless access to the internet is possible. The negative? Your internet activity, including your personal information, may be visible to neighboring users who connect to your unprotected network. Furthermore, if someone uses your network to conduct a crime or send out unauthorized spam, you might be held accountable.
Wi-Fi or Li-Fi? –
The common consensus is that Li-Fi technology is more secure than Wi-Fi. Li-Fi systems can be made more secure by integrating a variety of security features. Although these qualities might appear when Li-Fi is widely used in the near future, it is already thought to be safer because of a number of security features. Since the connection’s characteristics make it simpler to lock connections, limit access, and track users even in the absence of encryption and other security features, Li-Fi is seen as being safer. Li-Fi systems will be able to support new security protocols, which will not only enable high-speed networking but also open the door for innovative security techniques to strengthen connections.
Conclusion
A hacker can sniff the network packets without having to be in the same building where the network is located. As wireless networks communicate through radio waves, a hacker can easily sniff the network from a nearby location. Most attackers use network sniffing to find the SSID and hack a wireless network.
Any wireless network can theoretically be attacked in a number of different ways. Use of the default SSID or password, WPS pin authentication, insufficient access control, and leaving the access point available in open locations are all examples of potential vulnerabilities that could allow for the theft of sensitive data. Kismet’s architecture in WIDS mode may guard against DOS, MiTM, and MAC spoofing attacks. routine software updates on the other hand, the use of firewalls may help defend the network against outside intrusion. The act of finding infrastructure issues that could allow harmful code to be injected into a service, system, or organization is known as ethical hacking. They use this technique to prevent invasions by lawfully breaking into networks and looking for weak spots.

Introduction
Google Play has announced its new policy which will ensure trust and transparency on google play by providing a new framework for developer verification and app details. The new policy requires that new developer accounts on Google Play will have to provide a D-U-N-S number to verify the business. So when an organisation will create a new Play Console developer account the organisation will need to provide a D-U-N-S number. Which is a nine-digit unique identifier which will be used to verify their business. The new google play policy aims to enhance user trust. And the developer will provide detailed developer details on the app’s listing page. Users will get to know who is behind the app which they are installing.
Verifying Developer Identity with D-U-N-S Numbers
To boost security the google play new policy requires the developer account to provide the D-U-N-S number when creating a new Play Console developer account. The D-U-N-S number assigned by Dun & Bradstreet will be used to verify the business. Once the developer creates his new Play Console developer account by providing a D-U-N-S number, Google Play will verify the developer’s details, and he will be able to start publishing the apps. Through this step, Google Play aims to validate the business information in a more authentic way.
If your organisation does not have a D-U-N-S number, you may check on or request for it for free on this website (https://www.dnb.com/duns-number/lookup.html). The request process for D-U-N-S can take up to 30 days. Developers are also required to keep the information up to date.
Building User Trust with Enhanced App Details
In addition to verifying developer identities in a more efficient way, google play also requires that developer provides sufficient app details to the users. There will be an “App Support” section on the app’s store listing page, where the developer will display the app’s support email address and even can include their website and phone number for support.
The new section “About the developer” will also be introduced to provide users with verified identity information, including the developer’s name, address, and contact details. Which will make the users more informed about the valuable information of the app developers.
Key highlights of the Google Play Polic
- Google Play came up with the policy to keep the platform safe by verifying the developers’ identity and it will also help to reduce the spread of malware apps and help the users to make confident informed decisions about the apps they download. Google Play announced the policy by expanding its developer verification requirement to strengthen Google Play as a platform and build user trust. When you create a new Play Console Developer account and choose organisation as your account type you will now need to provide a D-U-N-S number.
- Users will get detailed information about the developers’ identities and contact information, building more transparency and encouraging responsible app development practices.
- This policy will enable the users to make informed choices about the apps they download.
- The new “App support” section will provide enhanced communication between users and developers by displaying support email addresses, website and support phone numbers, streamlining the support process and user satisfaction.
Timeline and Implementation
The new policy requirements for D-U-N-S numbers will start rolling out on 31 August 2023 for all new Play Console developer accounts. The “About the developer” section will be visible to users as soon as a new app is published. and In October 2023, existing developers will also be required to update and verify their existing accounts to comply with the new verification policy.
Conclusion
Google Play’s new policy will aim to enhance the more transparent app ecosystem. This new policy will provide the users with more information about the developers. Google Play aims to establish a platform where users can confidently discover and download apps. This new policy will enhance the user experience on google play in terms of a reliable and trustworthy platform.
Introduction
Recently, a Consultation Paper on Regulatory Mechanisms for Over-The-Top (OTT) Communication Services was published by the Telecom Regulatory Authority of India (TRAI). The paper explores several OTT regulation-related challenges and solicits input from stakeholders on a suggested regulatory framework. We’ll summarise the paper’s main conclusions in this blog.
Structure of the Paper
The Telecom Regulatory Authority of India’s Consultation Paper on Regulatory Mechanism for Over-The-Top (OTT) Communication Services and Selective Banning of OTT Services intends to solicit comments and recommendations from stakeholders about the regulation of OTT services in India. The paper is broken up into five chapters that cover the introduction and background, issues with regulatory mechanisms for OTT communication services, issues with the selective banning of OTT services, a summary of the issues for consultation, and an overview of international practices on the topic. Written comments from interested parties are requested and may be sent electronically to the Advisor (Networks, Spectrum and Licencing) at TRAI. These comments will also be posted on the TRAI website.
Overview of the Paper
- Chapter 1: Introduction and Background
- The first chapter of the essay introduces the subject of OTT communication services and argues why regulatory frameworks are necessary. The chapter also gives a general outline of the topics and the paper’s organisation that will be covered in the following chapters.
- Chapter 2: Examination of the Issues Related to Regulatory Mechanism for Over-The-Top Communication Services
- The second chapter of the essay looks at the problems with OTT communication service regulation. It talks about the many kinds of OTT services and how they affect the conventional telecom sector. The chapter also looks at the regulatory issues raised by OTT services and the various strategies used by various nations to address them.
- Chapter 3: Examination of the Issues Related to Selective Banning of OTT Services
- The final chapter of the essay looks at the problems of selectively outlawing OTT services. It analyses the justifications for government restrictions on OTT services as well as the possible effects of such restrictions on consumers and the telecom sector. The chapter also looks at the legal and regulatory structures that determine how OTT services are prohibited in various nations.
- Chapter 4: International Practices
- An overview of global OTT communication service best practices is given in the paper’s fourth chapter. It talks about the various regulatory strategies used by nations throughout the world and how they affect consumers and the telecom sector. The chapter also looks at the difficulties regulators encounter when trying to create efficient regulatory frameworks for OTT services.
- Chapter 5: Issues for Consultation
- This chapter is the spirit of the consultation paper as it covers the points and questions for consultation. This chapter has been classified into two sub-sections – Issues Related to Regulatory Mechanisms for OTT Communication Services and Issues Related to the Selective Banning of OTT Services. The inputs will be entirely focused on these sub headers, and the scope, extent, and ambit of the consultation paper rests on these questions and necessary inputs.
Conclusion
An important publication that aims to address the regulatory issues raised by OTT services is the Consultation Paper on Regulatory Mechanisms for Over-The-Top Communication Services. The paper offers a thorough analysis of the problems with OTT service regulation and requests input from stakeholders on the suggested regulatory structure. In order to make sure that the regulatory framework is efficient and advantageous for everyone, it is crucial for all stakeholders to offer their opinion on the document.

Introduction
Twitter Inc.’s appeal against barring orders for specific accounts issued by the Ministry of Electronics and Information Technology was denied by a single judge on the Karnataka High Court. Twitter Inc. was also given an Rs. 50 lakh fine by Justice Krishna Dixit, who claimed the social media corporation had approached the court defying government directives.
As a foreign corporation, Twitter’s locus standi had been called into doubt by the government, which said they were ineligible to apply Articles 19 and 21 to their situation. Additionally, the government claimed that because Twitter was only designed to serve as an intermediary, there was no “jural relationship” between Twitter and its users.
The Issue
In accordance with Section 69A of the Information Technology Act, the Ministry issued the directives. Nevertheless, Twitter had argued in its appeal that the orders “fall foul of Section 69A both substantially and procedurally.” Twitter argued that in accordance with 69A, account holders were to be notified before having their tweets and accounts deleted. However, the Ministry failed to provide these account holders with any notices.
On June 4, 2022, and again on June 6, 2022, the government sent letters to Twitter’s compliance officer requesting that they come before them and provide an explanation for why the Blocking Orders were not followed and why no action should be taken against them.
Twitter replied on June 9 that the content against which it had not followed the blocking orders does not seem to be a violation of Section 69A. On June 27, 2022, the Government issued another notice stating Twitter was violating its directions. On June 29, Twitter replied, asking the Government to reconsider the direction on the basis of the doctrine of proportionality. On June 30, 2022, the Government withdrew blocking orders on ten account-level URLs but gave an additional list of 27 URLs to be blocked. On July 10, more accounts were blocked. Compiling the orders “under protest,” Twitter approached the HC with the petition challenging the orders.
Legality
Additionally, the government claimed that because Twitter was only designed to serve as an intermediary, there was no “jural relationship” between Twitter and its users.
Government attorney Additional Solicitor General R Sankaranarayanan argued that tweets mentioning “Indian Occupied Kashmir” and the survival of LTTE commander Velupillai Prabhakaran were serious enough to undermine the integrity of the nation.
Twitter, on the other hand, claimed that its users have pushed for these rights. Additionally, Twitter maintained that under Article 14 of the Constitution, even as a foreign company, they were entitled to certain rights, such as the right to equality. They also argued that the reason for the account blocking in each case was not stated and that Section 69a’s provision for blocking a URL should only apply to the offending URL rather than the entire account because blocking the entire account would prevent the creation of information while blocking the offending tweet only applied to already-created information.
Conclusion
The evolution of cyberspace has been substantiated by big tech companies like Facebook, Google, Twitter, Amazon and many more. These companies have been instrumental in leading the spectrum of emerging technologies and creating a blanket of ease and accessibility for users. Compliance with laws and policies is of utmost priority for the government, and the new bills and policies are empowering the Indian cyberspace. Non Compliance will be taken very seriously, and the same is legalised under the Intermediary Guidelines 2021 and 2022 by Meity. Referring to Section 79 of the Information Technology Act, which pertains to an exemption from liability of intermediary in some instances, it was said, “Intermediary is bound to obey the orders which the designate authority/agency which the government fixes from time to time.”
Introduction
Cert-In (Indian Computer Emergency Response Team) has recently issued the “Guidelines on Information Security Practices” for Government Entities for Safe & Trusted Internet. The guideline has come at a critical time when the Draft Digital India Bill is about to be released, which is aimed at revamping the legal aspects of Indian cyberspace. These guidelines lay down the policy framework and the requirements for critical infrastructure for all government organisations and institutions to improve the overall cyber security of the nation.
What is Cert-In?
A Computer Emergency Response Team (CERT) is a group of information security experts responsible for the protection against, detection of and response to an organisation’s cybersecurity incidents. A CERT may focus on resolving data breaches and denial-of-service attacks and providing alerts and incident handling guidelines. CERTs also conduct ongoing public awareness campaigns and engage in research aimed at improving security systems. The Ministry of Electronics and Information Technology (MeitY) oversees CERT-In. It regularly releases alerts to help individuals and companies safeguard their data, information, and ICT (Information and Communications Technology) infrastructure.
Indian Computer Emergency Response Team (CERT-In) has been established and appointed as national agency in respect of cyber incidents and cyber security incidents in terms of the provisions of section 70B of Information Technology (IT) Act, 2000.
CERT-In requests information from service providers, intermediaries, data centres, and body corporates to coordinate reaction actions and emergency procedures regarding cyber security incidents. It is a focal point for incident reporting and offers round-the-clock security services. It manages cyber occurrences that are tracked and reported while continuously analysing cyber risks. It strengthens the security barriers for the Indian Internet domain.
Background
India is fast becoming one of the world’s largest connected nations – with over 80 Crore Indians (Digital Nagriks) presently connected and using the Internet and cyberspace – and with this number is expected to touch 120 Crores in the coming few years. The Digital Nagriks of the country are using the Internet for business, education, finance and various applications and services including Digital Government services. Internet provides growth and innovation and at the same time it has seen rise in cybercrimes, user harm and other challenges to online safety. The policies of the Government are aimed at ensuring an Open, Safe & Trusted and Accountable Internet for its users. Government is fully cognizant and aware of the growing cyber security threats and attacks.
It is the Government of India’s objective to ensure that Digital Nagriks experience a Safe & Trusted Internet. Along with ubiquitous applications of Information & Communication Technologies (ICT) in almost all facets of service delivery and operations, continuously evolving cyber threats have become a concern for the Government. Cyber-attacks can come in the form of malware, ransomware, phishing, data breach etc., that adversely affect an organisation’s information and systems. Cyber threats leading to cyber-attacks or incidents can compromise the confidentiality, integrity, and availability of an organisation’s information and systems and can have far reaching impact on essential services and national interests. To protect against cyber threats, it is important for government entities to implement strong cybersecurity measures and follow best practices. As ICT infrastructure of the Government entities is one of the preferred targets of the malicious actors, responsibility of implementing good cyber security practices for protecting computers, servers, applications, electronic systems, networks, and data from digital attacks, also remain with the ICT assets’ owner i.e. Government entity.
What are the new Guidelines about?
The Government of India (distribution of business) Rules, 1961’s First Schedule lists a number of Ministries, Departments, Secretariats, and Offices, along with their affiliated and subordinate offices, which are all subject to the rules. They also comprise all governmental organisations, businesses operating in the public sector, and other governmental entities under their administrative control.
“The government has launched a number of steps to guarantee an accessible, trustworthy, and accountable digital environment. With a focus on capabilities, systems, human resources, and awareness, we are extending and speeding our work in the area of cyber security, according to Rajeev Chandrasekhar, Minister of State for Electronics, Information Technology, Skill Development, and Entrepreneurship.
The Recommendations
- Various security domains are covered in the standards, including network security, identity and access management, application security, data security, third-party outsourcing, hardening procedures, security monitoring, incident management, and security audits.
- For instance, the rules advise using only a Standard User (non-administrator) account to use computers and laptops for regular work regarding desktop, laptop, and printer security in the workplace. Users may only be granted administrative access with the CISO’s consent.
- The usage of lengthy passwords containing at least eight characters that combine capital letters, tiny letters, numerals, and special characters; Never save any usernames or passwords in your web browser. Likewise, never save any payment-related data there.
- They include guidelines created by the National Informatics Centre for Chief Information Security Officers (CISOs) and staff members of Central government Ministries/Departments to improve cyber security and cyber hygiene in addition to adhering to industry best practises.
Conclusion
The government has been proactive in the contemporary times to eradicate the menace of cybercrimes and therreats from the Indian cyberspace and hence now we have seen a series of new bills and polices introduced by the Ministry of Electronics and Information Technology, and various other government organisations like Cert-In and TRAI. These policies have been aimed towards being relevant to time and current technologies. The threats from emerging technologies like web 3.0 cannot be ignored and hence with active netizen participation and synergy between government and corporates will lead to a better and improved cyber ecosystem in India.
Introduction
The Telecom Regulatory Authority of India (TRAI) issued a consultation paper titled “Encouraging Innovative Technologies, Services, Use Cases, and Business Models through Regulatory Sandbox in Digital Communication Sector. The paper presents a draft sandbox structure for live testing of new digital communication products or services in a regulated environment. TRAI seeks comments from stakeholders on several parts of the framework.
What is digital communication?
Digital communication is the use of internet tools such as email, social media messaging, and texting to communicate with other people or a specific audience. Even something as easy as viewing the content on this webpage qualifies as digital communication.
Aim of Paper
- Frameworks are intended to support regulators’ desire for innovation while also ensuring economic resilience and consumer protection. Considering this, the Department of Telecom (DoT) asked TRAI to offer recommendations on a regulatory sandbox framework. TRAI approaches the issue with the goal of encouraging creativity and hastening the adoption of cutting-edge digital communications technologies.
- Artificial intelligence, the Internet of Things, edge computing, and other emerging technologies are revolutionizing how we connect, communicate, and access information, driving the digital communication sector to rapidly expand. To keep up with this dynamic environment, an enabling environment for the development and deployment of novel technologies, services, use cases, and business models is required.
- The regulatory sandbox concept is becoming increasingly popular around the world as a means of encouraging innovation in a range of industries. A regulatory sandbox is a regulated environment in which businesses and innovators can test their concepts, commodities, and services while operating under changing restrictions.
- Regulatory Sandbox will benefit the telecom startup ecosystem by providing access to a real-time network environment and other data, allowing them to evaluate the reliability of new applications before releasing them to the market. Regulatory Sandbox also attempts to stimulate cross-sectoral collaboration for carrying out such testing by engaging the assistance of other ministries and departments in order to give the starting company with a single window for acquiring all clearances.
What is regulatory sandbox?
- A regulatory sandbox is a controlled regulatory environment in which new products or services are tested in real-time.
- It serves as a “safe space” for businesses because authorities may or may not allow certain relaxations for the sole purpose of testing.
- The sandbox enables the regulator, innovators, financial service providers, and clients to perform field testing in order to gather evidence on the benefits and hazards of new financial innovations, while closely monitoring and mitigating their risks.
What are the advantages of having a regulatory sandbox?
- Firstly, regulators obtain first-hand empirical evidence on the benefits and risks of emerging technologies and their implications, allowing them to form an informed opinion on the regulatory changes or new regulations that may be required to support useful innovation while mitigating the associated risks.
- Second, sandbox customers can evaluate the viability of a product without the need for a wider and more expensive roll-out. If the product appears to have a high chance of success, it may be authorized and delivered to a wider market more quickly.
Digital communication sector and Regulatory Sandbox
- Many countries’ regulatory organizations have built sandbox settings for telecom tech innovation.
- These frameworks are intended to encourage regulators’ desire for innovation while also promoting economic resilience and consumer protection.
- In this context, the Department of Telecom (DoT) had asked TRAI to give recommendations on a regulatory sandbox framework.
- Written comments on the drafting framework will be received until July 17, 2023, and counter-comments will be taken until August 1, 2023. The Authority’s goal in the digital communication industry is to foster creativity and expedite the use of emerging technologies such as artificial intelligence (AI), the Internet of Things (IoT), and edge computing. These technologies are changing the way individuals connect, engage, and access information, causing rapid changes in the industry.
Conclusion
According to TRAI, these technologies are changing how individuals connect, engage, and obtain information, resulting in significant changes in the sector.
The regulatory sandbox also wants to stimulate cross-sectoral collaboration for carrying out such testing by engaging the assistance of other ministries and departments in order to give the starting company with a single window for acquiring all clearances. The consultation paper covers some of the worldwide regulatory sandbox frameworks in use in the digital communication industry, as well as some of the frameworks in use inside the country in other sectors.

Introduction
The Telecom Regulatory Authority of India (TRAI) has directed all telcos to set up detection systems based on Artificial Intelligence and Machine Learning (AI/ML) technologies in order to identify and control spam calls and text messages from unregistered telemarketers (UTMs).
The TRAI Directed telcos
The telecom regulator, TRAI, has directed all Access Providers to detect Unsolicited commercial communication (UCC)by systems, which is based on Artificial Intelligence and Machine Learning to detect, identify, and act against senders of Commercial Communication who are not registered in accordance with the provisions of the Telecom Commercial Communication Customer Preference Regulations, 2018 (TCCCPR-2018). Unregistered Telemarketers (UTMs) are entities that do not register with Access Providers and use 10-digit mobile numbers to send commercial communications via SMS or calls.
TRAI steps to curb Unsolicited commercial communication
TRAI has taken several initiatives to reduce Unsolicited Commercial Communication (UCC), which is a major source of annoyance for the public. It has resulted in fewer complaints filed against Registered Telemarketers (RTMs). Despite the TSPs’ efforts, UCC from Unregistered Telemarketers (UTMs) continues. Sometimes, these UTMs use messages with bogus URLs and phone numbers to trick clients into revealing crucial information, leading to financial loss.
To detect, identify, and prosecute all Unregistered Telemarketers (UTMs), the TRAI has mandated that Access Service Providers implement the UCC.
Detect the System with the necessary functionalities within the TRAI’s Telecom Commercial Communication Customer Preference Regulations, 2018 framework.
Access service providers have implemented such detection systems based on their applicability and practicality. However, because UTMs are constantly creating new strategies for sending unwanted communications, the present UCC detection systems provided by Access Service providers cannot detect such UCC.
TRAI also Directs Telecom Providers to Set Up Digital Platform for Customer Consent to Curb Promotional Calls and Messages.
Unregistered Telemarketers (UTMs) sometimes use messages with fake URLs and phone numbers to trick customers into revealing essential information, resulting in financial loss.
TRAI has urged businesses like banks, insurance companies, financial institutions, and others to re-verify their SMS content templates with telcos within two weeks. It also directed telecom companies to stop misusing commercial messaging templates within the next 45 days.
The telecom regulator has also instructed operators to limit the number of variables in a content template to three. However, if any business intends to utilise more than three variables in a content template for communicating with their users, this should be permitted only after examining the example message, as well as adequate justifications and justification.
In order to ensure consistency in UCC Detect System implementations, TRAI has directed all Access Providers to deploy UCC and detect systems based on artificial intelligence and Machine Learning that are capable of constantly evolving to deal with new signatures, patterns, and techniques used by UTMs.
Access Providers have also been directed to use the DLT platform to share intelligence with others. Access Providers have also been asked to ensure that such UCC Detect System detects senders that send unsolicited commercial communications in bulk and do not comply with the requirements. All Access Providers are directed to follow the instructions and provide an update on actions done within thirty days.
The move by TRAI is to curb the menacing calls as due to this, the number of scam cases is increasing, and now a new trend of scams started as recently, a Twitter user reported receiving an automated call from +91 96681 9555 with the message “This call is from Delhi Police.” It then asked her to stay in the queue since some of her documents needed to be picked up. Then he said he works as a sub-inspector at the Kirti Nagar police station in New Delhi. He then inquired whether she had recently misplaced her Aadhaar card, PAN card, or ATM card, to which she replied ‘no’. The scammer then poses as a cop and requests that she authenticate the last four digits of her card because they have found a card with her name on it. And a lot of other people tweeted about it.

Conclusion
TRAI directed the telcos to check the calls and messages from Unregistered numbers. This step of TRAI will curb the pesky calls and messages and catch the Frauds who are not registered with the regulation. Sometimes the unregistered sender sends fraudulent links, and through these fraudulent calls and messages, the sender tries to take the personal information of the customers, which results in financial losses.

Introduction
To combat the problem of annoying calls and SMS, telecom regulator TRAI has urged service providers to create a uniform digital platform in two months that will allow them to request, maintain, and withdraw customers’ approval for promotional calls and messages. In the initial stage, only subscribers will be able to initiate the process of registering their consent to receive promotional calls and SMS, and later, business entities will be able to contact customers to seek their consent to receive promotional messages, according to a statement issued by the Telecom Regulatory Authority of India (TRAI) on Saturday.
TRAI Directs Telecom Providers to Set Up Digital Platform
TRAI has now directed all access providers to develop and deploy the Digital Consent Acquisition (DCA) facility for creating a unified platform and process to digitally register customers’ consent across all service providers and principal entities. Consent is received and maintained under the current system by several key entities such as banks, other financial institutions, insurance firms, trading companies, business entities, real estate businesses, and so on.
The purpose, scope of consent, and the principal entity or brand name shall be clearly mentioned in the consent-seeking message sent over the short code,” according to the statement.
It stated that only approved online or app links, call-back numbers, and so on will be permitted to be used in consent-seeking communications.
TRAI issued guidelines to guarantee that all voice-based Telemarketers are brought under a single Distributed ledger technology (DLT) platform for more efficient monitoring of nuisance calls and unwanted communications. It also instructs operators to actively deploy AI/ML-based anti-phishing systems as well as to integrate tech solutions on the DLT platform to deal with malicious calls and texts.
TRAI has issued two separate Directions to Access Service Providers under TCCCPR-2018 (Telecom Commercial Communications Customer Preference Regulations) to ensure that all promotional messages are sent through Registered Telemarketers (RTMs) using approved Headers and Message Templates on Distributed Ledger Technologies (DLT) platform, and to stop misuse of Headers and Message Templates,” the regulator said in a statement.
Users can already block telemarketing calls and texts by texting 1909 from their registered mobile number. By dialing 1909, customers can opt out of getting advertising calls by activating the do not disturb (DND) feature.
Telecom providers operate DLT platforms, and businesses involved in sending bulk promotional or transactional SMS must register by providing their company information, including sender IDs and SMS templates.
According to the instructions, telecom companies will send consent-seeking messages using the common short code 127. The goal, extent of consent, and primary entity/brand name must be clearly stated in the consent-seeking message delivered via the shortcode.
TRAI stated that only whitelisted URLs/APKs (Android package kits file format)/OTT links/call back numbers, etc., shall be used in consent-seeking messages.
Telcos must “ensure that promotional messages are not transmitted by unregistered telemarketers or telemarketers using telephone numbers (10 digits numbers).” Telecom providers have been urged to act against all erring telemarketers in accordance with the applicable regulations and legal requirements.
Users can, however, refuse to receive any consent-seeking messages launched by any significant Telcos have been urged to create an SMS/IVR (interactive voice response)/online service for this purpose.
According to TRAI’s timeline, the consent-taking process by primary companies will begin on September 1.According to a nationwide survey conducted by a local circle, 66% of mobile users continue to receive three or more bothersome calls per day, the majority of which originate from personal cell numbers.
There are scams surfacing on the internet with new types of scams, like WhatsApp international call scams. The latest scam is targeting Delhi police, the scammers pretend to be police officials of Delhi and ask for the personal details of the users and the calling them from a 9-digit number.
A recent scam
A Twitter user reported receiving an automated call from +91 96681 9555, stating, “This call is from Delhi Police.” It went on to ask her to stay in the queue since some of her documents needed to be picked up. Then he said he is a sub-inspector at New Delhi’s Kirti Nagar police station. He then questioned if she had lately misplaced her Aadhaar card, PAN card, or ATM card, to which she replied ‘no’. The fraudster then claims to be a cop and asks her to validate the final four digits of her card because they have discovered a card with her name on it. And so many other people tweeted about this.
The scams are constantly increasing as earlier these scammers asked for account details and claimed to be Delhi police and used 9-digit numbers for scamming people.
TRAI’s new guidelines regarding the consent to receive any promotional calls and messages to telecommunication providers will be able to curb the scams.
The e- KYC is an essential requirement as e-KYC offers a more secure identity verification process in an increasingly digital age that uses biometric technologies to provide quick results.
Conclusion
The aim is to prevent unwanted calls and communications sent to customers via digital methods without their permission. Once this platform is implemented, an organization can only send promotional calls or messages with the customer’s explicit approval. Companies use a variety of methods to notify clients about their products, including phone calls, text messages, emails, and social media. Customers, however, are constantly assaulted with the same calls and messages as a result of this practice. With the constant increase in scams, the new guideline of TRAI will also curb the calling of Scams. digital KYC prevents SIM fraud and offers a more secure identity verification method.

Introduction
Online Gaming has gained popularity over the past few years, attracting young players worldwide and global concerns. In response to the growing fame of this industry, the Indian government has recently announced introducing a set of regulations to address various concerns and ensure a safer and more regulated online gaming environment. In this blog post, we will explore the critical aspects of these regulations and their impact on the gaming industry.
Why are Regulations needed?
Recently some games faced a ban in India – games that involve betting, games that can be harmful to the user, and games that involve a factor of addiction. Furthermore, with rising popularity, With the exponential rise of online gaming platforms in India, extensive laws to safeguard players and ensure fair gameplay needs to be implemented. Players’ protection is one of the critical factors addressing the issues which involve online addiction, underage involvement, fraud, and data privacy has become critical for the well-being of Indian gamers.
Regulatory Ambiguity: The previous legislative structure, such as the outmoded Public Gambling Act of 1867, required an update to fit the digital gambling age fully.
Outline of the New Regulations
Implementing new regulations for online gaming in India represents the government’s commitment to addressing different issues and ensuring a safer and more regulated gaming sector. Let’s have a look at these rules in detail:
National-Level Standards: The Indian government is currently working on creating national-level standards to standardise online gaming practices across all states. These rules attempt to create a uniform platform for both operators and participants. The government has also made an announcement to set SRO within 90 days to regulate online gaming.
Licencing and Compliance: To legally operate in the Indian market, online gaming firms must secure licences. The operator’s financial soundness, security measures, and adherence to responsible gaming practices will be scrutinised throughout the licencing process. Operators will need to comply with the regulations in order to maintain operations.
Measures to Promote Ethical Gaming: The new regulations emphasise player protection and ethical gaming practices. This includes steps like age verification to prevent underage involvement, self-exclusion choices for gamers who want to limit their gaming activities, and adopting tools like session limits and reality checks to promote responsible gaming.
Data Privacy: Recognising the importance of data privacy, the laws are intended to contain protections for protecting user data. To safeguard sensitive player information from unauthorised access or exploitation, online gambling operators must comply with data protection regulations and deploy strong security measures.
Restrictions on Advertising and Marketing: The legislation may limit the advertising and marketing of online gaming platforms. The emphasis will be on eliminating aggressive marketing tactics that target vulnerable people, such as kids. Stricter standards for ad content and placement may be implemented.
Anti-Fraud and Anti-Money Laundering Measures: To combat criminal activity within the gaming ecosystem, the new legislation will almost certainly force online gambling companies to employ anti-fraud and anti-money laundering measures. Operators may need to set up mechanisms to detect fraud, report suspicious activity, and work with law enforcement.
Consumer Grievance Redressal: The legislation may emphasise the construction of efficient channels for resolving consumer complaints. Players should be able to report difficulties, seek resolution, and offer feedback on their play experiences through channels. The objective is to create a transparent and accountable conflict resolution mechanism.
Impact on Online Gaming Ecosystem
Adopting new laws for online gambling in India will likely have several consequences for the gaming industry. Let us look at some of these consequences:
Increased Player Trust: Implementing restrictions will increase player confidence in online gaming platforms. Establishing clear rules and procedures and steps to safeguard participants’ interests will develop a sense of trust and transparency. This can lead to increased participation and engagement in the gaming community.
Industry Consolidation: Stricter restrictions may result in industry consolidation. Compliance with the new legislation would need resources and investments, which might favour more prominent and more established gambling firms. Smaller and more non-compliant operators may find it challenging to fulfil regulatory standards, resulting in a more consolidated gaming sector.
Technological Progress: The requirement to comply with rules could lead to technological advancements in the online gambling sector. Operators may invest in modern identity verification systems, fraud detection methods, and responsible gaming solutions to satisfy their regulatory requirements. This can result in technological breakthroughs that improve gamers’ overall gaming experience.
Foreign Investment and Collaboration: Clear laws might entice overseas investors to enter the Indian gaming business. The regulated environment may appeal to international gambling enterprises looking to enter or extend their presence in India. Collaborations between Indian and foreign gaming firms may also expand, resulting in the sharing of experience, resources, and the production of high-quality gaming products.
Legal Clarity: Implementing particular laws would give online gambling operators and users clearer legal standards. This transparency can eliminate ambiguity and possible legal issues, allowing stakeholders to navigate the gaming ecosystem with better confidence and knowledge.
Contribution to the Indian Economy: A well-regulated online gaming business has the potential to contribute to the Indian economy. It has the potential to create jobs, attract investment, and produce tax money for the government. The economic effect of the gaming ecosystem is expected to increase as it grows under the new restrictions.
Challenges and Future Approach
One of the toughest challenges will be the efficient implementation and enforcement of the new regulations. Consistency in applying the legislation across multiple jurisdictions and guaranteeing compliance by all operators would necessitate comprehensive monitoring and regulatory measures. Developing suitable enforcement organisations and transparent standards for reporting and dealing with noncompliance will be critical. Besides this, online gaming is open to more than area-specific and many gaming platforms and operates internationally. Ensuring cross-border operations is a big challenge in addressing jurisdictional challenges will be complex. Collaborative efforts between nations can regulate cross-border online gaming. There may be increased collaboration between Indian and foreign gaming firms, resulting in the exchange of information, skills, and resources. This partnership can help the Indian gaming sector flourish while attracting foreign players and investments.
Esports Development: Esports have grown in popularity worldwide, and India is no exception. The Indian esports business has the potential to thrive with proper regulation and support, drawing both players and viewers. Esports-specific factors like player contracts, tournament integrity, and licencing requirements may be addressed in the regulations.
Conclusion
Despite obstacles, India’s new online gambling legislation can potentially establish a safer and more regulated gaming sector. the future depends on successful implementation, adjusting to a shifting landscape, finding the correct balance between regulation and innovation, and promoting ethical gaming practices. The Indian online gaming business can develop sustainably with the appropriate strategy, benefiting gamers and the broader economy.

Introduction
Ministry of Electronics and Information Technology (MeitY) Announces to Centre Government to Plan to Certify Permissible Online Games.
In a recent update to the notification released by the Ministry of Electronics and Information Technology (MeitY) on April 6, MeitY has requested gaming entities to establish self-regulatory organisations (SROs) within a timeframe of 30 days or a maximum of 90 days from the date of the notification, which is April 6, 2023. The Ministry of Electronics and Information Technology (MeitY) has further announced that the central government will certify which online games are permissible until the SROs are officially established. The intention behind establishing SROs is to assist intermediaries, such as Apple or Google, in determining what constitutes a permitted online game, but the SRO will take 2-3 months to complete. In the meanwhile, the Central government will step in and determine what is a permissible online game.
Information Technology (Intermediary Guidelines and Digital Media Ethics Code) Rules, 2021 & Intermediary Guidelines and Digital Media Ethics Code Amendment Rules, 2023
By enacting these rules, the Indian government has taken decisive action to protect Indian gamers and their financial resources against scams and fraud. The rules also serve to promote responsible gaming while preventing young and vulnerable users from being exposed to indecent or abusive content.
Amendment Rules developed the concept of a “Permissible online real money game.” This designation is reserved for games that have passed a review process conducted by a self-regulatory body (SRB). Amendment rules indicate that Online Gaming Intermediaries must ensure that they do not permit any third party to host non-permissible online real money games on their platforms. This development is important because it empowers us to distinguish between legitimate and illicit real money games.
The Amendment Rules define an online gaming provider as an “intermediary” under the Information Technology Act of 2000, creating a separate classification called ‘Online Gaming Intermediary’.

Central government to certify what is an ‘Online Permissible Game’
The industry has been wondering what games come under wagering and will be banned. So, until the SROs are officially established, the government, in the interim, will certify what is a permissible game, what is wagering, and what is not wagering. Games that involve elements of wagering are going to be barred. The new regulations prohibit wagering on any outcome, whether in skill-based or chance-based games. Hence gaming applications involving wagering and betting apps will be barred.
Self-Regulatory Organizations (SROs)
According to the new regulations by the Ministry of Electronics and Information Technology (MeitY), online gaming intermediaries must establish a Self-Regulatory Body (SRO) to approve games offered to users over the Internet. The SRO must be registered with the Ministry and develop a framework to ensure compliance with the IT Rules 2021 objectives. An ‘online game’ can be registered by the SRO if it meets specific criteria, which include that the game is offered by an online gaming intermediary that is a member of the self-regulatory body, the game is not containing any content harmful to India’s interests, and complying with all relevant Indian regulations. If these requirements are met, the intermediary can display a visible registration mark indicating its registration with the self-regulatory authority.
Conclusion
MeitY found that with the rapid growth of the gaming industry, the real money gaming (RMG) sector had to be regulated properly. Rules framed must be properly implemented to stop gambling, betting, and wagering apps.
The IT Rules 2021, along with the Amendment Rules 2023, are created to take concrete action to curb the proliferation of gambling, betting, and wagering apps in India. These rules empower to issue of directives to ban specific apps that facilitate or promote such activities. The app ban directive allows the government to take decisive action by blocking access to these apps, making them unavailable for download or use within the country. This measure is aimed at curbing the negative impact of gambling, betting, and wagering on individuals and society, including issues related to addiction, financial loss, and illegal activities. Rules aim to actively combat the spread and influence of such apps and provide a safer online environment for gaming users.
The self-regulatory body in the context of online gaming will have the authority to grant membership to gaming intermediaries, register online games, develop a framework for regulation, interact with the Central Government, address user complaints, report instances of non-compliance, and take necessary actions to safeguard online gaming users.
Introduction
India has been a nation where technology penetration has been a little slower in the previous decades; however, that has changed now. Cyberspace has influenced and touched every country and has significantly diminished the gap between developing nations, developed nations, and underdeveloped nations. This has also been substantiated and strengthened during the Covid-19 pandemic as the world went into lockdown and the cyberspace was the only medium of communication and information. India witnessed a rise of 61% in terms of internet users, and a significant part of this number represented rural India.
New Standards
These standards have been released in threefold aspects covering – Digital Television Receivers, USB Type-C chargers, and Video Surveillance Systems, thus streamlining the use of gadgets and reduction of e-waste for the country.
1. Digital Television Receivers
The Indian standard IS 18112:2022 specification for digital television, and this standard would enable reception of free-to-air TV and radio channels just by connecting a dish antenna with LNB mounted on a suitable area with good signal reception. This will help in the transmission of knowledge about government initiatives and schemes, the educational content of Doordarshan, and the repository of Indian cultural programs. Doordarshan is in the process of phasing out analog transmission, and free-to-air channels will continue to be broadcast using digital satellite transmission. The keen aspects of educational and awareness programs run by the Govt and CSOs will impact more Indians than before as the Ministry of Information and Broadcast intends to increase their free channels of Doordarshan from 55 to 200 by the end of this year, which shows the importance of developments in the mass media industry.
2. USB Type C
Standard (IS/IEC 62680-1-3:2022) for USB Type-C receptacles, plugs, and cables adopting the existing global standard IEC 62680-1-3:2022. This standard provides for the requirements for USB type C ports and cables for use in various electronic devices like laptops, mobile phones, and other gadgets. This standard is similar to the new European standard, which is also aimed at the reduction of carbon emissions and e-waste; this move will result in ease for the industry and the end users. This will also contribute towards the strengthening of the cyber security aspects and prevent threats like ‘Juice Jacking’ to a massive extent.
3. Video Surveillance System
IS 16190, this standard provides a detailed outline of the aspects of a video surveillance system, such as requirements for its components like camera devices, interfaces, system requirements, and tests to ascertain the camera’s image quality on different devices. This series of standards would assist customers, installers, and users in establishing their requirements and determining the appropriate equipment required for their intended application and also provide means of evaluating the performance of the VSS objectively. This will also help in the improvement of surveillance by the individuals, and this will also help in the better investigation by Law enforcement agencies and faster apprehension of criminals, thus contributing to an overall safe society.
The Advantages
These standards are in power with the Internationally prevalent standards, thus taking the safety factors to the global aspect. This will also allow the Indian industry to create world-class products which can be shared all across the globe. This will open India to various opportunities and job avenues, thus opening the world to invest in India. The aspect of Atma Nirbhar Bharat and Digital India will be strengthened to a new level as the nation will be able to deliver products in power with quality in developed countries. The end Indian consumer will benefit the most from these upgraded standards in terms of Digital Televisions, Type ‘C’ USB chargers, and Video surveillance systems, as these impacts the consumers’ daily activities in terms of security and access to information.
- Reduction in Carbon Emission
- Production of World Class components and devices
- Boost to the economy and Atmanirbhar Bharat
- New avenues and opportunities for startups and MSMEs
- Better transmission of Knowledge
- Boosting FDI
- Improved quality of products for the end consumer
- New innovation hubs and exposure to global talents
This government move simply shows how India is working toward securing the Sustainable development Goals (SDG) by United Nations. This clearly shares the message to the world that India is ready for the future and will also be a helping hand to various developing and underdeveloped nations in the times to come.
Conclusion
These standards will significantly contribute towards the reduction of E-Waste and unnecessary accessories for daily use gadgets. This strengthens the reduction in carbon emissions and thus contributes towards the perseverance of the environment and working towards sustainable development goals. Such standards will lead the future towards securing the netizens and their new and evolving digital habits. In the current phase of cyberspace, the most essential aspect of establishing Critical Infrastructure as the same will act as a shield against the threats of cyberspace.
