
#FactCheck: Old Ukraine Blast Video Falsely Shared as Iran Strike on Israeli Nuclear Site
Executive Summary
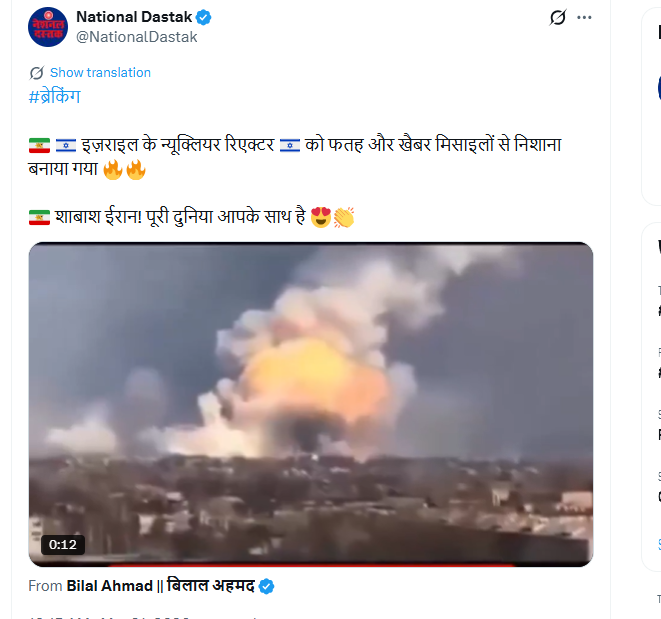
A video showing a massive fire and explosion is going viral on social media. The clip shows a large plume of smoke followed by a sudden blast. It is being shared with the claim that it depicts Iran attacking a nuclear reactor in Israel amid the ongoing Iran-Israel conflict. However, research by CyberPeace found that the claim is misleading. The viral video is actually from 2017 and shows a massive explosion at an ammunition depot in Ukraine.
Claim:
On social media platform X (formerly Twitter), a user shared the video on March 21, 2026, with the caption:“Israel’s nuclear reactor was targeted with Fateh and Khyber missiles. Well done Iran! The whole world is with you.”
Fact Check:
To verify the viral claim, we extracted keyframes from the video and conducted a reverse image search. During this process, we found the same video uploaded on March 23, 2017, on a YouTube channel named “null.” According to the upload, the video shows a massive explosion at an ammunition depot in Balakliya, Ukraine. Using these clues, we performed a keyword search and found a report published on March 24, 2017, by Global News.
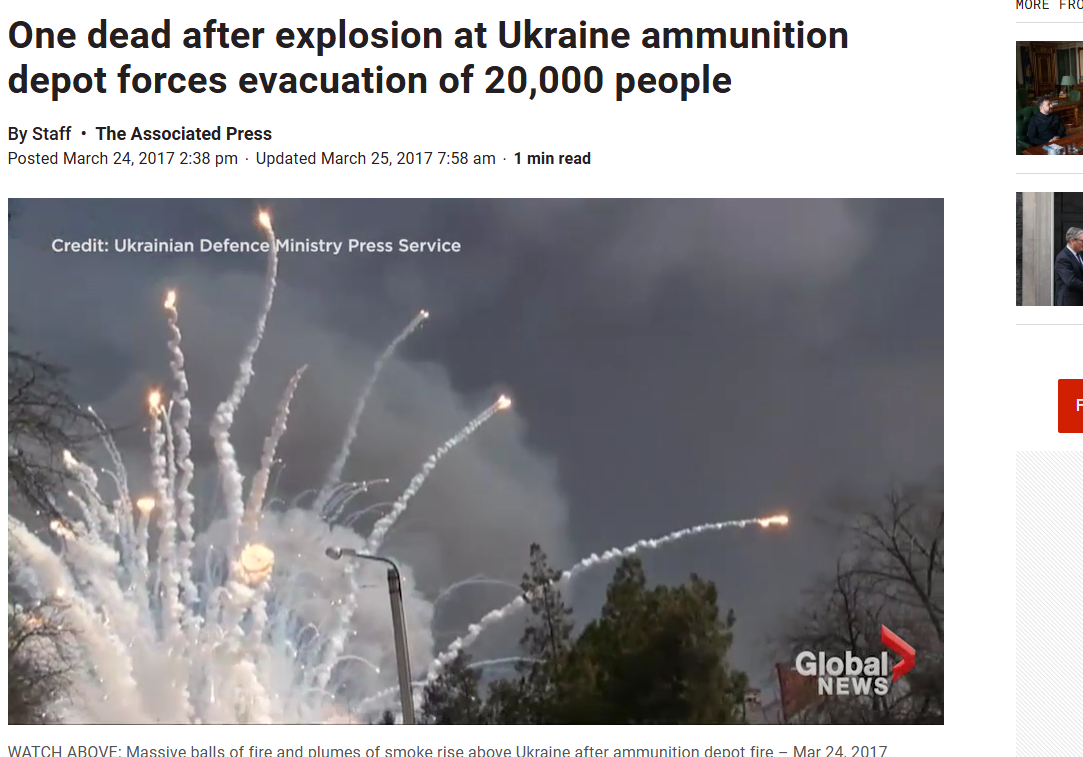
According to the report, a major fire and explosion broke out at a large military ammunition depot in Balakliya, located in Ukraine’s Kharkiv region. The incident resulted in one death, while nearly 20,000 people from surrounding areas were evacuated to safer locations.
Conclusion:
The claim that the video shows Iran attacking a nuclear reactor in Israel is misleading. The viral footage is actually from 2017 and depicts an explosion at an ammunition depot in Ukraine.

Related Blogs
Executive Summary
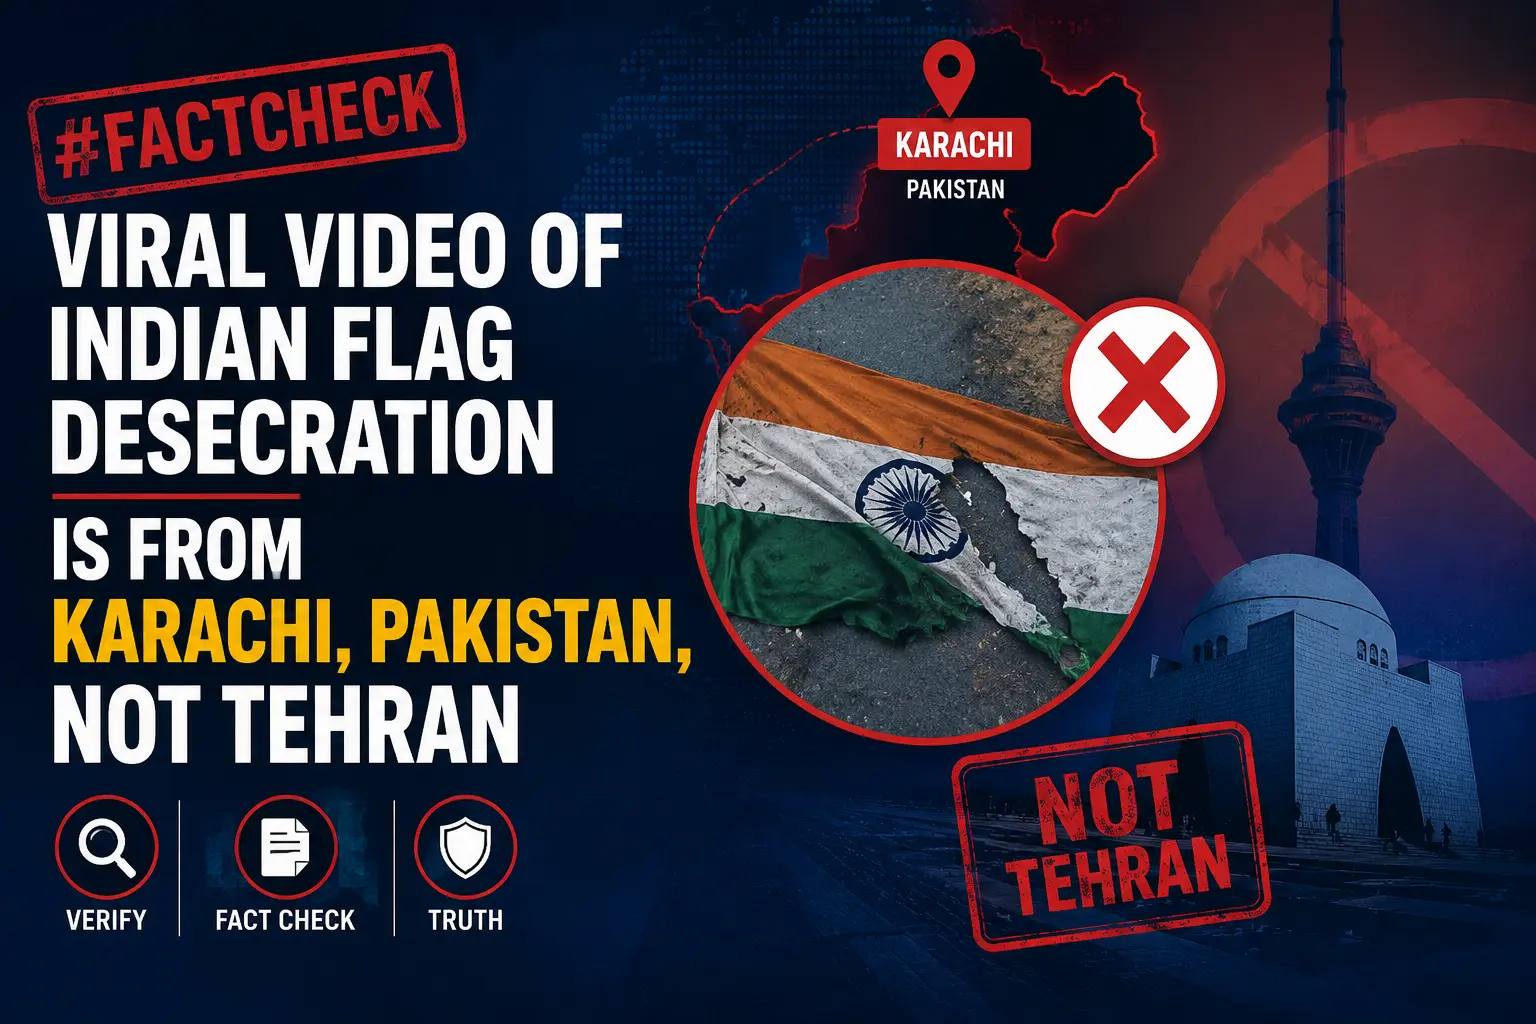
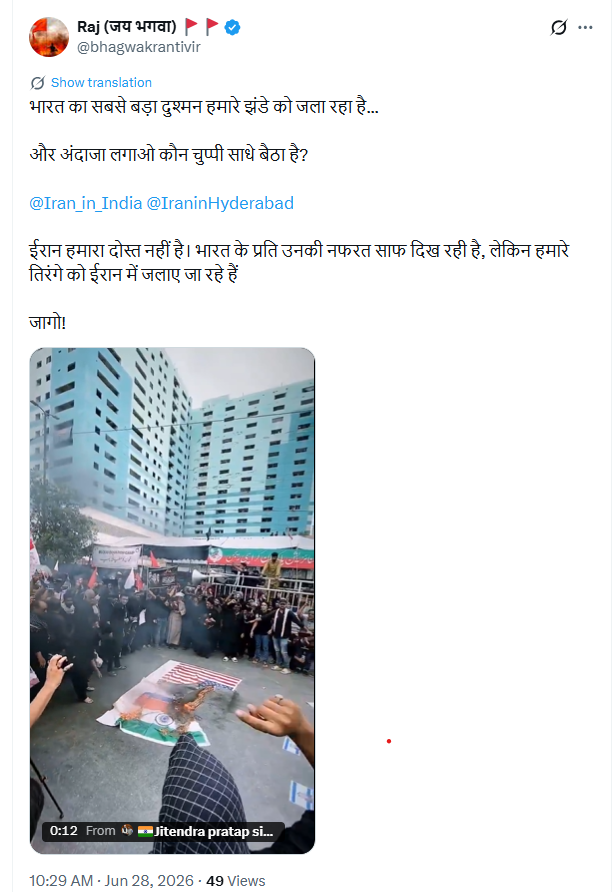
A video showing a large crowd disrespecting the Indian tricolor along with American and Israeli flags is being widely shared on social media. Users sharing the video claim that the incident recently took place in Iran's capital, Tehran, showcasing "Iran's hatred towards India." However, a fact-check done by the CyberPeace Research Wing has revealed that this claim is misleading. The viral video was not filmed in Iran, but rather during a procession in Karachi, Pakistan.
The Claim
A user on the social media platform X (formerly Twitter) shared the video with the caption: "India’s biggest enemy is burning our flag and guess who is sitting silently? Iran is not our friend. Their hatred towards India is clearly visible, but our tricolor is being burnt in Iran." https://x.com/bhagwakrantivir/status/2071096021183246667 , https://archive.ph/6mGE8
Factcheck
Keyframes extracted from the viral video were searched using Google Lens. This led to an Instagram post containing the exact same footage. The caption of this post identified the location as Karachi, Pakistan, noting that the demonstration was held in support of Iran, during which flags of India, the US, and Israel were burnt.
https://www.instagram.com/reels/DaDLQO6obcK/
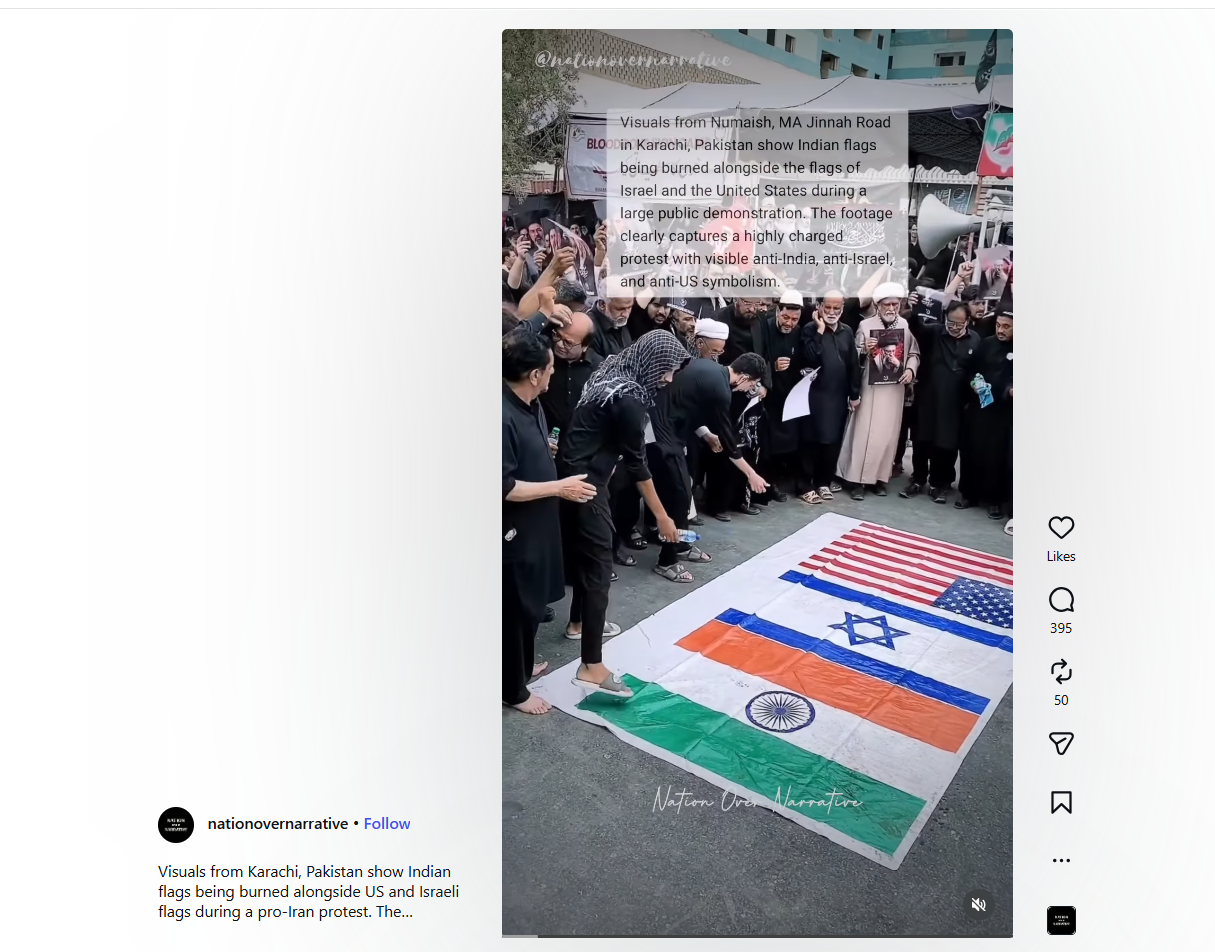
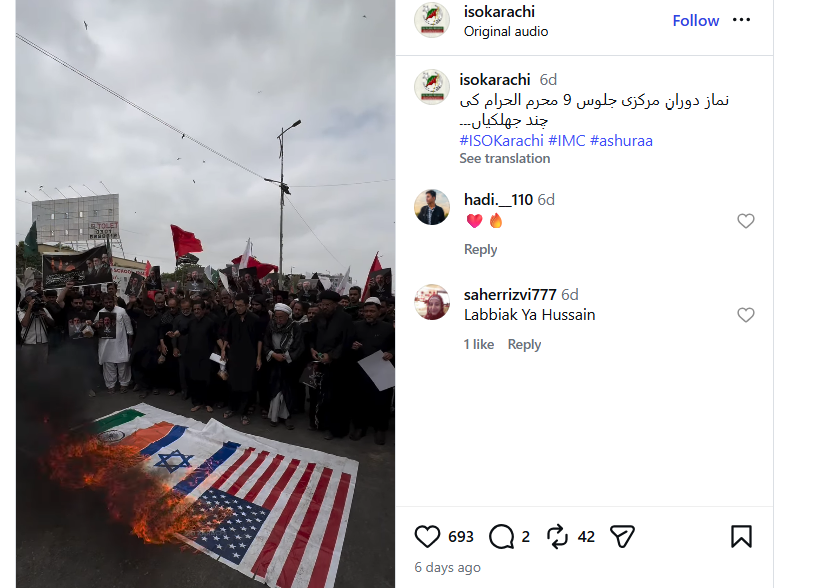
Further keyword searches led to the official Instagram account of the 'Imamia Students Organization Karachi'. A video uploaded on June 25, 2026, showed the same event captured from a different camera angle. According to the caption, the footage is from a '9th Muharram' procession in Karachi.
https://www.instagram.com/p/DaApSBfIpNQ/
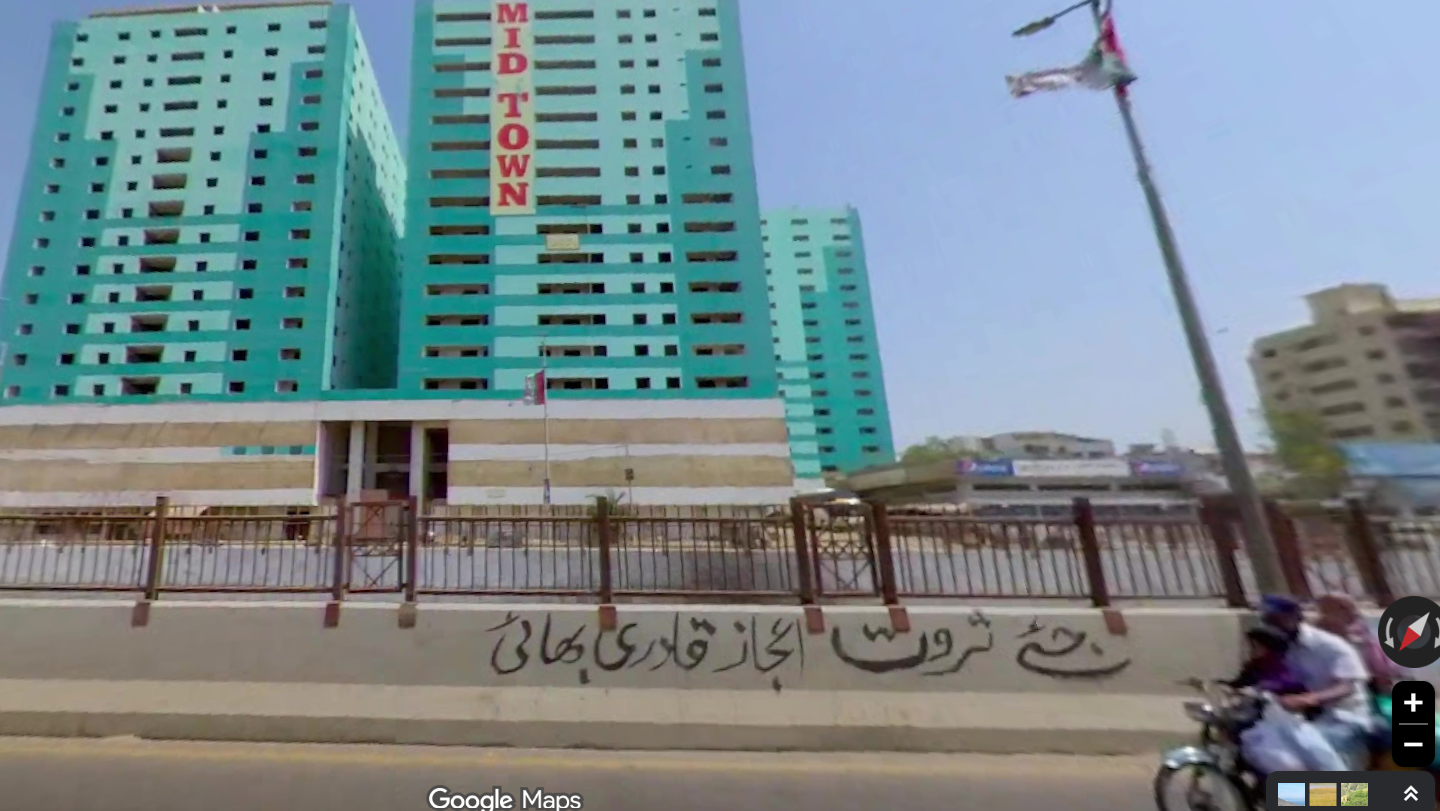
To conclusively establish the location, Google Maps Street View was used to cross-reference the physical landmarks seen in the video.The visual elements perfectly match Mohammad Ali Jinnah Road in Karachi, Pakistan.A distinct blue building named 'Mid Town', visible in the viral video, matches the Google Street View imagery of the location.
Conclusion
The research confirms that the video showing the burning and desecration of the Indian national flag is from Karachi, Pakistan, and not Tehran, Iran. The social media claims linking this incident to Iran are false and contextually misleading.
Introduction
Misinformation is no longer a challenge limited to major global platforms or widely spoken languages. In India and many other countries, false information is increasingly disseminated through local and vernacular languages, allowing it to reach communities more directly and intimately. While regional language content has played a crucial role in expanding access to information, it has also emerged as a powerful driver of misinformation by bad actors, and it often becomes harder to detect and counter. The challenge of local language misinformation is not merely digital in nature; it is deeply social, cultural, and shaped by specific local contexts.
Why Local-Language Misinformation Is More Impactful
A person’s mother tongue can be a highly effective medium for misinformation because it carries emotional resonance and a sense of authenticity. Information that aligns with an individual’s linguistic and cultural background is often trusted the most. When false narratives are framed using familiar expressions, local references, or community-specific concerns, they are more readily accepted and shared more widely.
Misinformation in a language like English, which is more heavily moderated, does not usually have the same impact as content in vernacular languages. In the latter case, such content tends to circulate within closed networks such as family WhatsApp groups, regional Facebook pages, local YouTube channels, and community forums. These spaces are often perceived as safe or trusted, which lowers scepticism and encourages the spread of unverified information.
The Role of Digital Platforms and Algorithms
Although social media platforms have opened up access to the content of regional languages, the moderation mechanisms have not kept up. The automated control systems for content are frequently trained mainly on the dominant languages, thus missing the detection of vernacular speech, slang, dialects, and code-mixing.
This results in a disparity in the enforcement of laws where misinformation in local languages:
- Doesn’t go through automated fact-checking tools
- Is subject to human moderation takes place at a slower pace
- Is less prone to being reported or flagged
- Gains unrestrained access for a longer time period than first imagined
The problem is further magnified by algorithmic amplification. Content that triggers very strong emotional reactions fear, anger, pride, or outrage, has a higher chance of being promoted, irrespective of its truthfulness. In regional situations, such content may very quickly sway public opinion even in very closely knit communities.
Forms of Vernacular Misinformation
Local-language misinformation appears in various forms:
- Health misinformation, with such examples as panic remedies, vaccine myths, and misleading medical prescriptions
- Political misinformation, which is mostly identified with regional identity, local grievances, or community narratives
- Rumours regarding disasters that are very hard to control and spread hatred during floods, earthquakes, or other public emergencies
- Economic and financial frauds that are perpetrated via the local dialect authorities or trusted institutions
- Cultural and religious untruths, which are based on exploiting the core of the beliefs
The regional aspect of such misinformation makes it very difficult to be corrected because the fact-checks in other languages may not get to that audience.
Community-Level Consequences
The effect of misinformation in local languages is not only about the misdirection of individuals. It can also:
- Negatively affect the process of public institutions gaining trust
- Support social polarisation and communal strife
- Get in the way of public health measures
- Help shape the decision-making process in elections at the grassroots level
- Take advantage of the digitally illiterate poor people
In a lot of scenarios, the damage done is not instant but rather accumulative, thus changing perceptions and supporting false worldviews more.
Why Countering Vernacular Misinformation Is Difficult
Multiple structural layers make it difficult to respond effectively:
- Variety of Languages: Just in India, there are many languages and dialects, which are very hard to monitor universally.
- Culturally Aware Systems: The local languages sometimes bear meanings that are deeply rooted in the culture, such as by using sarcasm or referring to history, and automated systems are unable to interpret it correctly.
- Reporting Not Common: Users might not spot misinformation or may not want to be a part of the struggle by showing the content shared by reliable members of the community.
- Insufficient Fact-Checking Capacity: Resources are often unavailable for fact-checking organisations to perform their duties worldwide in different languages effectively.
Building a Community-Centric Response
Overcoming misinformation in local languages needs a community-driven resilience approach instead of a platform-centric one. Some of the key actions are:
- Boosting Digital Literacy: Users will be able to question, verify, and put the content on hold before sharing it, thanks to the regional language awareness campaigns that will be conducted.
- Facilitating Local Fact-Checkers: Local journalists, educators, and NGOs are the main players in providing the context for verification.
- Accountability of Platforms: It is necessary for technology companies to support global moderation in several languages, the hiring of local experts, and the implementation of transparent enforcement mechanisms.
- Contemplating Policy and Governance: Regulatory frameworks should facilitate proactive risk assessment while controlling the right to free expression.
- Establishment of Trusted Local Intermediaries: Community leaders, health workers, teachers, and local organisations can engage in preventing misinformation among the networks that they are trusted in.
The Way Forward
Misinformation in local languages is not a minor concern; it is an issue that directly affects the future of digital trust. As the number of users accessing the internet through local language interfaces continues to grow, the volume and influence of regional content will also increase. If measures do not include all language groups, misinformation will remain least corrected and most influential at the community level, where it is also the hardest to identify and address.
Such a problem exists only if the power of language is not recognised. Therefore, one can say that it is necessary to protect the quality of information in local languages, not only for digital safety but for other factors as well, such as social cohesion, democratic participation, and public well-being.
Conclusion
Vernacular content has the potential to be very powerful in the ways it can inform, include and empower; meanwhile, if it goes unmonitored, it has the same potential to mislead, divide, and harm. Mis-disinformation in local languages calls for the cooperation of platforms, regulators, NGOs, and the communities involved. To win over the digital ecosystem, it has to speak all languages, not only for communication but also for protection.
References
- https://www.mdpi.com/2304-6775/10/2/15
- https://afpr.in/regional-languages-shaping-indias-online-discourse/
- https://medium.com/@pratikgsalvi03/how-indias-misinformation-surge-and-media-credibility-crisis-are-undermining-democracy-public-dc8ad7be8e12
- https://projectshakti.in/
- https://journals.sagepub.com/doi/10.1177/02683962211037693
- https://rsisinternational.org/journals/ijriss/Digital-Library/volume-8-issue-11/505-518.pdf
- https://www.irjmets.com/upload_newfiles/irjmets71200016652/paper_file/irjmets71200016652.pdf

Introduction
In the hyperconnected world, cyber incidents can no longer be treated as sporadic disruptions; such incidents have become an everyday occurrence. The attack landscape today is very consequential and shows significant multiplication in its frequency, with ransomware attacks incapacitating a health system, phishing attacks hitting a financial institution, or state-sponsored attacks on critical infrastructures. Towards counteracting such threats, traditional ways alone are not enough, they gravely rely on manual research and human intellect. Attackers exercise speed, scale, and stealth, and defenders are always four steps behind. With such a widening gap, it is deemed necessary to facilitate incident response and crisis management with the intervention of automation and artificial intelligence (AI) for faster detection, context-driven decision-making, and collaborative response beyond human capabilities.
Incident Response and Crisis Management
Incident response is the structured way in which organisations deal with responding to detecting, segregating, and recovering from security incidents. Crisis management takes this even further, dealing not only with the technical fallout of a breach but also its business, reputation, and regulatory implications. Echelon used to depend on manual teams of people sorting through logs, cross-correlating alarms, and generating responses, a paradigm effective for small numbers but quickly inadequate in today's threat climate. Today's opponents attack at machine speed, employing automation to launch attacks. Under such circumstances, responding with slow, manual methods means delay and draconian consequences. The AI and automation introduction is a paradigm change that allows organisations to equate the pace and precision with which attackers initiate attacks in responding to incidents.
How Automation Reinvents Response
Cybercrime automation liberates cybercrime analysts from boring and repetitive tasks that consume time. An analyst manually detects potential threats from a list of hundreds each day, while automated systems sift through noise and focus only on genuine threats. Malware can automatically cause infected computers to be disconnected from the network to avoid spreading or may automatically have its suspicious account permissions removed without human intervention. The security orchestration systems move further by introducing playbooks, predefined steps describing how incidents of a certain type (e.g., phishing attempts or malware infections) should be handled. This ensures fast containment while ensuring consistency and minimising human error amid the urgency of dealing with thousands of alerts.
Automation takes care of threat detection, prioritisation, and containment, allowing human analysts to refocus on more complex decision-making. Instead of drowning in the sea of trivial alerts, security teams can now devote their efforts to more strategic areas: threat hunting and longer-term resilience. Automation is a strong tool of defence, cutting response times down from hours to minutes.
The Intelligence Layer: AI in Action
If automation provides speed, then AI is what allows the brain to be intelligent and flexible. Working with old and fixed-rule systems, AI-enabled solutions learn from experiences, adapt to changes in threats, and discover hidden patterns of which human analysts themselves would be unaware. For instance, machine learning algorithms identify normal behaviour on a corporate network and raise alerts on any anomalies that could indicate an insider attack or an advanced persistent threat. Similarly, AI systems sift through global threat intelligence to predict likely attack vectors so organisations can have their vulnerabilities fixed before they are exploited.
AI also boosts forensic analysis. Instead of searching forever for clues, analysts let AI-driven systems trace back to the origin of an event, identify vulnerabilities exploited by attackers, and flag systems that are still under attack. During a crisis, AI is a decision support that predicts outcomes of different scenarios and recommends the best response. In response to a ransomware attack, for example, based on context, AI might advise separating a single network segment or restoring from backup or alerting law enforcement.
Real-World Applications and Case Studies
Already, this mitigation has been provided in the form of real-world applications of automation and AI. Consider, for example, IBM Watson for Cybersecurity, which has been applied in analysing unstructured threat intelligence and providing analysts with actionable results in minutes, rather than days. Like this, systems driven by AI in DARPA's Cyber Grand Challenge demonstrated the ability to automatically identify an instant vulnerability, patch it, and reveal the potential of a self-healing system. AI-powered fraud detection systems stop suspicious transactions in the middle of their execution and work all night to prevent losses. What is common in all these examples is that automation and AI lessen human effort, increase accuracy, and in the event of a cyberattack, buy precious time.
Challenges and Limitations
While promising, the technology is still not fully mature. The quality of an AI system is highly dependent on the training data provided; poor training can generate false positives that drown teams or worse false negatives that allow attackers to proceed unabated. Attackers have also started targeting AI itself by poisoning datasets or designing malware that does not get detected. Aside from risks that are more technical, the operational and financial costs involved in implementing advanced AI-based systems present expensive threats to any company. Organisations will have to make expenditures not only on technology but also for the training of staff to best utilise these tools. There are some ethical and privacy issues to consider as well because systems may be processing sensitive personal data, so global data protection laws such as the GDPR or India's DPDP Act could come into conflict.
Creating a Human-AI Collaboration
The future is not going to be one of substitution by machines but of creating human-AI synergy. Automation can do the drudgery, AI can provide smarts, and human professionals can use judgment, imagination, and ethical decisions. One would want to build AI-fuelled Security Operations Centres where technology and human experts work in tandem. Continuous training must be provided to AI models to reduce false alarms and make them most resistant against adversarial attacks. Regular conduct of crisis drills that combine AI tools and human teams can ensure preparedness for real-time events. Likewise, it is worth integrating ethical AI guidelines into security frameworks to ensure a stronger defence while respecting privacy and regulatory compliance.
Conclusion
Cyber-attacks are an eventuality in this modern time, but the actual impact need not be so harsh. The organisations can maintain the programmatic method of integrating automation and AI into incident response and crisis management so that the response against the very threat can be shifted from reactive firefighting to proactive resilience. Automation gives speed and efficiency while AI gives intelligence and foresight, hence putting the defenders on par and possibly exceeding the speed and sophistication of the attackers. But an utmost system without human inquisitiveness, ethical reasoning, and strategic foresight would remain imperfect. The best defence is in that human-machine relationship symbiotic system wherein automation and AI take care of how fast and how many cyber threats come in, whereas human intellect ensures that every response is aligned with larger organizational goals. This synergy is where cybersecurity resiliency will reside in the future-the defenders won't just be reacting to emergencies but will rather be driving the way.
References
- https://www.sisainfosec.com/blogs/incident-response-automation/
- https://stratpilot.ai/role-of-ai-in-crisis-management-and-its-critical-importance/
- https://www.juvare.com/integrating-artificial-intelligence-into-crisis-management/
- https://www.motadata.com/blog/role-of-automation-in-incident-management/
