
#FactCheck - AI-Generated Visuals Falsely Shared as Government Subsidy for Free Electricity and Air Conditioners in the Philippines
Executive Summary
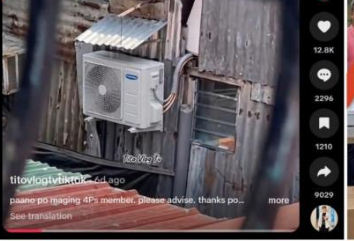
In the Philippines, social media users have been sharing a video and an image following complaints over sharp increases in electricity bills. The posts claim that, in exchange for higher electricity charges, low-income households are being provided free electricity and air conditioning units. However, a fact-check by CyberPeace Research Wing found no evidence to support these claims. A closer examination of the visuals revealed several inconsistencies and visual indicators suggesting that the content is likely AI-generated.
Claim
An image was also shared on Instagram on April 29, showing purported beneficiaries holding new air conditioning units allegedly provided “free by the government.”
Fact Check
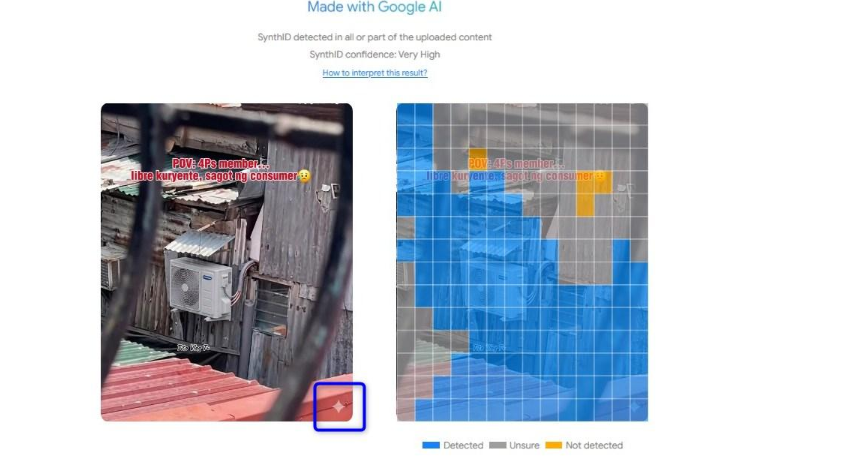
However, the video and image circulating on social media do not actually show beneficiaries receiving any subsidy. A closer analysis of the visuals indicates that the content is AI-generated. In the initial frames of the misrepresented video, a diamond-shaped icon can be seen in the bottom-right corner, which is the watermark associated with Google’s Gemini AI model.
Further analysis using Google’s SynthID Detector, a tool designed to identify AI-generated content, indicated with a “very high” level of confidence that the material was created using the company’s AI technology.
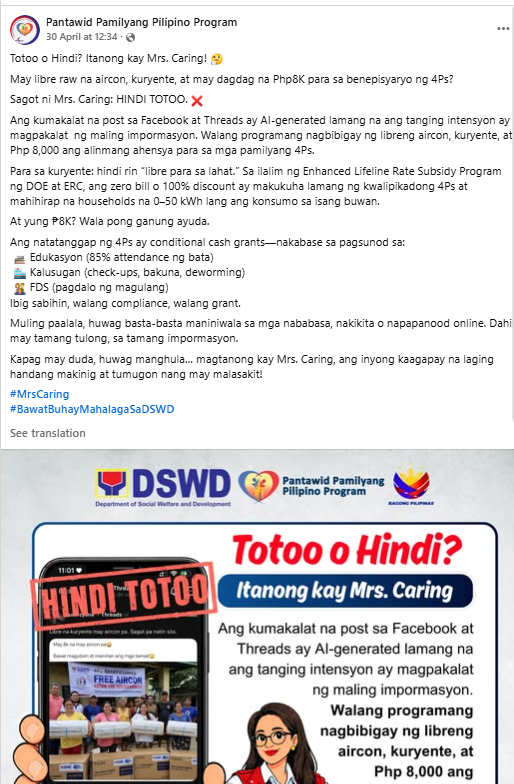
The country’s social welfare agency also issued a statement on Facebook on April 30, rejecting the claim and saying it is “not true” and intended only to “propagate wrong information.” Social welfare agency statement on Facebook
- https://www.facebook.com/photo?fbid=1373756198132587&set=a.665386155636265
Conclusion
However, the video and image circulating on social media do not actually show beneficiaries receiving any subsidy. A closer analysis of the visuals indicates that the content is AI-generated. In the initial frames of the misrepresented video, a diamond-shaped icon can be seen in the bottom-right corner, which is the watermark associated with Google’s Gemini AI model. The viral video and image are misleading. Multiple inconsistencies and visual cues suggest that the content is likely AI-generated, and the claim that low-income households are receiving free electricity and air conditioners is false.

Related Blogs
"India’s digital public infrastructure promises inclusion and efficiency. But when essential services depend on handing over data, children become legible to the state long before anyone listens to them."
India’s digital transformation deserves much of the praise it gets. Digital Public Infrastructure (DPI) has taken public services to people at a scale few countries have managed. Still, one question gets less attention than it should: what happens when the state’s wish for a neatly administered citizen starts to override the rights of a child?
Aditi Pillai takes this up in From Principle(al) to Practice: The Child as a Datafied Digital Citizen in India’s Digital Public Infrastructure. She doesn’t argue against digital infrastructure. Her point is that its claim to serve the public can’t be separated from the power it holds over the people enrolled in it. The most obvious example is children. When they are persons with rights today, they run the risk of being reduced to administrative categories, data points and future projections. A child’s citizenship is suspended until adulthood. These days, identity, privacy and agency are important but digital governance frequently views childhood as something that needs to be tracked, controlled and maximised.
Protection without participation
Pillai’s sharpest idea is what she calls “double paternalism.” She uses 49-story completion responses from parents who completed brief hypothetical situations regarding enrolling a child in a computerised system, as well as expert interviews. Her focus is on how parental and institutional power reinforce one another and prevent kids from making decisions about their own online life.
Consider the Automated Permanent Academic Account Registry (APAAR), which provides a permanent academic identification for every student. Consolidating records may well help administrators. The harder questions are whether enrolment is truly voluntary, whether refusing carries a penalty, and whether a family can question how data is collected and linked without risking the child’s schooling.
The answers weren’t encouraging. Many parents either accepted enrolment despite their reservations or viewed it as a requirement that wasn’t worth challenging. Out of the 48, only four exhibited aggressive resistance and just one admitted that the adolescent in the scenario might have a voice. It is not appropriate to interpret this little qualitative study as a statistical representation of Indian parents. Nevertheless, it implies that there was never a choice and that obedience may be mistaken for informed agreement.
That is the double edge. The state compels, or strongly nudges, parents to enrol their children. Parents then decide on the child’s behalf without involving them. Both layers claim to protect the child’s interests, and the child’s own voice is missing from both.
When convenience becomes compulsion
It is easy to treat digital systems as neutral tools. They aren’t. Every system embodies decisions about what is collected, which records are linked, who can see them, and what happens to someone who can’t or won’t comply.
Pillai points to what can follow when educational records are tied to identity systems. Persistent data trails can expose children to long-term profiling. Rigid identification rules can shut out those whose lives don’t fit the institutional template: children without reliable documents, those who have left abusive homes, those who can’t provide valid biometrics.
There is an irony here. A system built to make citizens more visible to the state can make its most vulnerable citizens less visible as people. When a child can’t meet the system’s requirements, the result is often exclusion, not accommodation.
All of this does not imply that India should abandon digital infrastructure.The true debate is whether people’s freedom of choice, privacy and equitable access should be sacrificed for efficiency. A system can’t call itself inclusive if participation is compulsory in practice and the exceptions are badly designed.
Parents can’t carry this alone
Pillai also names “potentiality risk,” the worry that data gathered in childhood will quietly shape future opportunities, reputation or identity. A school record can outlast the circumstances that produced it. A bad year, once logged, may follow a student if institutions come to read them through a permanent digital profile.
Parents are left in an impossible spot. They are expected to guard their children against risks they may not fully understand and have little power to control. Responsibility slides from the institutions that build and run these systems to the families who must live with them. That is a weak form of accountability. Parental consent can’t justify every kind of data processing involving a child, and parents shouldn’t have to bargain one by one with schools or authorities when the alternative is losing an essential service.
The Digital Personal Data Protection Act, 2023, treats children as a distinct category of data principals and requires verifiable parental consent, subject to its provisions and rules. That is a start. The deeper question remains: does a child-focused data regime only regulate what adults decide about children, or does it also leave room for children’s own evolving views and abilities? Protection without participation can turn into control by another name.
From data subjects to digital citizens
Pillai’s strategy is built on two interconnected concepts: a rights-based perspective of data justice rooted in the UN Convention on the Rights of the Child (UNCRC) and participatory digital citizenship.
In actuality, this entails consulting kids before systems are developed rather than after. Parents need clear information and practical options to raise concerns about enrolment. Accessible grievance procedures, real alternatives when necessary and safeguards against exclusion are all necessary for institutions. Collection and linking of data should be proportionate to a legitimate purpose with clear accountability for how it is used later. Above all, the child’s best interests should be a standard that actually governs decisions, not a phrase invoked to excuse administrative convenience.
India’s digital ambitions and children’s rights don’t have to collide. A public system is best judged by how it treats the people least able to challenge it. The real test of a digital state is not how many people it can enrol or connect, but whether they keep their dignity and agency once inside. Children should not end up as records to be maintained or risks to be managed. They are citizens now, and their rights matter now.
References
- Aditi Pillai, ‘From Principle(al) to Practice: The Child as a Datafied Digital Citizen in India’s Digital Public Infrastructure’ (2026) 22(2) Indian Journal of Law and Technology, Article 3. DOI: 10.55496/NFYV5618.
- Digital Personal Data Protection Act 2023, s 9.
- United Nations Convention on the Rights of the Child (adopted 20 November 1989, entered into force 2 September 1990) 1577 UNTS 3.
- Government of India, ‘G20 New Delhi Leaders’ Declaration’ (2023).

Introduction
With the ever-growing technology where cyber-crimes are increasing, a new cyber-attack is on the rise, but it’s not in your inbox or your computer- it's targeting your phone, especially your smartphone. Cybercriminals are expanding their reach in India, with a new text-messaging fraud targeting individuals. The Indian Computer Emergency Response Team (CERT-In) has warned against "smishing," or SMS phishing.
Understanding Smishing
Smishing is a combination of the terms "SMS" and "phishing." It entails sending false text messages that appear to be from reputable sources such as banks, government organizations, or well-known companies. These communications frequently generate a feeling of urgency in their readers, prompting them to click on harmful links, expose personal information, or conduct financial transactions.
When hackers "phish," they send out phony emails in the hopes of tricking the receiver into clicking on a dangerous link. Smishing is just the use of text messaging rather than email. In essence, these hackers are out to steal your personal information to commit fraud or other cybercrimes. This generally entails stealing money – usually your own, but occasionally also the money of your firm.
The cybercriminals typically use these tactics to lure victims and steal the information.
Malware- The cyber crooks send the smishing URL link that might tick you into downloading malicious software on your phone itself. This SMS malware may appear as legitimate software, deceiving you into putting in sensitive information and transmitting it to crooks.
Malicious website- The URL in the smishing message may direct you to a bogus website that seeks sensitive personal information. Cybercriminals employ custom-made rogue sites meant to seem like legitimate ones, making it simpler to steal your information.
Smishing text messages often appear to be from your bank, asking you to share personal sensitive information, ATM numbers, or account details. Mobile device cybercrime is increasing, as is mobile device usage. Aside from the fact that texting is the most prevalent usage of cell phones, a few additional aspects make this an especially pernicious security issue. Let's go over how smishing attacks operate.
Modus Operandi
The cyber crooks commit the fraud via SMS. As attackers assume an identity that might be of someone trusted, Smishing attackers can use social engineering techniques to sway a victim's decision-making. Three things are causing this deception:
- Trust- Cyber crooks target individuals, by posing to someone from a legitimate individual and organization, this naturally lowers a person’s defense against threats.
- Context- Using a circumstance that might be relevant to targets helps an attacker to create an effective disguise. The message feels personalized, which helps it overcome any assumption that it is spam.
- Emotion- The nature of the SMS is critical; it makes the victim think that is urgent and requires rapid action. Using these tactics, attackers craft communications that compel the receiver to act.
- Typically, attackers want the victim to click on a URL link within the text message, which takes them to a phishing tool that asks them for sensitive information. This phishing tool is frequently in the form of a website or app that also assumes a phony identity.
How does Smishing Spread?
As we have revealed earlier smishing attacks are delivered through both traditional texts. However, SMS phishing attacks primarily appear to be from known sources People are less careful while they are on their phones. Many people believe that their cell phones are more secure than their desktops. However, smartphone security has limits and cannot always guard against smishing directly.
Considering the fact phones are the target While Android smartphones dominate the market and are a perfect target for malware text messages, iOS devices are as vulnerable. Although Apple's iOS mobile technology has a high reputation for security, no mobile operating system can protect you from phishing-style assaults on its own. A false feeling of security, regardless of platform, might leave users especially exposed.
Kinds of smishing attacks
Some common types of smishing attacks that occurred are;
- COVID-19 Smishing: The Better Business Bureau observed an increase in reports of US government impersonators sending text messages requesting consumers to take an obligatory COVID-19 test via a connected website in April 2020. The concept of these smishing assaults may readily develop, as feeding on pandemic concerns is a successful technique of victimizing the public.
- Gift Smishing: Give away, shopping rewards, or any number of other free offers, this kind of smishing includes free services or products, from a reputable or other company. attackers plan in such a way that the offer is for a limited time or is an exclusive offer and the offers are so lucrative that one gets excited and falls into the trap.
CERT Guidelines
CERT-In shared some steps to avoid falling victim to smishing.
- Never click on any suspicious link in SMS/social media charts or posts.
- Use online resources to validate shortened URLs.
- Always check the link before clicking.
- Use updated antivirus and antimalware tools.
- If you receive any suspicious message pretending to be from a bank or institution, immediately contact the bank or institution.
- Use a separate email account for personal online transactions.
- Enforce multi-factor authentication (MFA) for emails and bank accounts.
- Keep your operating system and software updated with the latest patches.
Conclusion
Smishing uses fraudulent mobile text messages to trick people into downloading malware, sharing sensitive data, or paying cybercriminals money. With the latest technological developments, it has become really important to stay vigilant in the digital era not only protecting your computers but safeguarding the devices that fit in the palm of your hand, CERT warning plays a vital role in this. Awareness and best practices play a pivotal role in safeguarding yourself from evolving threats.
Reference
- https://www.ndtv.com/india-news/government-warns-of-smishing-attacks-heres-how-to-stay-safe-4709458
- https://zeenews.india.com/technology/govt-warns-citizens-about-smishing-scam-how-to-protect-against-this-online-threat-2654285.html
- https://www.the420.in/protect-against-smishing-scams-cert-in-advice-online-safety/
Executive Summary
A video is going viral on social media, claiming that an Indian Hindu father married his own biological daughter because he could not afford to pay her dowry. CyberPeace Research found that the video features scripted content being presented as a real-life incident, making the claim misleading. The claim that the man married his own biological daughter is false.
Claim:
A video is being shared on social media with the claim that an Indian Hindu father married his own biological daughter because he was unable to afford her dowry.
https://x.com/i/birdwatch/t/2112470461011599390?source=6
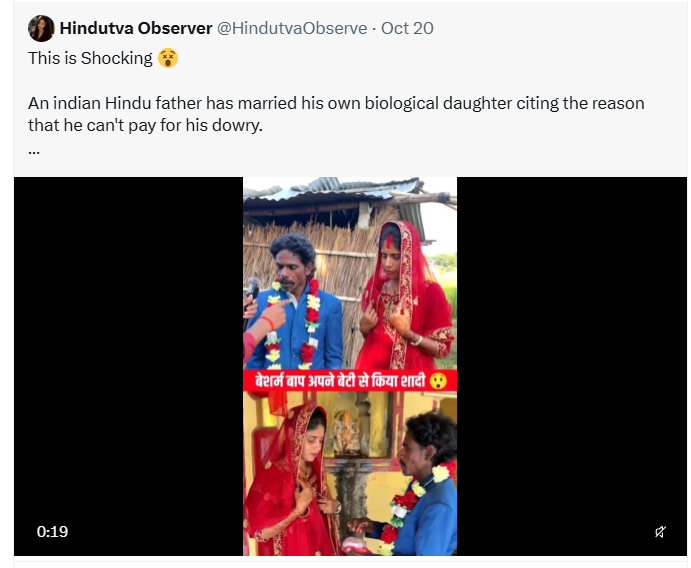
Fact Check
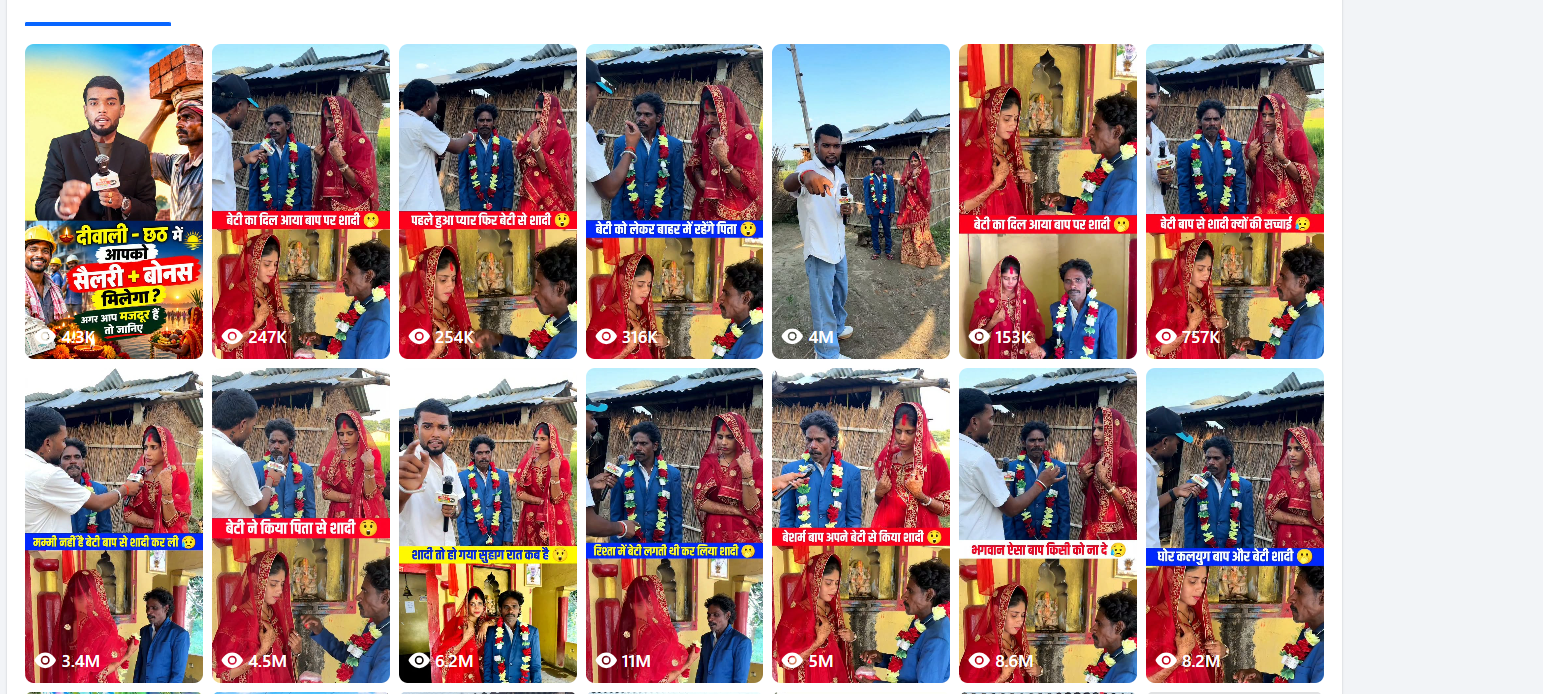
To verify the viral video, we conducted a reverse image search of its keyframes. However, we did not find any credible media reports about the incident. As the next step in our research, we found the video on a Facebook account named Kundan Kumar Mukhiya, where the creator had identified the video as scripted content.
https://www.facebook.com/reel/1170873325369168
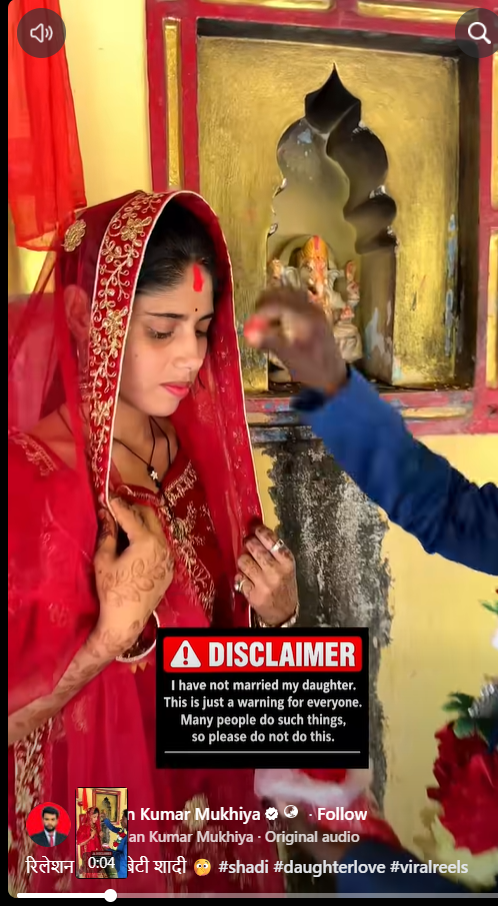
As the next step in our research, we found another video on the same page, which was also identified as scripted content.
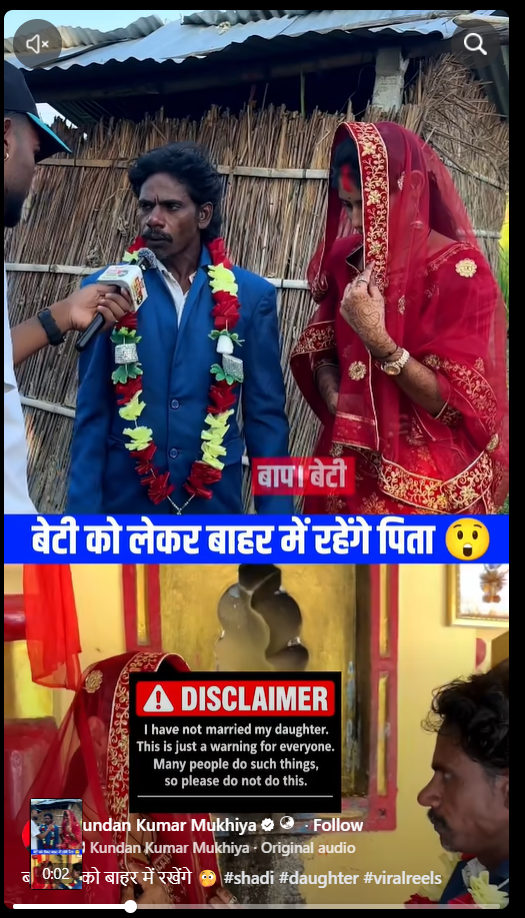
We examined the user's Facebook account and found that he is a content creator who makes scripted videos.
Conclusion
Our research found that the video features scripted content being shared with a misleading claim, presenting it as a real-life incident. The claim that the man married his own biological daughter is false.
