
#FactCheck - Edited Video of ‘India-India’ Chants at Republican National Convention
Executive Summary:
A video online alleges that people are chanting "India India" as Ohio Senator J.D. Vance meets them at the Republican National Convention (RNC). This claim is not correct. The CyberPeace Research team’s investigation showed that the video was digitally changed to include the chanting. The unaltered video was shared by “The Wall Street Journal” and confirmed via the YouTube channel of “Forbes Breaking News”, which features different music performing while Mr. and Mrs. Usha Vance greeted those present in the gathering. So the claim that participants chanted "India India" is not real.

Claims:
A video spreading on social media shows attendees chanting "India-India" as Ohio Senator J.D. Vance and his wife, Usha Vance greet them at the Republican National Convention (RNC).


Fact Check:
Upon receiving the posts, we did keyword search related to the context of the viral video. We found a video uploaded by The Wall Street Journal on July 16, titled "Watch: J.D. Vance Is Nominated as Vice Presidential Nominee at the RNC," at the time stamp 0:49. We couldn’t hear any India-India chants whereas in the viral video, we can clearly hear it.
We also found the video on the YouTube channel of Forbes Breaking News. In the timestamp at 3:00:58, we can see the same clip as the viral video but no “India-India” chant could be heard.

Hence, the claim made in the viral video is false and misleading.
Conclusion:
The viral video claiming to show "India-India" chants during Ohio Senator J.D. Vance's greeting at the Republican National Convention is altered. The original video, confirmed by sources including “The Wall Street Journal” and “Forbes Breaking News” features different music without any such chants. Therefore, the claim is false and misleading.
Claim: A video spreading on social media shows attendees chanting "India-India" as Ohio Senator J.D. Vance and his wife, Usha Vance greet them at the Republican National Convention (RNC).
Claimed on: X
Fact Check: Fake & Misleading

Related Blogs

Executive Summary
In the Philippines, social media users have been sharing a video and an image following complaints over sharp increases in electricity bills. The posts claim that, in exchange for higher electricity charges, low-income households are being provided free electricity and air conditioning units. However, a fact-check by CyberPeace Research Wing found no evidence to support these claims. A closer examination of the visuals revealed several inconsistencies and visual indicators suggesting that the content is likely AI-generated.
Claim
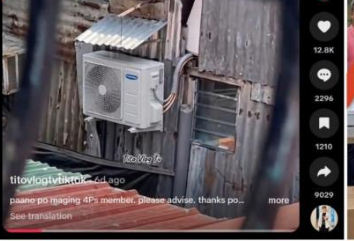
An image was also shared on Instagram on April 29, showing purported beneficiaries holding new air conditioning units allegedly provided “free by the government.”
Fact Check
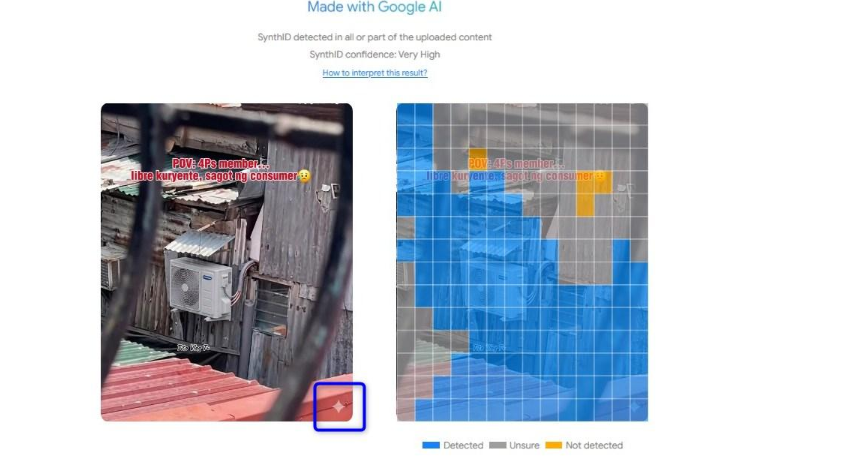
However, the video and image circulating on social media do not actually show beneficiaries receiving any subsidy. A closer analysis of the visuals indicates that the content is AI-generated. In the initial frames of the misrepresented video, a diamond-shaped icon can be seen in the bottom-right corner, which is the watermark associated with Google’s Gemini AI model.
Further analysis using Google’s SynthID Detector, a tool designed to identify AI-generated content, indicated with a “very high” level of confidence that the material was created using the company’s AI technology.
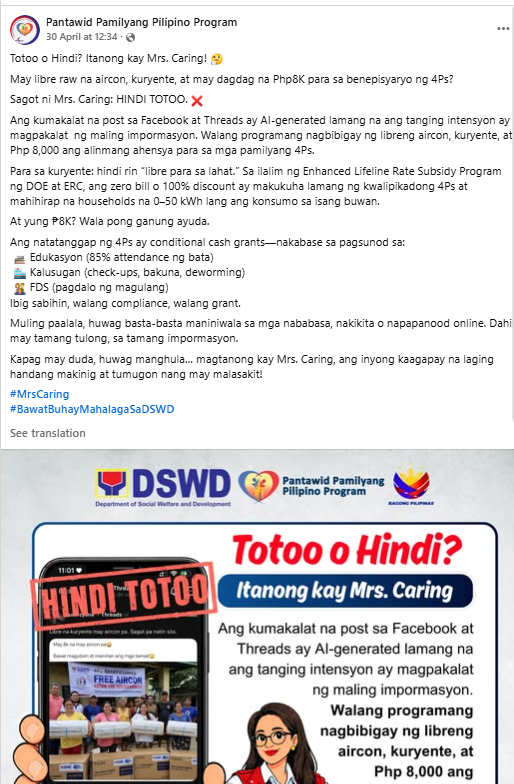
The country’s social welfare agency also issued a statement on Facebook on April 30, rejecting the claim and saying it is “not true” and intended only to “propagate wrong information.” Social welfare agency statement on Facebook
- https://www.facebook.com/photo?fbid=1373756198132587&set=a.665386155636265
Conclusion
However, the video and image circulating on social media do not actually show beneficiaries receiving any subsidy. A closer analysis of the visuals indicates that the content is AI-generated. In the initial frames of the misrepresented video, a diamond-shaped icon can be seen in the bottom-right corner, which is the watermark associated with Google’s Gemini AI model. The viral video and image are misleading. Multiple inconsistencies and visual cues suggest that the content is likely AI-generated, and the claim that low-income households are receiving free electricity and air conditioners is false.

Overview:
‘Kia Connect’ is the application that is used to connect ‘Kia’ cars which allows the user control various parameters of the vehicle through the application on his/her smartphone. The vulnerabilities found in most Kias built after 2013 with but little exception. Most of the risks are derived from a flawed API that deals with dealer relations and vehicle coordination.
Technical Breakdown of Exploitation:
- API Exploitation: The attack uses the vulnerabilities in Kia’s dealership network. The researchers also noticed that, for example, the logs generated while impersonating a dealer and registering on the Kia dealer portal would be sufficient for deriving access tokens needed for next steps.
- Accessing Vehicle Information: The license plate number allowed the attackers to get the Vehicle Identification Number (VIN) number of their preferred car. This VIN can then be used to look up more information about the car and is an essential number to determine for the shared car.
- Information Retrieval: Having the VIN number in hand, attackers can launch a number of requests to backends to pull more sensitive information about the car owner, including:
- Name
- Email address
- Phone number
- Geographical address
- Modifying Account Access: With this information, attackers could change the accounts settings to make them a second user on the car, thus being hidden from the actual owner of the account.
- Executing Remote Commands: Once again, it was discovered that attackers could remotely execute different commands on the vehicle, which includes:some text
- Unlocking doors
- Starting the engine
- Monitoring the location of the vehicle in terms of position.
- Honking the horn
Technical Execution:
The researchers demonstrated that an attacker could execute a series of four requests to gain control over a Kia vehicle:
- Generate Dealer Token: The attacker sends an HTTP request in order to create a dealer token.
- Retrieve Owner Information: As indicated using the generated token, they make another request to another endpoint that returns the owner’s email address and phone number.
- Modify Access Permissions: The attacker takes advantage of the leaked information (email address and VIN) of the owner to change between users accounts and make himself the second user.
- Execute Commands: As the last one, they can send commands to perform actions on the operated vehicle.
Security Response and Precautionary Measures for Vehicle Owners
- Regular Software Updates: Car owners must make sure their cars receive updates on the recent software updates provided by auto producers.
- Use Strong Passwords: The owners of Kia Connect accounts should develop specific and complex passwords for their accounts and then update them periodically. They should avoid using numbers like the birth dates, vehicle numbers and simple passwords.
- Enable Multi-Factor Authentication: For security, vehicle owners should turn on the use of the secondary authentication when it is available to protect against unauthorized access to an account.
- Limit Personal Information Sharing: Owners of vehicles should be careful with the details that are connected with the account on their car, like the e-mail or telephone number, sharing them on social networks, for example.
- Monitor Account Activity: It is also important to monitor the account activity because of change or access attempts that are unauthorized. In case of any abnormality or anything suspicious felt while using the car, report it to Kia customer support.
- Educate Yourself on Vehicle Security: Being aware of cyber threats that are connected to vehicles and learning about how to safeguard a vehicle from such threats.
- Consider Disabling Remote Features When Not Needed: If remote features are not needed, then it is better to turn them off, and then turn them on again when needed. This can prove to help diminish the attack vector for would-be hackers.
Industry Implications:
The findings from this research underscore broader issues within automotive cybersecurity:
- Web Security Gaps: Most car manufacturers pay more attention to equipment running in automobiles instead of the safety of the websites that the car uses to operate thereby exposing automobiles that are connected very much to risks.
- Continued Risks: Vehicles become increasingly connected to internet technologies. Auto makers will have to carry cyber security measures in their cars in the future.
Conclusion:
The weaknesses found in Kia’s connected car system are a key concern for Automotive security. Since cars need web connections for core services, suppliers also face the problem of risks and need to create effective safeguards. Kia took immediate actions to tighten the safety after disclosure; however, new threats will emerge as this is a dynamic domain involving connected technology. With growing awareness of these risks, it is now important for car makers not only to put in proper security measures but also to maintain customer communication on how it safeguards their information and cars against cyber dangers. That being an incredibly rapid approach to advancements in automotive technology, the key to its safety is in our capacity to shield it from ever-present cyber threats.
Reference:
- https://timesofindia.indiatimes.com/auto/cars/hackers-could-unlock-your-kia-car-with-just-a-license-plate-is-yours-safe/articleshow/113837543.cms
- https://www.thedrive.com/news/hackers-found-millions-of-kias-could-be-tracked-controlled-with-just-a-plate-number
- https://www.securityweek.com/millions-of-kia-cars-were-vulnerable-to-remote-hacking-researchers/
- https://news24online.com/auto/kia-vehicles-hack-connected-car-cybersecurity-threat/346248/
- https://www.malwarebytes.com/blog/news/2024/09/millions-of-kia-vehicles-were-vulnerable-to-remote-attacks-with-just-a-license-plate-number
- https://informationsecuritybuzz.com/kia-vulnerability-enables-remote-acces/
- https://samcurry.net/hacking-kia

Data has become a critical asset for the advancement of a nation’s economic, social, and technological development. India’s emergence as a global digital economy hub makes it necessary to create a robust framework that addresses the challenges and opportunities of digital transformation. The Indian government introduced the Draft National Data Governance Framework Policy in 2022, aiming to create a comprehensive data handling and governance framework. This policy draft addresses key challenges in data management, privacy, and digital economy growth. As per the recent media reports, the Draft National Data Governance Policy so prepared is under the finalisation stage, the government specified in its implementation document for the Budget 2023-24 announcement. The policy also aims to address the country's AI adoption and the issue of lack of datasets by providing widespread access to anonymized data.
Background and Need for the Policy
India has a robust digital economy with its adoption of the Digital India Initiative, Aadhaar digital identification, UPI for seamless payments and many more. In India, 751.5 million people connect to the internet, and is home to 462.0 million social media users in January 2024, equivalent to 32.2% of its total population (Data Reportal 2024). This has brought challenges including data privacy concerns, cybersecurity threats, digital exclusion, and a need for better regulation frameworks. To overcome them, the Draft National Data Governance Policy has been designed to provide institutional frameworks for data rules, standards, guidelines, and protocols for the sharing of non-personal data sets in a manner that ensures privacy, security, and trust so that they remain secure, transparent, and accountable.
Objectives omphasizesf the Framework
The objective of the Framework Policy is to accelerate Digital Governance in India. The framework will standardize data management and security standards across the Government. It will promote transparency, accountability, and ownership in Non-Personal data and dataset access and build a platform to receive and process data requests. It will also set quality standards and promote the expansion of the datasets program and overall non-personal ecosystem. Further, it aims to build India’s digital government goals and capacity, knowledge, and competency in Government departments and entities. All this would be done while ensuring greater citizen awareness, participation, and engagement.
Key Provisions of the Draft Policy
The Draft Framework Policy aims to establish a cohesive digital governance ecosystem in India that balances the need for data utilization with protecting citizens' privacy rights. It sets up an institutional framework of the "India Data Management Office (IDMO) set up under the Digital India Corporation (DIC) which will be responsible for developing rules, standards, and guidelines under this Policy.
The key provisions of the framework policy include:
- Promoting interoperability among government digital platforms, ensuring data privacy through data anonymization and security, and enhancing citizen access to government services through digital means.
- The policy e the creation of unified digital IDs, a standardisation in digital processes, and data-sharing guidelines across ministries to improve efficiency.
- It also focuses on building digital infrastructure, such as cloud services and data centres in order to support e-governance initiatives.
- Furthermore, it encourages public-private partnerships and sets guidelines for accountability and transparency in digital governance.
Implications and Concerns of the Framework
- The policy potentially impacts data sharing in India as it mentions data anonymization. The scale of data that would need to be anonymised in India is at a very large scale and it could become a potential challenge to engage in.
- Data localization and cross-border transfers have raised concerns among global tech companies and trade partners. They argue that such requirements could increase operational costs and hinder cross-border data flows. Striking a balance between protecting national interests and facilitating business operations remains a critical challenge.
- Another challenge associated with the policy is over-data centralization under the IDMO and the potential risks of government overreach in data access.
Key Takeaways and Recommendations
The GDPR in the European Union and the Digital Personal Data Protection Act passed in 2023 in India and many others are the data privacy laws in force in different countries. The policy needs to be aligned with the DPDP Act, 2023 and be updated as per the recent developments. It further needs to maintain transparency over the sharing of data and a user’s control. The policy needs engagement with industry experts, privacy advocates, and civil society to ensure a balance of innovation with privacy and security.
Conclusion
The Draft National Data Governance Framework Policy of 2022 represents a significant stage in shaping India's digital future. It ensures the evolution of data governance evolves alongside technological advancements. The framework policy seeks to foster a robust digital ecosystem that benefits citizens, businesses, and the government alike by focusing on the essentials of data privacy, transparency, and security. However, achieving this vision requires addressing concerns like data centralisation, cross-border data flows, and maintaining alignment with global privacy standards. Continued engagement with stakeholders and necessary updates to the draft policy will be crucial to its success in balancing innovation with user rights and data integrity. The final version of the policy is expected to be released soon.
References
- https://meity.gov.in/writereaddata/files/National-Data-Governance-Framework-Policy.pdf
- https://datareportal.com/?utm_source=DataReportal&utm_medium=Country_Article_Hyperlink&utm_campaign=Digital_2024&utm_term=India&utm_content=Home_Page_Link
- https://www.imf.org/en/Publications/fandd/issues/2023/03/data-by-people-for-people-tiwari-packer-matthan
- https://inc42.com/buzz/draft-national-data-governance-policy-under-finalisation-centre/
- https://legal.economictimes.indiatimes.com/news/industry/government-unveiled-national-data-governance-policy-in-budget-2023/97680515
