
#FactCheck-Viral Video of 'Melted' Traffic Signal in Europe Shared with False Heatwave Claim
Executive Summary
A video showing a completely melted traffic signal is going viral on social media. Users sharing the clip claim that an unprecedented and historic heatwave in European countries like Italy, Spain, France, and Germany has become so severe that modern infrastructure—including traffic lights—is literally melting under the sun However, factual research by the CyberPeace Research Wing reveals that this claim is false. The traffic signal did not melt due to weather conditions; it was damaged by a nearby car fire in Italy.
The Claim
On June 30, 2026, an Instagram user named 'khabribhaiyaa' shared the video with a caption stating:"Many European countries are currently in the grip of an unprecedented and historic heatwave. Temperatures in countries like Italy and Germany have neared 40 degree forcing authorities to issue red alerts. The situation is so bad that modern infrastructure is buckling under this deadly heat. Images and reports from the streets are shocking; traffic lights are melting and dripping due to the extreme heat. Not only this, but paved roads and highways are warping due to excessive temperatures, bringing traffic to a standstill. Additionally, railway tracks and other critical infrastructure are suffering heavy damage."
https://www.instagram.com/reels/DaMpGhjG7h4
https://perma.cc/STD7-75S9?type=standard
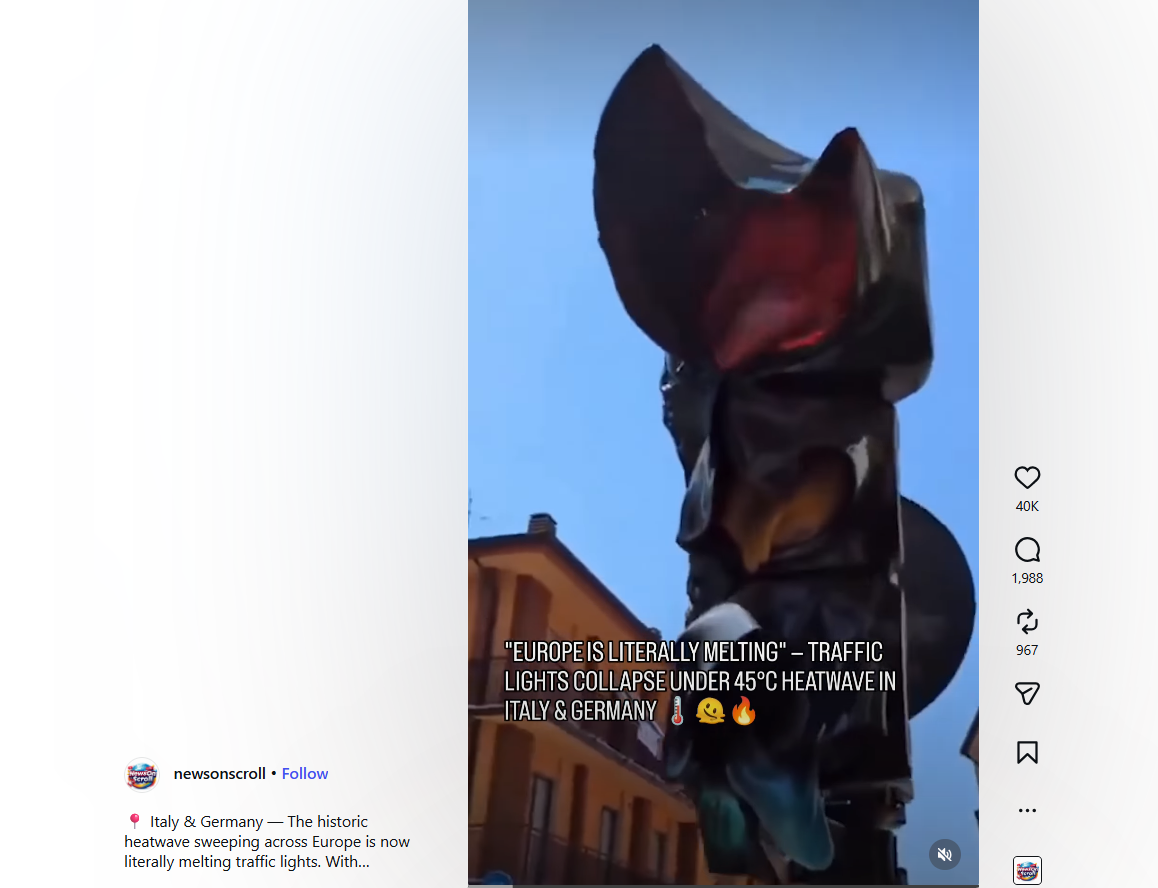
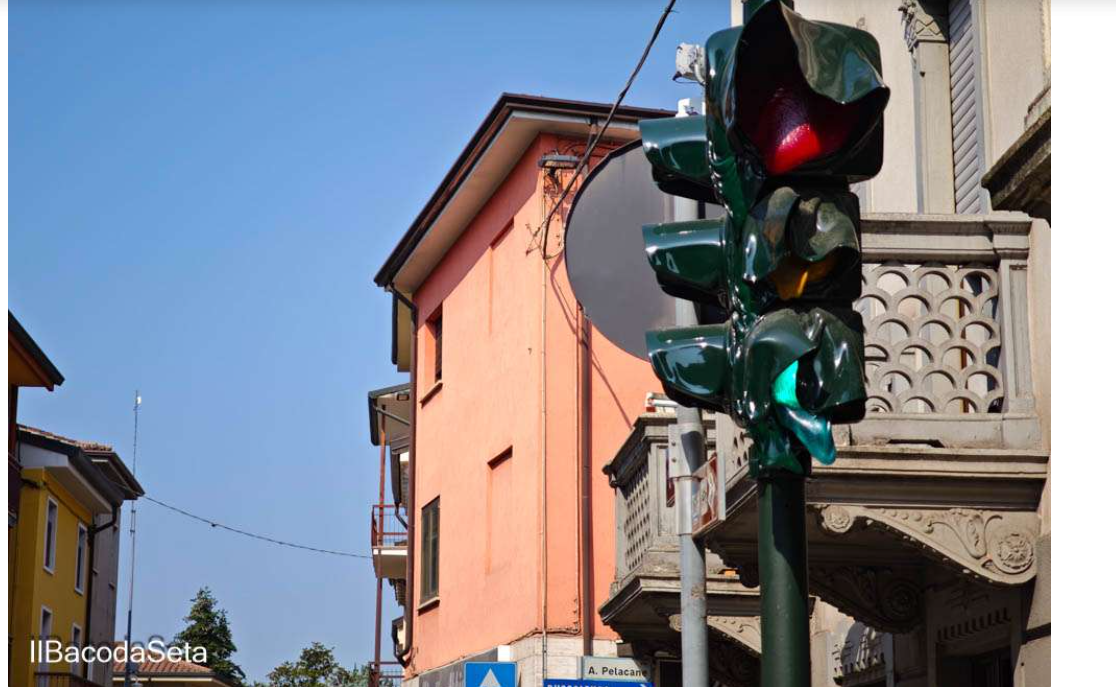
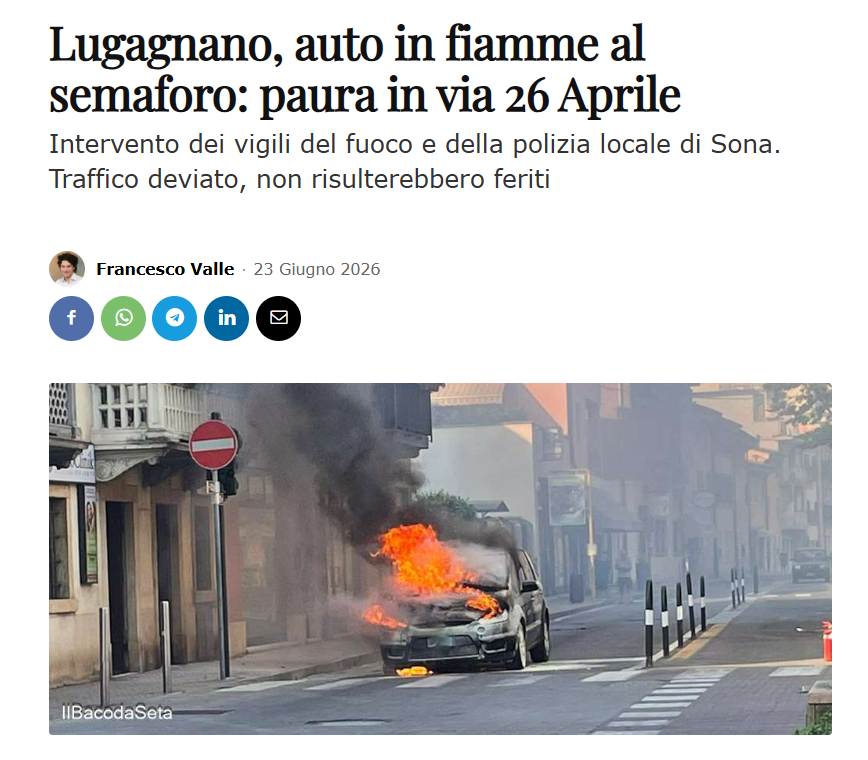
To verify the viral claim, we extracted keyframes from the video and ran a Google Lens search. This led us to a report published on June 28, 2026, by the Italian website 'ilbacodaseta'. The building structure visible in the background of the website's featured photo directly matched the backdrop of the viral video.
https://www.ilbacodaseta.org/lugagnano-auto-in-fiamme-al-semaforo-paura-in-via-26-aprile/#google_vignette
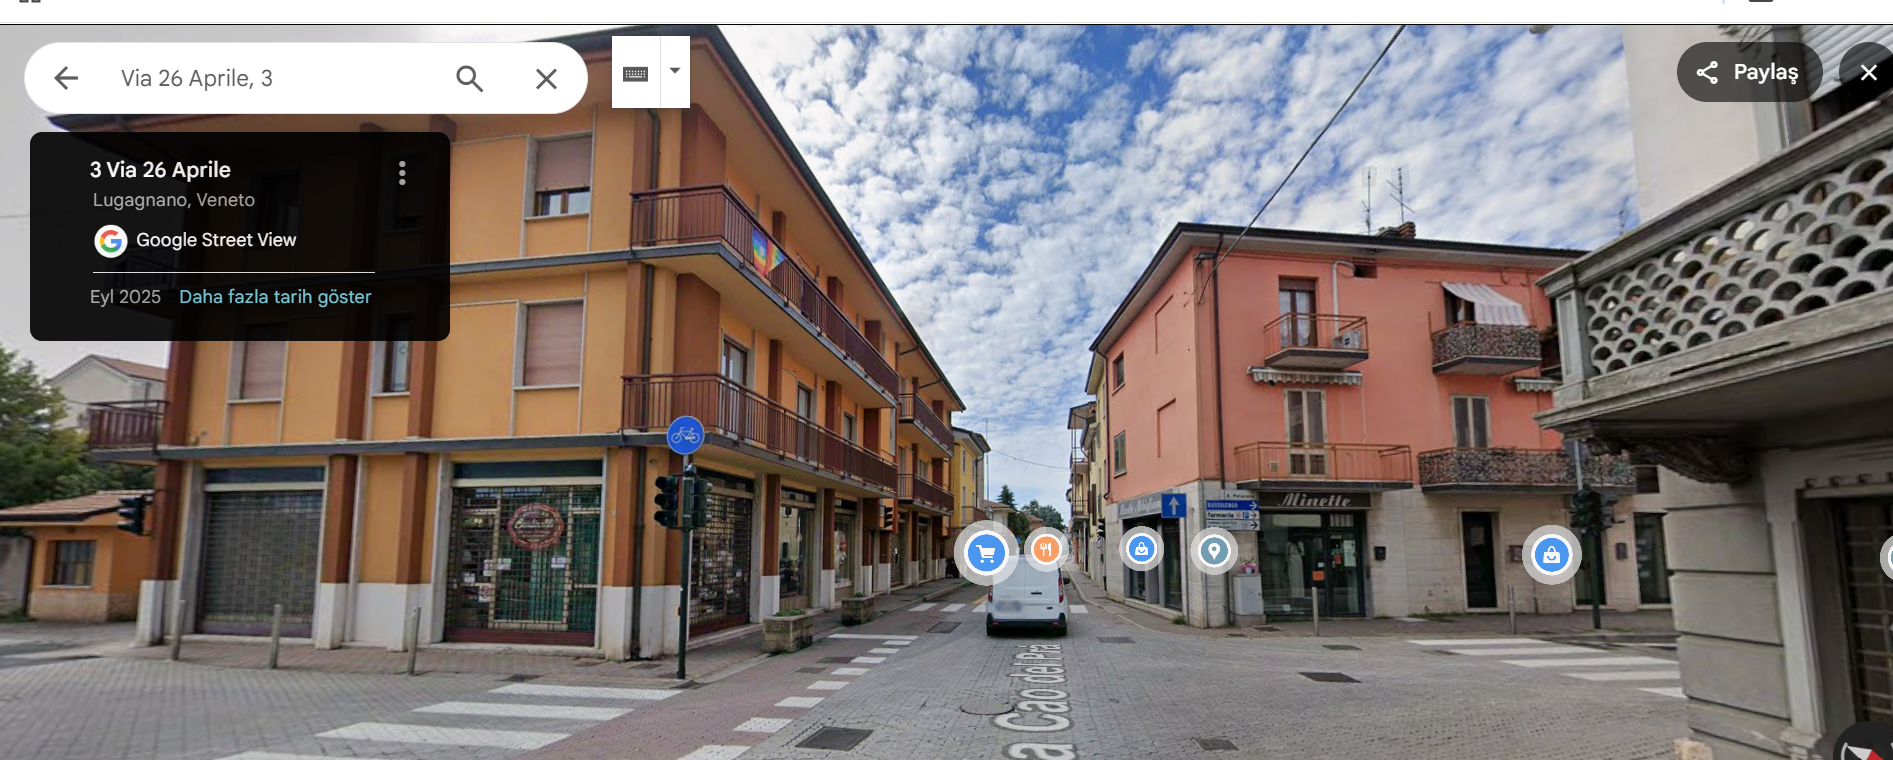
Furthermore, we cross-referenced the spot on Google Maps, confirming that the location perfectly matches the visuals seen in the viral clip.
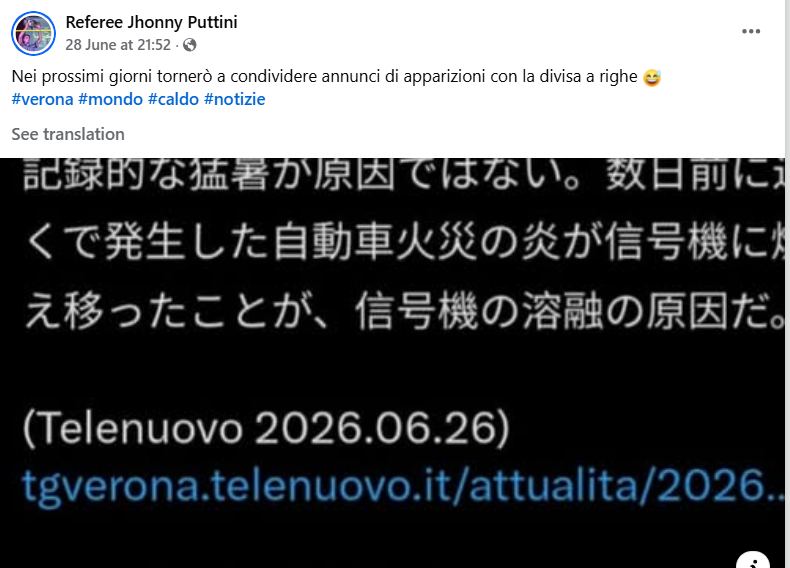
A report by 'tgverona' regarding the same car accident was also shared on Facebook by wrestling referee Johnny Puttini, further verifying that the damage was the result of an accidental fire, not atmospheric heatwaves.
Conclusion
The claim that European heatwaves are melting traffic lights is False. The viral video shows a traffic signal in Lugagnano, Italy, that melted in June 2026 due to a car fire right beneath it. It has nothing to do with the summer temperature or climate conditions.

Related Blogs
Introduction
Due to the rapid growth of high-capability AI systems around the world, growing concerns regarding safety, accountability, and governance have arisen throughout the world; thus, California has responded by passing the Transparency in Frontier Artificial Intelligence Act (TFAIA), the first state statute focused on "frontier" (highly capable) AI models. This statute is unique in that it does not only target harms caused by AI models in the form of consumer protection as compared to the majority of state statutes; rather, this statute addresses the catastrophic and systemic risks to society associated with large-scale AI systems. As California is a global technology leader, the TFAIA is positioned to have a significant impact on both domestic regulation and the evolution of international legal frameworks for AI technology (and as such has the potential to influence corporate compliance practices and the establishment of global norms related to the use of AI).
Understanding the Transparency in Frontier Artificial Intelligence Act
The Transparency in Frontier Artificial Intelligence Act provides a specific regulatory process for companies that create sophisticated AI systems with societal, economic, or national security implications. Covered developers are required to publish an extensive safety and transparency policy that details how they navigate risk throughout the artificial intelligence lifecycle. The act requires developers to notify the government of any significant incidents or failures with their deployed frontier models on a timely basis.
A significant aspect of the TFAIA is that it establishes the concept of "process transparency", which does not explicitly control how AI developers create their models, but rather holds them accountable for their internal safety governance by mandating that they develop Documented safety frameworks that outline risk assessment, mitigation, and monitoring processes. The act allows developers to protect their trade secrets, patents, and national defense concerns by providing them with limited opportunities for exemption and/or redaction of their documents so that they can maintain a balance between data openness and safeguarding sensitive information..
Extraterritorial Impact on Global AI Developers
While the Act is a state law, its implementation has far-reaching effects. Many of the largest AI companies have facilities, research labs or customers in California. Therefore, to be compliant with the TFAIA, these companies are required to do so commercially. The ability to develop a unified compliance model across regions enables companies to avoid developing duplicate compliance models.
This same pattern has occurred in other regulatory areas, like data protection regulations; where a region's regulations effectively became global compliance benchmarks for that regulatory area. The TFAIA could similarly serve as a global standard for transparency in frontier AI and shape how companies build their governance structure globally even if they don't have explicit regulations in the regions where they operate.
Influence on International AI Regulatory Models
The TFAIA offers a unique perspective on global discussions about regulating AI. In contrast to other legislation which defines different levels of risk depending on the type of AI, the TFAIA targets specifically high-impact or emerging technologies. Other nations may see value in this model of tiered regulations based on capability and apply it for their own regulation of AI, with the strictest obligations placed on those with the most critical potential harm.
The TFAIA may serve as a guide for international public policy makers by showing how they can reference existing standards and best practices in developing regulations, thus improving interoperability and potentially lessening regulatory barriers to cross-border AI innovations.
Corporate Governance, Compliance Costs, and Competition
From an industry perspective, the Act revolutionizes the way companies govern themselves. Developers are now required to create thorough risk assessments, red-teaming exercises, incident response protocols, and have board oversight for AI safety and regulation. The number of people involved in this process increases accountability but at the same time the increases will create a burden of cost for all involved.
The burden of compliance will be easier for large tech companies than for smaller or start-ups, and thus large tech companies may solidify their position of dominance over the development of frontier AI. Smaller and newer developers may be blocked from entering the market unless some form of proportional or scaled compliance mechanism for where they operate emerges. These developments certainly raise issues surrounding innovation policy and competition law at a global scale that will need to be addressed by regulators in conjunction with AI safety concerns.
Transparency, Public Trust, and Accountability
The TFAIA bolsters the capability of citizens, researchers and journalists to oversee the development and the use of artificial intelligence (AI) through its requirement for public disclosure of the safety framework of AI systems. The disclosures will allow citizens, researchers and journalists to critically evaluate corporate claims of responsible AI development. Over time, this evaluation could increase trust in publically regulated AI systems and would expose businesses that exhibit a poor risk management process.
However, how useful this transparency is depends on the quality and comparability of the information being disclosed. Many current disclosures are either too vague or too complex, thus limiting the ability to conduct meaningful oversight. There should be a push for clearer guidance and/or the establishment of standardised disclosure forms for the purposes of public accountability (i.e., citizens) and uniformity between countries.
Conclusion
The Transparency in Frontier Artificial Intelligence Act is a transformative development in the regulation of Artificial Intelligence Technology, specifically, a whole new risk profile of this new generation of AI / (Advanced High-Powered) Technologies such as Autonomous Vehicles. This new California law will create global impact because it Be will change how technology companies operate, create regulatory frameworks and develop standards to govern/oversee the use of Autonomous Vehicles. The Act creates a “transparent” means for regulating (or governing) Autonomous Vehicles as opposed to relying solely on “technical” means for these systems. As other regions experience similar challenges that US Government is facing with respect to this new generation of AI (written laws), California's approach will likely be used as an example for how AI laws are written in the future and develop a more unified and responsible international AI regulatory framework.
References
- https://www.whitecase.com/insight-alert/california-enacts-landmark-ai-transparency-law-transparency-frontier-artificial
- https://www.gov.ca.gov/2025/09/29/governor-newsom-signs-sb-53-advancing-californias-world-leading-artificial-intelligence-industry/
- https://www.mofo.com/resources/insights/251001-california-enacts-ai-safety-transparency-regulation-tfaia-sb-53
- https://www.dlapiper.com/en/insights/publications/2025/10/california-law-mandates-increased-developer-transparency-for-large-ai-models

Introduction
Significantly, in March 2023, the Prevention of Money Laundering Act, 2002's regulations placed Virtual Digital Asset Service Providers functioning located under the purview of the Anti Money Laundering/Counter Financing of Terrorism (AML-CFT) scheme. An important step toward controlling VDA SP operations and guaranteeing adherence to Anti-Money Laundering and Combating the Financing of Terrorism (AML-CFT) regulations.
The significance of AML-CFT procedures
The AML-CFT framework's incorporation of Virtual Digital Asset Service Providers (VDA SPs) is essential for protecting the banking industry from illegal activities including the laundering of funds and counter-financing of terrorist attacks. These regulations become more crucial as the market for digital assets develops and becomes more well-known.
The practice of money laundering is hiding the source of the sum received illegally, thus it's critical to have strict policies in place to track down and stop these kinds of operations. Furthermore, funding for terrorism is a serious danger to international safety, hence stopping the flow of money to terrorist companies is a top concern for global officials.
The goal of policymakers' move to include VDA SPs in the AML-CFT architecture is to set up control and surveillance procedures that will guarantee these organisations' open and honest operations. This involves tracking transactions, flagging questionable activity, and conducting extensive customer investigations. Incorporating such procedures not only reduces the potential for financial crimes but also builds confidence and trust in the electronic asset market.
It is important to see the significance of AML-CFT procedures and the changes in the legal framework to reflect the evolving characteristics of digital currencies. These procedures are essential to preserving the reliability and safety of the wider banking system.
Notifications of Compliance Show Cause
Under Section 13 of the PMLA Act 2002, FIU IND sent adherence Show Cause Notices to nine offshore Virtual Digital Asset Service Providers (VDA SPs) as part of its dedication to upholding compliance with regulations. This affirmative step requires organisations to be scrutinised and attempted to bring them under inspection.
Governmental Response
The Director of FIU IND has addressed the Secretary of the Ministry of Electronics and Information Technology to take further measures due to the disregard of offshore firms. According to the notification, URLs connected to these organisations that operate in India in violation of the PML Act's requirements must be blocked.
Mandatory Registration for VDA SPs
Virtual Digital Asset Service Providers (both onshore and offshore) who perform a range of operations, including the trading of digital goods for monetary currencies, the distribution of digital currency, and the management or preservation of electronic assets, are now obliged to register with FIU.
Range of Statutory Responsibilities
In accordance with the PML Act, VDA SPs are subject to several requirements, including documentation, disclosure, and other duties. One of their responsibilities is to register with the FIU IND. The primary focus is on guaranteeing that VDA SPs comply with AML-CFT protocols, hence enhancing the general reliability of the banking industry.
Difficulties with Offshore Compliance
There are many obstacles in guaranteeing that offshore organisations comply with Anti Money Laundering/Counter Financing of Terrorism (AML-CFT), chief amongst them being their unwillingness to undergo registration. Some overseas Virtual Digital Asset Service Providers (VDA SPs) have been reluctant to comply with the existing rules and regulations, even though they cater to a significant number of Indian users. There are several reasons for this hesitation, such as worries about heightened monitoring, the expense of compliance, and the apparent complexity of governmental processes. Regulatory organisations have taken steps to close the discrepancy between offshore businesses' real activities and the regulations they must follow. In addition to maintaining the trustworthiness of the economic system, resolving the issues with offshore adherence is essential for promoting confidence and openness in the market for electronic assets.
Conclusion
FIU IND has demonstrated its dedication to creating an effective regulatory framework for Virtual Digital Asset Service Providers through its recent measures. India hopes to fortify its countermeasures against money laundering and safeguard the financial well-being of its users by expanding the AML-CFT legislation to offshore firms. The continuous efforts to restrict the URLs of non-compliant companies show a proactive approach to stopping illicit activity and fostering a safe and law-abiding virtual asset ecosystem. The safety and soundness of the banking sector will be crucially maintained by laws and regulations as the digital world develops.
References
- https://pib.gov.in/PressReleasePage.aspx?PRID=1991372
- https://www.thehindubusinessline.com/books/reviews/business-economy/fiu-ind-issues-compliance-showcause-notices-to-nine-offshore-vda-sps/article67684613.ece
- https://business.outlookindia.com/news/fiu-issues-notice-to-9-offshore-crypto-platforms-writes-to-meity-for-blocking-of-urls

Introduction
Apple launched Passkeys with iOS 16 as a more authentic and secure mechanism. It is safer than passwords, and it is more efficient in comparison to passwords. Apple users using iOS 16 passkeys features should enable two-factor authentication. The passkeys are an unchallenging mechanism than the passwords for the passkeys. The user just has to open the apps and websites, and then the biometric sensor automatically recognises the face and fingerprints. There can be a PIN and pattern used to log instead of passwords. The passkeys add an extra coating of protection to the user’s systems against cyber threats like phishing attacks by SMS and one-time password-based. In a report 9 to 5mac, there is confirmation that 95% of users are using passkeys. Also, with the passkeys, users’ experience will be better, and it is a more security-proof mechanism. The passwords were weak, reused credentials and credentials leaked, and the chances of phishing attacks were real.
What are passkeys?
Passkey is a digital key linked to users’ accounts and websites or applications. Passkeys allow the user to log into any application and website without entering passwords, usernames, or other details. The aim of this new feature is to replace the old long pattern of entering passwords for going through any websites and applications.
The passkeys are developed by Microsoft, Apple, and Google together, and it is also called FIDO Authentication (Fast identity online). It eliminates the need to remember passwords and the need for typing. So, the passkeys work as they replace the password with a unique digital key, which is tied to the account then, the key is stored in the device itself, and it is end-to-end encrypted. The passkeys will always be on the sites on which users specifically created them. the passkeys use the technology of cryptography for more security purposes. And the passkeys guarantee against the phish.
And since the passkeys follow FIDO standards so, this also can be used for third-party nonapple devices as the third-party device generate a QR code that enables the iOS user to scan that to log in. It will recognise the face of the person for authentication and then asks for permission on another device to deny or allow.
How are passkeys more secure than passwords?
The passkeys follow the public key cryptographic protocols that support the security keys, and they work against phishing and other cyber threats. It is more secure than SMS and apps based on one-time passwords. And another type of multi-factor authentication.
Why are passwords insecure?
The users create passwords easily, and it is wondering if they are secure. The very important passwords are short and easy to crack as they generally relate to the user’s personal information or popular words. One password is reused by the user to the different accounts, and then, in this case, hacking one account gives access to all accounts to the hackers. The problem is that passwords have inherent flaws, like they could be easily stolen.
Are passkeys about to become obligatory?
Many websites restrict the type of passwords, as some websites ask for mixtures of numbers and symbols, and many websites ask for two-factor authentication. There is no surety about the obligation of passkeys widespread as it is still a new concept and it will take time, so it is going to be optional for a while.
- There was a case of a Heartland payment system data breach, and Heartland was handling over 100 million monthly credit card transactions for 175,000 retailers at the time of the incident. Visa and MasterCard detected the hack in January 2009 when they notified Heartland of suspicious transactions. And this happened due to a password breach. The corporation paid an estimated $145 million in settlement for illegal payments. Today, data-driven breaches affect millions of people’s personal information.
- GoDaddy reported a security attack in November that affected the accounts of over a million of its WordPress customers. The attacker acquired unauthorised access to GoDaddy’s Managed WordPress hosting environment by hacking into the provisioning system in the company’s legacy Managed WordPress code.
Conclusion
The use of strong and unique passwords is an essential requirement to safeguard information and data from cyberattacks, but still, passwords have its own disadvantages. And by the replacement of passwords, a passkey, a digital key that ensures proper safety and there is security against cyberattacks and cybercrimes through passkey. There are cases above-mentioned that happened due to the password’s weaker security. And in this technology world, there is a need for something for protection and prevention from cybercrimes, and the world dumps passwords and adopts passkeys.
References
- https://www.cnet.com/tech/mobile/switch-to-passkeys-more-secure-than-passwords-on-ios-16-iphone-14/
- https://economictimes.indiatimes.com/magazines/panache/google-is-ending-passwords-rolls-out-passkeys-for-easy-log-in-how-to-set-it/articleshow/99988444.cms?from=mdr
- https://security.googleblog.com/2023/05/making-authentication-faster-than-ever.html#:~:text=Because%20they%20are%20based%20on,%2Dfactor%20authentication%20(MFA).
