
#FactCheck-Videos of Thai Army Falsely Shared as Chinese Troops Entering Arunachal Pradesh
Introduction
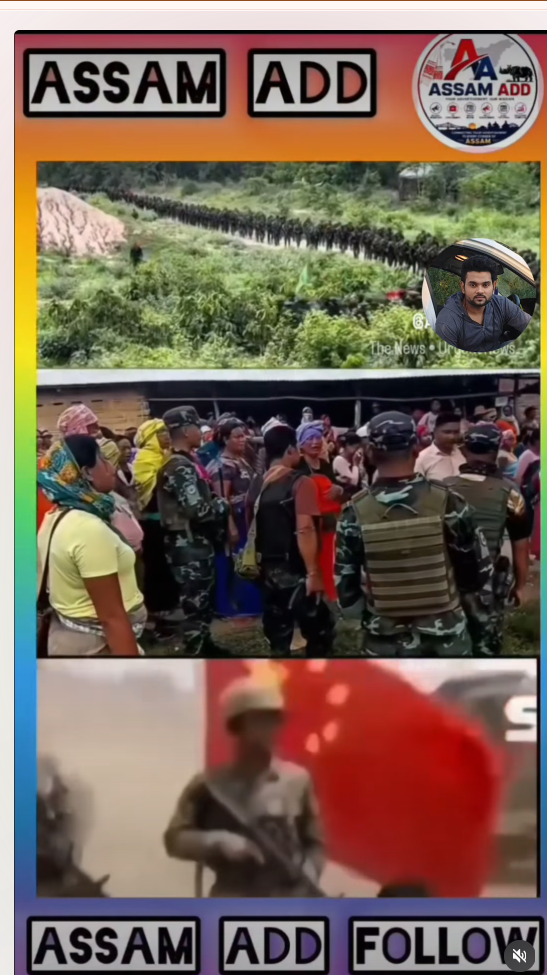
Two videos are being widely circulated on social media with the claim that Chinese troops have entered Arunachal Pradesh, India. The first video shows a large group of soldiers marching in formation, while the second shows armed personnel disembarking from military trucks. Social media users claim that the footage shows Chinese soldiers advancing into Indian territory. CyberPeace Research Wing’s research found the claim to be false. The two viral videos are unrelated to India and actually show Thai Army personnel during military training exercises. Both the Government of India and the Indian Army have also dismissed the claim of any recent Chinese intrusion into Indian territory.
Claim
An Instagram user, "mtkv.ideo," shared the viral videos on July 7, 2026, with the caption,"Chinese army has entered 60 km inside India."
https://www.instagram.com/reels/DaehrgExzUl/
Fact Check
To verify the claim, we extracted several keyframes from the viral videos and conducted a reverse image search using Google Lens.
During the research, we found one of the videos posted on June 16, 2026, on the Facebook page "Liangpha Kha Khaeng."
https://www.facebook.com/reel/992963226961409
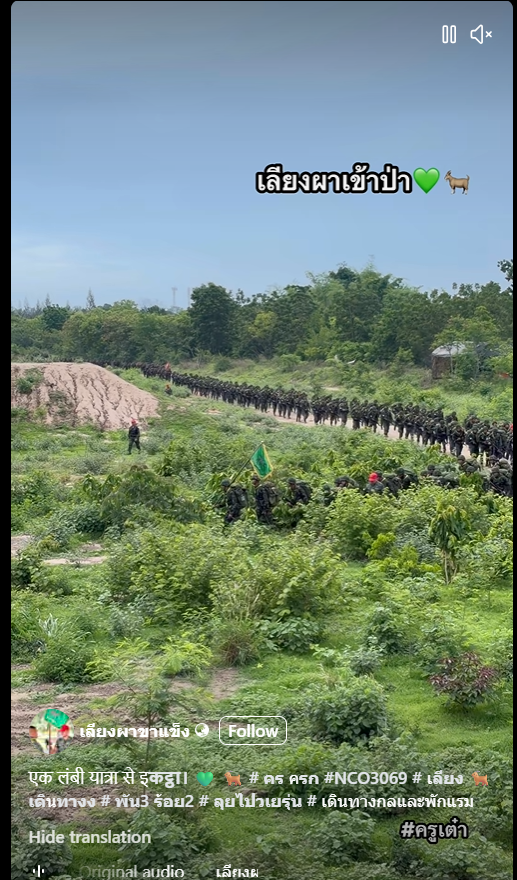
According to the information provided with the post, the video shows a training exercise of Non-Commissioned Officers (NCOs) from the 3rd Battalion, 2nd Regiment of the Royal Thai Army. The page also contains several other posts featuring Thai military drills and training activities. We further reviewed the Facebook page and found multiple training videos featuring the same flag carried by soldiers in the viral footage, confirming that the personnel shown belong to the Thai Army, not the Chinese military.
https://www.facebook.com/profile.php?id=61588894033585&locale=hi_IN

We also found a report published by The Times of India, quoting Union Minister Kiren Rijiju, who dismissed claims of any Chinese intrusion into Arunachal Pradesh. Rijiju clarified that no intrusion had taken place, adding that occasional movement across undemarcated areas occurs because the boundary has not been fully delineated. https://timesofindia.indiatimes.com/india/no-intrusion-transgression-in-absence-of-demarcation-kiran-rijiju/articleshow/132101410.cms

Conclusion
Our research found that the viral claim is false. The videos being shared as evidence of Chinese troops entering Arunachal Pradesh actually show Royal Thai Army personnel participating in military training exercises in Thailand. There is no evidence that the footage is related to India or that it depicts any recent Chinese military intrusion into Indian territory. Government officials have also rejected the viral claim.

Related Blogs

Introduction
With the ever-growing technology where cyber-crimes are increasing, a new cyber-attack is on the rise, but it’s not in your inbox or your computer- it's targeting your phone, especially your smartphone. Cybercriminals are expanding their reach in India, with a new text-messaging fraud targeting individuals. The Indian Computer Emergency Response Team (CERT-In) has warned against "smishing," or SMS phishing.
Understanding Smishing
Smishing is a combination of the terms "SMS" and "phishing." It entails sending false text messages that appear to be from reputable sources such as banks, government organizations, or well-known companies. These communications frequently generate a feeling of urgency in their readers, prompting them to click on harmful links, expose personal information, or conduct financial transactions.
When hackers "phish," they send out phony emails in the hopes of tricking the receiver into clicking on a dangerous link. Smishing is just the use of text messaging rather than email. In essence, these hackers are out to steal your personal information to commit fraud or other cybercrimes. This generally entails stealing money – usually your own, but occasionally also the money of your firm.
The cybercriminals typically use these tactics to lure victims and steal the information.
Malware- The cyber crooks send the smishing URL link that might tick you into downloading malicious software on your phone itself. This SMS malware may appear as legitimate software, deceiving you into putting in sensitive information and transmitting it to crooks.
Malicious website- The URL in the smishing message may direct you to a bogus website that seeks sensitive personal information. Cybercriminals employ custom-made rogue sites meant to seem like legitimate ones, making it simpler to steal your information.
Smishing text messages often appear to be from your bank, asking you to share personal sensitive information, ATM numbers, or account details. Mobile device cybercrime is increasing, as is mobile device usage. Aside from the fact that texting is the most prevalent usage of cell phones, a few additional aspects make this an especially pernicious security issue. Let's go over how smishing attacks operate.
Modus Operandi
The cyber crooks commit the fraud via SMS. As attackers assume an identity that might be of someone trusted, Smishing attackers can use social engineering techniques to sway a victim's decision-making. Three things are causing this deception:
- Trust- Cyber crooks target individuals, by posing to someone from a legitimate individual and organization, this naturally lowers a person’s defense against threats.
- Context- Using a circumstance that might be relevant to targets helps an attacker to create an effective disguise. The message feels personalized, which helps it overcome any assumption that it is spam.
- Emotion- The nature of the SMS is critical; it makes the victim think that is urgent and requires rapid action. Using these tactics, attackers craft communications that compel the receiver to act.
- Typically, attackers want the victim to click on a URL link within the text message, which takes them to a phishing tool that asks them for sensitive information. This phishing tool is frequently in the form of a website or app that also assumes a phony identity.
How does Smishing Spread?
As we have revealed earlier smishing attacks are delivered through both traditional texts. However, SMS phishing attacks primarily appear to be from known sources People are less careful while they are on their phones. Many people believe that their cell phones are more secure than their desktops. However, smartphone security has limits and cannot always guard against smishing directly.
Considering the fact phones are the target While Android smartphones dominate the market and are a perfect target for malware text messages, iOS devices are as vulnerable. Although Apple's iOS mobile technology has a high reputation for security, no mobile operating system can protect you from phishing-style assaults on its own. A false feeling of security, regardless of platform, might leave users especially exposed.
Kinds of smishing attacks
Some common types of smishing attacks that occurred are;
- COVID-19 Smishing: The Better Business Bureau observed an increase in reports of US government impersonators sending text messages requesting consumers to take an obligatory COVID-19 test via a connected website in April 2020. The concept of these smishing assaults may readily develop, as feeding on pandemic concerns is a successful technique of victimizing the public.
- Gift Smishing: Give away, shopping rewards, or any number of other free offers, this kind of smishing includes free services or products, from a reputable or other company. attackers plan in such a way that the offer is for a limited time or is an exclusive offer and the offers are so lucrative that one gets excited and falls into the trap.
CERT Guidelines
CERT-In shared some steps to avoid falling victim to smishing.
- Never click on any suspicious link in SMS/social media charts or posts.
- Use online resources to validate shortened URLs.
- Always check the link before clicking.
- Use updated antivirus and antimalware tools.
- If you receive any suspicious message pretending to be from a bank or institution, immediately contact the bank or institution.
- Use a separate email account for personal online transactions.
- Enforce multi-factor authentication (MFA) for emails and bank accounts.
- Keep your operating system and software updated with the latest patches.
Conclusion
Smishing uses fraudulent mobile text messages to trick people into downloading malware, sharing sensitive data, or paying cybercriminals money. With the latest technological developments, it has become really important to stay vigilant in the digital era not only protecting your computers but safeguarding the devices that fit in the palm of your hand, CERT warning plays a vital role in this. Awareness and best practices play a pivotal role in safeguarding yourself from evolving threats.
Reference
- https://www.ndtv.com/india-news/government-warns-of-smishing-attacks-heres-how-to-stay-safe-4709458
- https://zeenews.india.com/technology/govt-warns-citizens-about-smishing-scam-how-to-protect-against-this-online-threat-2654285.html
- https://www.the420.in/protect-against-smishing-scams-cert-in-advice-online-safety/
Executive Summary
A video featuring the newly appointed Chief of Army Staff (COAS), General Dhiraj Seth, is going viral on social media. The video claims that he made controversial remarks regarding Operation Sindoor and alleged that the previous military leadership hid the bodies of Indian soldiers martyred during the operation. It further claims that Defence Minister Rajnath Singh and Prime Minister Narendra Modi were also kept unaware of the matter. CyberPeace Research Wing research found the claim to be misleading. The research revealed that the viral video was digitally manipulated using artificial intelligence (AI), and the voice heard in the video is not authentic.
Claim
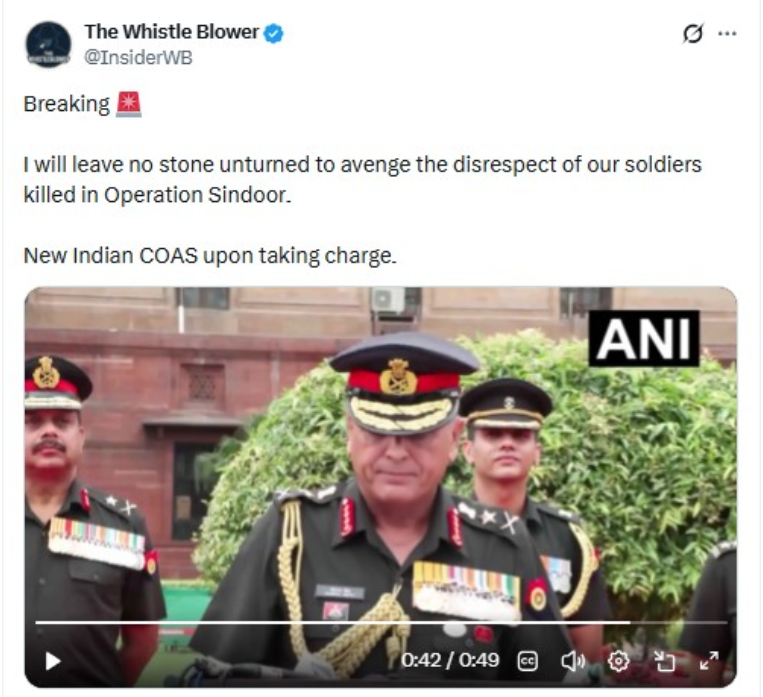
A viral video shared on social media platform X claims that newly appointed Chief of Army Staff (COAS) General Dhiraj Seth said that the bodies of Indian soldiers martyred during Operation Sindoor were hidden and that Defence Minister Rajnath Singh and Prime Minister Narendra Modi were not informed about it. https://archive.ph/oaOgB , https://x.com/InsiderWB/status/2072434480543899826
Fact Check
To verify the viral claim, we searched the internet using relevant keywords including “General Dhiraj Seth statement on Operation Sindoor”, “Operation Sindoor martyrs”, and “dead bodies hidden.” However, we did not find any credible media report stating that Army Chief General Dhiraj Seth made the remarks attributed to him in the viral video. We also checked the official social media handles of the Indian Army, but found no official statement or information supporting the viral claim. During the research, several keyframes from the viral video were extracted and analysed through reverse image search. The search led us to an ANI report published on July 1, 2026, whose watermark is also visible in the viral video. The original footage shows General Dhiraj Seth addressing the public after assuming charge as the Chief of Army Staff. We carefully reviewed General Dhiraj Seth’s entire address but found no mention of hiding the bodies of martyred soldiers or any statement related to the viral claim. The same address was also shared on the official platform of the Indian Army. The video review confirmed that it does not contain any such remarks.
https://www.facebook.com/reel/1592505052458589
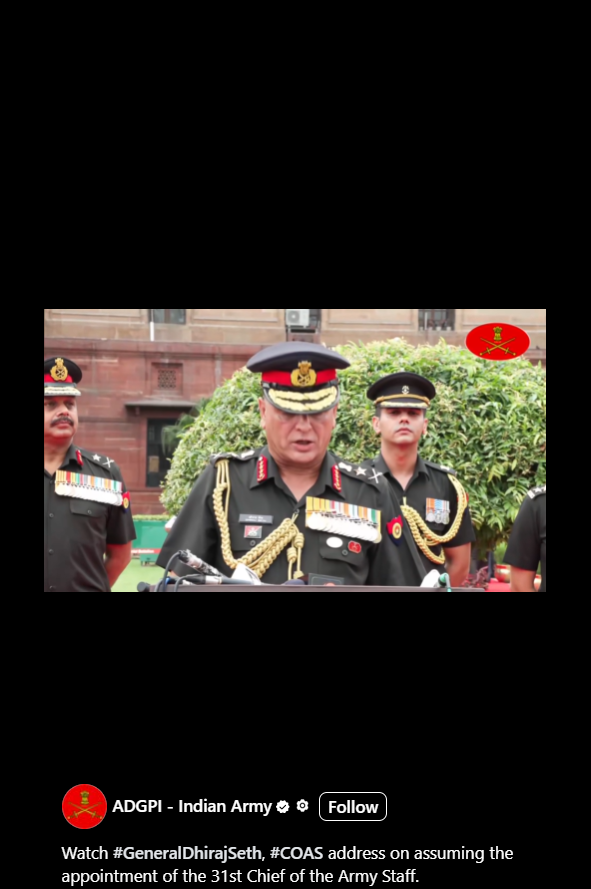
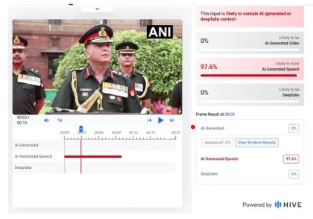
During the analysis, it was also observed that the name tag on General Dhiraj Seth’s uniform appears distorted in several frames. Such inconsistencies are commonly seen in AI-generated or digitally manipulated videos. To verify the authenticity of the video, we analysed it using multiple AI detection tools. The results from all the tools were consistent. Hive Moderation’s analysis indicated a high probability that the viral media contains AI-generated or deepfake content.
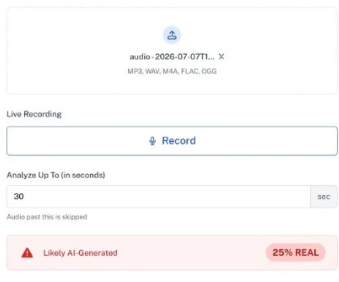
Undetectable AI’s analysis also concluded that the voice heard in the viral video was likely generated using artificial intelligence (AI).
Conclusion
Our research found that the viral video is not authentic. There is no evidence that Chief of Army Staff General Dhiraj Seth ever accused the previous military leadership of concealing the bodies of soldiers martyred during Operation Sindoor. The video has been digitally manipulated, and the claim being circulated on social media is misleading.

Introduction
India is confronting a wake-up call as a recent cyber incident aimed at the aviation sector underscores the fragile nature of digital systems that guide national air travel. The disclosure in Parliament has pushed the conversation on flight safety, signal integrity, and cyber readiness back into urgent focus. In a written response to a Parliamentary question, Civil Aviation Minister Ram Mohan Naidu acknowledged that GPS spoofing, a malicious method employed to alter navigation signals, had been noticed at seven major airports of the country. New Delhi flights had not been affected during the incident, but still, it was an event that again made air travel's safety, GNSS interference, and the overall cyber threat to India's airspace an issue of concern.
The Incident: What Happened?
Initial notices came from Indira Gandhi International Airport in Delhi, where the pilots of the different inbound flights talked about GPS spoofing as the reason for their landing. Spoofing is the process of sending counterfeit GPS signals which mislead the aircraft's navigation systems and may cause a wrong measure of the altitude, the position or the runway alignment. In Delhi, pilots operating under GPS-based landing procedures over Runway 10 experienced errors in their approaches and promptly switched to the alternative procedures without any delay.
The Minister said that apart from Delhi, other airports, viz. Kolkata, Amritsar, Mumbai, Hyderabad, Bengaluru, and Chennai were the 6 airports that recorded similar GNSS interference patterns consisting of both jamming and spoofing. Though no major interruptions or incidents occurred, these occurrences are a sign of a steady and enlarging threat.
Why Is GPS Spoofing So Dangerous?
Satellite navigation and communication systems are the backbone of modern aviation, which is now a matter of great precision. Signal jamming by malicious actors comes with a bunch of risks:
- Diversions and Delays: Pilots may be forced to either give up attempts to land or divert flights, which translates into higher consumption of fuel and more complicated operations due to the case of jamming.
- Threat of Safety Issue: Pilots are trained to deal with such incidents by following the prescribed fallback procedures, but still they depend very much on the GNSS signals that are accurate for safe manoeuvring, especially in low visibility situations.
- Pressure on Old Systems: Indian airports are still in the process of completely converting from ground-based navigation aids to GNSS. Signal disruptions entail the use of older technologies, which results in putting additional pressure on the already overburdened air traffic control systems.
- Opening Up Possibilities for Direct Attacks: Signal jamming can be made a tool for more clever tactics of operation that can include causing confusion during the busy traffic period or performing coordinated attacks to create chaos.
Aviation and Cyber Threats
The disturbances that have been mentioned at the seven airports are not unique. The civil aviation regulators all over the world have already reported an increase in GNSS jamming. The exemplary cases in the Middle East, Eastern Europe, and East Asia have revealed that the safety of airspace has turned into a tactical issue.
Moreover, India's quick adoption of digital technology in the aviation sector could open threat vulnerabilities from state-sponsored groups, hackers. In this instance, the government has not yet announced who was responsible for the spoofing, but the trend points to an adversary with advanced technology.
Government and Regulatory Response
The confirmation from the Civil Aviation Minister underscores a proactive stance by agencies such as:
- Directorate General of Civil Aviation (DGCA)
- Ministry of Civil Aviation
- Airports Authority of India (AAI)
The involved entities are collaborating now to do an inquiry into the cases and set up preventive measures.
The main steps that are taken in response are:
- More thorough observation of GNSS signal anomalies
- More pilot briefings and training on dealing with spoofing situations
- Improving navigation aids to set up a backup
- Working with IT security experts to find out the sources of interference
- Communicating with other global aviation authorities to share the best practices
India, being a significant player in the world aviation market, is not allowed to relax its guard. Cyberattacks on airports show how digital as well as physical security are becoming more and more intertwined.
The Bigger Picture: Protecting Critical Infrastructure
Aviation is a sector that very clearly shows that threats from cyberspace can easily translate into security issues for a nation. The airport system not only becomes more vulnerable to attacks but also the whole aviation industry as the digital ecosystems gain more complex forms together with integrated telecommunications networks, the Internet of Things (IoT)-enabled systems, and cloud-based services.
One of the many threats in the form of GNSS spoofing demonstrates so-called:
- Ransomware attacks on airport systems
- Contamination of air traffic control infrastructure
- Data breaches conducted by insiders
- Passenger data attacks
- Hinderance of airport logistics and baggage systems
What Needs to Happen Next?
India is compelled to embrace a multi-faceted approach in order to manage the intricacies of GNSS interference risk:
- Cybersecurity Measures in Aviation Enforced: New monitoring tools, anomaly detection systems, and instant response plans will be put into service.
- Redundant Technology: The non-GNSS-based navigation system will be expanded to guarantee the continuity of operations in the event of jamming.
- Cyber Drills Across all Sectors: To get pilots, air traffic control personnel, and airport operators ready, the aviation cyber drills will be conducted at the national level.
- Global Cooperation: International organisations will be approached to share the information and standardise the procedures.
- R&D and Innovations: Funding will be directed towards anti-spoofing technology, stronger satellite signals, and the domestic navigation system, like NavIC.
Conclusion
The cyberattack that targeted the seven airports serves as a clear reminder that aviation cybersecurity should not be considered a secondary issue anymore. Even though the quick reaction from the authorities managed to averted any disruptions, the event still shows the vulnerabilities of modern aviation systems. India's air travel infrastructure expansion will be a good time for the country to install its strong cybersecurity frameworks to protect its passengers, maintain the continuity of operations, and secure the airspace of its territory. At CyberPeace, we believe that a coordinated, proactive, and technology-driven approach is no longer an option, it is the new fundamental of aviation security in the digital age.
Reference
