
#FactCheck: Video of Jagannath Rath Yatra in Puri Falsely Shared as Anti-Reservation Protest at Jantar Mantar
Executive Summary
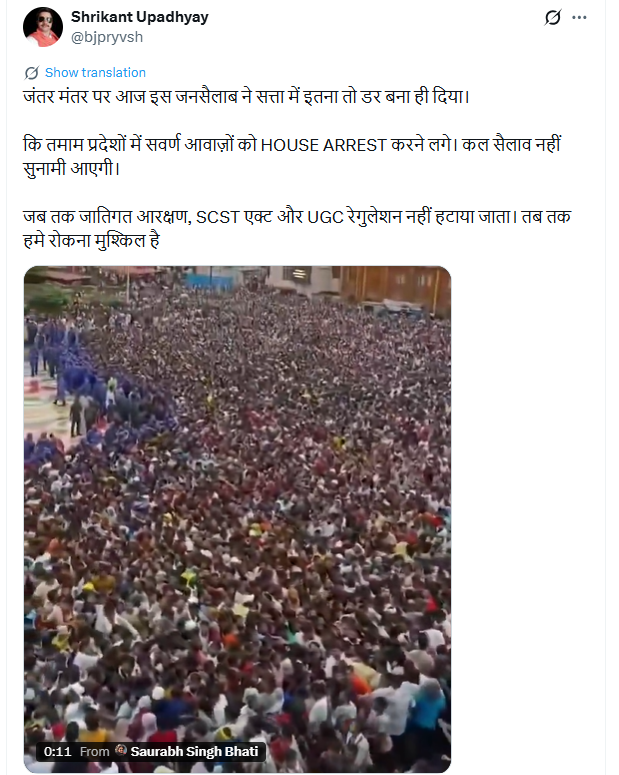
A video showing a massive crowd is being shared on social media with the claim that it shows an anti-reservation protest held at Jantar Mantar. However, a research done by the research wing of the CyberPeace revealed that the video is not from any anti-reservation protest at Jantar Mantar, but from the Jagannath Rath Yatra organized in Puri, Odisha.
Claim:
The video is being shared on X (formerly Twitter) with a viral caption that translates to: “Today, this massive gathering at Jantar Mantar created so much fear in the ruling government that upper-caste voices are being put under HOUSE ARREST across various states. Tomorrow will bring a tsunami, not just a surge. Until caste-based reservation, the SC/ST Act, and UGC regulations are removed, it will be difficult to stop us.”
https://x.com/bjpryvsh/status/2091554860785438887?s=20
Fact Check:
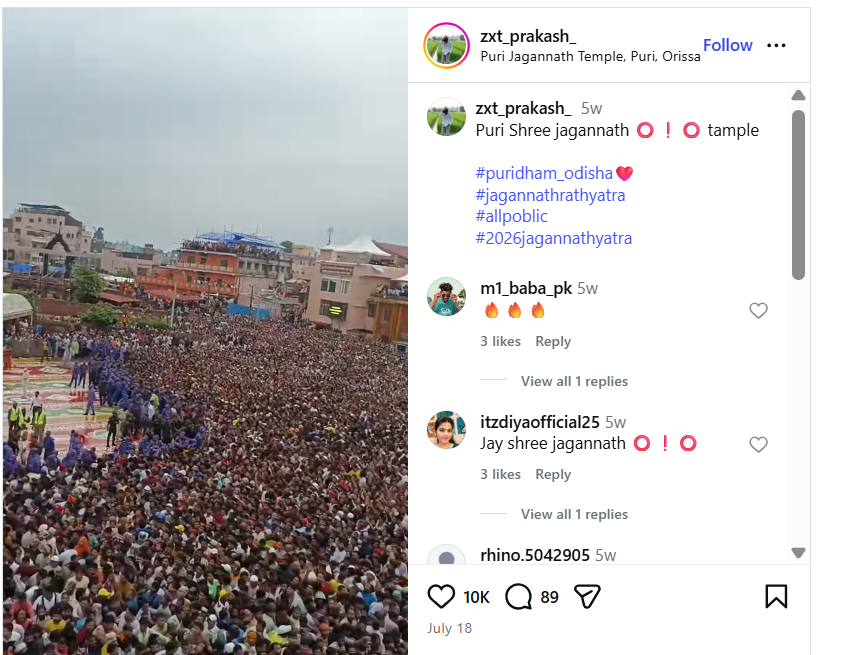
To investigate the viral video, reverse image searches were conducted using keyframes extracted from the clip. This led to an Instagram post uploaded on July 18. The caption accompanying the video clearly identified the footage as being from the Jagannath Rath Yatra in Puri, Odisha.
https://www.instagram.com/p/Da7tF2Etiae/
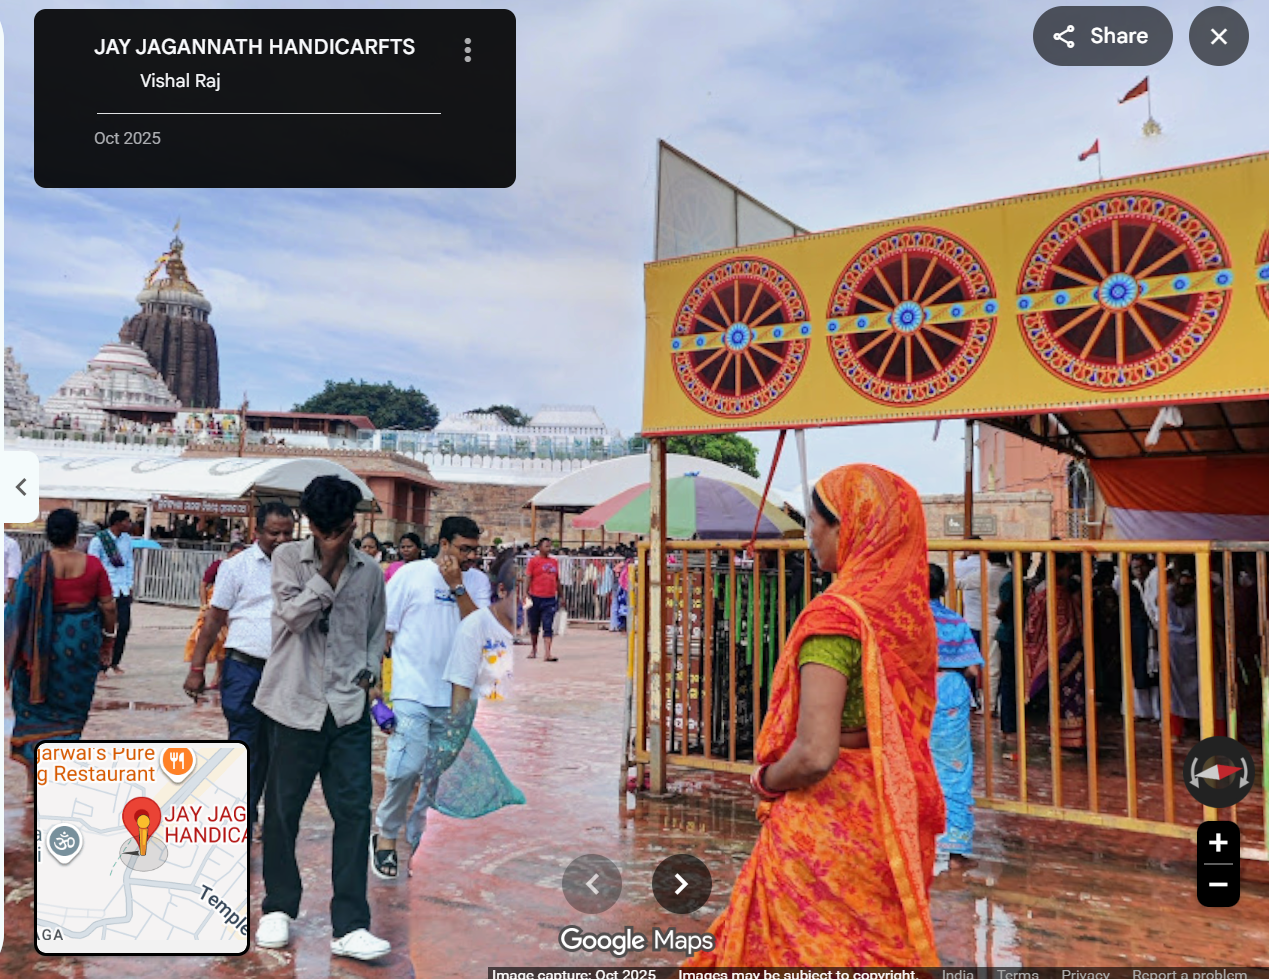
The visuals in the video were matched with the surroundings of the Jagannath Temple in Puri available on Google Maps Street View, confirming beyond doubt that the location in the video is near the Jagannath Temple in Puri.
https://www.google.com/maps/place/JAY+JAGANNATH+HANDICARFTS/@
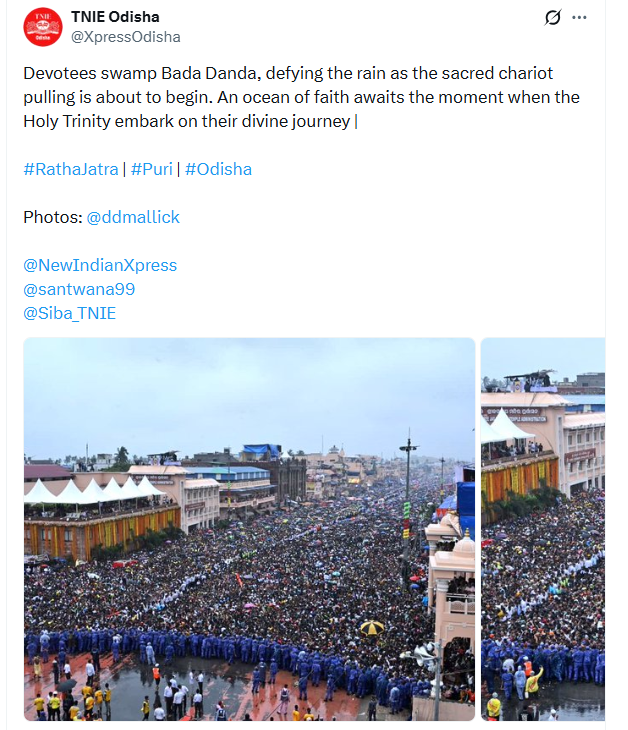
Similar visuals were found in photos uploaded by the X account of The New Indian Express Odisha on July 16, 2026. The imagery in these photographs closely matched the scenes in the viral video, and the caption stated that they were captured during the Jagannath Rath Yatra in Puri.
https://x.com/XpressOdisha/status/2077697637688775015
Conclusion:
Based on the evidence gathered during our research, it is clear that the video being falsely circulated as an anti-reservation protest at Jantar Mantar is actually footage of the Jagannath Rath Yatra in Puri, Odisha.

Related Blogs
Executive Summary
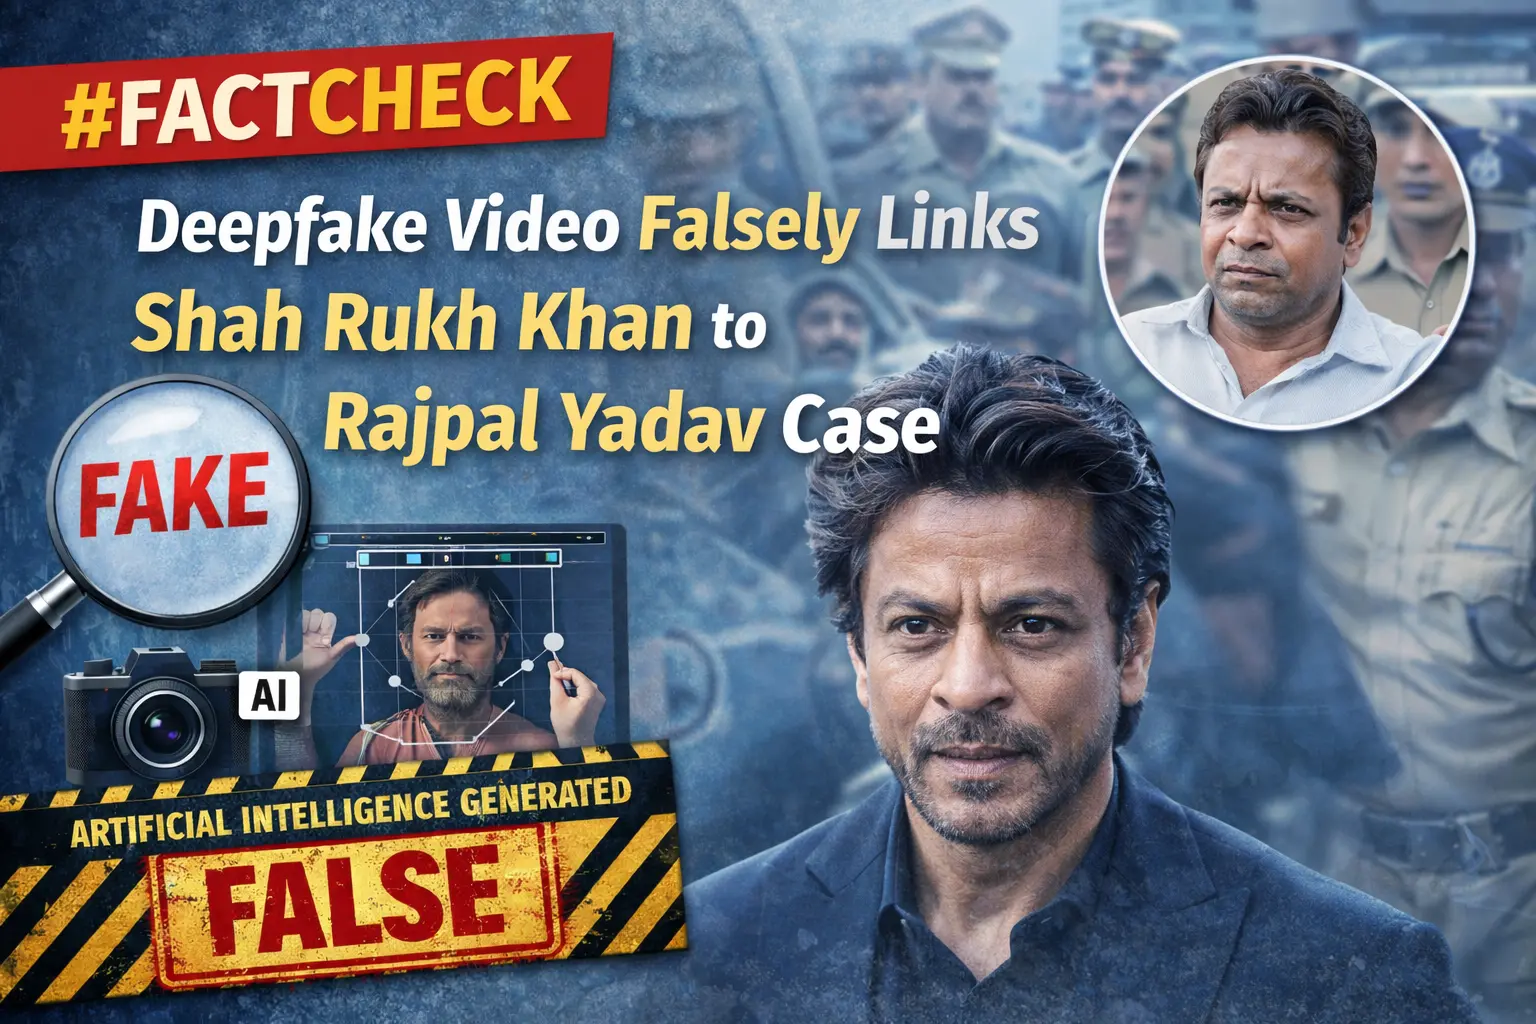
A video featuring popular comedian Rajpal Yadav has recently gone viral on social media, claiming that he is currently lodged in Tihar Jail in connection with a loan default and cheque bounce case. In connection with this, another video showing Bollywood superstar Shah Rukh Khan is being widely shared online. In the viral clip, Khan is purportedly seen saying that he would help Rajpal Yadav get out of jail and also offer him a role in his upcoming film. However, research by the CyberPeace found the viral video to be fake. The clip is a deepfake, in which the audio has been manipulated using artificial intelligence. In the original video, Shah Rukh Khan is speaking about his life and personal experiences. Although several prominent Bollywood personalities have expressed support for Rajpal Yadav, the claims made in the viral video are misleading.
Claim
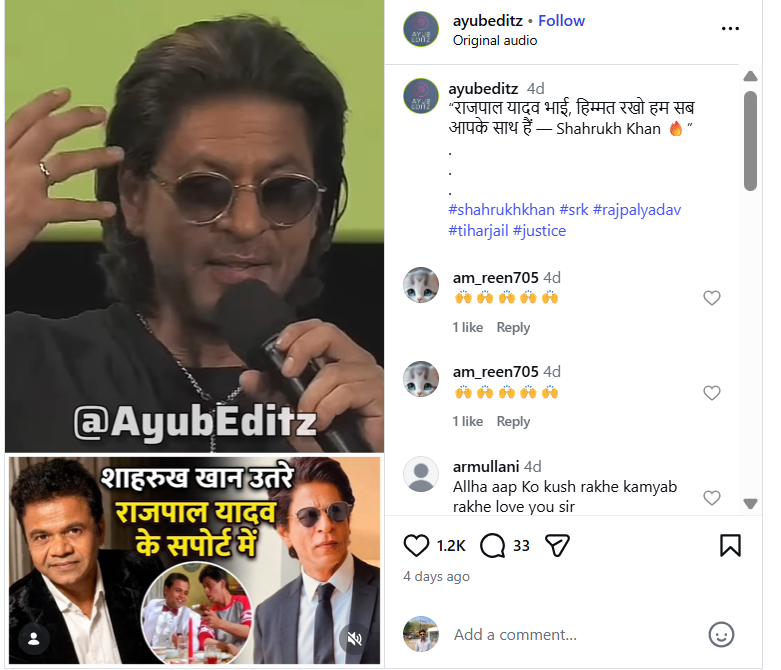
An Instagram user named “ayubeditz” shared the viral video on February 11, 2026, with the caption: “Rajpal Yadav bhai, stay strong, we are all with you — Shah Rukh Khan.” The link to the post and its archived version are provided below.
Fact Check
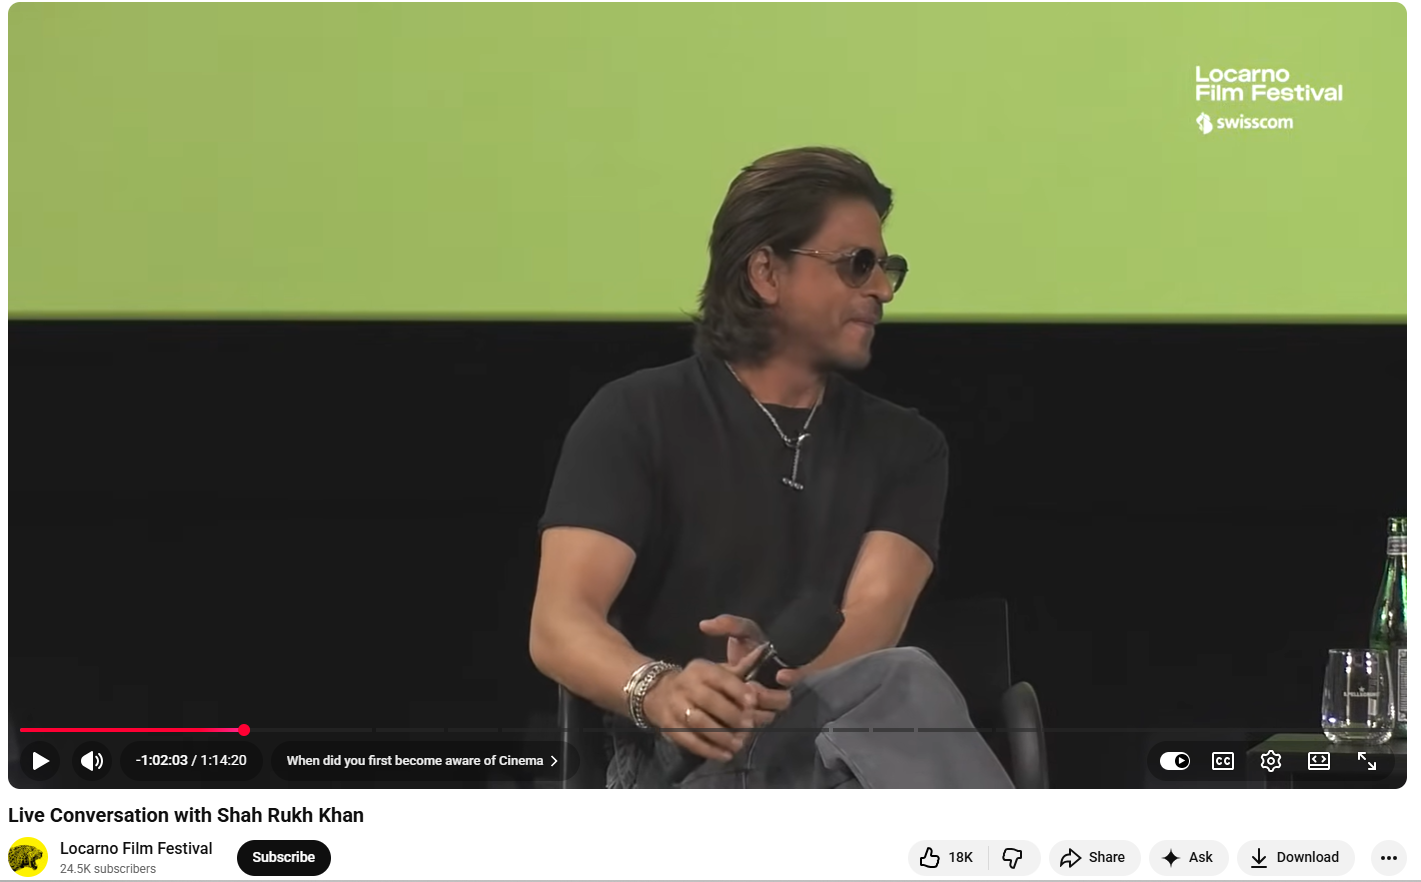
To verify the claim, we extracted key frames from the viral video and conducted a Google reverse image search. This led us to the original video uploaded on a YouTube channel titled “Locarno Film Festival” on August 11, 2024. According to the available information, Shah Rukh Khan was sharing insights about his life and career during a conversation with the festival’s Artistic Director, Giona A. Nazzaro. This raised strong suspicion that the viral video had been edited using AI.
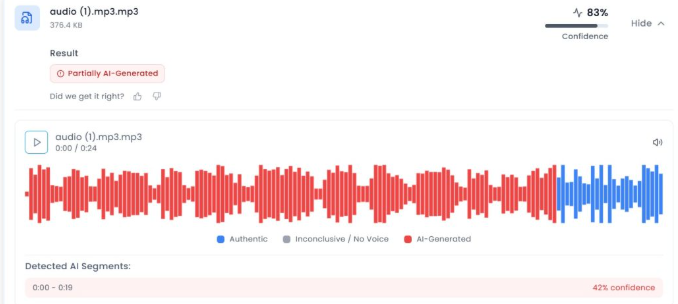
To further examine the authenticity of the audio, we analysed it using AI detection tools. The audio was first checked using Aurigin.ai, which indicated an 83 percent probability that the voice in the viral clip was AI-generated.
Conclusion
The CyberPeace’s research confirmed that the claim associated with Shah Rukh Khan’s viral video is false. The video is a deepfake in which the audio has been altered using artificial intelligence. In the original footage, Khan was discussing his life and experiences, and he did not make any statement about helping Rajpal Yadav.

Introduction
In today’s digital age, everyone is online, so is the healthcare sector worldwide. The latest victim of a data breach is Hong Kong healthcare provider OT&P Healthcare, which has recently suffered a data loss of 100,000 patients that exposed their medical history, and caused concern to the patients and their families. This breach has highlighted the vulnerability in the healthcare sector /industry and the importance of cybersecurity measures to protect sensitive information. This blog will explore the data breach, its impact on patients and families, and the best practices for safeguarding sensitive data.
Background: On 13 March 2023, an incident took place where the Cybercriminals deployed a variety of methods to breach the data, which included phishing attacks, malware, and exploiting software vulnerabilities. OT&P Health Care exploits the sensitive data of the patients. According to OT&P Healthcare, it is working together with law enforcement and has hired a cybersecurity firm to investigate the incident and tighten its security procedures. Like other data breaches, the inquiry will most certainly take some time to uncover the actual source and scope of the intrusion. Regardless of the cause of the breach, this event emphasises the significance of frequent cybersecurity assessments, vulnerability testing, and proactive data protection measures. Considering the dangers in the healthcare sector must be cautious in preserving the personal and medical records of the patients as they are sensitive in nature.
Is confidentiality at stake due to data breaches?
Medical data breaches represent a huge danger to patients, with serious ramifications for their privacy, financial security, and physical health. Some of the potential hazards and effects of medical data breaches are as follows:
- Compromise of patient data: Medical data breaches can expose patients’ sensitive information, such as their medical history, diagnoses, treatment, and medication regimens. If history is highly personal and reaches the wrong hands, it could harm someone’s reputation.
- Identity theft: the data stolen by the cybercriminals may be used by them to open credit accounts and apply for loans, Patients can suffer severe financial and psychological stress because of identity theft since they may spend years attempting to rebuild their credit and regain their good name.
- Medical Fraud: Medical data breaches can also result in medical fraud, which occurs when hackers use stolen medical information to charge insurance companies for services that were not performed or for bogus treatments or procedures. Medical fraud may result in financial losses for patients, insurance companies, and individuals obtaining ineffective or risky medical care.
Impact on patients
Data breach does not cause financial loss but may also profoundly impact their mental health and emotional well-being. let’s understand some psychological impacts:
- Anxiety and Stress: Patients whose medical data has been affected may experience feelings of stress and anxiety as they worry about the potential consequences of the data loss can be misused.
- Loss of faith: Patients may lose faith in their healthcare providers if they believe their personal and medical information needs to be properly As a result, patients may be reluctant to disclose sensitive information to their healthcare professionals, compromising the quality of their medical care.
- Sense of Embarrassment: Patients may feel disregarded or ashamed if their sensitive medical information is revealed, particularly if it relates to a sensitive or stigmatised This might lead to social isolation and a reluctance to seek further medical treatment.
- Post-Traumatic Stress Disorder (PTSD): Patients who have experienced a data breach may have PTSD symptoms such as nightmares, flashbacks, and avoidance behaviour. This can have long-term consequences for their mental health and quality of life.
Legal Implications of Data Breach
Patients have certain legal rights and compensations when a healthcare data breach occurs. Let’s have a look at them: –
- Legal Liability: Healthcare providers have a legal obligation to protect data under various privacy and security laws if they fail to take appropriate measures to protect patient data, they may be held legally liable for resulting harm.
- Legal recourse: Patients whose healthcare data leak has impacted them have the legal right to seek compensation and hold healthcare providers and organisations This could involve suing the healthcare practitioner or organisationresponsible for the breach.
- Right to seek compensation: the patients who have suffered from the data loss are liable to seek compensation.
- Notifications: As soon as a data breach takes place, it impacts the organisation and its customers. In this case, it is the responsibility of the OT&P to
- notify their patients about the data breach and inform them about the consequences.
- Take Away from OT &P Healthcare Data Breach: with the growing data breaches in the healthcare industry, here are some lessons that can be learned from the Hong Kong data breach.
- Cybersecurity: The OT&P Healthcare data breach points to the vital need to prioritisecybersecurity in healthcare. To secure themselves, hospitals and the healthcare sector must use the latest software to protect their data.
- Regular risk assessments: These assessments help find system vulnerabilities and security issues. This can assist healthcare providers and organisationsin taking the necessary actions to avoid data breaches and boost their cybersecurity defences.
- Staff Training: Healthcare workers should be taught cybersecurity best practices, such as detecting and responding to phishing attempts, handling sensitive data, and reporting suspected security breaches. This training should be continued to keep workers updated on the newest cybersecurity trends and threats.
- Incident Response Strategy: Healthcare providers and organisations should have an incident response policy in place to deal with data breaches and other security concerns. This strategy should include protocols for reporting instances, limiting the breach, and alerting patients and verified authorities.
Conclusion
The recent data breach in Hong Kong healthcare impact not only the patients but also their trust is shaken. As we continue to rely on digital technology for medical records and healthcare delivery, it is essential that healthcare providers and organisations take proactive steps to protect patient data from cyber-attacks and data breaches.
References

Introduction
The Department of Telecommunications on 28th October 2024 notified an amendment to the Flight and Maritime Connectivity Rules, 2018 (FMCR 2018).
Rule 9 of the principle rules in FMCR 2018 stated:
“Restrictions–(1) The IFMC service provider shall provide the operation of mobile communication services in aircraft at minimum height of 3000 meters in Indian airspace to avoid interference with terrestrial mobile networks. (2) Internet services through Wi-Fi in aircraft shall be made available when electronic devices are permitted to be used only in airplane mode.”
In 2022, an amendment was made to the attached form in the Rules for obtaining authorisation to provide IFMC services.
Subsequently, the 2024 amendment substitutes sub-rule (2), namely :
“ (2) Notwithstanding the minimum height in Indian airspace referred to in sub-rule (1), internet services through Wi-Fi in aircraft shall be made available when electronic devices are permitted to be used in the aircraft.”
Highlights of the Amendment
These rules govern the use of Wi-Fi in airplanes and ships within or above India or Indian territorial waters through In Flight and Maritime Connectivity (IFMC) services provided by IFMC service providers responsible for establishing and maintaining them.
Airplanes are equipped with antennas, onboard servers, and routers to connect to signals received from ground towers via Direct Air-to-Ground Communications (DA2GC) or through satellites. The DA2GC system offers connectivity through various communication methods, supporting services like in-flight Internet access and mobile multimedia. Licensed In-Flight Mobile Connectivity (IFMC) providers must adhere to standards set by international organizations such as the International Telecommunications Union (ITU), the European Telecommunications Standards Institute (ETSI), and the Institute of Electrical and Electronics Engineers (IEEE), or by international forums like the 3rd Generation Partnership Project (3GPP) to offer In-Flight Connectivity. Providers using Indian or foreign satellite systems must obtain approval from the Department of Space.
The IFMC service provider must operate mobile communication services on aircrafts at a minimum altitude of 3,000 meters within Indian airspace to prevent interference with terrestrial mobile networks. However, Wi-Fi access can be enabled at any point during the flight when device use is permitted, not just after reaching 3,000 meters. This flexibility is intended to allow passengers to connect to Wi-Fi earlier in the flight. This amendment aims to ensure that passengers can access the internet while maintaining the safety standards critical to in-flight communication systems.
Implications
- Increased Data Security Needs: There will be a need for robust cybersecurity measures against potential threats and data breaches.
- Increased Costs: Airplanes will have to incur the initial costs for installing antennae. Since airfare pricing in India is market-driven and largely unregulated, these costing changes might find their way into ticket prices, making flight tickets more expensive.
- Interference Management: A framework regarding the conditions under which Wi-FI must be switched off to avoid interference with terrestrial communication systems can be determined by stakeholders and communicated to passengers.
- Enhanced Connectivity Infrastructure: Airlines may need to invest in better flight-connectivity infrastructure to handle increased network traffic as more passengers access Wi-fi at lower altitudes and for longer durations.
Conclusion
The Flight and Maritime Connectivity (Amendment) Rules, 2024, enhance passenger convenience and align India with global standards for in-flight connectivity while complying with international safety protocols. Access to the internet during flights and at sea provides valuable real-time information, enhances safety, and offers access to health support during aviation and maritime operations. However, new challenges including the need for robust cybersecurity measures, cost implications for airlines and passengers, and management of interference with terrestrial networks will have to be addressed through a collaborative approach between airlines, IFMC providers, and regulatory authorities.
Sources
- https://dot.gov.in/sites/default/files/2018_12_17%20AS%20IFMC_2.pdf?download=1
- https://dot.gov.in/sites/default/files/Amendment%20dated%2004112024%20in%20flight%20and%20maritime%20connectivity%20rules%202018%20to%20IFMC%20Service%20Provider.pdf
- https://www.t-mobile.com/dialed-in/wireless/how-does-airplane-wifi-work
- https://tec.gov.in/public/pdf/Studypaper/DA2GC_Paper%2008-10-2020%20v2.pdf
- https://www.indiatoday.in/india/story/wifi-use-flights-no-longer-linked-altitude-now-subject-permission-2628118-2024-11-05
- https://pib.gov.in/Pressreleaseshare.aspx?PRID=1843408#:~:text=With%20the%20repeal%20of%20Air,issue%20directions%20to%20such%20airline.
