
High-risk warning by the Indian government of bugs in Google Chrome, Microsoft Edge and Adobe
Introduction
The Computer Emergency Response Team (CERT-in) is a nodal agency of the government established and appointed as a national agency in respect of cyber incidents and cyber security incidents in terms of the provisions of section 70B of the Information Technology (IT) Act, 2000. CERT-In has issued a cautionary note to Microsoft Edge, Adobe and Google Chrome users. Users have been alerted to many vulnerabilities by the government's cybersecurity agency, which hackers might use to obtain private data and run arbitrary code on the targeted machine. Users are advised by CERT-In to apply a security update right away in order to guard against the problem.
Vulnerability note
Vulnerability notes CIVN-2023-0361, CIVN-2023-0362 and CIVN-2023-0364 for Google Chrome for Desktop, Microsoft Edge and Adobe respectively, include more information on the alert. The problems have been categorized as high-severity issues by CERT-In, which suggests applying a security upgrade right now. According to the warning, there is a security risk if you use Google Chrome versions earlier than v120.0.6099.62 on Linux and Mac, or earlier than 120.0.6099.62/.63 on Windows. Similar to this, the vulnerability may also impact users of Microsoft Edge browser versions earlier than 120.0.2210.61.
Cause of the Problem
These vulnerabilities are caused by "Use after release in Media Stream, Side Panel Search, and Media Capture; Inappropriate implementation in Autofill and Web Browser UI, “according to the explanation in the issue note on the CERT-In website. The alert further warns that individuals who use the susceptible Microsoft Edge and Google Chrome browsers could end up being targeted by a remote attacker using these vulnerabilities to send a specially crafted request.” Once these vulnerabilities are effectively exploited, hackers may obtain higher privileges, obtain sensitive data, and run arbitrary code on the system of interest.
High-security issues: consequences
CERT-In has brought attention to vulnerabilities in Google Chrome, Microsoft Edge, and Adobe that might have serious repercussions and put users and their systems at risk. The vulnerabilities found in widely used browsers, like Adobe, Microsoft Edge, and Google Chrome, present serious dangers that might result in data breaches, unauthorized code execution, privilege escalation, and remote attacks. If these vulnerabilities are taken advantage of, private information may be violated, money may be lost, and reputational harm may result.
Additionally, the confidentiality and integrity of sensitive information may be compromised. The danger also includes the potential to interfere with services, cause outages, reduce productivity, and raise the possibility of phishing and social engineering assaults. Users may become less trusting of the impacted software as a result of the urgent requirement for security upgrades, which might make them hesitant to utilize these platforms until guarantees of thorough security procedures are provided.
Advisory
- Users should update their Google Chrome, Microsoft Edge, and Adobe software as soon as possible to protect themselves against the vulnerabilities that have been found. These updates are supplied by the individual software makers. Furthermore, use caution when browsing and refrain from downloading things from unidentified sites or clicking on dubious links.
- Make use of reliable ad-blockers and strong, often updated antivirus and anti-malware software. Maintain regular backups of critical data to reduce possible losses in the event of an attack, and keep up with best practices for cybersecurity. Maintaining current security measures with vigilance and proactiveness can greatly lower the likelihood of becoming a target for prospective vulnerabilities.
References

Related Blogs

Introduction
To every Indian’s pride, the maritime sector has seen tremendous growth under various government initiatives. Still, each step towards growth should be given due regard to security measures. Sadly, cybersecurity is still treated as a secondary requirement in various critical sectors, let alone to protect the maritime sector and its assets. Maritime cybersecurity includes the protection of digital assets and networks that are vulnerable to online threats. Without an adequate cybersecurity framework in place, the assets remain at risk from cyber threats, such as malware and scams, to more sophisticated attacks targeting critical shore-based infrastructure. Amid rising global cyber threats, the maritime sector is emerging as a potential target, underscoring the need for proactive security measures to safeguard maritime operations. In this evolving threat landscape, assuming that India's maritime domain remains unaffected would be unrealistic.
Overview of India’s Maritime Sector
India’s potential in terms of its resources and its ever-so-great oceans. India is well endowed with its dynamic 7,500 km coastline, which anchors 12 major ports and over 200 minor ones. India is strategically positioned along the world’s busiest shipping routes, and it has the potential to rise to global prominence as a key trading hub. As of 2023, India’s share in global growth stands at a staggering 16%, and India is reportedly running its course to become the third-largest economy, which is no small feat for a country of 1.4 billion people. This growth can be attributed to various global initiatives undertaken by the government, such as “Sagarmanthan: The Great Oceans Dialogue,” laying the foundation of an insightful dialogue between the visionaries to design a landscape for the growth of the marine sector. The rationale behind solidifying a security mechanism in the maritime industry lies in the fact that 95% of the country’s trade by volume and 70% by value is handled by this sector.
Current Cybersecurity Landscape in the Maritime Sector
All across the globe, various countries are recognising the importance of their seas and shores, and it is promising that India is not far behind its western counterparts. India has a glorious history of seas that once whispered tales of Trade, Power, and Civilizational glory, and it shall continue to tread its path of glory by solidifying and securing its maritime digital infrastructure. The path brings together an integration of the maritime sector and advanced technologies, bringing India to a crucial juncture – one where proactive measures can help bridge the gap with global best practices. In this context, to bring together an infallible framework, it becomes pertinent to incorporate IMO’s Guidelines on maritime cyber risk management, which establish principles to assess potential threats and vulnerabilities and advocate for enhanced cyber discipline. In addition, the guidelines that are designed to encourage safety and security management practices in the cyber domain warn the authorities against procedural lapses that lead to the exploitation of vulnerabilities in either information technology or operational technology systems.
Anchoring Security: Global Best Practices & Possible Frameworks
The Asia-Pacific region has not fallen behind the US and the European Union in realising the need to have a dedicated framework, with the growing prominence of the maritime sector and countries like Singapore, China, and Japan leading the way with their robust frameworks. They have in place various requirements that govern their maritime operations and keep in check various vulnerabilities, such as Cybersecurity Awareness Training, Cyber Incident Reporting, Data Localisation, establishing secure communications, Incident management, penalties, etc.
Every country striving towards growth and expanding its international trade and commerce must ensure that it is secure from all ends to boost international cooperation and trust. On that note, the maritime sector has to be fortified by placing the best possible practices or a framework that is inclined towards its commitment to growth. The following four measures are indispensable to this framework, and in the maritime industry, they must be adapted to the unique blend of Information Technology (IT) and Operational Technology (OT) used in ships, ports, and logistics. The following mechanisms are not exhaustive in nature but form a fundamental part of the framework:
- Risk Assessment: Identifying, analysing, and ensuring that all systems that are susceptible to cyber threats are prioritized and vulnerability scans are conducted of vessel control systems and shore-based systems. The critical assets that have a larger impact on the whole system should be kept formidable in comparison to other systems that may not require the same attention.
- Access Control: Restrictions with regard to authorisation, wherein access must be restricted to verified personnel to reduce internal threats and external breaches.
- Incident Response Planning: The nature of cyber risks is inherently dynamic in nature; there are no calls for cyber attacks or warfare techniques. Such attacks are often committed in the shadows, so as to require an action plan to respond to and to recover from cyber incidents effectively.
- Continuous Staff Training: Regularly educating all levels of maritime personnel about cyber hygiene, threat trends, and secure practices.
CyberPeace Suggests: Legislative & Executive Imperatives
It can be said with reasonable foresight that the Indian maritime sector is in need of a national maritime cybersecurity framework that operates in cooperation with the international framework. The national imperatives will include robust cyber hygiene requirements, real-time threat intelligence mechanisms, incident response obligations, and penalties for non-compliance. The government must strive to support Indian shipbuilders through grants or incentives to adopt cyber-resilient ship design frameworks.
The legislative quest should be to incorporate the National Maritime Cybersecurity Framework with the well-established CERT-In guidelines and data protection principles. The one indispensable requirement set under the framework should be to mandate Cybersecurity Awareness Training to help deploy trained personnel equipped to tackle cyber threats. The rationale behind such a requirement is that there can be no “one-size-fits-all” approach to managing cybersecurity risk, which is dynamic and evolving in nature, and the trained personnel will play a key role in helping establish a customised framework.
References
- https://pib.gov.in/PressNoteDetails.aspx?NoteId=153432®=3&lang=1
- https://bisresearch.com/industry-report/global-maritime-cybersecurity-market.html#:~:text=Maritime%20cybersecurity%20involves%20safeguarding%20digital,and%20protection%20against%20potential%20risks.
- https://www.shipuniverse.com/2025-maritime-cybersecurity-regulations-a-simplified-breakdown/#:~:text=Japan%3A,for%20incident%20response%20and%20recovery.
- https://wwwcdn.imo.org/localresources/en/OurWork/Security/Documents/MSC-FAL.1-Circ.3-Rev.2%20-%20Guidelines%20On%20Maritime%20Cyber%20Risk%20Management%20(Secretariat)%20(1).pdf
Introduction
Digital evidence has become part of almost every modern investigation. A photograph can place a person at a location, an audio recording can capture a conversation, and a video can appear to show an event as it happened. For years, the main forensic concern was whether such material had been altered. The rapid growth of generative artificial intelligence has added a harder question: even when a file is preserved exactly as received, can investigators still trust what it appears to show?
Deepfakes have made this question practical rather than theoretical. Synthetic or manipulated audio, video and images can imitate real people and real events with increasing realism. CERT-In describes deepfakes as a high-risk threat because they can support disinformation, fraud, social engineering and reputational harm.[1] NIST research likewise treats AI-generated media as a digital-forensics challenge that requires systematic evaluation of detection technologies.[2]
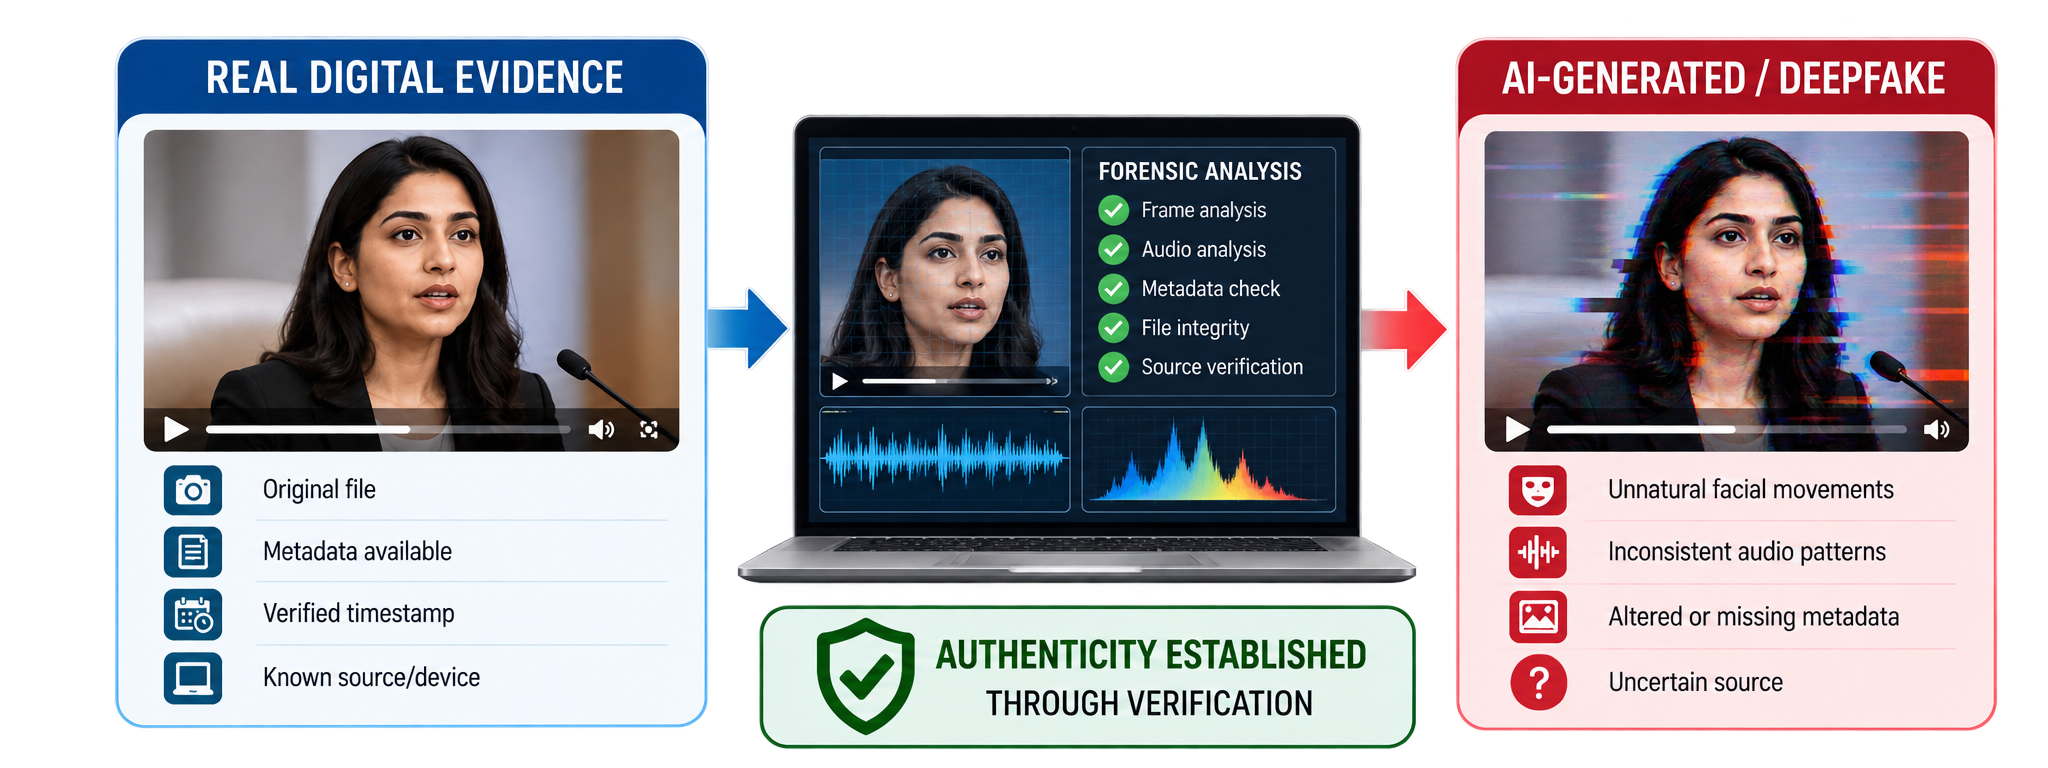
The result is an evidence problem. The answer is not to stop trusting digital evidence, but to become more disciplined about establishing its origin, integrity, context and authenticity.
The evidence problem begins before the laboratory
When a suspicious video reaches an investigator through WhatsApp, Telegram, email or social media, the file may already have passed through several transformations. It may have been compressed, re-encoded, cropped, renamed or stripped of metadata. A screenshot may preserve what is visible but lose the original file structure. A forwarded audio clip may contain no reliable information about where it was first recorded.
For that reason, forensic examination should begin with acquisition and provenance, not with a quick “deepfake detector” result. Investigators should ask: Who supplied the file? Where was it obtained? Is there an original version? What device or account produced it? What happened to the file before it reached the investigator?
Cryptographic hashing remains important because it can demonstrate that an acquired working copy has not changed during examination. But a valid hash does not prove that the underlying event was genuine. A perfectly preserved fake is still a fake.
What a professional examination should look for
A reliable assessment combines several forms of evidence rather than relying on one technical indicator.
Source and acquisition. The original artefact should be preserved whenever possible. Investigators should record the acquisition method, date and time, source account or device, and any known transformations before collection. A documented chain of custody is essential when material may later support a legal, disciplinary or regulatory decision.
Metadata and file structure. Metadata may provide useful clues about creation, encoding, editing software and timestamps. File structure, compression behaviour and related technical characteristics can also reveal inconsistencies. However, these indicators are supporting evidence, not proof on their own, because metadata can be removed or rewritten during normal processing.
Content-level examination. Forensic analysis can include frame-by-frame video review, audio waveform and spectral examination, and inspection for inconsistencies in lighting, reflections, facial movement, lip synchronisation or background elements. Such signs may help guide an investigation, but they are not a permanent checklist. Generative systems continue to improve.
Independent corroboration. This is often the strongest step. If a recording allegedly shows that a person was in a particular place at a particular time, investigators can compare it with CCTV, access-control records, device artefacts, communications, location information, eyewitness accounts or other independent records. The goal is to determine whether the wider evidence supports the event represented by the media.
A real-world lesson: the Pikesville case
The 2024 Pikesville High School incident in Maryland provides a practical example of why authenticity cannot be assumed from appearance alone. An audio recording circulated online that was presented as the principal making racist and antisemitic comments. On January 17, 2024, Baltimore County Public Schools said it could not yet confirm the recording’s veracity and opened an investigation.[3]
Several months later, the school district reported that investigators, with assistance from the FBI and other experts, had verified that the audio had been created using artificial intelligence.[4] Police subsequently arrested the school’s former athletic director in connection with the fabricated recording.[5]
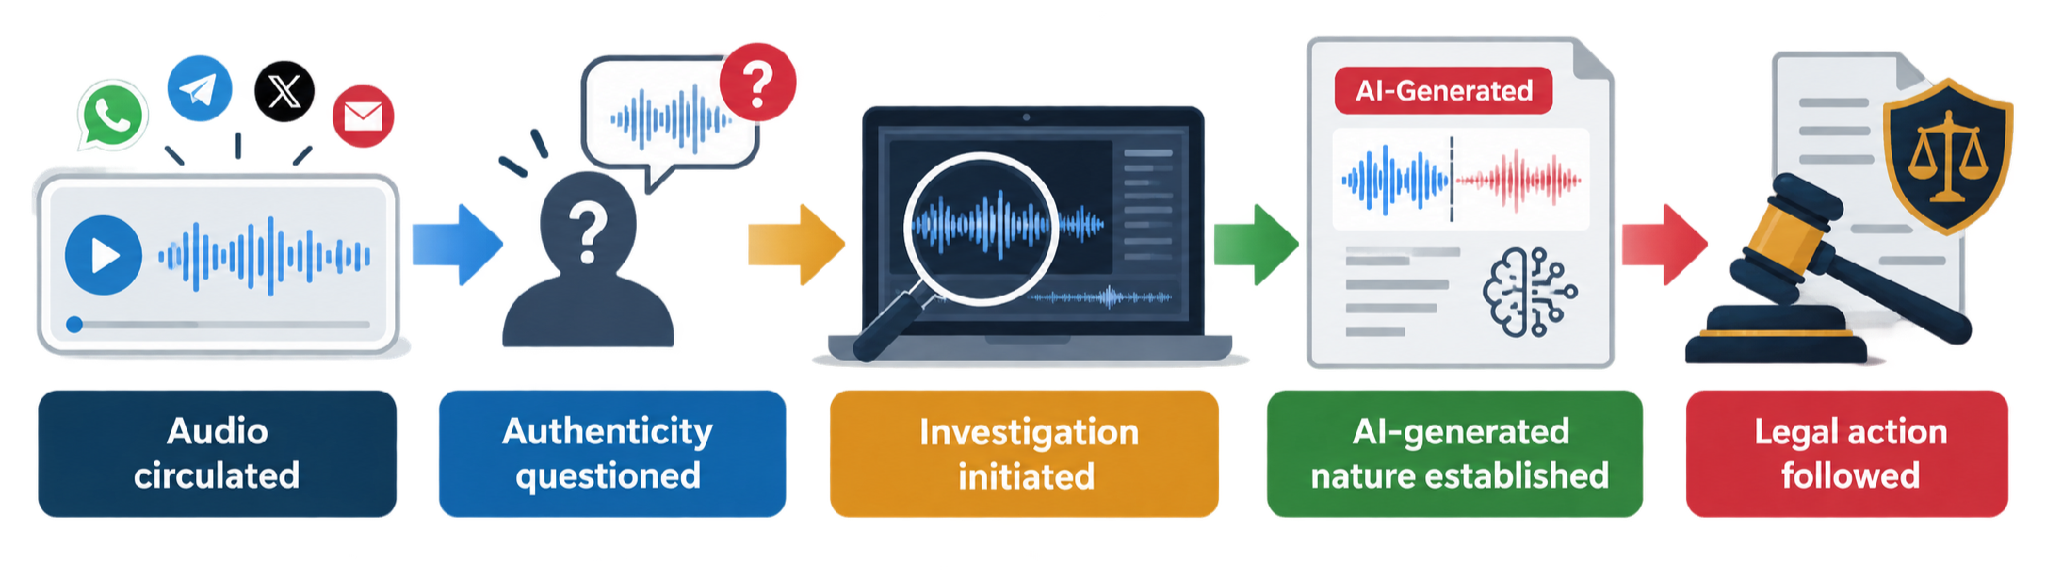
The forensic lesson is larger than the incident itself. The recording had social consequences before its authenticity was established. In a fast-moving online environment, the first version of an event can travel much further than the later correction. Deepfake investigations therefore have to consider not only whether media is authentic, but also how quickly unverified material can influence decisions.
From deepfake detection to content provenance
Detection tools will remain useful, but they should be treated as part of an examination rather than an automatic verdict. NIST’s Guardians of Forensic Evidence work reflects the need to evaluate how analytic systems perform against changing forms of AI-generated media and how well they generalise beyond controlled conditions.[2]
Another important direction is content provenance. The Coalition for Content Provenance and Authenticity (C2PA) has developed a technical framework for recording verifiable information about how digital content was created and changed. Content Credentials can bind provenance information to an asset using cryptographic techniques, allowing later users to inspect a recorded content history when that information is available.[6]
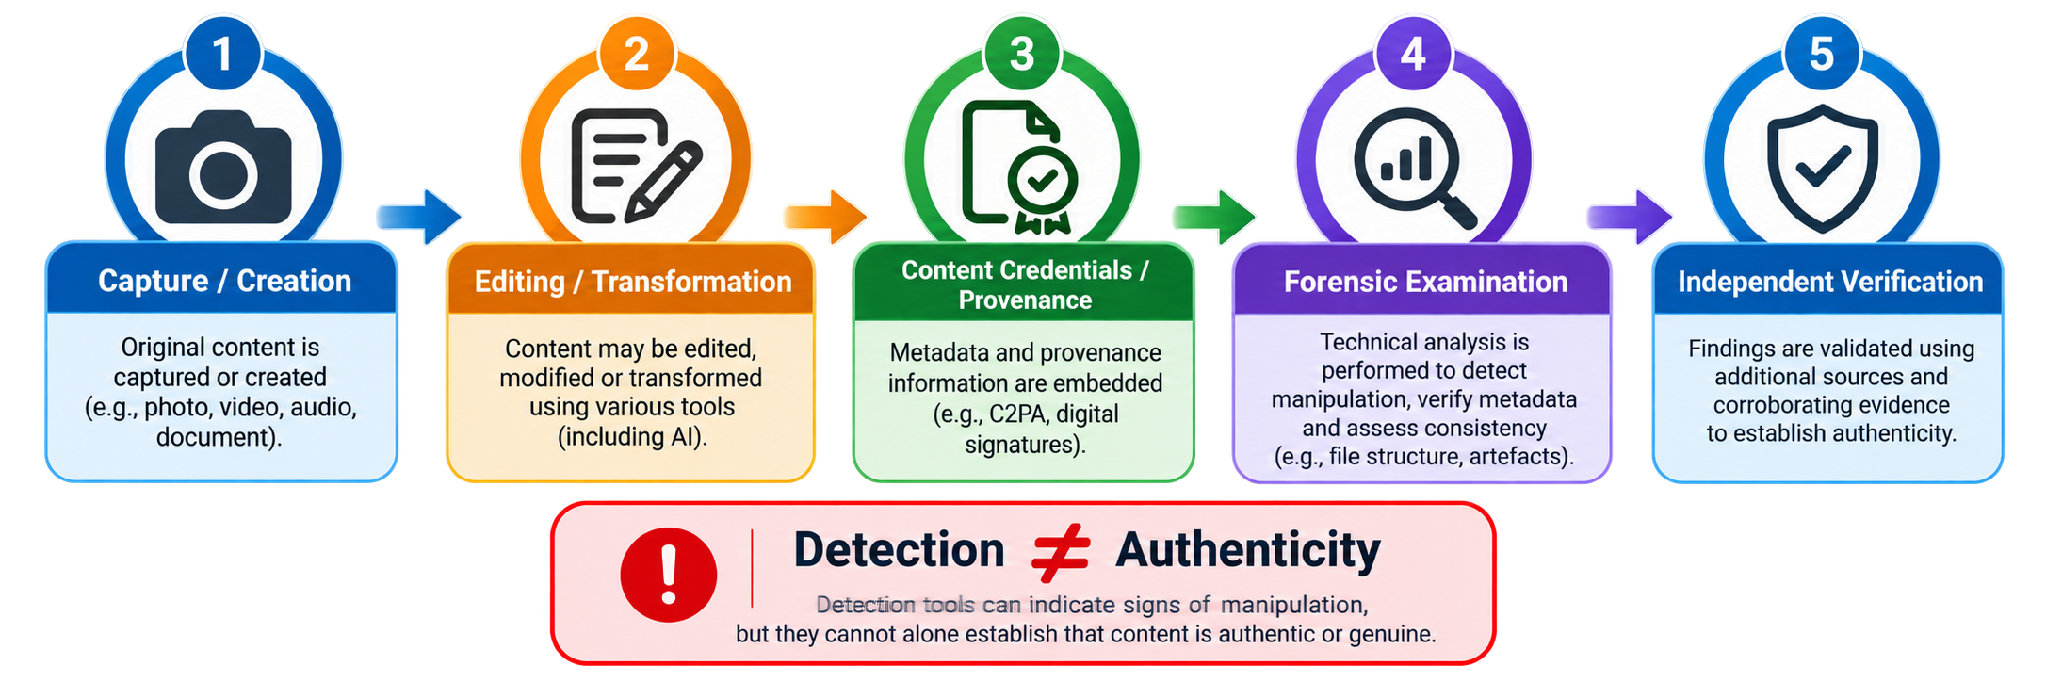
Provenance does not mean that every claim associated with a file is automatically true. It adds context: who created it, what actions were taken and how the asset changed. In a deepfake environment, that context can be as important as the content itself.
Why this matters in India
The issue is especially relevant to India’s fast-growing digital environment. CERT-In’s 2024 advisory identifies misinformation, fraud and reputational damage among the risks associated with synthetic media.[1] In August 2026, the Government of India stated that the regulatory framework addresses AI-generated deepfakes and noted amendments to the IT Rules in February 2026 concerning harms arising from synthetically generated information, including requirements related to labelling and traceable metadata for permissible AI-generated content.[7]
For organisations, deepfake response should therefore not be treated only as a media or public-relations issue. It can become an incident-response and forensic issue. A suspicious executive voice note, a manipulated employee video or a fabricated screen recording may require preservation, technical examination and independent corroboration before any action is taken.
Conclusion
Deepfakes do not make digital evidence useless. Deepfakes make handling of evidence more dangerous. The professional response is not to believe everything or to doubt everything. The professional response is to build a process around evidence: preserve the original where possible document how evidence was acquired, calculate and record hashes, examine metadata and technical characteristics use detection tools while understanding their limitations compare media with independent evidence and examine provenance information where it is available.
Importantly investigators and decision-makers should separate three questions: Is the file intact? Is the content authentic? Does the content actually prove the event being alleged? Deepfakes can pass the test while failing the other two.
In the age of AI evidence will increasingly be judged not only by how convincing it looks but, by how well its origin, integrity, context and history can be demonstrated. That is the standard that can help preserve trust when seeing and hearing're no longer enough.
References
1. CERT-In, “Deepfakes - Threats and Countermeasures,” Advisory CIAD-2024-0060, 27 November 2024. View source
2. NIST, “Guardians of Forensic Evidence: Evaluating Analytic Systems Against AI-Generated Deepfakes,” 27 January 2025. View source
3. Baltimore County Public Schools, “January 17, 2024, Community Update: Message from Superintendent Dr. Myriam Rogers Regarding Pikesville High School.” View source
4. Baltimore County Public Schools, “April 24, 2024 Staff and Community Update: Message from Superintendent Dr. Myriam Rogers Regarding Pikesville High School Investigation.” View source
5. The Baltimore Banner / WYPR, “Ex-athletic director framed principal with AI-generated voice, police say,” 25 April 2024. View source
6. Coalition for Content Provenance and Authenticity (C2PA), “Content Credentials: C2PA Technical Specification,” Version 2.1. View source
7. Government of India, Ministry of Electronics & Information Technology, “Government Strengthens Regulatory Framework to Address AI-Generated Deepfakes,” 6 August 2026. View source

Executive Summary:
A video of Pakistani Olympic gold medalist and Javelin player Arshad Nadeem wishing Independence Day to the People of Pakistan, with claims of snoring audio in the background is getting viral. CyberPeace Research Team found that the viral video is digitally edited by adding the snoring sound in the background. The original video published on Arshad's Instagram account has no snoring sound where we are certain that the viral claim is false and misleading.

Claims:
A video of Pakistani Olympic gold medalist Arshad Nadeem wishing Independence Day with snoring audio in the background.

Fact Check:
Upon receiving the posts, we thoroughly checked the video, we then analyzed the video in TrueMedia, an AI Video detection tool, and found little evidence of manipulation in the voice and also in face.


We then checked the social media accounts of Arshad Nadeem, we found the video uploaded on his Instagram Account on 14th August 2024. In that video, we couldn’t hear any snoring sound.

Hence, we are certain that the claims in the viral video are fake and misleading.
Conclusion:
The viral video of Arshad Nadeem with a snoring sound in the background is false. CyberPeace Research Team confirms the sound was digitally added, as the original video on his Instagram account has no snoring sound, making the viral claim misleading.
- Claim: A snoring sound can be heard in the background of Arshad Nadeem's video wishing Independence Day to the people of Pakistan.
- Claimed on: X,
- Fact Check: Fake & Misleading
