
#FactCheck-Old Bihar train protest video falsely linked to CJP protest and India’s first hydrogen train.
Executive Summary
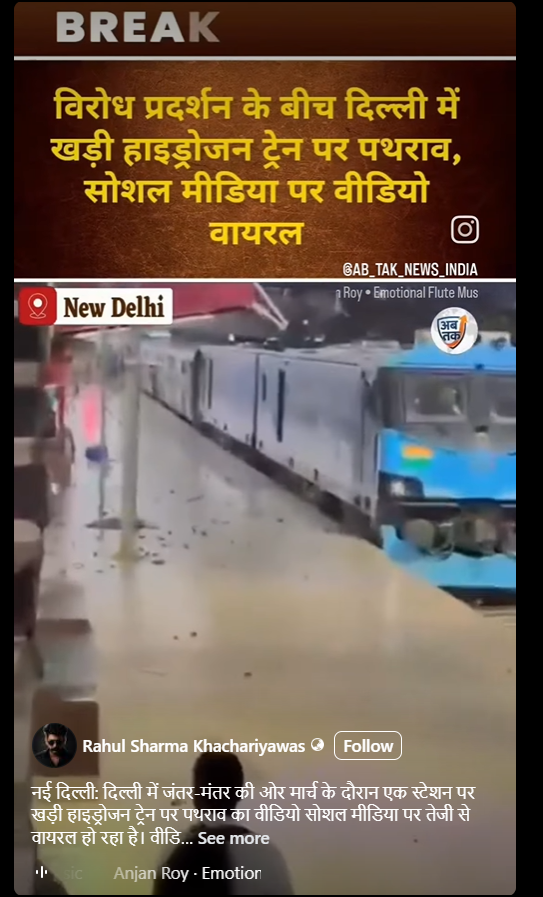
A video is being widely shared on social media with the claim that protesters during the Cockroach Janta Party (CJP) protest in Delhi pelted stones at India’s first hydrogen train. The viral video shows a train parked at a railway station being attacked with stones amid chaos and heavy commotion. Social media users are claiming that the incident took place at a Delhi railway station, where protesters targeted the country’s new hydrogen train during the CJP march towards Jantar Mantar and damaged public property. CyberPeace Research Wing’s research found the claim to be false. The viral video is not related to the CJP protest or India’s first hydrogen train. The video is from Bihar, where candidates appearing for a Bihar Police Prohibition Department examination had protested over train delays, leading to clashes and stone-pelting.
Claim:
A social media post claimed:“New Delhi: During the march towards Jantar Mantar, a video of stone-pelting on a hydrogen train parked at a railway station is going viral. Some people can be seen throwing stones at the train. Damaging public property is a punishable offence. Further action will be taken based on official information from authorities.”
https://www.facebook.com/reel/1573292581055475
Fact Check:
To verify the authenticity of the viral claim, we extracted keyframes from the video and conducted a reverse image search using Google Lens. During the research, we found the same video clip uploaded on the Facebook page News Bihar on June 14, 2026. According to the post’s caption, the incident took place at Danapur–Patliputra railway station in Patna, Bihar, where thousands of candidates appearing for the Bihar Police Prohibition Department examination became agitated due to train delays. The protest escalated after candidates blocked railway tracks, leading to a confrontation between police personnel and students, including stone-pelting.
https://www.facebook.com/reel/2476273089511309

During further research, we found a video uploaded by Republic World’s YouTube channel on June 14, 2026, which also contained visuals matching the viral clip. The report stated that students in Bihar staged an aggressive protest after trains were delayed. During the protest, clashes broke out between police and students, and authorities used mild force to control the situation.
https://www.youtube.com/shorts/AlamDZzPKLA

During our research, we also found a reply from the official X account of Northern Railway on a similar viral post. In its response, Northern Railway clarified that the train visible in the viral video was not a hydrogen train. The railway authority stated that the video was old and confirmed that hydrogen train services are operating safely and as per their scheduled timetable.

Conclusion:
CyberPeace Research Wing’s research found that the claim linking the viral video to stone-pelting on India’s first hydrogen train during the CJP protest is false. The viral video is from Bihar, where candidates appearing for the Bihar Police Prohibition Department examination protested over train delays, resulting in clashes and stone-pelting at a railway station. The video has been falsely linked to the CJP protest and hydrogen train.

Related Blogs
Introduction
Every domain of conflict has eventually had to learn restraint. The first Geneva Convention of 1864 grew out of one man's horror at what he saw after a single battle, and it rested on an idea that has since become the backbone of humanitarian law: even in war, there are things that must not be done to people. Cyberspace is the newest domain to face that test, and it is arguably the hardest. Code carries no uniform, an intrusion crosses borders without anyone noticing, and the same network can serve a soldier, a shopkeeper and a schoolchild at once. Whether the actor is a criminal group, an intelligence service or a military cyber unit, the consequences land on ordinary people. That is the case for a humanitarian approach to cyberspace, and it is why it has moved from a courtesy to a matter of national security.
Why the humanitarian lens matters to every nation
Cyberspace does not sort itself into civilian and military zones. The International Committee of the Red Cross (ICRC) has pointed out for years that military networks lean on civilian cyber infrastructure such as undersea cables, satellites and routers, while civilian supply chains and essential services run over the same channels. A cyber operation aimed at one can land on the other, and the ICRC has warned that incidental harm in this domain risks being widespread and crossing national borders.
It helps to separate three situations, because different rules govern each. Cybercrime, such as ransomware against a hospital, is a matter for criminal law and international police cooperation. Intrusion and espionage in peacetime fall under domestic law and the norms of responsible state behaviour agreed at the United Nations. Cyber operations during an armed conflict fall under international humanitarian law (IHL), which the ICRC and a growing number of states hold applies to cyber means just as it applies to any other weapon or method of warfare. Its core principles, humanity, necessity, proportionality and distinction, were linked to cyberspace in the 2021 report of the UN Group of Governmental Experts. Under those principles civilians and civilian infrastructure must not be attacked, and medical facilities enjoy special protection.
For a nation, the practical point is simpler. Its own hospitals, grids, water systems and payment networks are exactly the assets that erode first when restraint erodes. A country that argues for humanitarian limits is protecting itself as much as anyone else.
A lesson from Lebanon
The events of 17 and 18 September 2024 in Lebanon show what happens when everyday technology stops being trustworthy. On the first day, thousands of pagers detonated across the country within roughly an hour of each other. The next day, hand held radios followed. By the account UN High Commissioner for Human Rights Volker Türk gave the Security Council on 20 September, at least 37 people had been killed, including two children, and more than 3,400 had been injured in Lebanon alone. UN experts noted that medical personnel were among the dead.
Attribution in this case remained a matter of public allegation rather than official claim, and this piece does not try to settle it. What matters here is the method and how the UN read it legally. Türk told the Council that IHL prohibits booby traps in the form of apparently harmless portable objects designed and constructed to contain explosives, and that violence intended to spread terror among civilians is a war crime. He added that striking thousands of people simultaneously, without knowing who held the devices, where they were or who stood nearby, violates international human rights law and, where applicable, IHL. His summary was that this cannot become the new normal, and he called for an independent, thorough and transparent investigation.
The pager episode was physical, with explosives concealed in hardware, not malicious code. It belongs in a discussion of cyberspace because of how it worked: a compromised supply chain turned an ordinary civilian communication tool into a weapon. That is the same trust relationship every digital system depends on. When people cannot assume that the devices and software they use are what they appear to be, the line between civilian object and military instrument, the foundation of humanitarian law, survives on paper while wearing away in practice.
The Digital Emblem Project
What it is:Think of the red cross on a hospital roof or an ambulance. It tells anyone who sees it that the building or vehicle is protected and must not be attacked. The Digital Emblem is the same idea for computer systems. It is a digital marker, built on a cryptographic signature, that a protected server or network broadcasts to signal that it belongs to a medical or humanitarian organisation entitled to protection under international humanitarian law. The organisations allowed to use it are the same ones entitled to use the physical emblem.
What it aims to achieve:Its purpose is recognition. Someone probing a network cannot see a red cross, and may not realise they have entered a medical facility's systems or a Red Cross office. The digital emblem lets that fact be detected and verified by machines, so a military cyber unit or any other operator can recognise the system and avoid it. It does not create any new legal protection, and it does not replace cybersecurity. Like the physical emblem, it cannot stop an attack on its own. It makes existing protection visible.
Why it was created:The physical emblem has worked for more than 150 years, but it has no natural place online. Cyber operations are becoming a regular feature of armed conflict, and humanitarian bodies are targeted by criminals seeking money as well as by state linked actors. The ICRC learned this directly in 2022, when a breach of its own servers exposed the data of more than 515,000 people in vulnerable situations. It began researching a digital equivalent and, with ETH Zurich, developed a technical standard.
Where it stands today:The idea has moved from concept to working prototype. In October 2024, Resolution 2 was adopted at the International Conference of the Red Cross and Red Crescent, which includes all 196 states party to the Geneva Conventions, affirming that the duty to respect and protect medical services and humanitarian personnel applies to their use of information and communication technologies. In July 2026, the ICRC, with Microsoft's support, presented the emblem in Geneva and announced the next phase, with several national Red Cross societies already testing it. That phase is expected to take several years. Technical standards still need to be developed through bodies such as the International Telecommunication Union and the Internet Engineering Task Force, and international law would need to recognise the emblem formally, through an amendment to the Geneva Conventions framework or a new protocol.
For nations, the emblem offers a practical way to mark hospital and humanitarian networks as off limits, and it removes the excuse of not knowing when a marked system is attacked. That makes accountability clearer. It also supports the central argument of this piece: humanitarian principles only work in cyberspace if they can be seen and acted on, not just written down. Its success will depend on whether the people it addresses, state cyber forces and criminal groups alike, choose to honour it, which is why adoption and enforcement at national level will matter as much as the technology.
What nations can do now
None of this requires waiting for a new treaty. A country can publicly state its national position on how international law, including IHL, applies to cyber operations, since the ICRC itself treats the publication of national views as a form of capacity building. It can classify healthcare, humanitarian, water and energy networks as protected critical infrastructure in its national cyber strategy, and plan to adopt the digital emblem for its own hospitals as standards mature. It can invest in supply chain assurance for the devices and software that civilians and governments depend on, which is the most direct lesson of the Lebanon episode. It can ensure that military cyber units are trained in IHL and that cyber capabilities undergo legal review with an eye to humanitarian impact. And it can treat ransomware against hospitals as the serious crime it is, backed by international cooperation on evidence and victim protection.
Conclusion
A humanitarian approach to cyberspace is sometimes dismissed as idealism. It is closer to enlightened self interest. Every state relies on the reciprocal restraint that keeps hospitals, grids and communications networks out of the crossfire, and every state is, at some point, on the receiving end of the alternative. The Lebanon episode showed how quickly trust in ordinary technology can fail, and the Digital Emblem shows one way the international community is trying to rebuild it. Nations that commit early, in doctrine, in procurement and in practice, will help decide whether cyberspace develops guardrails or simply learns to live without them. The idea behind the first Geneva Convention was that even conflict has limits. Cyberspace is where that argument now needs to be made again.
References
- ICRC, "ICRC proposes digital red cross/crescent emblem to signal protection in cyberspace." https://www.icrc.org/en/document/icrc-proposes-digital-red-crosscrescent-emblem-signal-protection-cyberspace
- ETH Zurich, "Digital emblem for humanitarian law in cyberspace." https://ethz.ch/en/news-and-events/eth-news/news/2023/11/digital-emblem-for-humanitarian-law-in-cyberspace.html
- Digital Watch Observatory, "ICRC unveils digital emblem to protect humanitarian organisations online." https://dig.watch/updates/icrc-digital-emblem-cybersecurity
- Geneva Solutions, "ICRC and Microsoft launch digital emblem to prevent cyberattacks." https://genevasolutions.news/peace-humanitarian/icrc-and-microsoft-launch-digital-emblem-to-prevent-cyberattacks
- "Making humanitarian protection visible in cyberspace: The promise of the Digital Emblem." https://blogs.microsoft.com/on-the-issues/2026/07/09/making-humanitarian-protection-visible-in-cyberspace-the-promise-of-the-digital-emblem/
- ICRC Humanitarian Law and Policy Blog, "IHL's lighthouse: navigating towards a digital emblem." https://blogs.icrc.org/law-and-policy/2026/01/15/ihls-lighthouse-navigating-towards-a-digital-emblem/
- Digital Watch Observatory, "Building Trust and Protection for Essential Digital Services: From Standards to Deployment." https://dig.watch/event/wsis-forum-2026/building-trust-and-protection-for-essential-digital-services-from-standards-to-deployment
- UN OHCHR, "Exploding pagers and radios: A terrifying violation of international law, say UN experts." https://www.ohchr.org/en/press-releases/2024/09/exploding-pagers-and-radios-terrifying-violation-international-law-say-un
- UN OHCHR, "Disrespect for international law is a matter of international peace and security, High Commissioner Türk tells the UN Security Council." https://www.ohchr.org/en/statements-and-speeches/2024/09/disrespect-for-international-law-a-matter-of-international-peace-and-security-hc
- ASIL Insights, "Cyber Operations under International Humanitarian Law: Perspectives from the ICRC." https://asil.org/insights/volume-24-issue-11/
- Pager Attack in Lebanon, CyberPeace Blog https://cyberpeace.org/resources/blogs/pager-attack-in-lebanon

Introduction
On March 12, the Ministry of Corporate Affairs (MCA) proposed the Bill to curb anti-competitive practices of tech giants through ex-ante regulation. The Draft Digital Competition Bill is to apply to ‘Core Digital Services,’ with the Central Government having the authority to update the list periodically. The proposed list in the Bill encompasses online search engines, online social networking services, video-sharing platforms, interpersonal communications services, operating systems, web browsers, cloud services, advertising services, and online intermediation services.
The primary highlight of the Digital Competition Law Report created by the Committee on Digital Competition Law presented to the Parliament in the 2nd week of March 2024 involves a recommendation to introduce new legislation called the ‘Digital Competition Act,’ intended to strike a balance between certainty and flexibility. The report identified ten anti-competitive practices relevant to digital enterprises in India. These are anti-steering, platform neutrality/self-preferencing, bundling and tying, data usage (use of non-public data), pricing/ deep discounting, exclusive tie-ups, search and ranking preferencing, restricting third-party applications and finally advertising Policies.
Key Take-Aways: Digital Competition Bill, 2024
- Qualitative and quantitative criteria for identifying Systematically Significant Digital Enterprises, if it meets any of the specified thresholds.
- Financial thresholds in each of the immediately preceding three financial years like turnover in India, global turnover, gross merchandise value in India, or global market capitalization.
- User thresholds in each of the immediately preceding 3 financial years in India like the core digital service provided by the enterprise has at least 1 crore end users, or it has at least 10,000 business users.
- The Commission may make the designation based on other factors such as the size and resources of an enterprise, number of business or end users, market structure and size, scale and scope of activities of an enterprise and any other relevant factor.
- A period of 90 days is provided to notify the CCI of qualification as an SSDE. Additionally, the enterprise must also notify the Commission of other enterprises within the group that are directly or indirectly involved in the provision of Core Digital Services, as Associate Digital Enterprises (ADE) and the qualification shall be for 3 years.
- It prescribes obligations for SSDEs and their ADEs upon designation. The enterprise must comply with certain obligations regarding Core Digital Services, and non-compliance with the same shall result in penalties. Enterprises must not directly or indirectly prevent or restrict business users or end users from raising any issue of non-compliance with the enterprise’s obligations under the Act.
- Avoidance of favouritism in product offerings by SSDE, its related parties, or third parties for the manufacture and sale of products or provision of services over those offered by third-party business users on the Core Digital Service in any manner.
- The Commission will be having the same powers as vested to a civil court under the Code of Civil Procedure, 1908 when trying a suit.
- Penalty for non-compliance without reasonable cause may extend to Rs 1 lakh for each day during which such non-compliance occurs (max. of Rs 10 crore). It may extend to 3 years or with a fine, which may extend to Rs 25 crore or with both. The Commission may also pass an order imposing a penalty on an enterprise (not exceeding 1% of the global turnover) in case it provides incorrect, incomplete, misleading information or fails to provide information.
Suggestions and Recommendations
- The ex-ante model of regulation needs to be examined for the Indian scenario and studies need to be conducted on it has worked previously in different jurisdictions like the EU.
- The Bill should be aimed at prioritising the fostering of fair competition by preventing monopolistic practices in digital markets exclusively. A clear distinction from the already existing Competition Act, 2002 in its functioning needs to be created so that there is no overlap in the regulations and double jeopardy is not created for enterprises.
- Restrictions on tying and bundling and data usage have been shown to negatively impact MSMEs that rely significantly on big tech to reduce operational costs and enhance customer outreach.
- Clear definitions of "dominant position" and "anti-competitive behaviour" are essential for effective enforcement in terms of digital competition need to be defined.
- Encouraging innovation while safeguarding consumer data privacy in consonance with the DPDP Act should be the aim. Promoting interoperability and transparency in algorithms can prevent discriminatory practices.
- Regular reviews and stakeholder consultations will ensure the law adapts to rapidly evolving technologies.
- Collaboration with global antitrust bodies which is aimed at enhancing cross-border regulatory coherence and effectiveness.
Conclusion
The need for a competition law that is focused exclusively on Digital Enterprises is the need of the hour and hence the Committee recommended enacting the Digital Competition Act to enable CCI to selectively regulate large digital enterprises. The proposed legislation should be restricted to regulate only those enterprises that have a significant presence and ability to influence the Indian digital market. The impact of the law needs to be restrictive to digital enterprises and it should not encroach upon matters not influenced by the digital arena. India's proposed Digital Competition Bill aims to promote competition and fairness in the digital market by addressing anti-competitive practices and dominant position abuses prevalent in the digital business space. The Ministry of Corporate Affairs has received 41-page public feedback on the draft which is expected to be tabled next year in front of the Parliament.
References
- https://www.medianama.com/wp-content/uploads/2024/03/DRAFT-DIGITAL-COMPETITION-BILL-2024.pdf
- https://prsindia.org/files/policy/policy_committee_reports/Report_Summary-Digital_Competition_Law.pdf
- https://economictimes.indiatimes.com/tech/startups/meity-meets-india-inc-to-hear-out-digital-competition-law-concerns/articleshow/111091837.cms?from=mdr
- https://www.mca.gov.in/bin/dms/getdocument?mds=gzGtvSkE3zIVhAuBe2pbow%253D%253D&type=open
- https://www.barandbench.com/law-firms/view-point/digital-competition-laws-beginning-of-a-new-era
- https://www.linkedin.com/pulse/policy-explainer-digital-competition-bill-nimisha-srivastava-lhltc/
- https://www.lexology.com/library/detail.aspx?g=5722a078-1839-4ece-aec9-49336ff53b6c

Executive Summary:
A social media video claims that India's Udhampur Air Force Station was destroyed by Pakistan's JF-17 fighter jets. According to official sources, the Udhampur base is still fully operational, and our research proves that the video was produced by artificial intelligence. The growing problem of AI-driven disinformation in the digital age is highlighted by this incident.

Claim:
A viral video alleges that Pakistan's JF-17 fighter jets successfully destroyed the Udhampur Air Force Base in India. The footage shows aircraft engulfed in flames, accompanied by narration claiming the base's destruction during recent cross-border hostilities.

Fact Check :
The Udhampur Air Force Station was destroyed by Pakistani JF-17 fighter jets, according to a recent viral video that has been shown to be completely untrue. The audio and visuals in the video have been conclusively identified as AI-generated based on a thorough analysis using AI detection tools such as Hive Moderation. The footage was found to contain synthetic elements by Hive Moderation, confirming that the images were altered to deceive viewers. Further undermining the untrue claims in the video is the Press Information Bureau (PIB) of India, which has clearly declared that the Udhampur Airbase is still fully operational and has not been the scene of any such attack.

Our analysis of recent disinformation campaigns highlights the growing concern that AI-generated content is being weaponized to spread misinformation and incite panic, which is highlighted by the purposeful misattribution of the video to a military attack.
Conclusion:
It is untrue that the Udhampur Air Force Station was destroyed by Pakistan's JF-17 fighter jets. This claim is supported by an AI-generated video that presents irrelevant footage incorrectly. The Udhampur base is still intact and fully functional, according to official sources. This incident emphasizes how crucial it is to confirm information from reliable sources, particularly during periods of elevated geopolitical tension.
- Claim: Recent video footage shows destruction caused by Pakistani jets at the Udhampur Airbase.
- Claimed On: Social Media
- Fact Check: False and Misleading
