
#FactCheck-False Claim Says 20,000 Sikh and Muslim Soldiers Resigned from Indian Army
Executive Summary
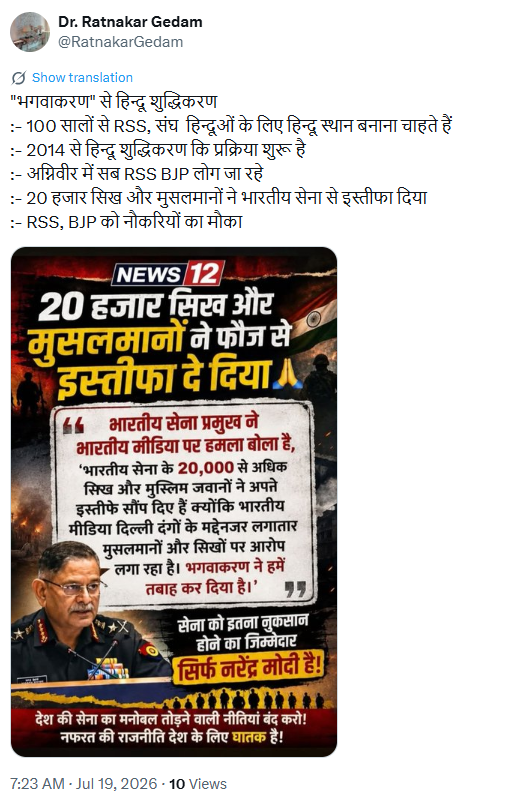
A claim is being widely circulated on social media alleging that more than 20,000 Sikh and Muslim personnel have resigned from the Indian Army.The viral graphic further attributes a statement to Chief of Army Staff General Upendra Dwivedi, claiming that the resignations were triggered by Indian media allegedly blaming Muslims and Sikhs for the Delhi riots. The graphic also includes the alleged remark that “Bhagwakaran (saffronisation) has destroyed us.” Several social media users are sharing the claim as genuine. CyberPeace Rresearch Wing ’s research found the viral claim to be false. Our research revealed that there is no credible evidence to support the allegation that more than 20,000 Sikh and Muslim soldiers resigned from the Indian Army. We found no official statement from the Indian Army or the Ministry of Defence confirming such resignations. Additionally, the statement attributed to Chief of Army Staff General Upendra Dwivedi has been fabricated and does not appear in his original speech. The viral claim is therefore misleading and based on false information.
Claim
An X user shared the viral graphic with the caption, “Under the guise of ‘Bhagwakaran’ (saffronisation), RSS has wanted a Hindu Rashtra for 100 years. Since 2014, the process of ‘Hindu purification’ has begun. Agniveer recruitment is being filled with RSS-BJP supporters. Twenty thousand Sikh and Muslim soldiers have resigned from the Indian Army, creating job opportunities for RSS and BJP supporters.”
Post Link:
https://x.com/RatnakarGedam/status/2078659496801661426?s=20
https://archive.ph/submit/?url
Fact Check
To verify the claim, we conducted keyword-based searches on Google using terms related to the alleged resignation of 20,000 Sikh and Muslim soldiers from the Indian Army. Our search found no credible news reports supporting the claim. We also found no official statement from the Indian Army or the Ministry of Defence confirming that such resignations had taken place. During the research , we located the original video of General Upendra Dwivedi, published by the news agency IANS. In the video, the Army Chief is addressing the Delhi Defence Dialogue, where he discusses modern warfare, emerging military technologies, future security challenges, and land warfare strategy.
His remarks are entirely focused on defence preparedness, technological advancements, and strategic military issues. At no point does he mention the resignation of 20,000 Sikh or Muslim soldiers, the Delhi riots, or any of the claims circulating on social media.
https://x.com/ians_india/status/1988566879053693282?s=20

The viral quote attributed to General Dwivedi does not appear anywhere in his speech and has been fabricated.
Conclusion
Our research found that the claim alleging 20,000 Sikh and Muslim soldiers resigned from the Indian Army is false.There is no credible evidence that such mass resignations took place, and General Upendra Dwivedi never made the statement attributed to him in the viral posts. The claim is based on a fabricated quote and is being circulated to mislead the public.

Related Blogs

In an exciting milestone achieved by CyberPeace, an ICANN APRALO At-Large organization, in collaboration with the Internet Corporation for Assigned Names and Numbers (ICANN), has successfully deployed and made operational an L-root server instance in Ranchi, Jharkhand. This initiative marks a significant step toward enhancing the resilience, speed, and security of internet connectivity in eastern India.
Understanding the DNS hierarchy – Starting from Root
Internet users access online information through different domain names and interactions with any web browser takes place through IP (Internet Protocol) addresses. Domain Name System (DNS) functions as the internet's equivalent of Yellow Pages or the phonebook of cyberspace. When a person uses a domain name like www.cyberpeace.org to access a website, their browser communicates with the internet protocol, and DNS converts the domain name to the corresponding IP address so that web browsers may load the web pages. The function of a DNS is to convert domain names to Internet Protocol addresses. It enables the respective browsers to load the resources from the Internet.
When a user types a domain name into your browser, a DNS query works behind the scenes to find the website’s IP address. First, your device asks a DNS resolver—often provided by your ISP or a third-party service—for the address. The resolver checks its cache for a match, and if none is found, it queries a root server to locate the top-level domain (TLD) server (like .com or .org). The resolver then asks the TLD server for the Authoritative nameserver responsible for the particular domain, which provides the specific IP address. Finally, the resolver sends this address back to your device, enabling it to connect to the website’s server and load the page. The entire process happens in milliseconds, ensuring seamless browsing.

Special focus on Root Server:
A root server is a name server that directly answers queries for records in the root zone and redirects requests for more specific domains to the appropriate top-level domain (TLD) servers. Root servers are an integral part of this system, acting as the first step in resolving a domain name into its corresponding IP address. They provide the initial direction needed to locate the authoritative servers for any domain.
The DNS root zone is served by 13 unique IP addresses, supported by hundreds of redundant root servers distributed worldwide connected through Anycast Routing to manage requests efficiently. As of January 8, 2025, the global root server system consists of 1921 instances operated by 12 independent root server operators. These servers ensure the smooth functioning of the internet by managing the backbone of DNS queries.

Type of Root Server Instances:
Well, in this regard, there are two types of root server instances that can be found– Global instance and Local instance.
Global root server instances are the primary root servers distributed strategically around the world. Local instances, on the other hand, are replicas of these global servers deployed in specific regions to handle local DNS traffic more efficiently. In each operator's list of sites, some instances are marked as global (globe icon) and some are marked as local (flag icon). The difference is in how widely available that instance will be, because of how routing for that instance is done. Recall that the routes for an instance are announced by BGP, the inter-domain routing protocol.
For global instances, the route advertisement is permitted to spread throughout the Internet, i.e., any router on the Internet could know the path to that instance. Of course, for a particular source, the route to that instance may not be the optimal route, so some other instance could be chosen as the destination.
With a local instance, however, the route advertisement is limited to only nearby networks. For example, the instance may be visible to just one ISP, or to ISPs that connect at a particular exchange point. Sources from farther away will not be able to see and query that local instance.
Deployment in Ranchi - The Journey & Significance:
CyberPeace in Collaboration with ICANN has successfully deployed an L-root server instance in Ranchi, marking a significant milestone in enhancing regional Internet infrastructure. This deployment, part of a global network of root servers, ensures faster and more reliable DNS query resolution for the region, reducing latency and enhancing cybersecurity.

The Journey of deploying the L-Root instance in Collaboration with ICANN followed the steps-
- Signing the Agreement: Finalized the L-SINGLE Hosting Agreement with ICANN to formalize the partnership.
- Procuring the Hardware: Acquired the required hardware appliance to meet technical standards for hosting the L-root server.
- Setup and Installation: Configured and installed the appliance to prepare it for seamless operation.
- Joining the Anycast Network: Integrated the server into ICANN's global Anycast network using BGP (Border Gateway Protocol) for efficient DNS traffic management.
The deployment of the L-root server in Ranchi marks a significant boost to the region’s digital ecosystem. It accelerates DNS query resolution, reducing latency and enhancing internet speed and reliability for users.
This instance strengthens cyber defenses by mitigating Distributed Denial of Service (DDoS) risks and managing local traffic efficiently. It also underscores Eastern India’s advanced digital infrastructure, aligning with initiatives like Digital India to meet evolving digital demands.
By handling local queries, the L-root server eases the load on global servers, contributing to a more stable and resilient global internet.
CyberPeace’s Commitment to a Secure and resilient Cyberspace
As an organization dedicated to promoting peace, security and resilience in cyberspace, CyberPeace views this collaboration with ICANN as a significant achievement in its mission. By strengthening the internet’s backbone in eastern India, this deployment underscores our commitment to enabling a secure, accessible, and resilient digital ecosystem.
Way forward and Roadmap for Strengthening India’s DNS Infrastructure:
The successful deployment of the L-root instance in Ranchi is a stepping stone toward bolstering India's digital ecosystem. CyberPeace aims to promote awareness about DNS infrastructure through workshops and seminars, emphasizing its critical role in a resilient digital future.
With plans to deploy more such root server instances across India, the focus is on expanding local DNS infrastructure to enhance efficiency and security. Collaborative efforts with government agencies, ISPs, and tech organizations will drive this vision forward. A robust monitoring framework will ensure optimal performance and long-term sustainability of these initiatives.
Conclusion
The deployment of the L-root server instance in Eastern India represents a monumental step toward strengthening the region’s digital foundation. As Ranchi joins the network of cities hosting root server instances, the benefits will extend not only to the local community but also to the global internet ecosystem. With this milestone, CyberPeace reaffirms its commitment to driving innovation and resilience in cyberspace, paving the way for a more connected and secure future.
Introduction
For more than 10 years, WhatsApp has been designed around one seemingly trivial but impactful idea: your phone number is your digital identity. This concept offered simplicity in terms of contact discovery and onboard- ing but inevitably exposed users to fraud, spam and the everyday necessity of sharing personal phone numbers with complete strangers in group chats and conversations. On June 29th Meta finally revealed a major move: you’ll now be able to choose and reservate a WhatsApp username and communicate without sharing your phone number.
This shift to a username based identity marks the company catching up to platforms like Telegram and Signal, which have utilized this functionality for years.
However, while presented as a push towards greater privacy for the millions using its platform, this new change has already created some alarm around impersonation, cybersquatting, and identity theft. The issues became amplified when, according to reports, the Indian Ministry of Electronics and Information Technology advised WhatsApp to halt the implementation of the new features while it clarifies details, shifting a mundane app update into a high-stakes discussion on digital privacy, platform responsibility, and government regulation.
How does the mechanism work?
“WhatsApp’s username is an added pseudonym layer on its current phone number architecture, not a replacement,” Meta said in a statement on Thursday, as reported by TechCrunch. A WhatsApp username is a three to 35-character name containing lower case letters, numbers, periods and underscores that must contain at least one letter and “should not look like a website address.” The feature will allow you to “reserve a unique identifier that you can share as an alternative to your phone number in WhatsApp Settings - Accounts - Username.”
It said the usernames will work in parallel with a username key which can serve as a passphrase to initiate conversation “with a recipient before sending a message for the first time.”
“The change - which will have some additional, protective measures like reserving usernames for people of public interest or those that would cause impersonation, and rate limits on claiming names - can help maintain phone number protection, while offering people more choices,” Meta said. WhatsApp said usernames will replace phone numbers as the primary way to initiate new chats, but will not be publicly searchable: “Anyone you message would need your exact username, and would still need you to respond.”
The Genuine Privacy Case
The upside is real. Phone numbers double as keys to two-factor authentication, banking apps and SIM-swap fraud, so handing one to a new acquaintance, a group chat of strangers or a customer-support bot has always carried quiet risk. Numbers harvested from public groups already fuel spam and scam campaigns, and a username-first model narrows that exposure considerably.
For journalists, small business owners and anyone who fields messages from people they've never met, decoupling identity from a number that also unlocks their bank account is a meaningful, overdue shift – and one that WhatsApp's closest competitors adopted years ago without major incident.
The Scammer's Paradise Scenario
The trouble lies in what a username removes. A phone number was never just an identifier; it was also a rough verification signal and, for law enforcement, a traceable data point. Security reporters testing the reservation system found that lookalike handles mimicking prominent Indian politicians, film stars and the Reserve Bank of India remained available to claim. Crypto executive Changpeng Zhao's own failed bid to capture his desired handle highlighted the first-come, first-served danger of the rollout and led researchers to advise people to manually activate the optional username key that Meta leaves disabled by default.
The Mozilla Foundation was unvarnished about the tradeoff, noting that impersonation from fake accounts and scams are an “inevitable consequence” of a design that abandons the “implicit signal of authenticity” that comes from owning a phone number.
Indian entrepreneur Ankur Warikoo called the rollout a potential “disaster” if robust enforcement against fraud isn’t immediately applied because scammers could register handles a few characters removed from a popular brand or public figure to launch investment and payment schemes, a concern mirrored by cyber security researchers who observed that many users neglect to check verification badges before trusting an account.
India's Regulatory Scrutiny of WhatsApp's Username Feature
So far the strongest reaction comes from New Delhi. The Ministry of Electronics and Information Technology (MeitY) issued an official notice to Meta's compliance office that it should “temporarily suspend the feature” in the country pending further consultations and “provided an explanation in three days”. The cited concerns involve “digital arrest” fraud, a rapid boom category that involves crooks impersonating investigators like those with India's CBI, judges or customs agents to extort victims, in addition to standard concerns around phishing and bank or government impersonation.
A subtler concern, for India’s government anyway, is “traceability.”
At present, say officials, an Indian mobile number is a launching pad to determine whether a given suspect is a domestic or international actor, while a username and foreign SIM would leave authorities nowhere to begin. The Department of Telecommunications independently voiced concerns over how the change intersects with its SIM-binding regulations and over WhatsApp's lag time for such requests. The MeitY notice, the legal basis for which, incidentally, is in contention with some digital rights groups, specifically invokes Section 79 of the IT Act and various IT Rules from 2021 and provisions on identity theft and impersonation that target individual criminals rather than the tech tools. Not everyone, however, shares MeitY’s reading of the legal ground: the Internet Freedom Foundation says that Section 79 “deal with liability of intermediary” and “does not confer on the government power to license the features of a product,” while arguing the relevant criminal statutes were designed to criminalize impersonators, not tech platforms whose services are misused, echoing concerns that killed a similar government advisement about AI models last spring.
In the meantime, Meta says usernames are unavailable in the country for now and the multilayered safeguards it designed were always intended for exactly this level of risk.
Conclusion
WhatsApp's username feature is neither a total privacy upgrade nor a major security problem; instead, it reallocates risk, reducing phone number exposure while adding a risk of identity spoofing and misuse. Whether it pays off will hinge on the strength of Meta's crackdown on fraudulent usernames, the uptake of extra security features like the username key and whether the company can adequately satisfy regulatory concerns about traceability and user safety. Until all those questions are fully settled, users may want to use the feature tentatively, secure a desired username, enable any other protections and be watchful about new contacts.
References
- https://blog.whatsapp.com/its-time-to-reserve-your-whatsapp-username
- https://www.businesstoday.in/technology/news/story/whatsapp-usernames-why-indias-top-creators-fear-scams-impersonation-and-identity-theft-540359-2026-07-02
- https://www.outlookindia.com/national/outlook-explains-why-is-the-indian-government-worried-about-whatsapp-usernames
- https://techcrunch.com/2026/06/29/whatsapp-now-lets-you-reserve-usernames/
- https://bestmediainfo.com/mediainfo/mediainfo-digital/whatsapp-says-username-feature-not-live-yet-after-meity-asks-meta-to-pause-rollout-12124813
Executive Summary
Amid rising tensions in the Middle East following attacks on Iran by the United States and Israel, a video is being shared on social media claiming that it shows a recent attack at Dubai International Airport. Research by the CyberPeace found the viral claim to be false. Our research revealed that the viral video is not real but has been created using artificial intelligence technology.
Claim:
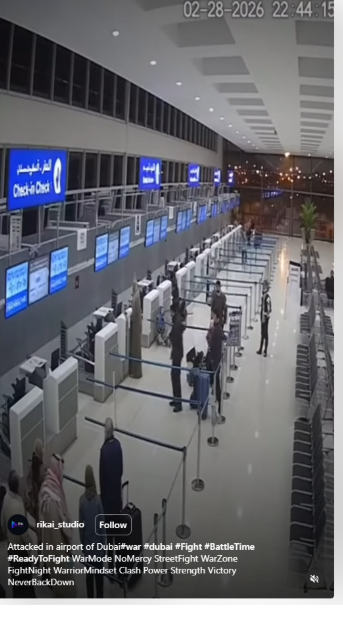
An Instagram user shared the viral video on March 1, 2026, claiming it shows an attack at Dubai Airport. The link to the post, the archive link, and a screenshot are provided below.
Fact Check:
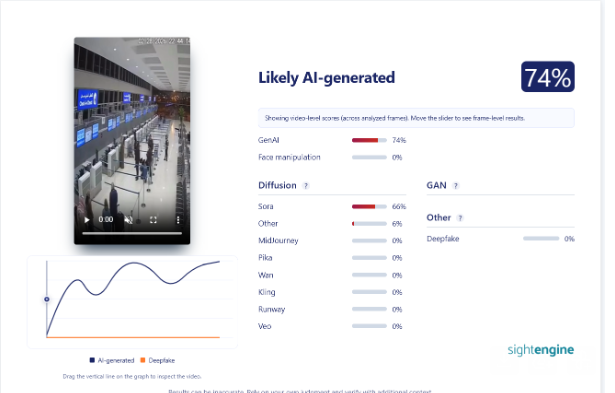
To verify the viral claim, we searched Google using relevant keywords. However, we did not find any credible media report confirming the claim.On closely examining the viral video, we noticed several unusual visuals and technical inconsistencies, raising suspicion that it might be AI-generated. To verify this, we scanned the video using the AI detection tool Sightengine. According to the results, around 74 percent of the video shows the likelihood of being AI-generated.
Conclusion:
Our research found that the viral video is not real but has been created using artificial intelligence technology.
