
#FactCheck -Digitally Altered MEA Briefing Video Falsely Attributes AI-Generated Remarks on Quad and India–US Relations
Executive Summary
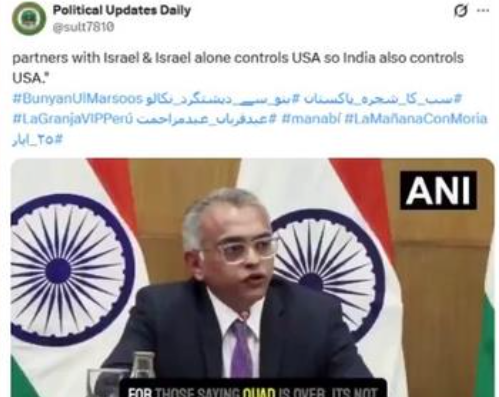
A video of an Additional Secretary in the Ministry of External Affairs (MEA), handling the Americas & Canada Division, is being widely circulated on social media. The clip is being shared with the claim that he said:“Even if the Quad ends, India will partner only with Israel, and since Israel controls the US, India also controls the US.”The viral post attempts to link this alleged statement to India’s foreign policy. Many users are sharing it as authentic. However, CyberPeace Research Wing research found the claim to be false. The video has been digitally altered, and no such statement was made by the official in the original briefing.
Claim
On social media platform X (formerly Twitter), the viral video is being shared with the claim that the MEA Additional Secretary said Israel controls the United States, and therefore India also controls the US.
- https://www.facebook.com/61562281661615/videos/1518036689691723/
- https://archive.ph/xGJHa#selection-967.0-978.0
Fact Check
To verify the claim, we extracted key frames from the viral video and conducted a reverse image search. During the research, we found the original video, which was streamed live on May 26, 2026, on the verified YouTube channel of the Ministry of External Affairs (MEA), titled: “Special Briefing by MEA on Quad Foreign Ministers’ Meeting”
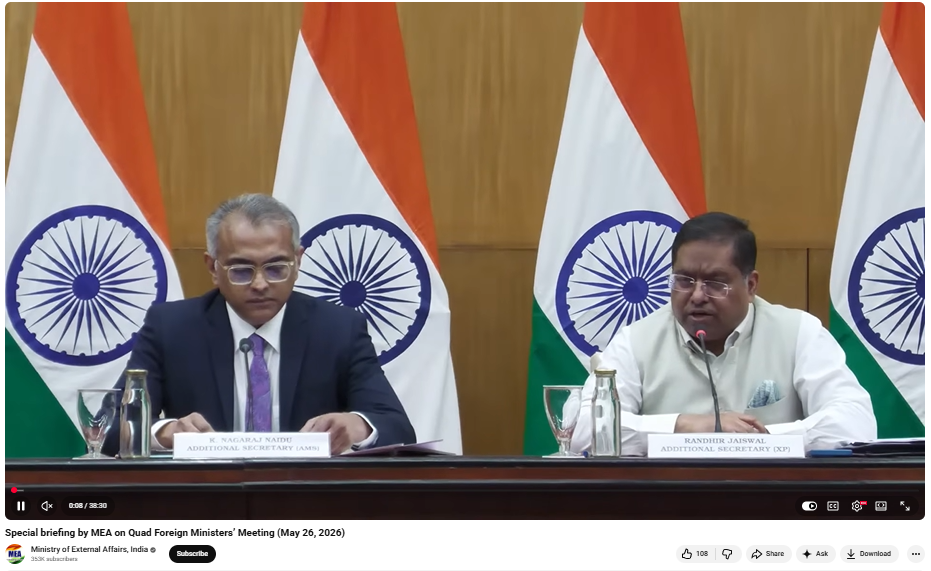
During the briefing, Naidu highlighted India’s commitment to a free and open Indo-Pacific region, mentioning new initiatives in maritime surveillance, critical minerals, and 6G development. He also noted the continued momentum of the Quad, stating that frequent ministerial meetings reflect strong and ongoing cooperation among member countries despite challenges in holding formal leaders’ summits.
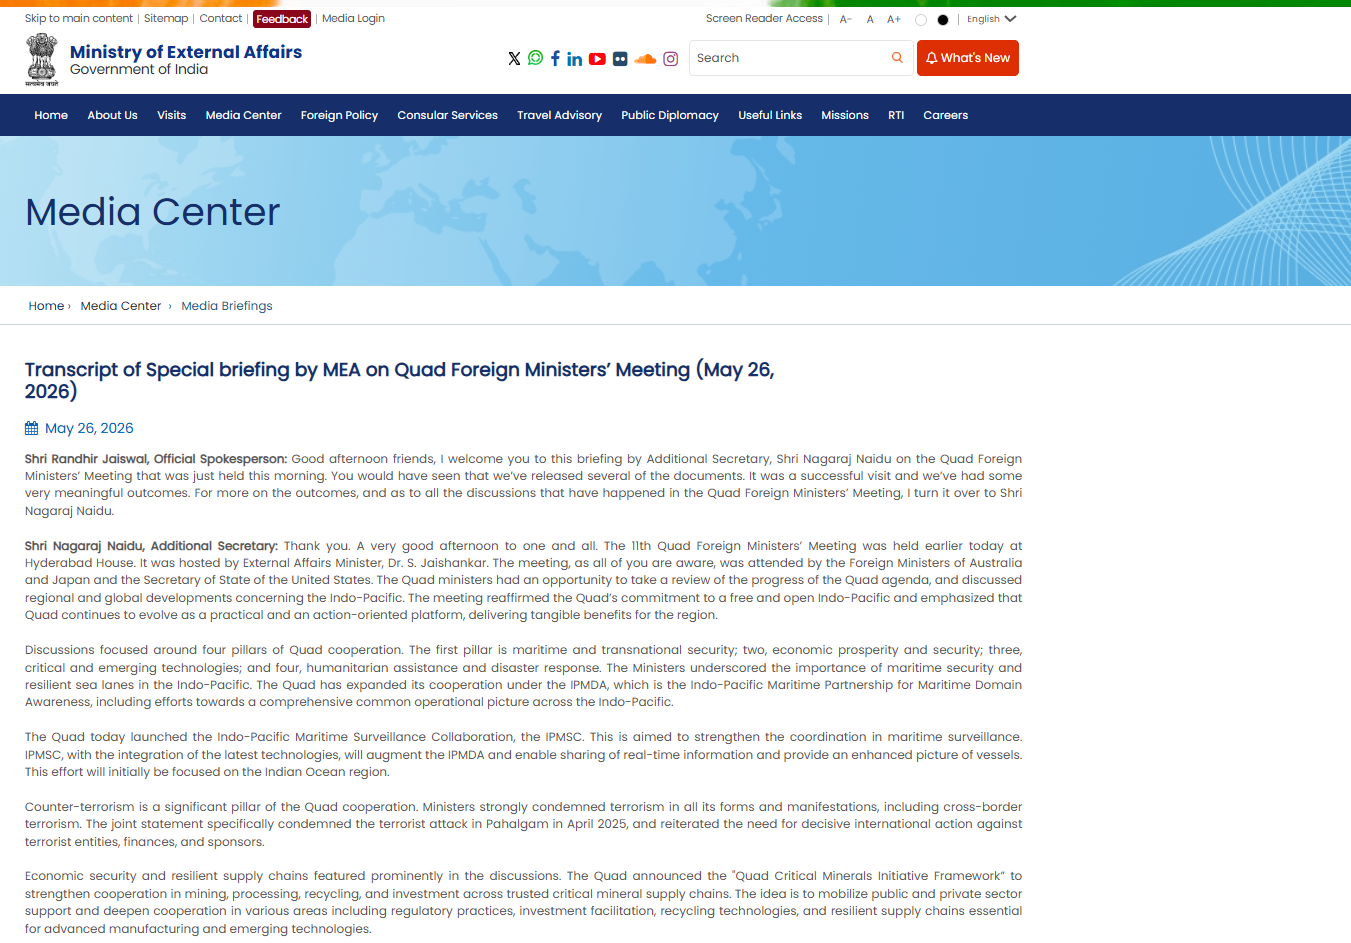
The official transcript of the briefing is also available on the MEA website:
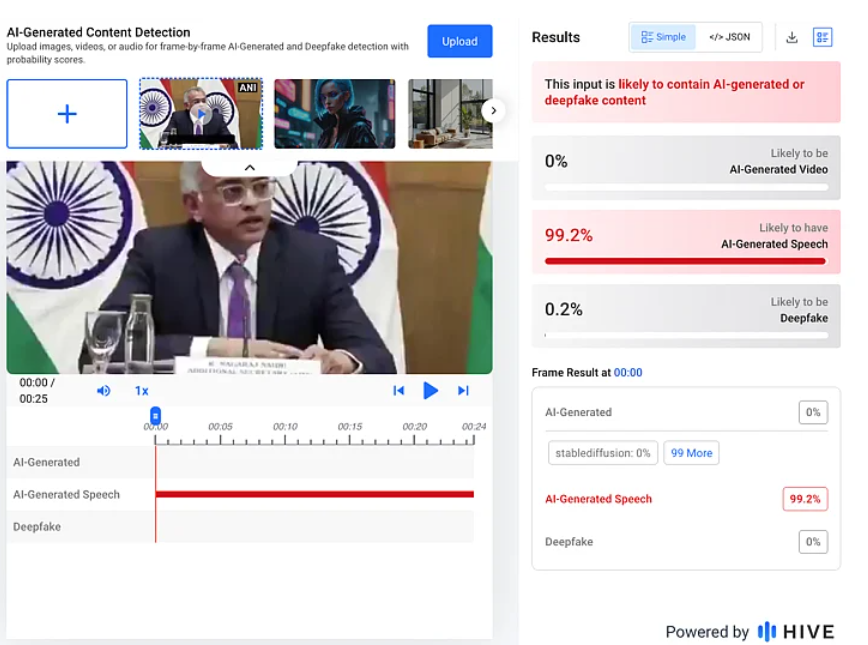
Since the viral statement was never made during the event, we further analysed the video using Deepfake Voice Detector and Hive Moderation’s AI-generated content detection tool. Hive moderation analysis indicated a 99.2% probability that the audio in the viral video is AI-generated.
Conclusion
CyberPeace Research Wing research found that the viral video is digitally altered. The Additional Secretary did not make any such statement during the official briefing. The audio in the clip has been manipulated and is being circulated with a misleading narrative.

Related Blogs
Executive Summary
A letter purportedly issued by the Embassy of Italy in New Delhi is being widely shared on social media. The letter claims that the embassy expressed “deep concern” and “strong disapproval” over alleged remarks made by Leader of Opposition in the Lok Sabha Rahul Gandhi about Italian Prime Minister Giorgia Meloni. The purported statement says political disagreement is an essential part of democracy, but disrespect toward the Italian prime minister is not acceptable. CyberPeace Research Wing’s research found the viral claim to be false. To verify the authenticity of the purported statement, we first searched the official website and social media accounts of the Embassy of Italy in India using relevant keywords. However, we found no official statement matching the contents of the viral letter or any response from the embassy regarding Rahul Gandhi or Giorgia Meloni.
Claim
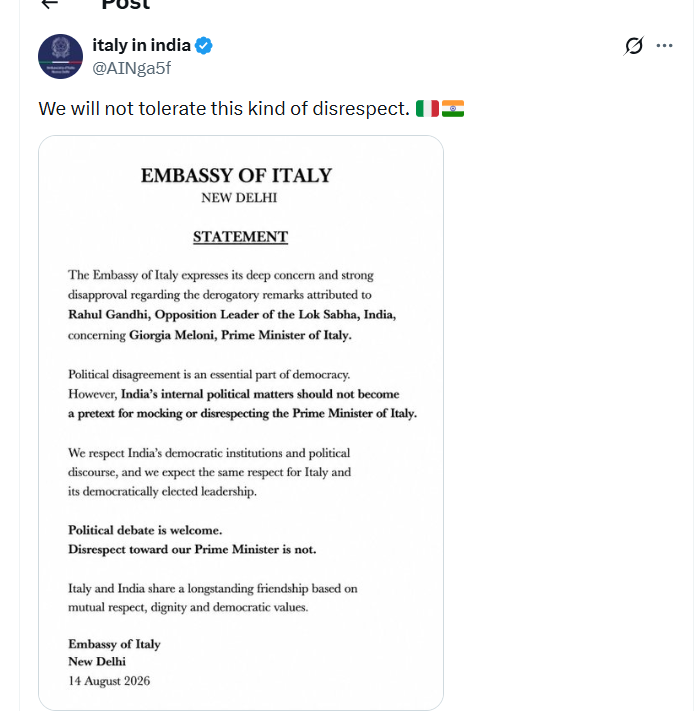
A user on X (formerly Twitter) shared the purported letter claiming that the Embassy of Italy had expressed strong disapproval over Rahul Gandhi’s alleged remarks about Italian Prime Minister Giorgia Meloni.
The purported statement reads: “The Embassy of Italy expresses its deep concern and strong disapproval regarding the derogatory remarks attributed to Rahul Gandhi, Opposition Leader of the Lok Sabha, India, concerning Giorgia Meloni, Prime Minister of Italy.”
It further states that political disagreement is an essential part of democracy but that India’s internal political matters should not become a pretext for mocking or disrespecting the Italian prime minister. The purported statement also says that while political debate is welcome, “disrespect toward our Prime Minister is not.”
https://x.com/AINga5f/status/2088109663128522982?s=20
https://archive.ph/st0qb
FactCheck
To verify the claim, we conducted a Google search using relevant keywords. However, we did not find any credible media report confirming that the Embassy of Italy had issued such a statement.
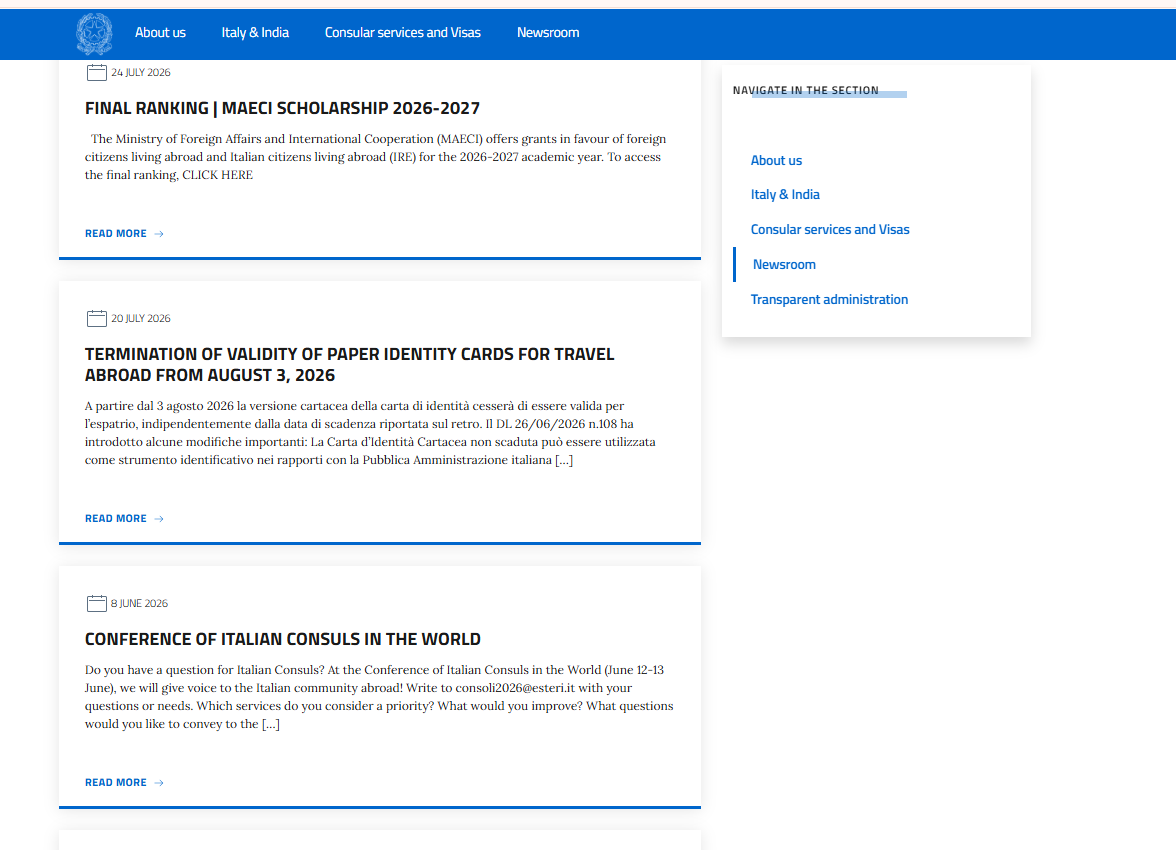
We then checked the official website of the Embassy of Italy in New Delhi for any statement or update concerning Rahul Gandhi or Giorgia Meloni. However, no report or official statement matching the viral letter was found.
https://ambnewdelhi.esteri.it/en/news/
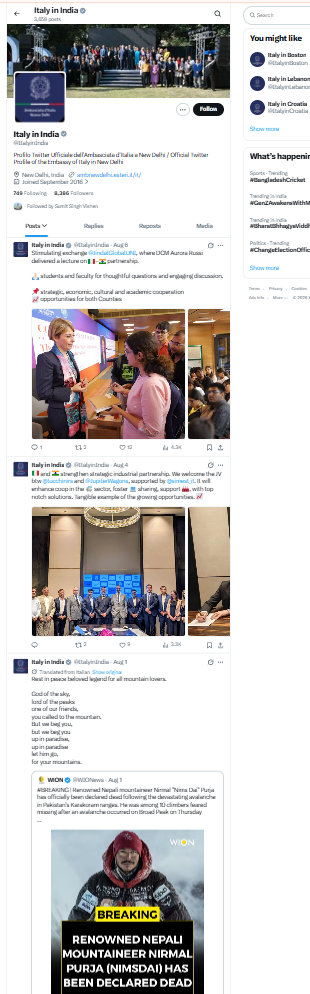
Next, we checked the embassy’s official X account for any post related to the alleged statement. However, no such post was found on the account.
https://x.com/italyinindia?lang=en
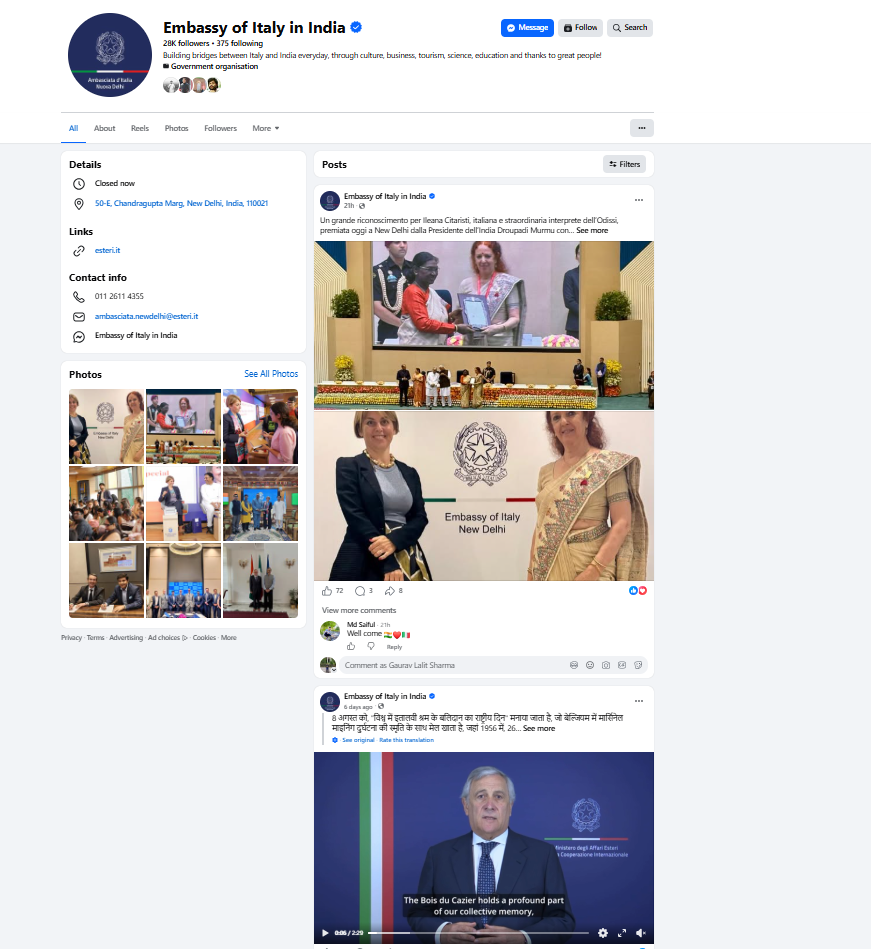
As part of our further research, we checked the official Facebook account of the Embassy of Italy in India. No post or statement confirming the viral claim was found there either.
https://www.facebook.com/ItalyInIndia/
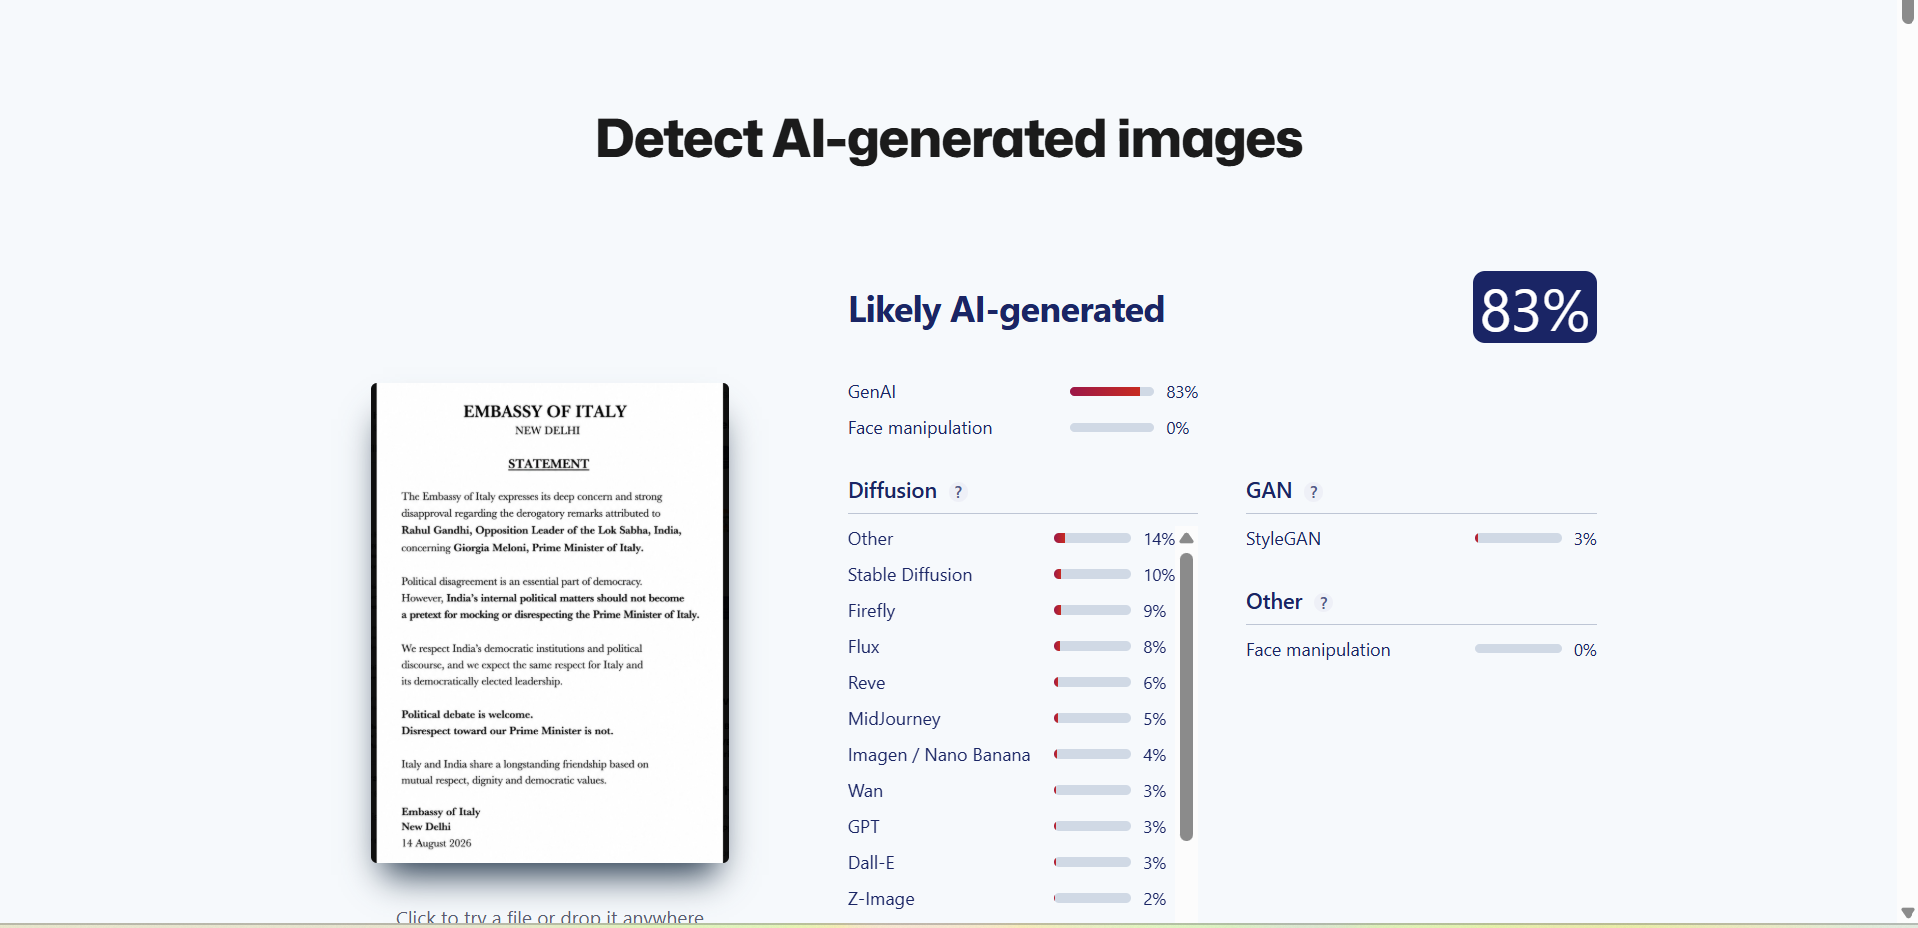
Finally, we scanned the viral letter using the AI-detection tool Sightengine. The tool indicated an 83 per cent probability that the viral letter was AI-generated.
Conclusion
The viral letter attributed to the Embassy of Italy in New Delhi is fake. Our research found no official statement on the embassy’s website or its verified social media accounts confirming the contents of the viral letter. Moreover, the letter was flagged by Sightengine as having an 83 per cent probability of being AI-generated. Therefore, the purported statement should not be considered an authentic communication from the Embassy of Italy.

Introduction
According to Statista, the global artificial intelligence software market is forecast to grow by around 126 billion US dollars by 2025. This will include a 270% increase in enterprise adoption over the past four years. The top three verticals in the Al market are BFSI (Banking, Financial Services, and Insurance), Healthcare & Life Sciences, and Retail & e-commerce. These sectors benefit from vast data generation and the critical need for advanced analytics. Al is used for fraud detection, customer service, and risk management in BFSI; diagnostics and personalised treatment plans in healthcare; and retail marketing and inventory management.
The Chairperson of the Competition Commission of India’s Chief, Smt. Ravneet Kaur raised a concern that Artificial Intelligence has the potential to aid cartelisation by automating collusive behaviour through predictive algorithms. She explained that the mere use of algorithms cannot be anti-competitive but in case the algorithms are manipulated, then that is a valid concern about competition in markets.
This blog focuses on how policymakers can balance fostering innovation and ensuring fair competition in an AI-driven economy.
What is the Risk Created by AI-driven Collusion?
AI uses predictive algorithms, and therefore, they could lead to aiding cartelisation by automating collusive behaviour. AI-driven collusion could be through:
- The use of predictive analytics to coordinate pricing strategies among competitors.
- The lack of human oversight in algorithm-induced decision-making leads to tacit collusion (competitors coordinate their actions without explicitly communicating or agreeing to do so).
AI has been raising antitrust concerns and the most recent example is the partnership between Microsoft and OpenAI, which has raised concerns among other national competition authorities regarding potential competition law issues. While it is expected that the partnership will potentially accelerate innovation, it also raises concerns about potential anticompetitive effects such as market foreclosure or the creation of barriers to entry for competitors and, therefore, has been under consideration in the German and UK courts. The problem here is in detecting and proving whether collusion is taking place.
The Role of Policy and Regulation
The uncertainties induced by AI regarding its effects on competition create the need for algorithmic transparency and accountability in mitigating the risks of AI-driven collusion. It leads to the need to build and create regulatory frameworks that mandate the disclosure of algorithmic methodologies and establish a set of clear guidelines for the development of AI and its deployment. These frameworks or guidelines should encourage an environment of collaboration between competition watchdogs and AI experts.
The global best practices and emerging trends in AI regulation already include respect for human rights, sustainability, transparency and strong risk management. The EU AI Act could serve as a model for other jurisdictions, as it outlines measures to ensure accountability and mitigate risks. The key goal is to tailor AI regulations to address perceived risks while incorporating core values such as privacy, non-discrimination, transparency, and security.
Promoting Innovation Without Stifling Competition
Policymakers need to ensure that they balance regulatory measures with innovation scope and that the two priorities do not hinder each other.
- Create adaptive and forward-thinking regulatory approaches to keep pace with technological advancements that take place at the pace of development and allow for quick adjustments in response to new AI capabilities and market behaviours.n
- Competition watchdogs need to recruit domain experts to assess competition amid rapid changes in the technology landscape. Create a multi-stakeholder approach that involves regulators, industry leaders, technologists and academia who can create inclusive and ethical AI policies.
- Businesses can be provided incentives such as recognition through certifications, grants or benefits in acknowledgement of adopting ethical AI practices.
- Launch studies such as the CCI’s market study to study the impact of AI on competition. This can lead to the creation of a driving force for sustainable growth with technological advancements.
Conclusion: AI and the Future of Competition
We must promote a multi-stakeholder approach that enhances regulatory oversight, and incentivising ethical AI practices. This is needed to strike a delicate balance that safeguards competition and drives sustainable growth. As AI continues to redefine industries, embracing collaborative, inclusive, and forward-thinking policies will be critical to building an equitable and innovative digital future.
The lawmakers and policymakers engaged in the drafting of the frameworks need to ensure that they are adaptive to change and foster innovation. It is necessary to note that fair competition and innovation are not mutually exclusive goals, they are complementary to each other. Therefore, a regulatory framework that promotes transparency, accountability, and fairness in AI deployment must be established.
References
- https://www.thehindu.com/sci-tech/technology/ai-has-potential-to-aid-cartelisation-fair-competition-integral-for-sustainable-growth-cci-chief/article69041922.ece
- https://www.marketsandmarkets.com/Market-Reports/artificial-intelligence-market-74851580.html
- https://www.ey.com/en_in/insights/ai/how-to-navigate-global-trends-in-artificial-intelligence-regulation#:~:text=Six%20regulatory%20trends%20in%20Artificial%20Intelligence&text=These%20include%20respect%20for%20human,based%20approach%20to%20AI%20regulation.
- https://www.business-standard.com/industry/news/ai-has-potential-to-aid-fair-competition-for-sustainable-growth-cci-chief-124122900221_1.html
Introduction
The Digital Personal Data Protection (DPDP) Act 2023 of India is a significant transition for privacy legislation in this age of digital data. A key element of this new law is a requirement for organisations to have appropriate, user-friendly consent mechanisms in place for their customers so that collection, use or removal of an individual's personal data occurs in a clear and compliant manner. As a means of putting this requirement into practice, the Ministry of Electronics and Information Technology (MeitY) issued a comprehensive Business Requirements Document (BRD) in June 2025 to guide organizations, as well as Consent Managers, on how to create a Consent Management System (CMS). This document establishes the technical and functional framework by which organizations and individuals (Data Principals) will exercise control over the way their data is gathered, used and removed.
Understanding the BRD and Its Purpose
BRD represents an optional guide created as part of the "Code for Consent" programme run by MeitY in India. The purpose of the BRD is to provide guidance to startups, digital platforms and other enterprises on how to create a technology system that supports management of user consent per the requirements of the DPDP Act. Although the contents of the BRD do not carry any legal weight, it lays out a clear path for organisations to create their own consent mechanisms using best practices that align with the principles of transparency, accountability and purpose limitation in the DPDP Act.
The goal is threefold:
- Enable complete consent lifecycle management from collection to withdrawal.
- Empower individuals to manage their consents actively and transparently.
- Support data fiduciaries and processors with an interoperable system that ensures compliance.
Key Components of the Consent Management System
The BRD proposes the development of a modular Consent Management System (CMS) that provides users with secure APIs and user-friendly interfaces. This system will allow for a variety of features and modules, including:
- Consent Lifecycle Management – consent should be specific, informed and tied to an explicit purpose. The CMS will manage the collection, validation, renewal, updates and withdrawal of consent. Each transaction of consent will create a tamper-proof “consent artifact,” which will include the timestamp of creation as well as an ID identifying the purpose for which it was given.
- User Dashboard – A user will be able to view and modify the status of their active, expired or withdrawn consent and revoke access at any time via the multilingual user-friendly interface. This would make the system accessible to people from different regions and cultures.
- Notification Engine – The CMS will automatically notify users, fiduciaries and processors of any action taken with respect to consent, in order to ensure real-time updates and accountability.
- Grievance Redress Mechanism – The CMS will include a complaints mechanism that allows users to submit complaints related to the misuse of consent or the denial of their rights. This will enable tracking of the complaint resolution status, and will allow for escalation if necessary.
- Audit and Logging – As part of the CMS's internal controls for compliance and regulatory purposes, the CMS must maintain an immutable record of every instance of consent for auditing and regulatory review. The records must be encrypted, time-stamped, and linked permanently to a user and purpose ID.
- Cookie Consent Management – A separate module will enable users to manage cookie consent for websites separately from any other consents.
Roles and Responsibilities
The BRD identifies the various stakeholders involved and their associated responsibilities.
- Data Principals (Users): The user has full authority to give, withhold, amend, or revoke their consent for the use of their personal data, at any time.
- Data Fiduciaries (Companies): Companies (the fiduciaries) must collect the data principals' consents for each particular reason and must only begin processing a data subject's personal data after validating that consent through the CMS. Companies must also provide the data principals with any information or notifications needed, as well as how to resolve their complaints.
- Data Processors: Data Processors must strictly adhere to the consent stated in the CMS, and Data Processors may only process personal data on behalf of the Data Fiduciary.
- Consent Managers: The Consent Managers are independent entities that are registered with the Data Protection Board. They are responsible for administering the CMS, allowing users to manage their consent across different platforms.
This layered structure ensures transparency and shared responsibility for the consent ecosystem.
Technical Specifications and Security
The following principles of the DPDP Act must be followed to remain compliant with the DPDP Act.
- End-to-End Encryption: All exchanges of data with users must be encrypted using a minimum of TSL 1.3 and also encrypting within that standard.
- API-First Approach: API’s will be utilized to validate, withdraw and update consent in a secured manner using external sources.
- Interoperability/Accessibility: The CMS needs to allow for users to utilize several different languages (e.g. Hindi, Tamil, etc.) and be appropriate for use with various types of mobile devices and different abilities.
- Data Retention Policy: The CMS should also include automatic deletion of consent data (when the consent has expired or has been withdrawn) in order to maintain compliance with data retention limits.
Legal Relevance and Timelines
While the BRD itself is not enforceable, it is directly aligned with the upcoming enforcement of the DPDP Act, 2023. The Act was passed in August 2023 but is expected to come into effect in stages, once officially notified by the central government. Draft implementation rules, including those defining the role of Consent Managers, were released for public consultation in early 2025.
For businesses, the BRD serves as an early compliance tool—offering both a conceptual roadmap and technical framework to prepare before the law is enforced. Legal experts have described it as a critical resource for aligning data governance systems with emerging regulatory expectations.
Implications for Businesses
Organizations that collect and process user data will be required to overhaul their consent workflows:
- No blanket consents: Every data processing activity must have explicit, separate consent.
- Granular audit logs: Companies must maintain tamper-proof logs for every consent action.
- Integration readiness: Enterprises need to integrate their platforms with third-party or in-house CMS platforms via the specified APIs.
- Grievance redress and user support: Systems must be in place to handle complaints and withdrawal requests in a timely, verifiable manner.
Failing to comply once the DPDP Act is in force may expose companies to penalties, reputational damage, and potential regulatory action.
Conclusion
The BRD on Consent Management of India is a forward-looking initiative laying a technological framework that is an essential component of the DPDP Act concerning user consent; Although not yet a legal document, it provides an extent of going into all the necessary discipline for companies to prepare. As data protection grows in importance, developing consent mechanisms based on security, transparency, and the needs of the user is no longer just a regulatory requirement, but rather a requirement for the development of trust. This is the time for businesses to establish or implement CMS solutions that support this objective to be better equipped for the future of data governance in India.
References
- https://d38ibwa0xdgwxx.cloudfront.net/whatsnew-docs/8d5409f5-d26c-4697-b10e-5f6fb2d583ef.pdf
- https://ssrana.in/articles/ministry-releases-business-requirement-document-for-consent-management-under-the-dpdp-act-2023/
- https://dpo-india.com/Blogs/consent-dpdpa/
- https://corporate.cyrilamarchandblogs.com/2025/06/the-ghost-in-the-machine-the-recent-business-requirement-document-on-consent/
- https://www.mondaq.com/india/privacy-protection/1660964/analysis-of-the-business-requirement-document-for-consent-management-system
