
#FactCheck - Viral Image of AIMIM President Asaduddin Owaisi Holding Lord Rama Portrait Proven Fake
Executive Summary:
In recent times an image showing the President of AIMIM, Asaduddin Owaisi holding a portrait of Hindu deity Lord Rama, has gone viral on different social media platforms. After conducting a reverse image search, CyberPeace Research Team then found that the picture was fake. The screenshot of the Facebook post made by Asaduddin Owaisi in 2018 reveals him holding Ambedkar’s picture. But the photo which has been morphed shows Asaduddin Owaisi holding a picture of Lord Rama with a distorted message gives totally different connotations in the political realm because in the 2024 Lok Sabha elections, Asaduddin Owaisi is a candidate from Hyderabad. This means there is a need to ensure that before sharing any information one must check it is original in order to eliminate fake news.

Claims:
AIMIM Party leader Asaduddin Owaisi standing with the painting of Hindu god Rama and the caption that reads his interest towards Hindu religion.


Fact Check:
In order to investigate the posts, we ran a reverse search of the image. We identified a photo that was shared on the official Facebook wall of the AIMIM President Asaduddin Owaisi on 7th April 2018.

Comparing the two photos we found that the painting Asaduddin Owaisi is holding is of B.R Ambedkar whereas the viral image is of Lord Rama, and the original photo was posted in the year 2018.

Hence, it was concluded that the viral image was digitally modified to spread false propaganda.
Conclusion:
The photograph of AIMIM President Asaduddin Owaisi holding up one painting of Lord Rama is fake as it has been morphed. The photo that Asaduddin Owaisi uploaded on a Facebook page on 7 Apr 2018 depicted him holding a picture of Bhimrao Ramji Ambedkar. This photograph was digitally altered and the false captions were written to give an altogether different message of Asaduddin Owaisi. It has even highlighted the necessity of fighting fake news that has spread widely through social media platforms especially during the political realm.
- Claim: AIMIM President Asaduddin Owaisi was holding a painting of the Hindu god Lord Rama in his hand.
- Claimed on: X (Formerly known as Twitter)
- Fact Check: Fake & Misleading

Related Blogs
Executive Summary
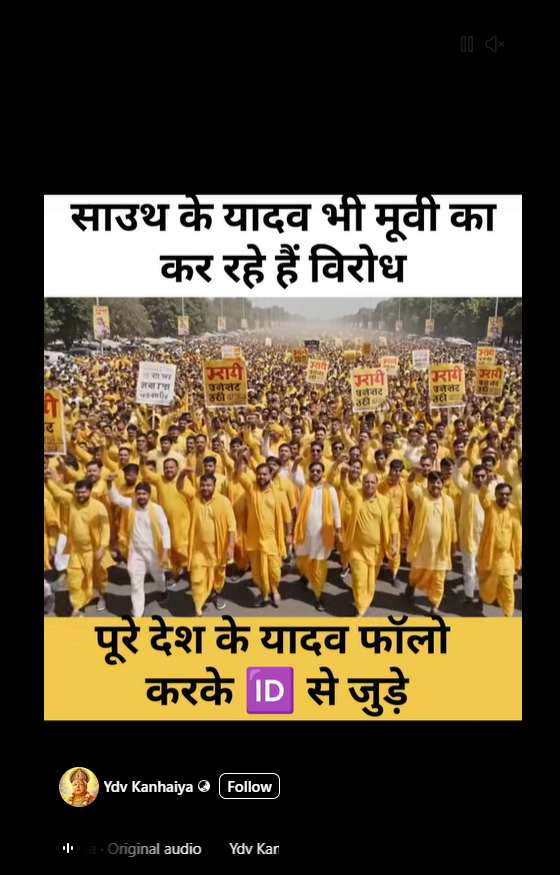
The film ‘Yadav Ji Ki Love Story’, scheduled to release on February 27, has become embroiled in controversy over its title. Several organizations have expressed objections, registering their displeasure regarding the name of the film. Amid the row, a video is being widely circulated on social media. The footage shows a large crowd holding banners and posters while staging a protest. Users sharing the clip claim that it is from South India, where members of the Yadav community have allegedly launched a large-scale agitation against the film. However, research conducted by the CyberPeace found the viral claim to be false. Our research revealed that the video is not authentic but AI-generated, and is being shared with a misleading narrative.
Claim
On February 22, 2026, a Facebook user shared the viral video claiming it depicts protests by the Yadav community in South India against the film. The original and archived links to the post are provided below
Fact Check:
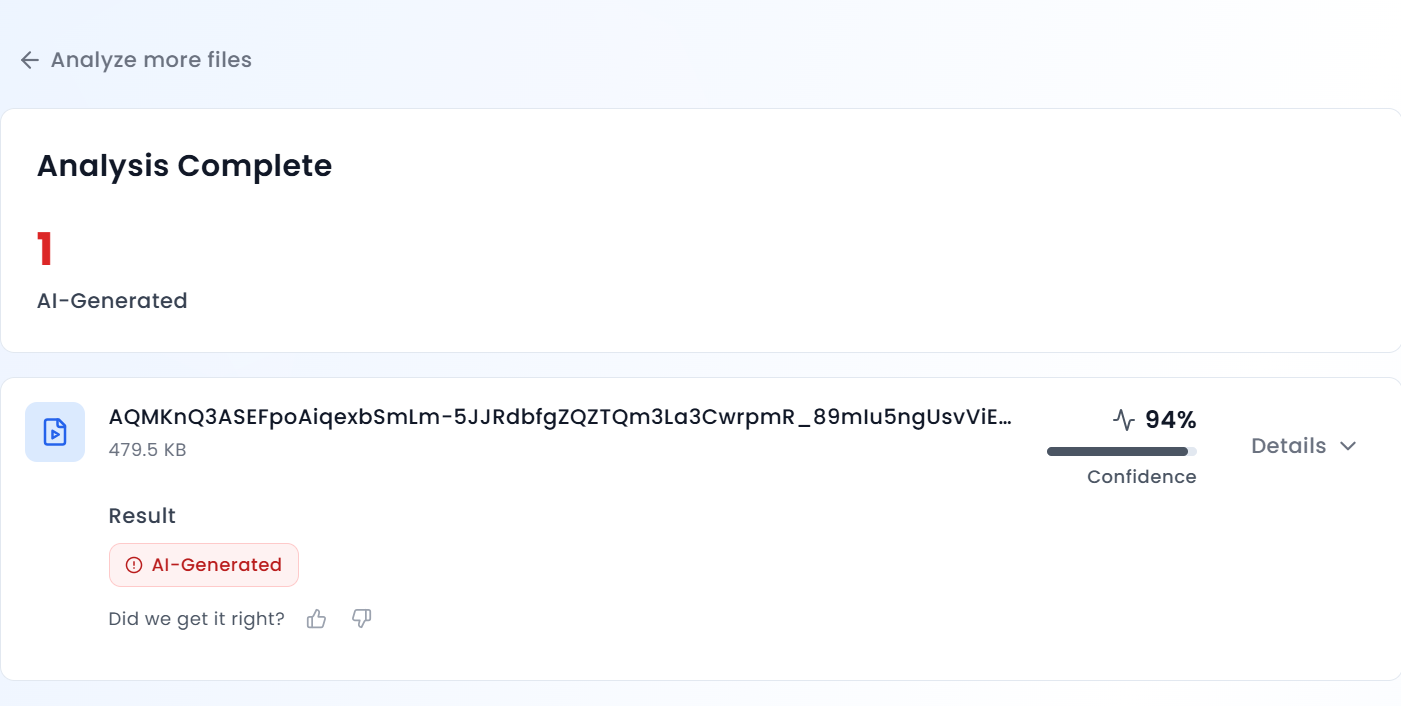
Upon closely examining the viral video, we noticed several anomalies in the visuals, crowd movements, and certain frames. The unnatural patterns and inconsistencies raised suspicions that the footage may have been generated using artificial intelligence. To verify this, we analyzed the video using the AI detection tool Aurigin AI, which indicated that the footage was AI-generated.
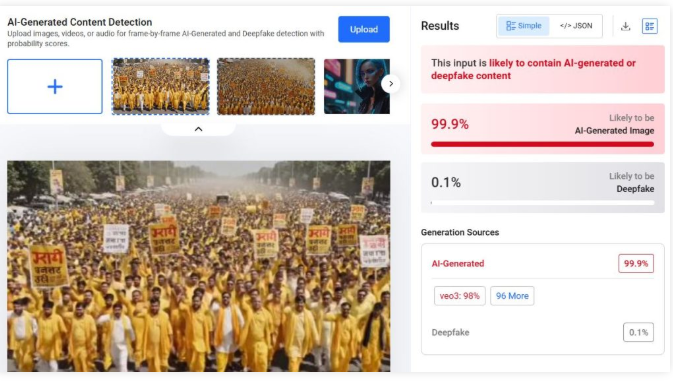
We further scanned the clip using another AI detection platform, Hive Moderation. The results showed a 99 percent probability that the video was AI-generated.
Conclusion
Our findings confirm that the viral video is not real. It has been artificially created using AI technology and is being circulated with a false and misleading claim.

Introduction
Google is set to change its storage and access of users' "Location History" in Google Maps, reducing the data retention period and making it impossible for the company to access it. This change will significantly impact "geofence warrants," a controversial legal tool used by authorities to force Google to hand over information about all users within a given location during a specific timeframe. This decision is a significant win for privacy advocates and criminal defense attorneys who have long decried these warrants.
The company aims to protect people's privacy by removing the repository of location data dating back months or years. Geofence warrants, which provide police with sensitive data on individuals, are considered dangerous and could turn innocent people into suspects.
Understanding Geofence Warrants
Geofence warrants, also known as reverse-location warrants, are used by law enforcement agencies to obtain locational data stored by tech companies within a specified geographical area and timeframe to identify devices near a crime scene. In contrast to general warrants, which allow law enforcement agencies to obtain data of one individual (usually the suspect), geofence warrants enable law enforcement authorities to obtain data for all individuals in a specific location and subsequently track and trace any device that may be linked to a crime scene. Geofence warrants have become a major issue, with law enforcement agencies utilising them to obtain location data from tech companies.
Privacy Concerns of Geofence Warrants
While Geofence warrants allow law enforcement agencies to determine and identify potential suspects, these warrants have sparked controversy for their invasive characteristics. Civil rights activities and various technology companies have raised concerns over the impact of these warrants on the rights of data principals. It is noted that geofence warrants mark a rise in cases of state surveillance and police harassment. Not only is any data principal in the vicinity of the crime scene classified as a potential suspect, but companies are also compelled to submit identifying personal data on every device/phone in a marked geographic space.
From Surveillance to Safeguards
Geofence warrants have become a contentious tool for law enforcement worldwide, with concerns over privacy and civil liberties, especially in sensitive situations like protests and healthcare. Google is considering allowing users to store their location data on their devices, potentially ending the use of geofence warrants, which law enforcement agencies use to obtain location data from tech companies.
Google is changing its handling of Location History data, moving it on-device instead of on its servers. The default data retention period will be reduced. Google Maps' product director, Marlo McGriff, stated that the company will automatically encrypt backed-up data for cloud backups, preventing anyone from reading it. When these changes are implemented, Google will have no geodata fishing options for users. Google confirmed that it will no longer be able to respond to new geofence warrants once these changes are implemented, as it will not have access to the relevant data. The changes were designed to put an end to dragnet searches of location data.
Conclusion
Google's decision to change storage and access policies for users' location history in Google Maps marks a pivotal step in the ongoing narrative of law enforcement's misuse of geofence warrants. This move aims to safeguard individual privacy by significantly restricting the data retention period and limiting Google's ability to comply with geofence warrants. This change is welcomed by privacy advocates and legal professionals who express concerns over the intrusive nature of these warrants, which may potentially turn innocent individuals into suspects based on their proximity to a crime scene. As technology companies take steps to enhance user privacy, the evolving landscape calls for a balance between law enforcement needs and protecting individual rights in an era of increasing digital surveillance.
References:
- https://telecom.economictimes.indiatimes.com/news/internet/google-to-end-geofence-warrant-requests-for-users-location-data/106081499
- https://www.forbes.com/sites/cyrusfarivar/2023/12/14/google-just-killed-geofence-warrants-police-location-data/?sh=313da3c32c86
- https://timesofindia.indiatimes.com/gadgets-news/explained-how-google-maps-is-preventing-authorities-from-accessing-users-location-history-data/articleshow/106086639.cms
Introduction
Every domain of conflict has eventually had to learn restraint. The first Geneva Convention of 1864 grew out of one man's horror at what he saw after a single battle, and it rested on an idea that has since become the backbone of humanitarian law: even in war, there are things that must not be done to people. Cyberspace is the newest domain to face that test, and it is arguably the hardest. Code carries no uniform, an intrusion crosses borders without anyone noticing, and the same network can serve a soldier, a shopkeeper and a schoolchild at once. Whether the actor is a criminal group, an intelligence service or a military cyber unit, the consequences land on ordinary people. That is the case for a humanitarian approach to cyberspace, and it is why it has moved from a courtesy to a matter of national security.
Why the humanitarian lens matters to every nation
Cyberspace does not sort itself into civilian and military zones. The International Committee of the Red Cross (ICRC) has pointed out for years that military networks lean on civilian cyber infrastructure such as undersea cables, satellites and routers, while civilian supply chains and essential services run over the same channels. A cyber operation aimed at one can land on the other, and the ICRC has warned that incidental harm in this domain risks being widespread and crossing national borders.
It helps to separate three situations, because different rules govern each. Cybercrime, such as ransomware against a hospital, is a matter for criminal law and international police cooperation. Intrusion and espionage in peacetime fall under domestic law and the norms of responsible state behaviour agreed at the United Nations. Cyber operations during an armed conflict fall under international humanitarian law (IHL), which the ICRC and a growing number of states hold applies to cyber means just as it applies to any other weapon or method of warfare. Its core principles, humanity, necessity, proportionality and distinction, were linked to cyberspace in the 2021 report of the UN Group of Governmental Experts. Under those principles civilians and civilian infrastructure must not be attacked, and medical facilities enjoy special protection.
For a nation, the practical point is simpler. Its own hospitals, grids, water systems and payment networks are exactly the assets that erode first when restraint erodes. A country that argues for humanitarian limits is protecting itself as much as anyone else.
A lesson from Lebanon
The events of 17 and 18 September 2024 in Lebanon show what happens when everyday technology stops being trustworthy. On the first day, thousands of pagers detonated across the country within roughly an hour of each other. The next day, hand held radios followed. By the account UN High Commissioner for Human Rights Volker Türk gave the Security Council on 20 September, at least 37 people had been killed, including two children, and more than 3,400 had been injured in Lebanon alone. UN experts noted that medical personnel were among the dead.
Attribution in this case remained a matter of public allegation rather than official claim, and this piece does not try to settle it. What matters here is the method and how the UN read it legally. Türk told the Council that IHL prohibits booby traps in the form of apparently harmless portable objects designed and constructed to contain explosives, and that violence intended to spread terror among civilians is a war crime. He added that striking thousands of people simultaneously, without knowing who held the devices, where they were or who stood nearby, violates international human rights law and, where applicable, IHL. His summary was that this cannot become the new normal, and he called for an independent, thorough and transparent investigation.
The pager episode was physical, with explosives concealed in hardware, not malicious code. It belongs in a discussion of cyberspace because of how it worked: a compromised supply chain turned an ordinary civilian communication tool into a weapon. That is the same trust relationship every digital system depends on. When people cannot assume that the devices and software they use are what they appear to be, the line between civilian object and military instrument, the foundation of humanitarian law, survives on paper while wearing away in practice.
The Digital Emblem Project
What it is:Think of the red cross on a hospital roof or an ambulance. It tells anyone who sees it that the building or vehicle is protected and must not be attacked. The Digital Emblem is the same idea for computer systems. It is a digital marker, built on a cryptographic signature, that a protected server or network broadcasts to signal that it belongs to a medical or humanitarian organisation entitled to protection under international humanitarian law. The organisations allowed to use it are the same ones entitled to use the physical emblem.
What it aims to achieve:Its purpose is recognition. Someone probing a network cannot see a red cross, and may not realise they have entered a medical facility's systems or a Red Cross office. The digital emblem lets that fact be detected and verified by machines, so a military cyber unit or any other operator can recognise the system and avoid it. It does not create any new legal protection, and it does not replace cybersecurity. Like the physical emblem, it cannot stop an attack on its own. It makes existing protection visible.
Why it was created:The physical emblem has worked for more than 150 years, but it has no natural place online. Cyber operations are becoming a regular feature of armed conflict, and humanitarian bodies are targeted by criminals seeking money as well as by state linked actors. The ICRC learned this directly in 2022, when a breach of its own servers exposed the data of more than 515,000 people in vulnerable situations. It began researching a digital equivalent and, with ETH Zurich, developed a technical standard.
Where it stands today:The idea has moved from concept to working prototype. In October 2024, Resolution 2 was adopted at the International Conference of the Red Cross and Red Crescent, which includes all 196 states party to the Geneva Conventions, affirming that the duty to respect and protect medical services and humanitarian personnel applies to their use of information and communication technologies. In July 2026, the ICRC, with Microsoft's support, presented the emblem in Geneva and announced the next phase, with several national Red Cross societies already testing it. That phase is expected to take several years. Technical standards still need to be developed through bodies such as the International Telecommunication Union and the Internet Engineering Task Force, and international law would need to recognise the emblem formally, through an amendment to the Geneva Conventions framework or a new protocol.
For nations, the emblem offers a practical way to mark hospital and humanitarian networks as off limits, and it removes the excuse of not knowing when a marked system is attacked. That makes accountability clearer. It also supports the central argument of this piece: humanitarian principles only work in cyberspace if they can be seen and acted on, not just written down. Its success will depend on whether the people it addresses, state cyber forces and criminal groups alike, choose to honour it, which is why adoption and enforcement at national level will matter as much as the technology.
What nations can do now
None of this requires waiting for a new treaty. A country can publicly state its national position on how international law, including IHL, applies to cyber operations, since the ICRC itself treats the publication of national views as a form of capacity building. It can classify healthcare, humanitarian, water and energy networks as protected critical infrastructure in its national cyber strategy, and plan to adopt the digital emblem for its own hospitals as standards mature. It can invest in supply chain assurance for the devices and software that civilians and governments depend on, which is the most direct lesson of the Lebanon episode. It can ensure that military cyber units are trained in IHL and that cyber capabilities undergo legal review with an eye to humanitarian impact. And it can treat ransomware against hospitals as the serious crime it is, backed by international cooperation on evidence and victim protection.
Conclusion
A humanitarian approach to cyberspace is sometimes dismissed as idealism. It is closer to enlightened self interest. Every state relies on the reciprocal restraint that keeps hospitals, grids and communications networks out of the crossfire, and every state is, at some point, on the receiving end of the alternative. The Lebanon episode showed how quickly trust in ordinary technology can fail, and the Digital Emblem shows one way the international community is trying to rebuild it. Nations that commit early, in doctrine, in procurement and in practice, will help decide whether cyberspace develops guardrails or simply learns to live without them. The idea behind the first Geneva Convention was that even conflict has limits. Cyberspace is where that argument now needs to be made again.
References
- ICRC, "ICRC proposes digital red cross/crescent emblem to signal protection in cyberspace." https://www.icrc.org/en/document/icrc-proposes-digital-red-crosscrescent-emblem-signal-protection-cyberspace
- ETH Zurich, "Digital emblem for humanitarian law in cyberspace." https://ethz.ch/en/news-and-events/eth-news/news/2023/11/digital-emblem-for-humanitarian-law-in-cyberspace.html
- Digital Watch Observatory, "ICRC unveils digital emblem to protect humanitarian organisations online." https://dig.watch/updates/icrc-digital-emblem-cybersecurity
- Geneva Solutions, "ICRC and Microsoft launch digital emblem to prevent cyberattacks." https://genevasolutions.news/peace-humanitarian/icrc-and-microsoft-launch-digital-emblem-to-prevent-cyberattacks
- "Making humanitarian protection visible in cyberspace: The promise of the Digital Emblem." https://blogs.microsoft.com/on-the-issues/2026/07/09/making-humanitarian-protection-visible-in-cyberspace-the-promise-of-the-digital-emblem/
- ICRC Humanitarian Law and Policy Blog, "IHL's lighthouse: navigating towards a digital emblem." https://blogs.icrc.org/law-and-policy/2026/01/15/ihls-lighthouse-navigating-towards-a-digital-emblem/
- Digital Watch Observatory, "Building Trust and Protection for Essential Digital Services: From Standards to Deployment." https://dig.watch/event/wsis-forum-2026/building-trust-and-protection-for-essential-digital-services-from-standards-to-deployment
- UN OHCHR, "Exploding pagers and radios: A terrifying violation of international law, say UN experts." https://www.ohchr.org/en/press-releases/2024/09/exploding-pagers-and-radios-terrifying-violation-international-law-say-un
- UN OHCHR, "Disrespect for international law is a matter of international peace and security, High Commissioner Türk tells the UN Security Council." https://www.ohchr.org/en/statements-and-speeches/2024/09/disrespect-for-international-law-a-matter-of-international-peace-and-security-hc
- ASIL Insights, "Cyber Operations under International Humanitarian Law: Perspectives from the ICRC." https://asil.org/insights/volume-24-issue-11/
- Pager Attack in Lebanon, CyberPeace Blog https://cyberpeace.org/resources/blogs/pager-attack-in-lebanon
