
#FactCheck-Video of Traditional Nepalese Festival Falsely Shared as Locals Chasing Away Chinese Soldiers in Arunachal Pradesh
Executive Summary
The Director General (DG) of the Indo-Tibetan Border Police (ITBP), Shatrujeet Singh Kapoor, made a statement in October 2026 regarding the situation along the Line of Actual Control (LAC) between India and China in Arunachal Pradesh. Following this, several social media posts claiming that Chinese troops had intruded into Arunachal Pradesh went viral. Vishvas News found several of these posts to be fake. Now, a video showing several people running in a hilly area is going viral on social media. Some users are sharing it with the claim that locals in Arunachal Pradesh chased away Chinese soldiers who were attempting to intrude into Indian territory. CyberPeace Research found that the viral video is from Nepal. A video of a traditional ceremony in the country is being shared with the false claim that it shows Chinese soldiers attempting to infiltrate Arunachal Pradesh.
Claim:
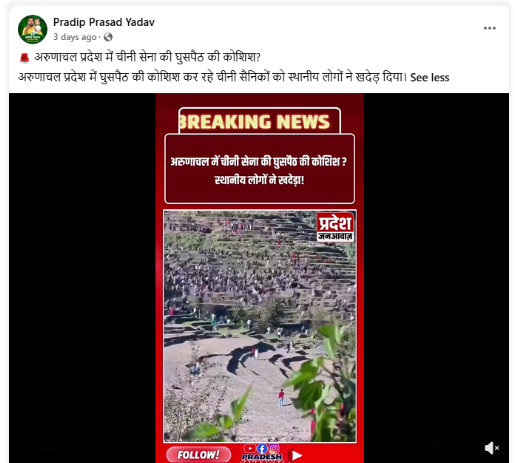
Facebook user ‘Pradip Prasad Yadav’ posted a video on October 27, 2026 (archive link), with the caption: “Attempted Chinese army intrusion in Arunachal Pradesh? Locals chased away Chinese soldiers who were trying to intrude into Arunachal Pradesh.”
https://www.facebook.com/reel/1653642966256321
Fact Check
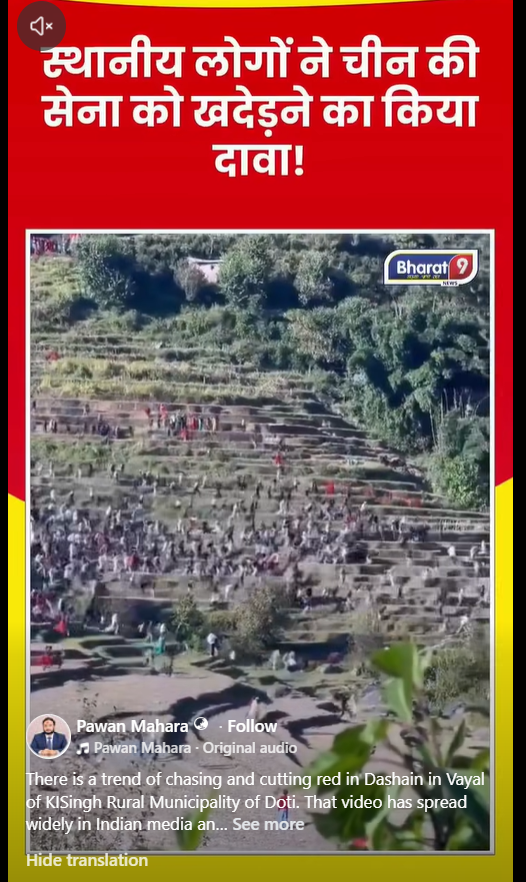
To verify the viral claim, we conducted a reverse image search of the video's keyframes using Google Lens. During the search, we found a post shared on October 28, 2026, by ‘Pawan Mahara’, a resident of Doti, Nepal.
In the post, he wrote: “There is a tradition of chasing animals and sacrificing them during Dashain in the ‘Vayal’ area of K.I. Singh Rural Municipality in Doti, Nepal. A video of this tradition is now going viral on social media, with the false claim that locals are chasing away Chinese soldiers from Arunachal Pradesh, India. The video actually shows the traditional practice of chasing and sacrificing buffaloes during Dashain in Vayal, K.I. Singh Rural Municipality, Doti district, Nepal. However, it is being shared with the misleading claim that locals are driving Chinese soldiers out of Arunachal Pradesh.”
https://www.facebook.com/reel/1719659220161956
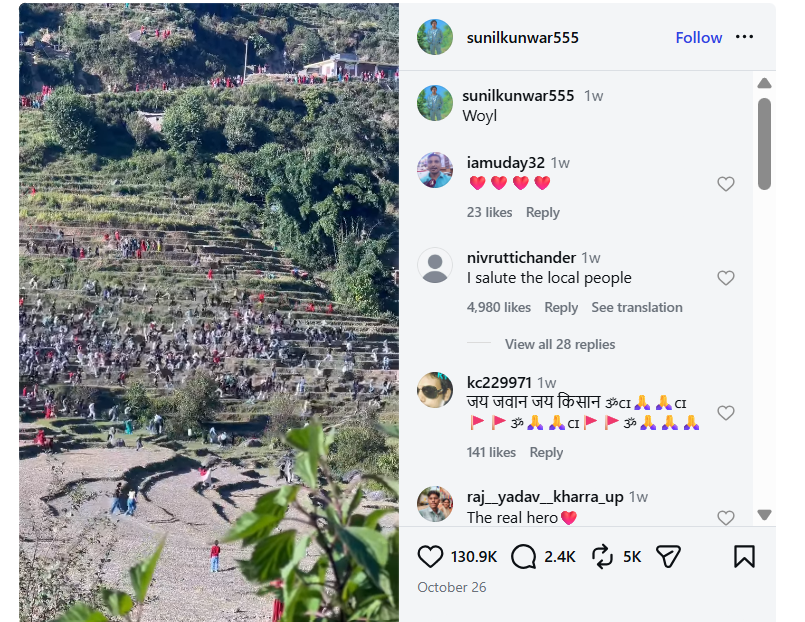
We also found the viral video on the Instagram account of user ‘patel.vishal’. It was posted on October 26, 2026, with the caption “Woyl”.In the comments section, some users identified the video as being from Nepal, while others linked it to a festival. One user commented that people were running after an animal for sacrifice.
https://www.instagram.com/p/De9B3JYuTi4
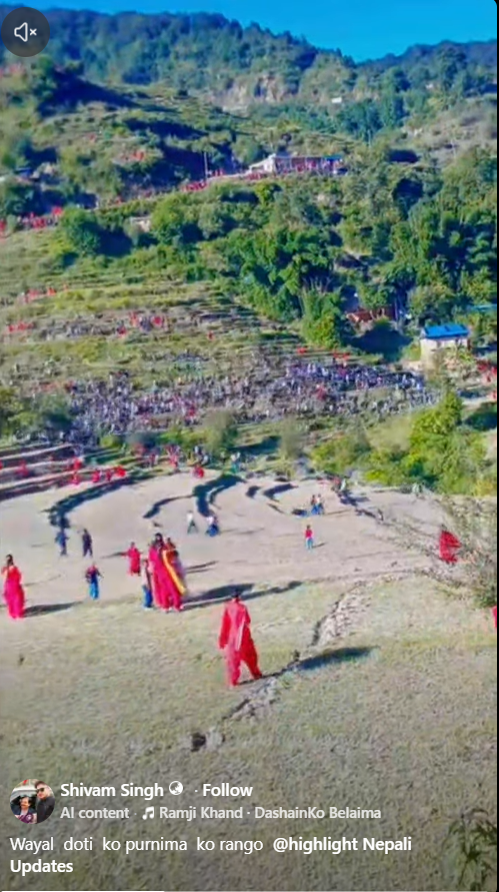
Another Nepal-based user, ‘Shivam Singh’, also posted a video of the same festival on Facebook on October 26, 2026, identifying the location as Vayal in Doti district.
https://www.facebook.com/reel/4596623463802320
Conclusion
A video of a festival in Nepal is being circulated with the false claim that it shows Chinese soldiers attempting to intrude into Arunachal Pradesh.

Related Blogs

Introduction
In an era where digital connectivity drives employment, investment, and communication, the most potent weapon of cybercriminals is ‘gaining trust’ with their sophisticated tactics. Prayagraj has been a recent battleground in India's cybercrime landscape. Within a one-year crackdown, over 10,400 SIM cards, 612 mobile device IMEIs, and 59 bank accounts were blocked, exposing a sprawling international fraud network. These activities primarily targeted unsuspecting individuals through Telegram job postings, fake investment tips, and mobile app scams, highlighting the darker side of convenience in cyberspace. With India now experiencing a wave of scams enabled by technology, this crackdown establishes a precedent for concerted cyber policing and awareness among citizens.
Digital Deceit: How the Scams Operated
SIM cards that have been issued through fake or stolen identities are increasingly being used by cybercriminals in Prayagraj and elsewhere. These SIMs were the initial weapon in a highly organised fraud system, allowing criminals to conduct themselves anonymously while abusing messaging services like WhatsApp and Telegram. The gangs involved in these scams, some of which have been linked by reports to nations like Nepal, Pakistan, China, Dubai, and Myanmar, enticed their victims with rich-yielding stock market advice, remote employment offers, and weekend employment promises. After getting a target engaged, victims were slowly manipulated into sending money in the name of application fees, verification fees, or investment contributions.
API Abuse and OTP Interception
What's more alarming about these scams is their tech-savviness. From Prayagraj's cybercrime squad, several syndicates are reported to have employed API-based mobile applications to intercept OTPs (One-Time Passwords) sent to Indian numbers. Such apps, cleverly disguised as genuine services or work-from-home software, collected personal details like bank account credentials and payment card data, allowing wrongdoers to carry out unauthorised transactions in a matter of minutes. The pilfered funds were then quickly transferred through several mule accounts, rendering the money trail almost untraceable.
The Human Impact: How Citizens Were Trapped
Victims tended to come from job-hunting groups, students, or housewives seeking to earn additional income. Often, the scammers persuaded users to join Telegram channels providing free investment advice or job-referral-based schemes, creating an illusion of authenticity. Once on board, victims were sometimes even paid small commissions initially, creating a false sense of success. This tactic, known as “advance-fee confidence building,” made victims more likely to invest larger sums later, ultimately leading to complete financial loss.
Digital Arrest Threats and Bitcoin Ransom Scams
Aside from investment and job scam complaints, the cybercrime cell also saw several "digital arrest" scams, where victims were forced to send money under the threat of engaging in criminal activities. Bitcoin extortion schemes were also used in some cases, with perpetrators threatening exposure of victims' personal information or browsing history on the internet unless they were paid in cryptocurrency.
Law Enforcement’s Cyber Shield: Local Action, Global Impact
Identifying the extent of the threat, Prayagraj authorities implemented strategic measures to enable local policing. Cyber Units have been formed in each of the 43 police stations in the district, each made up of a sub-inspector, head constable, constable, lady constable, and computer operator. This decentralised model enables response in real-time, improved victim support, and quicker forensic analysis of hacked devices. The nodal officer for cyber operations said that this multi-level action is not punitive but preventive, meant to break syndicates before more harm is caused.
CyberPeace Recommendations: Prevention is Power
As cybercrime gets advanced, citizens will also have to keep pace with it. Prayagraj's experience highlights the importance of public awareness, digital literacy, and instant response processes. To assist in preventing people from falling victim to such scams, CyberPeace advises the following:
- Don't click on dubious APK links sent on WhatsApp or Telegram.
- Do not share OTPs or confidential details, even if the source appears to be familiar.
- Never download unfamiliar apps that demand access to SMS or financial information.
- Block your SIM card, payment cards, and bank accounts at once if your phone is stolen.
- Report all cyber frauds to cybercrime.gov.in or your local Cyber Cell.
- Never join investment or job groups on social sites without verification.
- Refuse video calls from unknown numbers; some scammers use this method of recording or blackmailing victims.
Conclusion
Prayagraj crackdown uncovers both the magnitude and versatility of cybercrime in the present. From trans-border cartels to Telegram job scams, the cyber front is as intricate as ever. But this incident also illustrates what can be achieved when technology, law enforcement, and public awareness come together. To stay safe from cyber threats, a cyber-conscious citizenry is as important as an effective cyber cell for India. At CyberPeace, we know that defending cyberspace begins with cyber resilience, and the story of Prayagraj should encourage communities everywhere to take active digital precautions.
References
- https://www.hindustantimes.com/cities/lucknow-news/over-10k-sims-blocked-as-job-investment-frauds-rise-in-prayagraj-101753715061234.html
- https://consumer.ftc.gov/articles/how-recognize-and-avoid-phishing-scams
- https://faq.whatsapp.com/2286952358121083
- https://education.vikaspedia.in/viewcontent/education/digital-litercy/information-security/preventing-online-scams-cert-in-advisory?lgn=en
- https://cybercrime.gov.in/Accept.aspx
- https://www.linkedin.com/pulse/perils-advance-fee-fraud-protecting-yourself-from-scammers-sharma/
Introduction
On 27 July 2026, Bank of Baroda admitted to experiencing a cybersecurity attack, officially confirming many hours of chatter and speculation amongst Bank of Baroda customers and information security professionals. According to a statement by the bank issued through regulatory filing, the breach came about due to unauthorised access into some of its data via compromise of an employee’s email account; however, not much beyond these details was disclosed. In the meantime, allegations of a major large-scale data leak flooded into various platforms and forums of the cybersecurity world along with mainstream news outlets and, eventually, mainstream social networks. It’s now critically important for us to attempt to differentiate factual from unverified details about Bank of Baroda’s recent cybersecurity incident.
We will analyse and list what the bank has released, what our community research has discovered and also what questions are still left unanswered.
The bank's version
Bank of Baroda said the breach traced back to a single compromised employee email account, which gave an unknown party unauthorised access to "certain data". Crucially, the bank maintains that its core banking systems, that is, the infrastructure that actually moves customer money, were never touched. It says the incident was detected and contained quickly and that it is working with law enforcement and regulators while a forensic investigation continues. That's a fairly narrow admission compared with what had already surfaced on the dark web.
What the hackers claim
Days before the bank's statement, a relatively new ransomware and data-extortion group calling itself ‘TripleX’ listed Bank of Baroda on its dark web leak site, dated July 24. The group claimed to have pulled roughly 1 terabyte of data and, unusually, released the entire cache for free rather than holding it for ransom, framing the move on its leak page as punishment for the bank's weak passwords and security lapses.
Independent researcher Srikanth Lakshmanan, founder of the digital-rights group 'CashlessConsumer', examined samples of the leaked material before alerting the bank and authorities. He told India Today Tech that what he reviewed included internal branch audit files, loan appraisal documents, vigilance investigation records, audit reports tied to the bank's bob World mobile app, and customer account-opening forms.
Several outlets also reported that sample files appeared to contain Aadhaar numbers, customer photographs, and NetBanking details, alongside corporate and NRI banking records. It's worth being precise here, though: Reuters and other outlets have emphasised that the exact contents and true scale of the leak haven't been independently verified, and Bank of Baroda itself hasn't confirmed which specific data categories were exposed. Estimates of the dataset's size have also varied anywhere from around 700 gigabytes to a full terabyte, depending on the source.
A repeat offender
TripleX isn't new to targeting state-owned banks. The gang first appeared in May 2026, and only weeks before targeting Bank of Baroda, it claimed responsibility for hacking PT Bank Negara Indonesia – the largest of Indonesia's state-owned banks, which stole nearly 2 terabytes of documents, including contracts, IDs and transaction histories. Both compromises follow a familiar pattern. Identify one point of entry, extract widely, and instead of working in the background to negotiate for a ransom, publish everything for the largest damage possible.
This represents a notable break from typical ransomware attacks. Groups such as TripleX forego encryption, simply relying solely on the public pressure of (or actuality of) imminent disclosure to extort victims. It is the extortion component of "double extortion" with little incentive to pursue payment.
The regulatory clock
India's banking sector doesn't get much slack when something like this happens. The Reserve Bank of India's Cyber Security Framework for Banks requires an initial incident report within two to six hours of detection, and India's Computer Emergency Response Team (CERT-In) mandates reporting of specified incidents within six hours. Bank of Baroda has also reportedly filed a preliminary notice under a cyber-insurance programme arranged through National Insurance, offering total coverage of roughly $78 million, though it's far too early to know whether it will actually be paid out or how much will actually be paid out.
Looking ahead, India's Digital Personal Data Protection Rules are due to take effect in May 2027, which will tighten breach-notification obligations further. This incident lands right at the edge of that regulatory transition, arguably a preview of what's at stake for the next bank that gets hit.
A History of Data Security Missteps
This is not the first time banks’ technology has raised a red flag. In 2023, an investigation by The Reporters’ Collective and Al Jazeera discovered that bank employees had inserted the mobile numbers of unauthorised agents (including those belonging to staff and security guards) and other businesses into their customers' profiles to drive enrolment on the bank’s app – BoB World. Several of the bank's customers were later victims of fraud due to the unauthorised association of mobile numbers, and the bank had its own internally reported data issues that later led to the RBI mandating an audit and then prohibiting the bank from onboarding new Bob World users temporarily. Even though the two issues are not related, it serves as context; in the case of banks handling more than $300 billion in their global operations through over 8,400 domestic locations, room for security errors is marginal, and the damage, both public and regulatory, escalates from there on.
What it means for customers
For those who bank with the Bank of Baroda, the common-sense approach is checking statements for any unfamiliar transactions; beware unsolicited calls/messages referencing account details (which typically follow after identity document leaks are being used as a basis for secondary scams); and as a security precaution, change your NetBanking password and app PIN while no core systems of the bank are reported to have been breached; even so, it is advisable to apply. Because Aadhaar, if it has been really compromised, cannot be reset like a password, which is why a compromised identity document is typically of longer-term risk than a stolen password.
Conclusion
The bigger story here isn't just one bank's bad week. It's a reminder that in a system where a single compromised employee inbox can cascade into hundreds of gigabytes of exposed customer data, "our core systems weren't affected" is true and reassuring and, for anyone whose loan documents or ID numbers may now be sitting on a dark web forum, somewhat beside the point.
Sources
- Bank of Baroda confirms cyber incident after hackers claim data theft — The Record (Recorded Future News): https://therecord.media/india-bank-of-baroda-reports-cybersecurity-incident
- Bank of Baroda Data Leak: What We Know So Far — Gulf News: https://gulfnews.com/business/banking/bank-of-baroda-data-leak-what-we-know-so-far-about-alleged-cyber-breach-1.500621898
- Bank of Baroda Breach Tests Disclosure Readiness — GovInfoSecurity (ISMG): https://www.govinfosecurity.com/bank-baroda-breach-tests-disclosure-readiness-a-32335
- India's Bank of Baroda Faces Alleged 1TB Data Leak on Dark Web — Yahoo Finance / India Today Tech: https://finance.yahoo.com/technology/ai/articles/india-bank-baroda-faces-alleged-113047992.html
- Bank of Baroda Data Breach Exposes Customer Records — The Asian Banker: https://www.theasianbanker.com/updates-and-articles/india-s-bank-of-baroda-data-breach-exposes-customer-records-after-employee-email-compromise
- India's Bank of Baroda Expose Worsens: Agents Steal Money From Accounts (2023 background) — Al Jazeera: https://www.aljazeera.com/economy/2023/10/12/indias-bank-of-baroda-expose-worsens-agents-steal-money-from-accounts
- 'Immediate Containment Measures Implemented': Bank of Baroda Issues Clarity on Alleged 1TB Data Leak — Republic World: https://www.republicworld.com/business/immediate-containment-measures-implemented-bank-of-baroda-issues-clarity-on-1tb-data-leak-2026-07-27-133590

Introduction
In the labyrinthine world of cybersecurity, a new spectre has emerged from the digital ether, casting a long shadow over the seemingly impregnable orchards of Apple's macOS. This phantom, known as SpectralBlur, is a backdoor so cunningly crafted that it remained shrouded in the obscurity of cyberspace, undetected by the vigilant eyes of antivirus software until its recent unmasking. The discovery of SpectralBlur is not just a tale of technological intrigue but a narrative that weaves together the threads of geopolitical manoeuvring, the relentless pursuit of digital supremacy, and the ever-evolving landscape of cyber warfare.
SpectralBlur, a term that conjures images of ghostly interference and elusive threats, is indeed a fitting moniker for this new macOS backdoor threat. Cybersecurity researchers have peeled back the layers of the digital onion to reveal a moderately capable backdoor that can upload and download files, execute shell commands, update its configuration, delete files, and enter states of hibernation or sleep, all at the behest of a remote command-and-control server. Greg Lesnewich, a security researcher whose name has become synonymous with the relentless pursuit of digital malefactors, has shed light on this new threat that overlaps with a known malware family attributed to the enigmatic North Korean threat actors.
SpectralBlur similar to Lazarus Group’s KANDYKORN
The malware shares its DNA with KANDYKORN, also known as SockRacket, an advanced implant that functions as a remote access trojan capable of taking control of a compromised host. It is a digital puppeteer, pulling the strings of infected systems with a malevolent grace. The KANDYKORN activity also intersects with another campaign orchestrated by the Lazarus sub-group known as BlueNoroff, or TA444, which culminates in the deployment of a backdoor referred to as RustBucket and a late-stage payload dubbed ObjCShellz.
Recently, the threat actor has been observed combining disparate pieces of these two infection chains, leveraging RustBucket droppers to deliver KANDYKORN. This latest finding is another sign that North Korean threat actors are increasingly setting their sights on macOS to infiltrate high-value targets, particularly those within the cryptocurrency and blockchain industries. 'TA444 keeps running fast and furious with these new macOS malware families,' Lesnewich remarked, painting a picture of a relentless adversary in the digital realm.
Patrick Wardle, a security researcher whose insights into the inner workings of SpectralBlur have further illuminated the threat landscape, noted that the Mach-O binary was uploaded to the VirusTotal malware scanning service in August 2023 from Colombia. The functional similarities between KANDYKORN and SpectralBlur have raised the possibility that they may have been built by different developers with the same requirements. What makes the malware stand out are its attempts to hinder analysis and evade detection while using grant to set up a pseudo-terminal and execute shell commands received from the C2 server.
The disclosure comes as 21 new malware families designed to target macOS systems, including ransomware, information stealers, remote access trojans, and nation-state-backed malware, were discovered in 2023, up from 13 identified in 2022. 'With the continued growth and popularity of macOS (especially in the enterprise!), 2024 will surely bring a bevvy of new macOS malware,' Wardle noted, his words a harbinger of the digital storms on the horizon.
Hackers are beefing up their efforts to go after the best MacBooks as security researchers have discovered a brand new macOS backdoor which appears to have ties to another recently identified Mac malware strain. As reported by Security Week, this new Mac malware has been dubbed SpectralBlur and although it was uploaded to VirusTotal back in August of last year, it remained undetected by the best antivirus software until it recently caught the attention of Proofpoint’s Greg Lesnewich.
Lesnewich explained that SpectralBlur has similar capabilities to other backdoors as it can upload and download files, delete files and hibernate or sleep when given commands from a hacker-controlled command-and-control (C2) server. What is surprising about this new Mac malware strain though is that it shares similarities to the KandyKorn macOS backdoor which was created by the infamous North Korean hacking group Lazarus.
Just like SpectralBlur, KandyKorn is designed to evade detection while providing the hackers behind it with the ability to monitor and control infected Macs. Although different, these two Mac malware strains appear to be built based on the same requirements. Once installed on a vulnerable Mac, SpectralBlur executes a function that allows it to decrypt and encrypt network traffic to help it avoid being detected. However, it can also erase files after opening them and then overwrite the data they contain with zeros..
How to keep your Apple computers safe from hackers
As with the best iPhones, keeping your Mac up to date is the easiest and most important way to keep it safe from hackers. Hackers often prey on users who haven’t updated their devices to the latest software as they can exploit unpatched vulnerabilities and security flaws.
Checking to see if you're running the latest macOS version is quite easy. Just click on the Apple Logo in the top right corner of your computer, head to System Preferences and then click on Software Update. If you need a bit more help, check out our guide on how to update a Mac for more detailed instructions with pictures.
Even though your Mac has its own built-in malware scanner from Apple called xProtect, you should consider using one of the best Mac antivirus software solutions for additional protection. Paid antivirus software is often updated more frequently and you often also get access to other extras to help keep you safe online like a password manager or a VPN.
Besides updating your Mac frequently and using antivirus software, you must be careful online. This means sticking to trusted online retailers, carefully checking the URLs of the websites you visit and avoiding opening links and attachments sent to you via email or social media from people you don’t know. Likewise, you should also learn how to spot a phishing scam to know which emails you want to delete right away.
Conclusion
The thing about hackers and other cybercriminals is that they are constantly evolving their tactics and attack methods. This helps them avoid detection and allows them to devise brand-new ways to trick ordinary people. With the surge we saw in Mac malware last year, though, Apple will likely be working on beefing up xProtect and macOS to better defend against these new threats.
References
- https://www.scmagazine.com/news/new-macos-malware-spectralblur-idd-as-north-korean-backdoor
- https://www.tomsguide.com/news/this-new-macos-backdoor-lets-hackers-take-over-your-mac-remotely-how-to-stay-safe
- https://thehackernews.com/2024/01/spectralblur-new-macos-backdoor-threat.html
