
#FactCheck: Video of massive crowd at Kolkata’s Chorbagan Durga Puja pandal falsely shared as gathering in support of CJP against CEC Gyanesh Kumar
Executive Summary
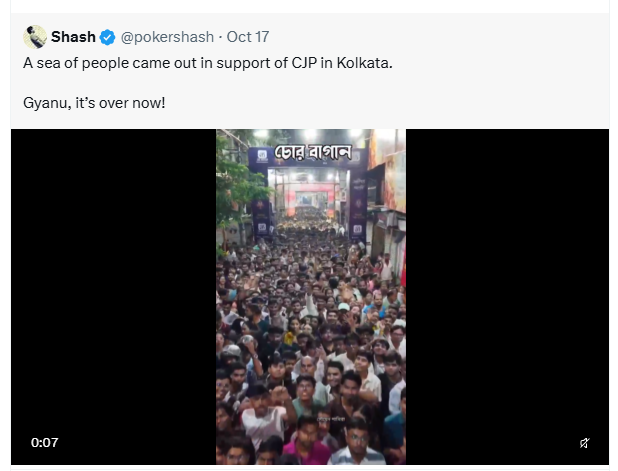
A social media post is going viral, claiming that a large number of people took to the streets in Kolkata in support of CJP. The post targets Chief Election Commissioner Gyanesh Kumar, stating, “Gyanesh Kumar, your game is over now!”
CyberPeace Research found that the viral video is not related to any protest against Chief Election Commissioner Gyanesh Kumar. The video shows a public Durga Puja celebration at Chorbagan in Kolkata, where a large number of people had gathered.
Claim:
A large number of people took to the streets in Kolkata in support of CJP. The protesters targeted Chief Election Commissioner Gyanesh Kumar, saying, “Gyanu, your game is over now!”
https://x.com/pokershash/status/2111337300848415032
Fact Check
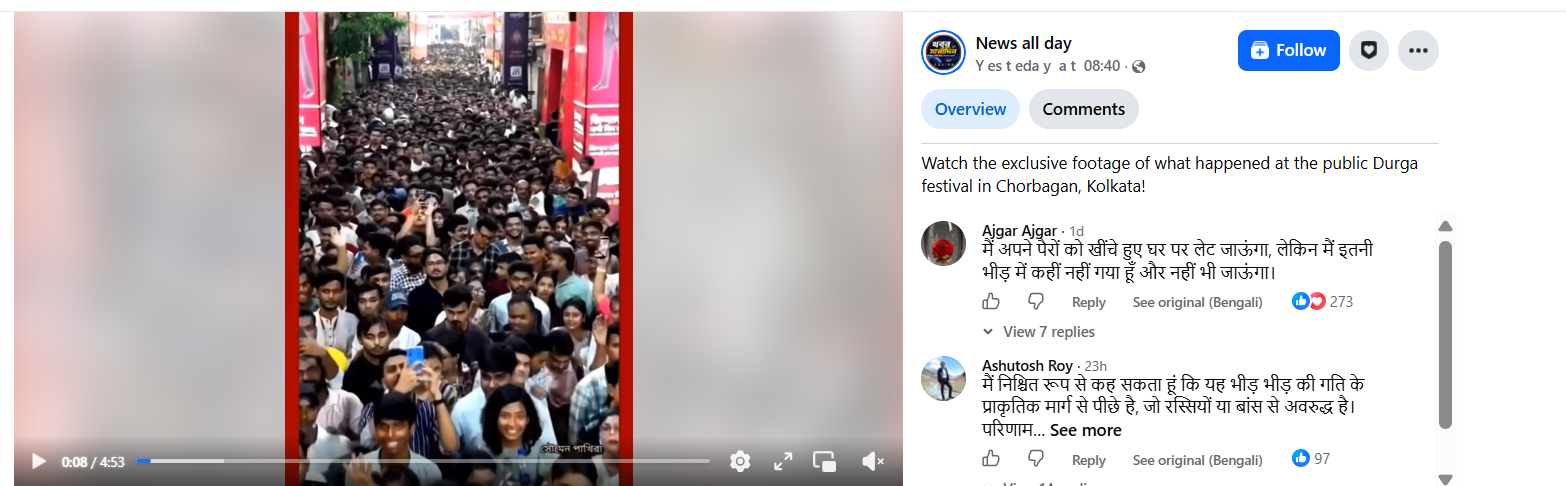
We conducted a reverse image search using keyframes from the viral video. During our research, we found the video on Facebook, where it was identified as footage from a public Durga Puja celebration organised at Chorbagan in Kolkata, which saw a large gathering of people.
https://www.facebook.com/watch/?v=29115417811386049
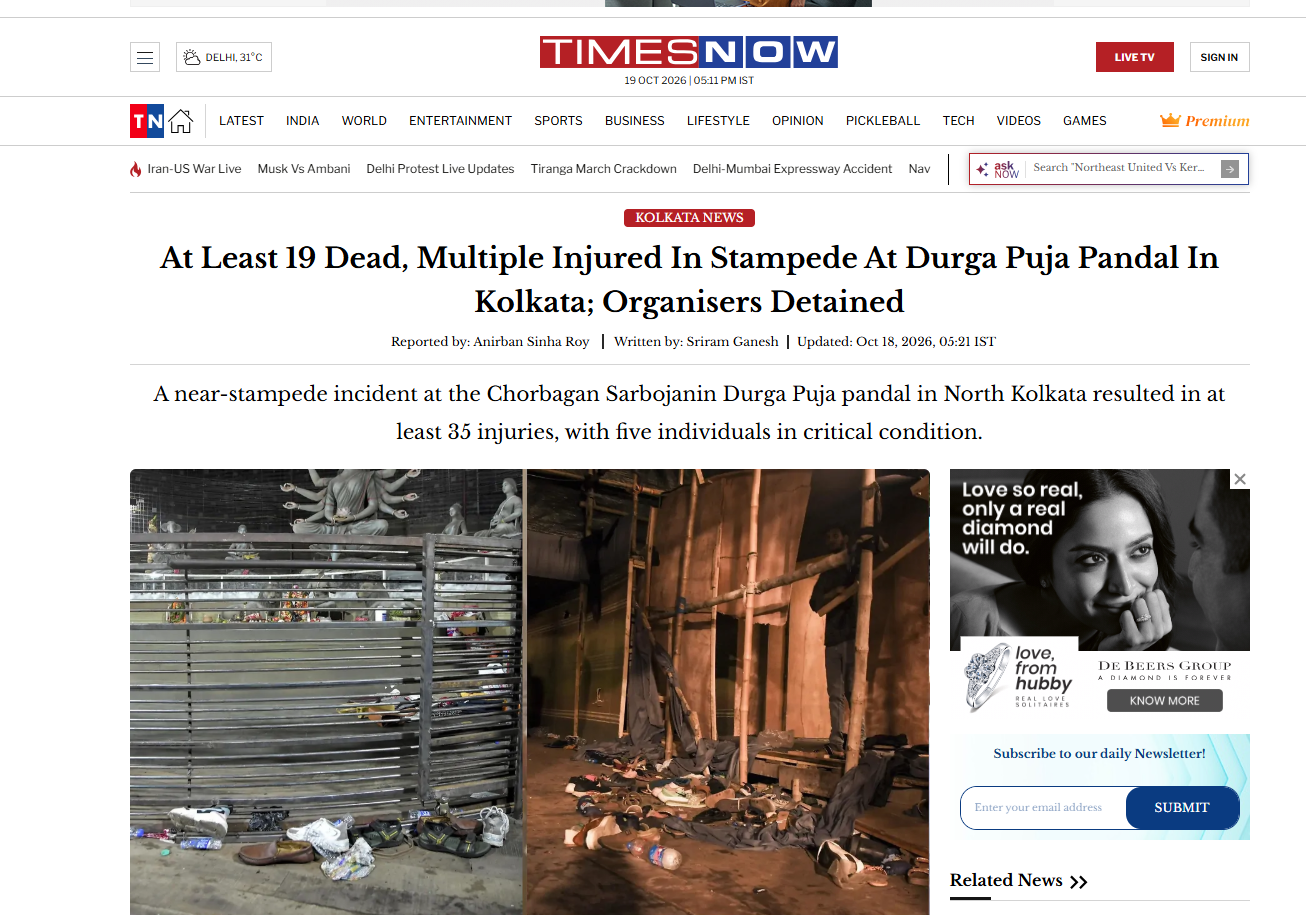
During our research, we found a video published by Times Now Bharat on October 17, 2026. According to the report, the footage shows a large crowd gathered at the Chorbagan Sarbojanin Durga Puja pandal in Kolkata. A near-stampede occurred at the venue, leaving 25 people injured, five of whom were reported to be in critical condition. This confirms that the video is unrelated to any gathering in support of CJP.
Conclusion
Our research found that the viral video is not related to any protest against Chief Election Commissioner Gyanesh Kumar. The video shows a public Durga Puja celebration at Chorbagan in Kolkata, where a large number of people had gathered.

Related Blogs

Recognizing As the Ministry of Electronic and Information Technology (MeitY) continues to invite proposals from academicians, institutions, and industry experts to develop frameworks and tools for AI-related issues through the IndiaAI Mission, it has also funded two AI projects that will deal with matters related to deepfakes as per a status report submitted on 21st November 2024. The Delhi court also ordered the nomination of the members of a nine-member Committee constituted by the MeitY on 20th November 2024 (to address deepfake issues) and asked for a report within three months.
Funded AI projects :
The two projects funded by MeitY are:
- Fake Speech Detection Using Deep Learning Framework- The project was initiated in December 2021 and focuses on detecting fake speech by creating a web interface for detection software this also includes investing in creating a speech verification software platform that is specifically designed for testing fake speech detection systems. It is set to end in December 2024.
- Design and Development of Software for Detecting Deepfake Videos and Images- This project was funded by MeitY from January 2022 to March 2024. It also involved the Centre for Development of Advanced Computing (C-DAC), Kolkata and Hyderabad as they have developed a prototype tool capable of detecting deepfakes. Named FakeCheck, it is designed as a desktop application and a web portal aiming to detect deepfakes without the use of the internet. Reports suggest that it is currently undergoing the testing phase and awaiting feedback.
Apart from these projects, MeitY has released their expression of interest for proposals in four other areas which include:
- Tools that detect AI-generated content along with traceable markers,
- Tools that develop an ethical AI framework for AI systems to be transparent and respect human values,
- An AI risk management and assessment tool that analyses threats and precarious situations of AI-specific risks in public AI use cases and;
- Tools that can assess the resilience of AI in stressful situations such as cyberattacks, national disasters, operational failures, etc.
CyberPeace Outlook
Deepfakes pose significant challenges to critical sectors in India, such as healthcare and education, where manipulated content can lead to crimes like digital impersonation, misinformation, and fraud. The rapid advancement of AI, with developments (regarding regulation) that can’t keep pace, continues to fuel such threats. Recognising these risks, MeitY’s IndiaAI mission, promoting investments and encouraging educational institutions to undertake AI projects that strengthen the country's digital infrastructure comes in as a guiding light. A part of the mission focuses on developing indigenous solutions, including tools for assessment and regulation, to address AI-related threats effectively. While India is making strides in this direction, the global AI landscape is evolving rapidly, with many nations advancing regulations to mitigate AI-driven challenges. Consistent steps, including inviting proposals and funding projects provide the much-needed impetus for the mission to be realized.
References
- https://economictimes.indiatimes.com/tech/technology/meity-dot-at-work-on-projects-for-fair-ai-development/articleshow/115777713.cms?from=mdr
- https://www.hindustantimes.com/india-news/meity-seeks-tools-to-detect-deepfakes-label-ai-generated-content-101734410291642.html
- https://www.msn.com/en-in/news/India/meity-funds-two-ai-projects-to-detect-fake-media-forms-committee-on-deepfakes/ar-AA1vMAlJ
- https://indiaai.gov.in/

Introduction:
The G7 Summit is an international forum that includes member states from France, the United States, the United Kingdom, Germany, Japan, Italy, Canada and the European Union (EU). The annual G7 meeting that is held every year was hosted by Japan this year in May 2023. It took place in Hiroshima. Artificial Intelligence (AI) was the major theme of this G7 summit. Key takeaways from this G7 summit highlight that leaders together focused on escalating the adoption of AI for beneficial use cases across the economy and the government and improving the governing structure to mitigate the potential risks of AI.
Need for fair and responsible use of AI:
The G7 recognises that they really need to work together to ensure the responsible and fair use of AI to help establish technical standards for the same. Members of the G7 countries agreed to adopt an open and enabling environment for the development of AI technologies. They also emphasized that AI regulations should be based on democratic values. G7 summit calls for the responsible use of AI. The ministers discussed the risks involved in AI technology programs like ChatGPT. They came up with an action plan for promoting responsible use of AI with human beings leading the efforts.
Further Ministers from the Group of Seven (G7) countries (Canada, France, Germany, Italy, Japan, the UK, the US, and the EU) met virtually on 7 September 2023 and committed to creating ‘international guiding principles applicable for all AI actors’, and a code of conduct for organisations developing ‘advanced’ AI systems.
What is HAP (Hiroshima AI Process)
Hiroshima AI Process (HAP) aims to establish trustworthy AI technical standards at the international level. The G7 agreed on creating a ministerial forum to prompt the fair use of AI. Hiroshima AI Process (HAP) is an effort by G7 to determine a way forward to regulate AI. The HAP establishes a forum for international discussions on inclusive AI governance and interoperability to achieve a common vision and goal of trustworthy AI at the global level.
The HAP will be operating in close connection with organisations including the Organisation for Economic Co-operation and Development (OECD) and the Global Partnership on AI (GPAI).
This Hiroshima AI Process (HAP) initiated at the Annual G7 Summit held in Hiroshima, Japan is a significant step towards regulating AI and the Hiroshima AI Process (HAP) is likely to conclude by December 2023.
G7 leaders emphasized fostering an environment where trustworthy AI systems are designed, developed and deployed for the common good worldwide. They advocated for international standards and interoperable tools for trustworthy AI that enable Innovation by creating a comprehensive policy framework, including overall guiding principles for all AI actors in the AI ecosystem.
Stressing upon fair use of advanced technologies:
The impact and misuse of generative AI was also discussed by the G7 leaders. The G7 members also stressed misinformation and disinformation in the realm of generative AI models. As they are capable of creating synthetic content such as deepfakes. In particular, they noted that the next generation of interactive generative media will leverage targeted influence content that is highly personalized, localized, and conversational.
In the digital landscape, there is a rapid advancement of technologies such as generative
Artificial Intelligence (AI), deepfake, machine learning, etc. Such technologies offer convenience to users in performing several tasks and are capable of assisting individuals and business entities. Since these technologies are easily accessible, cyber-criminals leverage AI tools and technologies for malicious activities, hence certain regulatory mechanisms at the global level will ensure and advocate for the ethical, reasonable and fair use of such advanced technologies.
Conclusion:
The G7 summit held in May 2023 focused on advanced international discussions on inclusive AI governance and interoperability to achieve a common vision and goal of trustworthy AI, in line with shared democratic values. AI governance has become a global issue, countries around the world are coming forward and advocating for the responsible and fair use of AI and influence on global AI governance and standards. It is significant to establish a regulatory framework that defines AI capabilities and identifies areas prone to misuse. And set forth reasonable technical standards while also fostering innovations. Hence overall prioritizing data privacy, integrity, and security in the evolving nature of advanced technologies.
References:
- https://www.politico.eu/wp-content/uploads/2023/09/07/3e39b82d-464d-403a-b6cb-dc0e1bdec642-230906_Ministerial-clean-Draft-Hiroshima-Ministers-Statement68.pdf
- https://www.g7hiroshima.go.jp/en/summit/about/
- https://www.drishtiias.com/daily-updates/daily-news-analysis/the-hiroshima-ai-process-for-global-ai-governance
- https://www.businesstoday.in/technology/news/story/hiroshima-ai-process-g7-calls-for-adoption-of-international-technical-standards-for-ai-382121-2023-05-20
Perth, Western Australia — For most of the past year, the name TeamPCP has circulated quietly within cybersecurity circles as shorthand for a particular kind of dread: not the dread of a phishing email or a suspicious link, but the dread of software you already trusted turning against you. This week, that quiet circulation became public record. The Australian Federal Police, working alongside the FBI and the Western Australia Police Force, arrested and charged two Western Australian men, aged 21 and 23, with a combined 14 offences over their alleged role in the group.
The arrests themselves are notable. The story behind them is more so.
A Campaign Built on Borrowed Trust
TeamPCP's alleged method was not to break down the front door. It was to compromise the door itself, the trusted mechanisms by which developers pull code into their own projects every day. The group has been linked to widespread supply-chain attacks that targeted open-source software and developer platforms to steal credentials, authentication secrets, and source code, with high-profile incidents affecting projects including Trivy, LiteLLM, Telnyx, SAP, and TanStack, alongside breaches at organisations such as the European Commission, Mistral AI, OpenAI, and GitHub. Reporting has also linked the campaign to ecosystems including GitHub Actions, Docker Hub, npm, PyPI and OpenVSX, the invisible plumbing through which most modern software is assembled.
The scale, as alleged by investigators, is difficult to overstate. Authorities say the malicious code potentially compromised over a thousand organisations worldwide, enabling the theft of roughly half a million credentials and the exfiltration of at least 300GB of data, figures that should be understood as allegations under active investigation rather than an independently verified victim count. The AFP itself has said the compromise of a small number of trusted software components had a significant global impact, with remediation costs estimated in the hundreds of millions of dollars.
Why This Attack Was So Hard to See Coming
The mechanics matter. Rather than tricking a user into clicking something malicious, the alleged operation worked by compromising the credentials developers use to publish legitimate software updates, then pushing tampered versions out through the same trusted distribution pipelines millions of applications rely on automatically. There is no obviously suspicious file, no rogue website, only a routine update, arriving exactly where it was expected.
Investigators also describe a cascading structure to the intrusions: credentials harvested from one compromised project reportedly opened the door to the next, turning isolated breaches into a chain reaction across the open-source ecosystem. TeamPCP has been described as running one of the most consequential campaigns of software supply-chain attacks investigators have tracked, and the group's reach extended notably into the AI stack — LiteLLM, one of the projects reportedly compromised, is an open-source gateway widely used to connect applications to large language model providers, meaning the attack's blast radius extended into the very infrastructure powering today's AI boom.
The Investigation and the Charges
The two men were charged following a joint investigation by the AFP and WAPF, working in parallel with the FBI, into what authorities describe as a sophisticated cybercrime syndicate accused of creating malicious open-source software to defraud thousands of global businesses. The charges span identity theft, unauthorised data modification, and money laundering, with maximum penalties ranging from three to twenty years' imprisonment. Search warrants were executed in Perth on 26 August 2026, and investigators seized electronic devices for forensic analysis after raids at properties in Cottesloe, Hamilton Hill, and Mandurah. FBI Cyber Division Assistant Director Brett Leatherman noted the significance of the international cooperation involved in the case, while investigators have not ruled out further arrests.
The Real Story: A Governance Problem, Not Just a Crime Story
It would be easy to file this under "hackers caught" and move on. But the more consequential story is structural. Modern organisations do not merely secure their own infrastructure, they inherit risk from every library, package, CI/CD pipeline, repository, vendor and developer tool they depend on, often without ever auditing that dependency chain directly. Guidance from the U.S. Cybersecurity and Infrastructure Security Agency (CISA) on securing open-source software has increasingly emphasised managing these dependencies through software bills of materials (SBOMs), precisely because so few organisations can otherwise answer a basic question: what, exactly, is running inside our systems?
TeamPCP's alleged campaign is a case study in why that question can no longer be optional. If an organisation's security posture is only as strong as the thousands of components it silently trusts, then supply-chain security is not a developer problem to be quietly patched — it is a governance issue, deserving board-level attention, vendor accountability frameworks, and mandatory disclosure practices.
CyberPeace's Take
At CyberPeace, we've been watching campaigns like TeamPCP's less as isolated incidents and more as a pattern that keeps repeating with higher stakes each time. What stands out to our team isn't the sophistication of the code, open-source poisoning is, frankly, not a new technique, it's the sophistication of patience. Compromising a maintainer's publishing credentials and simply waiting for the next scheduled release to carry the payload downstream is a strategy built for an ecosystem that still largely operates on implicit trust rather than continuous verification. That gap between how fast software moves and how slowly trust is actually checked is precisely where operations like this thrive.
We'd also push back gently on treating this as a "developer hygiene" story. Most engineering teams pulling in a package from npm or PyPI are not, and should not be expected to be, forensically auditing every dependency update by hand, that isn't scalable, and it was never a realistic line of defence. The actual fix has to sit further upstream: provenance verification baked into CI/CD pipelines, signed commits and releases treated as non-negotiable rather than optional, and SBOMs that are actually queried during incident response rather than generated once and filed away.
Our broader concern, honestly, is about incentive alignment. Open-source maintainers are frequently unpaid or under-resourced volunteers holding publishing keys to software depended on by billion-dollar enterprises. Until organisations that consume open-source software at scale start meaningfully funding its security, not just its development, this pattern isn't going away. It will simply find its next entry point.
References
- Australian Federal Police. Two WA men charged following AFP-FBI-WAPF disruption of alleged global cybercrime syndicate. afp.gov.au
- Bleeping Computer. Australia arrests alleged TeamPCP hackers behind supply-chain attacks. bleepingcomputer.com
- CyberScoop. Two alleged TeamPCP members arrested and charged after months of software supply-chain chaos. cyberscoop.com
- Cyber Daily. Busted! Alleged Aussie hackers linked to TeamPCP arrested in joint AFP-FBI-WAPF operation. cyberdaily.au
- Help Net Security. Two alleged TeamPCP hackers arrested over global supply chain attacks. helpnetsecurity.com
- Krebs on Security. Two Alleged 'TeamPCP' Hackers Arrested in Australia. krebsonsecurity.com
- TechCrunch. Australian police arrest two over TeamPCP hacks targeting Mercor, OpenAI, and others. techcrunch.com
- The Hacker News. Alleged TeamPCP Hackers Charged in Australia Over Major Supply Chain Attacks. thehackernews.com
