
#FactCheck: Old Video Falsely Linked to October 10 Protest at Delhi’s Jantar Mantar
Executive Summary
The Cockroach Janta Party (CJP) announced a protest at Jantar Mantar in Delhi on October 10, seeking the removal of Chief Election Commissioner Gyanesh Kumar. Media reports claimed that more than 250 trains, including local services bound for Delhi, had been cancelled. There were also claims that people planning to join the demonstration were being detained or kept under house arrest, while internet services at the protest venue had been suspended. However, CyberPeace Research found that the viral video was unrelated to the October 10 protest. Our research revealed that the footage had already been circulating on social media since September 5, well before the planned demonstration. Therefore, the video does not establish that it shows the October 10 protest.
Claim:
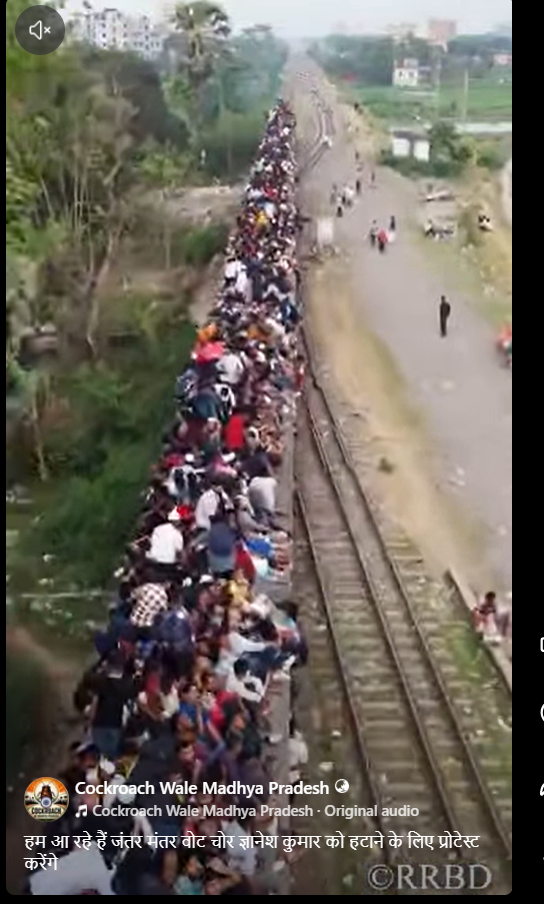
A Facebook user posted the video alongside a caption stating that they were heading to Jantar Mantar to demand the removal of Chief Election Commissioner Gyanesh Kumar, whom the post accused of stealing votes. The caption was originally written in Hindi. An archived version of the post is available below.
https://www.facebook.com/reel/1098834383046385
Fact-check
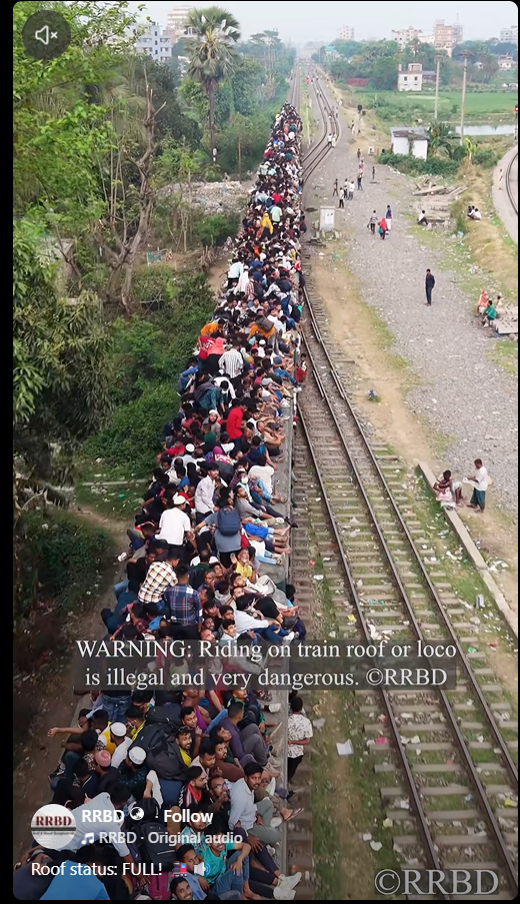
A reverse image search revealed that the viral video was shared on Facebook by a user named ‘RRBD’ on September 5. The account has more than 636,000 followers. The video was posted with the caption, “Roof status: FULL!”
https://www.facebook.com/reel/1720670926511274
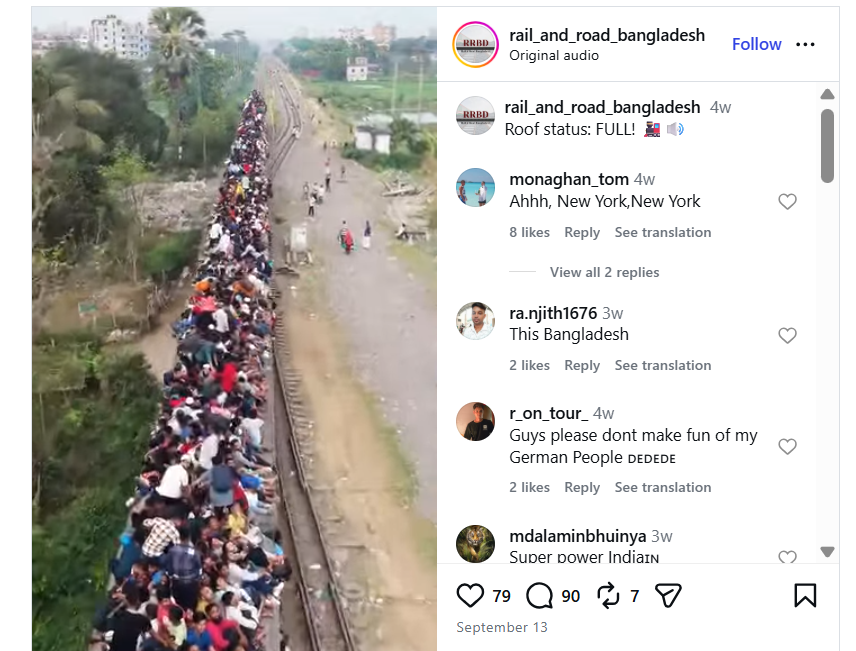
The Facebook account’s description also links to an Instagram account named ‘rail_and_road_bangladesh’, which has over 307,000 followers. The video was shared on this Instagram account on September 13 with the same caption as the Facebook post.
https://www.instagram.com/rail_and_road_bangladesh/reel/DdN6Dx9CVMH/
Conclusion
Our research found that the viral video is unrelated to the protest held at Jantar Mantar in Delhi on October 10. The video has been circulating on social media since September 5 and predates the protest. Therefore, the viral claim is false.

Related Blogs
Executive Summary
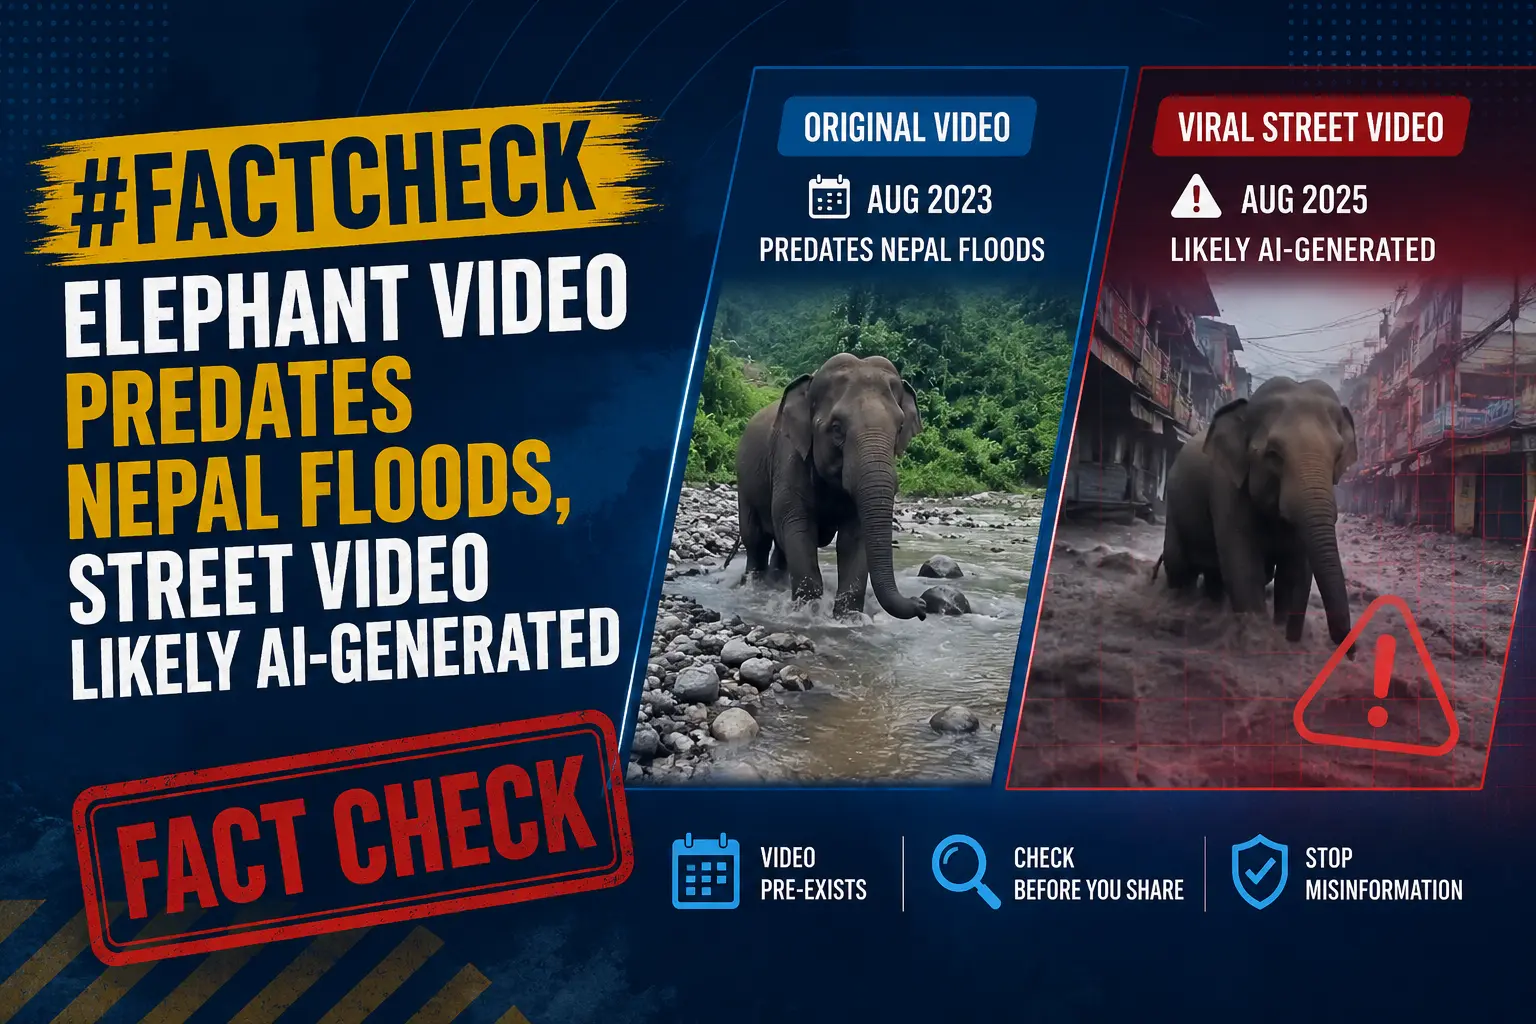
Amid the floods in Nepal, several videos are being shared on social media, claiming to show the current situation in the country. A research done by the Research Wing of the CyberPeace found that the video showing elephants is from an incident that occurred before the floods in Nepal, while the video showing the street is likely AI-generated.
Claim 1
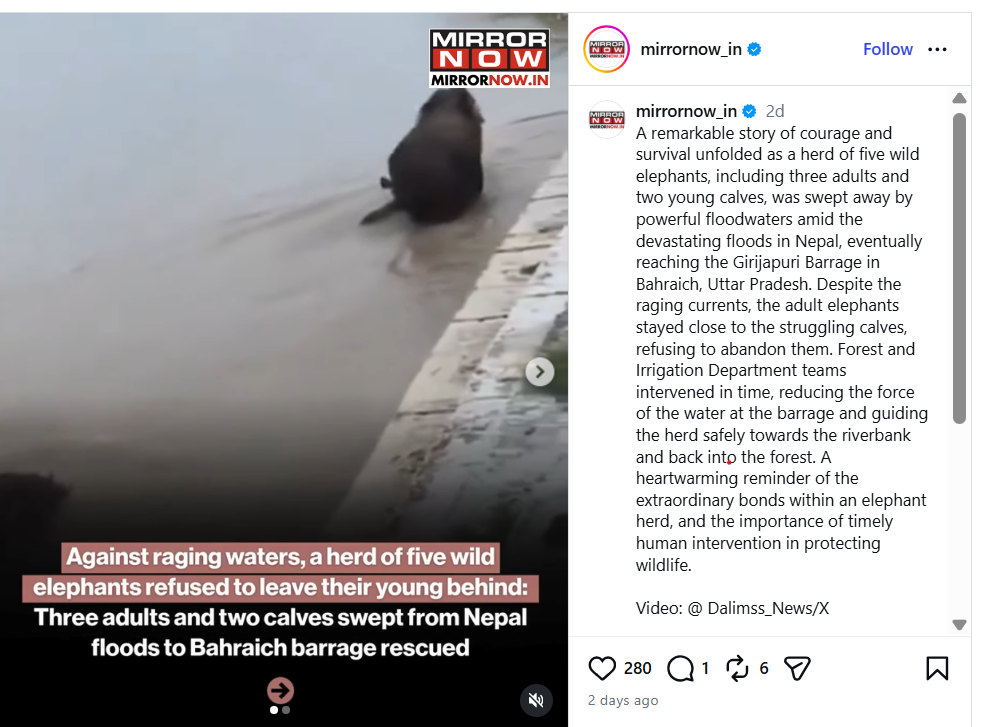
Videos claiming to show a street being swept away by flash floods in Nepal and a herd of elephants being carried away by the floods and reaching Uttar Pradesh are going viral on social media.
https://www.instagram.com/p/DcimGaiiCa7/
Claim 2
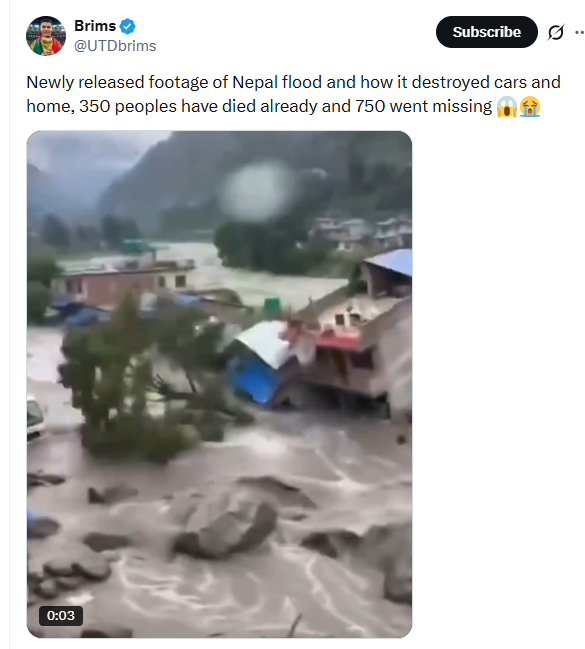
A newly surfaced video purportedly shows the devastation caused by floods in Nepal, with cars and homes being destroyed. It is being claimed that 350 people have died and 750 are missing so far
https://x.com/UTDbrims/status/2092829398462341484?s=48
Fact Check 1
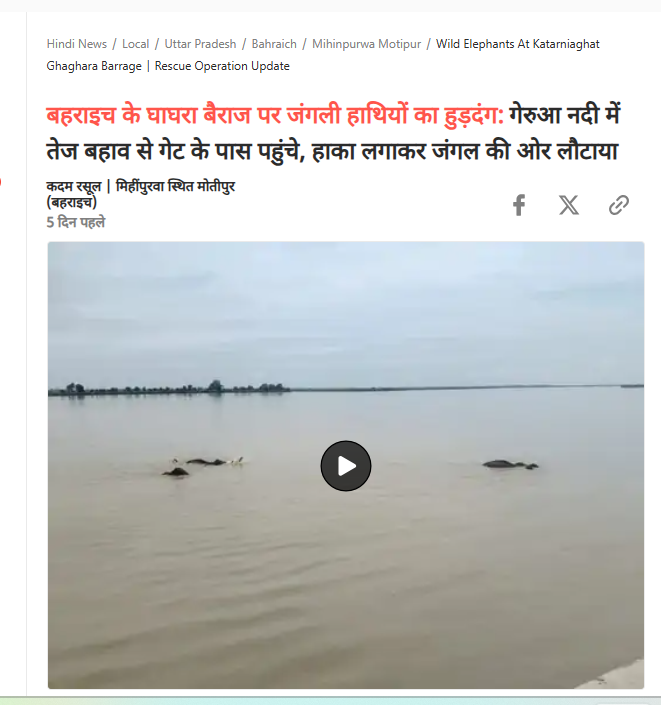
The first video claims to show a herd of wild elephants that was swept away by the floods in Nepal and reached Uttar Pradesh. We conducted a reverse image search of the first video using Google Lens and found a report by Hindi news publication Dainik Bhaskar, which shared a video featuring visuals similar to those in the viral clip. According to the report, a herd of wild elephants coming from the Gerua River reached the gates of the Chaudhary Charan Singh Ghaghra Barrage in Bahraich district, Uttar Pradesh, due to the strong current of the river. The report also quoted the Forest Range Officer as saying that the area is adjacent to an elephant corridor, which is why elephants frequently move through the region.
Fact Check 2
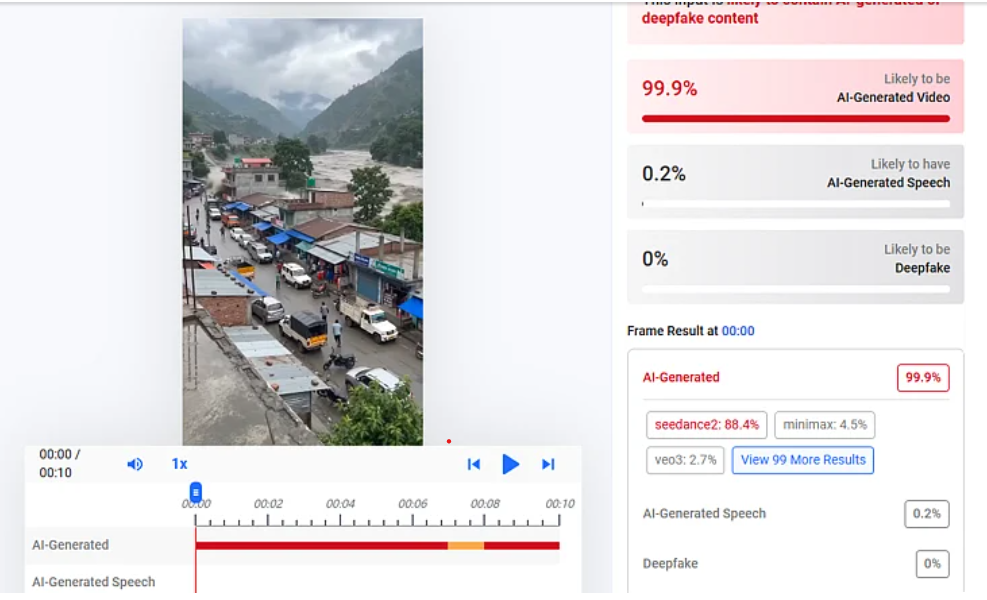
The second video shows a street being completely swept away by floodwaters. We conducted a reverse image search of the video using Google Lens but could not find any credible source that had shared the footage. Following this, we ran the video through the AI detection tool Hive Moderation, which flagged it as 99 percent likely to be AI-generated.
Conclusion
Our research found that the viral videos being shared as scenes of devastation caused by the recent floods in Nepal are misleading. The video showing a herd of elephants is from a separate incident in Bahraich, Uttar Pradesh, and predates the Nepal floods. Meanwhile, the video showing a street being swept away could not be traced to any credible source and was flagged as 99 percent likely to be AI-generated by Hive Moderation.

CERT-In, India's national cybersecurity agency, operates under mounting pressure. Cyberattacks in the country have doubled from 1.4 million in FY2022 to 2.9 million in FY2026, even as the window between a vulnerability's discovery and its exploitation continues to narrow. Rather than wait for access to the most advanced AI security tools, some of which face export restrictions, the agency has spent recent months building its own solution.
CERT-In has developed a new sandbox platform built with open-source AI, designed to identify cybersecurity gaps in public-sector systems. The sandbox functions as an isolated testing environment, allowing teams to safely evaluate software and applications without exposing the broader system to risk. Officials have framed this as a foundation rather than a substitute. MeitY Secretary S Krishnan described the platform as a step toward building a secure environment for eventual access to international AI models — suggesting the current approach is understood as an interim measure, not a permanent alternative to global tools.
This effort sits within a broader policy push: encouraging domestic AI development and tightening oversight of AI use in finance and online content. Taken together, these moves suggest a deliberate strategy of capacity-building through incremental, self-reliant steps, rather than a story about capability gaps or resource shortfalls.
A Crisis Measured in Millions
It helps to look at why this matters so much right now. A joint study by the Data Security Council of India and BCG found that recorded cyberattacks in the country roughly doubled in four years, from about 1.4 million in FY22 to 2.9 million in FY26. What's more worrying is how little time defenders now have to react to the average time it takes attackers to exploit a newly found vulnerability dropped from 745 days in FY22 to just 44 days in FY26, largely because attackers are using AI themselves to scout targets and build exploits faster. Banking, financial services, healthcare, telecom and government portals bear the brunt of this, with ransomware-as-a-service groups and state-linked actors increasingly slipping in through vendor portals and supply-chain weak points.
Turning Existing AI Into a Working Defence
CERT-In's Sandbox in Action
Instead of treating the lack of any one frontier model as a dealbreaker, CERT-In simply built its own closed trial platform officials have taken to calling it a "war room" where open-source and other AI models are set loose on software code to find vulnerabilities and shape secure workflows for India's top public sector companies, including in financial services. At a press conference, Meity secretary S. Krishnan pointed out that these substitute models already match roughly 60 to 70 per cent of the performance of the most advanced security-focused systems out there globally. That's a fairly substantial chunk of the capability, and it's coming from tools India can actually access today. The testing has stretched to core digital infrastructure like Aadhaar and government login systems, while some of the country's biggest tech firms are already using currently available AI models to patch widely used enterprise software, banking platforms included. The logic is simple enough: build the muscle now with whatever's on hand, so the enterprise environment is already in better shape by the time more capable tools eventually arrive.
Investing in Sovereign Capability
Arguably the more important move here is a longer-term one , India's bet on building its own frontier-grade security AI. The Centre has reportedly asked domestic AI developers Sarvam AI and BharatGen to build advanced cybersecurity capabilities of their own, hosted on the government's isolated computer infrastructure and eventually put to work protecting critical infrastructure. There's no public timeline yet for when these indigenous models will be ready, but the intent behind the move isn't hard to read: cut India's reliance on any single foreign provider for defending the systems that underpin banking, identity and public administration, while keeping sensitive testing and deployment on Indian soil. Officials have also signalled a preference for on-premises deployment of high-capability AI tools where the stakes are highest, rather than leaning entirely on overseas cloud infrastructure. It's a choice that points toward building lasting, self-reliant capacity rather than making a one-off purchase.
A Tightening Regulatory Net
RBI's Model Risk Guardrails
None of this is happening in a vacuum. On 24 June 2026, the Reserve Bank of India released draft guidance on model risk management that, for the first time, brings AI and machine learning systems used by banks, NBFCs and other regulated entities under a single, board-level governance framework. The draft asks institutions to keep a full inventory of every model they use, rank each one by risk, and build in human override and "kill-switch" mechanisms so a malfunctioning AI system can be shut down immediately. It also makes one thing very clear: banks can't shrug off accountability just because the technology came from a vendor.
MeitY's Deepfake and Synthetic-Content Rules
Around the same time, the Ministry of Electronics and Information Technology notified amendments to the IT Rules that formally define "synthetically generated information," require deepfakes and AI-altered media to carry clear, persistent labels and embedded provenance metadata, and cut the takedown window for unlawful synthetic content down to just three hours. Taken together, the RBI and MeitY rules form the regulatory backbone that CERT-In's technical sandbox is meant to plug into giving India a more coordinated response to both the defensive and the deceptive sides of AI.
One Chain of Command
Officials have gone out of their way to stress that all these moving parts aren't creating confusion in India's cybersecurity reporting structure. CERT-In director general Sanjay Bahl has said the National Security Council Secretariat remains the overarching body, with CERT-In as the top cyber reporting and investigations organisation across sectors, and that sectoral regulators like the RBI and SEBI still report into this one structure rather than running their own parallel systems.
Conclusion
Look at CERT-In's sandbox, the push for sovereign AI, and the tightening regulatory net together, and a clearer picture forms. This isn't really a story about a piece of technology India doesn't have. It's a story about capability being built, deliberately and in the open. The country is using the AI tools available right now to close real security gaps, backing homegrown alternatives for the long haul, and pairing both with governance rules that keep banks, platforms and public infrastructure honest. If there's a lesson in all this, it's that real resilience against a fast-moving cyberthreat landscape rarely arrives all at once. It gets built the way most lasting capability does piece by piece, mostly at home, without waiting for any single outside breakthrough to show up first.
References
- https://inc42.com/buzz/centre-asks-sarvam-ai-bharatgen-to-develop-mythos-like-cyber-ai-models/
- https://inc42.com/buzz/centre-asks-sarvam-ai-bharatgen-to-develop-mythos-like-cyber-ai-models/
- https://www.newkerala.com/news/a/govt-prioritises-access-anthropics-mythos-ai-model-strengthen-475.htm
- https://blog.qualys.com/product-tech/2026/06/24/cert-in-ai-vulnerability-blueprint-machine-speed-risk-operations
- https://www.business-standard.com/technology/tech-news/mythos-threat-govt-tech-firms-test-their-softwares-for-vulnerabilities-126052700386_1.html
- https://inc42.com/buzz/centre-asks-sarvam-ai-bharatgen-to-develop-mythos-like-cyber-ai-models/
- https://www.finextra.com/blogposting/32142/rbis-model-risk-management-guidance-2026--summary
- https://www.medianama.com/2026/06/223-rbi-ai-guidelines-2026-banks-kill-switch/
- https://www.freshfields.com/en/our-thinking/blogs/technology-quotient/india-targets-deepfakes-and-ai-generated-content-key-changes-under-meitys-2026-102mjwn

Introduction
In recent times the evolution of cyber laws has picked up momentum, primarily because of new and emerging technologies. However, just as with any other law, the same is also strengthened and substantiated by judicial precedents and judgements. Recently Delhi High Court has heard a matter between Tata Sky and Linkedin, where the court has asked them to present their Chief Grievance Officer details and SoP per the intermediary guidelines 2021.
Furthermore, in another news, officials from RBI and Meity have been summoned by the Parliamentary Standing Committee in order to address the rising issues of cyber securities and cybercrimes in India. This comes on the very first day of the monsoon session of the parliament this year. As we move towards the aspects of digital India, addressing these concerns are of utmost importance to safeguard the Indian Netizen.
The Issue
Tata Sky changed its name to Tata Play last year and has since then made its advent in the OTT sector as well. As the rebranding took place, the company was very cautious of anyone using the name Tata Sky in a bad light. Tata Play found that a lot of people on Linkedin had posted their work experience in Tata Sky for multiple years, as any new recruiter cannot verify the same. This poses a misappropriation of the brand’s name. This issue was reported to Linkedin multiple times by officials of Tata Play, but no significant action was seen. This led to an issue between the two brands; hence, a matter has been filed in front of the Hon’ble Delhi High Court to address the issue. The court has taken due cognisance of the issue, and hence in accordance with the Intermediary Guidelines 2021, the court has directed Linkedlin to provide the details of their Cheif Grievance Officer in the public domain and also to share the SoP for the redressal of issues and grievances. The guidelines made it mandatory for all intermediaries to set up a dedicated office in India and appoint a Chief Grievance Officer responsible for effective and efficient redressal of the platform-related offences and grievances within the stipulated period.
The job platform has also been ordered to share the SoPs and the various requirements and safety checks for users to create profiles over Linkedin. The policy of Linkedin is focused towards the users as well as the companies existing on the platform in order to create a synergy between the two.
RBI and Meity Official at Praliament
As we go deeper into cyberspace, especially after the pandemic, we have seen an exponential rise in cybercrimes. Based on statistics, 4 out of 10 people have been victims of cybercrimes in 2022-23, and it is estimated that 70% of the population has been subjected to direct or indirect cybercrime. As per the latest statistics, 85% of Indian children have been subjected to cyberbullying in some form or the other.
The government has taken note of the rising numbers of such crimes and threats, and hence the Parliamentary Committee has summoned the officials from RBI and the Ministery of Electronics and Information Technology to the parliament on July 20, 2023, i.e. the first day of monsoon session at the parliament. This comes at a very crucial time as the Digital Personal Data Protection Bill is to be tabled in the parliament this session and this marks the revamping of the legislation and regulations in the Indian cyberspace. As emerging technologies have started to surround us it is pertinent to create legal safeguards and practices to protect the Indian Netizen at large.
Conclusion
The legal crossroads between Tata Sky and Linkedin will go a long way in establishing the mandates under the Intermediary guidelines in the form of legal precedents. The compliance with the rule of law is the most crucial aspect of any democracy. Hence the separation of power between the Legislature, Judiciary and Execution has been fundamental in safeguarding basic and fundamental rights. Similarly, the RBI and Meity officials being summoned to the parliament shows the transparency in the system and defines the true spirit of democracy., which will contribute towards creating a safe and secured Indian Cyberspace.
