
#FactCheck: False Claim About Indian Flag Hoisted in Balochistan amid the success of Operation Sindoor
Executive Summary:
A video circulating on social media claims that people in Balochistan, Pakistan, hoisted the Indian national flag and declared independence from Pakistan. The claim has gone viral, sparking strong reactions and spreading misinformation about the geopolitical scenario in South Asia. Our research reveals that the video is misrepresented and actually shows a celebration in Surat, Gujarat, India.

Claim:
A viral video shows people hoisting the Indian flag and allegedly declaring independence from Pakistan in Balochistan. The claim implies that Baloch nationals are revolting against Pakistan and aligning with India.

Fact Check:
After researching the viral video, it became clear that the claim was misleading. We took key screenshots from the video and performed a reverse image search to trace its origin. This search led us to one of the social media posts from the past, which clearly shows the event taking place in Surat, Gujarat, not Balochistan.

In the original clip, a music band is performing in the middle of a crowd, with people holding Indian flags and enjoying the event. The environment, language on signboards, and festive atmosphere all confirm that this is an Indian Independence Day celebration. From a different angle, another photo we found further proves our claim.

However, some individuals with the intention of spreading false information shared this video out of context, claiming it showed people in Balochistan raising the Indian flag and declaring independence from Pakistan. The video was taken out of context and shared with a fake narrative, turning a local celebration into a political stunt. This is a classic example of misinformation designed to mislead and stir public emotions.
To add further clarity, The Indian Express published a report on May 15 titled ‘Slogans hailing Indian Army ring out in Surat as Tiranga Yatra held’. According to the article, “A highlight of the event was music bands of Saifee Scout Surat, which belongs to the Dawoodi Bohra community, seen leading the yatra from Bhagal crossroads.” This confirms that the video was from an event in Surat, completely unrelated to Balochistan, and was falsely portrayed by some to spread misleading claims online.

Conclusion:
The claim that people in Balochistan hoisted the Indian national flag and declared independence from Pakistan is false and misleading. The video used to support this narrative is actually from Surat, Gujarat, India, during “The Tiranga Yatra”. Social media users are urged to verify the authenticity and source of content before sharing, to avoid spreading misinformation that may escalate geopolitical tensions.
- Claim: Mass uprising in Balochistan as citizens reject Pakistan and honor India.
- Claimed On: Social Media
- Fact Check: False and Misleading

Related Blogs
Introduction
On June 2nd, 2026, even as thousands of Class 12 students across the nation flocked to submit re-evaluation and verification applications on the CBSE’s newly rolled-out On-Screen Marking (OSM) portal, a decidedly different kind of visitor had logged in an attacker carrying automation scripts, botnet traffic, and malicious intentions to either shut the system down or steal its contents. The attack, which CBSE then openly reported on its official X account, flooded the portal with 1.5 million hits in two minutes and sent over a lakh unauthorized file access attempts.
Understanding the Attack Architecture: The Two-Pronged Operation
The CBSE cyberattack was actually not a single exploit but rather a layered, orchestrated attack. The attack can be understood in two prongs:
- The DoS Attack:Firstly, attackers initiated a large-scale DoS (Denial of Service) attack, producing approximately 1.5 million requests in 120 seconds, or approximately 12,500 per second, in order to saturate the server. By overloading the systems with bogus requests, the attackers sought not just to disable the site but also to throw off security personnel from their primary task of stabilizing the portal during its launch period.
The File Probing: These attacks usually include the following methods:
- Path Traversal Attacks - Attackers will attempt to navigate outside of the current directory by supplying inputs such as "../../etc/passwd" in URL parameters or in a file upload.
- Forced Browsing / Directory Enumeration - An attacker may have used tools to attempt to find vulnerable files and directories like answer sheets, exam scans, student identification documents, and admin-related files by systematically guessing names.
- API Endpoint Fuzzing: If any REST or GraphQL API was present for the portal, the attacker may have tried sending a various number of inputs to parameters to attempt to retrieve records, find IDORs, or escalate privileges.
- Session Token Harvesting - For high-load environments, some systems may use insecure session management. Attackers would attempt to predict or guess the token to hijack another student's or administrator's session.
Why Are Educational Portals High-Value Targets?
Here's why the Indian education sector is an attractive target for cyber-attacks:
- Concentrated PII: Millions of students are present on these education portals, and their data (names, birth dates, Aadhaar linkage information, parents' details, address, education profiles, etc.) is of the highest value on the dark web and can be used for identity theft, financial fraud, credential reuse, and targeting.
- Low Investment Relative to the Data Value: The education system is chronically under-invested in cybersecurity. Many of these systems were built for a function/scale, rather than security by design, and are highly vulnerable.
- High-Pressure Launches: Launching a massive, public-facing system like the CBSE OSM verification site that needs to service millions of students on day 1 often requires time constraints that preclude proper penetration testing, stress testing, security auditing, or staged deployment; these launches often launch with numerous known security flaws.
- Large Attack Surface: The education ecosystem is comprised of many integrated systems, APIs, cloud instances, third-party systems, and authentication infrastructure. Each dependency increases the overall attack surface and provides multiple potential avenues to compromise these systems, such as IDOR, API abuse, or credential-based attacks.
- Geopolitical Motivation: Following the Op Sindoor attack in 2025, there was a significant increase in public institutions targeted by cyber-attacks with prolonged DDoS against critical systems. Highly visible, public-facing student portals catering to more than 35 million students make a tantalizing target for both nation-state attackers and hacktivist groups to cause disruption or gather intelligence.
The CBSE's Response
A balanced perspective on CBSE's public response is necessary:
- The portal did not go down and served about 14000 users at any point during the attack and had over 28000 successful submissions by 10pm June 2nd.
- In real-time, sessions are continuously being optimized for the students, and session timeouts are being extended.
- Management was on top of the situation and maintained good communication through social media.
To withstand a sustained attack volume of roughly 12,500 requests per second, CBSE would surely need more than one security control implemented on its infrastructure. In all probability, rate limiting was the primary reason it could sustain this attack volume by limiting the requests from an IP or client over a certain period of time and automatically aborting requests from systems sending automated data. This, coupled with perhaps load balancing, will distribute the attack across several systems, none of which will have become bottlenecks. Finally, it is possible that traffic could have also been routed via a Content Delivery System (CDN) or dedicated DDoS mitigation service capable of detecting and cleaning requests of malicious code before they even reach the origin servers.
Technical Recommendations
It is not sustainable for India's exam infrastructure to continue operating in a post-breach, patching-in mode forever. The systems need to embrace Privacy By Design (PBD) as an integral part of their DNA. Here are suggestions for short-term hardening and long-term resilience:
- Deploy a zero-trust file access architecture: Each request to access any file should be authenticated, authorized using role-based access control (RBAC), and logged in an immutable audit trail. Direct access to file paths should not be permissible; rather, pre-signed, time-limited tokens are recommended to control file access.
- Implement a multi-layered DDoS mitigation architecture: A combination of network edge traffic scrubbing (CDNs & DDoS mitigation services) along with rate limiting at the application layer via WAF is necessary. An Anycast-based multi-PoP architecture and pre-provisioning scrubbing capacity may further increase resiliency
- Conduct pre-launch penetration testing and red teaming exercises: Penetration testing with OWASP Top 10 audits, API security reviews, and load-based penetration testing should be conducted by CERT-In empanelled auditors prior to the launch of the examination. The red team exercise should simulate blended DoS and file-probing attacks.
- Secure Payments: The secure payment surface should support PCI-DSS Level 1 certified payments and tokenisation and employ velocity checks against automated abuse and support 3D Secure 2.0 (3DS2) on card payments.
- Implement SOC: Security operations centers (SOCs) should have real-time access to CERT-In threat feeds and ISAC intelligence, allowing them to act quickly on emerging attack vectors before anything malicious can be exploited.
- Encryption: Students' data should be encrypted with AES-256; keys should be stored separately in a Hardware Security Module (HSM) system and not co-located with the data storage system. Student data must also support the data minimisation principle, while storing it should be encrypted with AES-256 and keys should be stored securely in HSM.
- Monitoring: 24/7 SOC monitoring, ongoing vulnerability scanning on all pipelines, anomalous detection baselining, and frequent tabletop exercises for cyber resilience at 24x7 and post-examination activities.
Beyond the Breach: Governance, Accountability, and the Growing Cyber Threat to India's Education Sector
The CBSE attack is merely one example of a wider truth, a truth that extends beyond an isolated security event and highlights security as not only an issue of governance but of national security. Although it was during a period in which there was considerable change in leadership within the CBSE (some officials had been removed from their positions), and although it may be impossible to prevent administrative change, security vulnerability is an inherent risk when it cannot be ensured that the new incumbents have had knowledge transferred from the previous administration in terms of system design, vendor management, configuration, and incident response procedures. It has become apparent that a requirement for digital system governance must be considered to be just as serious a requirement as an academic and administrative governance requirement.
The attack is also indicative of a wider problem, and in 2025 there were in excess of 265 million cyber-attacks, and increasingly, critical infrastructure is being attacked by all manner of actors, including criminals, hacktivists, and state-sponsored groups. Educational institutions offer a prime target due to the amount of personal data held within their systems and the historically low security investment they tend to have. Worldwide trends that support the similar narrative of "data of immense value protected by under-resourced programs" (universities hit by ransomware and mass student data breaches included) are being constantly illustrated. For an examining body of tens of millions of students, cybersecurity cannot be an afterthought and needs to be clearly addressed within the governance and risk-management framework of the institution and, therefore, become a fundamental pillar of public trust.
Conclusion
The June 2026 cyberattack on the CBSE's OSM portal both illustrated the advancing capabilities of today's threat actors and highlighted the critical role cyber resilience must play in India's education sector. A high-volume DoS attack combined with over 100,000 file access attempts indicates a concerted and strategic operation both for disruption and the opportunity for data theft. Though the CBSE's infrastructure did hold, the attack should not offer comfort. Educational institutions are responsible for a significant amount of sensitive personal data, and they are major targets to state-sponsored and financially motivated attackers. Attacks are bound to continue. It is essential that cybersecurity become a fundamental pillar of the governance and trustworthiness of education and not a technical afterthought.
References
- CBSE Official Statement on Cyberattack, X (formerly Twitter), @cbseindia29, June 2, 2026.
- Indian Express, "CBSE OSM Row: Portal attack was a 'coordinated, two-pronged operation' says cybersecurity expert," June 3, 2026.
- Srinivas L, Joint MD & Joint CEO, 63SATS Cybertech (subsidiary of 63 moons technologies limited), was quoted in Indian Express, June 3, 2026.
- The Federal, "CBSE re-evaluation portal faces cyberattack, records 1.5 million hits in two minutes," June 2, 2026. https://thefederal.com
- CERT-In (Indian Computer Emergency Response Team), Empanelled Security Auditor Framework. https://www.cert-in.org.in
- OWASP Top 10 Web Application Security Risks, 2021 edition. https://owasp.org/www-project-top-ten/
- National Institute of Standards and Technology (NIST), Zero Trust Architecture (SP 800-207), August 2020. https://doi.org/10.6028/NIST.SP.800-207
- Indian Express, "What CBSE ignored: Its own panel found glitches in dry run, said delay OSM by a year," June 3, 2026.
- Asianet Newsable, "CBSE Class 12 re-evaluation portal withstands major DoS cyberattack," June 2, 2026. https://newsable.asianetnews.com
Executive Summary
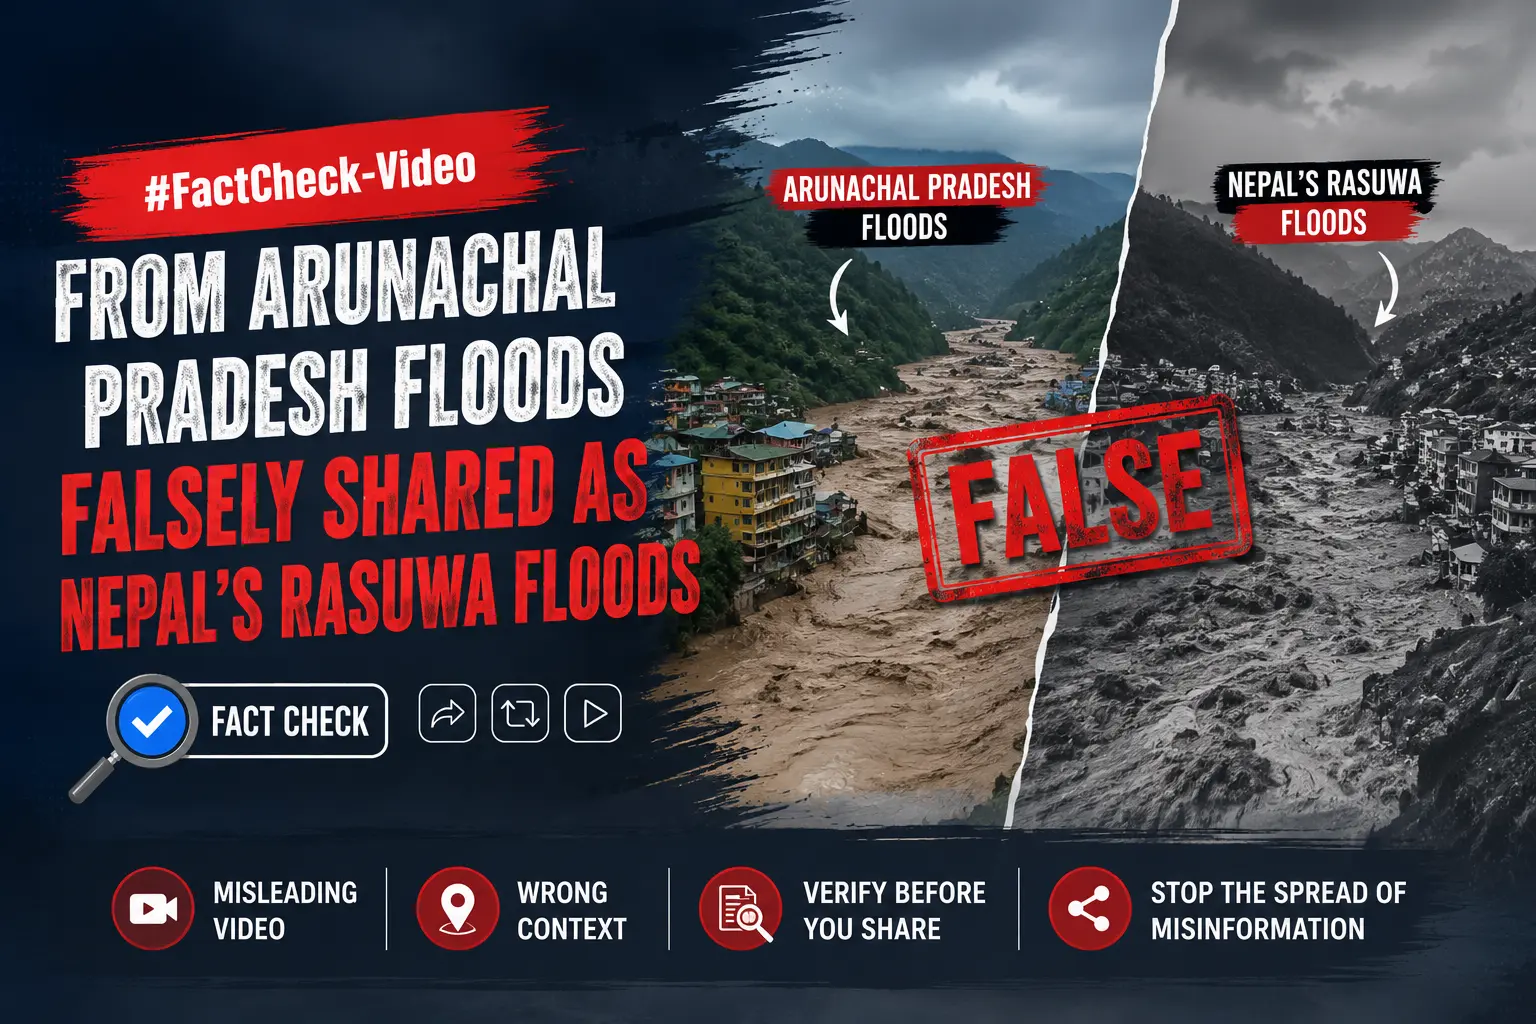
A video showing several houses being swept away by floodwaters is being shared on social media, claiming that it shows flooding in the Rasuwa area of Nepal. Research done by the CyberPeace research wing found that the video is not from Nepal, but is from the floods that occurred in Keyi Panyor district of Arunachal Pradesh in June.
Claim
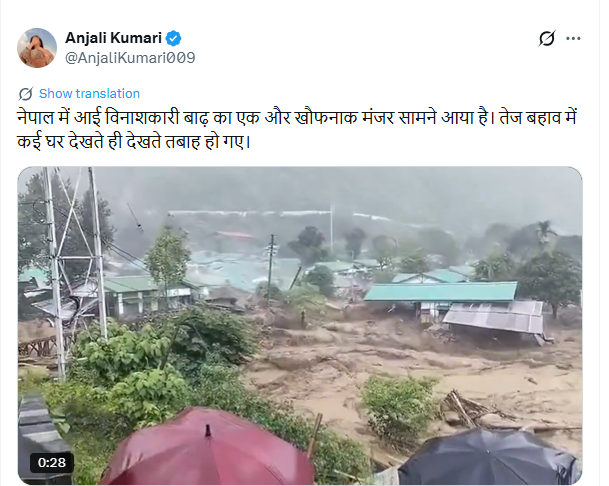
The video was shared on X with the caption: “Another horrifying scene from the devastating floods in Nepal has emerged. Several houses were destroyed within moments by the strong current.”
https://x.com/anjalikumari009/status/2093257147094335652
FactCheck
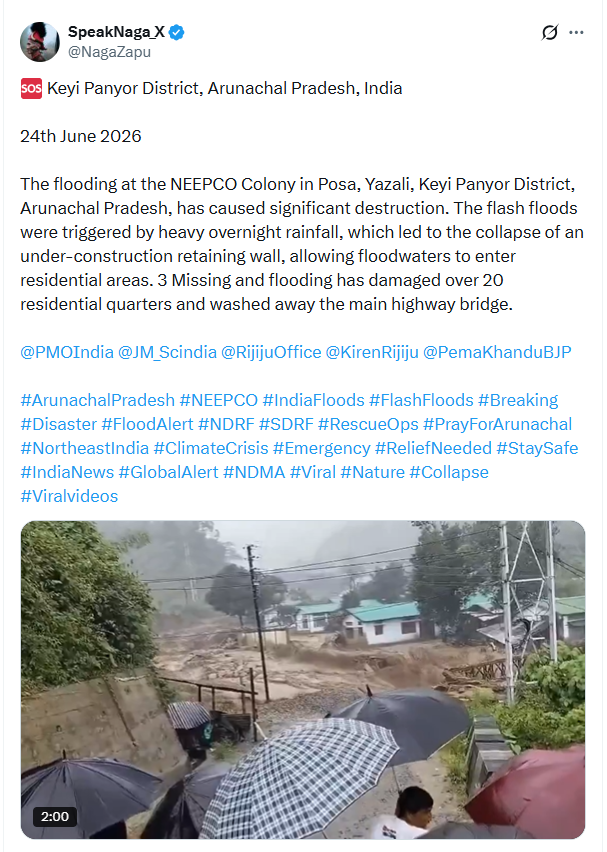
During our research of the video being shared as footage of floods in Nepal’s Rasuwa area, we conducted a reverse image search using keyframes and found a longer version of the video posted on an X account on June 24, 2026. The caption accompanying the video identified it as footage of a flash flood and the resulting devastation in Nipko Colony, Possa, in Arunachal Pradesh’s Keyi Panyor district, on June 24.
https://x.com/NagaZapu/status/2069747140608331962
During the research, we also found videos of the flooding in Nipko Colony uploaded on several social media accounts from Arunachal Pradesh on June 24. These posts contained visuals matching those seen in the viral video.
https://www.facebook.com/reel/977442025167230
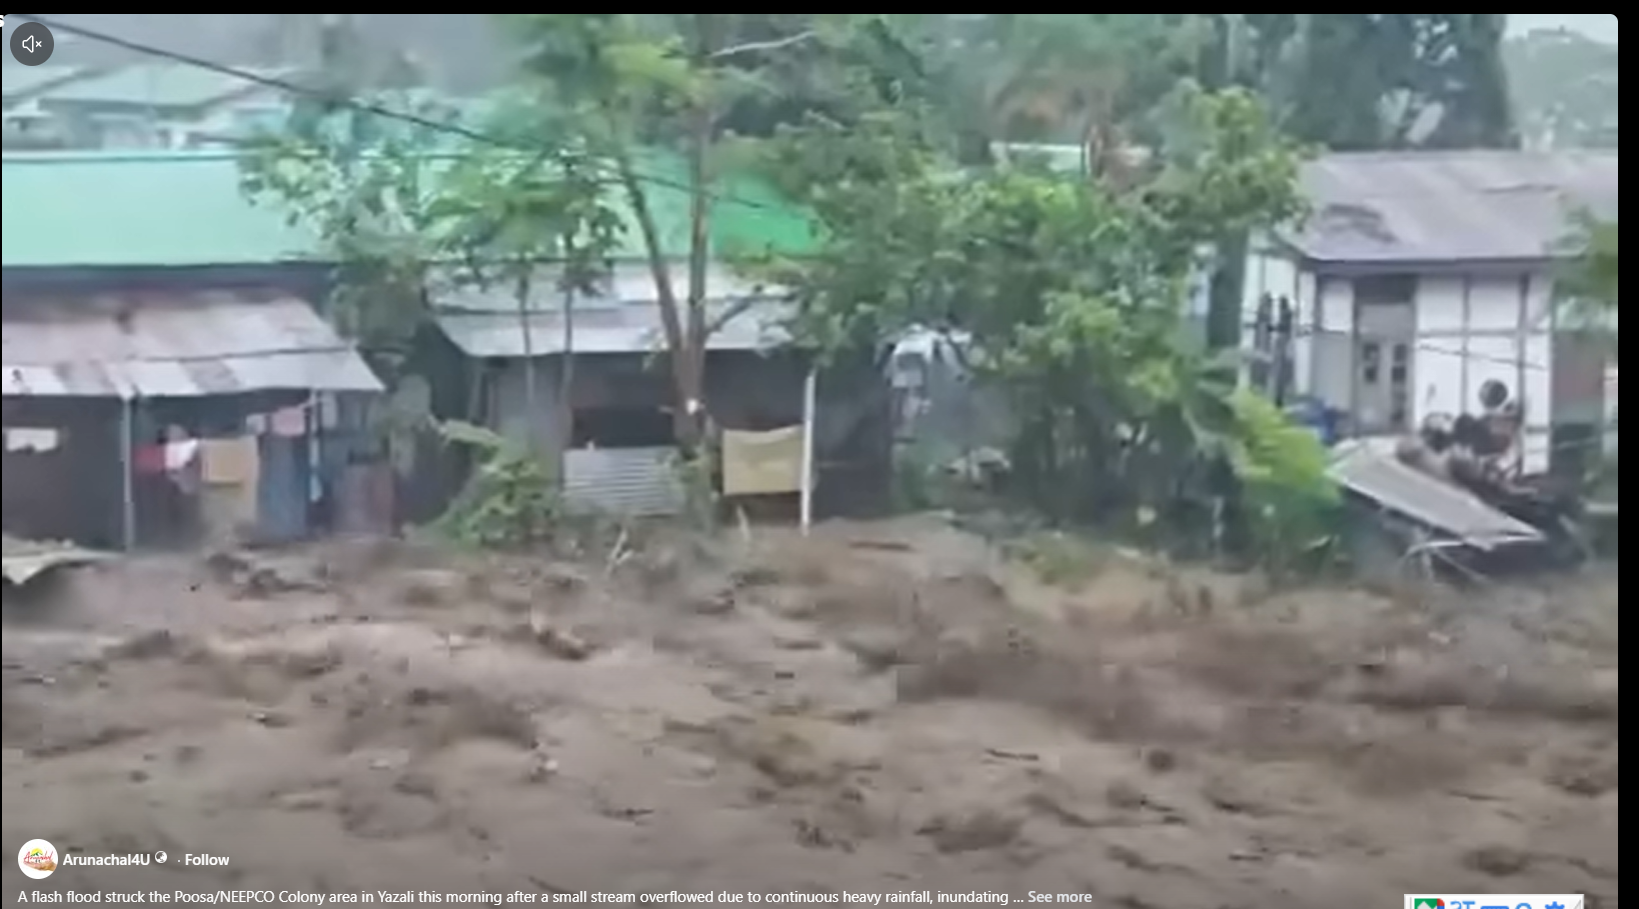
Additionally, we found a video report uploaded on June 24, 2026, on the Facebook account of a media outlet from Arunachal Pradesh. The report featured footage of the flooding in Nipko Colony. In the audio accompanying the video, the person recording the footage can also be heard describing the devastation caused by the floods.
https://www.facebook.com/reel/1571580381035813
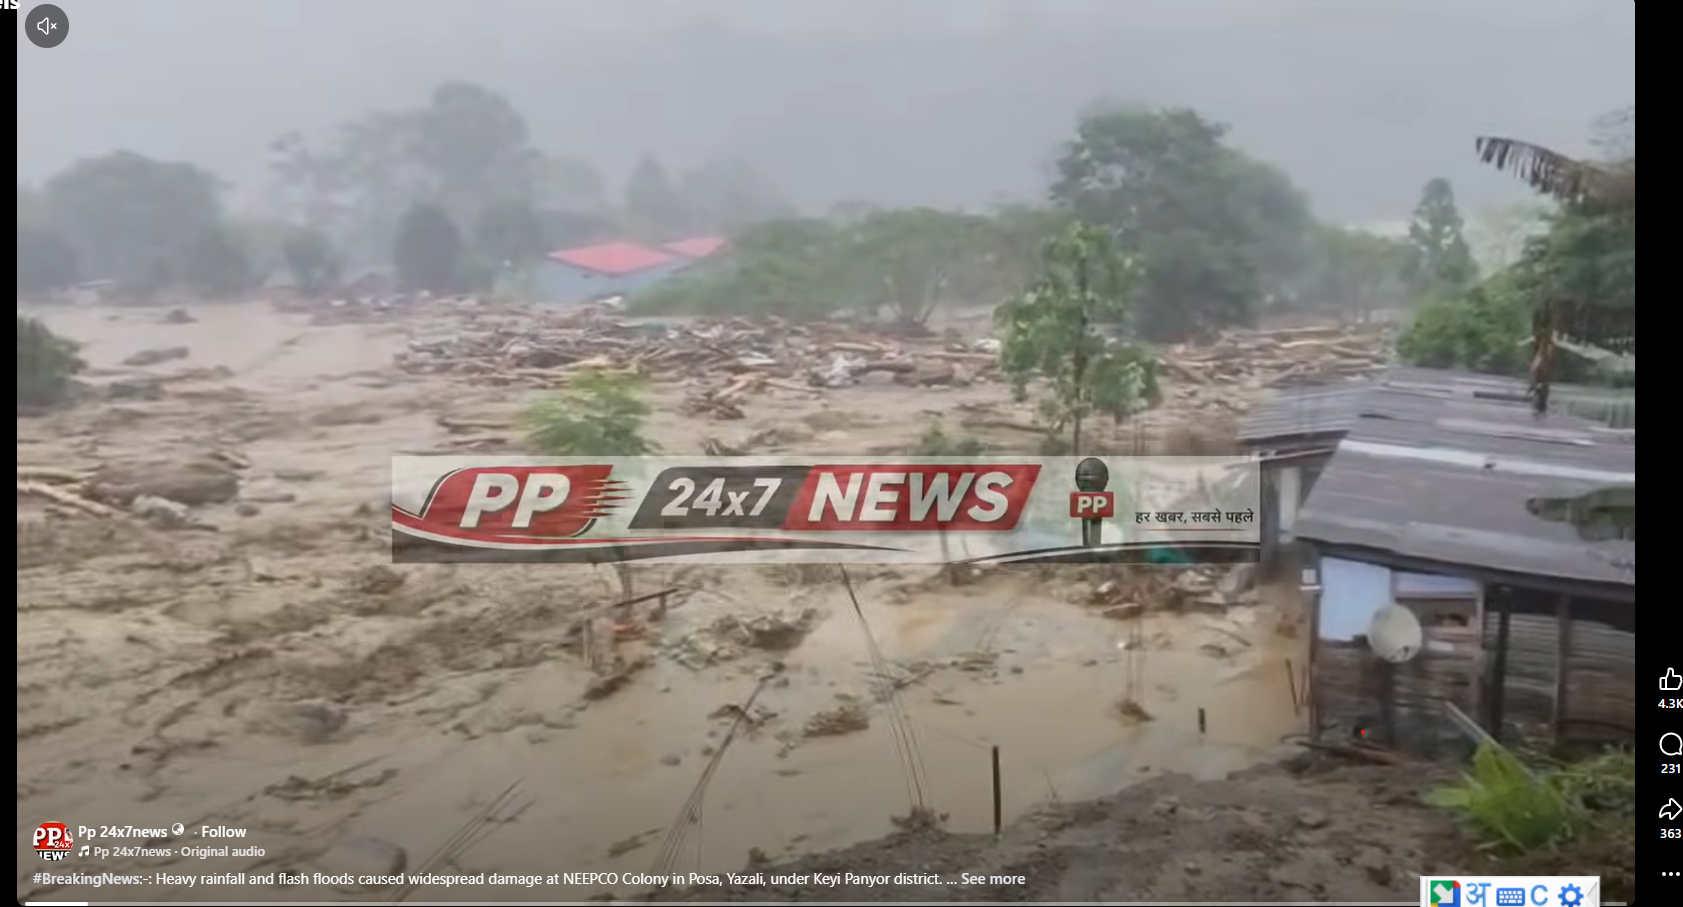
Additionally, we found visuals matching those in the viral video in a 4-minute-35-second video posted on the Press Trust of India’s X account on June 24, 2026. According to media reports, around three people were killed in the floods in Nipko Colony, while approximately 18 houses were swept away.
https://x.com/PTI_News/status/2069747746525835341
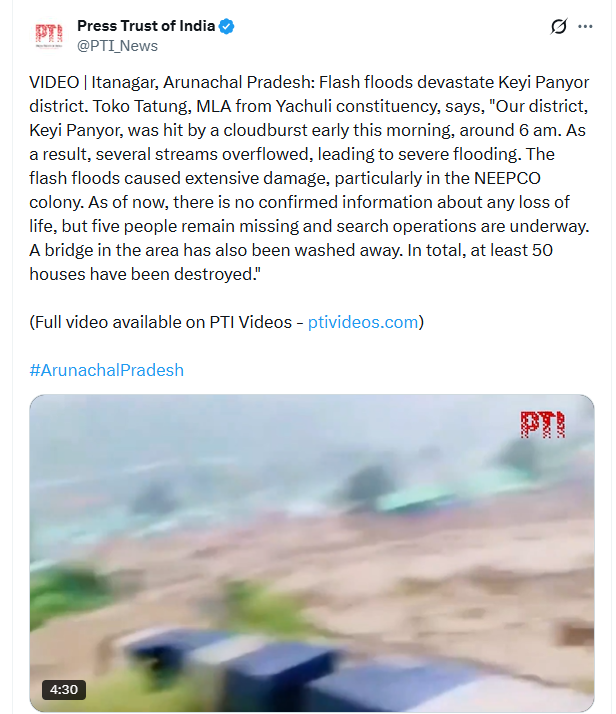
Conclusion
The evidence gathered during our research clearly establishes that the video being shared as footage of the floods in Nepal’s Rasuwa area is actually from the floods that struck Keyi Panyor district in Arunachal Pradesh on June 24.

Along with the loss of important files and information, data loss can result in downtime and lost revenue. Unexpected occurrences, including natural catastrophes, cyber-attacks, hardware malfunctions, and human mistakes, can result in the loss of crucial data. Recovery from these without a backup plan may be difficult, if not impossible.
The fact is that the largest threat to the continuation of your organization today is cyberattacks. Because of this, disaster recovery planning should be approached from a data security standpoint. If not, you run the risk of leaving your vital systems exposed to a cyberattack. Cybercrime has been more frequent and violent over the past few years. In the past, major organizations and global businesses were the main targets of these attacks by criminals. But nowadays, businesses of all sizes need to be cautious of digital risks.
Many firms might suffer a financial hit even from a brief interruption to regular business operations. But imagine if a situation forced a company to close for a few days or perhaps weeks! The consequences would be disastrous.
One must have a comprehensive disaster recovery plan in place that is connected with the cybersecurity strategy, given the growing danger of cybercrime.
Let’s look at why having a solid data security plan and a dependable backup solution are essential for safeguarding a company from external digital threats.
1. Apply layered approaches
One must specifically use precautionary measures like antivirus software and firewalls. One must also implement strict access control procedures to restrict who may access the network.
One must also implement strict access control procedures to restrict who may access the network.
2. Understand the threat situation
If someone is unaware of the difficulties one should be prepared for, how can they possibly expect to develop a successful cybersecurity strategy? They can’t, is the simple response.
Without a solid understanding of the threat landscape, developing the plan will require a lot too much speculation. With this strategy, one can allocate resources poorly or perhaps completely miss a threat.
Because of this, one should educate themselves on the many cyber risks that businesses now must contend with.
3. Adopt a proactive security stance
Every effective cybersecurity plan includes a number of reactive processes that aren’t activated until an attack occurs. Although these reactive strategies will always be useful in cybersecurity, the main focus of your plan should be proactiveness.
There are several methods to be proactive, but the most crucial one is to analyze your network for possible threats regularly. your network securely. Having a SaaS Security Posture Management (SSPM) solution in place is beneficial for SaaS applications, in particular.
A preventive approach can lessen the effects of a data breach and aid in keeping data away from attackers.
4. Evaluate your ability to respond to incidents
Test your cybersecurity disaster recovery plan’s effectiveness by conducting exercises and evaluating the outcomes. Track pertinent data during the exercise to see if your plan is working as expected.
Meet with your team after each drill to evaluate what went well and what didn’t. This strategy enables you to continuously strengthen your plan and solve weaknesses. This procedure may be repeated endlessly and should be.
You must include cybersecurity protections in your entire disaster recovery plan if you want to make sure that your business is resilient in the face of cyber threats. You may strengthen data security and recover from data loss and corruption by putting in place a plan that focuses on both the essential components of proactive data protection and automated data backup and recovery.
For instance, Google distributes all data among several computers in various places while storing each user’s data on a single machine or collection of machines. To prevent a single point of failure, chunk the data and duplicate it across several platforms. As an additional security safeguard, they give these data chunks random names that are unreadable to the human eye.[1]
The process of creating and storing copies of data that may be used to safeguard organizations against data loss is referred to as backup and recovery. In the case of a main data failure, the backup’s goal is to make a duplicate of the data that can be restored.
5. Take zero-trust principles
Don’t presume that anything or anybody can be trusted; zero trust is a new label for an old idea. Check each device, user, service, or other entity’s trustworthiness before providing it access, then periodically recheck trustworthiness while access is allowed to make sure the entity hasn’t been hacked. Reduce the consequences of any breach of confidence by granting each entity access to only the resources it requires. The number of events and the severity of those that do happen can both be decreased by using zero-trust principles.
6. Understand the dangers posed by supply networks
A nation-state can effectively penetrate a single business, and that business may provide thousands of other businesses with tainted technological goods or services. These businesses will then become compromised, which might disclose their own customers’ data to the original attackers or result in compromised services being offered to customers. Millions of businesses and people might be harmed as a result of what began with one infiltrating corporation.
In conclusion, a defense-in-depth approach to cybersecurity won’t vanish. Organizations may never be able to totally eliminate the danger of a cyberattack, but having a variety of technologies and procedures in place can assist in guaranteeing that the risks are kept to a minimum.
