
#FactCheck: Old Salman Khan Video From 2019 Misleadingly Shared as Eid Post
Executive Summary:
A video of actor Salman Khan is being widely shared on social media with the claim that he posted a special video on the occasion of Eid. However, a research by the CyberPeace found the claim to be misleading. The viral video is not recent but dates back to 2019. Meanwhile, Salman Khan did share a different video with his family this year.
Claim:
On Facebook, a user shared the viral video on March 21, 2026, with the caption ,“Salman Khan shared a special video on Eid.”
Post link and archive link:
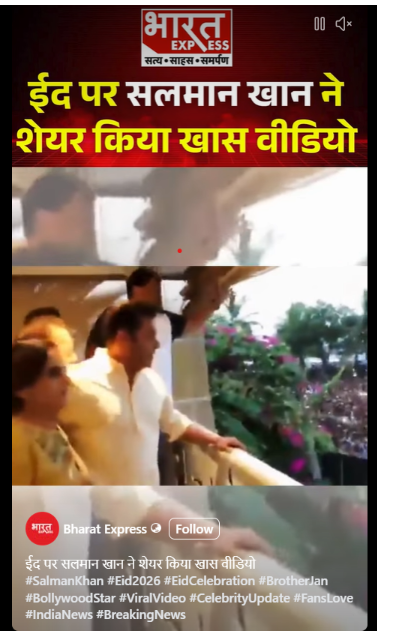
Fact Check
To verify the claim, we examined Salman Khan’s social media accounts. On his Instagram handle, we found a video posted on March 21, 2026, in which he is seen greeting fans from a bulletproof balcony along with his family on the occasion of Eid.
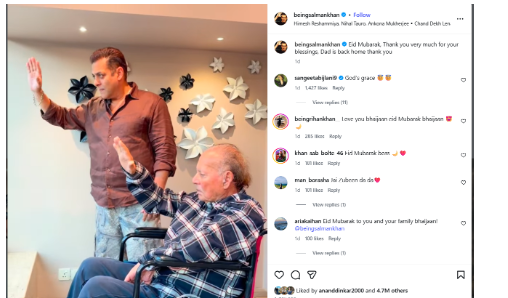
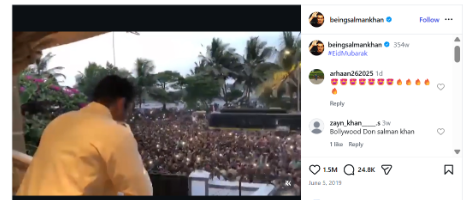
This video is completely different from the viral clip and has no connection to it. Further, we extracted keyframes from the viral video and conducted a reverse image search using Google Lens. During the research, we found the same video on Salman Khan’s Instagram account, where it was originally posted on June 5, 2019.
Post link:
https://www.instagram.com/p/ByVMS6alo76/?igsh=MTA3ZDBqdGlidmRhMQ%3D%3D
Conclusion:
The viral claim is misleading. The video being shared is not recent but from 2019. Salman Khan did share a video this year, but it is different from the one going viral.

Related Blogs
With AI touching new milestones everyday an increasing need for making it secure is also arising. As these AI companies increase their operations and position in the market as providers of powerful tools in the market. A recent concern due to Anthropic's recent privacy policy update which will be effective from July 8, 2026 shows how companies have begun expanding the amount of personal information they collect in the name of safety, compliance, and trust. While they are being demonstrated as measures to improve safety of users and prevent abuse, it raises important questions about privacy, biometric data, surveillance, data retention, and user autonomy, some of which we will be addressing in this article.
Identity Verification of consumers
One of the most notable update to Anthropic's privacy policy is the category of "Verification Data." According to the policy, users may be asked to verify their age or identity in certain circumstances. Depending on the verification method, Anthropic may collect:
- Images of government-issued identity documents;
- Information appearing on those documents, including identification numbers and date of birth for age verification;
- Photographs or videos of the user;
- Facial geometry templates, which may constitute biometric data under certain legal frameworks; and
- The outcome of the verification process.
At first, this may appear similar to the Know Your Customer (KYC) procedures employed by banks or financial institutions but Claude is not a banking service. It is a consumer AI platform. The issue is not that verification exists, but that the circumstances under which it may be required remain undefined.
THE PROBLEM WITH “CERTAIN CIRCUMSTANCES”
The policy refers to verification being required in "certain circumstances." The public notification from Anthropic mentions that these circumstances may include access to particular features, routine platform integrity checks, abuse prevention mechanisms, policy enforcement activities, or legal compliance obligations. The ambiguity of this phrase raises important concerns. From a user perspective, it is difficult to determine, When verification may be triggered ? Whether verification applies only to suspicious accounts ? Whether access to future features may depend upon verification ? Whether users in particular regions will face more frequent verification requirements ? Whether verification requests may increase as AI regulation expands ? This broad language and discretionary power that the company has along with flexibility in the hands of the company creates uncertainty for users who may have initially joined a platform expecting only an email address and payment information to be required.
Government IDs collection: A new risk category
Almost all AI services have operated without collecting government-issued identity documents. Once a company begins processing such information, the privacy implications change dramatically. Because government issued IDs contain: Full legal names, Dates of birth, Identification numbers, Addresses, Photographs and information regarding nationality. When companies collect these documents, they will have an important database of highly sensitive personal information. Even if the company itself does not retain the documents indefinitely, the existence of a verification process introduces additional privacy and security risks. As per Anthropic has stated that identity verification is conducted through third-party providers such as Persona. According to article on the official site titled ‘Identity verification on Claude’, Persona stores the identity documents and selfie data, while Anthropic retains access to verification records when necessary. From the user's perspective, several important realities remain: First, the data still exists somewhere. Second, another third party organization is now involved in processing highly sensitive personal information. Third, Anthropic retains the ability to access verification records under certain circumstances. Therefore, although Anthropic may not directly maintain copies of every uploaded identity document, the practical result remains that sensitive information enters a broader ecosystem of entities and systems. Identity documents today are among the most valuable forms of personal information from the perspective of fraudsters, cybercriminals, and malicious actors. Therefore, any system that handles such documents becomes an attractive target for attack.
More information on persona’s government ID verification- https://withpersona.com/blog/what-is-government-id-verification
The Biometric Dimension
Another significant aspect of the update is the reference to facial geometry templates. Unlike passwords, biometric identifiers cannot easily be changed if compromised. A person can replace a password or even obtain a new identification card, but they cannot simply obtain a new face. Facial geometry templates are sensitive because they enable automated identity matching. Although these templates, as claimed, are not equivalent to photographs, they are nevertheless derived from unique physical characteristics of a person. In many jurisdictions, including parts of the European Union and several U.S. states, biometric data receives enhanced legal protection because of its permanence and sensitivity, let us see how it unfolds in these jurisdictions.
The Unanswered Retention Question
It is unclear in the policy as to how long the data will be retained because retention limits serve as one of the most important safeguards in modern privacy law, they have given another vague answer that “They're bound to protect it with industry-standard security controls and delete it in line with the retention limits we've set and applicable law.” The longer sensitive information remains stored, the greater the likelihood of unauthorized access, misuse, accidental disclosure, or legal compulsion.
Court Orders and Government Access
Anthropic may be required to disclose information pursuant to valid legal processes such as subpoenas, court orders, warrants, or regulatory directives. The existence of identity verification records means that future requests could potentially be linked to verified identities rather than pseudonymous accounts. This does not mean governments receive unrestricted access to user data. However, it does mean that once identity verification information exists within a company's ecosystem, it may become subject to lawful disclosure requirements. The privacy implications are therefore materially different from those associated with anonymous or pseudonymous AI usage.
Shifting Responsibility onto Users
Another concern is that the privacy policy states that users are responsible for ensuring they possess the necessary rights, permissions, or authority when uploading files, connecting third-party services, or instructing Claude to retrieve information. Anthropic is effectively informing users that they bear responsibility for ensuring that uploaded or connected data is lawfully accessible. As AI assistants gain greater capabilities, this transfer of responsibility from platform to user is likely to become increasingly common. Beyond individual privacy, Anthropic's verification policy also raises larger questions about data sovereignty and the cross-border movement of sensitive personal information. In India, the Justice K.S. Puttaswamy (Retd.) v. Union of India judgment recognized privacy as a fundamental right under Article 21 of the Constitution, affirming that individuals have the right to informational self-determination and control over their personal data. Yet, under Anthropic's verification framework, an Indian user may be required to upload a government-issued identity document and biometric information, which are processed by Persona, a U.S.-based identity verification company acting on behalf of Anthropic. Although users voluntarily consent to this process, it nevertheless results in highly sensitive identity information crossing national borders and entering the control of foreign private entities governed primarily by foreign contractual arrangements and multiple legal regimes. While governments issue identity documents as sovereign instruments of citizenship, their verification and processing are increasingly outsourced to multinational technology companies. Questions arise not only about how securely such information is handled, but also about which country's laws ultimately govern access, retention, disclosure, and accountability when personal data leaves the jurisdiction in which it originated. Under the Digital Personal Data Protection Act, 2023, cross-border transfer of personal data is generally permitted unless the Central Government specifically restricts transfers to certain jurisdictions. Therefore, a foreign company processing identity documents is not, by itself, unlawful but this legality does not eliminate legitimate concerns. Users realistically have limited bargaining power and little practical understanding of how long their identity documents, biometric templates, or verification records will be retained, who within the corporate ecosystem may access them, or how they may be disclosed pursuant to foreign legal processes.
Conclusion
The policy is commendable in some respects because it openly identifies the categories of information that may be collected rather than obscuring them behind vague terminology. However, important concerns remain regarding the extent of verification triggers, the handling of biometric information, the absence of clearly disclosed retention periods, and the long-term implications of linking AI accounts to government-issued identities. As AI systems become more integrated into daily life, these questions will likely become central issues in debates about digital privacy, surveillance, autonomy, and the future governance of artificial intelligence.
Introduction
Valentine’s Day celebrates the bond between people, their romantic love, and their deep relationships with others. The increasing use of digital platforms in modern relationships has created a situation where cybercriminals use this time of year to exploit human emotions for money-making schemes. The period around 14 February often sees a rise in online romance scams, phishing attacks, and fake shopping websites that specifically target people who are emotionally vulnerable and active online. People need to be aware of these scams because this awareness helps them protect their personal information and their financial resources.
The Rise of Romance Scams
Modern romance scams have evolved from their original form because criminals now execute their schemes through more advanced methods. Fraudsters create authentic-looking fake identities, which they use to deceive victims through dating applications, social media platforms and networking websites. The profiles use stolen images and fake job histories, together with convincing emotional stories, which help them establish trust with potential victims.
Scammers usually begin their deception after they have built an emotional connection with their targets. Once trust is established, they introduce a crisis or an opportunity that pressures the victim to act quickly. This is often presented as a problem that needs urgent help or a chance that should not be missed, such as:
- A sudden medical emergency that requires money for treatment
- Requests for travel expenses to finally come and meet in person
- Fake investment opportunities that promise quick or guaranteed returns
- Demands for customs, courier, or clearance fees to release a supposed package or gift
They make the victim give money to them and buy gift cards and handle personal banking details. The scam takes place for several weeks or months until the victim starts to show doubt about what is happening. The psychological manipulation that occurs in romance scams causes severe harm to their victims. Victims experience two types of damage because criminals steal their money, and they suffer emotional pain, and their social standing gets damaged.
Fake E-Commerce and “Valentine’s Deals”
Valentine's Day marks the beginning of a shopping rush, which leads people to buy various gifts, including flowers, jewellery and customised products, as well as making reservations for events. Cybercriminals create fake websites to exploit this demand by providing fake discounts and temporary promotional offers.
Common warning signs include:
- Newly registered domains that lack valid user reviews
- Websites that contain multiple spelling mistakes and display poor design
- Payment requests through methods that cannot be tracked
- Online platforms that lack secure payment processing systems
Consumers who make purchases on such sites face the risk of losing money while their card information is stolen for future fraudulent activities.
Phishing in the Name of Love
During the holiday season, phishing campaigns increase their focus on particular targets. Users may receive:
- Valentine's Day discount emails
- Messages that claim to show secret admirer intentions
- Links that lead to supposed romantic surprises
- Delivery notifications that inform about unreceived gifts
Malicious links result in credential theft, malware installation and unauthorised financial transactions. At first glance, these attacks show resemblance to authentic brands and logistics companies, which makes them hard to identify.
Investment and Crypto Romance Fraud
A rising type of romance scams now uses cryptocurrency and online trading platforms as their new approach. Scammers who establish trust with their victims will convince them to invest in digital assets that appear to generate high returns. The fake dashboards display excellent investment results to convince investors to commit more funds. The process stops when they block all withdrawal requests and stop all contact with the user. The combination of emotional manipulation with financial fraud shows how cybercrime develops according to technological advancements.
Why Seasonal Scams Work
Seasonal scams succeed because they match the predictable behaviour patterns that people exhibit during specific times of the year. During Valentine’s season:
- People experience their highest emotional vulnerability
- People shop more frequently through online platforms
- People use digital platforms at increased rates
- Users will decrease their level of scepticism while trying to establish connections with others
Cybercriminals use urgent situations together with emotional ties and social norms as their primary attack methods. The combination of psychological triggers and digital convenience creates fertile ground for deception.
CyberPeace Recommendations for Staying Safe This Valentine’s Season
The digital platforms provide people who search for connections with valuable opportunities to connect with others, yet users must remain careful about their online activities. People can protect themselves from online fraud by following these steps:
- They should confirm identity details before they give away their private data.
- They should not send money to people whom they met only through internet platforms.
- They should verify website ownership and examine customer feedback before making online purchases.
- They should activate multi-factor authentication for their social media accounts and financial accounts.
- People should treat unexpected links with great care, especially those links that create a sense of urgency.
- The Cybercrime reporting portal www.cybercrime.gov.in with 24x7 helpline 1930 is an effective tool at the disposal of victims of cybercrimes to report their complaints.
- In case of any cyber threat, issue or discrepancy, you can also seek assistance from the CyberPeace Helpline at +91 9570000066 or write to us at helpline@cyberpeace.net. Immediate reporting protects victims and helps to combat cybercrime.
Conlusion
Online safety during festive seasons requires shared responsibility among multiple parties. Digital resilience is strengthened through the combined efforts of platforms, financial institutions, regulators, and civil society organisations. The digital ecosystem becomes safer through three essential elements, which include awareness campaigns, stronger verification systems, and timely reporting mechanisms.
Valentine’s Day centres on the building of trust between people who want to connect with each other. To maintain trust in digital environments, users need to practice digital literacy skills, which should be shared by everyone. People who stay updated about cybersecurity threats can celebrate Valentine’s Day more safely, because their expressions of love remain protected from online scams.
References
- https://www.cloudsek.com/blog/valentines-day-cyber-attack-landscape-exploiting-love-through-digital-deception
- https://about.fb.com/news/2025/02/how-avoid-romance-scams-this-valentines-day/
- https://www.fbi.gov/contact-us/field-offices/sanfrancisco/fbi-san-francisco-warns-romance-scams-increasing-across-the-bay-area-this-valentines-day
- https://abc11.com/post/romance-scams-surge-ahead-valentines-day/18581079/
- https://www.moneycontrol.com/technology/5-common-online-scams-you-should-avoid-this-valentine-s-day-article-13820108.html
Executive Summary
A video is being widely shared on social media with the claim that a female journalist was assaulted by the Delhi Police. The video is being shared with the claim that a female police officer from the Delhi Police is seen assaulting and misbehaving with a female journalist. In the video, a woman wearing a police uniform can be seen allegedly assaulting another woman. Research by the Research Wing of CyberPeace found that the video is actually from a movie shoot. Social media users are sharing it with a misleading claim.
Claim
Social media users shared the video with the caption: “A female journalist is being beaten up by the Delhi Police. What will happen to ordinary people?”
https://www.facebook.com/reel/1599067985010003
https://archive.ph/mgCqt

Fact Check
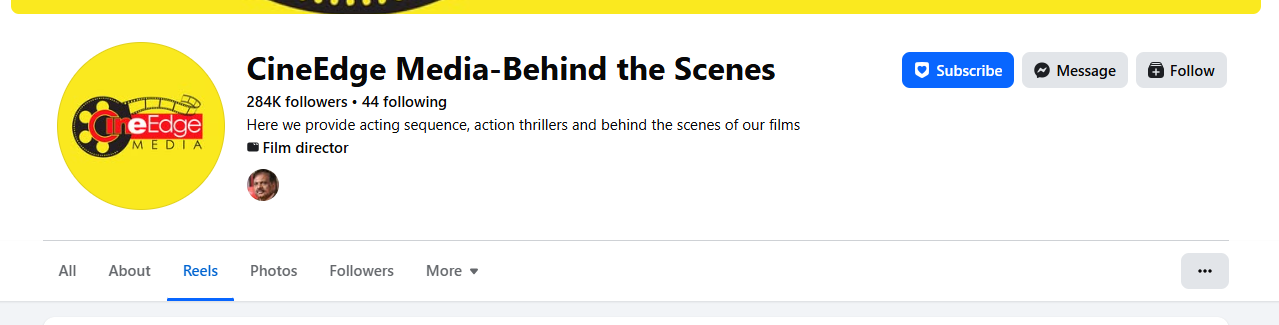
While investigating the video being shared with the claim that a female journalist was assaulted by the Delhi Police, we conducted a reverse image search of its keyframes. During the search, we found the same video on a Facebook page called ‘CineEdge Media-Behind the Scenes’. The video was uploaded on the page on June 26, 2026. The description and hashtags used with the video indicate that it is not footage of an actual police action, but is related to a film shoot.
https://www.facebook.com/reel/1542614027395118

In addition, the bio of the aforementioned Facebook page states that it posts videos featuring film acting sequences, action thrillers, and behind-the-scenes footage from movies
https://www.facebook.com/profile.php?id=61578948364025&sk=reels_tab
As part of the research, we also examined the CineEdge Media YouTube account. We found that the account has uploaded videos related to films and acting

Conclusion
The evidence gathered during our research makes it clear that the video being shared with the claim that a female journalist was assaulted by the Delhi Police is actually footage from a movie shoot. The video was found on a social media page that shares film-related content, including acting sequences, action scenes and behind-the-scenes footage. Therefore, the claim that the video shows a female journalist being assaulted by the Delhi Police is misleading.
