
#FactCheck-Old Accident Involving Delhi Police Head Constable Falsely Linked to CJP Protest
Executive Summary
A social media post is being widely circulated claiming that Delhi Police personnel Amit died during the Cockroach Janata Party (CJP) ‘Sansad Chalo’ protest held on July 20, 2026. The post attempts to link his death to violence that allegedly took place during the demonstration. CyberPeace Research Wing’s research found the claim to be false. The research revealed that the death of Head Constable Amit was not related to the CJP protest held on July 20. He died on July 15 after being hit by a speeding vehicle while on duty at Singhu Border. An old accident has been falsely linked to the recent protest through a misleading claim.
Claim:
A Facebook user shared a post on July 23, 2026, claiming that a police personnel was martyred during the alleged protest carried out by “student goons and their supporters from Congress and Kejriwal’s party” on July 20. The user further claimed that the protest was responsible for the death of a police personnel and questioned criticism over alleged police action against protesters.
The post’s link, archive link and screenshot are provided below:
https://www.facebook.com/photo?fbid=3562630610568369&set=a.100838436747621
https://ghostarchive.org/archive/m8QM8

Fact Check:
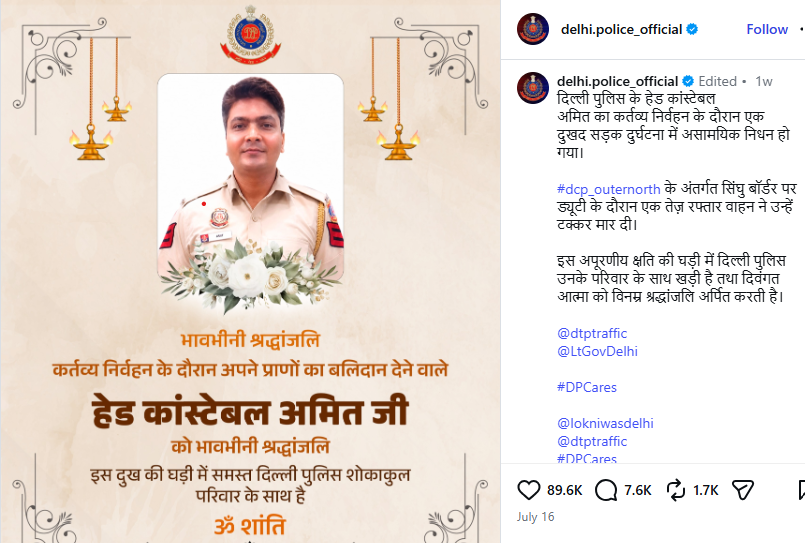
To verify the authenticity of the viral claim, the Desk first examined the official social media accounts of Delhi Police. During the research, the Desk found a post shared on Delhi Police’s official Instagram account on July 16, 2026, which contained the same image being circulated in the viral post.
https://www.instagram.com/p/Da19BQxEmQv/?igsh=cnN1bXZhaHg5OWRs
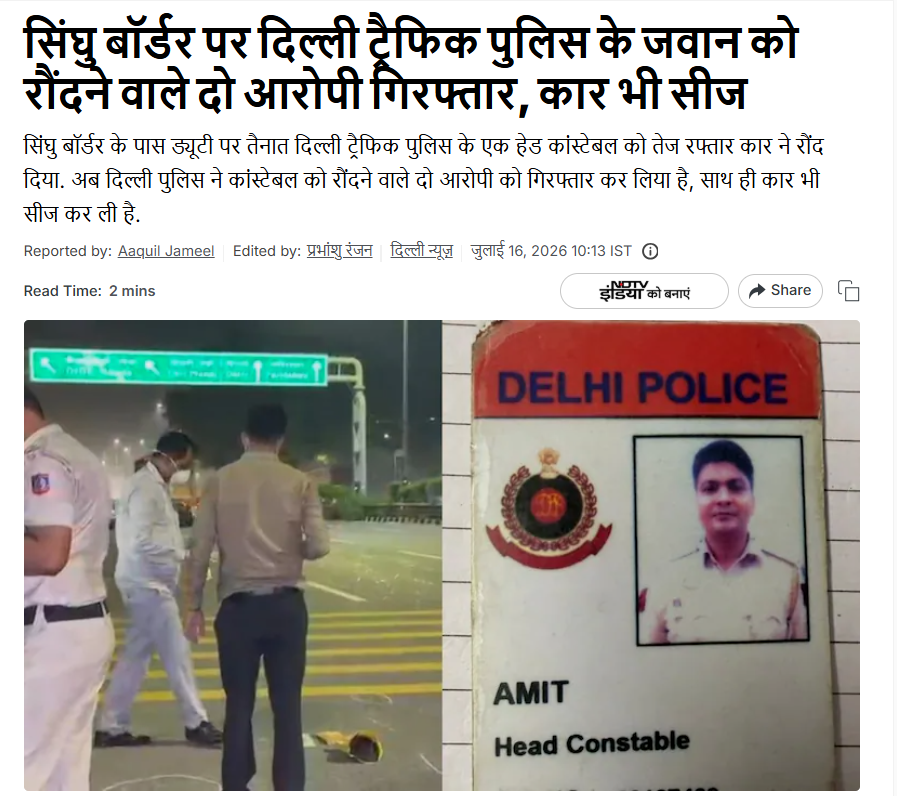
In the next stage of the research, the Desk found an NDTV report published on July 16, 2026. According to the report, Delhi Police had arrested two accused in connection with the death of Head Constable Amit. The arrested individuals were identified as Kuldeep alias Karan and Neeraj. The report stated that police had also seized the vehicle bearing registration number DL11CG2268, which was involved in the accident. An FIR was registered at Alipur Police Station and further research was underway.
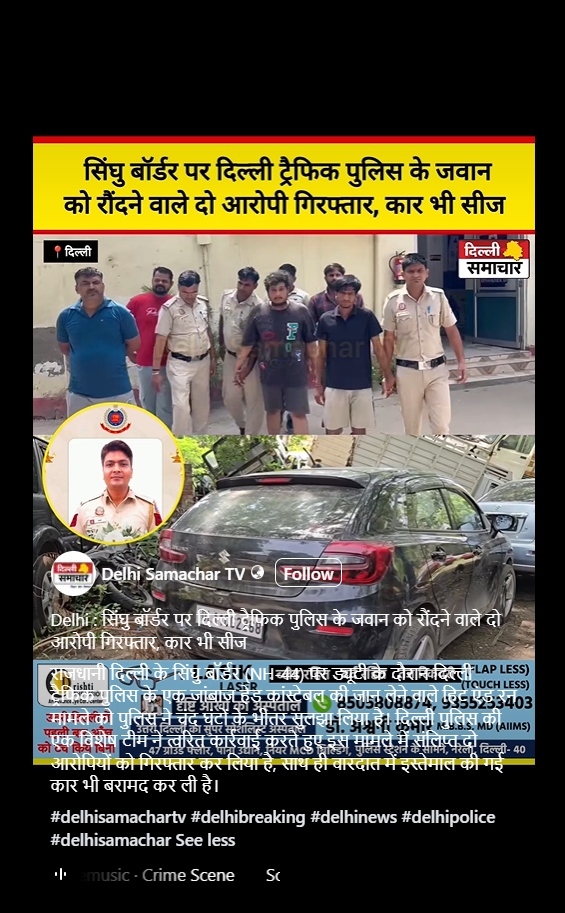
Further research led the Desk to a related post on the Facebook page of Delhi Samachar TV. According to the post, the hit-and-run case involving Head Constable Amit, who was hit while performing duty at Singhu Border (NH-44), was solved by Delhi Police within hours. The police team arrested two accused and recovered the vehicle used in the incident.
The post’s link and screenshot are provided below:
https://www.facebook.com/reel/1006635078843860
Conclusion:
The research established that the death of Delhi Police Head Constable Amit was not connected to the CJP ‘Sansad Chalo’ protest held on July 20, 2026. Amit died on July 15 after being hit by a speeding vehicle while on duty at Singhu Border. The old accident is being falsely linked to the recent protest with a misleading claim.

Related Blogs

Introduction
The recent investigation of Patan Cyber Crime Police as part of Operation Mule Hunt 2.0 reveals the sheer scale and intricacy of India's burgeoning cyber fraud economy. Police found that a total of 13 current accounts were being operated at a cooperative bank in the Patan district of Gujarat and used for siphoning 398.43 crore of cyber fraud transaction data on 228 cybercrime cases across states. Further investigations against 14 current account holders and intermediaries show the indispensability of mule accounts in laundering criminal money. The recent incident cannot be taken as isolated; the story points at a formalised and industrialised fraud economy with a robust banking infrastructure, a growing payment gateway, and complex networks.
What Is a Mule Account and Why Should You Care?
The term "mule account" is benign but plays a critical role in modern cybercrime networks. The Reserve Bank of India defines a mule account as a bank account that serves as a vehicle to transfer money proceeds from unlawful transactions and can be operated by people coerced by the prospect of high earnings or by way of inducement.
This mechanism can be witnessed through the investigation of the Patan cybercrime incident, where an investor can be defrauded by a fake investment website, employment fraud, or a digital arrest scheme. After transactions from the victim account, funds would quickly flow into the mule account, which would be held by a legitimate KYC customer. These transactions would then be passed on, between 1 lakh and 5 lakh transactions within hours, to multiple accounts as alleged by the Indian Cyber Crime Coordination Centre (I4C) before they get difficult to trace by being passed through informal channels or converted to cryptocurrency.
In the Patan case, it is alleged that the middlemen enticed locals and offered commissions to open firms and current accounts at Harij Nagrik Sahakari Bank and subsequently gave up their ATM cards, checkbooks, SIMs, and net banking facilities to the operators of the account. It is estimated that such accounts channeled an amount of 398.43 crore to 228 Indian cybercrime cases.
The Scale of India's Mule Account Crisis
The scale of the mule account ecosystem is reflected in India's rapidly worsening cybercrime statistics. As of data from the National Cyber Crime Reporting Portal (NCCRP), a total of 22.68 lakh complaints were registered in 2024, a jump by 42% from 2023. This was not even half the rate of financial loss, which jumped by 206% in 2023 (22,845 crore) and stood at 22,495 crore in 2025 (complaints jumped to 28.15 lakh). The increase in fraudulent transactions therefore outweighs the stability in financial losses significantly.
Mule accounts are the backbone of this crime network. To curb this phenomenon, the Indian Cyber Crime Coordination Centre (I4C) launched a Suspect Registry along with Indian banks and financial institutions in September 2024. 24.67 lakh accounts of suspected mules were identified in this, preventing over 8,031 crore in fraudulent transactions. Despite these efforts, a recent statement from the ED found over 12,000 crore being routed via mule accounts, shell firms, and cryptocurrency.
This isn't isolated to certain banks. 2024 alone saw over 65,000 mule accounts detected in Karnataka. By analyzing the Citizen Financial Cyber Frauds Reporting and Management System, about 40,000 such accounts were detected in SBI branches, and thousands more were detected across the PNB, Canara Bank, Kotak Mahindra Bank, and Airtel Payments Bank. The Patan case also clearly highlights that cooperative banks' lack of compliance and lower levels of transaction-monitoring systems contribute to easily creating and using mule accounts.
Operation Mule Hunt: Gujarat's Coordinated Offensive
This bust in Patan is just one manifestation of a much wider coordinated effort by the state government. Operation Mule Hunt 1.0, which ran from November to December 2025 across the state of Gujarat, was a month-long campaign by Gujarat Police's Cyber Centre of Excellence (CCOE) that unearthed 2,289 crore of fraudulent transactions, led to the registration of 565 FIRs, arrest of 638 accused, and impounding of 913 mule accounts with connections to over 4,000 cases of cybercrime nationwide.
This was followed up with the second installment of the operation, which was kicked off in all districts of Gujarat in 2026. The two-week campaign, which began across the state on January 8 this year, resulted in the Surat City Police alone arresting 77 people and uncovering close to 23.85 crore in fraudulent transactions. In what looks like one of the single largest single-district bust-ups in the operation, the Patan incident itself, with a staggering 398.43 crore routed through only 13 accounts, is remarkable.
The extraordinary nature of the operation is seen in the intelligence capabilities that drove it. It wasn't that police accidentally stumbled upon the Patan network; they worked back on it. After using data from the union government’s inter-agency platform, SAMANVAYA, a coordination platform for data on cybercrimes and the NCCRP, they traced suspicious clusters of transactions in the Harij Nagrik Sahakari Bank accounts to build a chain of evidence connecting the accountholders to the middlemen and, from the middlemen, to the whole ring of fraud. Twenty accused have been chargesheeted under the Bharatiya Nyaya Sanhita (BNS), and fourteen have been arrested, while six are still absconding.
The Human Cost Nobody Talks About
Behind every crore of scam money lies a real person who actually lost the real money. Of the 75%+ fraud losses incurred in 2025, 75% are from investment scams alone. Victims of stock trading scams lost ₹4,636 crore, spread across 2.28 lakh complaints filed in 2024. "Digital arrest" scams, in which fraudsters posing as law enforcement officials psychologically blackmail the victims to transfer money, claimed ₹2,576 crore between 2022 and the first quarter of 2025.
For the victims it's never about the money: it's the retired teacher's lifetime savings from Chhattisgarh, the small trader's capital from Rajkot, the emergency money of the Bhopal family, or just savings from an ordinary person. And the mule accounts' networks are why most of it is never retrieved. Once the money is thrown into the layering chain, it's exponentially more difficult to trace it after every jump.
Then there's another category of victims that often gets overlooked, and they are the mule account holders themselves, many being semi-literate people from semi-urban or rural backgrounds approached with ₹10,000 in commission and with no awareness about the legalities of lending their bank details. With the BNS now they stand to get convicted for grave crimes, but the awareness of this trap is very low.
Recommendations and Suggestions
This isn't something India is facing passively. I4C, along with RBI, has developed Mule Account Hunter software. This software can be used by banks for the detection of suspect accounts through the use of behavioral analysis, device intel, and transaction pattern recognition. The Union Home Minister has directly asked all cooperative banks across the country to adopt this software at the earliest. Failure to do so, he warned, would make consumer safety from cyber fraud incomplete.
Apart from technology, three other areas need to go hand in hand: stringent KYC enforcement for cooperative and small finance banks; the prime locations of the mule recruitment network; greater awareness for the masses regarding the criminal liability one takes up when lending their accounts; and efficient inter-agency coordination so that the intelligence gathered on platforms like SAMANVAYA is converted into arrests before the accounts are dumped and the network reforms in another location.
Operation Mule Hunt 2.0 proves that this is feasible. 13 accounts in a small district of Gujarat. 398 crore. 228 victims. 14 arrested. The pipeline did exist, and it has been broken.
Yet, even as one network is broken, another is forming, somewhere right now. The accounts will appear legitimate. The holders of these accounts may not even realize what they have got into. That is the true danger of the mule accounts and work that cannot stop.
Conclusion
The Patan investigation has clearly shown that mule accounts have now moved from being a subsidiary tool of financial crime to becoming the infrastructure that underpins the economy of cyber-fraud in India. Every financial fraud, including investment fraud, digital arrest fraud, and phishing scams, is backed by a string of real bank accounts where the proceeds of crime are transferred and the trail is obscured. Though attempts such as the I4C Suspect Registry have made attempts to break down this network, it remains an overwhelming task. Robust KYC norms, real-time monitoring of transactions, and coordination between banks, police, and regulators are the key in preventing further industrialisation of cyber financial fraud in India.
References
- https://timesofindia.indiatimes.com/city/ahmedabad/operation-mule-hunt-2-0-gujarat-
- police-bust-rs-398-43-crore-cyber-fraud-14-held/articleshow/131594240.cms?utm_source=contentofinterest&utm_medium=text&utm_campaign=cppst
- https://the420.in/india-cybercrime-2024-42-percent-spike-sims-imei-mule-accounts/
- https://www.thehansindia.com/news/national/ed-explains-how-mule-accounts-and-crypto-networks-enabled-12000-crore-cyber-fraud-1047606
- https://www.zigram.tech/article/mule-accounts-tier-1-tier-2-cities-india/
- https://risk.lexisnexis.com/global/en/insights-resources/article/stopping-money-mules-in-india
- https://timesofindia.indiatimes.com/city/ahmedabad/operation-mule-hunt-2-0-gujarat-police-bust-rs-398-43-crore-cyber-fraud-14-held/articleshow/131594240.cms
Executive Summary:
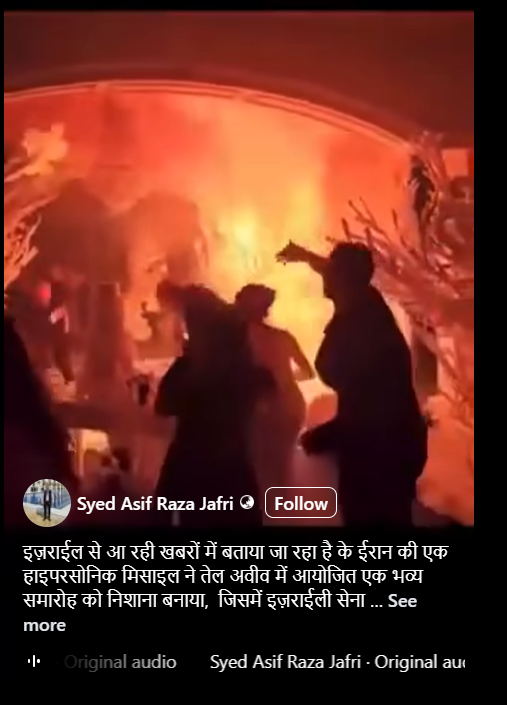
Amid the ongoing conflict involving the United States, Israel, and Iran, a video showing a building engulfed in flames is being widely circulated on social media. In the clip, a large fire can be seen inside a building while several people appear to be running in panic. The video is being shared with the claim that Iran fired a hypersonic missile targeting a ceremony in Tel Aviv, Israel, allegedly killing several Israeli military generals and other prominent figures.
However, research by the CyberPeace found that the claim is false. The video being circulated as footage of an attack in Israel actually predates the current conflict and shows a fire that broke out during a wedding ceremony.
Claim
A Facebook user named “Syed Asif Raza Jafri” shared the video on March 13, 2026, claiming that an Iranian hypersonic missile had struck a grand ceremony in Tel Aviv, where several Israeli military officers, generals, soldiers, and other important personalities were present. According to the post, the attack resulted in multiple casualties.
Source:
- https://www.facebook.com/reel/902182825912364
- https://ghostarchive.org/archive/rZryr
Fact Check
To verify the claim, we began our research using the Google Lens reverse image search tool. Several key frames from the viral video were extracted and searched online.
During the search, we found the same video shared earlier on multiple foreign social media accounts. A Facebook user named “Es de Bombero” from Chile had posted the video on January 17, 2026, describing it in Spanish as footage of a fire that broke out during a wedding celebration.
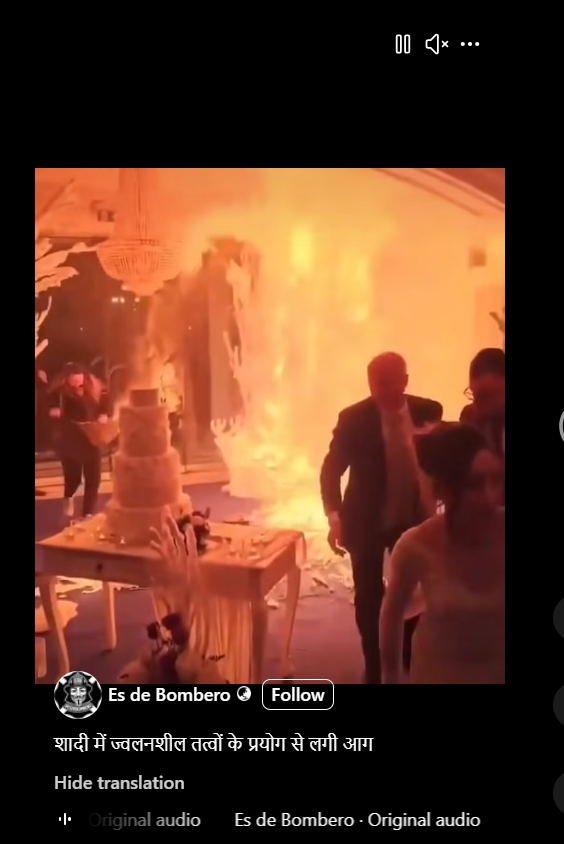
Our research shows that the viral video had been circulating on social media since at least January 15, 2026, well before the escalation of the current conflict. According to a report published on March 1, 2026, by BBC, the large-scale attacks on Iran by the United States and Israel began on February 28, 2026, after which Iran’s Supreme Leader Ali Khamenei was reported dead.
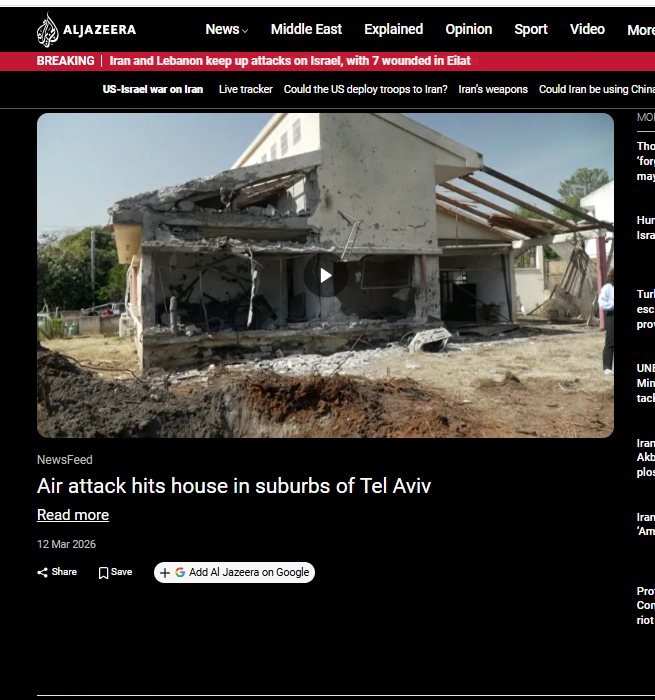
Additionally, a March 12, 2026 report by Al Jazeera stated that a house near Tel Aviv in central Israel was damaged by a rocket reportedly fired by Hezbollah, which has previously carried out joint attacks in coordination with Iran.
Conclusion
The viral video being shared as footage of an Iranian hypersonic missile strike in Tel Aviv is misleading. The clip is an older video of a fire that reportedly broke out during a wedding ceremony and was circulating online before the current conflict began.
While the exact location of the incident shown in the video cannot be independently verified, it is clear that the footage has no connection to the ongoing war between the United States, Israel, and Iran.
Introduction
The traditional logic of workplace security is built on the baseline assumption that an employee would be able to identify a suspicious request by form and/or sound. The rollout of AI-generated voice and video is steadily dismantling this assumption. The authenticated voice of a familiar executive or the face of a colleague in a video meeting is no longer a guarantee of variety. This paper reviews recent survey evidence of deepfake-enabled social engineering, briefly considers the Arup fraud as a case study and reviews Gartner's and United States government agency guidance. It argues that organisations should stop relying on employees to spot fakes and instead build independent verification, limited authority and escalation into the everyday workflows that move money and grant access, long before a convincing fake can do damage.
The Scale of the Threat
Gartner revealed in September 2026 that the survey (of 297 senior cybersecurity leaders, March to May 2026) found 41% had been subject to at least one deepfake social engineering attack during an audio employee call in the last 12 months; 36% of deepfake social engineering attacks happened on a video call with an employee in the last 12 months. Gartner concluded that AI makes social engineering more prolific, personalised and believable, while it makes common detection signals less dependable.
The survey also highlights the continued use of older methods. 79% of respondents reported at least one email phishing, spear-phishing, or business email compromise incident, and 58% vishing or smishing. Deepfakes are not replacing tried-and-true techniques but supplementing them. Craig Porter, a director analyst at Gartner, said, "Attackers can combine phishing, business email compromise, synthetic media and the aggregation of personal context across multiple channels, yet most attacks still rely on compromised credentials, simple account takeover and poor recovery processes."
Why it matters: Ability to receive requests can now be routed through the same communication systems that high-trust messages go through. With information gathered from the web, as well as synthetic voice and video, fraudsters can impersonate executives, vendors, suppliers, colleagues, or customers.
Why Spotting the Fake Is Not Enough
The 2024 attack on Arup is an example of this. A finance staff member in an engineering firm in Hong Kong took part in a video conference in which he thought he was speaking to the firm's CFO and others, but all participants were deepfakes. The employee initially suspected a phishing email, but he put aside his doubts after the video call because the participants looked and sounded like colleagues he recognised. He then approved 15 payments of a total HK$200m (US$25.6m). Arup confirmed the voices and faces were fake, though its internal cybersecurity was not breached, and its global CIO, Rob Greig, said attacks of this kind had increased substantially in recent months. The firm's East Asia chairman said staff were warned of increasing attacks of this kind around the world.
This case is instructive because the control that failed was human judgement with a plausible performance. The employee's first reaction was right; it was a video call that overruled this. Detection by the request recipient was the only control.
Government guidance points the same way. A joint information sheet from the NSA, FBI and CISA warns that the most substantial synthetic media threats include impersonating leaders and financial officers and using fraudulent communications to gain access to networks and sensitive information. It advises organisations to have a response plan and to consider technologies that detect deepfakes and establish the provenance of media. Detection tools have a place, but they are one layer, not a foundation.
Building Verification into Workflows
Achyuth Krishna, Head of IT, Information Security and Procurement at Whatfix, says that the real question is no longer 'Can the employee tell that the message is generated by AI?' But whether your organisation has designed its workflow so that a single deceptive interaction cannot become a security incident. "Trust itself has now become a new attack surface," he says.
Gartner's suggested mitigations echo this sentiment. "Porter recommends that CISOs evaluate AI-led social engineering risks with the same level of scrutiny as identity and access risks," the analyst firm said. Among the suggestions that the firm made to organisations that want to defend against AI-led social engineering attempts include establishing secure verification as standard operating procedure for any important request, by whatever means they are communicated, by email, voice, video, collaboration platform or AI system, and using trusted channels of verification as well as stronger authentication for account recovery, privileged access, and payment approval. In terms of design, this suggests a few principles:
1. Before deciding to authorise payments, change privileged access or disclose information, make sure that you get independent confirmation from a different source.
2. This should apply to everyone, including requests that appear to come from a known senior executive, so that employees never need to challenge authority personally.
3. Clearly outline situations where your team needs to stop, confirm, and escalate.
4. Test these procedures in scenarios that are as close to reality as possible rather than just training on an annual basis.
In this case, a simple video call would not have been enough to trigger the release of the money. Validation would have taken place outside the attacker's communication channel.
Extending Identity to AI Agents
As companies open up apps and business data to software agents, Krishna says those agents need their own identities, limited rights, and audit logs. Gartner has also identified that compromised AI apps, prompt injection, and agents acting outside of their bounds are threats that security teams will need to handle.
The logic is the same as in the human case. An agent, given virtually unlimited power, can be misused in exactly the same way that a human employee can be. Seen as identities to be verified, constrained and observed rather than as trusted, remoting extensions of their original creators, agents preserve the principle of limited authority.
Conclusion
Deepfakes have made impersonation cheap, personal and persuasive, and many organisations have already been hit. Detection will remain useful, but it cannot carry the burden alone. The stronger response is structural: independent verification for consequential requests, narrow permissions for people and agents, and regular testing of escalation procedures. The aim is to ensure that no single call, message or agent holds enough unchecked authority to turn a successful deception into a financial loss or a data breach.
Sources
- Tech Observer: Deepfakes are turning trust into a new enterprise security risk
- Gartner: Survey Finds 41% of CISOs Reported At Least One Social Engineering Incident Involving a Deepfake in the Past 12 Months
- Help Net Security: The latest deepfake numbers give CISOs plenty to worry about
- NSA: NSA, U.S. Federal Agencies Advise on Deepfake Threats
- CNN: British engineering giant Arup revealed as $25 million deepfake scam victim (syndicated copy)
