
#FactCheck-Old 2020 Lockdown Video of PM Modi Resurfaces as Recent
Executive Summary
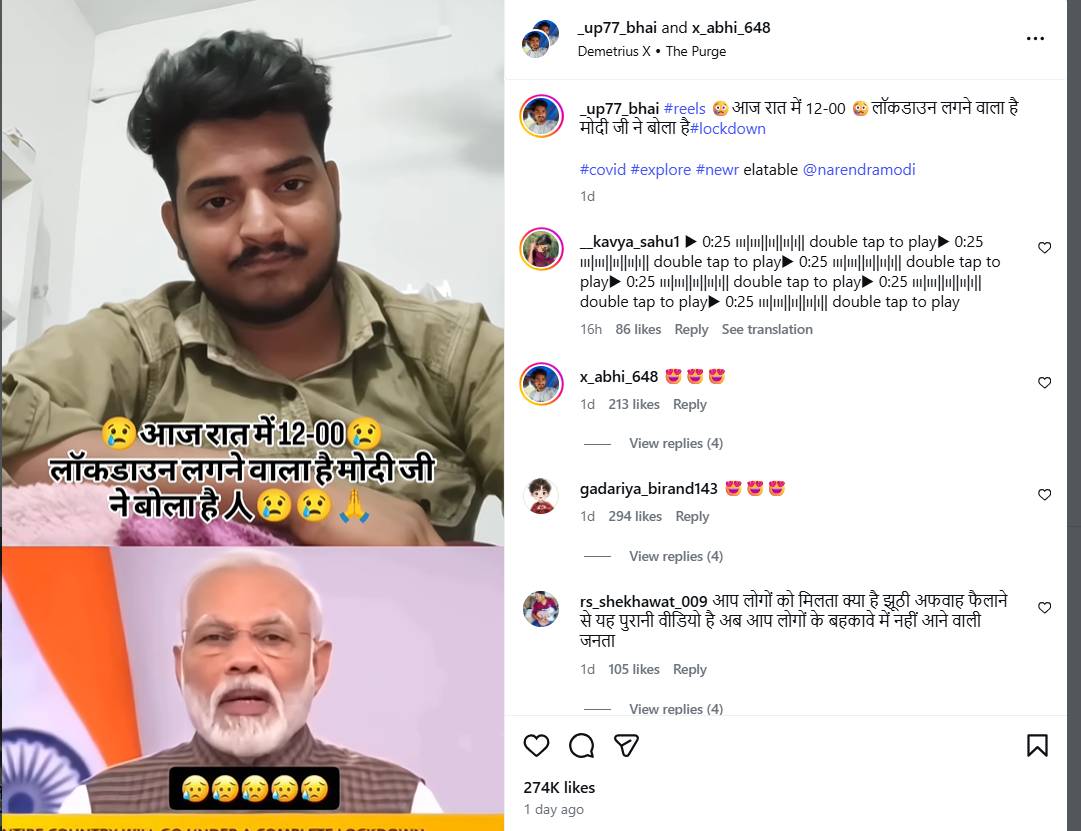
A video is being shared on social media in which Prime Minister Narendra Modi can be heard saying that “a complete lockdown will be imposed from midnight to save the country.” Research by the CyberPeace found the viral claim to be misleading. Our probe revealed that the video is from March 2020, when PM Modi had announced a nationwide lockdown to curb the spread of COVID-19.
Claim:
An Instagram user shared the viral video on March 25, 2026. The link and archive link of the post are given below.
Fact Check:
To verify the claim, we conducted a keyword search on Google. However, we did not find any credible media reports confirming that such a lockdown announcement had been made recently. We then extracted keyframes from the viral video and performed a reverse image search using Google Lens. During this process, we found the same video on a YouTube channel, where it had been uploaded on March 24, 2020.
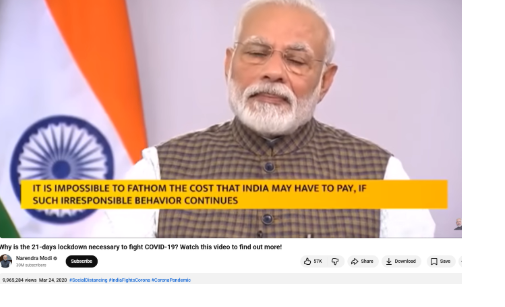
The viral portion of the clip appears around the 40-second mark in the original video.
Conclusion:
Our research found that the viral video is not recent. It dates back to March 24, 2020, when PM Modi announced a nationwide lockdown during the COVID-19 pandemic. The clip is being shared with a misleading claim.

Related Blogs

Executive Summary:
A video gone viral on Facebook claims Union Finance Minister Nirmala Sitharaman endorsed the government’s new investment project. The video has been widely shared. However, our research indicates that the video has been AI altered and is being used to spread misinformation.

Claim:
The claim in this video suggests that Finance Minister Nirmala Sitharaman is endorsing an automotive system that promises daily earnings of ₹15,00,000 with an initial investment of ₹21,000.
Fact Check:
To check the genuineness of the claim, we used the keyword search for “Nirmala Sitharaman investment program” but we haven’t found any investment related scheme. We observed that the lip movements appeared unnatural and did not align perfectly with the speech, leading us to suspect that the video may have been AI-manipulated.
When we reverse searched the video which led us to this DD News live-stream of Sitharaman’s press conference after presenting the Union Budget on February 1, 2025. Sitharaman never mentioned any investment or trading platform during the press conference, showing that the viral video was digitally altered. Technical analysis using Hive moderator further found that the viral clip is Manipulated by voice cloning.

Conclusion:
The viral video on social media shows Union Finance Minister Nirmala Sitharaman endorsing the government’s new investment project as completely voice cloned, manipulated and false. This highlights the risk of online manipulation, making it crucial to verify news with credible sources before sharing it. With the growing risk of AI-generated misinformation, promoting media literacy is essential in the fight against false information.
- Claim: Fake video falsely claims FM Nirmala Sitharaman endorsed an investment scheme.
- Claimed On: Social Media
- Fact Check: False and Misleading

Introduction
Digital Public Infrastructure (DPI) serves as the backbone of e-governance, enabling governments to deliver services more efficiently, transparently, and inclusively. By leveraging information and communication technology (ICT), digital governance systems reconfigure traditional administrative processes, making them more accessible and citizen-centric. However, the successful implementation of such systems hinges on overcoming several challenges, from ensuring data security to fostering digital literacy and addressing infrastructural gaps.
This article delves into the key enablers that drive effective DPI and outlines the measures already undertaken by the government to enhance its functionality. Furthermore, it outlines strategies for their enhancement, emphasizing the need for a collaborative, secure, and adaptive approach to building robust e-governance systems.
Key Enablers of DPI
Digital Public Infrastructure (DPI), the foundation for e-governance, relies on common design, robust governance, and private sector participation for efficiency and inclusivity. This requires common principles, frameworks for collaboration, capacity building, and the development of common standards. Some of the key measures undertaken by the government in this regard include:
- Data Protection Framework: The Digital Personal Data Protection (DPDP) Act of 2023 establishes a framework to ensure consent-based data sharing and regulate the processing of digital personal data. It delineates the responsibilities of data fiduciaries in safeguarding users' digital personal data.
- Increasing Public-Private Partnerships: Refining collaboration between the government and the private sector has accelerated the development, maintenance, expansion, and trust of the infrastructure of DPIs, such as the AADHAR, UPI, and Data Empowerment and Protection Architecture (DEPA). For example, the Asian Development Bank attributes the success of UPI to its “consortium ownership structure”, which enables the wide participation of major financial stakeholders in the country.
- Coordinated Planning: The PM-Gati Shakti establishes a clear coordination framework involving various inter-governmental stakeholders at the state and union levels. This aims to significantly reduce project duplications, delays, and cost escalations by streamlining communication, harmonizing project appraisal and approval processes, and providing a comprehensive database of major infrastructure projects in the country. This database called the National Master Plan, is jointly accessible by various government stakeholders through APIs.
- Capacity Building for Government Employees: The National e-Governance Division of the Ministry of Electronics and Information Technology routinely rolls out multiple training programs to build the technological and managerial skills required by government employees to manage Digital Public Goods (DPGs). For instance, it recently held a program on “Managing Large Digital Transformative Projects”. Additionally, the Ministry of Personnel, Public Grievances, and Pensions has launched the Integrated Government Online Training platform (iGOT) Karmayogi for the continuous learning of civil servants across various domains.
Digital Governance; Way Forward
E-governance utilizes information and communication technology (ICT) such as Wide Area Networks, the Internet, and mobile computing to implement existing government activities, reconfiguring the structures and processes of governance systems. This warrants addressing certain inter-related challenges such as :
- Data Security: The dynamic and ever-changing landscape of cyber threats necessitates regular advancements in data and information security technologies, policy frameworks, and legal provisions. Consequently, the digital public ecosystem must incorporate robust data cybersecurity measures, advanced encryption technologies, and stringent privacy compliance standards to safeguard against data breaches.
- Creating Feedback Loops: Regular feedback surveys will help government agencies improve the quality, efficiency, and accessibility of digital governance services by tailoring them to be more user-friendly and enhancing administrative design. This is necessary to build trust in government services and improve their uptake among beneficiaries. Conducting the decennial census is essential to gather updated data that can serve as a foundation for more informed and effective decision-making.
- Capacity Building for End-Users: The beneficiaries of key e-governance projects like Aadhar and UPI may have inadequate technological skills, especially in regions with weak internet network infrastructure like hilly or rural areas. This can present challenges in the access to and usage of technological solutions. Robust capacity-building campaigns for beneficiaries can provide an impetus to the digital inclusion efforts of the government.
- Increasing the Availability of Real-Time Data: By prioritizing the availability of up-to-date information, governments and third-party enterprises can enable quick and informed decision-making. They can effectively track service usage, assess quality, and monitor key metrics by leveraging real-time data. This approach is essential for enhancing operational efficiency and delivering improved user experience.
- Resistance to Change: Any resistance among beneficiaries or government employees to adopt digital governance goods may stem from a limited understanding of digital processes and a lack of experience with transitioning from legacy systems. Hand-holding employees during the transitionary phase can help create more trust in the process and strengthen the new systems.
Conclusion
Digital governance is crucial to transforming public services, ensuring transparency, and fostering inclusivity in a rapidly digitizing world. The successful implementation of such projects requires addressing challenges like data security, skill gaps, infrastructural limitations, feedback mechanisms, and resistance to change. Addressing these challenges with a strategic, multi-stakeholder approach can ensure the successful execution and long-term impact of large digital governance projects. By adopting robust cybersecurity frameworks, fostering public-private partnerships, and emphasizing capacity building, governments can create efficient and resilient systems that are user-centric, secure, and accessible to all.
References
- https://www.adb.org/sites/default/files/publication/865106/adbi-wp1363.pdf
- https://www.jotform.com/blog/government-digital-transformation-challenges/
- https://aapti.in/wp-content/uploads/2024/06/AaptixONI-DPIGovernancePlaybook_compressed.pdf
- https://community.nasscom.in/sites/default/files/publicreport/Digital%20Public%20Infrastructure%2022-2-2024_compressed.pdf
- https://proteantech.in/articles/Decoding-Digital-Public-Infrastructure-in-India/

Introduction
In today's digital economy, data is not only a business asset but also the fuel for innovation, decision-making, and consumer trust. However, the digitisation of services has made personal or sensitive data a top target for cybercriminals. The stakes are high: a data breach can cost millions of fines, cause damage to reputation and devastate the confidence of consumers. Therefore, regulatory compliance and data protection have become a strategic imperative.
From the General Data Protection Regulation (GDPR) in the EU to the Digital Personal Data Protection (DPDP) Act of India, various sector-specific regulations like HIPAA for healthcare in the US, companies are now subject to a web of data protection and compliance laws. The challenge is to balance compliance efforts with strong security, a balance that demands both policy restraint and technical resilience. This blog examines pivotal pillars, shifting trends and actionable best practices for dominating data protection and compliance in 2025 and beyond.
Why Data Protection and Compliance Matter More Than Ever
Data protection isn't just about keeping fines at bay, it's about preserving the relationship with customers, partners and regulators. A 2024 IBM report says the average data-breach cost has now exceeded USD 4.5 million, with regulatory fines constituting a large portion of the cost. In addition to economics, breaches tend to result in intellectual property loss, customer loss and long-term brand attenuation. Compliance ensures organisations remain within certain legislative necessities for collecting, holding, transferring and setting of personal and sensitive information. Failure to conformity can lead to serious penalties: under GDPR, fines could be up to 4% of the company's annual turnover or €20 million, whichever is higher. In regulated sectors like banking and healthcare, compliance breaches can also lead to the suspension of licenses.
Important Regulatory Frameworks Informing 2025
- GDPR and Its Global Ripple Effect
GDPR was enacted in 2018 and continues to have a ripple effect on privacy legislation worldwide. Its tenets of lawfulness, transparency, data minimisation and purpose limitation have been replicated in many jurisdictions such as Brazil's LGPD and South Korea's PIPA.
- India's DPDP Act
The DPDP Act, 2023, gives high importance to consent-based processing of data, transparent notice rules and fiduciary responsibilities for data. With a penalty for default of up to INR 250 crore, it's amongst the most impactful laws for digital personal data protection.
- Sectoral Regulations
- HIPAA for healthcare information in the US.
- PCI DSS for payment card security.
- DORA (Digital Operational Resilience Act) in the EU for financial organisations.
- These industry-specific models generate overlapping compliance responsibilities, making cross-enterprise compliance programs vital.
Key Pillars of a Sound Data Protection & Compliance Program
- Data Governance and Classification
Having insight into what data you have to store, where it is stored and who can have access to it is the keystone of compliance. Organisations need to have data classification policies in place to group information based on sensitivity and impose more rigorous controls on sensitive data.
- Security Controls and Privacy by Design
Strong technical defences, encryption, multi-factor authentication, and intrusion detection are the initial defences. Privacy by design integrated in product development guarantees compliance is thought through from the initial stage, not added on afterwards.
- Consent and Transparency
Contemporary data legislation highlights informed consent. This entails simple, non-technical privacy notices, detailed opt-in choices, and straightforward withdrawal options. Transparency produces trust and lessens legal danger.
- Incident Response and Breach Notification
Most laws demand timely breach notifications, and GDPR insists on reporting within 72 hours. Having a documented incident response plan maintains legal deadlines and reduces harm.
- Employee Training and Awareness
Human mistake is the top source of data breaches. Ongoing training in prevention of phishing, password management, basic cyber hygiene and compliance requirements is crucial.
Upcoming Trends in 2025
- AI-Powered Compliance Monitoring
Organisations are embracing AI-powered solutions to systematically monitor data flows, identify policy breaches and auto-create compliance reports. The solutions assist in closing the loop between IT security teams and compliance officers.
- Cross-Border Data Transfer Mechanisms
With increasingly severe regulations, companies are spending more on secure cross-border data transfer frameworks like Standard Contractual Clauses (SCCs) and Binding Corporate Rules (BCRs).
- Privacy-Enhancing Technologies (PETs)
Methods such as homomorphic encryption and differential privacy are picking up steam, enabling organisations to sift through datasets without revealing sensitive personal data.
- ESG and Data Ethics
Data handling is increasingly becoming a part of Environmental, Social and Governance (ESG) reporting. Ethical utilisation of customer data, not just compliance, has become a reputational differentiator.
Challenges in Implementation
Despite having transparent frameworks, data protection plans encounter challenges like jurisdictions having competing needs, and global compliance is becoming expensive. The emerging technologies, such as generative AI, often bring privacy threats that haven’t been fully covered by legislation. Small and micro enterprises have neither the budget nor the skills to implement enterprise-level compliance programs. Qualifying these challenges often needs a risk-based strategy, allocations of resources to top areas of impact and automating the compliance chores wherever possible.
Best Practices for 2025 and Beyond
In 2025, regulatory compliance and data protection are no longer a precaution or a response to a breach but are strategic drivers of resilience and trust. As regulatory analysis rises, cyber threats evolve, and consumer expectations grow, administrations need to integrate compliance into the very fabric of their actions. By bringing governance and technology together, organisations can break free from a "checklist" mentality and instead adopt a proactive and risk-sensitive approach. Eventually, data protection is not just about not getting in trouble; it's about developing a kind that succeeds in the digital era.
References
- GDPR – Official EU Regulation Page: https://gdpr.eu
- India’s DPDP Act Overview – MeitY: https://www.meity.gov.in/data-protection-framework
- HIPAA – US Department of Health & Human Services: https://www.hhs.gov/hipaa
- PCI DSS Standards: https://www.pcisecuritystandards.org
- IBM Cost of a Data Breach Report 2024: https://www.ibm.com/reports/data-breach
- OECD – Privacy Guidelines: https://www.oecd.org/sti/privacy-guidelines
