
#FactCheck: No, PM Modi Did Not Appear in Royal Attire,Image Is AI-Generated
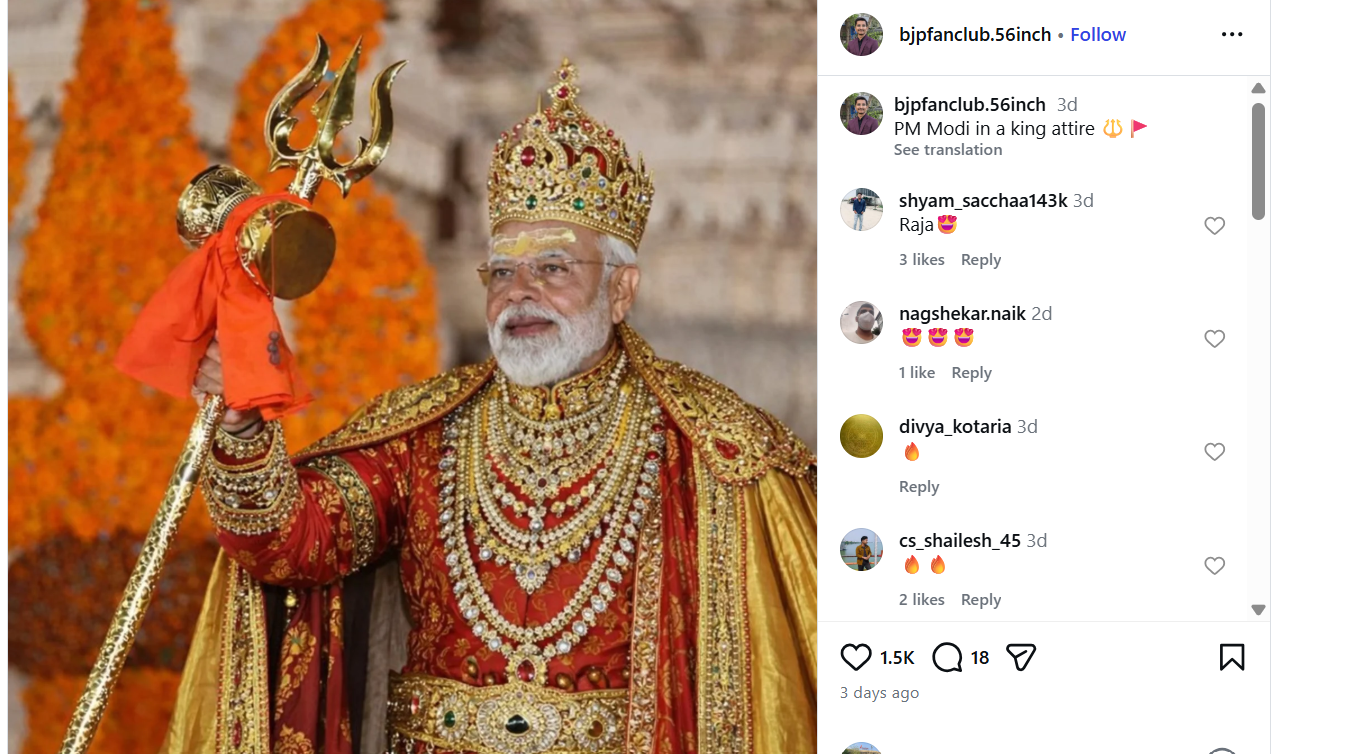
A photograph showing Prime Minister Narendra Modi holding a trident and dressed in royal attire is being widely shared on social media. Users circulating the image are claiming that it shows PM Modi in a regal outfit.
However, a verification by the Cyber Peace Foundation’s Research Desk has found that the claim is false. The investigation established that the viral image is not authentic and has been generated using Artificial Intelligence (AI).
Claim:
On January 11, 2026, several Instagram users shared the image with captions describing it as a photograph of Prime Minister Modi in royal attire.
Links and archived versions of the posts, along with screenshots, are provided below.
Fact Check:
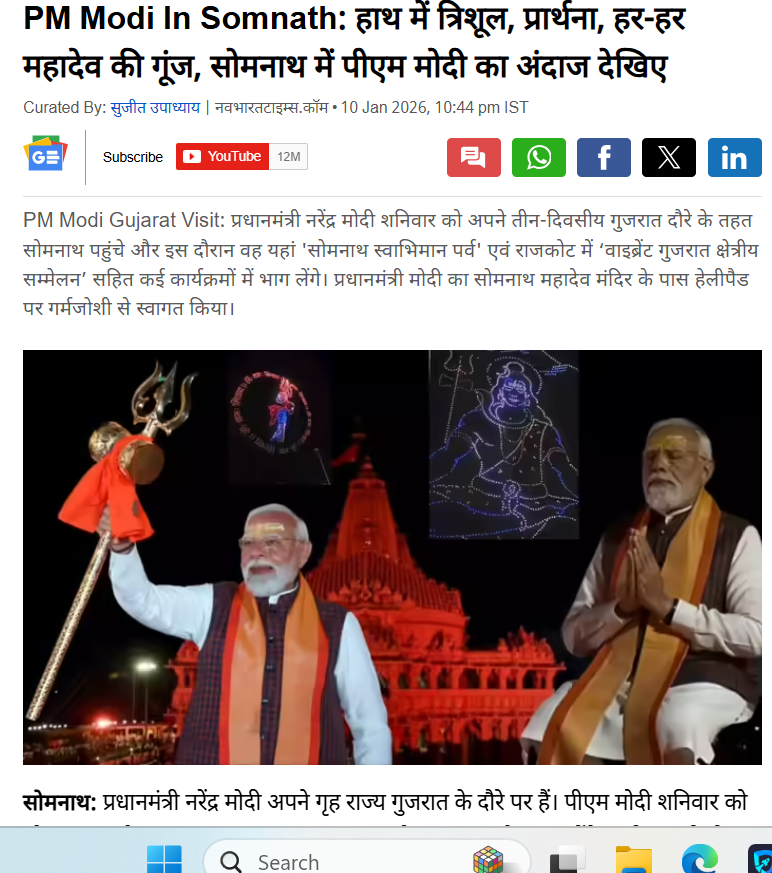
To verify the claim, relevant keywords such as “PM Modi holding trishul” were searched on Google. This led to a report published by Navbharat Times on January 10, 2025. The report features photographs of Prime Minister Modi holding a trident during his visit to the Somnath Temple. However, in the original images, he is seen wearing normal attire, not royal clothing as shown in the viral image. Link and screenshot
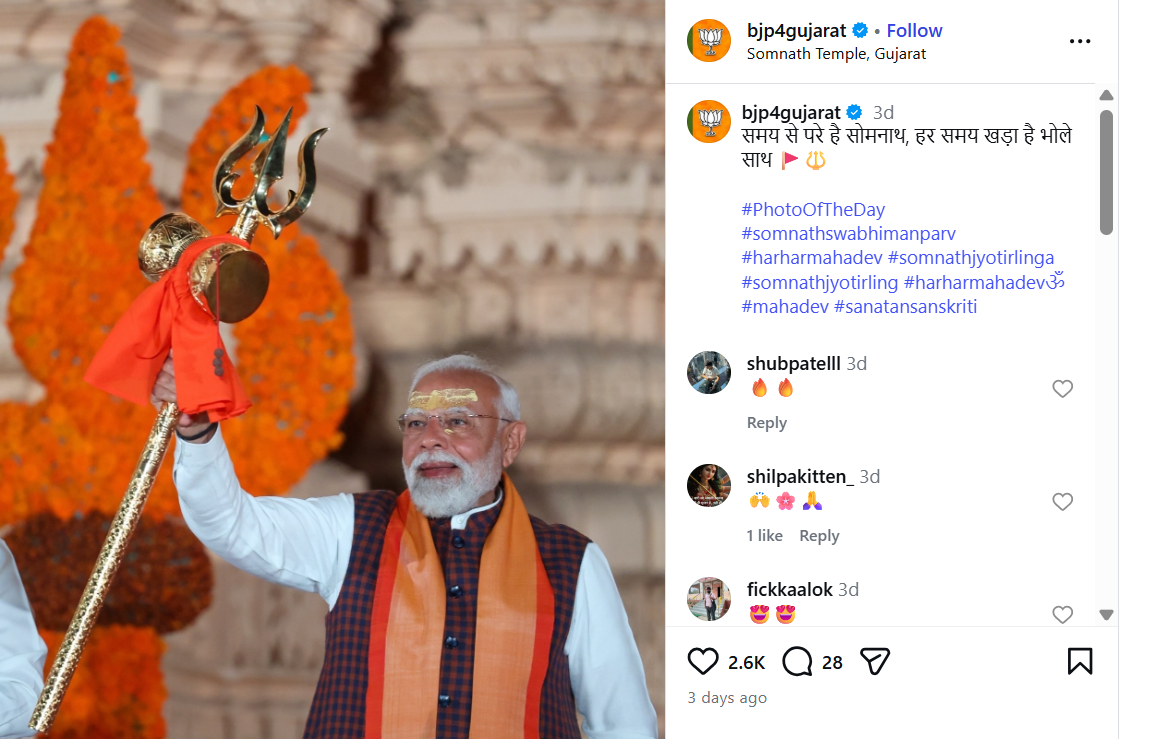
In the next step of the investigation, the original photograph was traced to the official Instagram account of BJP Gujarat, where it was posted on January 11, 2026. The post clearly identifies the image as being from Somnath Temple. Link and screenshot: https://www.instagram.com/p/DTVlb-9Da1V
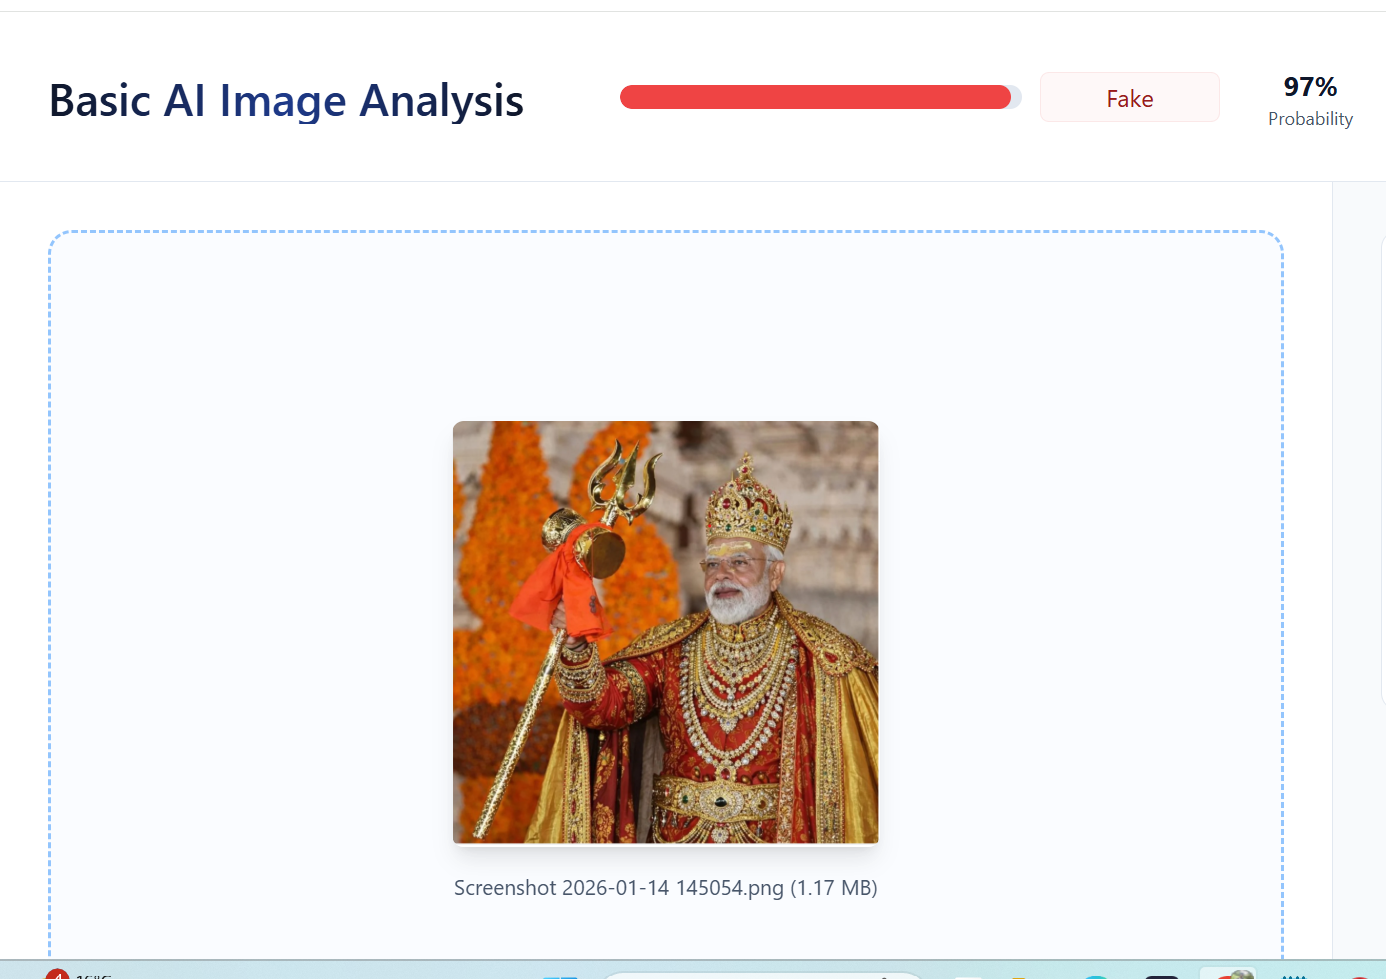
A close examination of the viral image raised suspicion about digital manipulation. The image was then analysed using the AI detection tool TruthScan. The tool’s assessment indicated a 97 percent likelihood that the image was AI-generated.
Further comparison between the viral image and the original photograph revealed that all visual elements match except the clothing, confirming that the attire was digitally altered using AI tools.
Conclusion
The claim that Prime Minister Narendra Modi appeared in royal attire is false. The Cyber Peace Foundation’s research confirms that the viral image was created using AI by altering the clothing in an original photograph taken during PM Modi’s visit to Somnath Temple. The manipulated image was shared online to mislead users.

Related Blogs
CyberPeace | Automotive Cybersecurity & Digital Forensics
Introduction
After a crash, the story usually comes from the driver, a witness or a police report. But a modern vehicle can leave another version behind - a digital one. An Event Data Recorder (EDR), commonly called a car's black box, can preserve selected information from the seconds around a crash. NHTSA describes EDRs as recording vehicle dynamics, driver inputs, crash characteristics, restraint status and some post-crash information.[1] The exact fields depend on the vehicle. A black box is not a magical device that records everything; it is one evidence source inside a much larger vehicle.
A modern vehicle can also contain safety controllers, diagnostic interfaces, ADAS, telematics and software-update systems. For an investigator, the question is what evidence can be linked to the EDR and what that combined record can actually support.
What Is Actually in the Black Box?
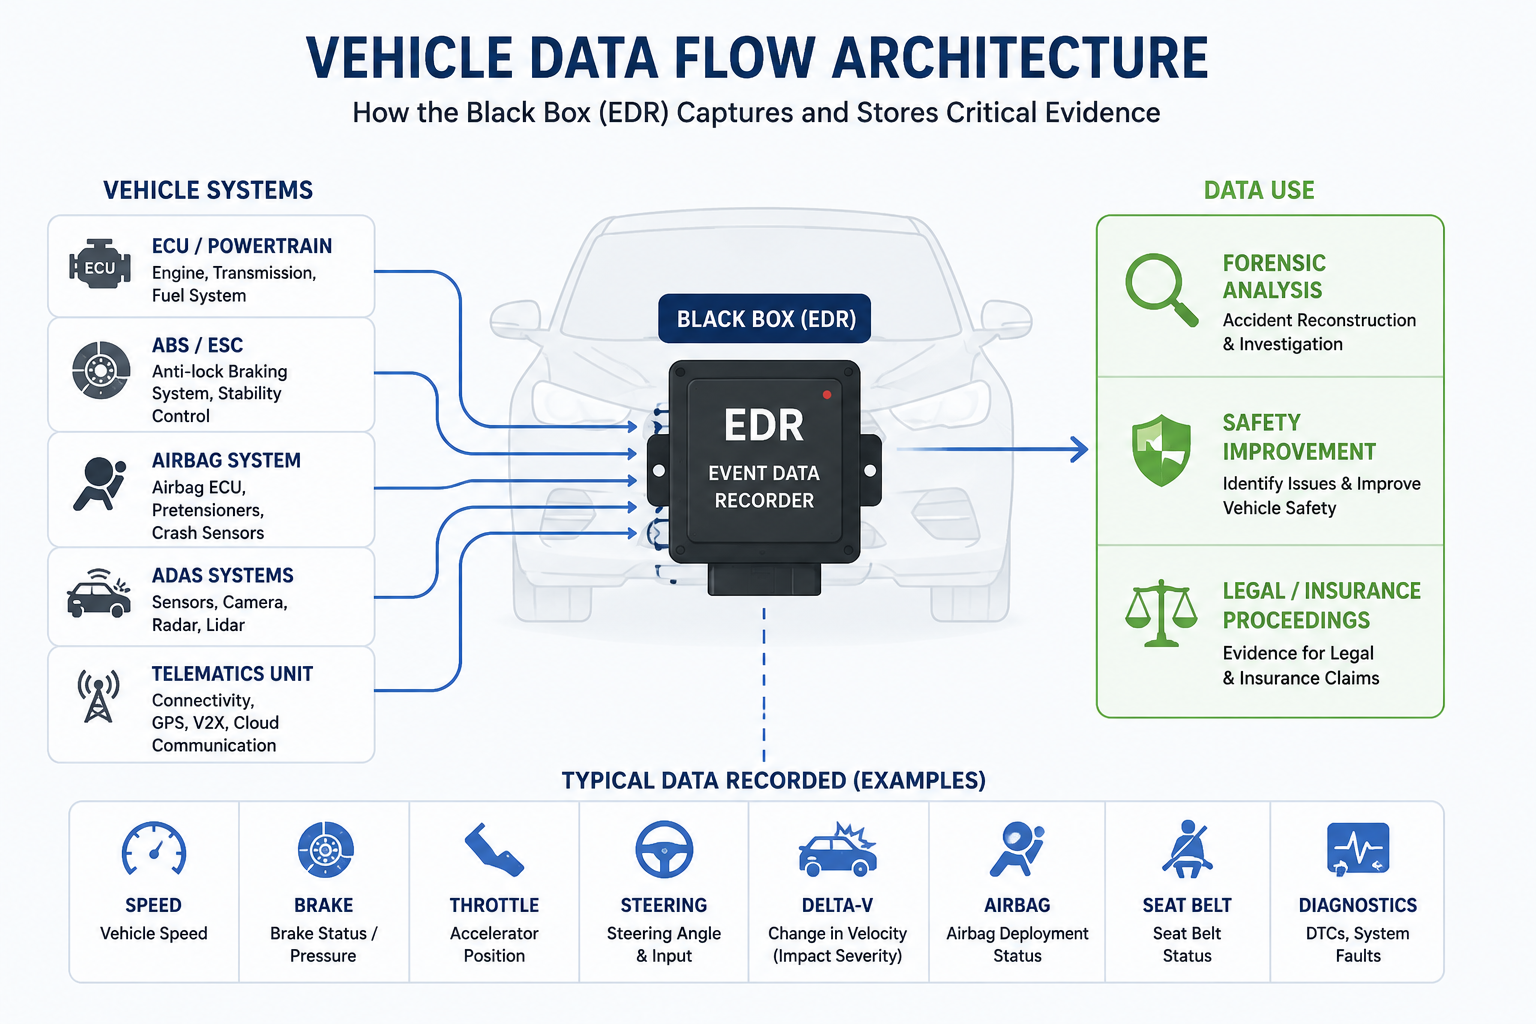
An EDR is best understood as a short event record, not a continuous driving diary. Depending on the vehicle and its configuration, forensic extraction may reveal items such as speed, acceleration, delta-V, engine RPM, throttle position, brake status, steering input, ABS or stability-control activity, seat-belt status and airbag or restraint events. NHTSA's published EDR material shows that data elements can include longitudinal and lateral acceleration, delta-V, vehicle speed, engine speed, throttle, service-brake status, roll/pitch/yaw information and steering input.[2] Do not overread the data: A field that exists in one model should not automatically be assumed to exist in another. A forensic report must identify exactly which module and fields were available and actually recovered.
What Can a Forensic Examination Recover?
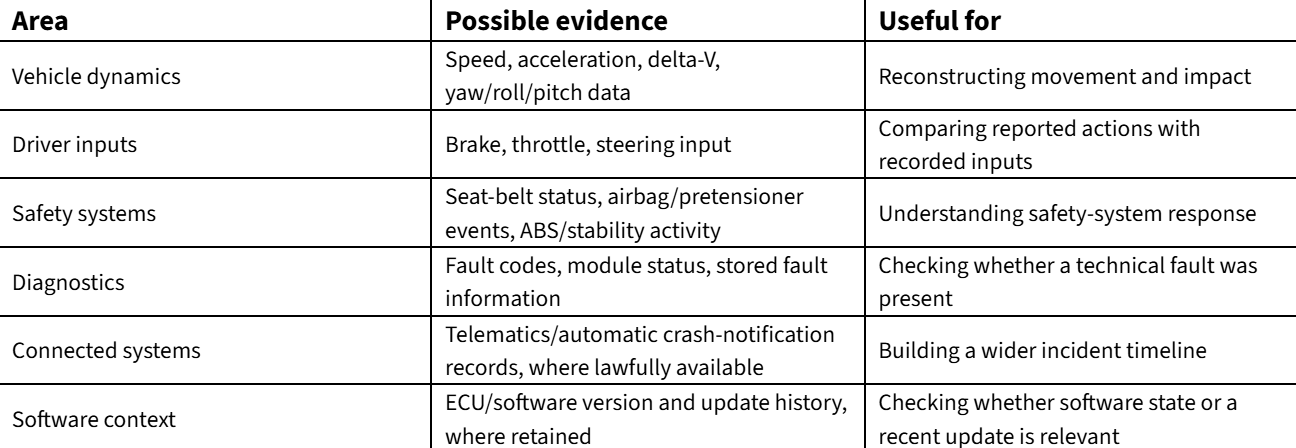
A Brake Failure Example
Consider a driver who reports: “I pressed the brake, but nothing happened.” The statement should be preserved, but a forensic investigation should test it. Was brake status captured? What was the speed before the event? Did ABS activate? What were the acceleration and delta-V patterns? Were there relevant fault codes? Was the vehicle recently repaired or updated? Suppose the recovered records show a brake input, ABS activity and a change in vehicle speed before impact. That does not prove the brakes were mechanically perfect. It does, however, make the sentence “nothing happened” too simple. Conversely, a relevant fault appearing just before the event may give investigators a stronger lead. The important part is the comparison: human account, vehicle record, physical evidence and technical history should be examined together.
Smart Vehicles, Digital Evidence and Cybersecurity Investigation
A connected vehicle can communicate through cellular networks, Bluetooth, Wi-Fi, mobile applications, workshop tools and cloud services. If unusual activity appears around a safety-critical incident, investigators may need to look beyond the EDR. Useful questions include:
• Was there unusual diagnostic or service activity before the incident?
• Was a software update or configuration change recently applied?
• Do timestamps from different modules line up, or is there clock drift?
• Can the extracted record be tied back to the original vehicle and module?
• Is there a non-cyber explanation - such as a hardware fault or software defect - that fits the evidence better?
The mindset matters: A cyberattack should be a conclusion supported by evidence, not the default explanation for strange vehicle behaviour.
The Forensic View: From Data to Evidence
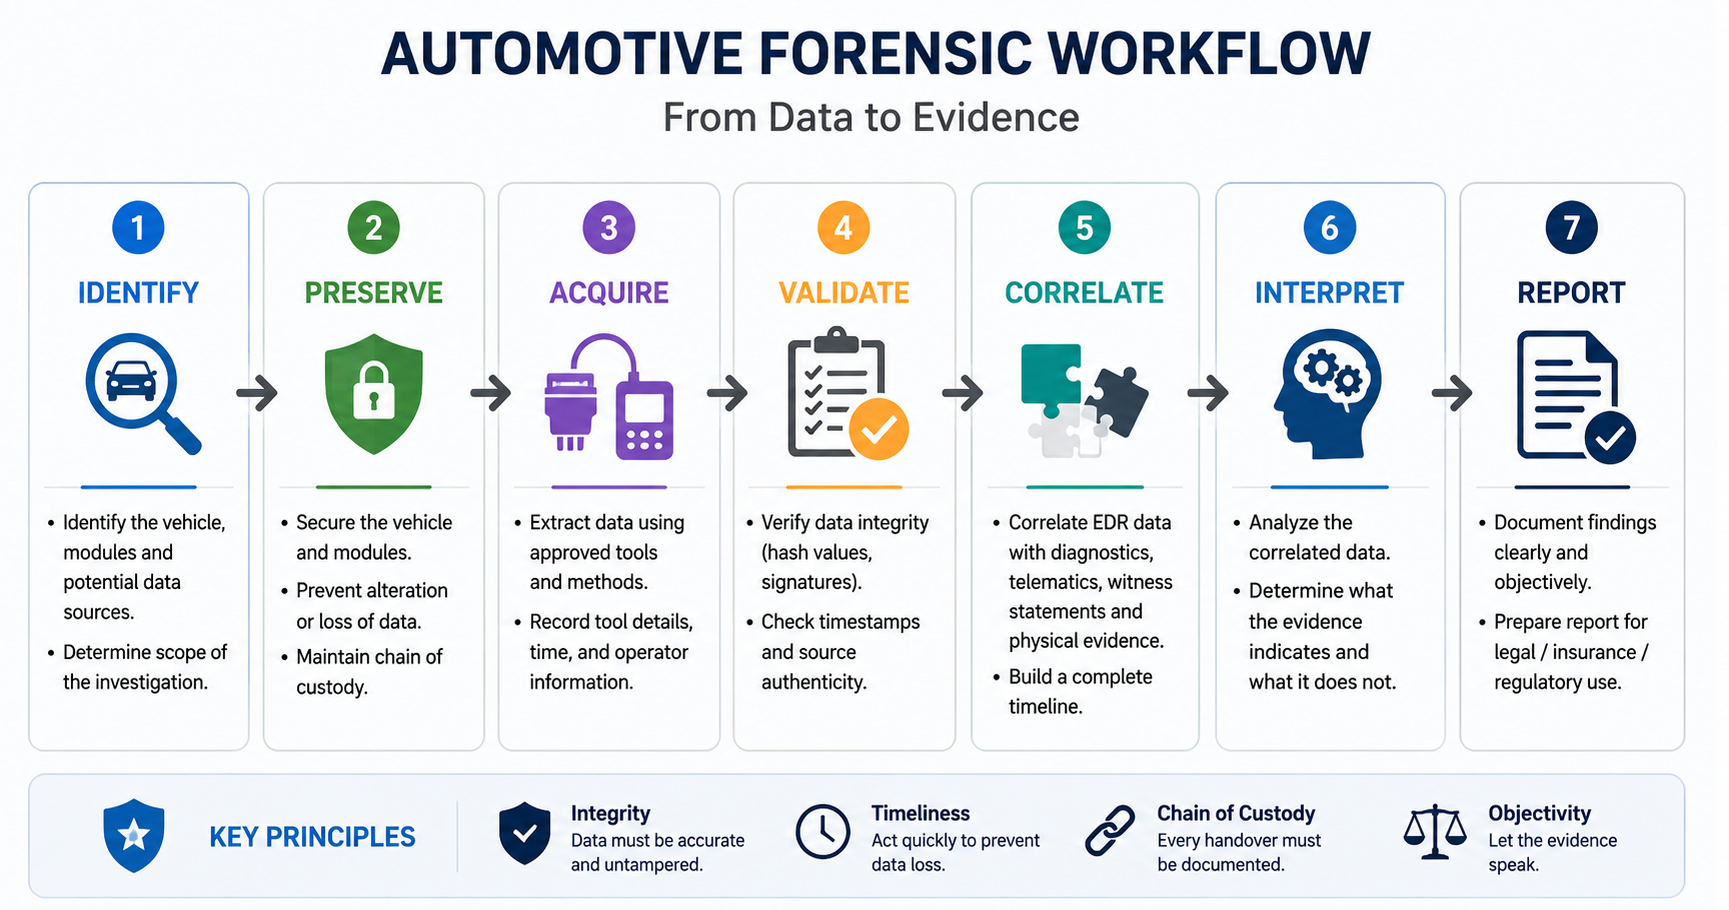
Automotive forensics is not simply plugging in a tool and exporting a report. The investigator should document the vehicle identity, module involved, extraction method, tool version, acquisition time and evidence-preservation steps. The goal is to make the work repeatable and defensible.
• Identify the relevant modules and evidence sources.
• Preserve the vehicle and extracted data against unnecessary alteration.
• Acquire data using a documented and appropriate method.
• Validate provenance, integrity, timestamps and completeness.
• Correlate EDR, diagnostics, software history, connected records and physical evidence.
• Report both findings and uncertainty.
A useful forensic rule: “Recorded” does not mean “proven.” Evidence becomes persuasive when its source, integrity and context are clear.
What the Law and Standards Are Changing
India is moving toward a more formal automotive cybersecurity lifecycle. IS-189 focuses on vehicle cybersecurity and the Cyber Security Management System (CSMS), while AIS-190 deals with software updates and the Software Update Management System (SUMS).[4][5] The wider statutory and type-approval framework is provided by the Motor Vehicles Act, 1988 and the Central Motor Vehicles Rules, 1989. For vehicle prototypes, Rule 126 provides for testing and approval by authorized testing agencies.[6][7]
In June 2026, the Ministry of Road Transport and Highways (MoRTH) came out with draft G.S.R. 503(E). The draft proposes new CMVR Rules 125-T and 125-U covering cybersecurity and software-update requirements. Since G.S.R. 503(E) is still a draft notification, its proposed requirements and the dates from which they may apply should be verified with the latest final notification before treating them as applicable law.[8]
At the international level, UN Regulation No. 155 addresses vehicle cybersecurity, while UN Regulation No. 156 covers software updates and their management.[9][10] This matters to forensics because lifecycle cybersecurity creates an expectation that manufacturers should be able to understand and manage security risks over time. In other words, logs, software-state information, vulnerability records and incident evidence can become part of the security story, not merely post-incident paperwork.
The Real Takeaway
The black box is valuable because it can reduce guesswork. It may tell us how fast the vehicle was moving, whether the driver applied the brake, how the vehicle responded, and what certain safety systems were doing around the event. But it rarely answers the whole case on its own. The strongest investigation is built by joining several pieces: EDR data, diagnostics, software context, connected-system evidence and what was found at the crash scene.
For cybersecurity professionals, the lesson is simple: a secure vehicle should not only resist attacks. It should also leave trustworthy evidence when something goes wrong. Good access controls, reliable timestamps and careful evidence handling help turn “something failed” into a defensible explanation.
Conclusion
The phrase “car black box” sounds simple, but the evidence behind it is not. An EDR can preserve a small but valuable window into a crash. During forensic examination, investigators may also be able to recover diagnostic, safety-system, software and connected-vehicle information, depending on the vehicle and what has been retained. The job is not to collect the largest possible amount of data. It is to collect the right data, preserve it properly and understand what each record can - and cannot - prove.
That is where automotive cybersecurity and digital forensics meet. As vehicles become more connected and software-driven, the ability to reconstruct an incident becomes part of security itself.
References
1. National Highway Traffic Safety Administration (NHTSA), Event Data Recorder (EDR) overview and research resources.
2. NHTSA, Use of Event Data Recorder (EDR) Technology for Highway Crash Data Analysis.
3. NHTSA, Light-Vehicle Event Data Recorder Technologies Update.
4. Automotive Research Association of India (ARAI), AIS-189, Approval of Vehicles with Regards to Cyber Security and Cyber Security Management System, April 2024.
5. Automotive Research Association of India (ARAI), AIS-190, Approval of Vehicles with Regards to Software Update and Software Update Management System, April 2024.
6. Government of India, Motor Vehicles Act, 1988.
7. Government of India, Central Motor Vehicles Rules, 1989, Rule 126.
8. Ministry of Road Transport and Highways, G.S.R. 503(E), 17 June 2026, draft Central Motor Vehicles (Amendment) Rules concerning cybersecurity and software updates.
9. UNECE, UN Regulation No. 155, Cyber Security and Cyber Security Management System.
10. UNECE, UN Regulation No. 156, Software Update and Software Update Management System.
11. NIST, SP 800-86, Guide to Integrating Forensic Techniques into Incident Response.
Executive Summary
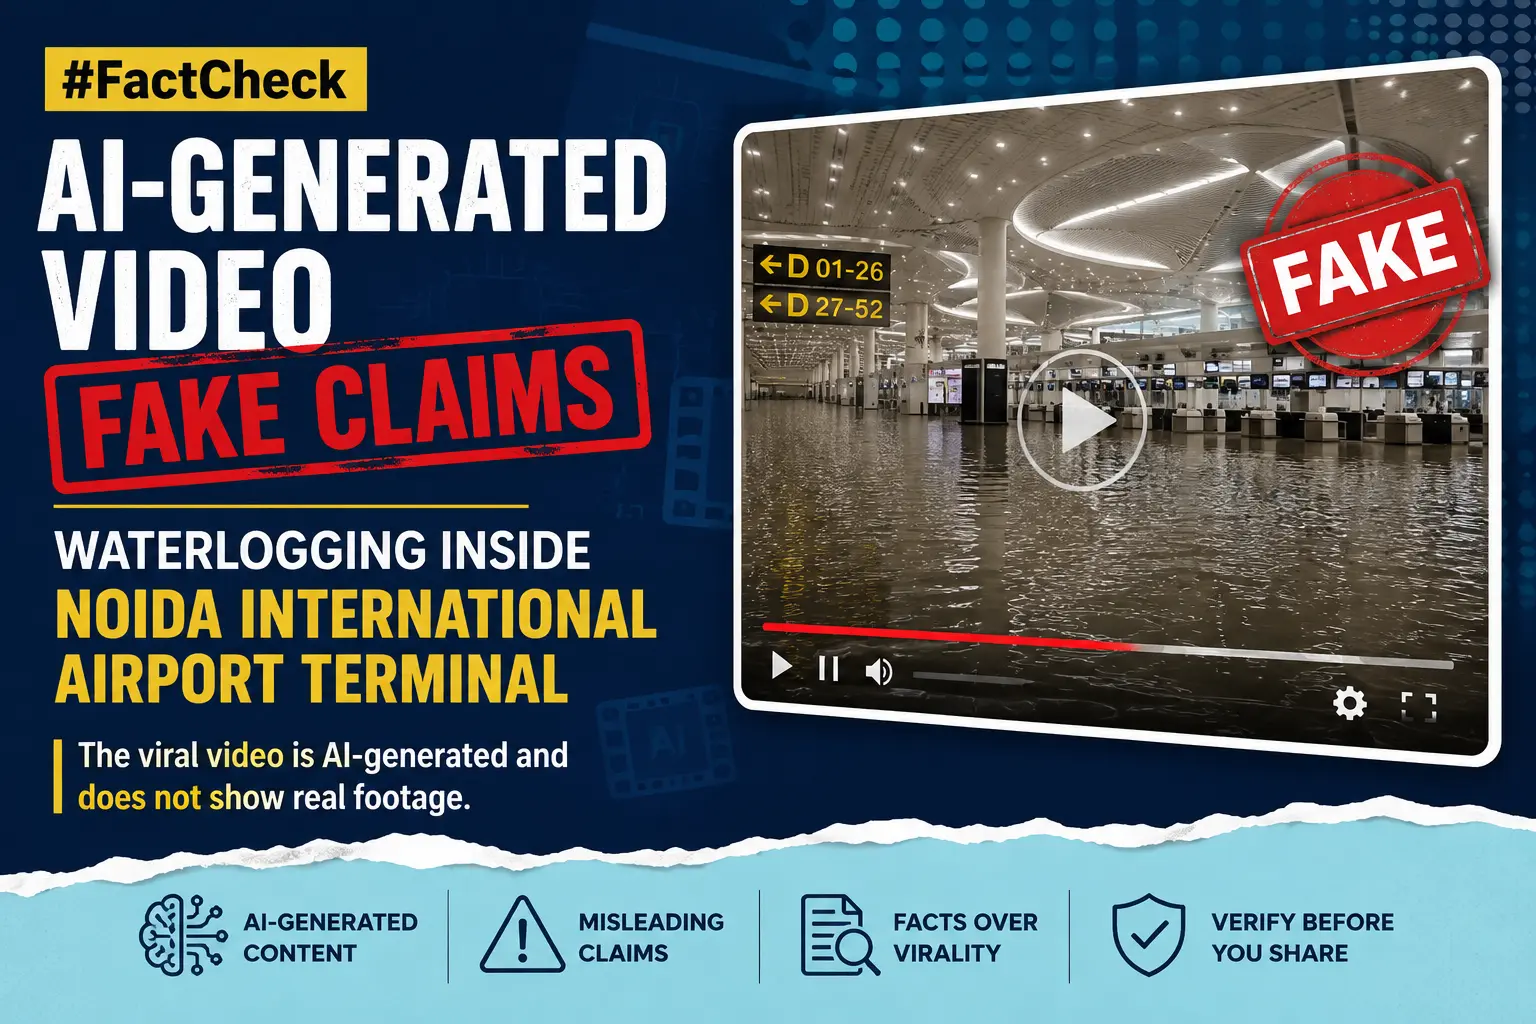
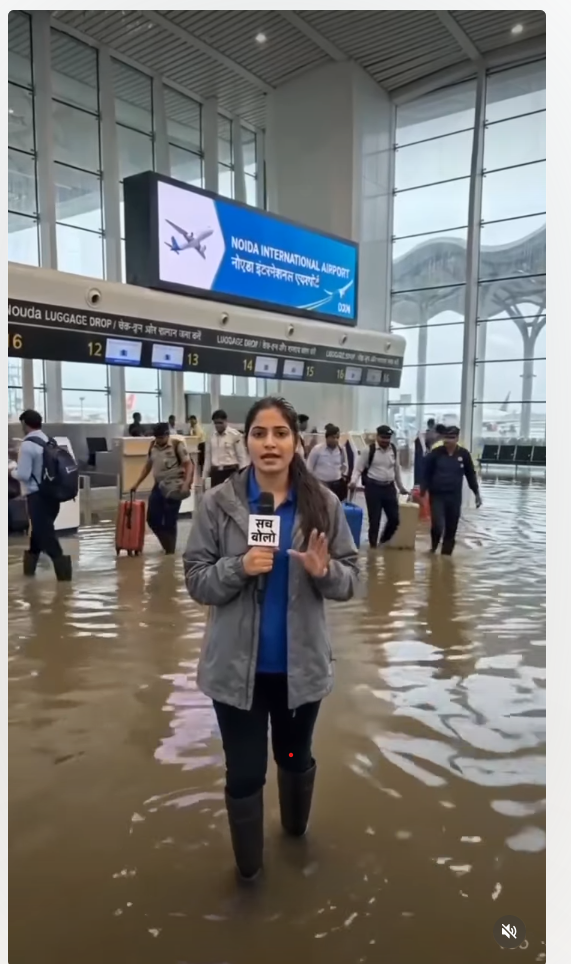
A video circulating rapidly on social media claims to show severe waterlogging inside the passenger terminal of the newly constructed Noida International Airport in Uttar Pradesh. The clip displays passengers navigating flooded check-in areas with their luggage, while a female reporter holding a mic labeled "Sach Bolo" criticizes the state government over poor infrastructure. However, a research by the CyberPeace Research Wing confirmed that the video is completely fake and created using artificial intelligence (AI).
The Claim
On August 14, 2026, Instagram user shyamgupta_yuvaneta posted the clip with a caption targeting the government over alleged corruption and poor infrastructure at the Noida Airport
https://www.instagram.com/reels/DcAOGgcgUrp
Fact-Check
An initial analysis of the video revealed unnatural physical movements among the people shown and an artificial voice modulation typical of AI-generated content. To verify this, the video was run through standard AI detection tools:
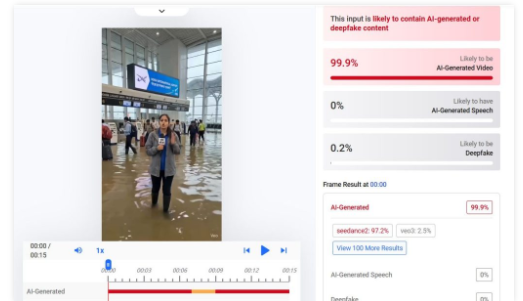
Hive Moderation: Flagged the video as 99.9% likely to be AI-generated.
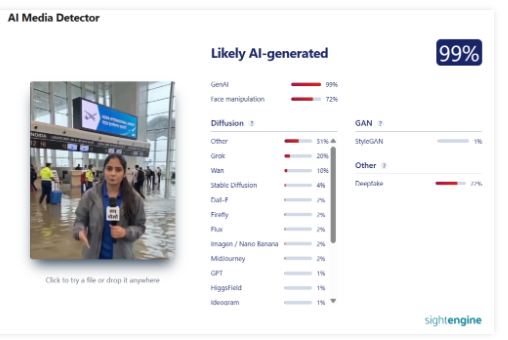
Sightengine: Returned a 99% probability that the content was artificially generated.
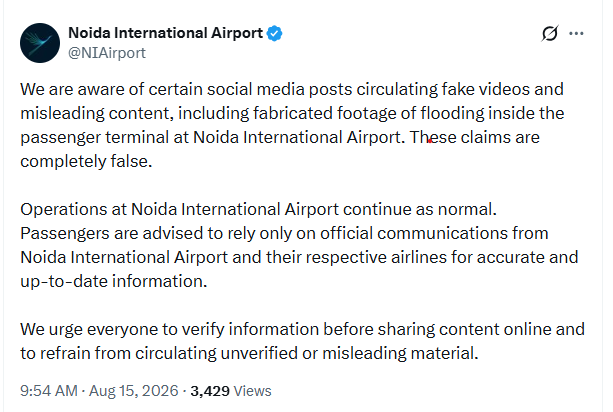
Further verification of official communications revealed a post by the official X (formerly Twitter) account of Noida International Airport (@NIAirport) on August 15, 2026. The airport authority clarified that fake videos depicting waterlogging inside the passenger terminal were circulating online and refuted the claims entirely. While recent heavy rainfall did cause temporary water accumulation in an underpass connecting the terminal to the parking area, the passenger terminal building itself remained unaffected.
https://x.com/NIAirport/status/2088481969462272065?s=20
Conclusion
The viral video showing waterlogging inside the Noida International Airport terminal is fake and AI-generated. The actual incident of waterlogging was restricted to an outer subway connecting the parking area, not the main terminal building.
Executive Summary
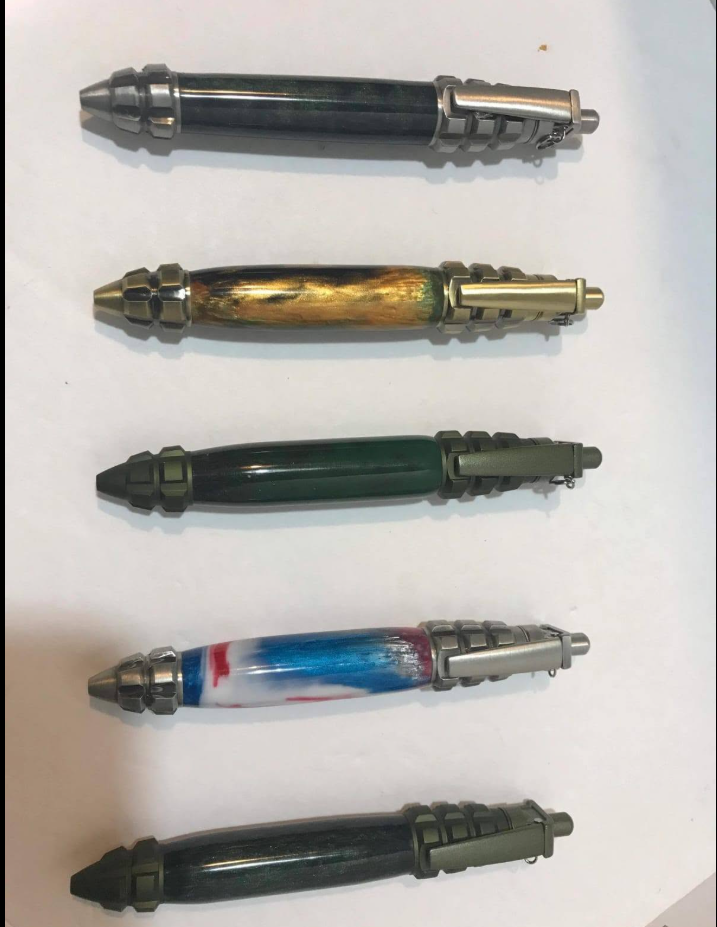
A picture of grenade-style pens is being circulated on social media with the claim that they are actually small bombs responsible for explosions in Gujarat. Users are being warned not to pick up any object resembling the pen, with posts alleging that similar devices are causing blasts in different parts of the state. CyberPeace Research Wing research found the claim to be completely false. The viral image shows a novelty military-style pen, not an explosive device. The same product is listed on the American e-commerce platform Etsy, where it is described as a military tank or grenade-style ink pen that uses refillable ink cartridges.
Claim
The viral image shows five grenade-shaped pens. It is being shared with a caption claiming: “Do not pick up anything that looks like this pen. If you find one lying somewhere, do not touch it. It is a small bomb, and incidents like this are happening wherever such pens are found in Gujarat.”The post also includes photographs of injured individuals to reinforce the claim.
https://www.facebook.com/groups/273456550609813/posts/1721798935775560/
Fact Check
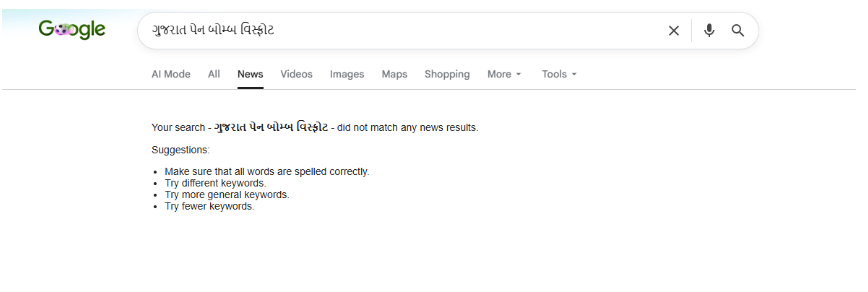
To verify the claim, we first searched for relevant news reports using English and Gujarati keywords. However, we found no credible media reports linking grenade-shaped pens to any explosions in Gujarat. During the search, we came across reports mentioning that certain Khalistani groups had allegedly sent emails threatening blasts in Ahmedabad and Gandhinagar. However, none of those reports mentioned grenade-style pens or any similar explosive devices.
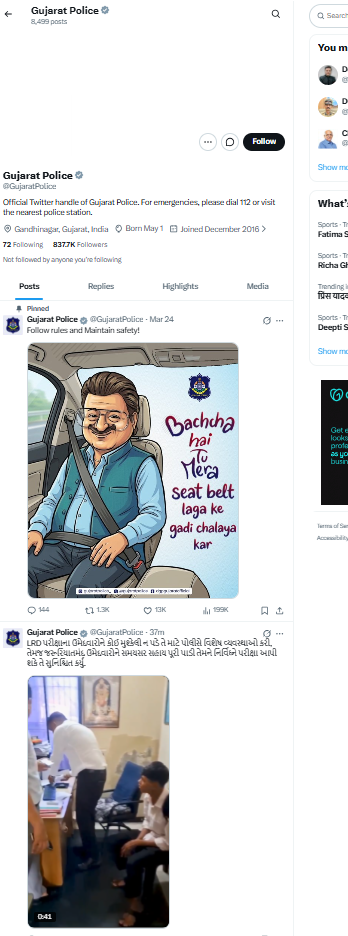
We also checked whether Gujarat Police had issued any warning, advisory, or public notice regarding such objects. However, no such advisory was found on any official Gujarat Police social media handle or public platform.
Next, we conducted a reverse image search of the viral photograph. The search led us to a listing on the American e-commerce website Etsy, where the product is described as a “Military Novelty Tank or Grenade Ink Pen.”
https://www.etsy.com/listing/889188479/military-novelty-tank-or-grenade-ink
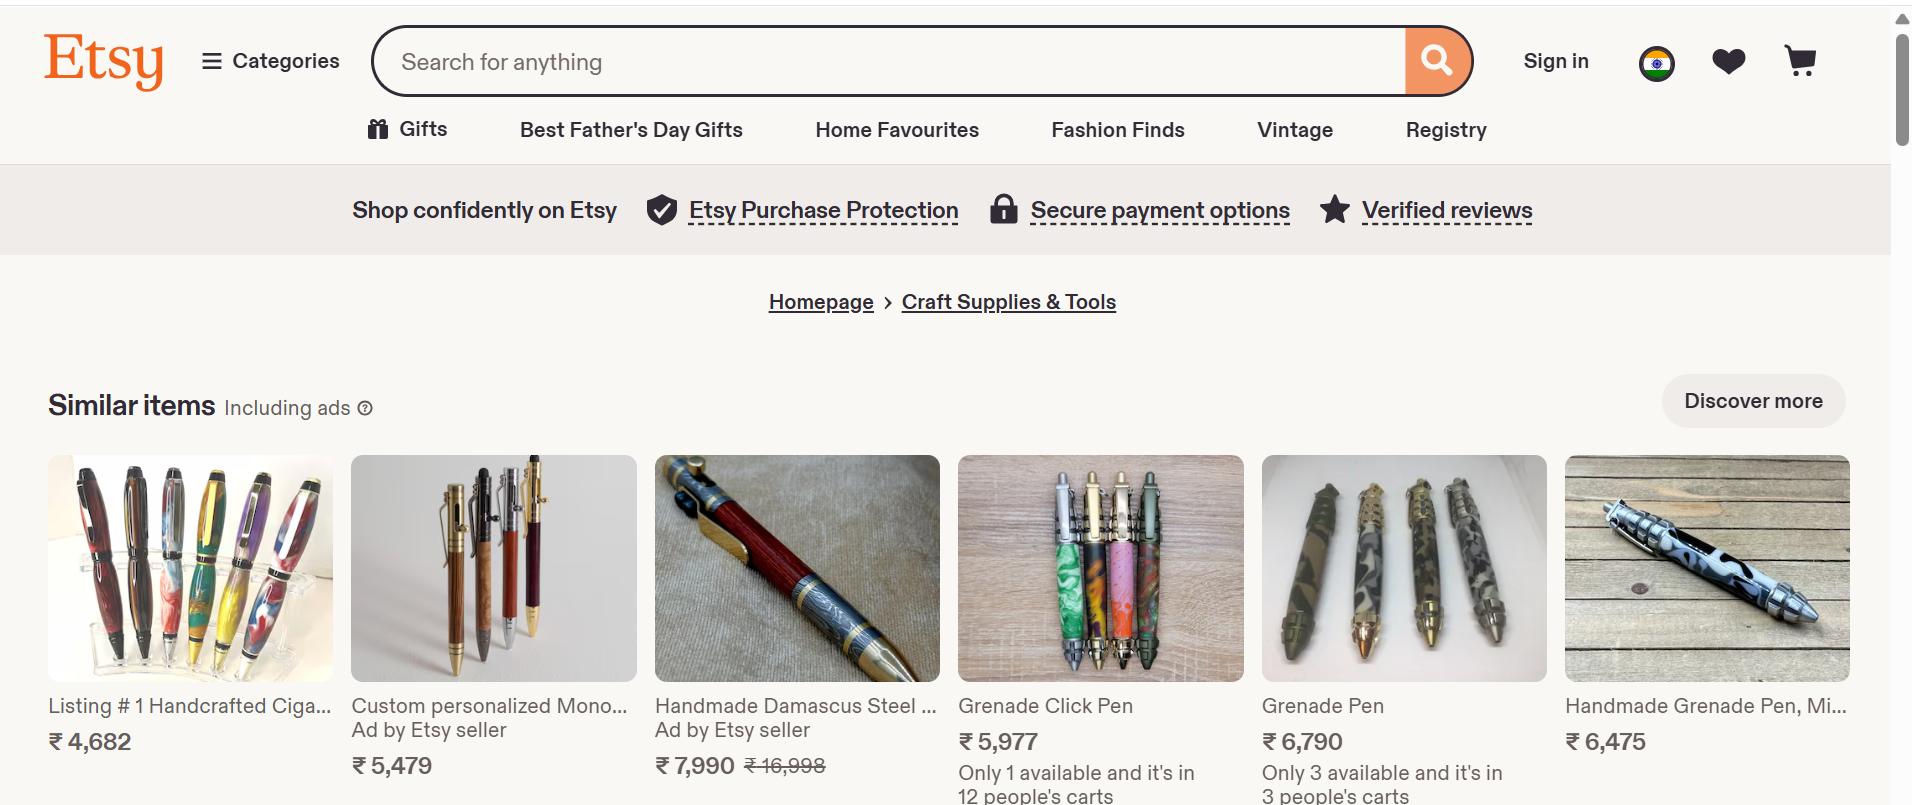
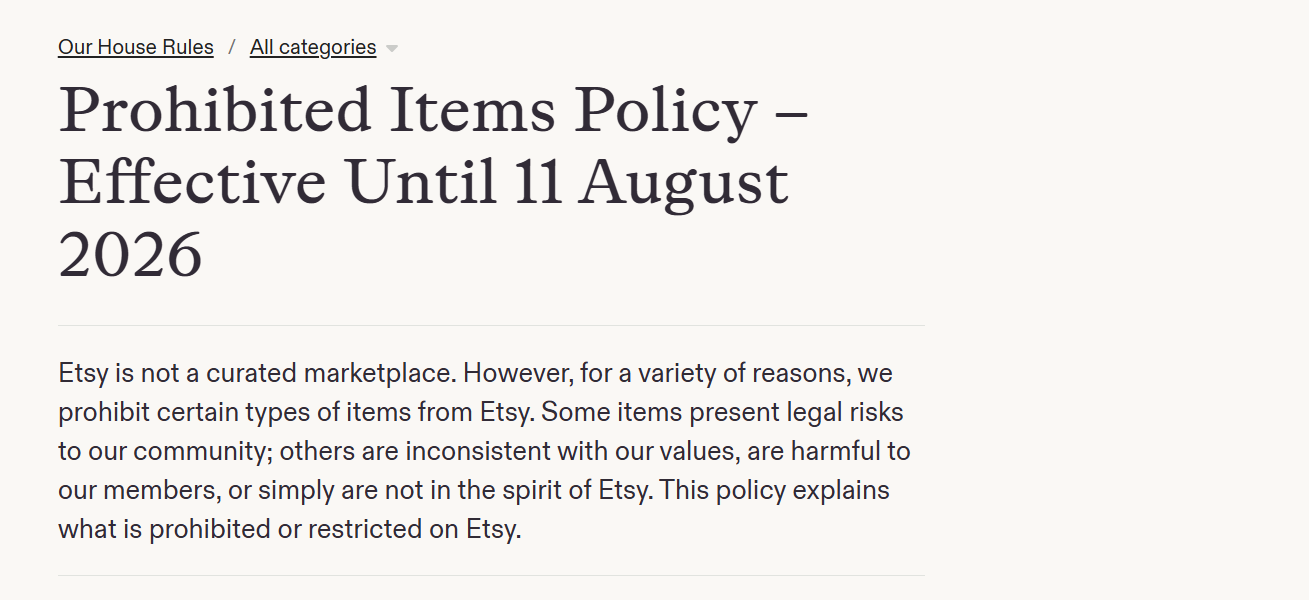
The product description indicates that it is a novelty writing instrument that uses refillable ink cartridges and is intended purely as a decorative or novelty item. We also reviewed Etsy’s prohibited items policy. According to the platform, weapons, explosives, and other dangerous items are not permitted to be sold on the website.
https://www.etsy.com/legal/prohibited/
Additionally, we attempted to contact Michael Dobbs, associated with the product listing, for clarification. This report will be updated if a response is received.
Conclusion
The evidence gathered during our research clearly shows that the claim is false. The viral image does not depict a bomb but a novelty grenade-style ink pen sold online. There is no evidence that such pens are causing explosions in Gujarat, and the claim being circulated on social media is entirely misleading.
