
#FactCheck: Viral AI image shown as AI -171 caught fire after collision
Executive Summary:
A dramatic image circulating online, showing a Boeing 787 of Air India engulfed in flames after crashing into a building in Ahmedabad, is not a genuine photograph from the incident. Our research has confirmed it was created using artificial intelligence.

Claim:
Social media posts and forwarded messages allege that the image shows the actual crash of Air India Flight AI‑171 near Ahmedabad airport on June 12, 2025.

Fact Check:
In our research to validate the authenticity of the viral image, we conducted a reverse image search and analyzed it using AI-detection tools like Hive Moderation. The image showed clear signs of manipulation, distorted details, and inconsistent lighting. Hive Moderation flagged it as “Likely AI-generated”, confirming it was synthetically created and not a real photograph.

In contrast, verified visuals and information about the Air India Flight AI-171 crash have been published by credible news agencies like The Indian Express and Hindustan Times, confirmed by the aviation authorities. Authentic reports include on-ground video footage and official statements, none of which feature the viral image. This confirms that the circulating photo is unrelated to the actual incident.

Conclusion:
The viral photograph is a fabrication, created by AI, not a real depiction of the Ahmedabad crash. It does not represent factual visuals from the tragedy. It’s essential to rely on verified images from credible news agencies and official investigation reports when discussing such sensitive events.
- Claim: An Air India Boeing aircraft crashed into a building near Ahmedabad airport
- Claimed On: Social Media
- Fact Check: False and Misleading

Related Blogs
Executive Summary
A claim circulating on social media alleges that India refused to unload crude oil from two Iranian tankers following a call between US President Donald Trump and Prime Minister Narendra Modi, after the US announced fresh restrictions on Iranian oil exports. However, research by the CyberPeace Research Wing found the claim to be misleading. The probe revealed that two supertankers carrying Iranian crude are currently anchored off India’s western and eastern coasts. No credible evidence or reports suggest that India refused to unload the cargo or sent the vessels back.
Claim
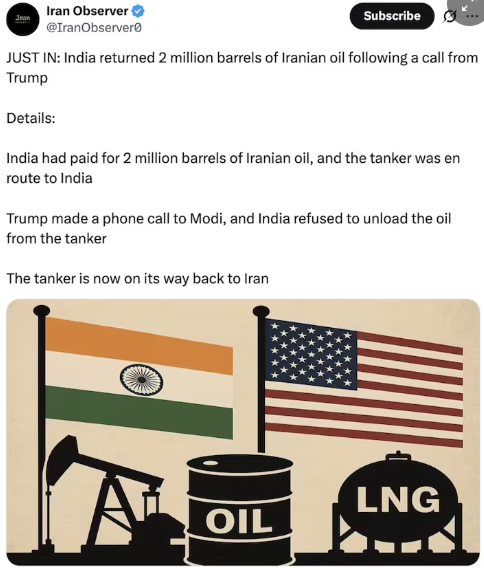
A user on X claimed that India returned 2 million barrels of Iranian crude oil after a phone call from Donald Trump. According to the post, India had already paid for the oil and the tanker was en route, but following the call with Narendra Modi, authorities refused to unload the shipment and sent the tanker back to Iran.
Fact Check
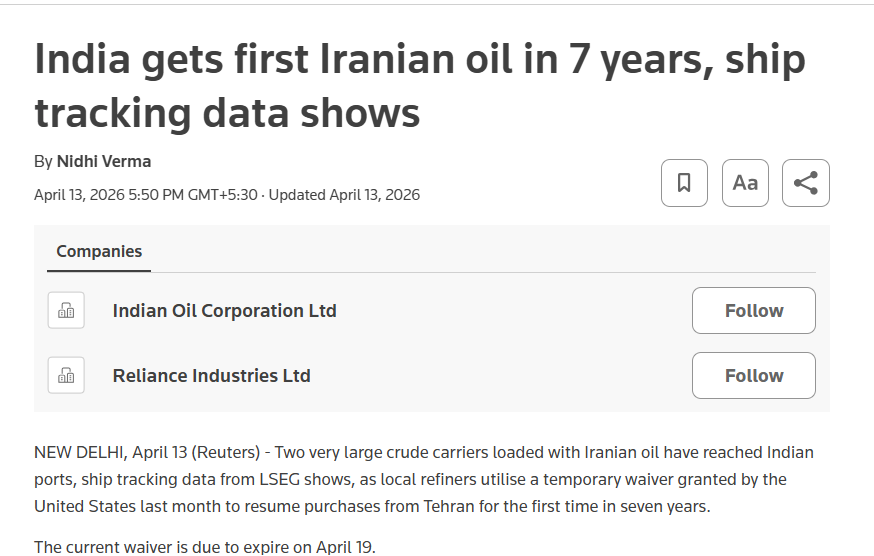
No credible national or international media reports were found to support the claim that India refused to accept Iranian oil or returned the tankers. Given the global scrutiny on oil shipments amid tensions in West Asia, any such development would have drawn widespread coverage. According to Reuters, two large crude carriers loaded with Iranian oil reached Indian ports on April 13. The Iran-flagged Felicity arrived near Sikka port in Gujarat, while the Curacao-flagged Jaya reached Paradip port in Odisha. The report noted that this marked the first purchase of Iranian oil by Indian refiners since 2019.
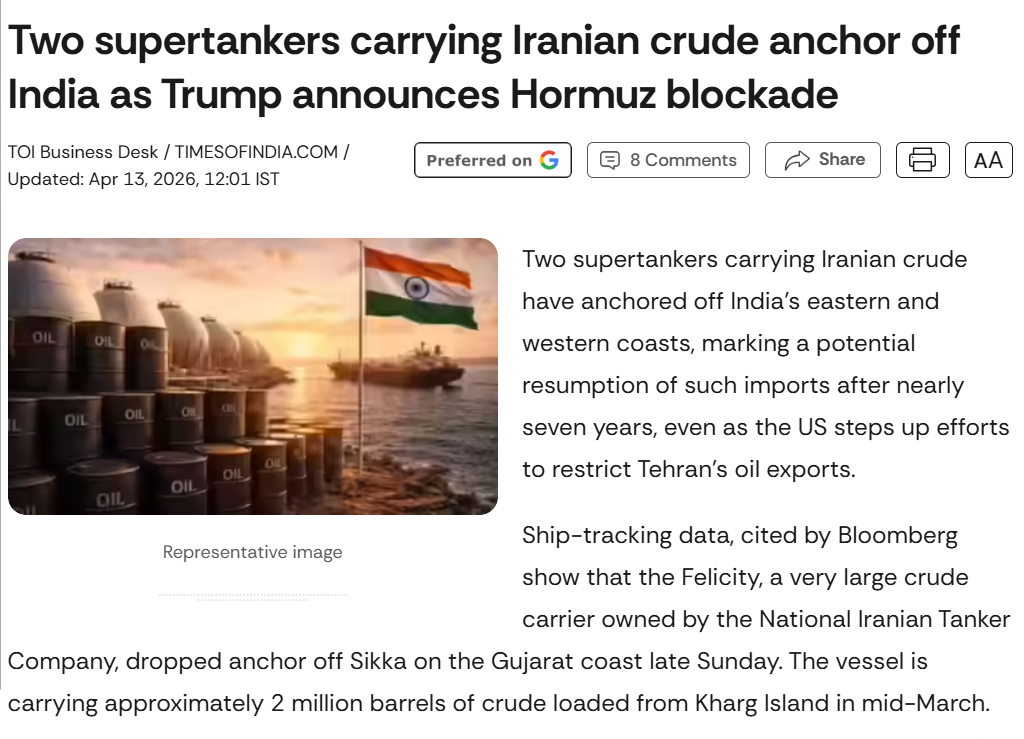
Further, The Times of India reported that Felicity, owned by the National Iranian Tanker Company, anchored off Sikka on April 12 carrying around 2 million barrels of crude loaded from Kharg Island in mid-March. The second tanker, Jaya, also anchored near Paradip around the same time, having departed with a similar volume of crude in late February. While the buyers of these cargoes have not been officially disclosed, Paradip port is primarily used by Indian Oil Corporation, while Sikka port is used by Reliance Industries and Bharat Petroleum Corporation.
Conclusion
The viral claim is false and misleading. Available evidence shows that the Iranian oil tankers are stationed near Indian ports, and there is no confirmation that India refused to unload the cargo or sent the vessels back.

Introduction
Artificial Intelligence (AI) is fast transforming our future in the digital world, transforming healthcare, finance, education, and cybersecurity. But alongside this technology, bad actors are also weaponising it. More and more, state-sponsored cyber actors are misusing AI tools such as ChatGPT and other generative models to automate disinformation, enable cyberattacks, and speed up social engineering operations. This write-up explores why and how AI, in the form of large language models (LLMs), is being exploited in cyber operations associated with adversarial states, and the necessity for international vigilance, regulation, and AI safety guidelines.
The Shift: AI as a Cyber Weapon
State-sponsored threat actors are misusing tools such as ChatGPT to turbocharge their cyber arsenal.
- Phishing Campaigns using AI- Generative AI allows for highly convincing and grammatically correct phishing emails. Unlike the shoddily written scams of yesteryears, these AI-based messages are tailored according to the victim's location, language, and professional background, increasing the attack success rate considerably. Example: It has recently been reported by OpenAI and Microsoft that Russian and North Korean APTs have employed LLMs to create customised phishing baits and malware obfuscation notes.
- Malware Obfuscation and Script Generation- Big Language Models (LLMs) such as ChatGPT may be used by cyber attackers to help write, debug, and camouflage malicious scripts. While the majority of AI instruments contain safety mechanisms to guard against abuse, threat actors often exploit "jailbreaking" to evade these protections. Once such constraints are lifted, the model can be utilised to develop polymorphic malware that alters its code composition to avoid detection. It can also be used to obfuscate PowerShell or Python scripts to render them difficult for conventional antivirus software to identify. Also, LLMs have been employed to propose techniques for backdoor installation, additional facilitating stealthy access to hijacked systems.
- Disinformation and Narrative Manipulation
State-sponsored cyber actors are increasingly employing AI to scale up and automate disinformation operations, especially on election, protest, and geopolitical dispute days. With LLMs' assistance, these actors can create massive amounts of ersatz news stories, deepfake interview transcripts, imitation social media posts, and bogus public remarks on online forums and petitions. The localisation of content makes this strategy especially perilous, as messages are written with cultural and linguistic specificity, making them credible and more difficult to detect. The ultimate aim is to seed societal unrest, manipulate public sentiments, and erode faith in democratic institutions.
Disrupting Malicious Uses of AI – OpenAI Report (June 2025)
OpenAI released a comprehensive threat intelligence report called "Disrupting Malicious Uses of AI" and the “Staying ahead of threat actors in the age of AI”, which outlined how state-affiliated actors had been testing and misusing its language models for malicious intent. The report named few advanced persistent threat (APT) groups, each attributed to particular nation-states. OpenAI highlighted that the threat actors used the models mostly for enhancing linguistic quality, generating social engineering content, and expanding operations. Significantly, the report mentioned that the tools were not utilized to produce malware, but rather to support preparatory and communicative phases of larger cyber operations.
AI Jailbreaking: Dodging Safety Measures
One of the largest worries is how malicious users can "jailbreak" AI models, misleading them into generating banned content using adversarial input. Some methods employed are:
- Roleplay: Simulating the AI being a professional criminal advisor
- Obfuscation: Concealing requests with code or jargon
- Language Switching: Proposing sensitive inquiries in less frequently moderated languages
- Prompt Injection: Lacing dangerous requests within innocent-appearing questions
These methods have enabled attackers to bypass moderation tools, transforming otherwise moral tools into cybercrime instruments.
Conclusion
As AI generations evolve and become more accessible, its application by state-sponsored cyber actors is unprecedentedly threatening global cybersecurity. The distinction between nation-state intelligence collection and cybercrime is eroding, with AI serving as a multiplier of adversarial campaigns. AI tools such as ChatGPT, which were created for benevolent purposes, can be targeted to multiply phishing, propaganda, and social engineering attacks. The cross-border governance, ethical development practices, and cyber hygiene practices need to be encouraged. AI needs to be shaped not only by innovation but by responsibility.
References
- https://www.microsoft.com/en-us/security/blog/2024/02/14/staying-ahead-of-threat-actors-in-the-age-of-ai/
- https://www.bankinfosecurity.com/openais-chatgpt-hit-nation-state-hackers-a-28640
- https://oecd.ai/en/incidents/2025-06-13-b5e9
- https://www.microsoft.com/en-us/security/security-insider/meet-the-experts/emerging-AI-tactics-in-use-by-threat-actors
- https://www.wired.com/story/youre-not-ready-for-ai-hacker-agents/
- https://www.cert-in.org.in/PDF/Digital_Threat_Report_2024.pdf
- https://cdn.openai.com/threat-intelligence-reports/5f73af09-a3a3-4a55-992e-069237681620/disrupting-malicious-uses-of-ai-june-2025.pdf

Introduction
In the sprawling and ever-evolving landscape of cybercrime, phishing links, phoney emails, and dubious investment offers are no longer the only tools used by scammers. Cybercriminals are becoming skilled at taking advantage of commonplace digital behaviours, undermining confidence, and turning popular features of our most essential apps into weapons. A fast expanding international threat has been revealed by the National Cybercrime Threat Analytics Unit (NCTAU) of the Indian Cybercrime Coordination Centre(I4C)’s most recent advisory on “WhatsApp account renting”. This scam uses QR codes to trick users into connecting their WhatsApp accounts to fraudulent sites under the guise of a “quick income” opportunity. What initially appears innocuous turns into a tool for thieves to take control of accounts and use them for illicit purposes.
The Global Rise of Cyber Mule Networks
Initially the word “mule” in cybercrime networks referred to a bank account used, knowingly often unknowingly, to transfer or “launder” money obtained from fraud and illegal activities. In light of the evolving nature of this cybercrime, Cyber mules in the present scenario can be referred to as, individuals who knowingly or unknowingly allow their digital identities, devices, or bank accounts to be used for illegal activity.
Various cybersecurity companies as well as Europol and Interpol, have frequently cautioned that hackers are increasingly using digital mule recruiting, which frequently takes the form of the following:
- Work-from-home Offers
- Streams of passive income
- Monetisation of social media
- Roles for verification assistants
- Apps that earn commissions
Earlier versions involved money transfers through personal bank accounts . Criminals now want your digital identity rather than just your money, as the trend has been reported to be changing.
Scammers frequently “rent” victims’ Facebook, LINE, Telegram, and WeChat accounts in parts of Southeast Asia and Africa in order to conduct impersonation frauds or assist with criminal operations. The WhatsApp variant that is making its way to India is a logical progression, although it comes only with the widely used WhatsApp Web linked-device capability.
How the WhatsApp Account Renting Scam Works
I4C’s advisory dated 15th October, 2025, highlights a sophisticated yet psychologically simple scheme that exploits trust, curiosity, and the illusion of easy income.The scam’s lifetime is as follows:
1. The Hook: “Automatically Earn Passive Income”
Threat actors claim users can earn daily rewards by connecting their WhatsApp accounts to a new “partner platform” in their polished and professional Instagram and Facebook ads.
This strategy imitates international scam factories in Cambodia and Myanmar, where victims are lured into investment schemes or bogus tasks by social media advertisements.
2.The Redirect: Rogue APKs & Fake Websites
When victims click on the advertisement, they are sent to
- Fake dashboards for earnings
- Untrustworthy websites that imitate authentic financial interfaces
- Instructions for installing Android APKs from sources other than the Play Store
- These APKs often carry spyware or remote-access malware.
3.The Trap: Scanning a QR Code
The user is asked to scan a QR code through WhatsApp’s “Linked Devices” feature, which is normally used for WhatsApp Web.
Without ever touching the victim’s phone, the con artist obtains complete session access to their WhatsApp account as soon as the QR is scanned.
Threat actors are able to:
- Transmit and receive messages
- Get access to contact lists
- Participate in or start groups
- Assume the victim’s identity
- Conduct frauds using their identities
4.The Illusion: A Multi-Level Commission Structure
A pyramid-style earnings model is displayed to maintain credibility:
- 10% off direct invites
- 5% of secondary invites
- 2% of tertiary invitations
These figures are designed to encourage victims to recruit more users, increasing the number of compromised WhatsApp accounts.
5.The Misuse: “Mule WhatsApp accounts”
The victim’s account becomes a digital mule once it is connected, allowing fraudsters to:
- Start UPI fraud and phishing
- Distribute harmful links
- Impersonate the victim to scam their contacts
- Participate in bulk messaging campaigns
- Get additional mule accounts
Precautions Issued by I4C
I4C has advised citizens to take the following precautions:
- You could face criminal charges or similar consequences if you carelessly rent or link your WhatsApp account for money
- Installing APKs from non-official app shops should be avoided
- Advertisements that promise automatic revenue, referral bonuses, or passive income should be avoided.
- Regularly check linked devices on WhatsApp: Settings → Linked Devices
- Use WhatsApp’s Official support page to report hacked accounts or impersonation: https://www.whatsapp.com/contact/forms/1534459096974129
- Report financial fraud immediately by calling 1930 or visiting cybercrime.gov.in
CyberPeace Outlook
The WhatsApp account rental fraud is not an isolated phenomenon; rather, it is the latest mutation of a global cybercrime apparatus that feeds on social engineering, digital identity theft, and international mule networks. Its simplicity, all it takes to take over your digital life is a QR code scan, makes it especially hazardous. I4C’s timely warning serves as an important reminder that easy money is nearly always a trap in the digital world and that, if we let our guard down, our most reliable platforms can become attack surfaces. Stay informed, and stay safe. In order to protect our identities, data, and communities, cyber hygiene is now a must.
References
- https://www.cnbctv18.com/personal-finance/mule-account-fraud-on-the-rise-what-it-is-and-how-to-shttps://i4c.mha.gov.in/theme/resources/advisories/Mule%20Whatsapp%20V1.4.pdftay-safe-19662507.htm
- https://i4c.mha.gov.in/theme/resources/advisories/Mule%20Whatsapp%20V1.4.pdf
