
#FactCheck - Viral Claim of Highway in J&K Proven Misleading
Executive Summary:
A viral post on social media shared with misleading captions about a National Highway being built with large bridges over a mountainside in Jammu and Kashmir. However, the investigation of the claim shows that the bridge is from China. Thus the video is false and misleading.

Claim:
A video circulating of National Highway 14 construction being built on the mountain side in Jammu and Kashmir.

Fact Check:
Upon receiving the image, Reverse Image Search was carried out, an image of an under-construction road, falsely linked to Jammu and Kashmir has been proven inaccurate. After investigating we confirmed the road is from a different location that is G6911 Ankang-Laifeng Expressway in China, highlighting the need to verify information before sharing.


Conclusion:
The viral claim mentioning under-construction Highway from Jammu and Kashmir is false. The post is actually from China and not J&K. Misinformation like this can mislead the public. Before sharing viral posts, take a brief moment to verify the facts. This highlights the importance of verifying information and relying on credible sources to combat the spread of false claims.
- Claim: Under-Construction Road Falsely Linked to Jammu and Kashmir
- Claimed On: Instagram and X (Formerly Known As Twitter)
- Fact Check: False and Misleading

Related Blogs

Executive Summary
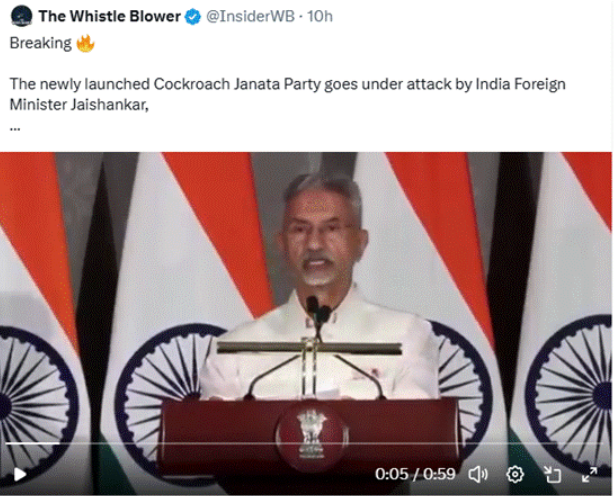
A video featuring India’s External Affairs Minister S. Jaishankar is being widely circulated on social media with the claim that he urged US Secretary of State Marco Rubio and US President Donald Trump to hand over the “handlers” of the so-called “Cockroach Janata Party” to India. The viral post further alleges that Jaishankar described the organisation as a “Pakistani and Iranian proxy group.” CyberPeace Research Wing research found the viral claim to be fake. External Affairs Minister S. Jaishankar did not make any statement regarding the “Cockroach Party” or its alleged handlers during the press conference. The viral video has been edited and is being shared with a misleading claim.
Claim
A verified X (formerly Twitter) user shared the viral clip and claimed that during a joint press conference, Jaishankar said:“I request Marco Rubio and Trump to hand over the handlers of the Cockroach Party because they are Pakistani and Iranian proxy groups.”
Fact Check
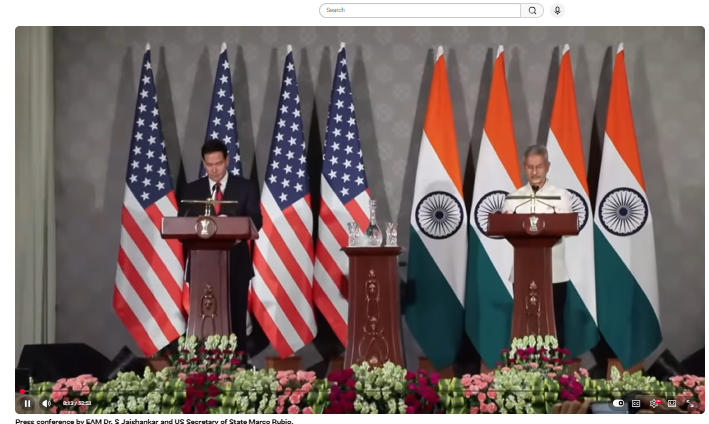
To verify the claim, we converted the viral clip into key frames and conducted a reverse image search. During the research, we found the original video uploaded on May 24, 2026, on the official YouTube channel of the Ministry of External Affairs.
The video was captioned:“Press conference of EAM Dr S Jaishankar and US Secretary of State Marco Rubio.”
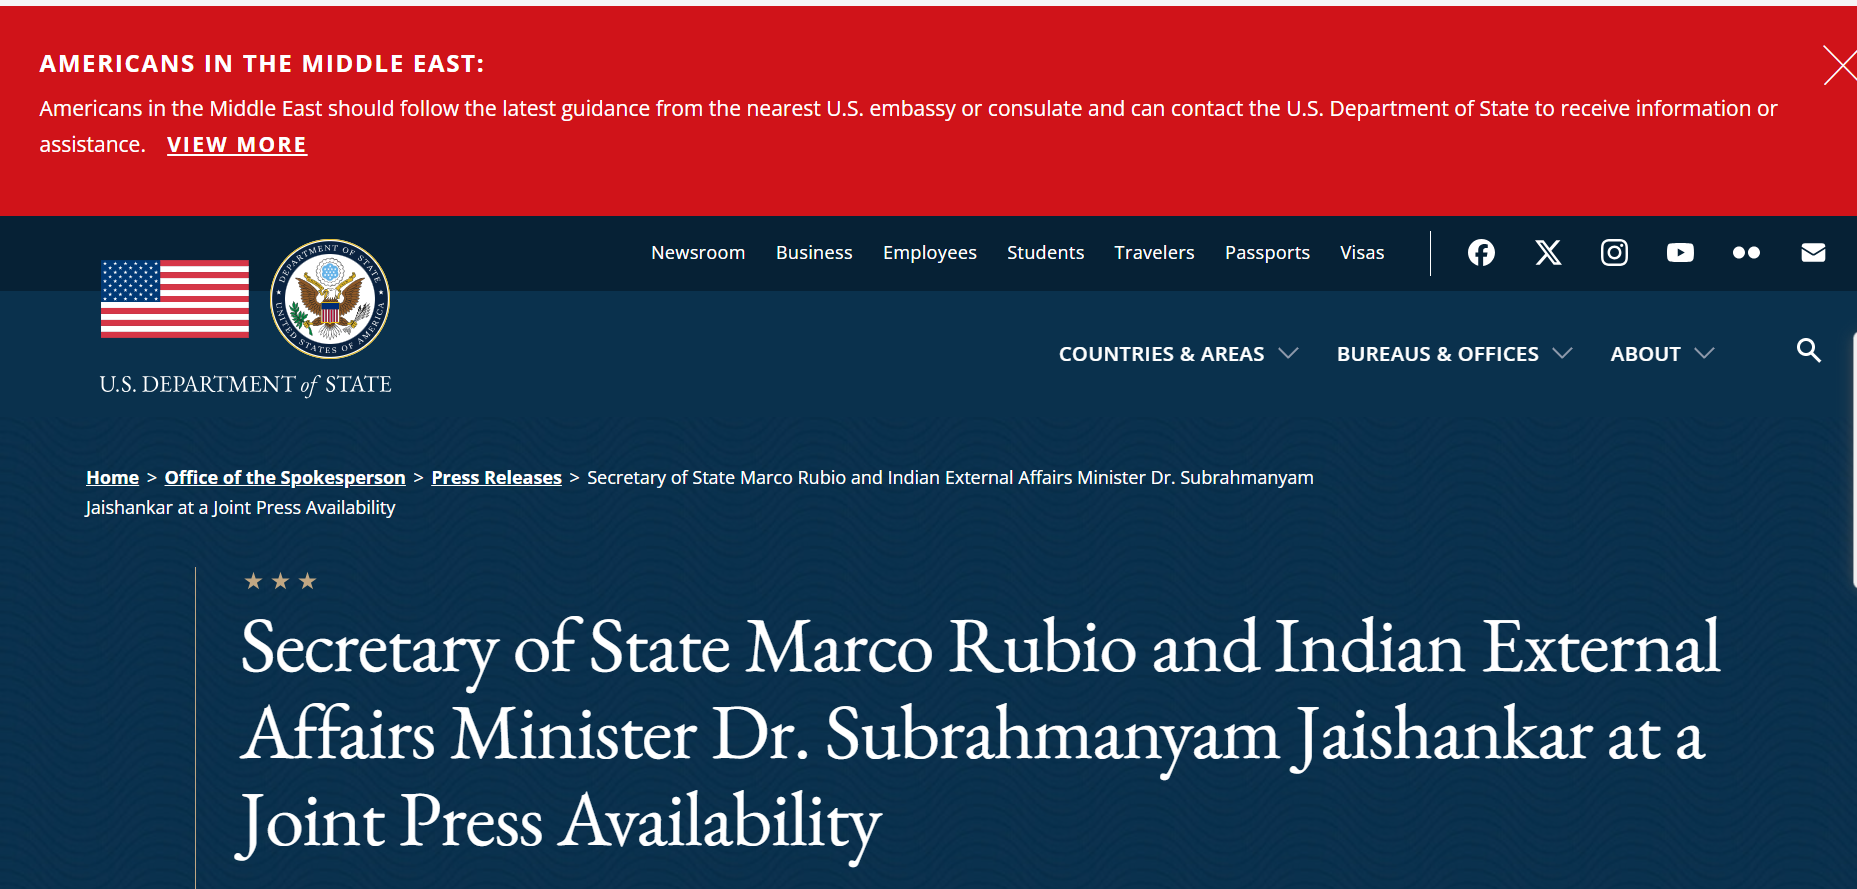
A review of the full press conference confirmed that Jaishankar made no mention of any “Cockroach Party,” its alleged handlers, or any Pakistani or Iranian proxy network. Further verification of the official transcripts published by both the Indian Ministry of External Affairs and the United States Department of State also found no references to the terms “Cockroach Party,” “handlers,” “Pakistani proxy,” or any statements matching the viral claim.
https://www.state.gov/releases/office-of-the-spokesperson/2026/05/secretary-of-state-marco-rubio-and-indian-external-affairs-minister-dr-subrahmanyam-jaishankar-at-a-joint-press-availability
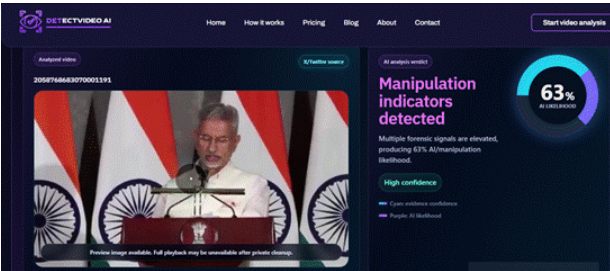
In the final stage of verification, the viral clip was analysed using an AI detection tool. The analysis suggested that the audio had been manipulated and that the video appeared to be edited. The tool indicated a 63 percent probability that the clip had been altered using AI-based editing techniques.
Conclusion
The research confirms that the viral claim is fake. S. Jaishankar did not make any statement regarding the “Cockroach Party” or its alleged handlers during the press conference. The viral clip has been edited and is being shared with misleading claims.
Introduction
Every domain of conflict has eventually had to learn restraint. The first Geneva Convention of 1864 grew out of one man's horror at what he saw after a single battle, and it rested on an idea that has since become the backbone of humanitarian law: even in war, there are things that must not be done to people. Cyberspace is the newest domain to face that test, and it is arguably the hardest. Code carries no uniform, an intrusion crosses borders without anyone noticing, and the same network can serve a soldier, a shopkeeper and a schoolchild at once. Whether the actor is a criminal group, an intelligence service or a military cyber unit, the consequences land on ordinary people. That is the case for a humanitarian approach to cyberspace, and it is why it has moved from a courtesy to a matter of national security.
Why the humanitarian lens matters to every nation
Cyberspace does not sort itself into civilian and military zones. The International Committee of the Red Cross (ICRC) has pointed out for years that military networks lean on civilian cyber infrastructure such as undersea cables, satellites and routers, while civilian supply chains and essential services run over the same channels. A cyber operation aimed at one can land on the other, and the ICRC has warned that incidental harm in this domain risks being widespread and crossing national borders.
It helps to separate three situations, because different rules govern each. Cybercrime, such as ransomware against a hospital, is a matter for criminal law and international police cooperation. Intrusion and espionage in peacetime fall under domestic law and the norms of responsible state behaviour agreed at the United Nations. Cyber operations during an armed conflict fall under international humanitarian law (IHL), which the ICRC and a growing number of states hold applies to cyber means just as it applies to any other weapon or method of warfare. Its core principles, humanity, necessity, proportionality and distinction, were linked to cyberspace in the 2021 report of the UN Group of Governmental Experts. Under those principles civilians and civilian infrastructure must not be attacked, and medical facilities enjoy special protection.
For a nation, the practical point is simpler. Its own hospitals, grids, water systems and payment networks are exactly the assets that erode first when restraint erodes. A country that argues for humanitarian limits is protecting itself as much as anyone else.
A lesson from Lebanon
The events of 17 and 18 September 2024 in Lebanon show what happens when everyday technology stops being trustworthy. On the first day, thousands of pagers detonated across the country within roughly an hour of each other. The next day, hand held radios followed. By the account UN High Commissioner for Human Rights Volker Türk gave the Security Council on 20 September, at least 37 people had been killed, including two children, and more than 3,400 had been injured in Lebanon alone. UN experts noted that medical personnel were among the dead.
Attribution in this case remained a matter of public allegation rather than official claim, and this piece does not try to settle it. What matters here is the method and how the UN read it legally. Türk told the Council that IHL prohibits booby traps in the form of apparently harmless portable objects designed and constructed to contain explosives, and that violence intended to spread terror among civilians is a war crime. He added that striking thousands of people simultaneously, without knowing who held the devices, where they were or who stood nearby, violates international human rights law and, where applicable, IHL. His summary was that this cannot become the new normal, and he called for an independent, thorough and transparent investigation.
The pager episode was physical, with explosives concealed in hardware, not malicious code. It belongs in a discussion of cyberspace because of how it worked: a compromised supply chain turned an ordinary civilian communication tool into a weapon. That is the same trust relationship every digital system depends on. When people cannot assume that the devices and software they use are what they appear to be, the line between civilian object and military instrument, the foundation of humanitarian law, survives on paper while wearing away in practice.
The Digital Emblem Project
What it is:Think of the red cross on a hospital roof or an ambulance. It tells anyone who sees it that the building or vehicle is protected and must not be attacked. The Digital Emblem is the same idea for computer systems. It is a digital marker, built on a cryptographic signature, that a protected server or network broadcasts to signal that it belongs to a medical or humanitarian organisation entitled to protection under international humanitarian law. The organisations allowed to use it are the same ones entitled to use the physical emblem.
What it aims to achieve:Its purpose is recognition. Someone probing a network cannot see a red cross, and may not realise they have entered a medical facility's systems or a Red Cross office. The digital emblem lets that fact be detected and verified by machines, so a military cyber unit or any other operator can recognise the system and avoid it. It does not create any new legal protection, and it does not replace cybersecurity. Like the physical emblem, it cannot stop an attack on its own. It makes existing protection visible.
Why it was created:The physical emblem has worked for more than 150 years, but it has no natural place online. Cyber operations are becoming a regular feature of armed conflict, and humanitarian bodies are targeted by criminals seeking money as well as by state linked actors. The ICRC learned this directly in 2022, when a breach of its own servers exposed the data of more than 515,000 people in vulnerable situations. It began researching a digital equivalent and, with ETH Zurich, developed a technical standard.
Where it stands today:The idea has moved from concept to working prototype. In October 2024, Resolution 2 was adopted at the International Conference of the Red Cross and Red Crescent, which includes all 196 states party to the Geneva Conventions, affirming that the duty to respect and protect medical services and humanitarian personnel applies to their use of information and communication technologies. In July 2026, the ICRC, with Microsoft's support, presented the emblem in Geneva and announced the next phase, with several national Red Cross societies already testing it. That phase is expected to take several years. Technical standards still need to be developed through bodies such as the International Telecommunication Union and the Internet Engineering Task Force, and international law would need to recognise the emblem formally, through an amendment to the Geneva Conventions framework or a new protocol.
For nations, the emblem offers a practical way to mark hospital and humanitarian networks as off limits, and it removes the excuse of not knowing when a marked system is attacked. That makes accountability clearer. It also supports the central argument of this piece: humanitarian principles only work in cyberspace if they can be seen and acted on, not just written down. Its success will depend on whether the people it addresses, state cyber forces and criminal groups alike, choose to honour it, which is why adoption and enforcement at national level will matter as much as the technology.
What nations can do now
None of this requires waiting for a new treaty. A country can publicly state its national position on how international law, including IHL, applies to cyber operations, since the ICRC itself treats the publication of national views as a form of capacity building. It can classify healthcare, humanitarian, water and energy networks as protected critical infrastructure in its national cyber strategy, and plan to adopt the digital emblem for its own hospitals as standards mature. It can invest in supply chain assurance for the devices and software that civilians and governments depend on, which is the most direct lesson of the Lebanon episode. It can ensure that military cyber units are trained in IHL and that cyber capabilities undergo legal review with an eye to humanitarian impact. And it can treat ransomware against hospitals as the serious crime it is, backed by international cooperation on evidence and victim protection.
Conclusion
A humanitarian approach to cyberspace is sometimes dismissed as idealism. It is closer to enlightened self interest. Every state relies on the reciprocal restraint that keeps hospitals, grids and communications networks out of the crossfire, and every state is, at some point, on the receiving end of the alternative. The Lebanon episode showed how quickly trust in ordinary technology can fail, and the Digital Emblem shows one way the international community is trying to rebuild it. Nations that commit early, in doctrine, in procurement and in practice, will help decide whether cyberspace develops guardrails or simply learns to live without them. The idea behind the first Geneva Convention was that even conflict has limits. Cyberspace is where that argument now needs to be made again.
References
- ICRC, "ICRC proposes digital red cross/crescent emblem to signal protection in cyberspace." https://www.icrc.org/en/document/icrc-proposes-digital-red-crosscrescent-emblem-signal-protection-cyberspace
- ETH Zurich, "Digital emblem for humanitarian law in cyberspace." https://ethz.ch/en/news-and-events/eth-news/news/2023/11/digital-emblem-for-humanitarian-law-in-cyberspace.html
- Digital Watch Observatory, "ICRC unveils digital emblem to protect humanitarian organisations online." https://dig.watch/updates/icrc-digital-emblem-cybersecurity
- Geneva Solutions, "ICRC and Microsoft launch digital emblem to prevent cyberattacks." https://genevasolutions.news/peace-humanitarian/icrc-and-microsoft-launch-digital-emblem-to-prevent-cyberattacks
- "Making humanitarian protection visible in cyberspace: The promise of the Digital Emblem." https://blogs.microsoft.com/on-the-issues/2026/07/09/making-humanitarian-protection-visible-in-cyberspace-the-promise-of-the-digital-emblem/
- ICRC Humanitarian Law and Policy Blog, "IHL's lighthouse: navigating towards a digital emblem." https://blogs.icrc.org/law-and-policy/2026/01/15/ihls-lighthouse-navigating-towards-a-digital-emblem/
- Digital Watch Observatory, "Building Trust and Protection for Essential Digital Services: From Standards to Deployment." https://dig.watch/event/wsis-forum-2026/building-trust-and-protection-for-essential-digital-services-from-standards-to-deployment
- UN OHCHR, "Exploding pagers and radios: A terrifying violation of international law, say UN experts." https://www.ohchr.org/en/press-releases/2024/09/exploding-pagers-and-radios-terrifying-violation-international-law-say-un
- UN OHCHR, "Disrespect for international law is a matter of international peace and security, High Commissioner Türk tells the UN Security Council." https://www.ohchr.org/en/statements-and-speeches/2024/09/disrespect-for-international-law-a-matter-of-international-peace-and-security-hc
- ASIL Insights, "Cyber Operations under International Humanitarian Law: Perspectives from the ICRC." https://asil.org/insights/volume-24-issue-11/
- Pager Attack in Lebanon, CyberPeace Blog https://cyberpeace.org/resources/blogs/pager-attack-in-lebanon
Somewhere in a compliance meeting right now, someone is saying "we have eighteen months, we're fine." That sentence is doing the same thing a snooze button does at 6 a.m.: technically buying time, while quietly making the actual wake up call worse. India's data protection law just started its countdown, and the 18 months everyone keeps citing is not a grace period to procrastinate through. It is closer to a runway before takeoff. Runways exist for one purpose: building up speed until the plane has no choice but to leave the ground. Standing still on one is not a strategy.
What actually got notified, and when
On 13 November 2025, the Ministry of Electronics and Information Technology notified the Digital Personal Data Protection Rules, 2025, giving operational shape to the Digital Personal Data Protection Act that Parliament had passed back in August 2023. Alongside the Rules themselves, MeitY issued a separate Enforcement Notification setting out exactly when different provisions kick in, and a further notification establishing the Data Protection Board of India, headquartered in the National Capital Region with four members. The final Rules followed a genuinely deliberative process, MeitY had floated draft Rules in January 2025 for public consultation and received 6,915 individual inputs from startups, industry bodies, civil society groups, and citizens before finalising the version now in force. The headline structural decision, and the one causing the most confusion in boardrooms, is that the Rules do not commence all at once. They commence in three distinct phases spread across eighteen months, and different obligations become legally binding at each stage.
The phased timeline, laid out plainly
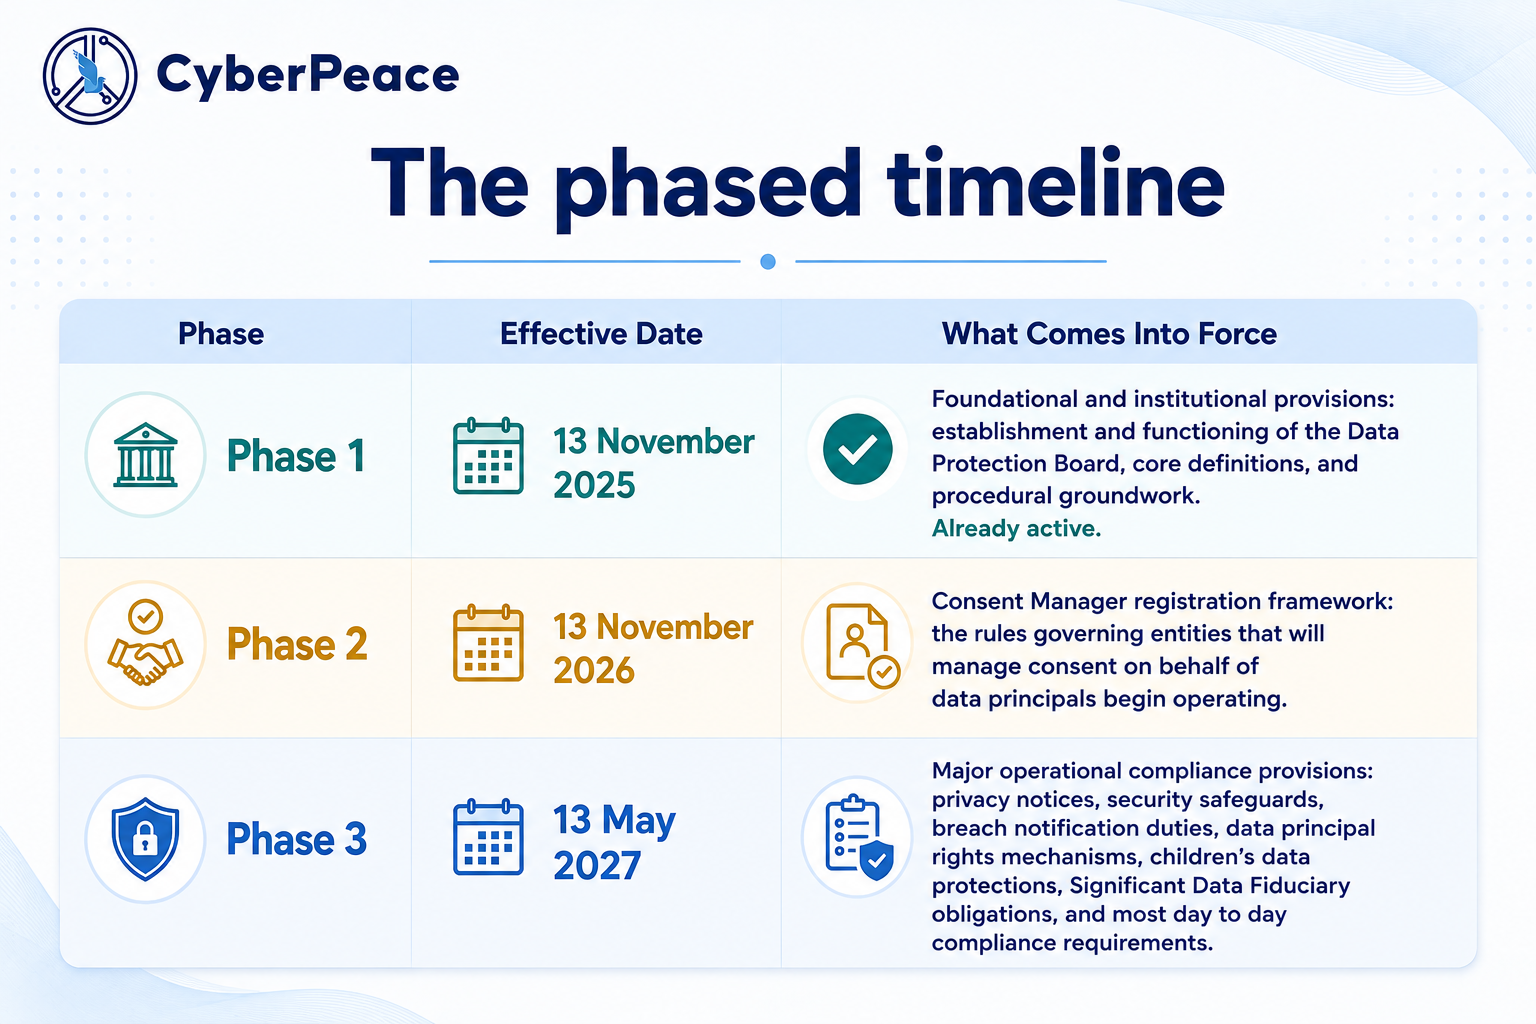
That third date, 13 May 2027, is the one that matters most for the vast majority of organisations, since it is where the bulk of actual operational obligations, the parts that touch product design, customer facing notices, and breach response, become enforceable. Legal commentary tracking the rollout has been consistent that this is described as a hard deadline with no grace period expected once it arrives, since the Data Protection Board is already operational and can begin receiving complaints well before Phase 3 obligations formally take effect.
Why "later" is a genuinely expensive plan
The financial stakes attached to Phase 3 non-compliance are not modest. The Schedule to the DPDP Act sets fixed penalty ceilings rather than turnover linked fines, which sounds gentler than Europe's GDPR model until you look at the actual numbers. Failure to implement reasonable security safeguards that results in a data breach can draw a penalty of up to 250 crore rupees per instance, the single highest tier in the Schedule. Failing to notify the Board or affected individuals after a breach occurs can draw up to 200 crore rupees, as can non-compliance with the Act's specific protections for children's data. Because these are assessed per instance rather than as a single capped exposure, a single incident that trips more than one obligation, say, inadequate safeguards that also delay breach notification, can compound into penalty exposure running into hundreds of crores from one event. All penalties collected go to the Consolidated Fund of India rather than to affected individuals directly, meaning the deterrent is aimed squarely at organisational behaviour, not compensation.
The part everyone keeps underestimating: this is not just a legal department problem
Perhaps the most consequential shift buried inside the DPDP framework is who actually has to own it. Reading the Rules as a checklist for the legal or privacy team alone misses how far the obligations actually reach. Building a compliant consent lifecycle touches product design. Security safeguards touch cybersecurity and IT infrastructure directly. Retention and deletion logic touches data governance and engineering. Third party risk review touches procurement. Breach preparedness touches internal audit and incident response. And increasingly, as organisations deploy AI systems that process personal data, AI governance enters the picture too, since a model trained or fine tuned on personal data inherits the same DPDP obligations as any other processing activity.
That cross functional reality is where most readiness programmes currently fall short. Treating DPDP compliance as a documentation exercise, updating a privacy policy PDF and calling it done, produces the appearance of compliance without the operational substance a Data Protection Board investigation would actually test. A breach response plan that exists only on paper and has never been rehearsed will not hold up against the 72 hour data principal notification window the Rules impose once Phase 3 lands. A consent mechanism bolted onto a website without corresponding backend logic to honour withdrawal requests will not satisfy an actual audit.
What a serious readiness posture looks like right now
Organisations that are ahead of this curve are already treating the eighteen month window as three overlapping workstreams rather than one deadline to hit at the end.
- The first is discovery: mapping what personal data exists, where it flows, who owns each system that touches it, and why it is collected in the first place, since compliance is structurally impossible without first knowing what you are protecting. This stage typically surfaces uncomfortable findings, shadow data sets nobody formally owns, vendor integrations nobody fully mapped, legacy systems still holding data well past any reasonable retention justification.
- The second is build: standing up the actual mechanisms, consent flows that can genuinely honour a withdrawal request end to end, rights request handling that does not depend on a single overworked employee checking an inbox, retention and deletion logic wired into the systems themselves rather than described only in a policy document, and security controls proportionate to the sensitivity of what is being protected.
- The third is proof: generating the internal evidence, audit trails, documented decisions, tested response procedures, that demonstrates governance was real rather than retrofitted after the fact. A Data Protection Board investigation, when it eventually happens, will not be satisfied by a well written policy; it will look for evidence that the policy was actually operational.
The actual question worth asking
The right question was never "when does DPDP become enforceable." Phase 1 already answered that; the law is live, and the Data Protection Board already exists and can act. The better question, the one worth taking into any leadership review between now and May 2027, is simpler and considerably less comfortable: will the organisation actually be ready when each phase's obligations become operational, or will readiness be assembled in a scramble once the deadline stops being theoretical. 18 months sounds long right up until the week it does not, and by the time Phase 3 lands, "we'll get to it" will no longer be a sentence any organisation gets to finish.
References
- Ministry of Electronics and Information Technology, Digital Personal Data Protection Rules, 2025, notified 13 November 2025. Press Information Bureau, "Digital Personal Data Protection Rules, 2025 Notified," 14 November 2025. https://static.pib.gov.in/WriteReadData/specificdocs/documents/2025/nov/doc20251117695301.pdf
- Shardul Amarchand Mangaldas & Co, "Enforcement of the DPDP Act and notification of the DPDP rules." https://www.amsshardul.com/insight/enforcement-of-the-dpdp-act-and-notification-of-the-dpdp-rules/
- S&R Associates, "India's Digital Personal Data Protection Regime Takes Effect." https://www.snrlaw.in/indias-digital-personal-data-protection-regime-takes-effect/
- Khurana & Khurana, "MeitY Notifies Rules Operationalising The DPDP Framework." https://www.khuranaandkhurana.com/update-meity-notifies-rules-operationalising-the-dpdp-framework-in-india
- Exchange4media, "DPDP Act 2025: Penalties for violations can reach Rs 250 crore." https://www.exchange4media.com/digital-news/dpdp-act-2025-penalties-for-confirmed-violations-can-reach-rs-250-crore-149360.html
- Seclore, "DPDP Rules 2025: India's Complete Compliance Guide." https://www.seclore.com/fundamentals/dpdp-rules-2025-compliance-guide/
