
#FactCheck - Deepfake Video Falsely Claims Indian Defence Secretary Admitted Pakistan ‘Jammed Indian Systems’
Executive Summary
A video allegedly showing India’s Defence Secretary Rajesh Kumar Singh making remarks about Pakistan’s cyber capabilities is being widely shared on social media. The clip claims that Singh admitted Pakistan had “jammed Indian systems” on May 10 and described Pakistan’s cyber and electronic warfare capabilities as a major challenge for India. Research by CyberPeace Research Wing found that the viral clip is an AI-generated deepfake being circulated to spread misinformation. Rajesh Kumar Singh never made any such statement.
Claim
An X user shared the viral video claiming that India’s Defence Secretary had acknowledged Pakistan’s technological superiority. The post alleged that Singh admitted Pakistan successfully jammed Indian systems and claimed that India was lagging behind in cyber and electronic warfare technology.

Fact Check
To verify the claim, we searched relevant keywords on Google but found no credible media reports carrying such a statement from the Defence Secretary. We then extracted keyframes from the viral clip and conducted a reverse image search. During the research, we found the original video uploaded on the YouTube channel of ANI on April 30, 2026.

A review of the full video confirmed that Rajesh Kumar Singh never made the remarks heard in the viral clip. The original footage had been manipulated and altered using AI-generated audio techniques.
Conclusion
Our research confirms that the viral video is fake and AI-manipulated. The statement attributed to India’s Defence Secretary Rajesh Kumar Singh is fabricated, and the deepfake clip is being shared with misleading claims to spread disinformation.

Related Blogs
A video clip of journalist Palki Sharma is being widely shared on social media. Along with the video, it is being claimed that during Prime Minister Narendra Modi’s recent Middle East visit, she questioned Jordan’s diplomatic protocol.
In the viral clip, Palki Sharma is allegedly seen asking why Jordan’s King Abdullah II did not come to the airport to receive Prime Minister Modi, and whether this indicated a downgrade in the level of welcome.
However, an investigation by the Cyber Peace Foundation found this claim to be misleading. The probe revealed that while the visuals in the viral video are genuine, the audio has been altered using Artificial Intelligence (AI).
On the social media platform ‘X’, a user named “Ammar Solangi” shared this video on 18 December. The post claimed that the video was related to questions raised about Jordan’s diplomatic protocol during Prime Minister Modi’s visit. According to the post, Palki Sharma questioned why King Abdullah II did not receive Prime Minister Modi at the airport. The archive link of the viral post can be seen here: https://ghostarchive.org/archive/26aK0
Verification
During the investigation, the fact-check desk noticed the ‘Firstpost’ logo in the top-left corner of the viral video. Based on this clue, a customized Google search was conducted, which led to the original news report.
The investigation revealed that the viral video was taken from an episode of journalist Palki Sharma’s show “Vantage with Palki Sharma”, which aired on 17 December.
Analysis of the video showed that the visuals appearing at the 33 minutes 30 seconds timestamp in the original report exactly match those used in the viral clip. However, in the original broadcast, Palki Sharma neither questioned Jordan’s protocol nor made any comment about King Abdullah II not being present at the airport.
In the original video, Palki Sharma says:
“Prime Minister Modi was on a diplomatic tour of Jordan, Ethiopia, and Oman, and in Jordan he was received at the airport by the country’s Prime Minister…” The link to the original report can be seen here: https://www.youtube.com/watch?v=-VYZYe9l6Bs
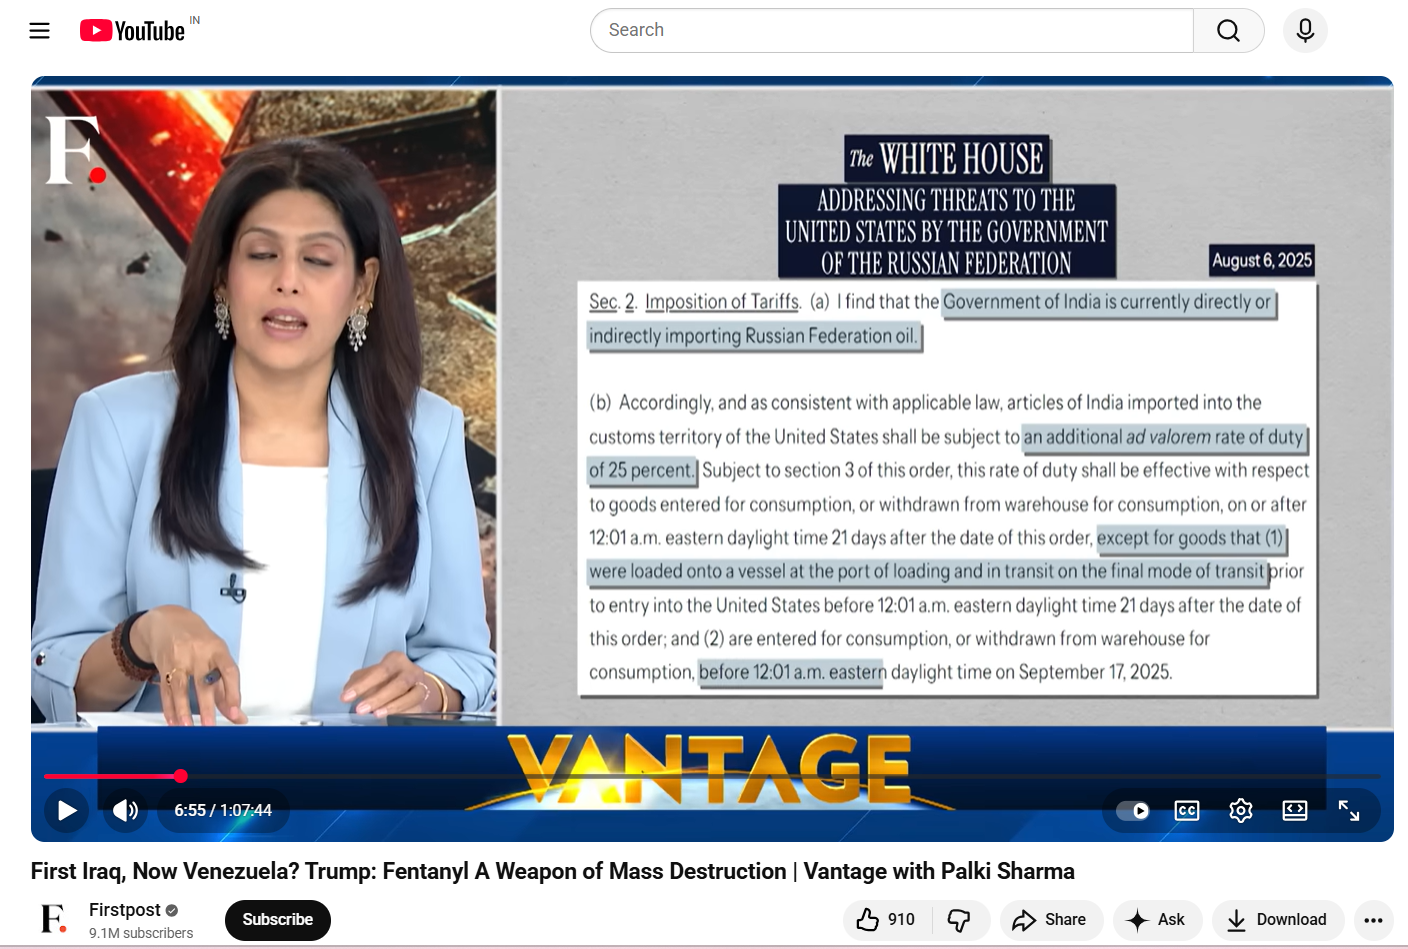
AI Audio Examination
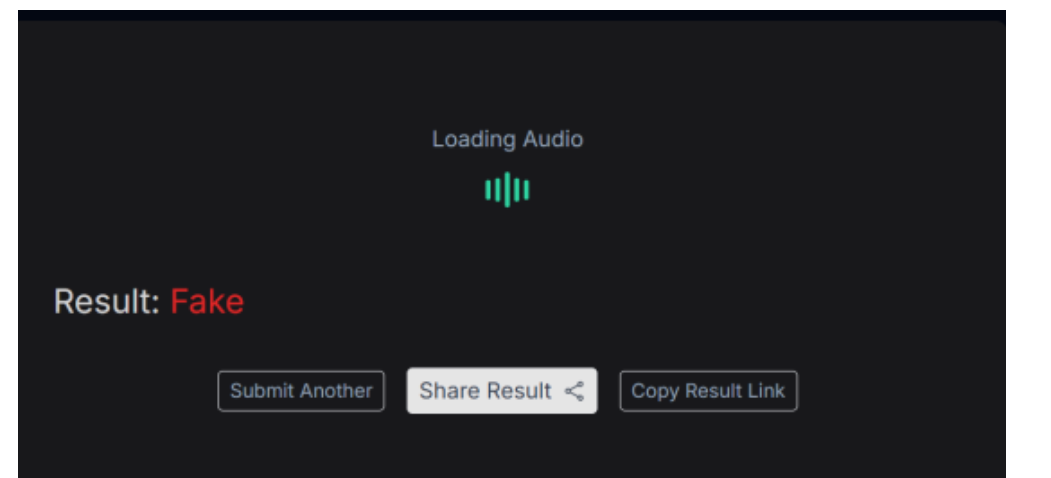
Further investigation involved separating the audio from the viral video and analyzing it using the AI voice detection tool ‘Resemble AI’. The tool’s results confirmed that fake, AI-generated audio had been added over the real footage in the viral clip to spread a misleading claim. A screenshot of the results from this examination can be seen below.
Conclusion
The video being circulated in the name of journalist Palki Sharma has been tampered with. Her voice has been altered using AI technology, and the claim made regarding the Jordan visit is completely misleading.

Introduction
Significantly, in March 2023, the Prevention of Money Laundering Act, 2002's regulations placed Virtual Digital Asset Service Providers functioning located under the purview of the Anti Money Laundering/Counter Financing of Terrorism (AML-CFT) scheme. An important step toward controlling VDA SP operations and guaranteeing adherence to Anti-Money Laundering and Combating the Financing of Terrorism (AML-CFT) regulations.
The significance of AML-CFT procedures
The AML-CFT framework's incorporation of Virtual Digital Asset Service Providers (VDA SPs) is essential for protecting the banking industry from illegal activities including the laundering of funds and counter-financing of terrorist attacks. These regulations become more crucial as the market for digital assets develops and becomes more well-known.
The practice of money laundering is hiding the source of the sum received illegally, thus it's critical to have strict policies in place to track down and stop these kinds of operations. Furthermore, funding for terrorism is a serious danger to international safety, hence stopping the flow of money to terrorist companies is a top concern for global officials.
The goal of policymakers' move to include VDA SPs in the AML-CFT architecture is to set up control and surveillance procedures that will guarantee these organisations' open and honest operations. This involves tracking transactions, flagging questionable activity, and conducting extensive customer investigations. Incorporating such procedures not only reduces the potential for financial crimes but also builds confidence and trust in the electronic asset market.
It is important to see the significance of AML-CFT procedures and the changes in the legal framework to reflect the evolving characteristics of digital currencies. These procedures are essential to preserving the reliability and safety of the wider banking system.
Notifications of Compliance Show Cause
Under Section 13 of the PMLA Act 2002, FIU IND sent adherence Show Cause Notices to nine offshore Virtual Digital Asset Service Providers (VDA SPs) as part of its dedication to upholding compliance with regulations. This affirmative step requires organisations to be scrutinised and attempted to bring them under inspection.
Governmental Response
The Director of FIU IND has addressed the Secretary of the Ministry of Electronics and Information Technology to take further measures due to the disregard of offshore firms. According to the notification, URLs connected to these organisations that operate in India in violation of the PML Act's requirements must be blocked.
Mandatory Registration for VDA SPs
Virtual Digital Asset Service Providers (both onshore and offshore) who perform a range of operations, including the trading of digital goods for monetary currencies, the distribution of digital currency, and the management or preservation of electronic assets, are now obliged to register with FIU.
Range of Statutory Responsibilities
In accordance with the PML Act, VDA SPs are subject to several requirements, including documentation, disclosure, and other duties. One of their responsibilities is to register with the FIU IND. The primary focus is on guaranteeing that VDA SPs comply with AML-CFT protocols, hence enhancing the general reliability of the banking industry.
Difficulties with Offshore Compliance
There are many obstacles in guaranteeing that offshore organisations comply with Anti Money Laundering/Counter Financing of Terrorism (AML-CFT), chief amongst them being their unwillingness to undergo registration. Some overseas Virtual Digital Asset Service Providers (VDA SPs) have been reluctant to comply with the existing rules and regulations, even though they cater to a significant number of Indian users. There are several reasons for this hesitation, such as worries about heightened monitoring, the expense of compliance, and the apparent complexity of governmental processes. Regulatory organisations have taken steps to close the discrepancy between offshore businesses' real activities and the regulations they must follow. In addition to maintaining the trustworthiness of the economic system, resolving the issues with offshore adherence is essential for promoting confidence and openness in the market for electronic assets.
Conclusion
FIU IND has demonstrated its dedication to creating an effective regulatory framework for Virtual Digital Asset Service Providers through its recent measures. India hopes to fortify its countermeasures against money laundering and safeguard the financial well-being of its users by expanding the AML-CFT legislation to offshore firms. The continuous efforts to restrict the URLs of non-compliant companies show a proactive approach to stopping illicit activity and fostering a safe and law-abiding virtual asset ecosystem. The safety and soundness of the banking sector will be crucially maintained by laws and regulations as the digital world develops.
References
- https://pib.gov.in/PressReleasePage.aspx?PRID=1991372
- https://www.thehindubusinessline.com/books/reviews/business-economy/fiu-ind-issues-compliance-showcause-notices-to-nine-offshore-vda-sps/article67684613.ece
- https://business.outlookindia.com/news/fiu-issues-notice-to-9-offshore-crypto-platforms-writes-to-meity-for-blocking-of-urls

Introduction
Recently, in April 2025, security researchers at Oligo Security exposed a substantial and wide-ranging threat impacting Apple's AirPlay protocol and its use via third-party Software Development Kit (SDK). According to the research, the recently discovered set of vulnerabilities titled "AirBorne" had the potential to enable remote code execution, escape permissions, and leak private data across many different Apple and third-party AirPlay-compatible devices. With well over 2.35 billion active Apple devices globally and tens of millions of third-party products that incorporate the AirPlay SDK, the scope of the problem is enormous. Those wireless-based vulnerabilities pose not only a technical threat but also increasingly an enterprise- and consumer-level security concern.
Understanding AirBorne: What’s at Stake?
AirBorne is the title given to a set of 23 vulnerabilities identified in the AirPlay communication protocol and its related SDK utilised by third-party vendors. Seventeen have been given official CVE designations. The most severe among them permit Remote Code Execution (RCE) with zero or limited user interaction. This provides hackers the ability to penetrate home networks, business environments, and even cars with CarPlay technology onboard.
Types of Vulnerabilities Identified
AirBorne vulnerabilities support a range of attack types, including:
- Zero-Click and One-Click RCE
- Access Control List (ACL) bypass
- User interaction bypass
- Local arbitrary file read
- Sensitive data disclosure
- Man-in-the-middle (MITM) attacks
- Denial of Service (DoS)
Each vulnerability can be used individually or chained together to escalate access and broaden the attack surface.
Remote Code Execution (RCE): Key Attack Scenarios
- MacOS – Zero-Click RCE (CVE-2025-24252 & CVE-2025-24206) These weaknesses enable attackers to run code on a MacOS system without any user action, as long as the AirPlay receiver is enabled and configured to accept connections from anyone on the same network. The threat of wormable malware propagating via corporate or public Wi-Fi networks is especially concerning.
- MacOS – One-Click RCE (CVE-2025-24271 & CVE-2025-24137) If AirPlay is set to "Current User," attackers can exploit these CVEs to deploy malicious code with one click by the user. This raises the level of threat in shared office or home networks.
- AirPlay SDK Devices – Zero-Click RCE (CVE-2025-24132) Third-party speakers and receivers through the AirPlay SDK are particularly susceptible, where exploitation requires no user intervention. Upon compromise, the attackers have the potential to play unauthorised media, turn microphones on, or monitor intimate spaces.
- CarPlay Devices – RCE Over Wi-Fi, Bluetooth, or USB CVE-2025-24132 also affects CarPlay-enabled systems. Under certain circumstances, the perpetrators around can take advantage of predictable Wi-Fi credentials, intercept Bluetooth PINs, or utilise USB connections to take over dashboard features, which may distract drivers or listen in on in-car conversations.
Other Exploits Beyond RCE
AirBorne also opens the door for:
- Sensitive Information Disclosure: Exposing private logs or user metadata over local networks (CVE-2025-24270).
- Local Arbitrary File Access: Letting attackers read restricted files on a device (CVE-2025-24270 group).
- DoS Attacks: Exploiting NULL pointer dereferences or misformatted data to crash processes like the AirPlay receiver or WindowServer, forcing user logouts or system instability (CVE-2025-24129, CVE-2025-24177, etc.).
How the Attack Works: A Technical Breakdown
AirPlay sends on port 7000 via HTTP and RTSP, typically encoded in Apple's own plist (property list) form. Exploits result from incorrect treatment of these plists, especially when skipping type checking or assuming invalid data will be valid. For instance, CVE-2025-24129 illustrates how a broken plist can produce type confusion to crash or execute code based on configuration.
A hacker must be within the same Wi-Fi network as the targeted device. This connection might be through a hacked laptop, public wireless with shared access, or an insecure corporate connection. Once in proximity, the hacker has the ability to use AirBorne bugs to hijack AirPlay-enabled devices. There, bad code can be released to spy, gain long-term network access, or spread control to other devices on the network, perhaps creating a botnet or stealing critical data.
The Espionage Angle
Most third-party AirPlay-compatible devices, including smart speakers, contain built-in microphones. In theory, that leaves the door open for such devices to become eavesdropping tools. While Oligo did not show a functional exploit for the purposes of espionage, the risk suggests the gravity of the situation.
The CarPlay Risk Factor
Besides smart home appliances, vulnerabilities in AirBorne have also been found for Apple CarPlay by Oligo. Those vulnerabilities, when exploited, may enable attackers to take over an automobile's entertainment system. Fortunately, the attacks would need pairing directly through USB or Bluetooth and are much less practical. Even so, it illustrates how networks of connected components remain at risk in various situations, ranging from residences to automobiles.
How to Protect Yourself and Your Organisation
- Immediate Actions:
- Update Devices: Ensure all Apple devices and third-party gadgets are upgraded to the latest software version.
- Disable AirPlay Receiver: If AirPlay is not in use, disable it in system settings.
- Restrict AirPlay Access: Use firewalls to block port 7000 from untrusted IPs.
- Set AirPlay to “Current User” to limit network-based attack.
- Organisational Recommendations:
- Communicate the patch urgency to employees and stakeholders.
- Inventory all AirPlay-enabled hardware, including in meeting rooms and vehicles.
- Isolate vulnerable devices on segmented networks until updated.
Conclusion
The AirBorne vulnerabilities illustrate that even mature systems such as Apple's are not immune from foundational security weaknesses. The extensive deployment of AirPlay across devices, industries, and ecosystems makes these vulnerabilities a systemic threat. Oligo's discovery has served to catalyse immediate response from Apple, but since third-party devices remain vulnerable, responsibility falls to users and organisations to install patches, implement robust configurations, and compartmentalise possible attack surfaces. Effective proactive cybersecurity hygiene, network segmentation, and timely patches are the strongest defences to avoid these kinds of wormable, scalable attacks from becoming large-scale breaches.
References
- https://www.oligo.security/blog/airborne
- https://www.wired.com/story/airborne-airplay-flaws/
- https://thehackernews.com/2025/05/wormable-airplay-flaws-enable-zero.html
- https://www.securityweek.com/airplay-vulnerabilities-expose-apple-devices-to-zero-click-takeover/
- https://www.pcmag.com/news/airborne-flaw-exposes-airplay-devices-to-hacking-how-to-protect-yourself
- https://cyberguy.com/security/hackers-breaking-into-apple-devices-through-airplay/
