
#FactCheck - Debunking Manipulated Photos of Smiling Secret Service Agents During Trump Assassination Attempt
Executive Summary:
Viral pictures featuring US Secret Service agents smiling while protecting former President Donald Trump during a planned attempt to kill him in Pittsburgh have been clarified as photoshopped pictures. The pictures making the rounds on social media were produced by AI-manipulated tools. The original image shows no smiling agents found on several websites. The event happened with Thomas Mathew Crooks firing bullets at Trump at an event in Butler, PA on July 13, 2024. During the incident one was deceased and two were critically injured. The Secret Service stopped the shooter, and circulating photos in which smiles were faked have stirred up suspicion. The verification of the face-manipulated image was debunked by the CyberPeace Research Team.

Claims:
Viral photos allegedly show United States Secret Service agents smiling while rushing to protect former President Donald Trump during an attempted assassination in Pittsburgh, Pennsylvania.


Fact Check:
Upon receiving the posts, we searched for any credible source that supports the claim made, we found several articles and images of the incident but in those the images were different.

This image was published by CNN news media, in this image we can see the US Secret Service protecting Donald Trump but not smiling. We then checked for AI Manipulation in the image using the AI Image Detection tool, True Media.


We then checked with another AI Image detection tool named, contentatscale AI image detection, which also found it to be AI Manipulated.

Comparison of both photos:

Hence, upon lack of credible sources and detection of AI Manipulation concluded that the image is fake and misleading.
Conclusion:
The viral photos claiming to show Secret Service agents smiling when protecting former President Donald Trump during an assassination attempt have been proven to be digitally manipulated. The original image found on CNN Media shows no agents smiling. The spread of these altered photos resulted in misinformation. The CyberPeace Research Team's investigation and comparison of the original and manipulated images confirm that the viral claims are false.
- Claim: Viral photos allegedly show United States Secret Service agents smiling while rushing to protect former President Donald Trump during an attempted assassination in Pittsburgh, Pennsylvania.
- Claimed on: X, Thread
- Fact Check: Fake & Misleading

Related Blogs

Executive Summary:
BrazenBamboo’s DEEPDATA malware represents a new wave of advanced cyber espionage tools, exploiting a zero-day vulnerability in Fortinet FortiClient to extract VPN credentials and sensitive data through fileless malware techniques and secure C2 communications. With its modular design, DEEPDATA targets browsers, messaging apps, and password stores, while leveraging reflective DLL injection and encrypted DNS to evade detection. Cross-platform compatibility with tools like DEEPPOST and LightSpy highlights a coordinated development effort, enhancing its espionage capabilities. To mitigate such threats, organizations must enforce network segmentation, deploy advanced monitoring tools, patch vulnerabilities promptly, and implement robust endpoint protection. Vendors are urged to adopt security-by-design practices and incentivize vulnerability reporting, as vigilance and proactive planning are critical to combating this sophisticated threat landscape.
Introduction
The increased use of zero-day vulnerabilities by more complex threat actors reinforces the importance of more developed countermeasures. One of the threat actors identified is BrazenBamboo uses a zero-day vulnerability in Fortinet FortiClient for Windows through the DEEPDATA advanced malware framework. This research explores technical details about DEEPDATA, the tricks used in its operations, and its other effects.
Technical Findings
1. Vulnerability Exploitation Mechanism
The vulnerability in Fortinet’s FortiClient lies in its failure to securely handle sensitive information in memory. DEEPDATA capitalises on this flaw via a specialised plugin, which:
- Accesses the VPN client’s process memory.
- Extracts unencrypted VPN credentials from memory, bypassing typical security protections.
- Transfers credentials to a remote C2 server via encrypted communication channels.
2. Modular Architecture
DEEPDATA exhibits a highly modular design, with its core components comprising:
- Loader Module (data.dll): Decrypts and executes other payloads.
- Orchestrator Module (frame.dll): Manages the execution of multiple plugins.
- FortiClient Plugin: Specifically designed to target Fortinet’s VPN client.
Each plugin operates independently, allowing flexibility in attack strategies depending on the target system.
3. Command-and-Control (C2) Communication
DEEPDATA establishes secure channels to its C2 infrastructure using WebSocket and HTTPS protocols, enabling stealthy exfiltration of harvested data. Technical analysis of network traffic revealed:
- Dynamic IP switching for C2 servers to evade detection.
- Use of Domain Fronting, hiding C2 communication within legitimate HTTPS traffic.
- Time-based communication intervals to minimise anomalies in network behavior.
4. Advanced Credential Harvesting Techniques
Beyond VPN credentials, DEEPDATA is capable of:
- Dumping password stores from popular browsers, such as Chrome, Firefox, and Edge.
- Extracting application-level credentials from messaging apps like WhatsApp, Telegram, and Skype.
- Intercepting credentials stored in local databases used by apps like KeePass and Microsoft Outlook.
5. Persistence Mechanisms
To maintain long-term access, DEEPDATA employs sophisticated persistence techniques:
- Registry-based persistence: Modifies Windows registry keys to reload itself upon system reboot.
- DLL Hijacking: Substitutes legitimate DLLs with malicious ones to execute during normal application operations.
- Scheduled Tasks and Services: Configures scheduled tasks to periodically execute the malware, ensuring continuous operation even if detected and partially removed.
Additional Tools in BrazenBamboo’s Arsenal
1. DEEPPOST
A complementary tool used for data exfiltration, DEEPPOST facilitates the transfer of sensitive files, including system logs, captured credentials, and recorded user activities, to remote endpoints.
2. LightSpy Variants
- The Windows variant includes a lightweight installer that downloads orchestrators and plugins, expanding espionage capabilities across platforms.
- Shellcode-based execution ensures that LightSpy’s payload operates entirely in memory, minimising artifacts on the disk.
3. Cross-Platform Overlaps
BrazenBamboo’s shared codebase across DEEPDATA, DEEPPOST, and LightSpy points to a centralised development effort, possibly linked to a Digital Quartermaster framework. This shared ecosystem enhances their ability to operate efficiently across macOS, iOS, and Windows systems.
Notable Attack Techniques
1. Memory Injection and Data Extraction
Using Reflective DLL Injection, DEEPDATA injects itself into legitimate processes, avoiding detection by traditional antivirus solutions.
- Memory Scraping: Captures credentials and sensitive information in real-time.
- Volatile Data Extraction: Extracts transient data that only exists in memory during specific application states.
2. Fileless Malware Techniques
DEEPDATA leverages fileless infection methods, where its payload operates exclusively in memory, leaving minimal traces on the system. This complicates post-incident forensic investigations.
3. Network Layer Evasion
By utilising encrypted DNS queries and certificate pinning, DEEPDATA ensures that network-level defenses like intrusion detection systems (IDS) and firewalls are ineffective in blocking its communications.
Recommendations
1. For Organisations
- Apply Network Segmentation: Isolate VPN servers from critical assets.
- Enhance Monitoring Tools: Deploy behavioral analysis tools that detect anomalous processes and memory scraping activities.
- Regularly Update and Patch Software: Although Fortinet has yet to patch this vulnerability, organisations must remain vigilant and apply fixes as soon as they are released.
2. For Security Teams
- Harden Endpoint Protections: Implement tools like Memory Integrity Protection to prevent unauthorised memory access.
- Use Network Sandboxing: Monitor and analyse outgoing network traffic for unusual behaviors.
- Threat Hunting: Proactively search for indicators of compromise (IOCs) such as unauthorised DLLs (data.dll, frame.dll) or C2 communications over non-standard intervals.
3. For Vendors
- Implement Security by Design: Adopt advanced memory protection mechanisms to prevent credential leakage.
- Bug Bounty Programs: Encourage researchers to report vulnerabilities, accelerating patch development.
Conclusion
DEEPDATA is a form of cyber espionage and represents the next generation of tools that are more advanced and tunned for stealth, modularity and persistence. While Brazen Bamboo is in the process of fine-tuning its strategies, the organisations and vendors have to be more careful and be ready to respond to these tricks. The continuous updating, the ability to detect the threats and a proper plan on how to deal with incidents are crucial in combating the attacks.
References:
Overview of the Advisory
On 18 November 2025, the Ministry of Information and Broadcasting (I&B) published an Advisory that addresses all of the private satellite television channels in India. The advisory is one of the critical institutional interventions to the broadcast of sensitive content regarding recent security incidents concerning the blast at the Red Fort on November 10th, 2025. This advisory came after the Ministry noticed that some news channels have been broadcasting content related to alleged persons involved in Red Fort blasts, justifying their acts of violence, as well as information/video on explosive material. Broadcasting like this at this critical situation may inadvertently encourage or incite violence, disrupt public order, and pose risks to national security.
Key Instructions under the Advisory
The advisory provides certain guidelines to the TV channels to ensure strict compliance with the Programming and Advertising Code under the Cable Television Networks (Regulation) Act, 1995. The television channels are advised to exercise the highest level of discretion and sensitivity possible in reporting on issues involving alleged perpetrators of violence, and especially when reporting on matters involving the justification of acts of violence or providing instructional media on making explosive materials. The fundamental focus is to be very strict in following the Programme and Advertising Code as stipulated in the Cable Television Network Rules. In particular, broadcasters should not make programming that:
- Contain anything obscene, defamatory, deliberately false, or suggestive innuendos and half-truths.
- Likely to encourage or incite violence, contain anything against the maintenance of law and order, or promote an anti-national attitude.
- Contain anything that affects the integrity of the Nation.
- Could aid, abet or promote unlawful activities.
Responsible Reporting Framework
The advisory does not constitute outright censorship but instead a self-regulatory system that depends on the discretion and sensitivity of the TV channels focused on differentiating between broadcasting legitimate news and the content that crosses the threshold from information dissemination to incitement.
Why This Advisory is Important in a Digital Age
With the modern media systems, there has been an erosion of the line between the journalism of the traditional broadcasting medium and digital virality. The contents of television are no longer limited to the scheduled programs or cable channels of distribution. The contents of a single news piece, especially that of dramatic or contentious nature, can be ripped off, revised and repackaged on social media networks within minutes of airing- often without the context, editorial discretion or timing indicators.
This effect makes sensitive content have a multiplier effect. The short news item about a suspect justifying violence or containing bombs can be viewed by millions on YouTube, WhatsApp, Twitter/X, Facebook, by spreading organically and being amplified by an algorithm. Studies have shown that misinformation and sensational reporting are much faster to circulate compared to factual corrections- a fact that has been noticed in the recent past during conflicts and crisis cases in India and other parts of the world.
Vulnerabilities of Information Ecosystems
- The advisory is created in a definite information setting that is characterised by:
- Rapid Viral Mechanism: Content spreads faster than the process of verification.
- Algorithmic-driven amplification: Platform mechanism boosts emotionally charged content.
- Coordinated amplification networks: Organised groups are there to make these posts, videos viral, to set a narrative for the general public.
- Deepfake and synthetic media risks: Original broadcasts can be manipulated and reposted with false attribution.
Interconnection with Cybersecurity and National Security
Verified or sensationalised reporting of security incidents poses certain weaknesses:
- Trust Erosion: Trust is broken when the masses observe broadcasters in the air giving unverified claims or emotional accounts as facts. This is even to security agencies, law enforcement and government institutions themselves. The lack of trust towards the official information gives rise to information gaps, which are occupied by rumours, conspiracy theories, and enemy tales.
- Cognitive Fragmentation: Misinformation develops multiple versions of the truth among the people. The narratives given to citizens vary according to the sources of the media that they listen to or read. This disintegration complicates organising the collective response of the society an actual security threat because the populations can be organised around misguided stories and not the correct data.
- Radicalisation Pipeline: People who are interested in finding ideological backgrounds to violent action might get exposed to media-created materials that have been carefully distorted to evidence justifications of terrorism as a valid political or religious stand.
How Social Instability Is Exploited in Cyber Operations and Influence Campaigns
Misinformation causes exploitable vulnerability in three phases.
- First, conflicting unverified accounts disintegrate the information environment-populations are presented with conflicting versions of events by various media sources.
- Second, institutional trust in media and security agencies is shaken by exposure to subsequently rectified false information, resulting in an information vacuum.
- Third, in such a distrusted and puzzled setting, the population would be susceptible to organised manipulation by malicious agents.
- Sensationalised broadcasting gives opponents assets of content, narrative frameworks, and information gaps that they can use to promote destabilisation movements. These mechanisms of exploitation are directly opposed by responsible broadcasting.
Media Literacy and Audience Responsibility
Structural Information Vulnerabilities-
A major part of the Indian population is structurally disadvantaged in information access:
- Language barriers: Infrastructure in the field of fact-checking is still highly centralised in English and Hindi, as vernacular-language misinformation goes viral in Tamil, Telugu, Marathi, Punjabi, and others.
- Digital literacy gaps: It is estimated that there are about 40 million people in India who have been trained on digital literacy, but more than 900 million Indians access digital content with different degrees of ability to critically evaluate the content.
- Divides between rural and urban people: Rural citizens and less affluent people experience more difficulty with access to verification tools and media literacy resources.
- Algorithmic capture: social media works to maximise engagement over accuracy, and actively encourages content that is emotionally inflammatory or divisive to its users, according to their history of engagement.
Conclusion
The advisory of the Ministry of Information and Broadcasting is an acknowledgment of the fact that media accountability is a part of state security in the information era. It states the principles of responsible reporting without interference in editorial autonomy, a balance that various stakeholders should uphold. Implementation of the advisory needs to be done in concert with broadcasters, platforms, civil society, government and educational institutions. Information integrity cannot be handled by just a single player. Without media literacy resources, citizens are unable to be responsible in their evaluation of information. Without open and fast communication with the media stakeholders, government agencies are unable to combat misinformation.
The recommendations include collaborative governance, i.e., institutional forms in which media self-regulation, technological protection, user empowerment, and policy frameworks collaborate and do not compete. The successful deployment of measures will decide whether India can continue to have open and free media without compromising on information integrity that is sufficient to provide national security, democratic governance and social stability during the period of high-speed information flow, algorithmic amplification, and information warfare actions.
References
https://mib.gov.in/sites/default/files/2025-11/advisory-18.11.2025.pdf
Executive Summary
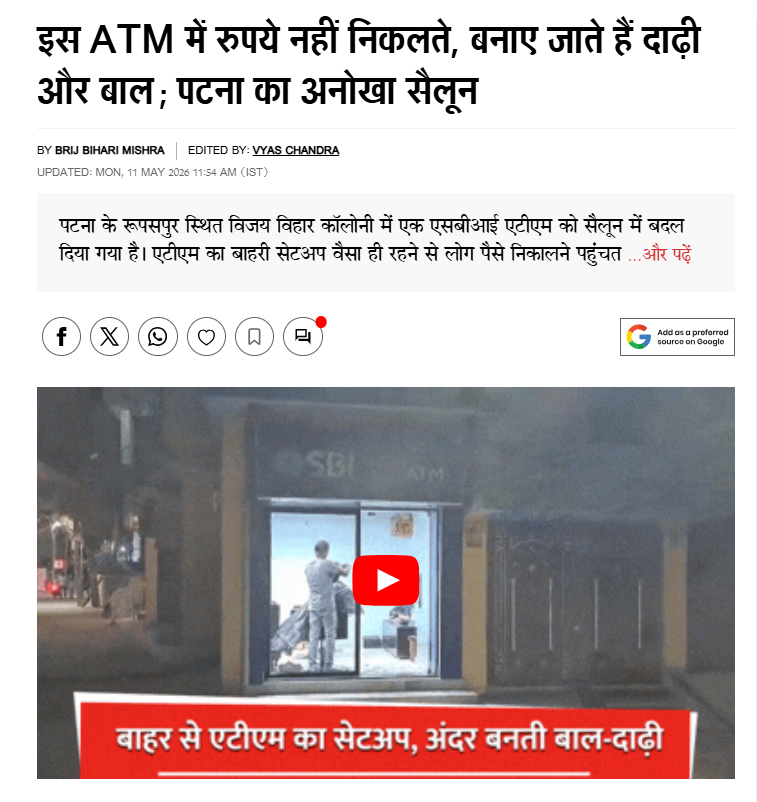
A video is going viral on social media claiming that a salon has been opened inside a State Bank of India (SBI) ATM in Bihar. The video is also being used by some users to take political jibes at the central and state governments led by the Bharatiya Janata Party (BJP). However, the CyberPeace Research Wing’s research has found that this claim is misleading. The location shown in the viral video was earlier an SBI ATM, which had been shut down around six months ago. After the bank discontinued its operations at the site, the ATM machine and other equipment were removed. However, the external structure of the ATM cabin and the SBI signage were not removed at that time. After the premises were vacated, the property owner rented out the space to a salon operator. Since the SBI board and branding were still visible on the structure, the video created confusion and went viral with misleading claims.
Following the circulation of the video, the bank later removed its signage from the location and also cleared all remaining SBI branding from the structure. Our research also found that the bank had removed the ATM machine and equipment months earlier, but the cabin structure and SBI board were left behind. After that, the space was rented out for commercial use as a salon. In this context, it would be incorrect to claim that a salon was opened inside an active SBI ATM.
Claim
A Facebook user ‘Soumitra Roy’ shared a video on 11 May 2026 claiming:
“Someone has opened a barber shop inside an SBI ATM in Bihar. The BJP’s double-engine government has developed Bihar so much that loan EMIs can now be deducted directly inside ATMs. This is Modi’s masterstroke.”
- https://www.facebook.com/reel/980962511535926
- https://perma.cc/WTY2-WEQQ

Fact Check
To verify the viral claim, a keyword search based on the video was conducted. Several media reports were found, which clarified the full context of the incident. A report uploaded on the YouTube channel ‘Live Cities’ on 12 May 2026 stated that a salon was running at a former ATM location in Danapur, Bihar. The bank had already vacated the premises about six months earlier, but its signage had not been removed. The report also includes an interview with the property owner, who confirmed that the bank had removed its ATM machine and equipment six months ago and later the space was rented out to a salon operator.

The viral video was also found on the Jagran website in a news report dated 11 May 2026. The report states that an SBI ATM previously existed at the location. The bank had removed the ATM machine due to operational reasons but left behind the external structure and signage. Later, the space was rented out to a salon operator, who began running his business from the same setup.
Conclusion
Our research found that the viral post is misleading. It is incorrect to claim that a salon was opened inside an SBI ATM. The truth is that the bank had shut down the ATM at this location around six months ago and removed all machines and equipment. After that, the premises were rented out to a salon operator, which led to confusion due to the presence of old SBI signage.

