
#FactCheck-RBI's Alleged Guidelines on Ink Colour for Cheque Writing
Executive Summary:
A viral message is circulating claiming the Reserve Bank of India (RBI) has banned the use of black ink for writing cheques. This information is incorrect. The RBI has not issued any such directive, and cheques written in black ink remain valid and acceptable.

Claim:
The Reserve Bank of India (RBI) has issued new guidelines prohibiting using black ink for writing cheques. As per the claimed directive, cheques must now be written exclusively in blue or green ink.

Fact Check:
Upon thorough verification, it has been confirmed that the claim regarding the Reserve Bank of India (RBI) issuing a directive banning the use of black ink for writing cheques is entirely false. No such notification, guideline, or instruction has been released by the RBI in this regard. Cheques written in black ink remain valid, and the public is advised to disregard such unverified messages and rely only on official communications for accurate information.
As stated by the Press Information Bureau (PIB), this claim is false The Reserve Bank of India has not prescribed specific ink colors to be used for writing cheques. There is a mention of the color of ink to be used in point number 8, which discusses the care customers should take while writing cheques.


Conclusion:
The claim that the Reserve Bank of India has banned the use of black ink for writing cheques is completely false. No such directive, rule, or guideline has been issued by the RBI. Cheques written in black ink are valid and acceptable. The RBI has not prescribed any specific ink color for writing cheques, and the public is advised to disregard unverified messages. While general precautions for filling out cheques are mentioned in RBI advisories, there is no restriction on the color of the ink. Always refer to official sources for accurate information.
- Claim: The new RBI ink guidelines are mandatory from a specified date.
- Claimed On: Social Media
- Fact Check: False and Misleading

Related Blogs

Introduction
Cyber financial offences in India have experienced an alarming surge both in terms of frequency and complexity. Be it phishing attacks or organised fraud syndicates, the nation has been facing a spurt in online financial threats, which leave the victims at their mercy because of procedural lags on the part of law enforcement agencies. To counter this, the Government of India has stepped up measures to create a Cyber-Secure Bharat, focusing on speedy resolution, accountability, and digital empowerment. A key move in this direction is the introduction of the e-Zero FIR initiative, brought forth by the Ministry of Home Affairs (MHA) with Union Home Minister Amit Shah at the helm. This newly developed digital-first system is expected to revolutionise the way cyber financial crimes, particularly those that result in high monetary losses, are handled and investigated.
What Is the e-Zero FIR Initiative?
The e-Zero FIR program is a technology-based platform that enables the automated registration of Zero FIRs for value cyber financial crimes. Led by the Indian Cybercrime Coordination Centre (I4C), Ministry of Home Affairs, the programme is now piloted in Delhi and aims to fill a pressing lacuna: the time lag involved in transitioning cybercrime complaints to First Information Reports (FIRs).
Complaints of financial frauds worth more than ₹10 lakh, reported through the National Cybercrime Reporting Portal (NCRP) or helpline number 1930, will be automatically turned into e-Zero FIRs under this scheme. Such electronic FIRs are directed to the e-Crime Police Station in Delhi, regardless of jurisdiction, and then relayed to the corresponding territorial cybercrime unit. Complainants can visit the cybercrime Police Station within 3 days and get the Zero FIR converted into a regular FIR.
Key Features of the Initiative
- Pilot Implementation in Delhi
Launched as a pilot project in Delhi, it will later serve as the first use case for the national rollout. The success of the pilot will determine its implementation in other states and Union Territories.
- Seamless Digital Integration
The project provides strong back-end integration between:
- NCRP (National Cybercrime Reporting Portal)
- e-FIR System (Delhi Police)
- CCTNS (Crime and Criminal Tracking Network & Systems – NCRB)
This integrated model enables complaints to pass smoothly between platforms and agencies.
- Zero FIR Auto-Registration and Routing
Now, for complaints lodged through 1930 or the National Cyber Crime Reporting Portal related to financial losses exceeding the threshold of ₹10 lakh, the system will automatically register a Zero FIR to the e-Crime Police Station of Delhi and then route it to the concerned territorial cybercrime police station, triggering immediate case processing.
- Victim-Centric Conversion Mechanism
Complainants are given 3 days from the time of filing to physically report to the police station and transform the e-Zero FIR into a conventional regular FIR under Section 173 (1) and 1(ii) of the newly enacted Bhartiya Nagrik Suraksha Sanhita (BNSS). This ensures legal redress is quicker and easier.
Impact and Significance: The CyberPeace View
The e-Zero FIR system is a significant change in India's cybercrime enforcement, offering quicker response times and improved recovery opportunities. Cyber fraud reported within the "golden hour" can boost recovery levels of financial fraud. The system also eliminates jurisdictional barriers and procedural bottlenecks, making it more victim-friendly. Union Home Minister Amit Shah emphasised the initiative's alignment with Prime Minister Narendra Modi's vision of a digitally resilient India. The system is a scalable national model of tech-based policing supported by organised digital workflows. The initiative allows for real-time analysis of fraud graphs and detection of fraud syndicates through identification and device-based clustering. This is a step towards more automated, context-aware cyber policing, focusing on AI, identity graphs, and velocity to prevent crimes. The system is a step towards a next-generation cyber law enforcement strategy, focusing on AI, identity graphs, and velocity.
Conclusion
The roll-out of the e-Zero FIR program is a turning point in India's battle against cybercrime. By marrying automation with inter-agency coordination and easy-to-use mechanisms, the government has eradicated one of the major stumbling blocks for victims, the delay in taking legal action. Though its pilot phase targets high-value financial frauds in Delhi, its potential for having a countrywide impact is vast. With digital transactions on the upswing and frauds getting more cunning, efforts like these are the key to making a safe, responsive, and victim-centric cyber environment. CyberPeace commends and welcomes this important move towards establishing a Cyber-Secure Bharat, wherein all citizens can make digital transactions with confidence.
References
- https://www.pib.gov.in/PressReleasePage.aspx?PRID=2129715
- https://www.mha.gov.in/en
- https://cybercrime.gov.in/
- https://www.ncrb.gov.in/
- https://economictimes.indiatimes.com/wealth/save/new-e-zero-fir-govt-launches-pilot-for-swift-action-against-cybercrimes-how-it-can-help-you/articleshow/121314437.cms?from=mdr
Executive Summary
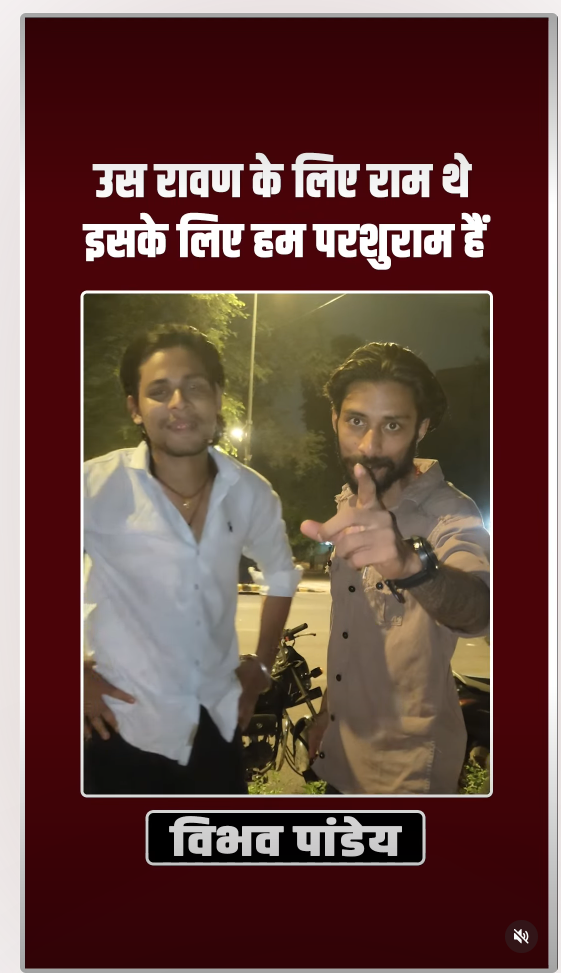
A video of Swatantra Bhardwaj is being shared on social media. Another man can also be seen with Bhardwaj in the video. Swatantra Bhardwaj came into the spotlight following an alleged assault involving the father of a protester during a protest by the Cockroach Janta Party at Jantar Mantar. Social media posts claim that the video was recorded immediately after his release from jail and shows him openly threatening people. CyberPeace Research Wing’s Research found the viral claim to be false. Our Research revealed that the video being shared on social media is old. Swatantra Bhardwaj was released from jail on September 17, while our Research found that the video has been available online since June. Therefore, the claim that the video was recorded immediately after Bhardwaj’s release from jail is misleading.
Claim:
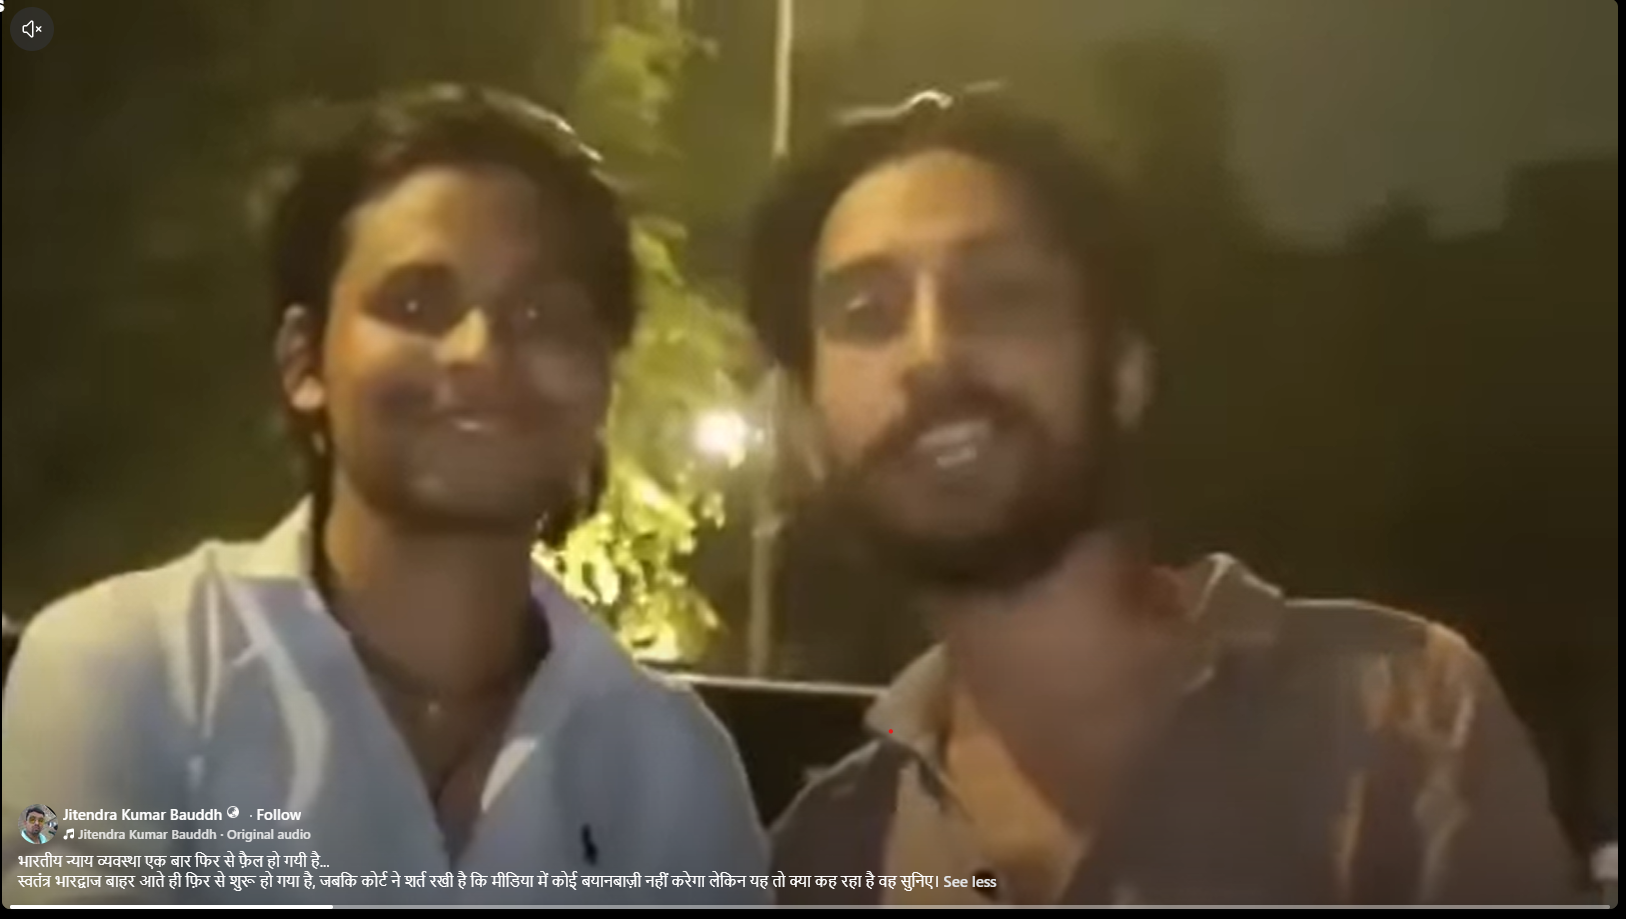
A Facebook user shared the viral video on September 17, 2026, with the caption: “The Indian judicial system has failed once again... Swatantra Bhardwaj has started again immediately after coming out, even though the court has imposed a condition that he will not make any statements to the media. But listen to what he is saying.” The post link, archive link, and screenshot are provided below.
https://www.facebook.com/reel/1349048917301713
Fact Check
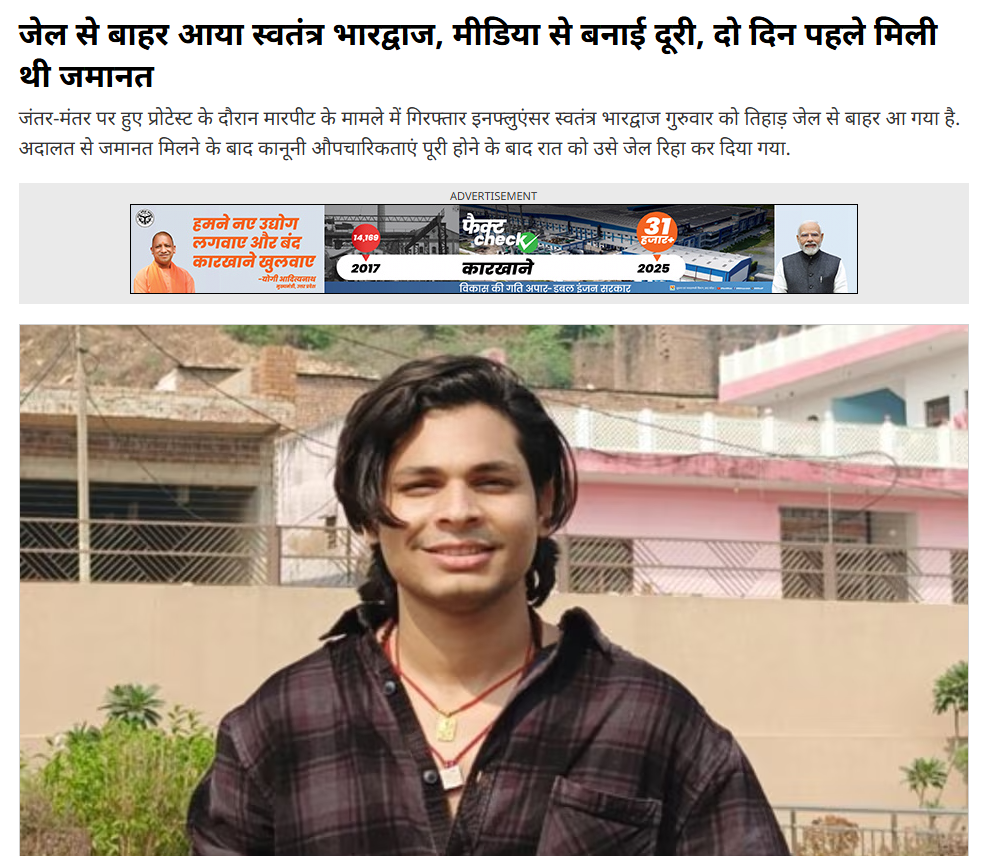
To verify the date of Swatantra Bhardwaj’s release from jail, we searched Google using relevant keywords. During the search, we found a report published by Aaj Tak on September 18, 2026. According to the report, social media influencer Swatantra Bhardwaj, who came into the spotlight following an alleged assault during a protest at Jantar Mantar, was released from Delhi’s Tihar Jail on September 17, 2026, after being granted bail by the court and completing the necessary legal formalities. Soon after walking out of the main gate of the jail, he ran towards a taxi and left without speaking to the media personnel present there. The post link and screenshot are provided below.
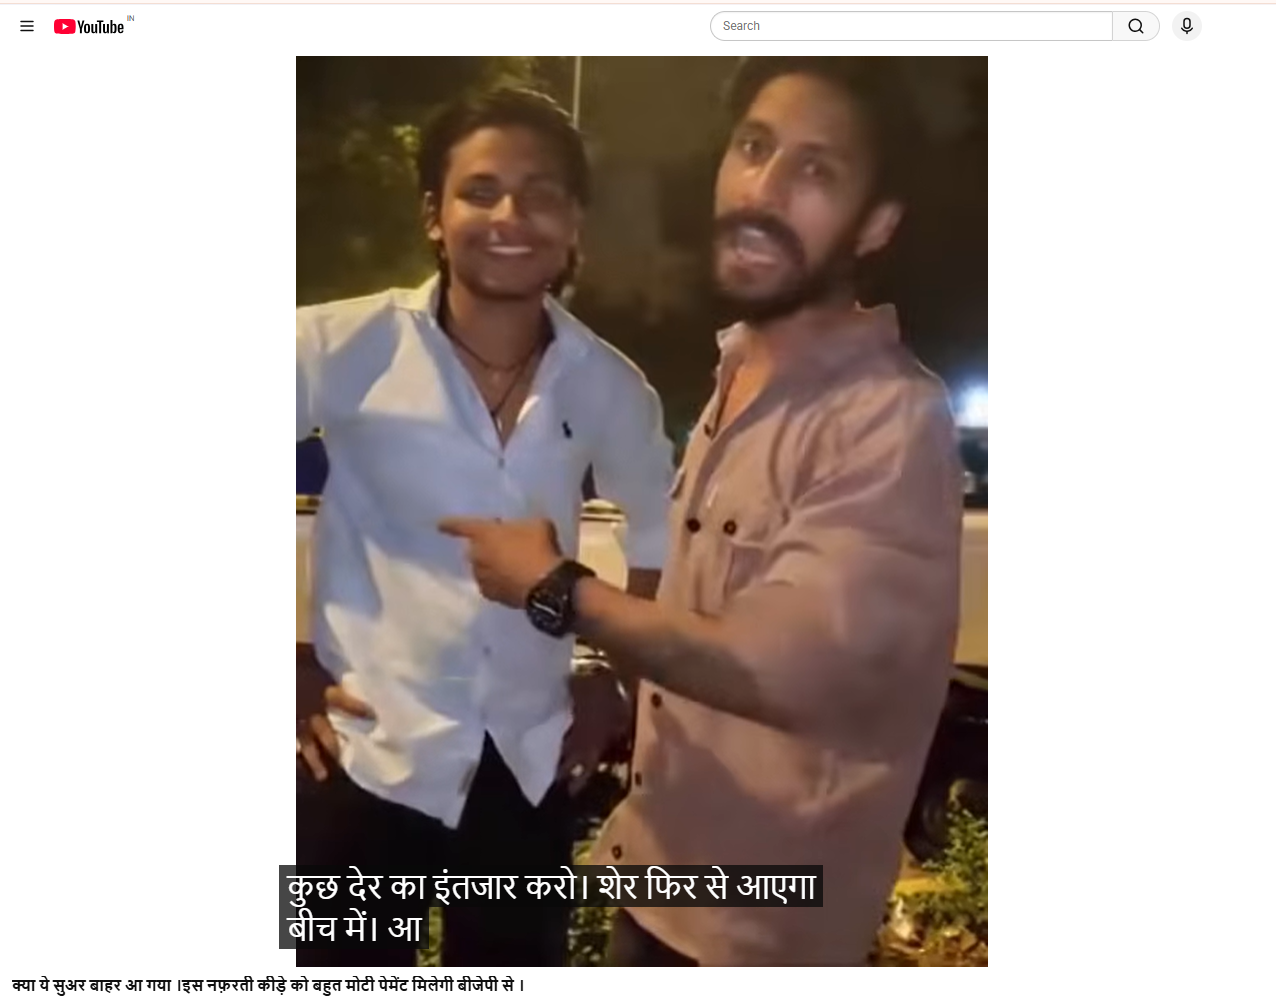
To verify the authenticity of the viral claim, we conducted a reverse image search of the keyframes from the video. During the search, we found the same video on a YouTube channel, where it was published on September 7, 2026. Meanwhile, the report mentioned above clearly states that Swatantra Bhardwaj was released from Delhi’s Tihar Jail on September 17, 2026. The report link and screenshot are provided below.
https://www.youtube.com/watch?v=-3V0pwJbpwg
At the end of our Research, we found another version of the same video, which was uploaded by a person identified as Vaibhav Kumar on June 26, 2026. The post link and screenshot are provided below.
https://www.instagram.com/reels/DaBs7Q-T8xc/
Conclusion
Our Research found that the video being shared on social media is old. Swatantra Bhardwaj was released from jail on September 17, while our Research found that the video had already been available online since June. Therefore, the claim that the video was recorded immediately after Bhardwaj’s release from jail is misleading.

Introduction
Personalised advertisements deploy a mechanism that derives from the collection of the user’s data. Although it allows for a more tailored user experience, one cannot ignore the method through which this is achieved. Recently, as per a report by the Indian Express on 13th November 2024, Meta has come up with a less personalised ad option on Facebook and Instagram for its users in the European Union (EU). This was done due to the incompatibility of their previous ad offer with the EU’s Digital Markets Act (DMA).
Relevant Legislation
In October 2023, Meta came up with a “Pay or Consent” option for their users in the EU. It gave the users two options: either to pay a monthly subscription fee to avail of the ad-free usage variant of Facebook and Instagram, or to give consent to see personalised ads based on the user’s data. This consent model was introduced in their attempts to comply with the EU’s DMA. However, this was found to be incompatible with the said mandate, according to the EU regulators, as they believed that the users should not only have the option to consent to ads but also have access to less personalised but equivalent alternatives. It is this decision that pushed Meta to come up with less personalised ad options for users in the EU. The less-personalised ad option claims to rely on limited data and show ads that are only based on the context of what is being viewed i.e. during a Facebook or Instagram session requiring a minimum set of data points such as location, age, gender, and the user’s engagement with the ads. However, choosing this option also allows for such ads to be less skippable.
The EU’s Digital Markets Act came into force on November 1, 2022. The purpose was to make the digital marketing sector fairer and in doing so, identify what they consider to be “Gatekeepers” (core platform services such as messenger services, search engines, and app stores) and a list of do’s and don’ts for them. One of them, applicable to the case mentioned above, is the effective consent required by the user in case the gatekeeper decides to target advertisements enabled by tracking the users' activity outside the gatekeeper's core platform services.
The Indian Context
Although no such issues have been raised in India yet, it is imperative to know that in the Indian context, the DPDP (Digital Personal Data Protection) Act 2023 governs personal data regulation. This includes rules for Data Fiduciaries (those who, alone or in partnership with others, determine the means and purpose of processing personal data), the Data Principal (those who give data), Consent Managers, and even rules regarding processing data of children.
CyberPeace Recommendations:
At the level of the user, one can take steps to ensure limited collection of personal data by following the mentioned steps:
- Review Privacy Settings- Reviewing Privacy settings for one’s online accounts and devices is a healthy practice to avoid giving unnecessary information to third-party applications.
- Private Browsing- Browsing through private mode or incognito is encouraged, as it prevents websites from tracking your activity and personal data.
- Using Ad-blockers- Certain websites have a user option to block ads when the user first visits their page. Availing of this prevents spam advertisements from the respective websites.
- Using VPN- Using Virtual Private Networks enables users to hide their IP address and their data to be encrypted, preventing third-party actors from tracking the users' online activities
- Other steps include clearing cookies and cache data and using the location-sharing feature with care.
Conclusion
Meta’s compliance with the EU’s DMA signals that social media platforms cannot circumnavigate their way around rules. Balancing the services provided while respecting user privacy is of the utmost importance. The EU has set precedence for a system that respects this and can be used as an example to help set guidelines for how other countries can continue to deal with similar issues and set standards accordingly.
References
- https://indianexpress.com/article/technology/tech-news-technology/meta-less-personalised-ads-eu-regulatory-demands-9667266/
- https://rainmaker.co.in/blog/view/the-price-of-personalization-how-targeted-advertising-breaches-data-privacy-and-challenges-the-gdprs-shield
- https://www.infosecurity-magazine.com/magazine-features/fines-data-protection-violations/
- https://www.forbes.com/councils/forbestechcouncil/2023/09/01/the-landscape-of-personalized-advertising-efficiency-versus-privacy/
- https://iapp.org/news/a/pay-or-consent-personalized-ads-the-rules-and-whats-next
- https://economictimes.indiatimes.com/news/how-to/how-to-safeguard-privacy-in-the-era-of-personalised-ads/articleshow/102748711.cms?from=mdr
- https://www.business-standard.com/technology/tech-news/facebook-instagram-users-in-europe-can-opt-for-less-personalised-ads-124111201558_1.html
- https://digital-markets-act.ec.europa.eu/about-dma_en
