
#FactCheck - AI-Generated Clip of Lion Carrying Woman Shared as Real Incident
Executive Summary
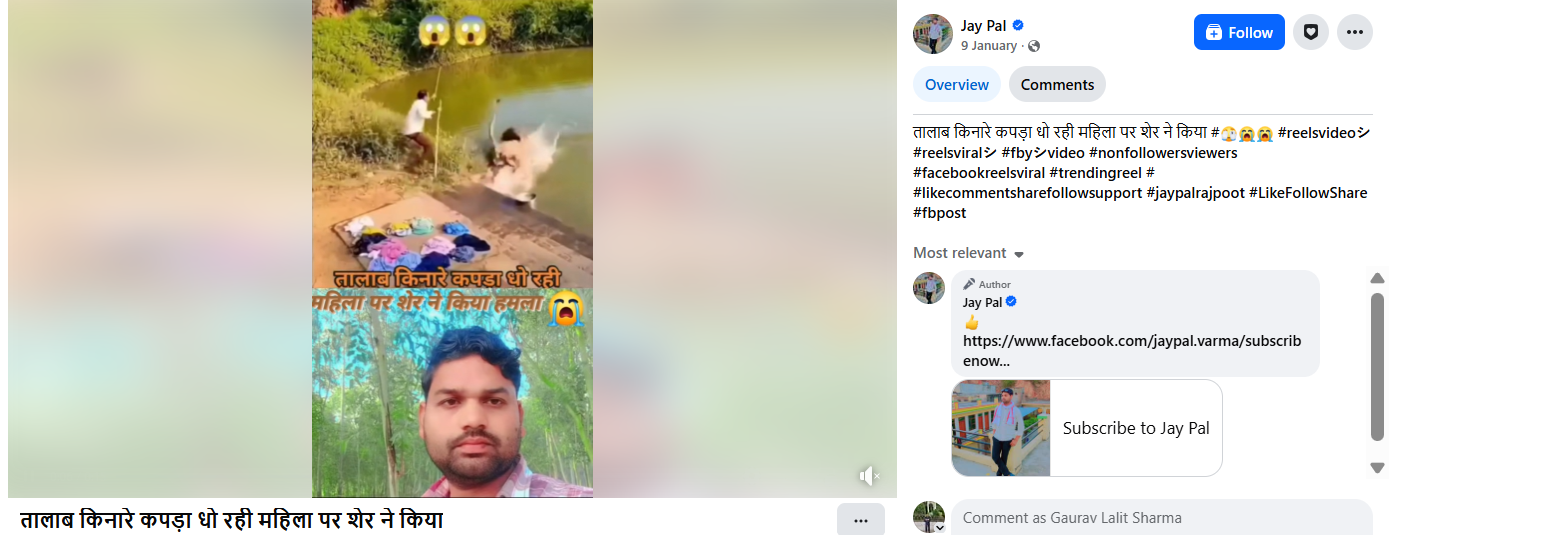
A video circulating on social media shows a lion carrying away a woman who was washing clothes near a pond. Users are sharing the clip claiming it depicts a real incident. However, research by CyberPeace found the viral claim to be false. The research revealed that the video is not real but AI-generated.
Claim
A user on Facebook shared the viral video claiming that a lion attacked and carried away a woman from a pond while she was washing clothes. The link to the post and its archived version are provided below
Fact Check:
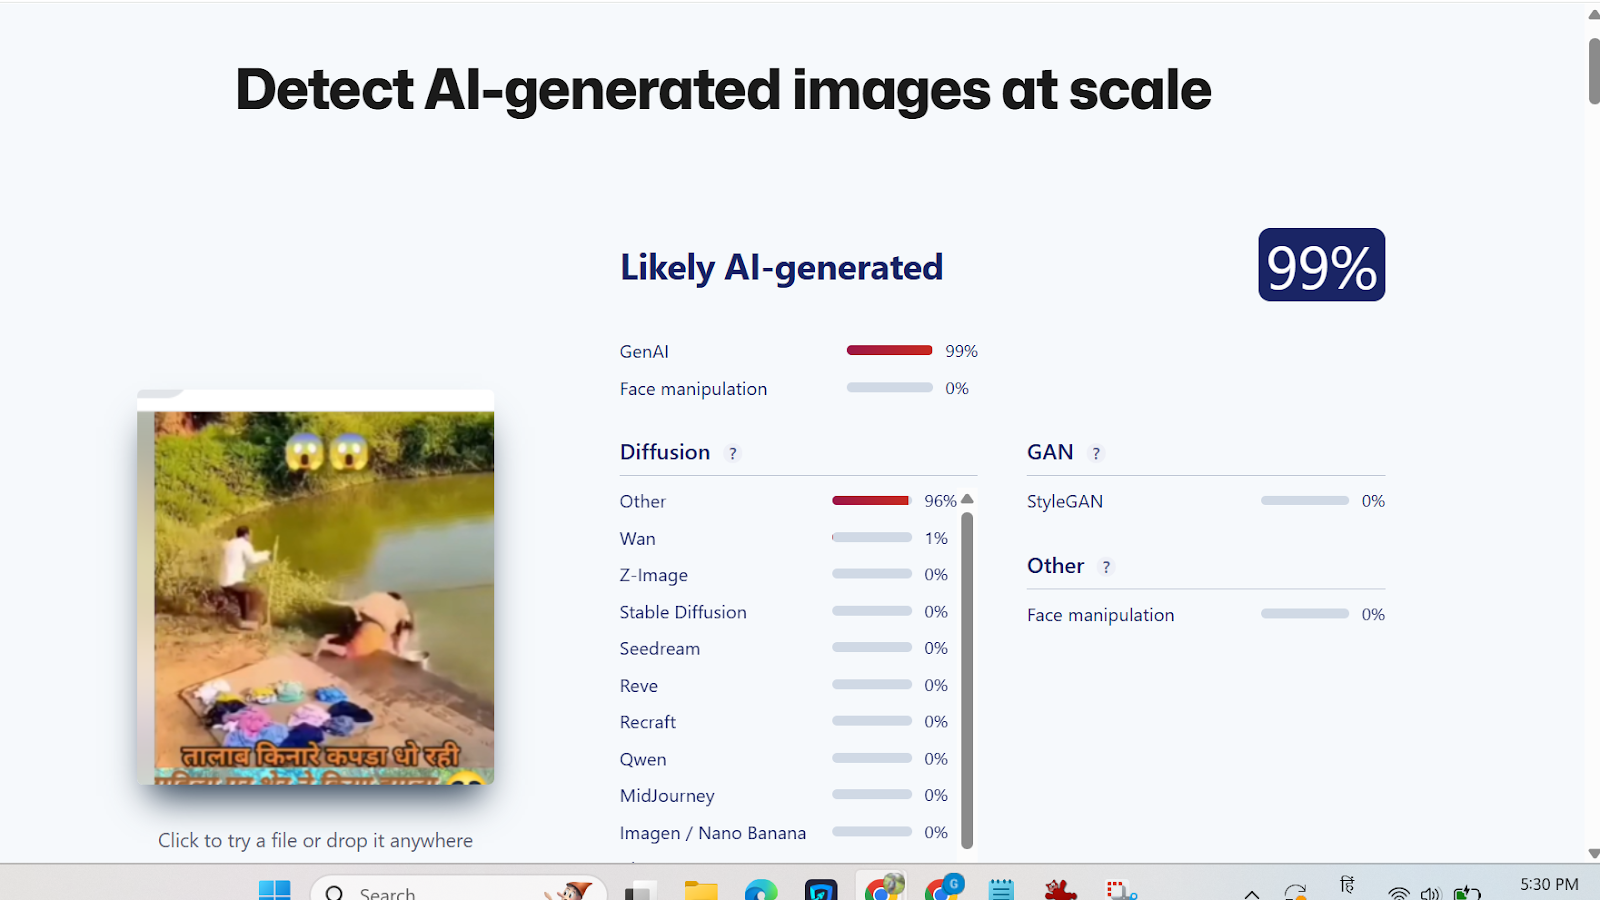
Upon closely examining the viral clip, we noticed several visual inconsistencies that raised suspicion about its authenticity. The video was then analyzed using the AI-detection tool Sightengine. According to the analysis results, the viral video was identified as AI-generated.
Conclusion
The research confirms that the viral video does not depict a real incident. The clip is digitally created using artificial intelligence and is being falsely shared as a genuine event.

Related Blogs

Introduction:
With the rapid advancement in technologies, vehicles are also being transformed into moving data centre. There is an introduction of connectivity, driver assistance systems, advanced software systems, automated systems and other modern technologies are being deployed to make the experience of users more advanced and joyful. Software plays an important role in the overall functionality and convenience of the vehicle. For example, Advanced technologies like keyless entry and voice assistance, censor cameras and communication technologies are being incorporated into modern vehicles. Addressing the cyber security concerns in the vehicles the Ministry of Road Transport and Highways (MoRTH) has proposed standard Cyber Security and Management Systems (CSMS) rules for specific categories of four-wheelers, including both passenger and commercial vehicles. The goal is to protect these vehicles and their functions against cyber-attacks or vulnerabilities. This move will aim to ensure standardized cybersecurity measures in the automotive industry. These proposed standards will put forth certain responsibilities on the vehicle manufacturers to implement suitable and proportional measures to secure dedicated environments and to take steps to ensure cyber security.
The New Mandate
The new set of standards requires automobile manufacturers to install a new cybersecurity management system, which will be inclusive of protection against several cyberattacks on the vehicle’s autonomous driving functions, electronic control unit, connected functions, and infotainment systems. The proposed automotive industry standards aim to fortify vehicles against cyberattacks. These standards, expected to be notified by early next month, will apply to all M and N category vehicles. This includes passenger vehicles, goods carriers, and even tractors if they possess even a single electronic control unit. The need for enhanced cybersecurity in the automotive sector is palpable. Modern vehicles, equipped with advanced technologies, are highly prone to cyberattacks. The Ministry of Road Transport and Highways has thus taken a precautionary measure to safeguard all new-age commercial and private vehicles against cyber threats and vulnerabilities.
Cyber Security and Management Systems (CSMS)
The proposed standards by the Ministry of Road Transport and Highways (MoRTH) clarify that CSMS refers to a systematic risk-based strategy that defines organisational procedures, roles, and governance to manage and mitigate risks connected with cyber threats to vehicles, eventually safeguarding them from cyberattacks. According to the draft regulations, all manufacturers will be required to install a cyber security management system in their vehicles and provide the government with a certificate of compliance at the time of vehicle type certification.
Electrical vehicle charging system
Electric vehicle charging stations could also be susceptible and prone to cyber threats and vulnerabilities, which significantly requires to have in place standards to prevent them. It is highlighted that the Indian Computer Emergency Response Team (CERT-In), a designated authority to track and monitor cybersecurity incidents in India, had received reports of vulnerabilities in products and applications related to electric vehicle charging stations. Electric cars or vehicles becoming increasingly popular as the world shifts to green technology. EV owners may charge their cars at charging points in convenient spots. When you charge an EV at a charging station, data transfers between the car, the charging station, and the company that owns the device. This trail of data sharing and EV charging stations in many ways can be exploited by the bad actors. Some of the threats may include Malware, remote manipulation, and disturbing charging stations, social engineering attacks, compromised aftermarket devices etc.
Conclusion
Cyber security is necessary in view of the increased connectivity and use of software systems and other modern technologies in vehicles. As the automotive industry continues to adopt advanced technologies, it will become increasingly important that organizations take a proactive approach to ensure cybersecurity in the vehicles. A balanced approach between technology innovation and security measures will be instrumental in ensuring the cybersecurity aspect in the automotive industry. The recent proposed policy standard by the Ministry of Road Transport and Highways (MoRTH) can be seen as a commendable step to make the automotive industry cyber-resilient and safe for everyone.
References:
- https://economictimes.indiatimes.com/news/india/road-transport-ministry-proposes-uniform-cyber-security-system-for-four-wheelers/articleshow/105187952.cms
- https://www.financialexpress.com/business/express-mobility-cybersecurity-in-the-autonomous-vehicle-the-next-frontier-in-mobility-3234055/
- https://www.gktoday.in/morth-proposes-uniform-cyber-security-standards-for-four-wheelers/
- https://cybersecurity.att.com/blogs/security-essentials/the-top-8-cybersecurity-threats-facing-the-automotive-industry-heading-into-2023
Executive Summary
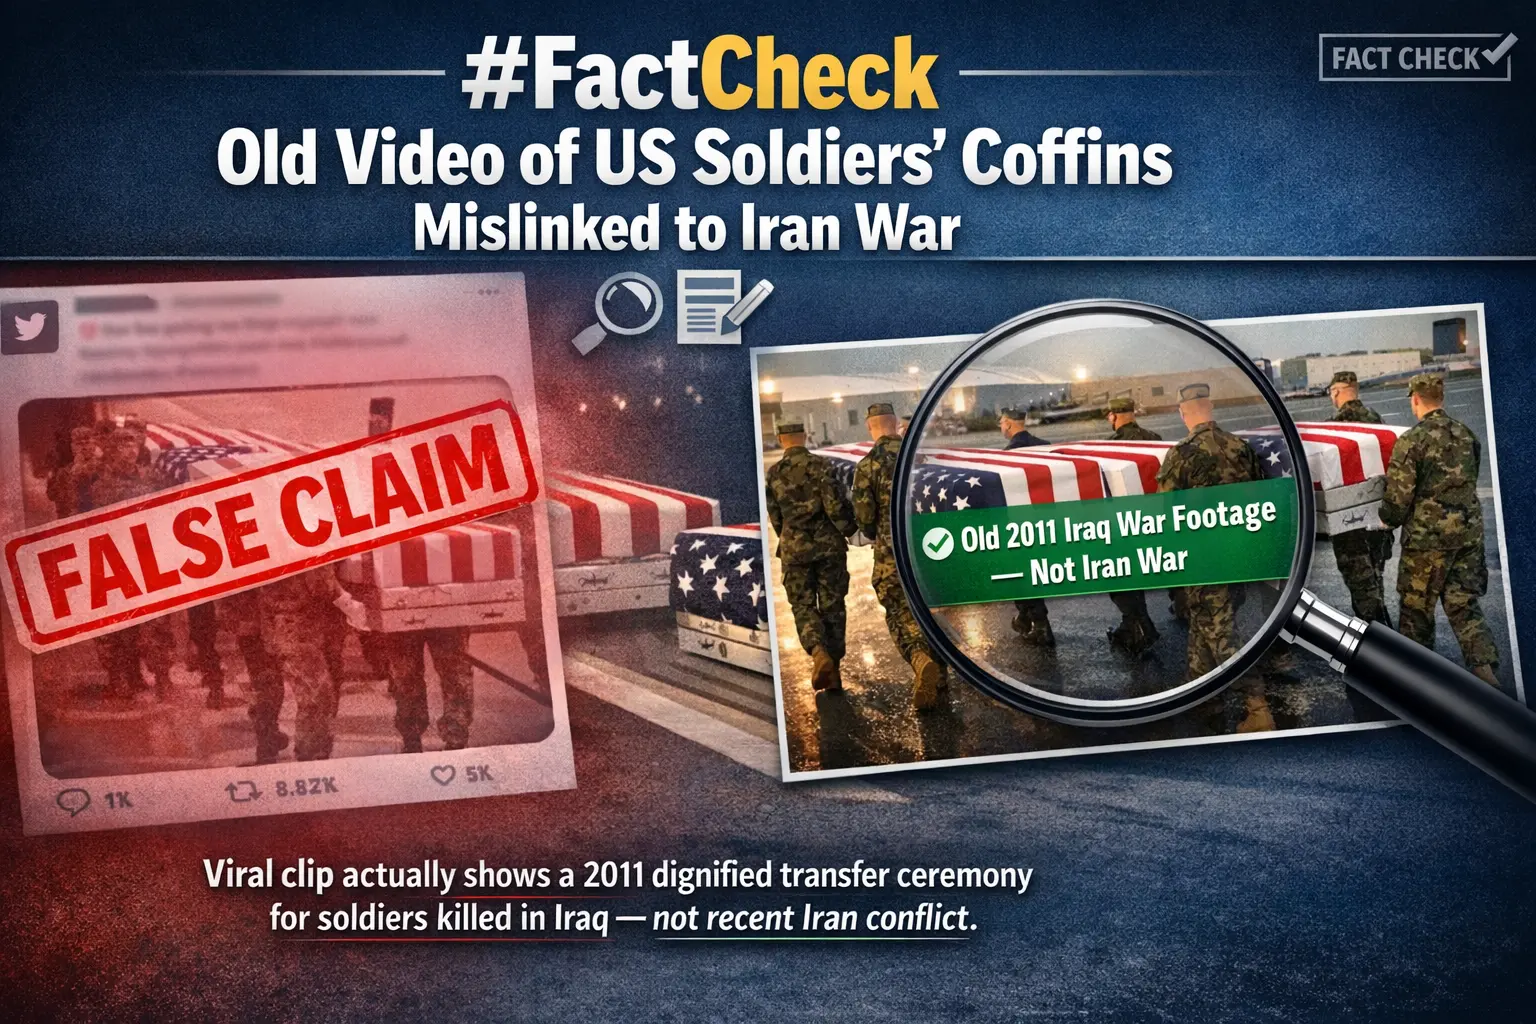
A video is being widely shared on social media showing soldiers carrying coffins with full military honours. Users are claiming that the footage shows the bodies of American soldiers who were killed in the war with Iran being brought back to the United States.
However, research by the CyberPeacefound the viral claim to be misleading. Our research revealed that the video has no connection to the recent Iran-Israel conflict. The footage actually dates back to December 2025, when an Islamic State gunman in Syria killed two US soldiers and a US civilian.
Following that incident, the bodies of the victims were transported with military honours, and the ceremony was recorded in the viral video. The clip is now being circulated online with a false claim.
Claim
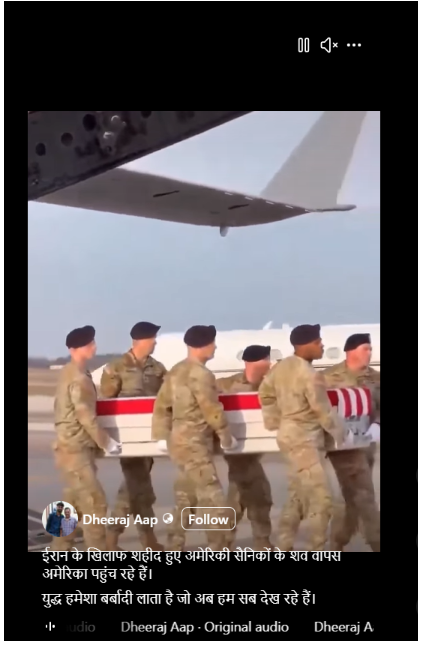
On March 1, 2026, an Instagram user shared the viral video claiming that it shows the bodies of American soldiers returning to the US after being killed in the war against Iran. The caption of the post reads: “Bodies of American soldiers martyred against Iran are returning to the United States. War always brings destruction, which we are now witnessing.”
The link to the post and its archived version can be seen below.
Fact check
To verify the claim, we extracted key frames from the viral video and performed a reverse image search using Google Lens. During the search, we found the full version of the video in a report published by BBC on December 18, 2025. This confirms that the footage predates the current developments.

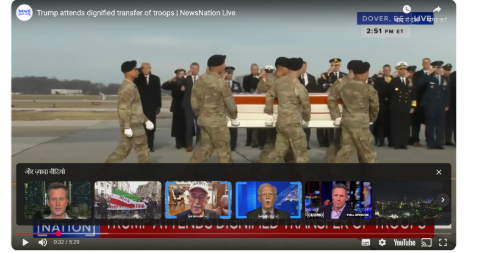
According to the BBC report, US President Donald Trump attended a dignified transfer ceremony for two members of the US National Guard and a US civilian who were killed in Syria. The somber ceremony took place at Dover Air Force Base in Delaware, United States. The US Central Command (Centcom) stated that the two soldiers and a civilian interpreter were killed in an ambush carried out by an Islamic State (IS) gunman in Syria. The US Army identified the two soldiers as Sgt. Edgar Brian Torres-Tovar (25) of Des Moines and Sgt. William Nathaniel Howard (29) of Marshalltown. A US civilian interpreter, Ayad Mansoor Sakat, was also killed in the attack. Officials said that three other service members were injured during the attack, and the gunman was engaged and killed. Syria’s state media also reported that two Syrian security personnel were injured in the incident.
Further research led us to a report published on the News Nation YouTube channel on December 18, 2025, which also featured the same footage related to the incident.
Conclusion
Our research found that the viral video is not related to the recent Iran-Israel conflict. The footage dates back to December 2025, when two US soldiers and a US civilian were killed in an Islamic State attack in Syria. The video shows the dignified transfer of their remains and is now being shared on social media with a misleading claim.

Introduction
As India moves full steam ahead towards a trillion-dollar digital economy, how user data is gathered, processed and safeguarded is under the spotlight. One of the most pervasive but least known technologies used to gather user data is the cookie. Cookies are inserted into every website and application to improve functionality, measure usage and customize content. But they also present enormous privacy threats, particularly when used without explicit user approval.
In 2023, India passed the Digital Personal Data Protection Act (DPDP) to give strong legal protection to data privacy. Though the act does not refer to cookies by name, its language leaves no doubt as to the inclusion of any technology that gathers or processes personal information and thus cookies regulation is at the centre of digital compliance in India. This blog covers what cookies are, how international legislation, such as the GDPR, has addressed them and how India's DPDP will regulate their use.
What Are Cookies and Why Do They Matter?
Cookies are simply small pieces of data that a website stores in the browser. They were originally designed to help websites remember useful information about users, such as your login session or what is in your shopping cart. Netscape initially built them in 1994 to make web surfing more efficient.
Cookies exist in various types. Session cookies are volatile and are deleted when the browser is shut down, whereas persistent cookies are stored on the device to monitor users over a period of time. First-party cookies are made by the site one is visiting, while third-party cookies are from other domains, usually utilised for advertisements or analytics. Special cookies, such as secure cookies, zombie cookies and tracking cookies, differ in intent and danger. They gather information such as IP addresses, device IDs and browsing history information associated with a person, thus making it personal data per the majority of data protection regulations.
A Brief Overview of the GDPR and Cookie Policy
The GDPR regulates how personal data can be processed in general. However, if a cookie collects personal data (like IP addresses or identifiers that can track a person), then GDPR applies as well, because it sets the rules on how that personal data may be processed, what lawful bases are required, and what rights the user has.
The ePrivacy Directive (also called the “Cookie Law”) specifically regulates how cookies and similar technologies can be used. Article 5(3) of the ePrivacy Directive says that storing or accessing information (such as cookies) on a user’s device requires prior, informed consent, unless the cookie is strictly necessary for providing the service requested by the user.
In the seminal Planet49 decision, the Court of Justice of the European Union held that pre-ticked boxes do not represent valid consent. Another prominent enforcement saw Amazon fined €35 million by France's CNIL for using tracking cookies without user consent.
Cookies and India’s Digital Personal Data Protection Act (DPDP), 2023
India's Digital Personal Data Protection Act, 2023 does not refer to cookies specifically but its provisions necessarily come into play when cookies harvest personal data like user activity, IP addresses, or device data. According to DPDP, personal data is to be processed for legitimate purposes with the individual's consent. The consent has to be free, informed, clear and unambiguous. The individuals have to be informed of what data is collected, how it will be processed.. The Act also forbids behavioural monitoring and targeted advertising in the case of children.
The Ministry of Electronics and IT released the Business Requirements Document for Consent Management Systems (BRDCMS) in June 2025. Although it is not binding by law, it provides operational advice on cookie consent. It recommends that websites use cookie banners with "Accept," "Reject," and "Customize" choices. Users must be able to withdraw or change their consent at any moment. Multi-language handling and automatic expiry of cookie preferences are also suggested to suit accessibility and privacy requirements.
The DPDP Act and the BRDCMS together create a robust user-rights model, even in the absence of a special cookie law.
What Should Indian Websites Do?
For the purposes of staying compliant, Indian websites and online platforms need to act promptly to harmonise their use of cookies with DPDP principles. This begins with a transparent and simple cookie banner providing users with an opportunity to accept or decline non-essential cookies. Consent needs to be meaningful; coercive tactics such as cookie walls must not be employed. Websites need to classify cookies (e.g., necessary, analytics and ads) and describe each category's function in plain terms under the privacy policy. Users must be given the option to modify cookie settings anytime using a Consent Management Platform (CMP). Monitoring children or their behavioural information must be strictly off-limits.
These are not only about being compliant with the law, they're about adhering to ethical data stewardship and user trust building.
What Should Users Do?
Cookies need to be understood and controlled by users to maintain online personal privacy. Begin by reading cookie notices thoroughly and declining unnecessary cookies, particularly those associated with tracking or advertising. The majority of browsers today support blocking third-party cookies altogether or deleting them periodically.
It is also recommended to check and modify privacy settings on websites and mobile applications. It is possible to minimise surveillance with the use of browser add-ons such as ad blockers or privacy extensions. Users are also recommended not to blindly accept "accept all" in cookie notices and instead choose "customise" or "reject" where not necessary for their use.
Finally, keeping abreast of data rights under Indian law, such as the right to withdraw consent or to have data deleted, will enable people to reclaim control over their online presence.
Conclusion
Cookies are a fundamental component of the modern web, but they raise significant concerns about individual privacy. India's DPDP Act, 2023, though not explicitly referring to cookies, contains an effective legal framework that regulates any data collection activity involving personal data, including those facilitated by cookies.
As India continues to make progress towards comprehensive rulemaking and regulation, companies need to implement privacy-first practices today. And so must the users, in an active role in their own digital lives. Collectively, compliance, transparency and awareness can build a more secure and ethical internet ecosystem where privacy is prioritised by design.
References
- https://prsindia.org/billtrack/digital-personal-data-protection-bill-2023
- https://gdpr-info.eu/
- https://d38ibwa0xdgwxx.cloudfront.net/create-edition/7c2e2271-6ddd-4161-a46c-c53b8609c09d.pdf
- https://oag.ca.gov/privacy/ccpa
- https://www.barandbench.com/columns/cookie-management-under-the-digital-personal-data-protection-act-2023#:~:text=The%20Business%20Requirements%20Document%20for,the%20DPDP%20Act%20and%20Rules.
- https://samistilegal.in/cookies-meaning-legal-regulations-and-implications/#
- https://secureprivacy.ai/blog/india-digital-personal-data-protection-act-dpdpa-cookie-consent-requirements
- https://law.asia/cookie-use-india/
- https://www.cookielawinfo.com/major-gdpr-fines-2020-2021/#:~:text=4.,French%20websites%20could%20refuse%20cookies.
