
#Factcheck-False Claims of Houthi Attack on Israel’s Ashkelon Power Plant
Executive Summary:
A post on X (formerly Twitter) has gained widespread attention, featuring an image inaccurately asserting that Houthi rebels attacked a power plant in Ashkelon, Israel. This misleading content has circulated widely amid escalating geopolitical tensions. However, investigation shows that the footage actually originates from a prior incident in Saudi Arabia. This situation underscores the significant dangers posed by misinformation during conflicts and highlights the importance of verifying sources before sharing information.

Claims:
The viral video claims to show Houthi rebels attacking Israel's Ashkelon power plant as part of recent escalations in the Middle East conflict.

Fact Check:
Upon receiving the viral posts, we conducted a Google Lens search on the keyframes of the video. The search reveals that the video circulating online does not refer to an attack on the Ashkelon power plant in Israel. Instead, it depicts a 2022 drone strike on a Saudi Aramco facility in Abqaiq. There are no credible reports of Houthi rebels targeting Ashkelon, as their activities are largely confined to Yemen and Saudi Arabia.

This incident highlights the risks associated with misinformation during sensitive geopolitical events. Before sharing viral posts, take a brief moment to verify the facts. Misinformation spreads quickly and it’s far better to rely on trusted fact-checking sources.
Conclusion:
The assertion that Houthi rebels targeted the Ashkelon power plant in Israel is incorrect. The viral video in question has been misrepresented and actually shows a 2022 incident in Saudi Arabia. This underscores the importance of being cautious when sharing unverified media. Before sharing viral posts, take a moment to verify the facts. Misinformation spreads quickly, and it is far better to rely on trusted fact-checking sources.
- Claim: The video shows massive fire at Israel's Ashkelon power plant
- Claimed On:Instagram and X (Formerly Known As Twitter)
- Fact Check: False and Misleading

Related Blogs

Executive Summary:
This report discloses a new cyber threat contributing to the list of threats targeting internet users in the name of "Aarong Ramadan Gifts". The fraudsters are imitating the popular Bangladeshi brand Aarong, which is known for its Bengali ethnic wear and handicrafts, and allure the victims with the offer of exclusive gifts for Ramadan. The moment when users click on the link, they are taken through a fictitious path of quizzes, gift boxes, and social proof, that simply could damage their personal information and system devices. Through knowing how this is done we can educate users to take caution and stop themselves from falling into cyber threats.
False Claim:
The false message accompanied by a link on social media, claims that Aarong, one of the most respected brands in Bangladesh for their exquisite ethnic wear and handicrafts, is providing Ramadan gifts exclusively through online promotion. And while that may be the facade of the scam, its real aim is to lead users to click on harmful links that may end up in their personal data and devices being compromised.

The Deceptive Journey:
- The Landing page starts with a salutation and a catchy photo of Aarong store, and later moves ahead encouraging the visitors to take a part of a short quiz to claim the gift. This is designed for the purpose of creating a false image of authenticity and trustworthiness.
- A certain area at the end of the page looks like a social media comment section, and users are posting the positive impacts the claim has on them. This is one of the techniques to build the image of a solid base of support and many partakers.
- The quiz starts with a few easy questions on how much the user knows about Aarong and their demographics. This data is vital in the development of more complex threats and can be used to address specific targets in the future.
- After the user hits the OK button, the screen displays a matrix of the Gift boxes, and the user then needs to make at least 3 attempts to attain the reward. This is a commonly used approach which allows the scammer to keep users engaged longer and increases the chances of making them comply with the fraudulent scheme.
- The user is instructed to share the campaign on WhatsApp from this point of the campaign, and the user must keep clicking the WhatsApp button until the progress bar is complete. This is a way to both expand and perpetuate the scam, affecting many more users.
- After completing the steps, the user is shown instructions on how to claim the prize.
The Analysis:
- The home page and quiz are structured to maintain a false impression of genuineness and proficiency, thus allowing the victims to partake in the fraudulent design. The compulsion to forward the message in WhatsApp is the way they inspire more and more users and eventually get into the scam.
- The final purpose of the scam could be to obtain personal data from the user and eventually enter their devices, which could lead to a higher risk of cyber threats, such as identity theft, financial theft, or malware installation.
- We have also cross-checked and as of now there is no well established and credible source or any official notification that has confirmed such an offer advertised by Aarong.
- The campaign is hosted on a third party domain instead of the official Website, this raised suspicion. Also the domain has been registered recently.
- The intercepted request revealed a connection to a China-linked analytical service, Baidu in the backend.

- Domain Name: apronicon.top
- Registry Domain ID: D20231130G10001G_13716168-top
- Registrar WHOIS Server: whois.west263[.]com
- Registrar URL: www.west263[.]com
- Updated Date: 2024-02-28T07:21:18Z
- Creation Date: 2023-11-30T03:27:17Z (Recently created)
- Registry Expiry Date: 2024-11-30T03:27:17Z
- Registrar: Chengdu west dimension digital
- Registrant State/Province: Hei Long Jiang
- Registrant Country: CN (China)
- Name Server: amos.ns.cloudflare[.]com
- Name Server: zara.ns.cloudflare[.]com
Note: Cybercriminal used Cloudflare technology to mask the actual IP address of the fraudulent website.
CyberPeace Advisory:
- Do not open those messages received from social platforms in which you think that such messages are suspicious or unsolicited. In the beginning, your own discretion can become your best weapon.
- Falling prey to such scams could compromise your entire system, potentially granting unauthorized access to your microphone, camera, text messages, contacts, pictures, videos, banking applications, and more. Keep your cyber world safe against any attacks.
- Never, in any case, reveal such sensitive data as your login credentials and banking details to entities you haven't validated as reliable ones.
- Before sharing any content or clicking on links within messages, always verify the legitimacy of the source. Protect not only yourself but also those in your digital circle.
- For the sake of the truthfulness of offers and messages, find the official sources and companies directly. Verify the authenticity of alluring offers before taking any action.
Conclusion:
Aarong Ramadan Gift scam is a fraudulent act that takes advantage of the victims' loyalty to a reputable brand. The realization of the mechanism used to make the campaign look real, can actually help us become more conscious and take measures to our community not to be inattentive against cyberthreats. Be aware, check the credibility, and spread awareness to others wherever you can, to contribute in building a security conscious digital space.

Introduction
“GPS Spoofing” though formerly was confined to conflict zones as a consequence, has lately become a growing hazard for pilots and aircraft operators across the world, and several countries have been facing such issues. This definition stems from the US Radio Technical Commission for Aeronautics, which delivers specialized advice for government regulatory authorities. Global Positioning System (GPS) is considered an emergent part of aviation infrastructure as it supersedes traditional radio beams used to direct planes towards the landing. “GPS spoofing” occurs when a double-dealing radio signal overrides a legitimate GPS satellite alert where the receiver gets false location information. In the present times, this is the first time civilian passenger flights have faced such a significant danger, though GPS signal interference of this character has existed for over a decade. According to the Agency France-Presse (AFP), false GPS signals mislead onboard plane procedures and problematise the job of airline pilots that are surging around conflict areas. GPS spoofing may also be the outcome of military electronic warfare systems that have been deployed in zones combating regional tension. GPS spoofing can further lead to significant upheavals in commercial aviation, which include arrivals and departures of passengers apart from safety.
Spoofing might likewise involve one country’s military sending false GPS signals to an enemy plane or drone to impede its capability to operate, which has a collateral impact on airliners operating at a near distance. Collateral impairment in commercial aircraft can occur as confrontations escalate and militaries send faulty GPS signals to attempt to thwart drones and other aircraft. It could, therefore, lead to a global crisis, leading to the loss of civilian aircraft in an area already at a high-risk zone close to an operational battle area. Furthermore, GPS jamming is different from GPS Spoofing. While jamming is when the GPS signals are jammed or obstructed, spoofing is very distinct and way more threatening.
Global Reporting
An International Civil Aviation Organization (ICAO) assessment released in 2019 indicated that there were 65 spoofing incidents across the Middle East in the preceding two years, according to the C4ADS report. At the beginning of 2018, Euro control received more than 800 reports of Global Navigation Satellite System (GNSS) interference in Europe. Also, GPS spoofing in Eastern Europe and the Middle East has resulted in up to 80nm divergence from the flight route and aircraft impacted have had to depend on radar vectors from Air Traffic Control (ATC). According to Forbes, flight data intelligence website OPSGROUP, constituted of 8,000 members including pilots and controllers, has been reporting spoofing incidents since September 2023. Similarly, over 20 airlines and corporate jets flying over Iran diverted from their planned path after they were directed off the pathway by misleading GPS signals transmitted from the ground, subjugating the navigation systems of the aircraft.
In this context, vicious hackers, however at large, have lately realized how to override the critical Inertial Reference Systems (IRS) of an airplane, which is the essential element of technology and is known by the manufacturers as the “brains” of an aircraft. However, the current IRS is not prepared to counter this kind of attack. IRS uses accelerometers, gyroscopes and electronics to deliver accurate attitude, speed, and navigation data so that a plane can decide how it is moving through the airspace. GPS spoofing occurrences make the IRS ineffective, and in numerous cases, all navigation power is lost.
Red Flag from Agencies
The European Union Aviation Safety Agency (EASA) and the International Air Transport Association (IATA) correspondingly hosted a workshop on incidents where people have spoofed and obstructed satellite navigation systems and inferred that these direct a considerable challenge to security. IATA and EASA have further taken measures to communicate information about GPS tampering so that crew and pilots can make sure to determine when it is transpiring. The EASA had further pre-cautioned about an upsurge in reports of GPS spoofing and jamming happenings in the Baltic Sea area, around the Black Sea, and regions near Russia and Finland in 2022 and 2023. According to industry officials, empowering the latest technologies for civil aircraft can take several years, and while GPS spoofing incidents have been increasing, there is no time to dawdle. Experts have noted critical navigation failures on airplanes, as there have been several recent reports of alarming cyber attacks that have changed planes' in-flight GPS. As per experts, GPS spoofing could affect commercial airlines and cause further disarray. Due to this, there are possibilities that pilots can divert from the flight route, further flying into a no-fly zone or any unauthorized zone, putting them at risk.
According to OpsGroup, a global group of pilots and technicians first brought awareness and warning to the following issue when the Federal Aviation Administration (FAA) issued a forewarning on the security of flight risk to civil aviation operations over the spate of attacks. In addition, as per the civil aviation regulator Directorate General of Civil Aviation (DGCA), a forewarning circular on spoofing threats to planes' GPS signals when flying over parts of the Middle East was issued. DGCA advisory further notes the aviation industry is scuffling with uncertainties considering the contemporary dangers and information of GNSS jamming and spoofing.
Conclusion
As the aviation industry continues to grapple with GPS spoofing problems, it is entirely unprepared to combat this, although the industry should consider discovering attainable technologies to prevent them. As International conflicts become convoluted, technological solutions are unrestricted and can be pricey, intricate and not always efficacious depending on what sort of spoofing is used.
As GPS interference attacks become more complex, specialized resolutions should be invariably contemporized. Improving education and training (to increase awareness among pilots, air traffic controllers and other aviation experts), receiver technology (Creating and enforcing more state-of-the-art GPS receiver technology), ameliorating monitoring and reporting (Installing robust monitoring systems), cooperation (collaboration among stakeholders like government bodies, aviation organisations etc.), data/information sharing, regulatory measures (regulations and guidelines by regulatory and government bodies) can help in averting GPS spoofing.
References
- https://economictimes.indiatimes.com/industry/transportation/airlines-/-aviation/false-gps-signal-surge-makes-life-hard-for-pilots/articleshow/108363076.cms?from=mdr
- https://nypost.com/2023/11/20/lifestyle/hackers-are-taking-over-planes-gps-experts-are-lost-on-how-to-fix-it/
- https://www.timesnownews.com/india/planes-losing-gps-signal-over-middle-east-dgca-flags-spoofing-threat-article-105475388
- https://www.firstpost.com/world/gps-spoofing-deceptive-gps-lead-over-20-planes-astray-in-iran-13190902.html
- https://www.forbes.com/sites/erictegler/2024/01/31/gps-spoofing-is-now-affecting-airplanes-in-parts-of-europe/?sh=48fbe725c550
- https://www.insurancejournal.com/news/international/2024/01/30/758635.htm
- https://airwaysmag.com/gps-spoofing-commercial-aviation/
- https://www.wsj.com/articles/aviation-industry-to-tackle-gps-security-concerns-c11a917f
- https://www.deccanherald.com/world/explained-what-is-gps-spoofing-that-has-misguided-around-20-planes-near-iran-iraq-border-and-how-dangerous-is-this-2708342
Executive Summary
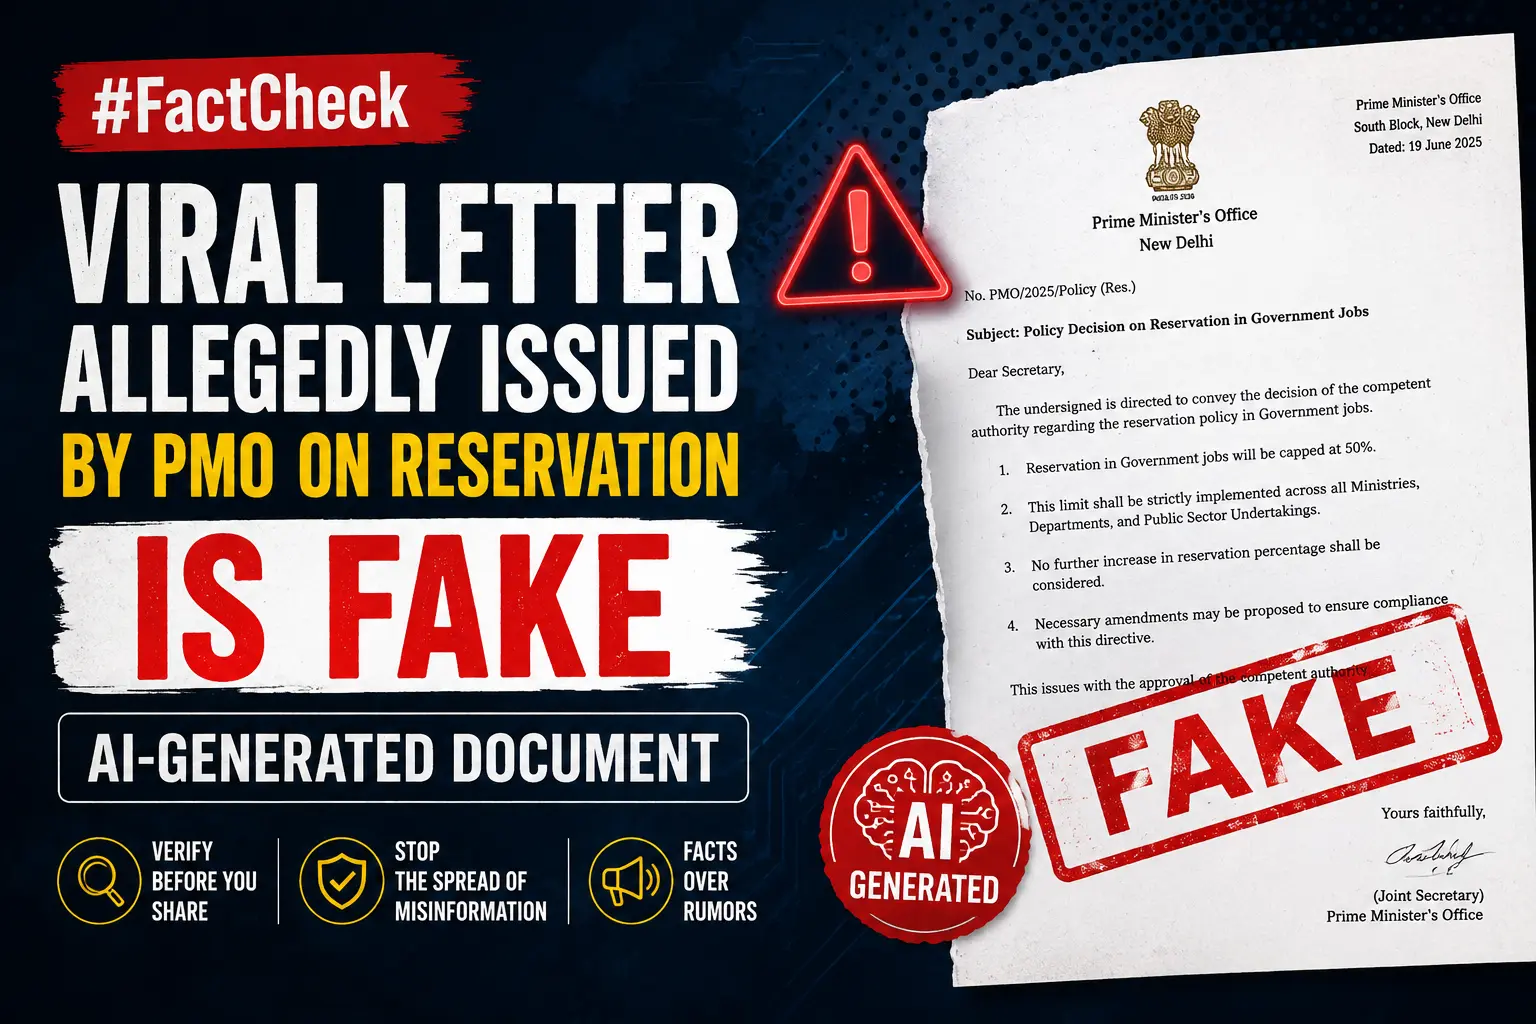
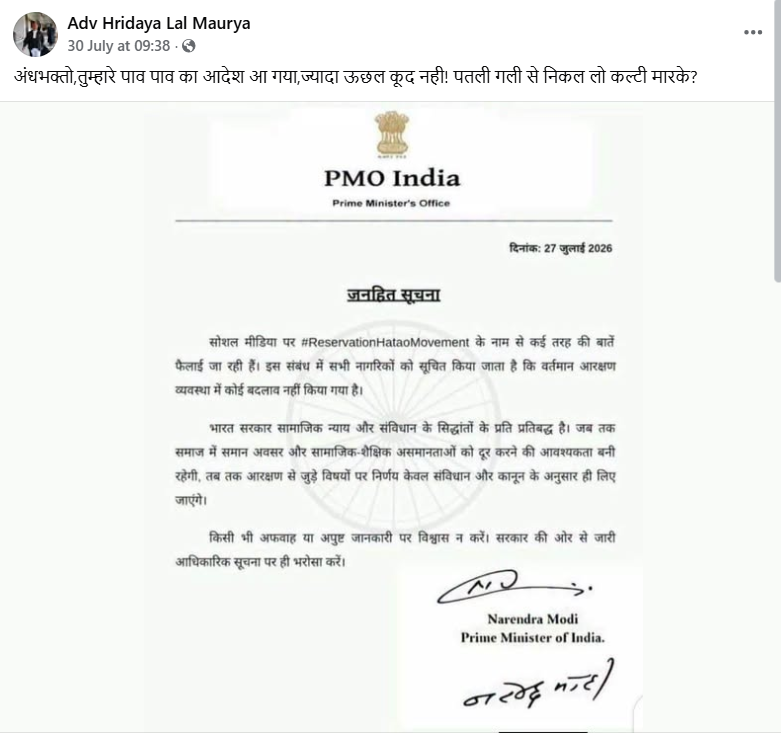
A purported letter issued in the name of the Prime Minister’s Office (PMO) is being widely shared on social media. The letter claims that the government has not made any changes to the reservation system regarding the “Remove Reservation Movement” and appeals to people not to pay attention to rumours. The viral letter is dated July 27, 2026, and also carries what appear to be Prime Minister Narendra Modi’s signatures in both Hindi and English.
CyberPeace Research Wing’s research found the viral claim to be false. The research revealed that the Prime Minister’s Office (PMO) has neither issued any official statement regarding reservation nor released any such letter. No credible media reports related to the alleged letter were found. The research further revealed that the purported reservation-related letter circulating on social media was a fake document created with the help of AI.
Claim:
A Facebook user shared the alleged letter issued in the name of the Prime Minister’s Office on July 30, 2026, claiming that the government has not made any changes to the reservation system in connection with the “Remove Reservation Movement” and appealed to citizens not to believe rumours. The viral letter bears the date July 27, 2026, and displays signatures of Prime Minister Narendra Modi in both Hindi and English. The archived link and screenshot of the post are provided below:
https://www.facebook.com/share/p/1b9nD5k3As/
Factcheck
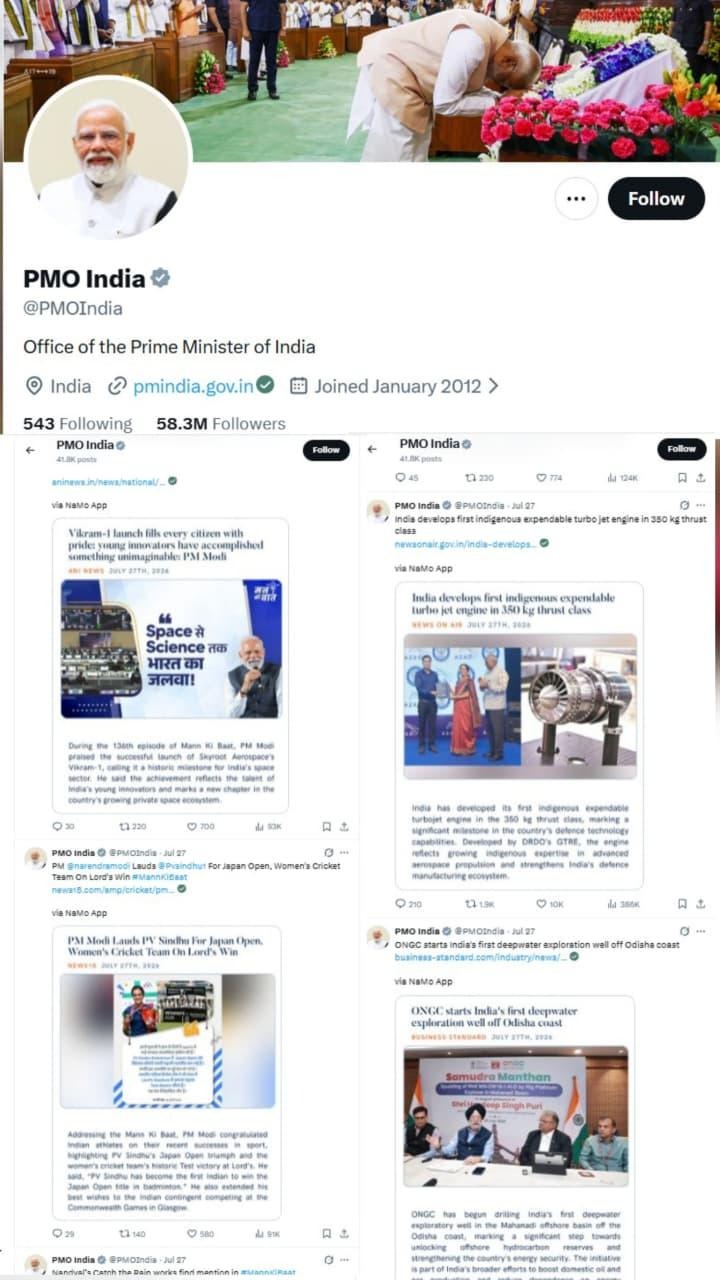
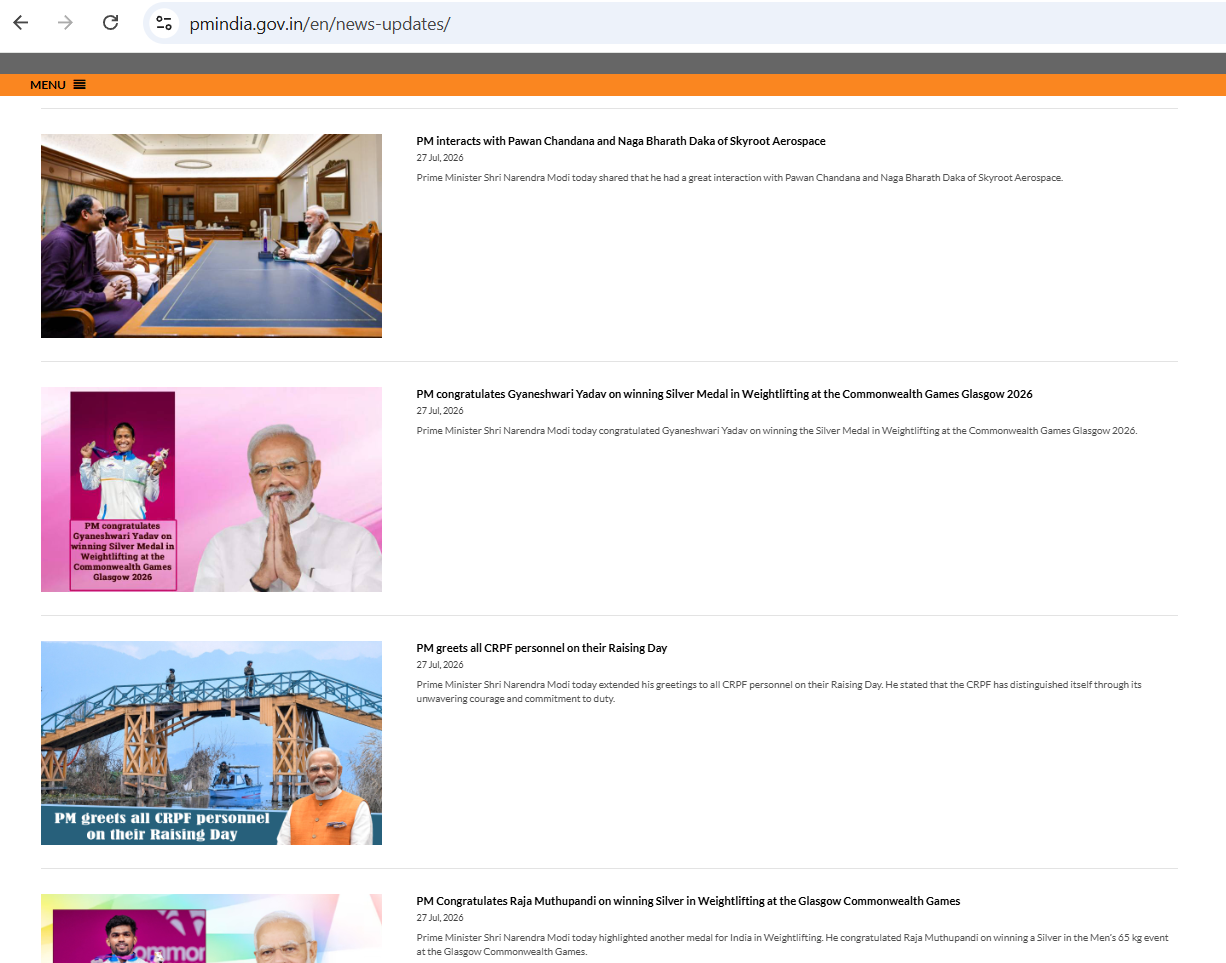
To verify the authenticity of the viral claim, we conducted a Google search using relevant keywords. However, no credible media reports related to the alleged letter were found. During the next stage of the research, we scanned the official X account (formerly Twitter) of PMO India. We did not find any such letter posted on July 27 or around that date. Continuing the research, we checked the official website of PMO India. No such letter was found in the news updates section or anywhere else on the website that could confirm the viral claim.
Further, we reviewed the press releases issued by the Prime Minister’s Office on July 27 available on the official website of the Press Information Bureau (PIB). We found no press release or official communication related to reservation or matching the viral letter.
https://www.pmindia.gov.in/en/
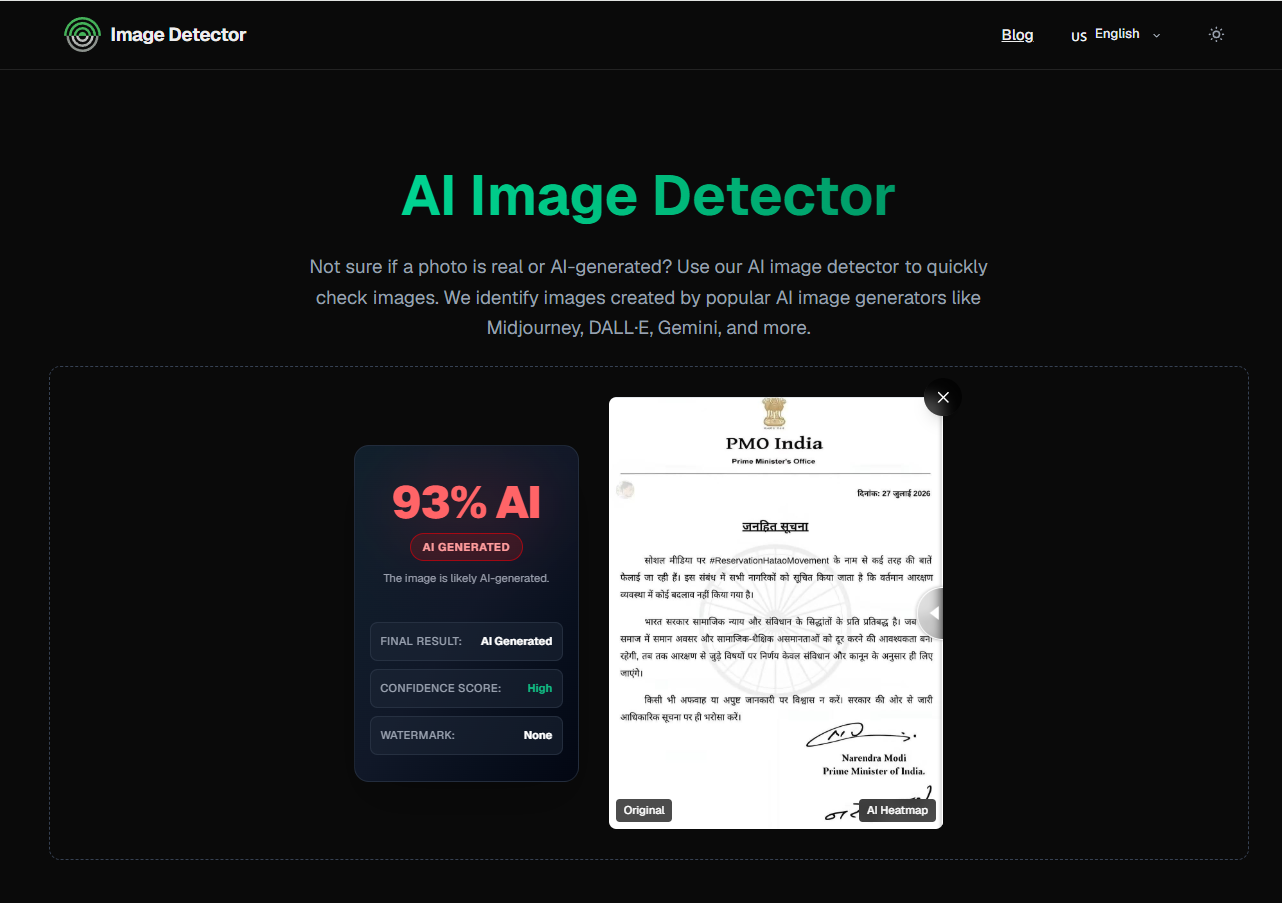
As part of the research, we scanned the viral letter using the AI detection tool Image Detector. The results indicated that the document was 93 percent likely to be AI-generated.
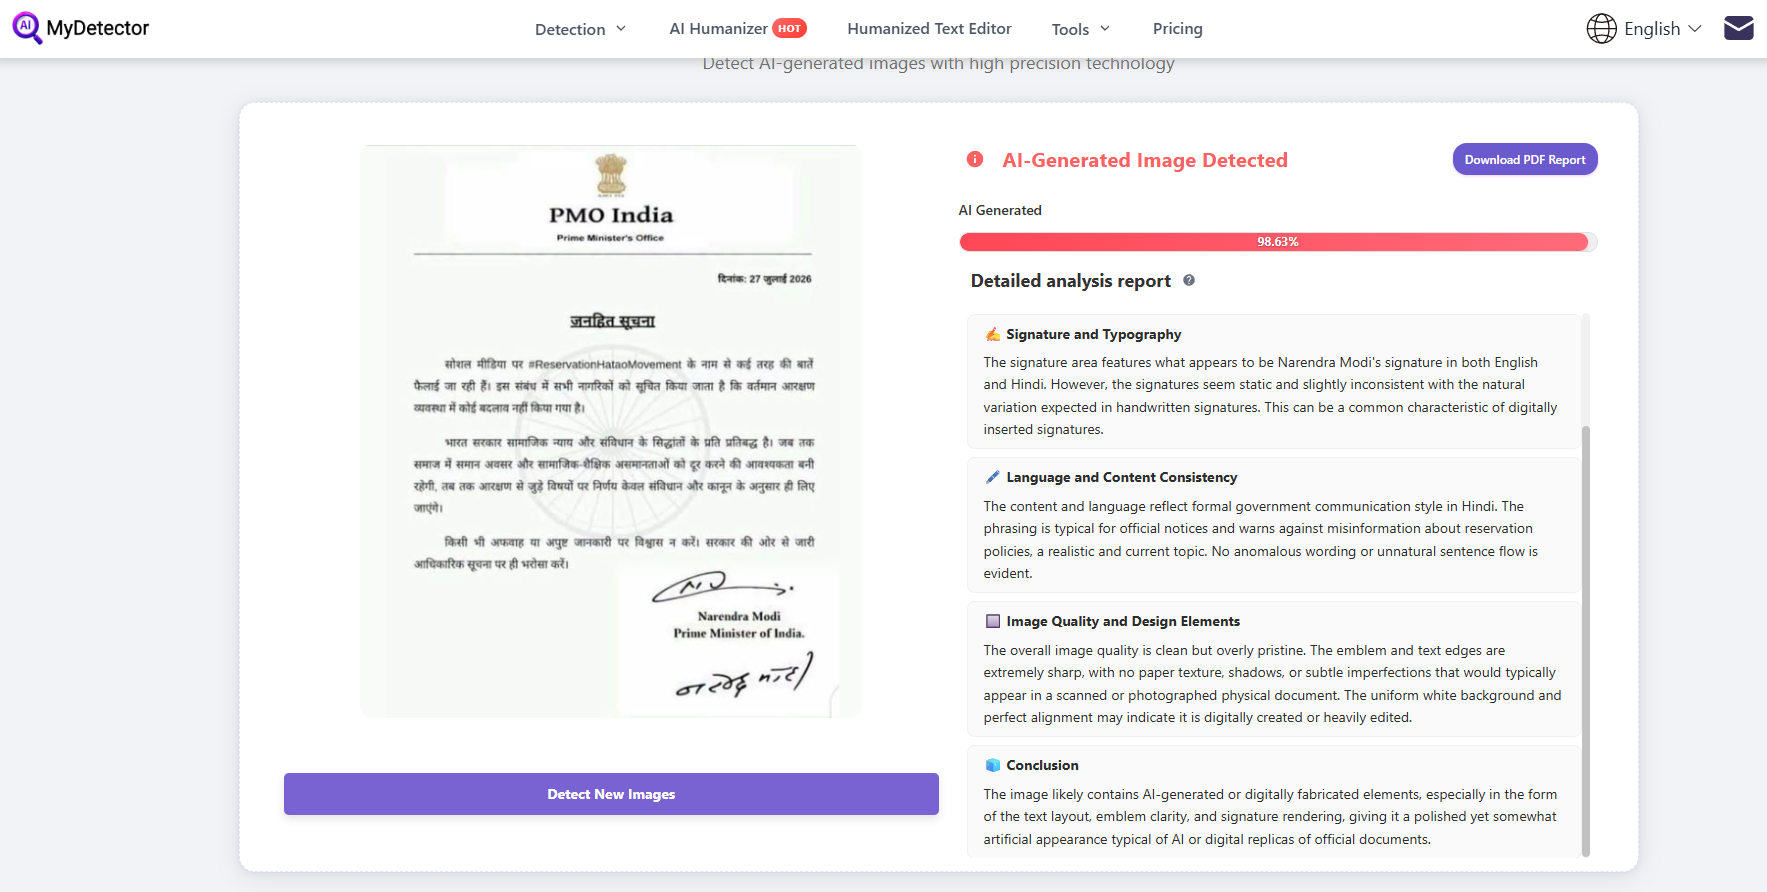
We also analysed the viral letter using another AI detection tool, My Detector. The results showed a 98 percent probability that the letter was created using AI.
Conclusion:
Our research found no official evidence confirming that the Prime Minister’s Office issued the viral letter. The purported PMO letter regarding reservation was found to be fake and AI-generated.
