
#FactCheck: Fake Claim on Delhi Authority Culling Dogs After Supreme Court Stray Dog Ban Directive 11 Aug 2025
Executive Summary:
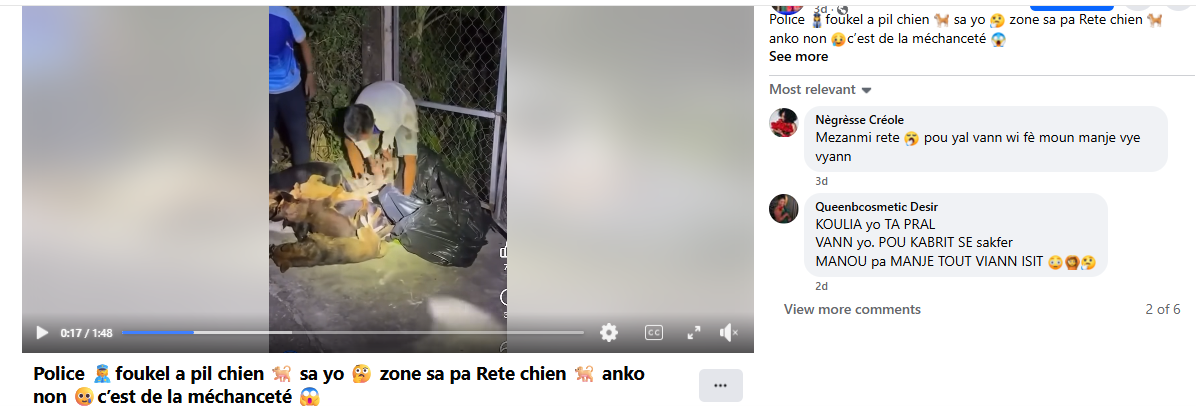
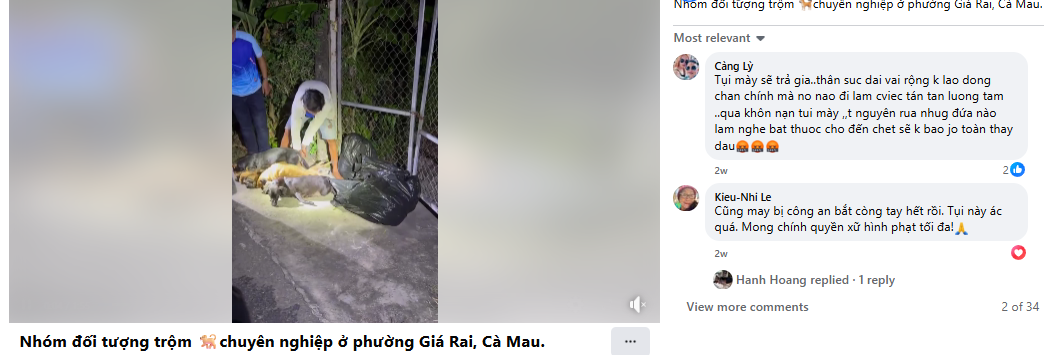
A viral claim alleges that following the Supreme Court of India’s August 11, 2025 order on relocating stray dogs, authorities in Delhi NCR have begun mass culling. However, verification reveals the claim to be false and misleading. A reverse image search of the viral video traced it to older posts from outside India, probably linked to Haiti or Vietnam, as indicated by the use of Haitian Creole and Vietnamese language respectively. While the exact location cannot be independently verified, it is confirmed that the video is not from Delhi NCR and has no connection to the Supreme Court’s directive. Therefore, the claim lacks authenticity and is misleading
Claim:
There have been several claims circulating after the Supreme Court of India on 11th August 2025 ordered the relocation of stray dogs to shelters. The primary claim suggests that authorities, following the order, have begun mass killing or culling of stray dogs, particularly in areas like Delhi and the National Capital Region. This narrative intensified after several videos purporting to show dead or mistreated dogs allegedly linked to the Supreme Court’s directive—began circulating online.
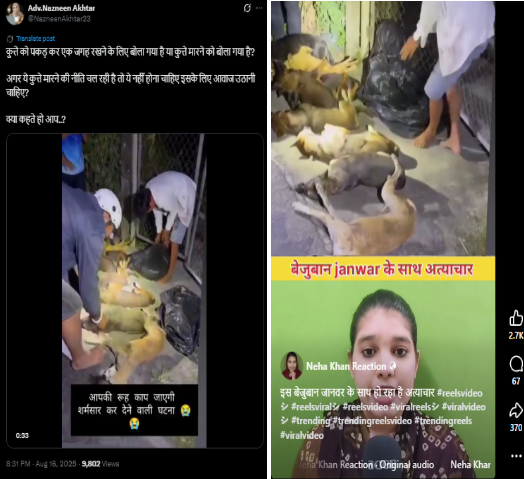
Fact Check:
After conducting a reverse image search using a keyframe from the viral video, we found similar videos circulating on Facebook. Upon analyzing the language used in one of the posts, it appears to be Haitian Creole (Kreyòl Ayisyen), which is primarily spoken in Haiti. Another similar video was also found on Facebook, where the language used is Vietnamese, suggesting that the post associates the incident with Vietnam.
However, it is important to note that while these posts point towards different locations, the exact origin of the video cannot be independently verified. What can be established with certainty is that the video is not from Delhi NCR, India, as is being claimed. Therefore, the viral claim is misleading and lacks authenticity.
Conclusion:
The viral claim linking the Supreme Court’s August 11, 2025 order on stray dogs to mass culling in Delhi NCR is false and misleading. Reverse image search confirms the video originated outside India, with evidence of Haitian Creole and Vietnamese captions. While the exact source remains unverified, it is clear the video is not from Delhi NCR and has no relation to the Court’s directive. Hence, the claim lacks credibility and authenticity.
Claim: Viral fake claim of Delhi Authority culling dogs after the Supreme Court directive on the ban of stray dogs as on 11th August 2025
Claimed On: Social Media
Fact Check: False and Misleading

Related Blogs
Executive Summary
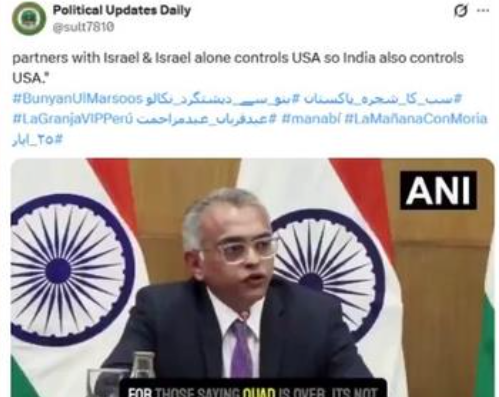
A video of an Additional Secretary in the Ministry of External Affairs (MEA), handling the Americas & Canada Division, is being widely circulated on social media. The clip is being shared with the claim that he said:“Even if the Quad ends, India will partner only with Israel, and since Israel controls the US, India also controls the US.”The viral post attempts to link this alleged statement to India’s foreign policy. Many users are sharing it as authentic. However, CyberPeace Research Wing research found the claim to be false. The video has been digitally altered, and no such statement was made by the official in the original briefing.
Claim
On social media platform X (formerly Twitter), the viral video is being shared with the claim that the MEA Additional Secretary said Israel controls the United States, and therefore India also controls the US.
- https://www.facebook.com/61562281661615/videos/1518036689691723/
- https://archive.ph/xGJHa#selection-967.0-978.0
Fact Check
To verify the claim, we extracted key frames from the viral video and conducted a reverse image search. During the research, we found the original video, which was streamed live on May 26, 2026, on the verified YouTube channel of the Ministry of External Affairs (MEA), titled: “Special Briefing by MEA on Quad Foreign Ministers’ Meeting”
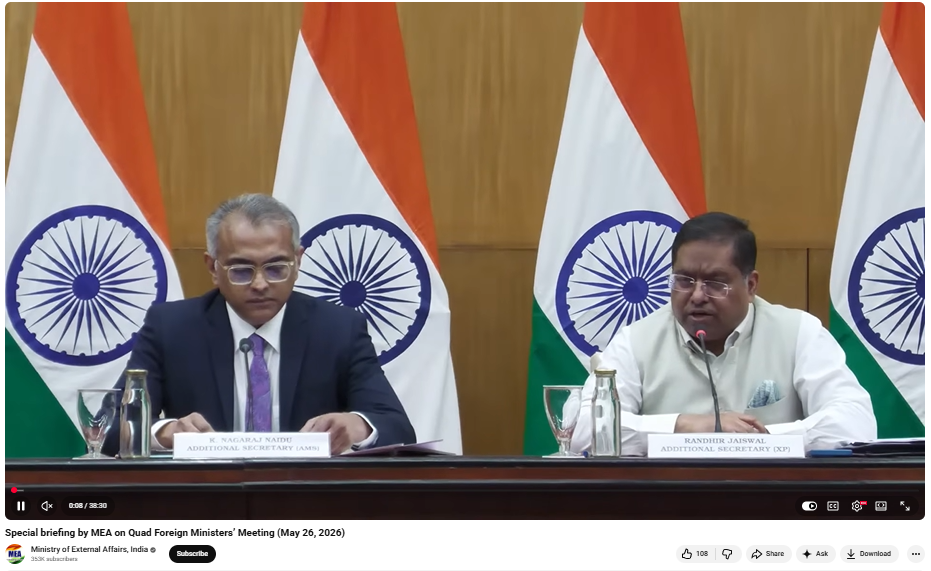
During the briefing, Naidu highlighted India’s commitment to a free and open Indo-Pacific region, mentioning new initiatives in maritime surveillance, critical minerals, and 6G development. He also noted the continued momentum of the Quad, stating that frequent ministerial meetings reflect strong and ongoing cooperation among member countries despite challenges in holding formal leaders’ summits.
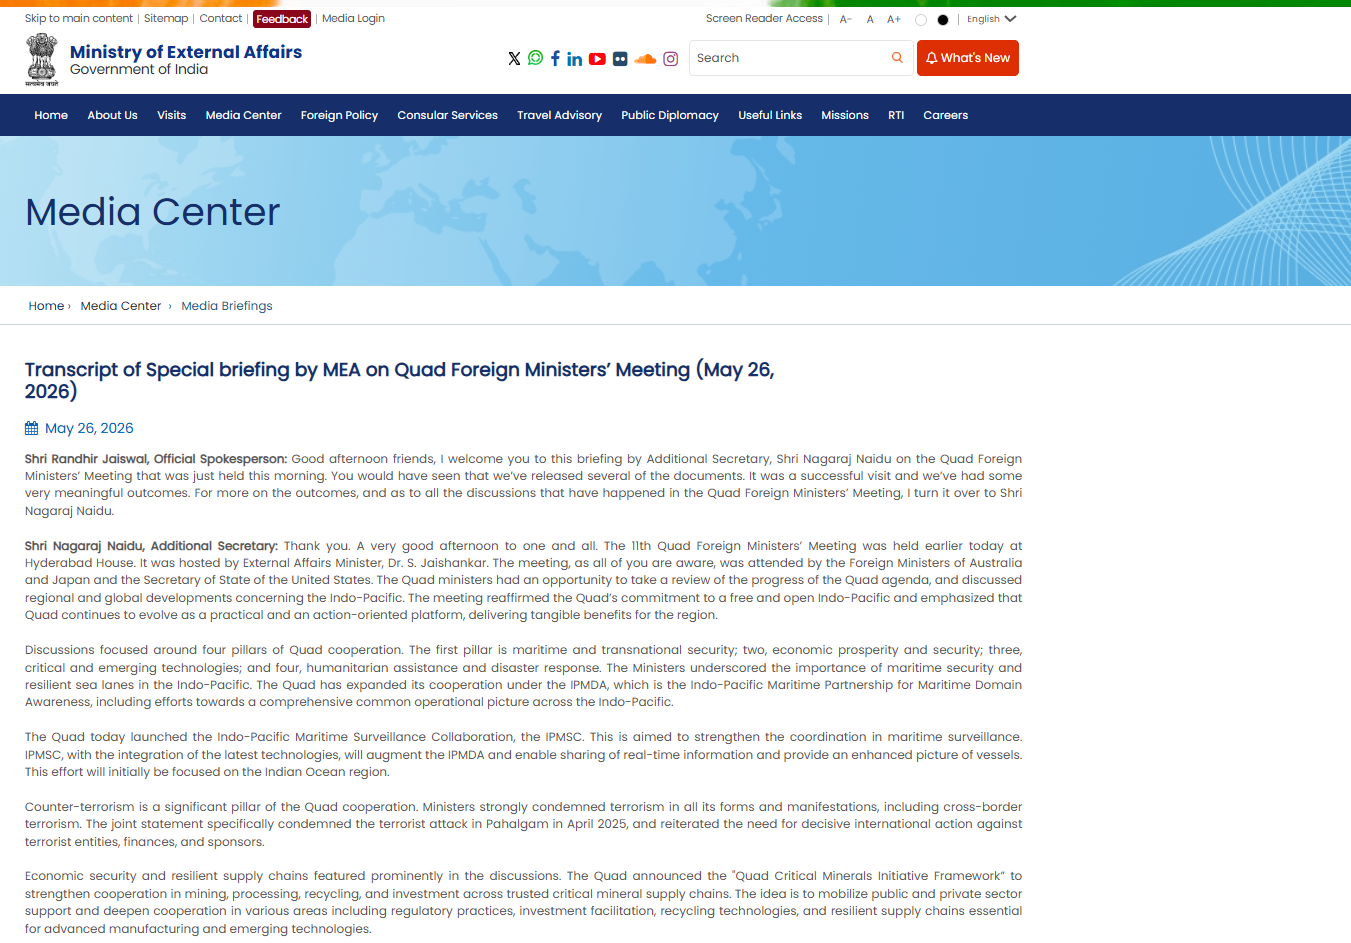
The official transcript of the briefing is also available on the MEA website:
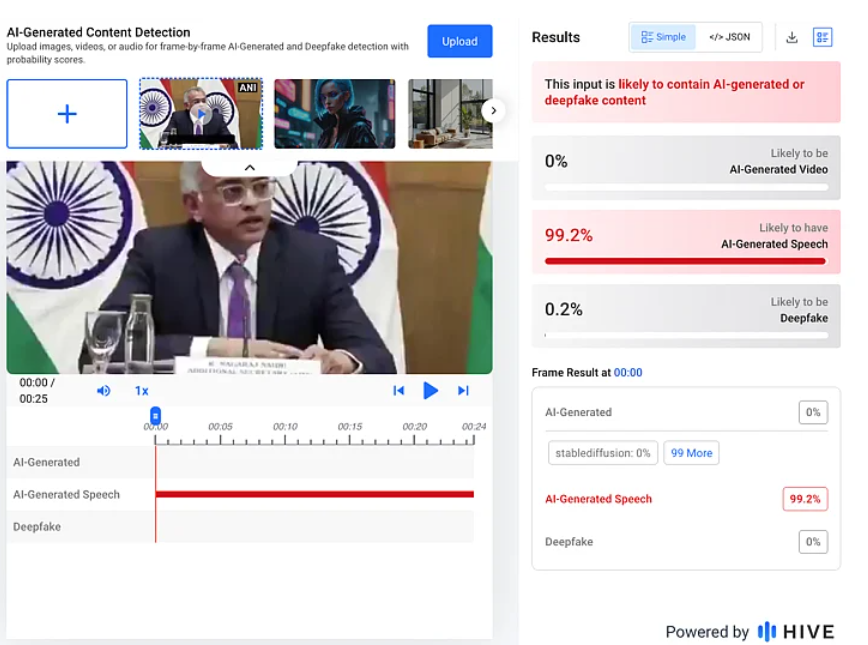
Since the viral statement was never made during the event, we further analysed the video using Deepfake Voice Detector and Hive Moderation’s AI-generated content detection tool. Hive moderation analysis indicated a 99.2% probability that the audio in the viral video is AI-generated.
Conclusion
CyberPeace Research Wing research found that the viral video is digitally altered. The Additional Secretary did not make any such statement during the official briefing. The audio in the clip has been manipulated and is being circulated with a misleading narrative.
Introduction
Imagine receiving a WhatsApp message from your CEO late on a Friday afternoon. The message is urgent: a confidential business deal requires an immediate wire transfer before markets close. The profile picture matches, the tone sounds familiar, and the account it came from has your CEO's name on it. Everything appears legitimate except it is not. This is the essence of the 'Boss Scam,' a sophisticated form of CEO impersonation fraud that has emerged as one of the most financially devastating cybercrime trends of 2025. India's Indian Cyber Crime Coordination Centre (I4C), under the Ministry of Home Affairs, issued an urgent national advisory on this threat in June 2025, warning that organisations across the country are falling victim to an evolved and technically advanced version of executive impersonation fraud that bypasses many traditional cybersecurity safeguards.
Understanding the Boss Scam
What Is CEO Impersonation Fraud?
CEO fraud, also known as Business Email Compromise (BEC) or executive impersonation fraud, is a targeted cyberattack in which criminals assume the digital identity of a high-ranking executive most commonly the Chief Executive Officer to deceive subordinate employees into authorising fraudulent financial transactions or divulging sensitive information. Unlike generic phishing campaigns that cast a wide net, CEO fraud is a precision attack. Cybercriminals invest significant time and resources researching their targets, studying organisational hierarchies, communication styles, and internal financial workflows before executing the scam. The attack is devastatingly effective because it weaponises one of the most powerful forces in any workplace: authority. An instruction that appears to originate from the CEO carries an implicit demand for immediate compliance, often bypassing normal checks and verification procedures. The FBI's Internet Crime Complaint Center (IC3) has consistently identified BEC as one of the most financially destructive categories of cybercrime, with adjusted losses of approximately USD 2.77 billion reported in 2024 alone across the United States.
The New and Evolved Variant: India's I4C Advisory
The variant identified by India's I4C represents a dangerous evolution of traditional CEO fraud. The earlier versions of this scam relied on spoofed email addresses or fake WhatsApp profiles that merely mimicked an executive's account. Employees were trained to spot tell-tale warning signs suspicious domains, unusual sender addresses, or spelling errors in email IDs. The latest
Boss Scam variant eliminates many of these red flags entirely by hijacking the executive's actual and legitimate WhatsApp account. This sophisticated attack begins not with the employee, but with the CEO. Cybercriminals approach senior executives through email or WhatsApp while posing as regulatory authorities in India's context, this includes impersonating officials from the Reserve Bank of India (RBI) or other government bodies. These messages claim an urgent compliance violation or regulatory breach requiring immediate remedial action. The communication contains a compressed ZIP archive, which the executive is prompted to open. Inside the archive are malicious executable (.exe) and Dynamic Link Library (.dll) files that, when run on a Windows system, deploy a Trojan dropper a form of malware capable of establishing persistent access on the device and hijacking active WhatsApp Web session tokens.
Once the session token is compromised, the attacker gains complete control over the executive's WhatsApp account without needing the phone, password, or any two-factor authentication code. The legitimate account is now in criminal hands, and any message sent from it appears entirely authentic to recipients.
How the Boss Scam Operates: A Step-by-Step Breakdown
Stage 1: Targeting the Executive: The operation begins with careful reconnaissance. Attackers study the target organisation's leadership, identify the CEO or a senior executive, and gather publicly available information about their communication patterns, business relationships, and company operations through LinkedIn, corporate websites, and news sources. They then contact the executive under a false regulatory identity, engineering a sense of crisis and urgency.
Stage 2: Malware Deployment:The fraudulent regulatory communication contains a ZIP file disguised as a compliance document, a security patch, or a mandatory software update. Upon execution on a Windows machine, the embedded malware installs itself and begins hijacking the WhatsApp Web session. Critically, in many documented cases, the CEO innocently forwards this regulatory message and the malicious attachment to their own finance officer or IT team, inadvertently widening the attack surface.
Stage 3: Account Takeover and Impersonation:With the CEO's legitimate WhatsApp account now under their control, cybercriminals send highly convincing messages to subordinate staff, particularly those in finance, accounts payable, or treasury functions. These messages carry the full weight of genuine executive authority correct name, profile photo, and account history making them extraordinarily difficult to distinguish from authentic communications.
Stage 4: The Financial Strike:The fraudulent instruction typically requests an urgent, confidential wire transfer to an unfamiliar account, often accompanied by requests for complete secrecy. The employee, believing the instruction to be genuine and fearing the consequences of non-compliance with a directive from their CEO, processes the transaction. By the time the fraud is discovered, the funds have been routed through multiple mule accounts, making recovery extremely difficult.
The Broader Landscape: Scale and Impact
The Boss Scam is not an isolated Indian phenomenon it represents the cutting edge of a global epidemic of executive impersonation fraud. According to the FBI's data, BEC has been the costliest category of cybercrime for several years running, with cumulative global losses that officials have described as exceeding USD 50 billion over the past decade. A 2025 fraud survey found that 90 per cent of U.S. companies experienced attempted cyber-fraud in 2024, with business email compromise and impersonation scams surging by 103 per cent year-on-year. The technological sophistication of these attacks has grown in lockstep with the availability of AI tools. In early 2024, a finance worker at a multinational firm in Hong Kong was tricked into authorising a payment of USD 25 million after attending a video conference in which the CFO and other senior executives were entirely fabricated using deepfake technology. In March 2025, a similar attack unfolded in Singapore, where a finance director authorised nearly USD 499,000 after joining a Zoom call populated entirely by AI-generated deepfakes of company executives. Deepfake attacks against businesses reportedly surged by 3,000 per cent in 2023, and voice cloning fraud rose by 680 per cent the following year. In India, the Telangana Cyber Security Bureau reported over 300 complaints related to the Boss Scam variant alone within a twenty-day period in June 2025. In one prominent case, formerPrime Minister I.K. Gujral's son, Naresh Gujral, reportedly lost approximately Rs 7.8 crorethrough a messaging-app impersonation scheme targeting his company's Chief Financial Officer.
Warning Signs Every Employee Must Recognise
Identifying a Boss Scam attempt requires situational awareness and healthy scepticism. The following red flags should prompt immediate caution:
● Any request for urgent or secret financial transfers received via WhatsApp or email, without prior discussion or formal documentation.
● Instructions to bypass standard approval procedures or to maintain secrecy from colleagues or senior management.
● Compressed files (.zip, .rar) or executable attachments received from any source, including apparently known contacts, claiming to be compliance documents or regulatory updates.
● Messages from executives at unusual hours, particularly those emphasising that a transaction must be completed immediately.
● Claims that a request comes from a government regulator, such as the RBI, delivered through informal channels like WhatsApp.
● Any communication that creates extreme urgency, invokes authority, and simultaneously demands confidentiality the classic triangle of social engineering manipulation. Protective Measures: Defending Against the Boss Scam
For Employees and Finance Teams
The I4C advisory and global cybersecurity authorities recommend several concrete steps that employees can take. The most important is to independently verify any urgent financial instruction through a direct voice call or in-person confirmation before taking action, regardless of how convincing the digital message appears. No financial transaction of significance should be authorised on the basis of a WhatsApp message or email alone.
For Organisations and Leadership
Organisations must implement multi-layered verification protocols for all wire transfers above a defined threshold, making dual authorisation and out-of-band verification mandatory. IT teams should deploy updated malware detection tools, enforce software restriction policies that block unauthorised executable files, and regularly audit devices for signs of compromise. WhatsApp linked devices should be reviewed periodically. Leadership must also commit to regular, mandatory cybersecurity awareness training for all staff, with particular attention to social engineering tactics. The I4C has also emphasised that legitimate regulatory bodies including the RBI , do not distribute software, compliance tools, or security patches via WhatsApp or email attachments. Any such communication must be treated as a potential attack vector and reported immediately.
Conclusion
The Boss Scam exploits organisational trust and human psychology rather than technical vulnerabilities and with deepfake technology now capable of replicating familiar voices and faces, traditional verification instincts are no longer reliable. The strongest defence is a culture of verification without embarrassment, where questioning an unusual instruction is seen as diligence, not insubordination. Awareness, clear protocols, and scepticism towards urgency remain our most powerful tools. If you've encountered such a scam, contact India's National Cybercrime Helpline at 1930 or report at cybercrime.gov.in.
References
- https://www.cybercrime.gov.in
- https://www.business-standard.com/india-news/boss-scam-ceo-impersonation-fraudgovt- advisory-i4c-126062300353_1.html
- https://www.indiatvnews.com/news/india/boss-scam-all-about-the-new-cyber-fraudtargeting- corporates-and-precautions-listed-by-mha-2026-06-23-1045827
- https://www.freepressjournal.in/business/boss-scam-on-whatsapp-new-ceo-fraudbypasses- traditional-cybersecurity-checks
- https://hyderabadmail.com/tgcsb-warns-boss-scam-ceo-impersonation-fraud-malwarealert/
- https://www.newkerala.com/news/a/rising-boss-scam-threat-targets-senior-executiveswarns- 242.html
- https://www.ic3.gov
- https://www.mcafee.com/learn/is-that-really-your-boss/
- https://abnormal.ai/glossary/ceo-fraud
- https://www.brside.com/blog/deepfake-ceo-fraud-50m-voice-cloning-threat-cfos
- https://www.eftsure.com/blog/cyber-crime/these-7-deepfake-ceo-scams-prove-that-nobusiness- is-safe/
- https://www.knowbe4.com/ceo-fraud
- https://trustpair.com/blog/ceo-fraud-how-to-protect-your-organization-from-fraudsters/
- https://hacked.com/services/executive-impersonation-and-ceo-fraud-protecting-high-networth- individuals/
- https://www.certifid.com/article/ceo-fraud
Executive Summary
A video is being widely shared on social media showing armed personnel attacking a helicopter. The video is being circulated with the claim that Iranian soldiers shot down a US military helicopter near the Strait of Hormuz amid rising tensions between the United States and Iran. CyberPeace Research Wing research found the claim to be false. The viral video is AI-generated and is being shared with misleading context.
Claim:
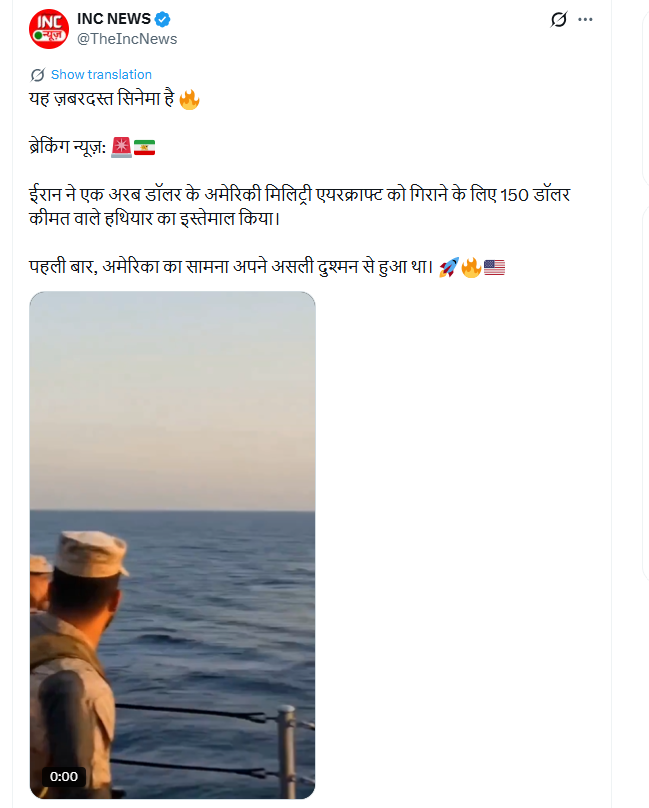
An X (formerly Twitter) user shared the video on June 10, 2026, with the caption: “This is great cinema. Breaking News: Iran used a $150 weapon to bring down a $1 billion US military aircraft. For the first time, America has met its real enemy.”
Post link and archive link can be seen below:
https://x.com/TheIncNews/status/2064758088012607544?s=20
https://archive.ph/LUDUz
Fact-Check
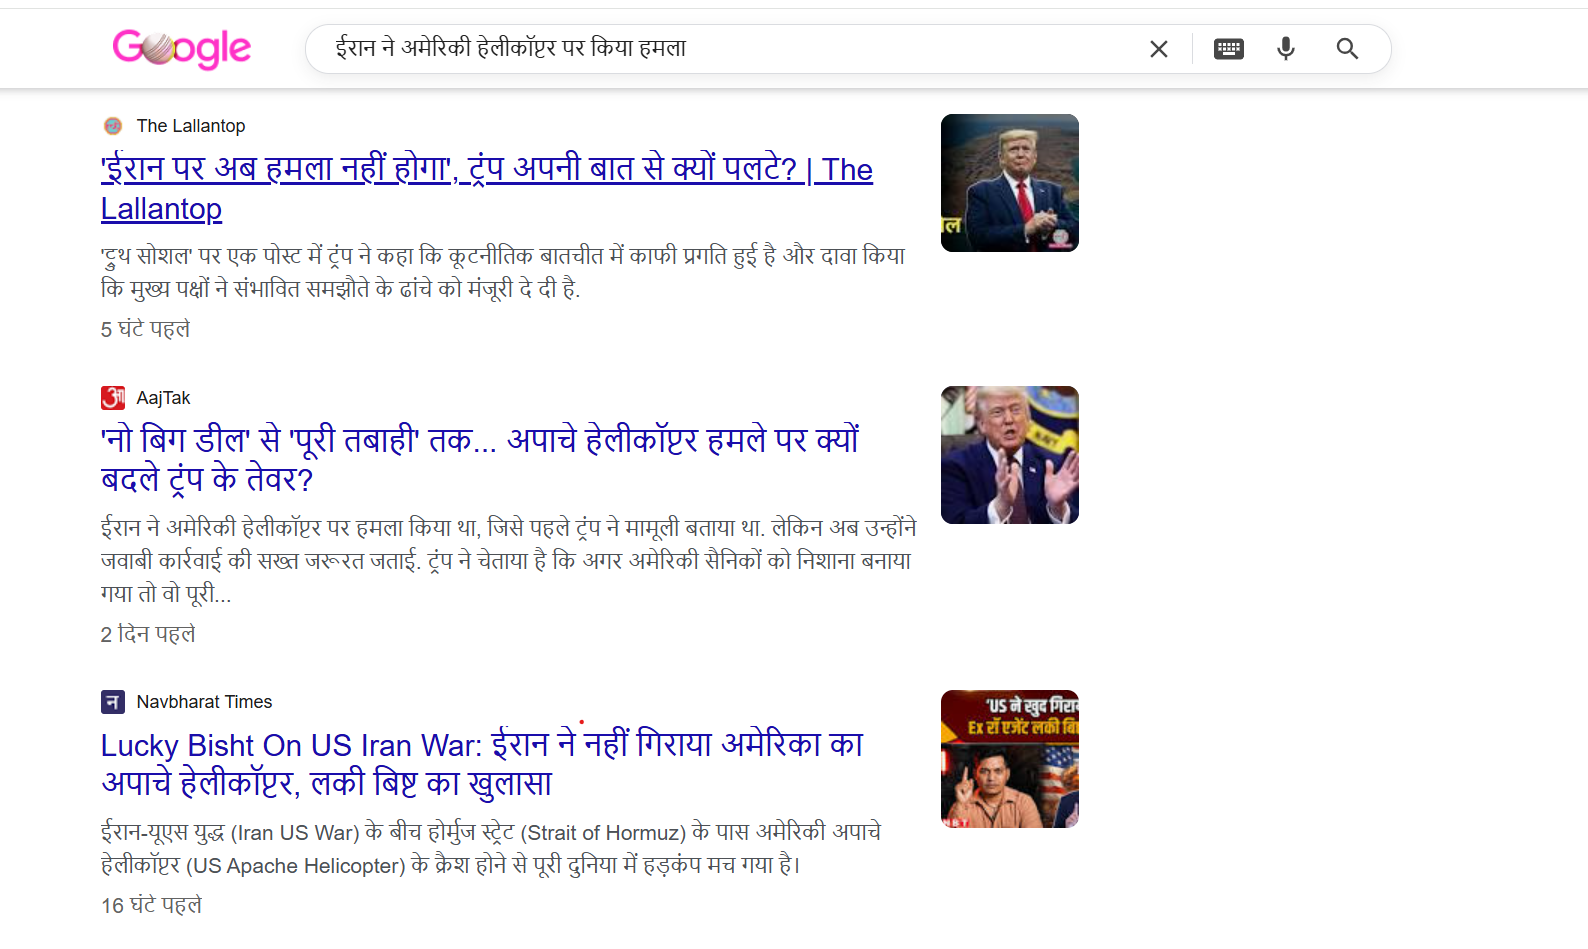
To verify the claim, we conducted a keyword search on Google. However, no credible media reports were found supporting this claim.
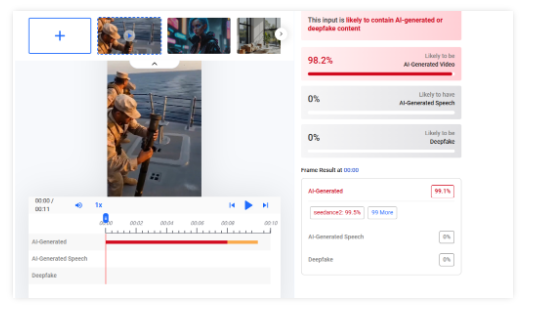
On closely examining the video, we suspected it to be AI-generated. We then analyzed it using the AI detection tool HIVE MODERATION. The results indicated that the video is 98% likely to be AI-generated.
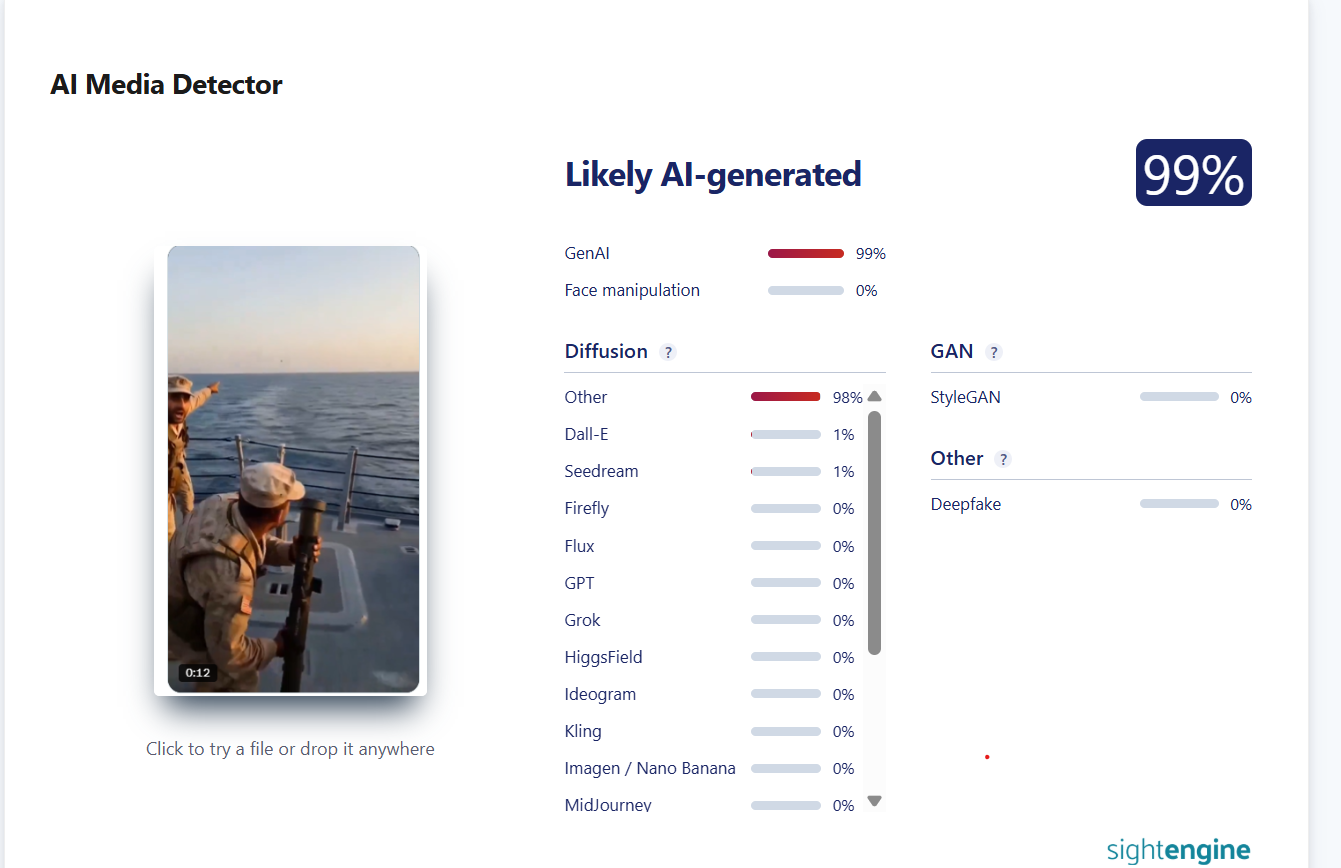
In the next step, we further analyzed the video using another AI detection tool, SIGHTENGINE. The results showed a 99% probability of the video being AI-generated.
Conclusion:
Our research confirms that the viral video is AI-generated and does not depict any real-world incident. The content is being circulated with a misleading and false narrative, falsely linking it to ongoing geopolitical tensions, despite there being no credible evidence or verified reports supporting such a claim.
