
#FactCheck - Virat Kohli's Ganesh Chaturthi Video Falsely Linked to Ram Mandir Inauguration
Executive Summary:
Old footage of Indian Cricketer Virat Kohli celebrating Ganesh Chaturthi in September 2023 was being promoted as footage of Virat Kohli at the Ram Mandir Inauguration. A video of cricketer Virat Kohli attending a Ganesh Chaturthi celebration last year has surfaced, with the false claim that it shows him at the Ram Mandir consecration ceremony in Ayodhya on January 22. The Hindi newspaper Dainik Bhaskar and Gujarati newspaper Divya Bhaskar also displayed the now-viral video in their respective editions on January 23, 2024, escalating the false claim. After thorough Investigation, it was found that the Video was old and it was Ganesh Chaturthi Festival where the cricketer attended.
Claims:
Many social media posts, including those from news outlets such as Dainik Bhaskar and Gujarati News Paper Divya Bhaskar, show him attending the Ram Mandir consecration ceremony in Ayodhya on January 22, where after investigation it was found that the Video was of Virat Kohli attending Ganesh Chaturthi in September, 2023.


The caption of Dainik Bhaskar E-Paper reads, “ क्रिकेटर विराट कोहली भी नजर आए ”
Fact Check:
CyberPeace Research Team did a reverse Image Search of the Video where several results with the Same Black outfit was shared earlier, from where a Bollywood Entertainment Instagram Profile named Bollywood Society shared the same Video in its Page, the caption reads, “Virat Kohli snapped for Ganapaati Darshan” the post was made on 20 September, 2023.

Taking an indication from this we did some keyword search with the Information we have, and it was found in an article by Free Press Journal, Summarizing the article we got to know that Virat Kohli paid a visit to the residence of Shiv Sena leader Rahul Kanal to seek the blessings of Lord Ganpati. The Viral Video and the claim made by the news outlet is false and Misleading.
Conclusion:
The recent Claim made by the Viral Videos and News Outlet is an Old Footage of Virat Kohli attending Ganesh Chaturthi the Video back to the year 2023 but not of the recent auspicious day of Ram Mandir Pran Pratishtha. To be noted that, we also confirmed that Virat Kohli hadn’t attended the Program; there was no confirmation that Virat Kohli attended on 22 January at Ayodhya. Hence, we found this claim to be fake.
- Claim: Virat Kohli attending the Ram Mandir consecration ceremony in Ayodhya on January 22
- Claimed on: Youtube, X
- Fact Check: Fake

Related Blogs
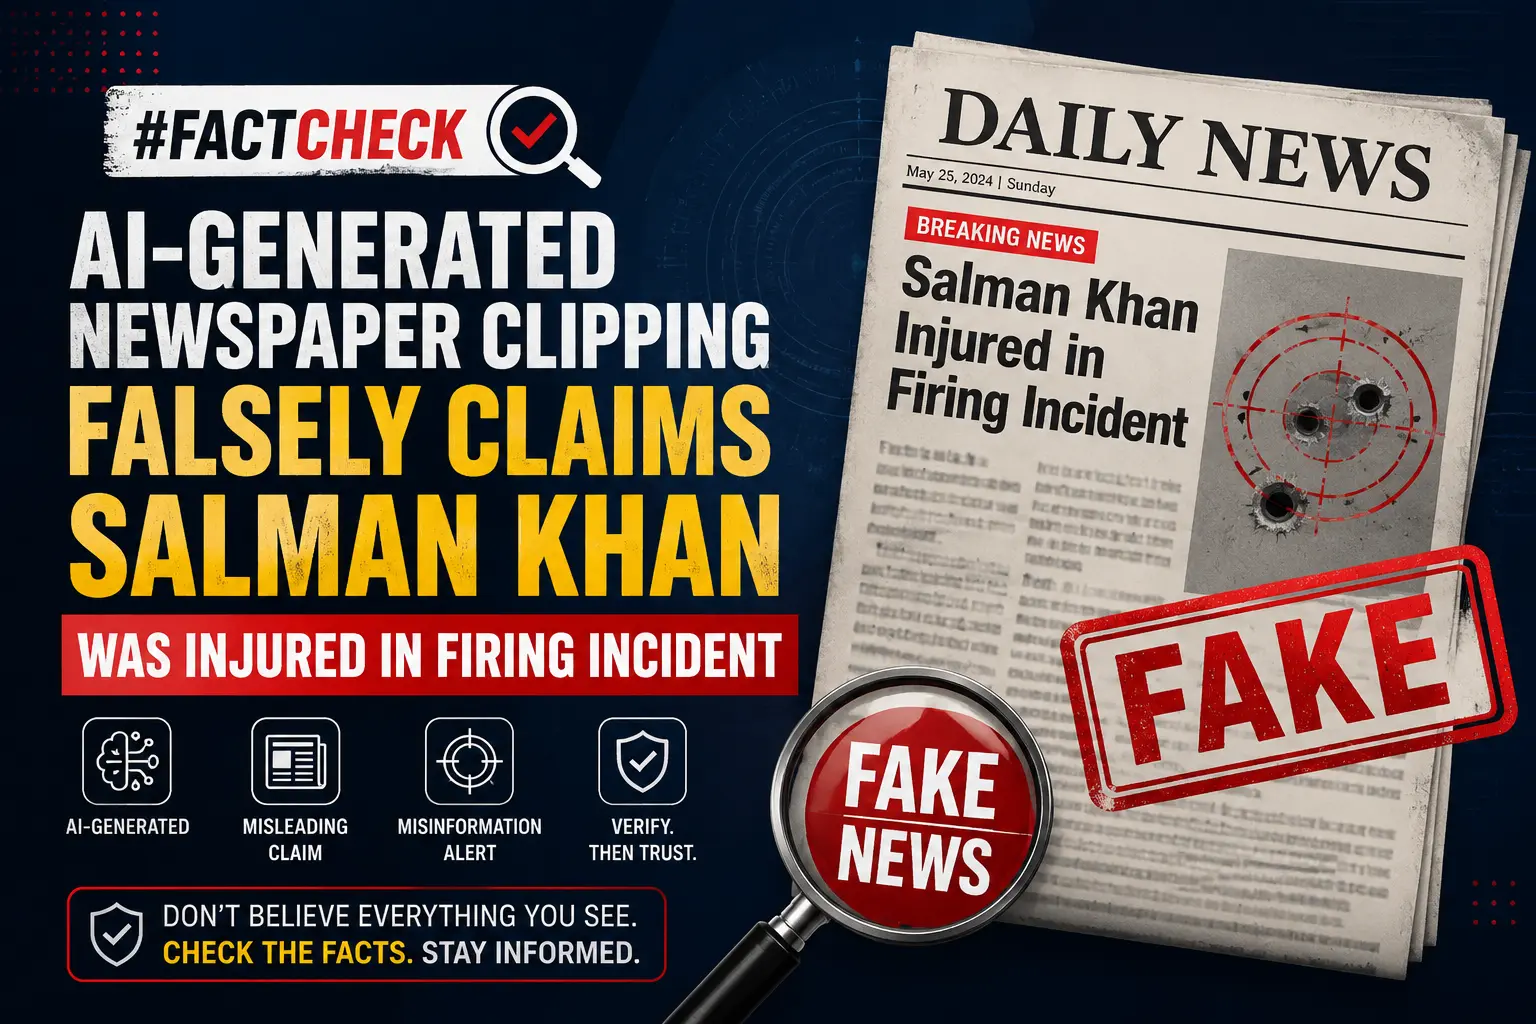
Executive Summary
A newspaper clipping is being widely shared on social media with the claim that more than 200 bullets were fired at actor Salman Khan’s vehicle, two of which allegedly hit him and left him seriously injured. CyberPeace Research Wing’s research found the viral claim to be false. The research revealed that Salman Khan is safe and healthy, and there is no credible information confirming any such firing incident. The probe further found that the alleged newspaper clipping circulating on social media was created using Artificial Intelligence (AI).
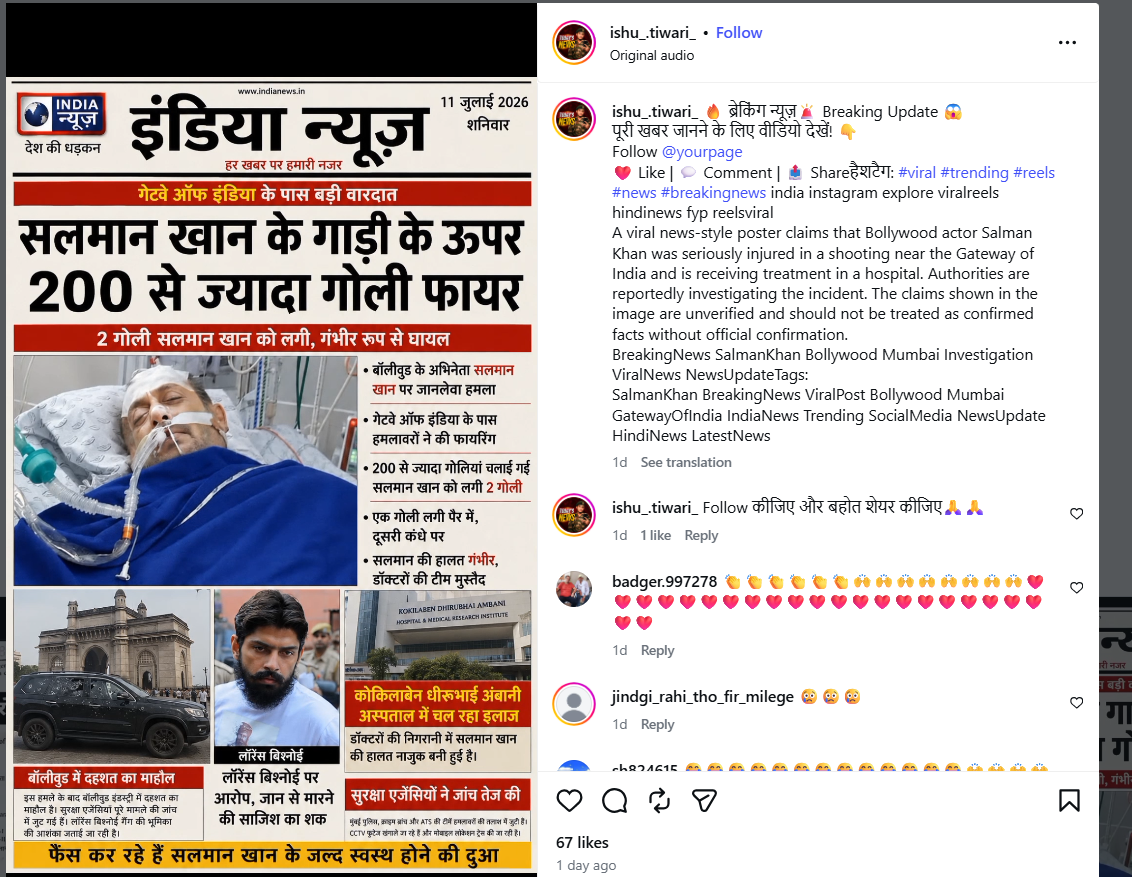
Claim
An Instagram user shared the viral newspaper clipping on July 11, 2026, claiming that more than 200 bullets were fired at Salman Khan’s vehicle, two bullets hit him, and he was seriously injured.
https://www.instagram.com/reel/DaqNtAfSGyI/
https://ghostarchive.org/archive/81qpF
Fact Check
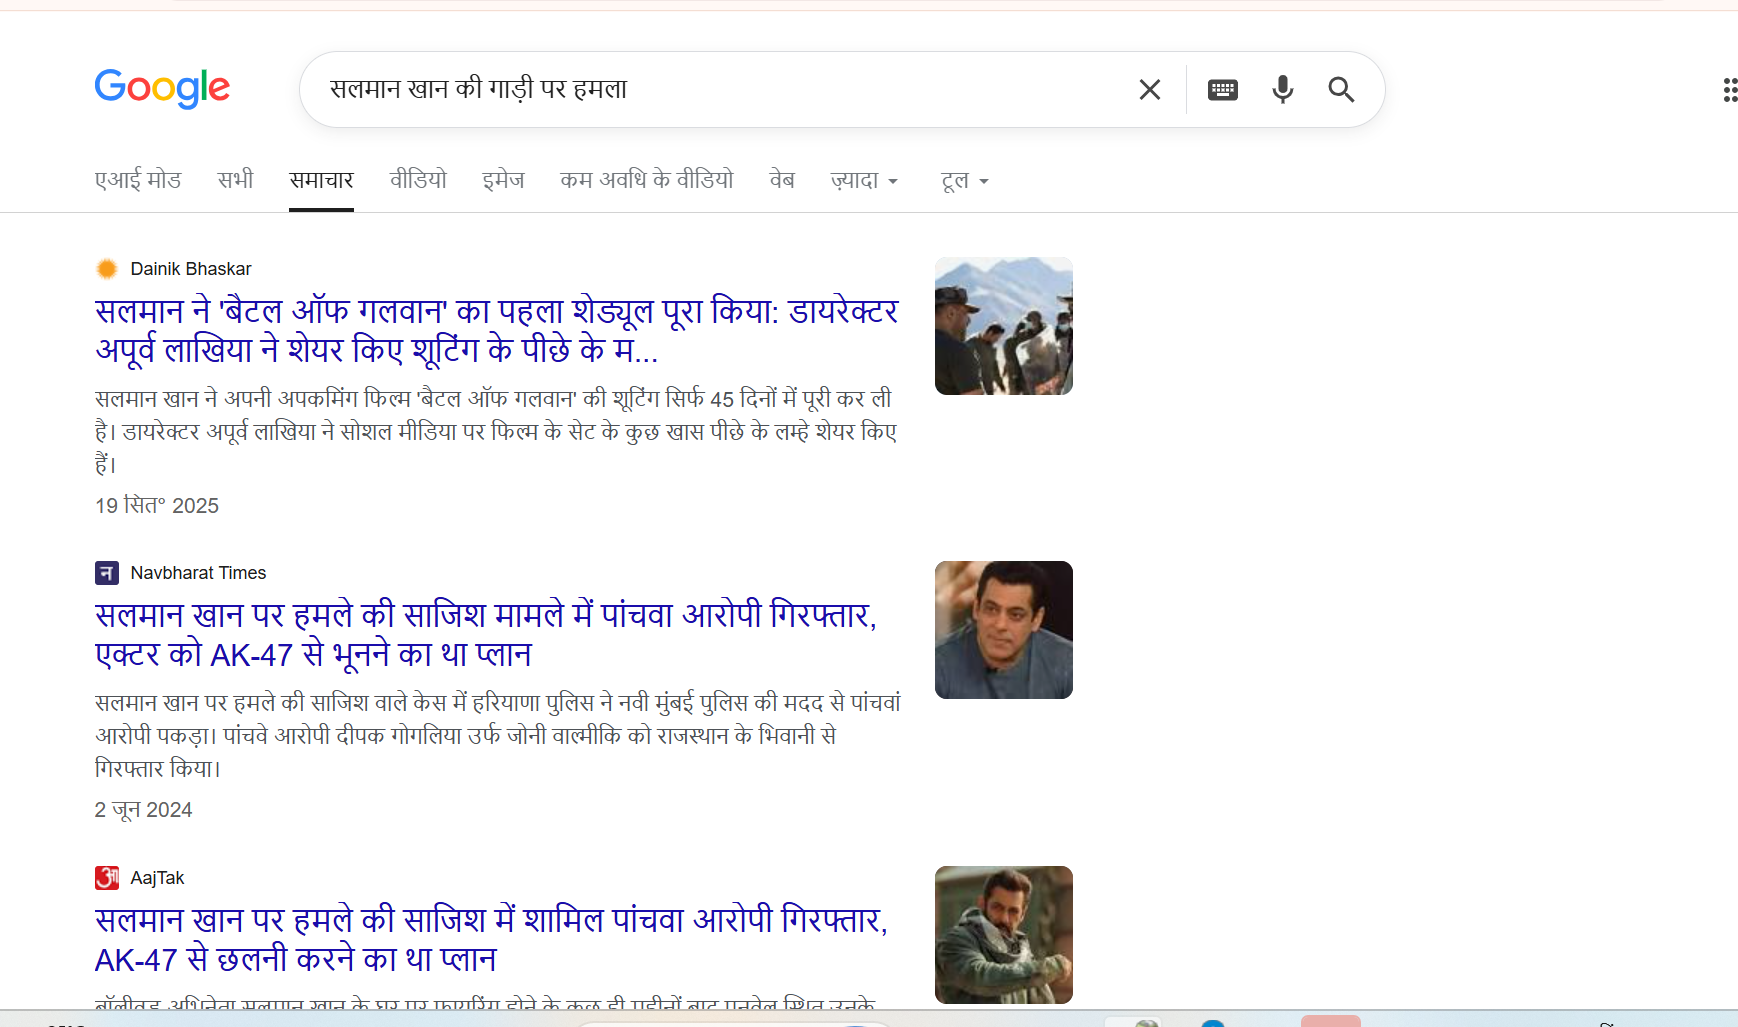
To verify the viral claim, we conducted a keyword-based search on Google. However, we did not find any credible media report confirming that Salman Khan was injured in any such firing incident.
During further research, we found a report published by Dainik Bhaskar on July 11, 2026. According to the report, actor Salman Khan sold another apartment located in Bandra, Mumbai. The report did not mention any incident involving an attack or injury.
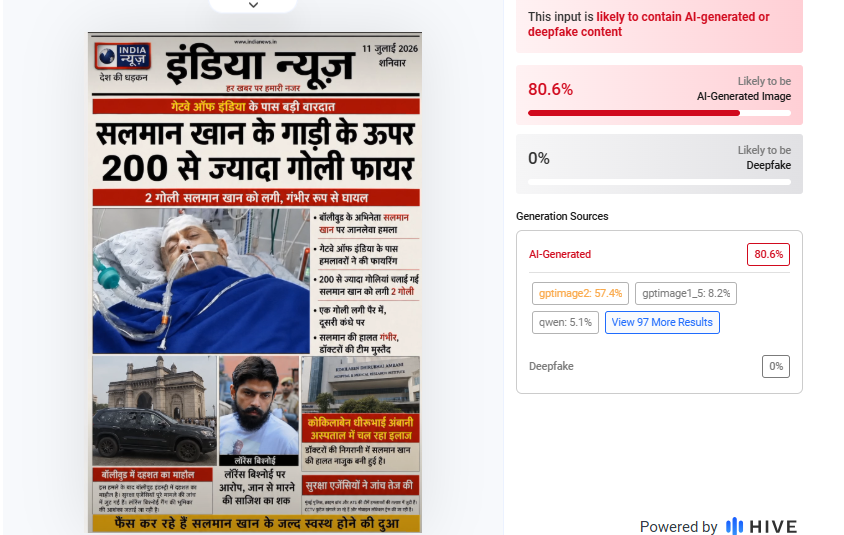
In the next step of the research, we analysed the viral newspaper clipping using the AI detection tool Hive Moderation. The tool’s analysis indicated an 80% probability that the newspaper clipping was AI-generated.
For further verification, the viral image was also checked using another AI detection tool, Sightengine. The tool’s result showed a 99% probability that the image was AI-generated.
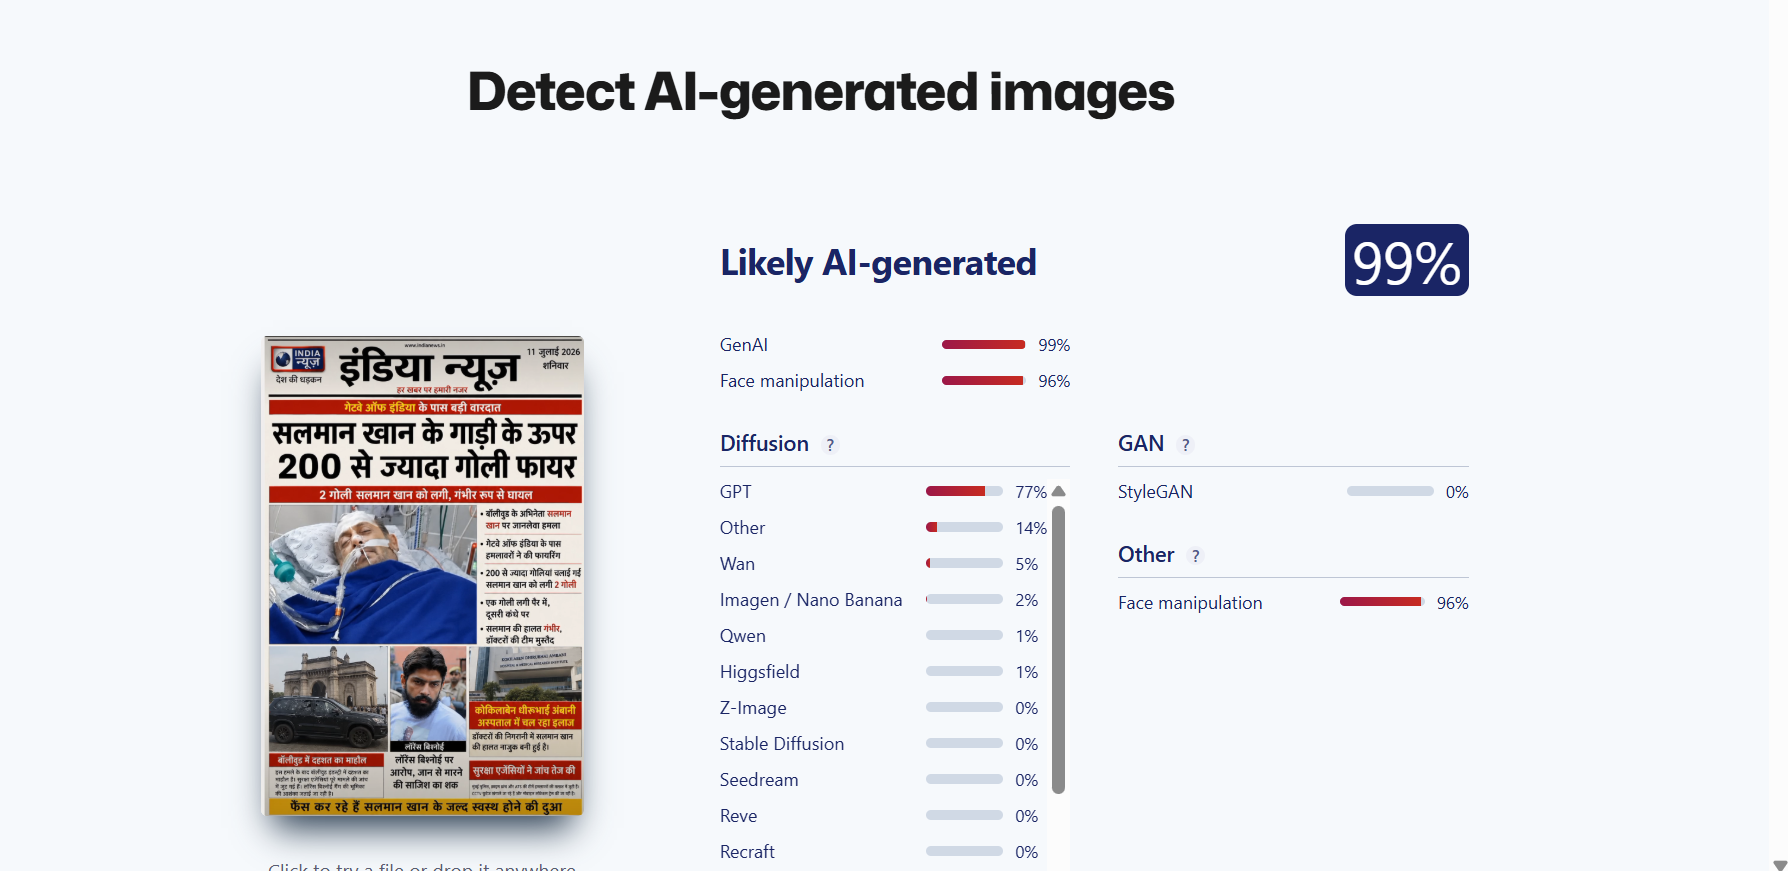
Conclusion
Our research found that the viral claim is false. There is no evidence that actor Salman Khan was injured in a firing incident or that more than 200 bullets were fired at his vehicle. The alleged newspaper clipping being circulated on social media was found to be AI-generated and is being shared with a false narrative

Introduction
The Data Security Council of India’s India Cyber Threat Report 2025 calculates that a staggering 702 potential attacks happened per minute on average in the country in 2024. Recent alleged data breaches on organisations such as Star Health, WazirX, Indian Council of Medical Research (ICMR), BSNL, etc. highlight the vulnerabilities of government organisations, critical industries, businesses, and individuals in managing their digital assets. India is the second most targeted country for cyber attacks globally, which warrants the development and adoption of cybersecurity governance frameworks essential for the structured management of cyber environments. The following global models offer valuable insights and lessons that can help strengthen cybersecurity governance.
Overview of Global Cybersecurity Governance Models
Cybersecurity governance frameworks provide a structured strategy to mitigate and address cyber threats. Different regions have developed their own governance models for cybersecurity, but they all emphasize risk management, compliance, and cross-sector collaboration for the protection of digital assets. Four such major models are:
- NIST CSF 2.0 (U.S.A): The National Institute of Standards and Technology Cyber Security Framework provides a flexible, voluntary, risk-based approach rather than a one-size-fits-all solution to manage cybersecurity risks. It endorses six core functions, which are: Govern, Identify, Protect, Detect, Respond, and Recover. This is a widely adopted framework used by both public and private sector organizations even outside the U.S.A.
- ISO/IEC 27001: This is a globally recognized standard developed jointly by the International Organization for Standardization (ISO) and the International Electrotechnical Commission (IEC). It provides a risk-based approach to help organizations of all sizes and types to identify, assess, and mitigate potential cybersecurity threats to Information Security Management Systems (ISMS) and preserve the confidentiality, integrity, and availability of information. Organizations can seek ISO 27001 certification to demonstrate compliance with laws and regulations.
- EU NIS2 Directive: The Network and Information Security Directive 2 (NIS2) is an updated EU cybersecurity law that imposes strict obligations on critical services providers in four overarching areas: risk management, corporate accountability, reporting obligations, and business continuity. It is the most comprehensive cybersecurity directive in the EU to date, and non-compliance may attract non-monetary remedies, administrative fines up to at least €10 million or 2% of the global annual revenue (whichever is higher), or even criminal sanctions for top managers.
- GDPR: The General Data Protection Regulation (GDPR)of the EU is a comprehensive data privacy law that also has major cybersecurity implications. It mandates that organizations must integrate cybersecurity into their data protection policies and report breaches within 72 hours, and it prescribes a fine of up to €20 million or 4% of global turnover for non-compliance.
India’s Cybersecurity Governance Landscape
In light of the growing nature of cyber threats, it is notable that the Indian government has taken comprehensive measures along with efforts by relevant agencies such as the Ministry of Electronics and Information Technology, Reserve Bank of India (RBI), National Payments Corporation (NPCI) and Indian Cyber Crime Coordination Centre (I4C), CERT-In. However, there is still a lack of an overarching cybersecurity governance framework or comprehensive law in this area. Multiple regulatory bodies in India oversee cybersecurity for various sectors. Key mechanisms are:
- CERT-In Guidelines: The Indian Computer Emergency Response Team, under the Ministry of Electronics and Information Technology (MeitY), is the nodal agency responsible for cybersecurity incident response, threat intelligence sharing, and capacity building. Organizations are mandated to maintain logs for 180 days and report cyber incidents to CERT-In within six hours of noticing them according to directions under the Information Technology Act, 2000 (IT Act).
- IT Act & DPDP Act: These Acts, along with their associated rules, lay down the legal framework for the protection of ICT systems in India. While some sections mandate that “reasonable” cybersecurity standards be followed, specifics are left to the discretion of the organisations. Enforcement frameworks are vague, which leaves sectoral regulators to fill the gaps.
- Sectoral regulations: The Reserve Bank of India (RBI), the Insurance Regulatory and Development Authority of India (IRDAI), the Department of Telecommunications, the Securities Exchange Board of India (SEBI), National Critical Information Infrastructure Protection Centre (NCIIPC) and other regulatory bodies require that cybersecurity standards be maintained by their regulated entities.
Lessons for India & Way Forward
As the world faces unprecedented security and privacy threats to its digital ecosystem, the need for more comprehensive cybersecurity policies, awareness, and capacity building has perhaps never been greater. While cybersecurity practices may vary with the size, nature, and complexity of an organization (hence “reasonableness” informing measures taken), there is a need for a centralized governance framework in India similar to NIST2 to unify sectoral requirements for simplified compliance and improve enforcement. India ranks 10th on the World Cybercrime Index and was found to be "specialising" in scams and mid-tech crimes- those which affect mid-range businesses and individuals the most. To protect them, India needs to strengthen its enforcement mechanisms across more than just the critical sectors. This can be explored by penalizing bigger organizations handling user data susceptible to breaches more stringently, creating an enabling environment for strong cybersecurity practices through incentives for MSMEs, and investing in cybersecurity workforce training and capacity building. Finally, there is a scope for increased public-private collaboration for real-time cyber intelligence sharing. Thus, a unified, risk-based national cybersecurity governance framework encompassing the current multi-pronged cybersecurity landscape would give direction to siloed efforts. It would help standardize best practices, streamline compliance, and strengthen overall cybersecurity resilience across all sectors in India.
References
- https://cdn.prod.website-files.com/635e632477408d12d1811a64/676e56ee4cc30a320aecf231_Cloudsek%20Annual%20Threat%20Landscape%20Report%202024%20(1).pdf
- https://strobes.co/blog/top-data-breaches-in-2024-month-wise/#:~:text=In%20a%20large%2Dscale%20data,emails%2C%20and%20even%20identity%20theft.
- https://www.google.com/search?q=nist+2.0&oq=nist+&gs_lcrp=EgZjaHJvbWUqBggBEEUYOzIHCAAQABiPAjIGCAEQRRg7MgYIAhBFGDsyCggDEAAYsQMYgAQyBwgEEAAYgAQyBwgFEAAYgAQyBwgGEAAYgAQyBggHEEUYPNIBCDE2MTJqMGo3qAIAsAIA&sourceid=chrome&ie=UTF-8
- https://www.iso.org/standard/27001
- https://nis2directive.eu/nis2-requirements/
- https://economictimes.indiatimes.com/tech/technology/india-ranks-number-10-in-cybercrime-study-finds/articleshow/109223208.cms?from=mdr

Introduction
Social media has emerged as a leading source of communication and information; its relevance cannot be ignored during natural disasters since it is relied upon by governments and disaster relief organisations as a tool for disseminating aid and relief-related resources and communications instantly. During disaster times, social media has emerged as a primary source for affected populations to access information on relief resources; community forums offering aid resources and official government channels for government aid have enabled efficient and timely administration of relief initiatives.
However, given the nature of social media, misinformation risks during natural disasters has also emerged as a primary concern that severely hampers aid administration during natural disasters. The disaster-disinformation network offers some sensationalised influential campaigns against communities at their most vulnerable. Victims who seek reliable resources during natural calamities often reach out to inhospitable campaigns and may experience delayed or lack of access to necessary healthcare, significantly impacting their recovery and survival. This delay can lead to worsening medical conditions and an increased death toll among those affected by the disaster. Victims may lack clear information on the appropriate agencies to seek assistance from, causing confusion and delays in receiving help.
Misinformation Threat Landscape during Natural Disaster
During the 2018 floods in Kerala, it was noted that a fake video on water leakage from the Mullaperyar Dam created panic among the citizens and negatively impacted the rescue operations. Similarly, in 2017, reports emerged claiming that Hurricane Irma had caused sharks to be displaced onto a Florida highway. Similar stories, accompanied by the same image, resurfaced following Hurricanes Harvey and Florence. The disaster-affected nation may face international criticism and fail to receive necessary support due to its perceived inability to manage the crisis effectively. This lack of confidence from the global community can further exacerbate the challenges faced by the nation, leaving it more vulnerable and isolated in its time of need.
The spread of misinformation through social media severely hinders the administration of aid and relief operations during natural disasters since it hinders first responders' efforts to counteract and reduce the spread of misinformation, rumours, and false information and declines public trust in government, media, and non-governmental organisations (NGOs), who are often the first point of contact for both victims and officials due to their familiarity with the region and the community. In Moldova, it was noted that foreign influence has exploited the ongoing drought to create divisions between the semi-autonomous regions of Transnistria and Gagauzia and the central government in Chisinau. News coverage critical of the government leverages economic and energy insecurities to incite civil unrest in this already unstable region. Additionally, First responders may struggle to locate victims and assist them to safety, complicating rescue operations. The inability to efficiently find and evacuate those in need can result in prolonged exposure to dangerous conditions and a higher risk of injury or death.
Further, international aid from other countries could be impeded, affecting the overall relief effort. Without timely and coordinated support from the global community, the disaster response may be insufficient, leaving many needs unmet. Further, misinformation also impedes military, reducing the effectiveness of rescue and relief operations. Military assistance often plays a crucial role in disaster response, and any delays can hinder efforts to provide immediate and large-scale aid.
Misinformation also creates problems of allocation of relief resources to unaffected areas which resultantly impacts aid processes for regions in actual need. Following the April 2015 earthquake in Nepal, a Facebook post claimed that 300 houses in Dhading needed aid. Shared over 1,000 times, it reached around 350,000 people within 48 hours. The originator aimed to seek help for Ward #4’s villagers via social media. Given the average Facebook user has 350 contacts, the message was widely viewed. However, the need had already been reported on quakemap.org, a crisis-mapping database managed by Kathmandu Living Labs, a week earlier. Helping Hands, a humanitarian group was notified on May 7, and by May 11, Ward #4 received essential food and shelter. The re-sharing and sensationalisation of outdated information could have wasted relief efforts since critical resources would have been redirected to a region that had already been secured.
Policy Recommendations
Perhaps the most important step in combating misinformation during natural disasters is the increasing public education and the rapid, widespread dissemination of early warnings. This was best witnessed in the November 1970 tropical cyclone in southeastern Bangladesh, combined with a high tide, struck southeastern Bangladesh, leaving more than 300,000 people dead and 1.3 million homeless. In May 1985, when a comparable cyclone and storm surge hit the same area, local dissemination of disaster warnings was much improved and the people were better prepared to respond to them. The loss of life, while still high (at about 10,000), the numbers were about 3% of that in 1970. On a similar note, when a devastating cyclone struck the same area of Bangladesh in May 1994, fewer than 1,000 people died. In India, the 1977 cyclone in Andra Pradesh killed 10,000 people, but a similar storm in the same area 13 years later killed only 910. The dramatic difference in mortalities was owed to a new early-warning system connected with radio stations to alert people in low-lying areas.
Additionally, location-based filtering for monitoring social media during disasters is considered as another best practice to curb misinformation. However, agencies should be aware that this method may miss local information from devices without geolocation enabled. A 2012 Georgia Tech study found that less than 1.4 percent of Twitter content is geolocated. Additionally, a study by Humanity Road and Arizona State University on Hurricane Sandy data indicated a significant decline in geolocation data during weather events.
Alternatively, Publish frequent updates to promote transparency and control the message. In emergency management and disaster recovery, digital volunteers—trusted agents who provide online support—can assist overwhelmed on-site personnel by managing the vast volume of social media data. Trained digital volunteers help direct affected individuals to critical resources and disseminate reliable information.
Enhancing the quality of communication requires double-verifying information to eliminate ambiguity and reduce the impact of misinformation, rumors, and false information must also be emphasised. This approach helps prevent alert fatigue and "cry wolf" scenarios by ensuring that only accurate, relevant information is disseminated. Prioritizing ground truth over assumptions and swiftly releasing verified information or acknowledging the situation can bolster an agency's credibility. This credibility allows the agency to collaborate effectively with truth amplifiers. Prebunking and Debunking methods are also effective way to counter misinformation and build cognitive defenses to recognise red flags. Additionally, evaluating the relevance of various social media information is crucial for maintaining clear and effective communication.
References
- https://www.nature.com/articles/s41598-023-40399-9#:~:text=Moreover%2C%20misinformation%20can%20create%20unnecessary,impacting%20the%20rescue%20operations29.
- https://www.redcross.ca/blog/2023/5/why-misinformation-is-dangerous-especially-during-disasters
- https://www.soas.ac.uk/about/blog/disinformation-during-natural-disasters-emerging-vulnerability
- https://www.dhs.gov/sites/default/files/publications/SMWG_Countering-False-Info-Social-M dia-Disasters-Emergencies_Mar2018-508.pdf
