
#FactCheck - Viral Video of US President Biden Dozing Off during Television Interview is Digitally Manipulated and Inauthentic
Executive Summary:
The claim of a video of US President Joe Biden dozing off during a television interview is digitally manipulated . The original video is from a 2011 incident involving actor and singer Harry Belafonte. He seems to fall asleep during a live satellite interview with KBAK – KBFX - Eyewitness News. Upon thorough analysis of keyframes from the viral video, it reveals that US President Joe Biden’s image was altered in Harry Belafonte's video. This confirms that the viral video is manipulated and does not show an actual event involving President Biden.

Claims:
A video shows US President Joe Biden dozing off during a television interview while the anchor tries to wake him up.


Fact Check:
Upon receiving the posts, we watched the video then divided the video into keyframes using the inVid tool, and reverse-searched one of the frames from the video.
We found another video uploaded on Oct 18, 2011 by the official channel of KBAK - KBFX - Eye Witness News. The title of the video reads, “Official Station Video: Is Harry Belafonte asleep during live TV interview?”

The video looks similar to the recent viral one, the TV anchor could be heard saying the same thing as in the viral video. Taking a cue from this we also did some keyword searches to find any credible sources. We found a news article posted by Yahoo Entertainment of the same video uploaded by KBAK - KBFX - Eyewitness News.

Upon thorough investigation from reverse image search and keyword search reveals that the recent viral video of US President Joe Biden dozing off during a TV interview is digitally altered to misrepresent the context. The original video dated back to 2011, where American Singer and actor Harry Belafonte was the actual person in the TV interview but not US President Joe Biden.
Hence, the claim made in the viral video is false and misleading.
Conclusion:
In conclusion, the viral video claiming to show US President Joe Biden dozing off during a television interview is digitally manipulated and inauthentic. The video is originally from a 2011 incident involving American singer and actor Harry Belafonte. It has been altered to falsely show US President Joe Biden. It is a reminder to verify the authenticity of online content before accepting or sharing it as truth.
- Claim: A viral video shows in a television interview US President Joe Biden dozing off while the anchor tries to wake him up.
- Claimed on: X (Formerly known as Twitter)
- Fact Check: Fake & Misleading

Related Blogs
Introduction
We inhabit an era where digital connectivity, while empowering, has also unleashed a relentless tide of cyber vulnerabilities, where personal privacy is constantly threatened, and crimes like sextortion are the perfect example of the sinister side of our hyperconnected world. Social media platforms, instant messaging apps, and digital content-sharing tools have all grown rapidly, changing how people communicate with one another and making it harder to distinguish between the private and public domains. The rise of sophisticated cybercrimes that use the very tools meant to connect us is the price paid for this unparalleled convenience. Sextortion, a portmanteau of “sex’ and “extortion”, stands out among them as a particularly pernicious kind of internet exploitation. Under the threat of disclosing their private information, photos, or videos, people are forced to engage in sexual behaviours or provide intimate content. Sextortion’s psychological component is what makes it particularly harmful, it feeds on social stigma, shame, and fear, which discourage victims from reporting the crime and feed the cycle of victimisation and silence. This cybercrime targets vulnerable people from all socioeconomic backgrounds and is not limited by age, gender, or location.
The Economy of Shame: Sextortion as a Cybercrime Industry
A news report from June 03, 2025, reveals a sextortion racket busted in Delhi, where a money trail of over Rs. 5 crore was identified by different teams of the Crime branch. From synthetic financial identities to sextortion and other cyber frauds, a recipe for a sophisticated cybercrime chain was found. To believe this is an aberration is to overlook the reality that it is symptomatic of a much wider and largely uncharted criminal framework. According to the FBI’s 2024 IC3 report, “extortion (including sextortion)” has skyrocketed to 86,415 complaints with losses of $143 million reported in the United States (US) alone. This indicates that coercive image-based threats are no longer an isolated cybercrime but an everyday occurrence. Sextortion is no longer an isolated cybercrime; it has metamorphosed into a systematic, industrialised criminal enterprise. Another news report dated 19th July, 2025, where Delhi Police has detained four people suspected of participating in a sextortion scheme that targeted a resident of the Bhagwanpur Khera neighbourhood of Shahdara. The suspected people were allegedly arrested on a complaint wherein the victim was manipulated and fell prey to a dating site.
The threat is amplified by the usage of deepfake technology, which allows offenders to create obscene content that looks believable. The approach, which relies on the stigma attached to sexual imagery in conservative societies like India, is that victims frequently give in to requests out of fear of damaging their reputations. The combination of cybercrime and cutting-edge technology highlights the lopsided power that criminals possess, leaving victims defenceless and law enforcement unable to keep up.
Legal Remedies and the Evolving Battle Against Sextortion
Given the complexity of these crimes, India has recognised sextortion and similar cyber-enabled financial crimes under a number of legal frameworks. A change to recognising cyber-enabled sexual exploitation as an organised criminal business is shown by the introduction of specific provisions like Section 111 in the Bhartiya Nyaya Sanhita (BNS), 2023, which classifies organised cybercrimes including extortion and frauds which fall under its expansive interpretation, as a serious offence. Similarly, Section 318 (2) criminalises cheating with a maximum sentence of three years in prison or a fine, whereas Section 336 (2) makes digital forgery a crime with a maximum sentence with a maximum sentence of two years in prison or a fine. In addition to these regulations, cheating by personation through computer resources is punishable by the Information Technology Act, 2000, specifically Section 66D, which carries a maximum sentence of three years in prison and a maximum fine of Rs. 1 lakh. Due to issues with attribution, cross-border jurisdiction, and the discreet nature of digital evidence, enforcement is still inconsistent even with current statutory restrictions.
The government and its agencies recognise that laws achieve real impact only when backed by awareness initiatives and accessible, localised mechanisms for redressal. Several Indian states and the Department of Telecommunications launched numerous campaigns to educate the public about and safeguard their mobile communication assets against identity theft, financial fraud, and cyberscams. Initiatives like Cyber Saathi Initiative and Cyber Dost by MHA, with the goal of improving forensic and victim reporting skills.
Conclusion
At CyberPeace, we understand that the best defence against online abuse is prevention. Our goal is to provide people with the information and resources to identify, avoid and report sextortion attempts like CyberPeace Helpline and organise awareness campaigns on safe digital habits. In order to remain updated with the constantly looming danger, our research and policy advocacy also focus on developing more robust legal and technological safeguards.
To every reader: think before you share, secure your accounts, and never let shame silence you. If you or someone you know becomes a victim, report it immediately, help is available, and justice is possible. Together we can reclaim the internet as a space of trust, not terror.
References
- https://www.hindustantimes.com/india-news/delhi-police-busts-sextortion-cyberfraud-rackets-6-held-101748959601825.html
- https://timesofindia.indiatimes.com/city/delhi/delhi-police-arrests-four-for-sextortion-and-blackmail-in-shahdara/articleshow/122767656.cms
- https://cdn.ncw.gov.in/wp-content/uploads/2025/05/CyberSaheli.pdf

Introduction
Taj Hotels Group is well known for its luxurious ambience and old-world grace and charm, blended with contemporary comforts and amenities for its guests or customers. But what can make all the netizens perplexed is the recent data breach incident which took place in Tata-owned Taj hotels. The hotel suffer from a data breach that compromises nearly 1.5 million customers' data which includes addresses, membership IDs, mobile numbers and other personally identifiable information, according to sources. This news was brought to light which raised concerns about the privacy and data protection of personal data of individuals. We are living in a space influenced by advanced technology and digital communication which throws a concern or challenge to secure the personal information of individuals.
Unveiling the incident
Tata-owned Taj Hotels group has suffered a data breach that compromise information of over 1.5 million customers, according to a news report. A bad actor or entity going by the name “Dnacookies” claimed data set contains data from the 2014-2020 period and has not been disclosed anywhere till now. Such personal data includes name, address, customer ID, mobile number and other personally identifiable information. This shows the risks or challenges of data protection and security. The incidents raise an alarm about the risks and vulnerabilities that might be faced even by the big corporate giants. The bad actor with the handle “Dnacookies” also demanded a ransom of a sum of about Rs 4.16 lakh from the Taj hotel group. In response to the incident, a spokesperson from the concerned hotel group said that we have been made aware of someone claiming possession of a limited data customer data set, which is non-sensitive in nature. Investigation is underway and relevant authorities have been notified about the incident.
A demand for ransom
The report from CNBC-TV18 clears that the bad actor not only purloined the data but also demanded around 4.16 lakh as a ransom for the database. Along with this, the bad actor kept three conditions ahead. Firstly there has to be a middleman for a negotiable deal secondly the data cannot be split either the entire data has to be taken with the ransom demand or no data at all. Thirdly additional samples of data will not be provided. Further, the spokesperson of Indian Hotel Company Limited mentioned that they have been escalated with the fact that someone is claiming authority in a limited data set. The bad actor claimed that the database contains information from 2014- 2020 which has been kept confidential till now. The audacity of the bad actor went to such an extent that the sample containing one thousand rows of unique entries from the bad actor dataset was also provided by the bad actor as proof of the deed. This incident underlines the growing threat in cyberspace and the urgency for individuals, organizations or entities to priorities data security measures and maintain cyber resilience.
Personal Data on Stake
Such data is the personal information of the individuals and also constitutes the personal tastes and preferences of individuals which can be exploited. The biggest gush of winds the hotel and individuals face by such a data breach is not only the volume of data compromised but also the potential ways it can get misused and exploited against the hotel or its customers by cyber crooks. This paves the way for cybercriminals to put forward any demand knowing the sensitivity of the data. Followed by creating a dilemmatic situation for the affected entities to either accept the ransom demands or to stand against ransom. Since the risks are high, going ahead with any of these situations can have an adverse impact on the security of personal data. The organisation or entities holding the personal data need to make sure that data under their realm is well protected and secured.
While the organisation has to sail through the aftermath of this breach, such incidents also pose a challenge for the organisation to maintain the trust and reputation of the organization since these incidents question the cyber security posture of the organisation. It is suggested to be transparent with its stakeholders, and open about the vulnerabilities and steps taken against this. They should also discuss the amplified step added for safeguarding their customer's personal data. Since Taj is well known for its out-of-the-box luxury and for providing comfort to its customers it should take a step ahead to reinforce its digital infrastructure to ensure the security of data.
Digital Personal Data Protection Act, 2023
The newly enacted Digital Personal Data Act, 2023 put certain obligations on data fiduciaries to take reasonable measures to maintain the security of personal data. The Act also requires to inform about the data breach to the data protection board constituted under the Act. The Act aims to protect the individual's digital personal data. The Act casts certain obligations on data principals and data fiduciaries. The Act provides penalty upto 250 crores in case of a data breach. The Act aims to provide consent-based data collection techniques. The Act also establishes the Data Protection Board to ensure compliance with the provisions of the Act and address grievances.
Conclusion
Data breach in such a big giant in the market serves as an alarming concern to be more cautious and proactively take precautionary measures to protect the security of data and compliance with data protection laws and regulations. We are living in an era where digital security is as important as the basic fundamental rights of an individual. Taj Hotels Group has actively taken steps to handle the aftermath of the data breach by informing the incident to law enforcement agencies and taking necessary steps. It is also on our part to be more aware, and vigilant about our personal data. Entities need to ensure compliance and measures to protect personal data and overall ensure a true cyber-safe & digital environment.
References

Introduction
Recent advances in space exploration and technology have increased the need for space laws to control the actions of governments and corporate organisations. India has been attempting to create a robust legal framework to oversee its space activities because it is a prominent player in the international space business. In this article, we’ll examine India’s current space regulations and compare them to the situation elsewhere in the world.
Space Laws in India
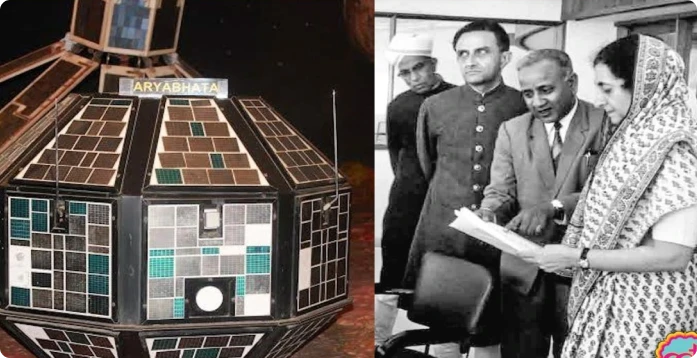
India started space exploration with Aryabhtta, the first satellite, and Rakesh Sharma, the first Indian astronaut, and now has a prominent presence in space as many international satellites are now launched by India. NASA and ISRO work closely on various projects
India currently lacks any space-related legislation. Only a few laws and regulations, such as the Indian Space Research Organisation (ISRO) Act of 1969 and the National Remote Sensing Centre (NRSC) Guidelines of 2011, regulate space-related operations. However, more than these rules and regulations are essential to control India’s expanding space sector. India is starting to gain traction as a prospective player in the global commercial space sector. Authorisation, contracts, dispute resolution, licencing, data processing and distribution related to earth observation services, certification of space technology, insurance, legal difficulties related to launch services, and stamp duty are just a few of the topics that need to be discussed. The necessary statute and laws need to be updated to incorporate space law-related matters into domestic laws.
India’s Space Presence
Space research activities were initiated in India during the early 1960s when satellite applications were in experimental stages, even in the United States. With the live transmission of the Tokyo Olympic Games across the Pacific by the American Satellite ‘Syncom-3’ demonstrating the power of communication satellites, Dr Vikram Sarabhai, the founding father of the Indian space programme, quickly recognised the benefits of space technologies for India.
As a first step, the Department of Atomic Energy formed the INCOSPAR (Indian National Committee for Space Research) under the leadership of Dr Sarabhai and Dr Ramanathan in 1962. The Indian Space Research Organisation (ISRO) was formed on August 15, 1969. The prime objective of ISRO is to develop space technology and its application to various national needs. It is one of the six largest space agencies in the world. The Department of Space (DOS) and the Space Commission were set up in 1972, and ISRO was brought under DOS on June 1, 1972.
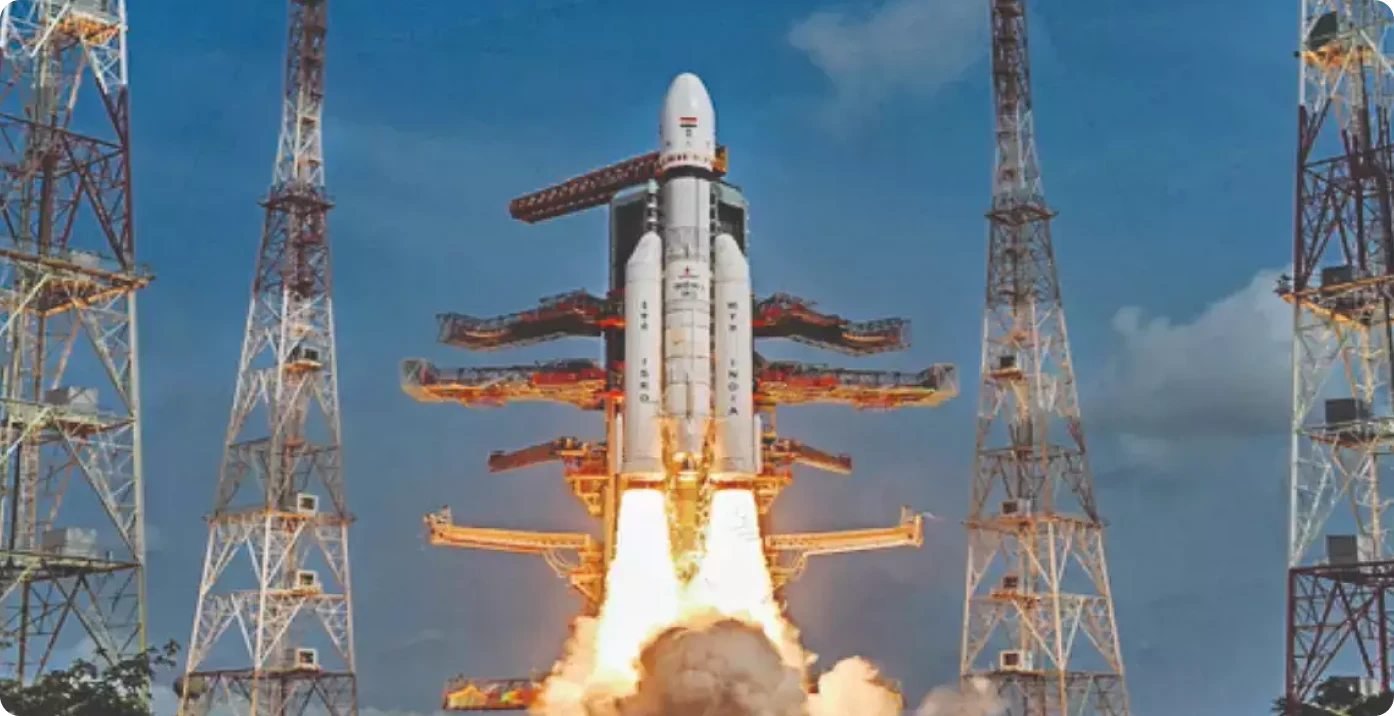
Since its inception, the Indian space programme has been orchestrated well. It has three distinct elements: satellites for communication and remote sensing, the space transportation system and application programmes. Two major operational systems have been established – the Indian National Satellite (INSAT) for telecommunication, television broadcasting, and meteorological services and the Indian Remote Sensing Satellite (IRS) for monitoring and managing natural resources and Disaster Management Support.
Global Scenario
The global space race has been on and ever since the moon landing in 1969, and it has now transformed into the new cold war among developed and developing nations. The interests and assets of a nation in space need to be safeguarded by the help of effective and efficient policies and internationally ratified laws. All nations with a presence in space do not believe in good for all policy, thus, preventive measures need to be incorporated into the legal system. A thorough legal framework for space activities is being developed by the United Nations Office for Outer Space Affairs (UNOOSA). The “Outer Space Treaty,” a collection of five international agreements on space law, establishes the foundation of international space law. The agreements address topics such as the peaceful use of space, preventing space from becoming militarised, and who is responsible for damage caused by space objects. Well-established space laws govern both the United States and the United Kingdom. The National Aeronautics and Space Act, which was passed in the US in 1958 and established the National Aeronautics and Space Administration (NASA) to oversee national space programmes, is in place there. The Outer Space Act of 1986 governs how UK citizens and businesses can engage in space activity.

Conclusion
India must create a thorough legal system to govern its space endeavours. In the space sector, there needs to be a legal framework to avoid ambiguity and confusion, which may have detrimental effects. The Pacific use of space for the benefit of humanity should be covered by domestic space legislation in India. The overall scenario demonstrates the requirement for a clearly defined legal framework for the international acknowledgement of a nation’s space activities. India is fifth in the world for space technology, which is an impressive accomplishment, and a strong legal system will help India maintain its place in the space business.
