
#FactCheck - "Viral Video Misleadingly Claims Surrender to Indian Army, Actually Shows Bangladesh Army”
Executive Summary:
A viral video has circulated on social media, wrongly showing lawbreakers surrendering to the Indian Army. However, the verification performed shows that the video is of a group surrendering to the Bangladesh Army and is not related to India. The claim that it is related to the Indian Army is false and misleading.

Claims:
A viral video falsely claims that a group of lawbreakers is surrendering to the Indian Army, linking the footage to recent events in India.


Fact Check:
Upon receiving the viral posts, we analysed the keyframes of the video through Google Lens search. The search directed us to credible news sources in Bangladesh, which confirmed that the video was filmed during a surrender event involving criminals in Bangladesh, not India.

We further verified the video by cross-referencing it with official military and news reports from India. None of the sources supported the claim that the video involved the Indian Army. Instead, the video was linked to another similar Bangladesh Media covering the news.

No evidence was found in any credible Indian news media outlets that covered the video. The viral video was clearly taken out of context and misrepresented to mislead viewers.
Conclusion:
The viral video claiming to show lawbreakers surrendering to the Indian Army is footage from Bangladesh. The CyberPeace Research Team confirms that the video is falsely attributed to India, misleading the claim.
- Claim: The video shows miscreants surrendering to the Indian Army.
- Claimed on: Facebook, X, YouTube
- Fact Check: False & Misleading

Related Blogs

Introduction
According to Statista, the global artificial intelligence software market is forecast to grow by around 126 billion US dollars by 2025. This will include a 270% increase in enterprise adoption over the past four years. The top three verticals in the Al market are BFSI (Banking, Financial Services, and Insurance), Healthcare & Life Sciences, and Retail & e-commerce. These sectors benefit from vast data generation and the critical need for advanced analytics. Al is used for fraud detection, customer service, and risk management in BFSI; diagnostics and personalised treatment plans in healthcare; and retail marketing and inventory management.
The Chairperson of the Competition Commission of India’s Chief, Smt. Ravneet Kaur raised a concern that Artificial Intelligence has the potential to aid cartelisation by automating collusive behaviour through predictive algorithms. She explained that the mere use of algorithms cannot be anti-competitive but in case the algorithms are manipulated, then that is a valid concern about competition in markets.
This blog focuses on how policymakers can balance fostering innovation and ensuring fair competition in an AI-driven economy.
What is the Risk Created by AI-driven Collusion?
AI uses predictive algorithms, and therefore, they could lead to aiding cartelisation by automating collusive behaviour. AI-driven collusion could be through:
- The use of predictive analytics to coordinate pricing strategies among competitors.
- The lack of human oversight in algorithm-induced decision-making leads to tacit collusion (competitors coordinate their actions without explicitly communicating or agreeing to do so).
AI has been raising antitrust concerns and the most recent example is the partnership between Microsoft and OpenAI, which has raised concerns among other national competition authorities regarding potential competition law issues. While it is expected that the partnership will potentially accelerate innovation, it also raises concerns about potential anticompetitive effects such as market foreclosure or the creation of barriers to entry for competitors and, therefore, has been under consideration in the German and UK courts. The problem here is in detecting and proving whether collusion is taking place.
The Role of Policy and Regulation
The uncertainties induced by AI regarding its effects on competition create the need for algorithmic transparency and accountability in mitigating the risks of AI-driven collusion. It leads to the need to build and create regulatory frameworks that mandate the disclosure of algorithmic methodologies and establish a set of clear guidelines for the development of AI and its deployment. These frameworks or guidelines should encourage an environment of collaboration between competition watchdogs and AI experts.
The global best practices and emerging trends in AI regulation already include respect for human rights, sustainability, transparency and strong risk management. The EU AI Act could serve as a model for other jurisdictions, as it outlines measures to ensure accountability and mitigate risks. The key goal is to tailor AI regulations to address perceived risks while incorporating core values such as privacy, non-discrimination, transparency, and security.
Promoting Innovation Without Stifling Competition
Policymakers need to ensure that they balance regulatory measures with innovation scope and that the two priorities do not hinder each other.
- Create adaptive and forward-thinking regulatory approaches to keep pace with technological advancements that take place at the pace of development and allow for quick adjustments in response to new AI capabilities and market behaviours.n
- Competition watchdogs need to recruit domain experts to assess competition amid rapid changes in the technology landscape. Create a multi-stakeholder approach that involves regulators, industry leaders, technologists and academia who can create inclusive and ethical AI policies.
- Businesses can be provided incentives such as recognition through certifications, grants or benefits in acknowledgement of adopting ethical AI practices.
- Launch studies such as the CCI’s market study to study the impact of AI on competition. This can lead to the creation of a driving force for sustainable growth with technological advancements.
Conclusion: AI and the Future of Competition
We must promote a multi-stakeholder approach that enhances regulatory oversight, and incentivising ethical AI practices. This is needed to strike a delicate balance that safeguards competition and drives sustainable growth. As AI continues to redefine industries, embracing collaborative, inclusive, and forward-thinking policies will be critical to building an equitable and innovative digital future.
The lawmakers and policymakers engaged in the drafting of the frameworks need to ensure that they are adaptive to change and foster innovation. It is necessary to note that fair competition and innovation are not mutually exclusive goals, they are complementary to each other. Therefore, a regulatory framework that promotes transparency, accountability, and fairness in AI deployment must be established.
References
- https://www.thehindu.com/sci-tech/technology/ai-has-potential-to-aid-cartelisation-fair-competition-integral-for-sustainable-growth-cci-chief/article69041922.ece
- https://www.marketsandmarkets.com/Market-Reports/artificial-intelligence-market-74851580.html
- https://www.ey.com/en_in/insights/ai/how-to-navigate-global-trends-in-artificial-intelligence-regulation#:~:text=Six%20regulatory%20trends%20in%20Artificial%20Intelligence&text=These%20include%20respect%20for%20human,based%20approach%20to%20AI%20regulation.
- https://www.business-standard.com/industry/news/ai-has-potential-to-aid-fair-competition-for-sustainable-growth-cci-chief-124122900221_1.html
Executive Summary
A picture is rapidly going viral on social media, showing Indian cricketer Virat Kohli and actor Anushka Sharma having breakfast together. Users are sharing this photo, presenting it as a "candid" (real) moment.
Research by the CyberPeace Research Wing revealed that the photo of Virat Kohli and Anushka Sharma having breakfast is completely fake. This image does not depict a real moment, but has been created using Artificial Intelligence (AI).
Claim
A picture is rapidly going viral on social media, showing Indian cricketer Virat Kohli and actor Anushka Sharma having breakfast together. Users are sharing this photo, presenting it as a "candid" (real) moment.
https://www.facebook.com/reel/951138134598230
Fact Check
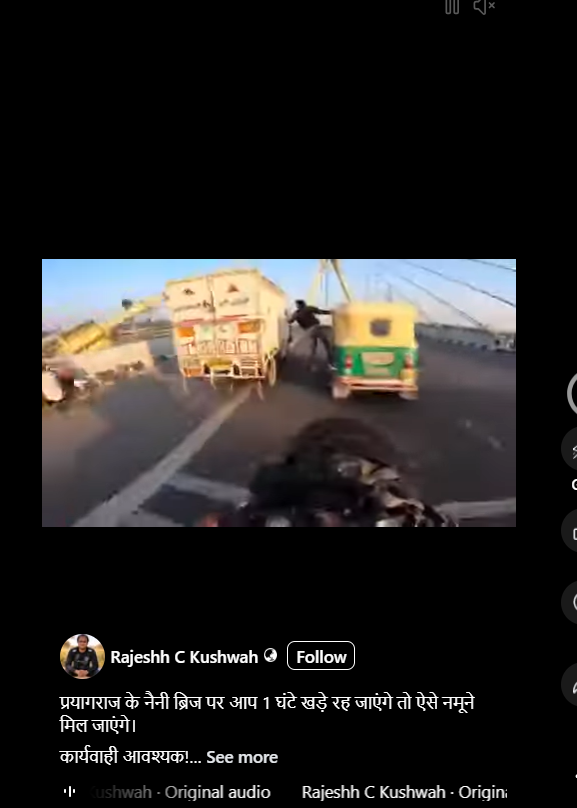
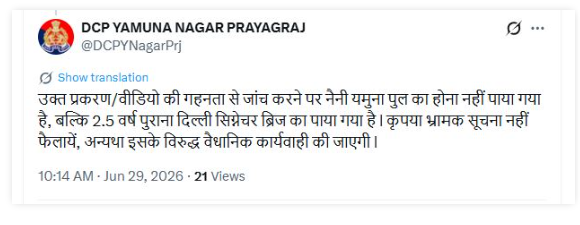
We extracted several keyframes from the viral video and searched them using the Google Lens tool. We found that this video was also quite viral on X (formerly Twitter). Responding to users, the official X handle of DCP Yamuna Nagar, Prayagraj, stated, “Upon a detailed research of the said matter/video, it has been found that it is not from the Naini Yamuna Bridge, but is a 2.5-year-old video from Delhi’s Signature Bridge. Please do not spread misleading information, otherwise legal action will be initiated against it.”
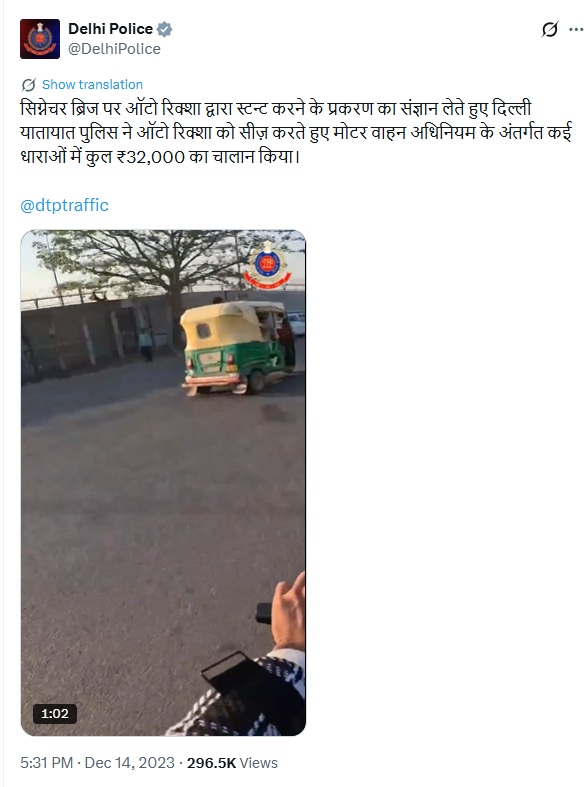
During our search, we found a post on the official X handle of the Delhi Police. Sharing the viral video, they wrote that taking cognizance of the auto-rickshaw stunt incident on the Signature Bridge, the Delhi Traffic Police seized the auto-rickshaw and issued a challan totaling ₹32,000 under various sections of the Motor Vehicles Act.
https://x.com/DelhiPolice/status/1735268792434057352?s=20
Conclusion
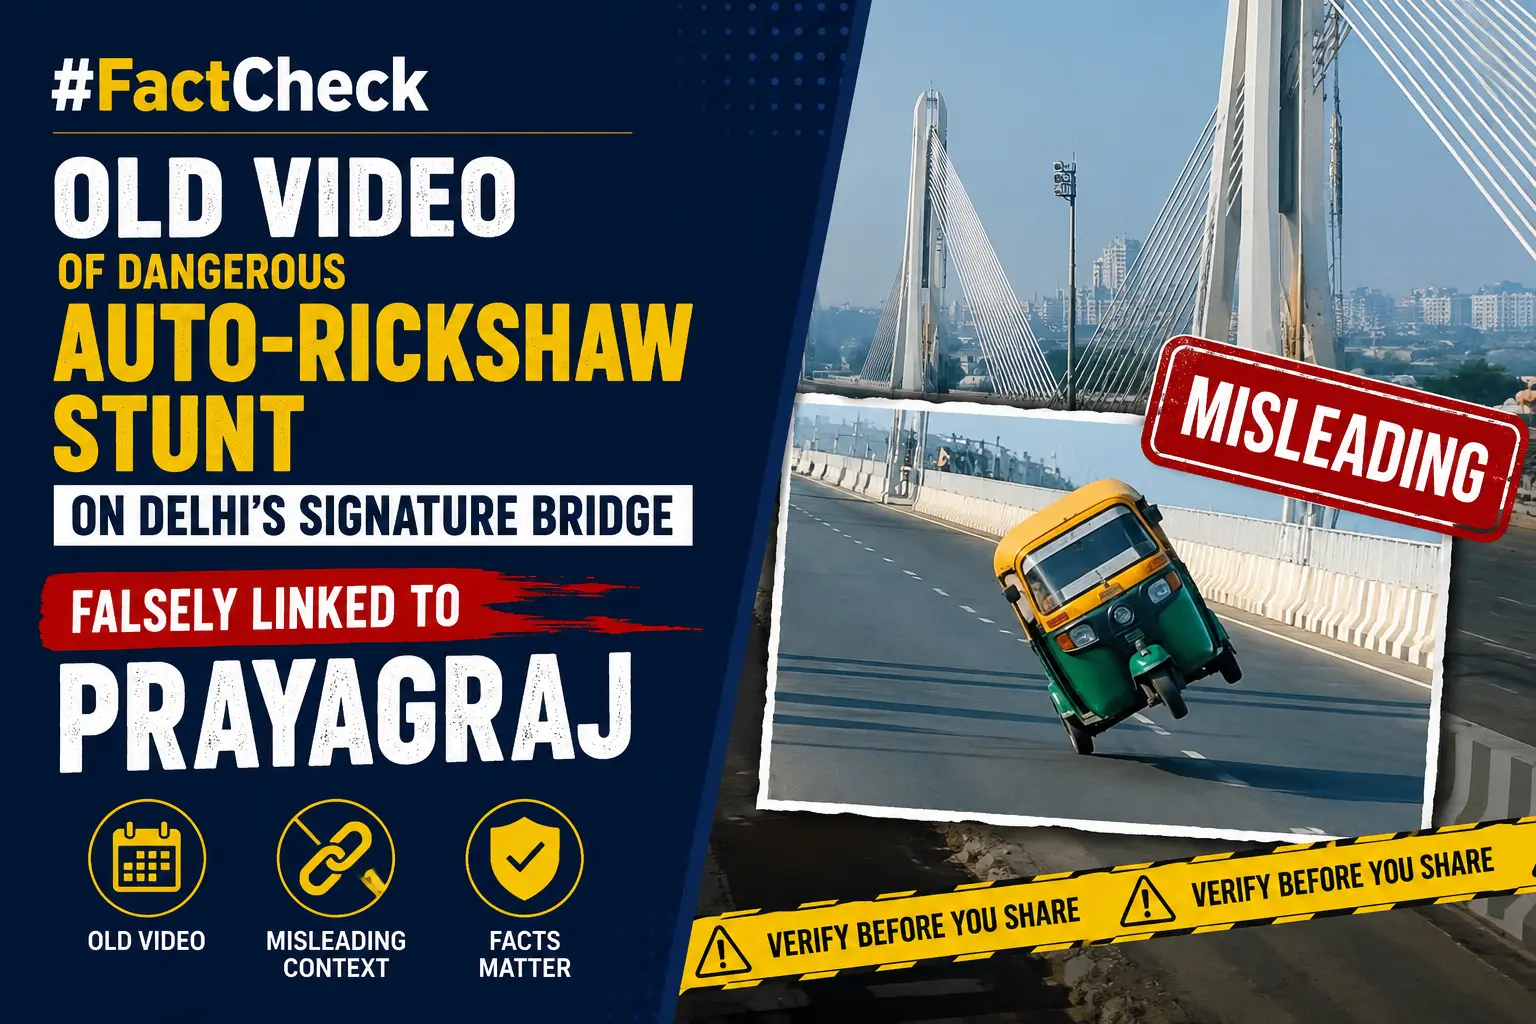
In our research, the viral post turned out to be fake. A video of an incident that took place on Delhi's Signature Bridge in 2023 is now being falsely circulated to spread misinformation as an incident from a bridge in Prayagraj. No such incident has taken place on the Naini Bridge in Prayagraj.
Perth, Western Australia — For most of the past year, the name TeamPCP has circulated quietly within cybersecurity circles as shorthand for a particular kind of dread: not the dread of a phishing email or a suspicious link, but the dread of software you already trusted turning against you. This week, that quiet circulation became public record. The Australian Federal Police, working alongside the FBI and the Western Australia Police Force, arrested and charged two Western Australian men, aged 21 and 23, with a combined 14 offences over their alleged role in the group.
The arrests themselves are notable. The story behind them is more so.
A Campaign Built on Borrowed Trust
TeamPCP's alleged method was not to break down the front door. It was to compromise the door itself, the trusted mechanisms by which developers pull code into their own projects every day. The group has been linked to widespread supply-chain attacks that targeted open-source software and developer platforms to steal credentials, authentication secrets, and source code, with high-profile incidents affecting projects including Trivy, LiteLLM, Telnyx, SAP, and TanStack, alongside breaches at organisations such as the European Commission, Mistral AI, OpenAI, and GitHub. Reporting has also linked the campaign to ecosystems including GitHub Actions, Docker Hub, npm, PyPI and OpenVSX, the invisible plumbing through which most modern software is assembled.
The scale, as alleged by investigators, is difficult to overstate. Authorities say the malicious code potentially compromised over a thousand organisations worldwide, enabling the theft of roughly half a million credentials and the exfiltration of at least 300GB of data, figures that should be understood as allegations under active investigation rather than an independently verified victim count. The AFP itself has said the compromise of a small number of trusted software components had a significant global impact, with remediation costs estimated in the hundreds of millions of dollars.
Why This Attack Was So Hard to See Coming
The mechanics matter. Rather than tricking a user into clicking something malicious, the alleged operation worked by compromising the credentials developers use to publish legitimate software updates, then pushing tampered versions out through the same trusted distribution pipelines millions of applications rely on automatically. There is no obviously suspicious file, no rogue website, only a routine update, arriving exactly where it was expected.
Investigators also describe a cascading structure to the intrusions: credentials harvested from one compromised project reportedly opened the door to the next, turning isolated breaches into a chain reaction across the open-source ecosystem. TeamPCP has been described as running one of the most consequential campaigns of software supply-chain attacks investigators have tracked, and the group's reach extended notably into the AI stack — LiteLLM, one of the projects reportedly compromised, is an open-source gateway widely used to connect applications to large language model providers, meaning the attack's blast radius extended into the very infrastructure powering today's AI boom.
The Investigation and the Charges
The two men were charged following a joint investigation by the AFP and WAPF, working in parallel with the FBI, into what authorities describe as a sophisticated cybercrime syndicate accused of creating malicious open-source software to defraud thousands of global businesses. The charges span identity theft, unauthorised data modification, and money laundering, with maximum penalties ranging from three to twenty years' imprisonment. Search warrants were executed in Perth on 26 August 2026, and investigators seized electronic devices for forensic analysis after raids at properties in Cottesloe, Hamilton Hill, and Mandurah. FBI Cyber Division Assistant Director Brett Leatherman noted the significance of the international cooperation involved in the case, while investigators have not ruled out further arrests.
The Real Story: A Governance Problem, Not Just a Crime Story
It would be easy to file this under "hackers caught" and move on. But the more consequential story is structural. Modern organisations do not merely secure their own infrastructure, they inherit risk from every library, package, CI/CD pipeline, repository, vendor and developer tool they depend on, often without ever auditing that dependency chain directly. Guidance from the U.S. Cybersecurity and Infrastructure Security Agency (CISA) on securing open-source software has increasingly emphasised managing these dependencies through software bills of materials (SBOMs), precisely because so few organisations can otherwise answer a basic question: what, exactly, is running inside our systems?
TeamPCP's alleged campaign is a case study in why that question can no longer be optional. If an organisation's security posture is only as strong as the thousands of components it silently trusts, then supply-chain security is not a developer problem to be quietly patched — it is a governance issue, deserving board-level attention, vendor accountability frameworks, and mandatory disclosure practices.
CyberPeace's Take
At CyberPeace, we've been watching campaigns like TeamPCP's less as isolated incidents and more as a pattern that keeps repeating with higher stakes each time. What stands out to our team isn't the sophistication of the code, open-source poisoning is, frankly, not a new technique, it's the sophistication of patience. Compromising a maintainer's publishing credentials and simply waiting for the next scheduled release to carry the payload downstream is a strategy built for an ecosystem that still largely operates on implicit trust rather than continuous verification. That gap between how fast software moves and how slowly trust is actually checked is precisely where operations like this thrive.
We'd also push back gently on treating this as a "developer hygiene" story. Most engineering teams pulling in a package from npm or PyPI are not, and should not be expected to be, forensically auditing every dependency update by hand, that isn't scalable, and it was never a realistic line of defence. The actual fix has to sit further upstream: provenance verification baked into CI/CD pipelines, signed commits and releases treated as non-negotiable rather than optional, and SBOMs that are actually queried during incident response rather than generated once and filed away.
Our broader concern, honestly, is about incentive alignment. Open-source maintainers are frequently unpaid or under-resourced volunteers holding publishing keys to software depended on by billion-dollar enterprises. Until organisations that consume open-source software at scale start meaningfully funding its security, not just its development, this pattern isn't going away. It will simply find its next entry point.
References
- Australian Federal Police. Two WA men charged following AFP-FBI-WAPF disruption of alleged global cybercrime syndicate. afp.gov.au
- Bleeping Computer. Australia arrests alleged TeamPCP hackers behind supply-chain attacks. bleepingcomputer.com
- CyberScoop. Two alleged TeamPCP members arrested and charged after months of software supply-chain chaos. cyberscoop.com
- Cyber Daily. Busted! Alleged Aussie hackers linked to TeamPCP arrested in joint AFP-FBI-WAPF operation. cyberdaily.au
- Help Net Security. Two alleged TeamPCP hackers arrested over global supply chain attacks. helpnetsecurity.com
- Krebs on Security. Two Alleged 'TeamPCP' Hackers Arrested in Australia. krebsonsecurity.com
- TechCrunch. Australian police arrest two over TeamPCP hacks targeting Mercor, OpenAI, and others. techcrunch.com
- The Hacker News. Alleged TeamPCP Hackers Charged in Australia Over Major Supply Chain Attacks. thehackernews.com
