
#FactCheck - AI Generated Photo Circulating Online Misleads About BARC Building Redesign
Executive Summary:
A photo circulating on the web that claims to show the future design of the Bhabha Atomic Research Center, BARC building, has been found to be fake after fact checking has been done. Nevertheless, there is no official notice or confirmation from BARC on its website or social media handles. Through the AI Content Detection tool, we have discovered that the image is a fake as it was generated by an AI. In short, the viral picture is not the authentic architectural plans drawn up for the BARC building.

Claims:
A photo allegedly representing the new outlook of the Bhabha Atomic Research Center (BARC) building is reigning over social media platforms.


Fact Check:
To begin our investigation, we surfed the BARC's official website to check out their tender and NITs notifications to inquire for new constructions or renovations.
It was a pity that there was no corresponding information on what was being claimed.

Then, we hopped on their official social media pages and searched for any latest updates on an innovative building construction, if any. We looked on Facebook, Instagram and X . Again, there was no information about the supposed blueprint. To validate the fact that the viral image could be generated by AI, we gave a search on an AI Content Detection tool by Hive that is called ‘AI Classifier’. The tool's analysis was in congruence with the image being an AI-generated computer-made one with 100% accuracy.

To be sure, we also used another AI-image detection tool called, “isitai?” and it turned out to be 98.74% AI generated.

Conclusion:
To conclude, the statement about the image being the new BARC building is fake and misleading. A detailed investigation, examining BARC's authorities and utilizing AI detection tools, proved that the picture is more probable an AI-generated one than an original architectural design. BARC has not given any information nor announced anything for such a plan. This makes the statement untrustworthy since there is no credible source to support it.
Claim: Many social media users claim to show the new design of the BARC building.
Claimed on: X, Facebook
Fact Check: Misleading

Related Blogs
Executive Summary
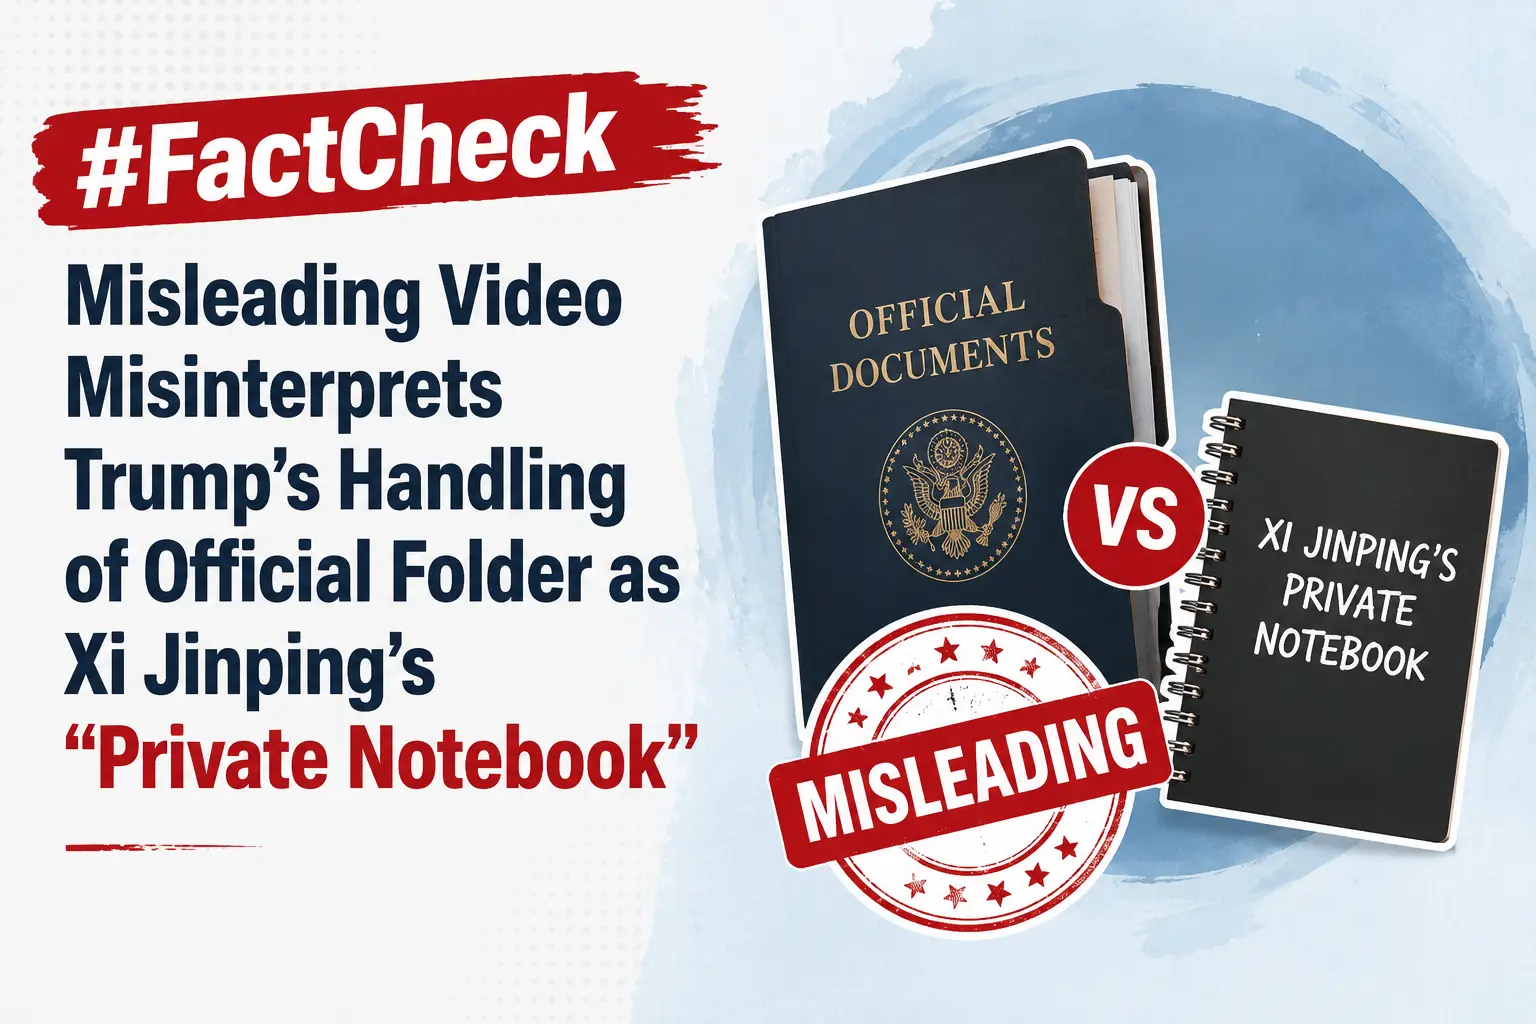
A video circulating on social media claims that during a summit in Beijing, Donald Trump was seen peeking into Chinese President Xi Jinping’s “private notebook” while Xi briefly stepped away. However, a fact-check by CyberPeace Research Wing found the claim to be baseless. A review of the full event footage clearly shows that the folder in question belonged to Donald Trump himself, not Xi Jinping. The viral interpretation is therefore misleading.
Claim
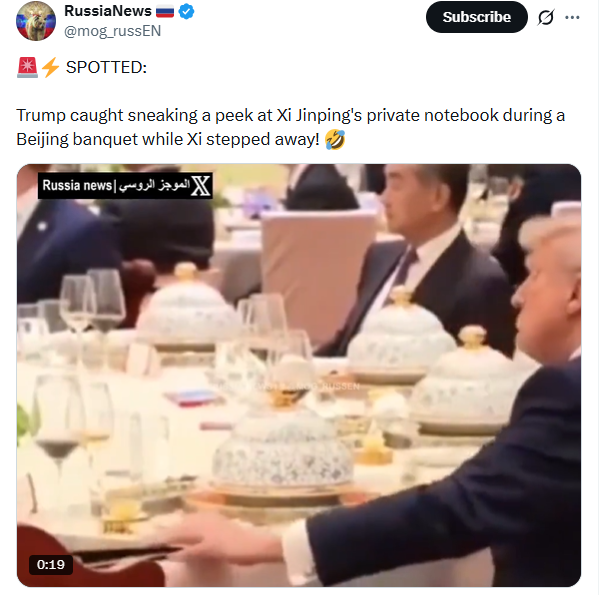
An X user shared the clip alleging, “Trump caught sneaking a peek at Xi Jinping’s private notebook during a Beijing banquet while Xi stepped away.”
Fact Check
A longer version of the video, shared by NBC News on May 14, shows the state banquet held at the Great Hall of the People in Beijing. Around the 1-minute-50-second mark, Xi Jinping, seated to Trump’s left, gets up and walks to the podium. The viral clip follows shortly after, showing Trump opening the folder placed to his left and flipping through its pages.
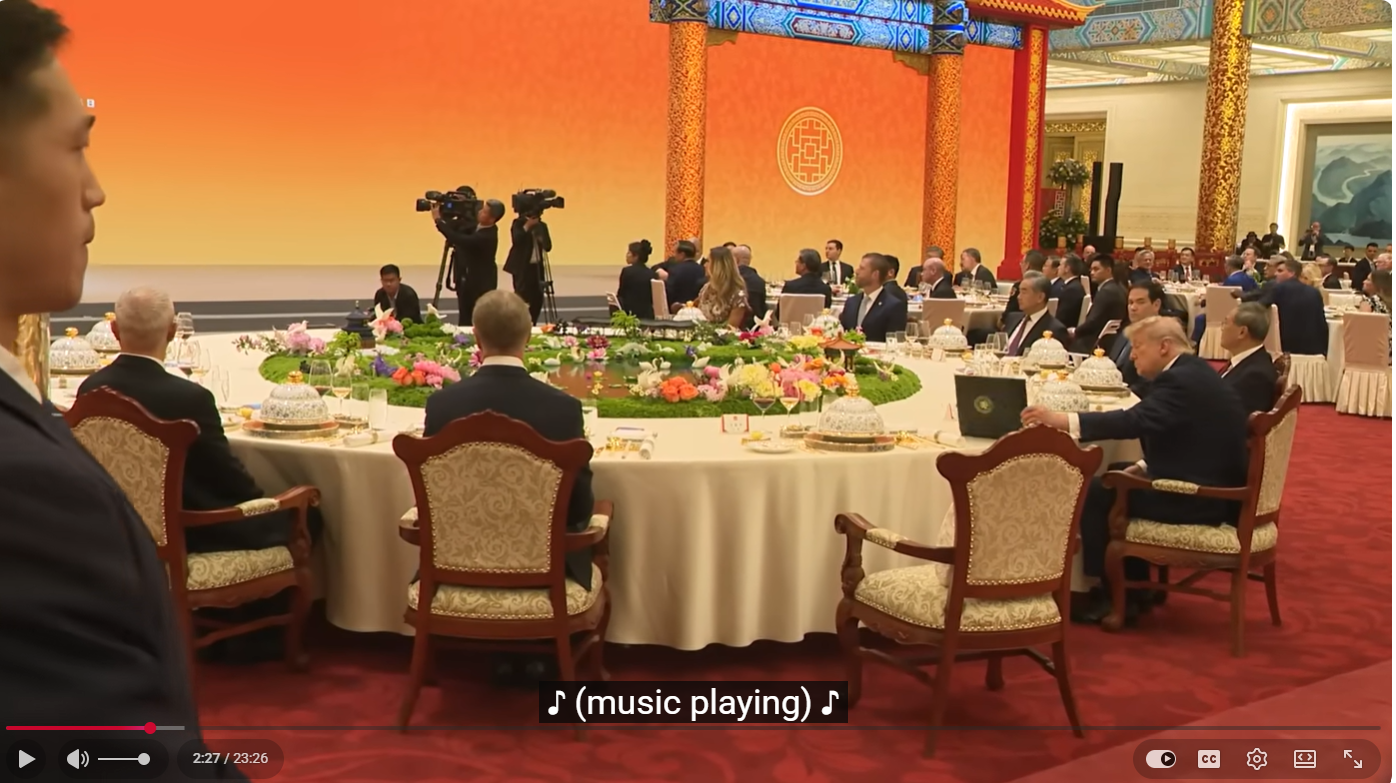

The White House also uploaded the full footage on its official YouTube channel, showing wider, uninterrupted shots of the event. Around the two-minute mark, the announcer says, “And now a toast by President Xi,” after which Xi Jinping stands up. Immediately after, Trump is seen opening the folder on his left and reading from it.
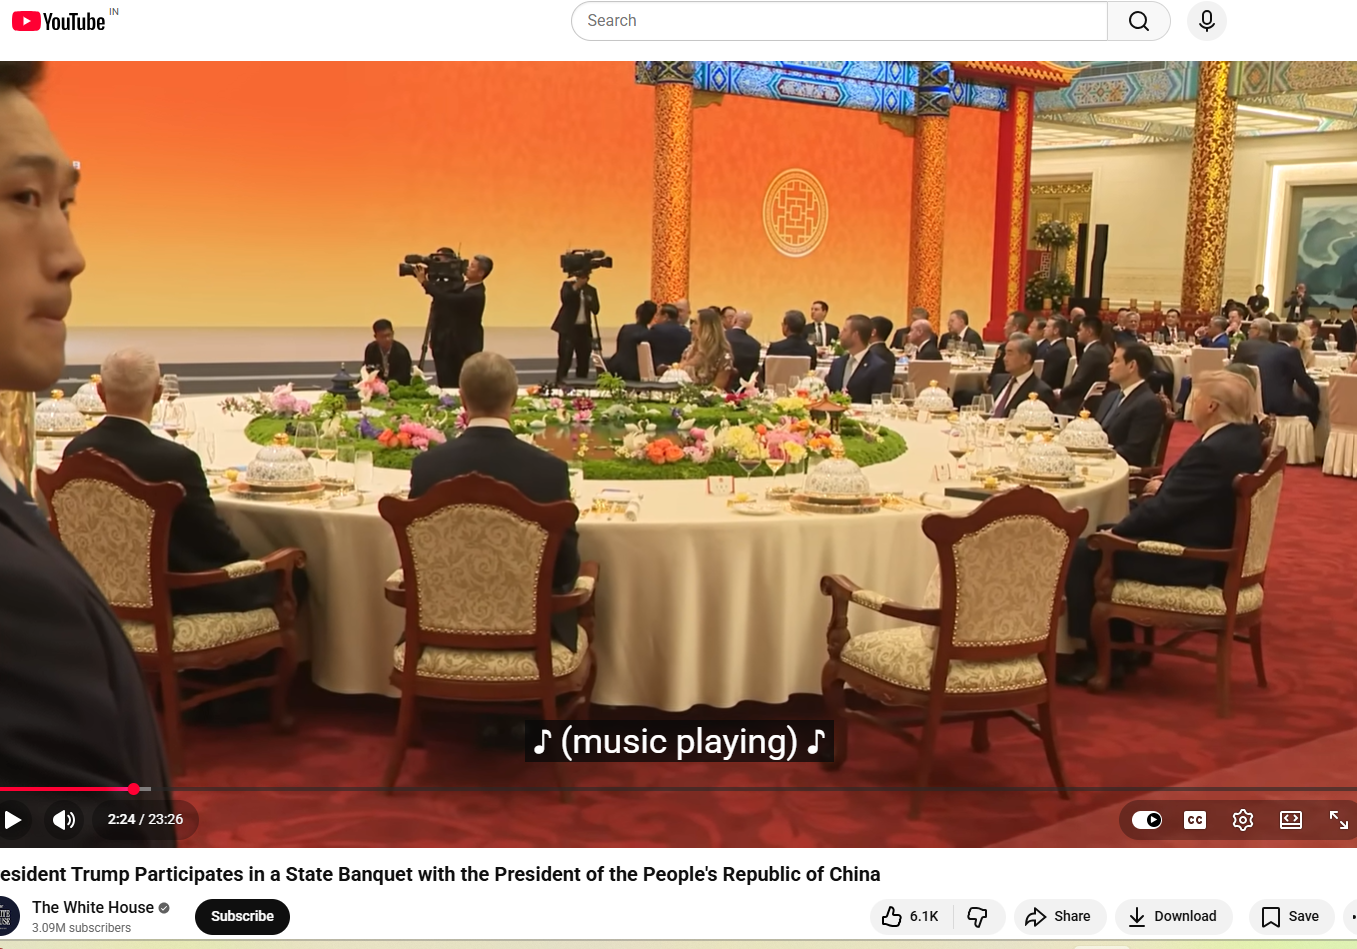
Later in the video, around the 12-minute mark, when Xi returns to his seat, Trump is seen standing up, taking the folder with him to the podium, turning pages, and reading from it. The same sequence can also be seen in the NBC News footage at around 11 minutes and 50 seconds. This clearly indicates that the folder belonged to the U.S. President and not Xi Jinping, and that Trump was not peeking into any private notebook. Another key detail is the embossed emblem on the folder, which closely resembles the Seal of the President of the United States. The American bald eagle, the national bird of the United States, is clearly visible at the centre. A comparison between the viral screenshot and the official seal shows they are nearly identical.
Conclusion
The viral claim is misleading and taken out of context. A detailed review of the full footage, including official recordings from NBC News and the White House, clearly shows that the folder in question belonged to Donald Trump and not Chinese President Xi Jinping. At multiple points in the video, Trump is seen opening, handling, and reading from the same folder, including while Xi Jinping is away from his seat and later after he returns. The visual evidence from the event also supports this conclusion. The embossed seal on the folder matches the official Seal of the President of the United States, further confirming that it was part of Trump’s official briefing material and not any private document belonging to Xi Jinping. Taken together, the full sequence of events and official video sources make it clear that the viral narrative has been incorrectly framed. There is no evidence to suggest that Trump was peeking into Xi Jinping’s personal notebook.
Introduction
The digital ecosystem has undergone a profound transformation due to the rapid growth of artificial intelligence, especially through its generative applications. While this progress has introduced innovative technologies, it has also intensified the risks of deepfakes, misinformation, and identity theft. The Information Technology (Intermediary Guidelines and Digital Media Ethics Code) Amendment Rules, 2026, introduced by the Government of India, mark an important step toward stronger digital governance and greater oversight of online activities. These latest amendments establish new regulatory standards and represent India’s most comprehensive effort so far to address synthetically generated information, including AI created audio, video, and images that closely imitate reality.
Understanding the Core Shift: From Reactive to Proactive Regulation
The 2026 amendment establishes its main characteristic through its shift from a reactive compliance system to a proactive due diligence system. Intermediaries must now operate as active participants who take responsibility for detecting, marking and controlling dangerous material instead of functioning as neutral channels. The rules establish an official definition for stands for Synthetically Generated Information(SGI), which they protect through legal regulations, while they address issues such as impersonation scams, election manipulation and non-consensual deepfake content. The current transition represents a worldwide pattern that shows that governments are starting to make online platforms responsible for the material they display.
Key Provisions of the IT Amendment Rules, 2026
1. Mandatory Labelling of AI-Generated Content
Platforms must ensure that all AI-generated content is clearly labelled or watermarked to distinguish it from authentic media. Users must reveal their uploaded content's synthetic origin while platforms must confirm the information.
2. The 3-Hour Takedown Rule
The most contentious aspect of this regulation establishes new rules that require content removal to be processed within much shorter timeframes.:
- The government and courts grant three-hour time limits for removing unlawful content.
- The two-hour deadline applies to media that includes non-consensual intimate imagery.
The current time frame allows content removal within three hours, which represents a major decrease from the previous content removal time, which lasted between 24 and 36 hours, because online misinformation needs urgent attention.
3. Traceability and Metadata Requirements
The rules require AI-generated content to include both digital fingerprints and metadata, which enables traceability and accountability through their embedded digital fingerprints. The provision serves as an essential tool for law enforcement to investigate cases while it helps identify which parties generated harmful content.
4. Safe Harbour Conditionality
Intermediaries who do not meet the following three conditions risk losing their safe harbour protection through Section 79 of the IT Act:
- The first requirement demands that intermediaries must implement proper labelling.
- The second requirement demands that intermediaries must complete their takedown responsibilities within specific timeframes
- The third requirement demands that intermediaries must complete their due diligence tasks.
This development represents a major transition for digital platforms, which will face increased responsibility for their actions.
5. Strengthened Grievance Redressal
The amendment establishes two new requirements for platforms. The amendment requires platforms to create systems that operate at all times to monitor their compliance with regulations.
Significance: Why These Rules Matter
The 2026 amendments are significant for multiple reasons:
- The rules require labelling and rapid content removal, which helps to stop the viral dissemination of misleading information.
- The framework provides better identity protection, defamation defence and protection against non-consensual imagery.
- The new rules make intermediaries responsible for their own compliance failures.
- The regulation of AI-generated misinformation protects democratic processes during electoral periods and public discussions.
The rules demonstrate India's goal to establish international standards for AI governance and digital responsibility.
Challenges and Concerns
The amendments present key issues that exist despite their positive aspects:
- The process of removing content at high speed creates risks for legitimate expression because safeguards need to be established through careful planning.
- The technical and infrastructural requirements governing compliance create financial burdens for smaller platforms that operate as intermediaries.
The existing challenges demonstrate the necessity for a solution that protects both human rights and security needs.
Conclusion
The IT Amendment Rules, 2026, establish a critical turning point for India's progress toward digital governance. The framework aims to establish a more secure digital environment through its solution of AI-generated content and deepfake detection problems, which create transparency and accountability issues. The rules will achieve their goals through proper implementation, which requires creating quick enforcement methods that protect both legal processes and free speech rights. The ongoing development of AI technology requires regulatory systems to keep changing while including all citizens and upholding democratic principles.
References
- https://vajiramandravi.com/current-affairs/it-rules-amendment-2026
- https://indianexpress.com/article/legal-news/indias-new-3-hour-deepfake-removal-rule-experts-urge-strict-compliance-10528122
- https://timesofindia.indiatimes.com/technology/tech-news/governments-new-it-rules-make-ai-content-labelling-mandatory-give-google-youtube-instagram-and-other-platforms-3-hours-for-takedowns/articleshow/128157496.cms
- https://www.drishtiias.com/daily-updates/daily-news-analysis/information-technology-amendment-rules-2026
- https://visionias.in/current-affairs/news-today/2026-02-11/science-and-technology/government-notified-the-information-technology-intermediary-guidelines-and-digital-media-ethics-code-amendment-rules-2026

Data localisation refers to restrictions in the data flow by limiting the physical storage and processing of data within a given jurisdiction’s boundaries.
An obvious benefit contributing to the importance of data localisation is the privacy benefits it offers. In addition to this, data localisation also has the potential to safeguard sensitive data and decrease the probability of cyber-attacks. In India, data localisation has become a key issue in the last decade due to the increase in the discourse for data privacy.
The Legal Framework in India
India passed the Digital Personal Data Protection Act of 2023 which directs the data fiduciaries (collectors and processors of digital personal data) to store the data of Indian citizens within India. This push for data localisation aligns with India’s position to enhance privacy, national security and regulatory control. It further requires data fiduciaries to adhere to the principles of data minimisation, purposeful limitation and consent of the data principles. Further, Section 17 of the Act prohibits the transfer of sensitive personal data to foreign jurisdictions unless they meet satisfactory privacy protection standards.
The Reserve Bank of India, via a circular for Payments Data Regulation in 2018, has mandated that all payment data be stored in India, though it can be processed abroad. It requires the telecom sector to ensure local storage and local processing of subscriber information. It further prohibits the transferring of subscribers’ account information overseas.
MeitY’s Information Technology (Intermediary Guidelines and Digital Media Ethics Code) Rules, 2021, emphasise data localisation, specifically when it involves government or critical data. The main idea behind this is that data related to Indian citizens or government activities should remain accessible to Indian law enforcement agencies and is not subject to external jurisdiction.
Common Misinformation about Data Localisation and its Impact
Misconceptions fuel misinformation and influence public perception and policy debates. A common misconception is that all data must be stored in India. It should be noted that non-critical and non-sensitive data are not subject to localisation, and can be cleared for cross-border transfers under specific circumstances.
Another misconception is that data localisation alone ensures complete security. A robust cybersecurity approach, infrastructure and capabilities are what guarantee security and this holds true regardless of the location of where the data is stored.
The notion that small businesses and startups will suffer the most is untrue. While data localisation policies may lead to increased costs, they foster innovation in the domestic infrastructure and services. This potentially fuels development and innovation in these small businesses and startups. Claims that data localisation will stifle global business are unfounded.
Proper regulations for data transfers can help balance data flows, enabling international trade while ensuring data sovereignty.
Real Impact of Data Localisation
Data localisation impacts several domains and has both positive and negative outcomes.
- It can be a driver for investment in local data centres and infrastructure, thereby inducing employment generation and boosting the domestic economy. And in contrast, the compliance costs may rise especially for MNCs that need to maintain multiple data storage systems.
- It can expedite the growth of local technology ecosystems while encouraging innovation in cloud computing and data storage solutions. On the other hand, small businesses might face struggles to afford the required infrastructure updates and upgrades.
- Law enforcement agencies will be able to gain access to data more swiftly while avoiding lengthy processes such as the Mutual Legal Assistance Treaties (MLATs). However, it should be noted that storing data locally does not automatically ensure that they are immune from attacks and breaches.
- A balance between sovereignty and global partnerships is a challenge that emerges with data localisation. International Trade Relationships are vulnerable to data localisations where countries favour a free data flow. This can hamper foreign collaborations with companies that rely on global data systems.
CyberPeace Outlook
It is important to clear misinformation about data localisation, some strategies that can be undertaken are:
- Launching public awareness campaigns to educate the stakeholders about the real requirements and the benefits of data localisation. Misinformation about data restrictions and security guarantees should be tackled fairly quickly.
- A balanced approach that promotes local economic development while at the same time allowing for the necessary cross-border data flows and creating a flexible and friendly business environment is important.
- India should work on international frameworks to streamline the process of data-sharing with other nations. This would protect national interests while making global cooperation easier.
Conclusion
Data localisation in India presents a valuable opportunity to enhance privacy, bolster national security, and stimulate economic growth through local infrastructure investment. Yet, addressing common misconceptions is crucial; the belief that all data must be stored domestically or that localisation alone ensures security is misleading.
It’s vital to pair local data storage with robust cybersecurity measures and foster international cooperation. Supporting small businesses, which may face challenges due to localisation requirements, is equally important. By addressing misinformation, promoting flexible regulations, and working towards global data-sharing frameworks, India can effectively manage the complexities of data localisation, safeguarding national interests while encouraging innovation and economic development.
References
- https://www.thehindu.com/sci-tech/technology/are-data-localisation-requirements-necessary-and-proportionate/article66131957.ece
- https://carnegieendowment.org/research/2021/04/how-would-data-localization-benefit-india?lang=en
- https://www.rbi.org.in/commonperson/English/Scripts/FAQs.aspx?Id=2995
- https://www.meity.gov.in/writereaddata/files/Information%20Technology%20%28Intermediary%20Guidelines%20and%20Digital%20Media%20Ethics%20Code%29%20Rules%2C%202021%20%28updated%2006.04.2023%29-.pdf
