
Innovation in Countering Misinformation: The Usage of Intelligent Communication System in the Army
Introduction
Attempts at countering the spread of misinformation can include various methods and differing degrees of engagement by different stakeholders. The inclusion of Artificial Intelligence, user awareness and steps taken on the part of the public at a larger level, focus on innovation to facilitate clear communication can be considered in the fight to counter misinformation. This becomes even more important in spaces that deal with matters of national security, such as the Indian army.
IIT Indore’s Intelligent Communication System
As per a report in Hindustan Times on 14th November 2024, IIT Indore has achieved a breakthrough on their project regarding Intelligent Communication Systems. The project is supported by the Department of Telecommunications (DoT), the Ministry of Electronics and Information Technology (MeitY), and the Council of Scientific and Industrial Research (CSIR), as part of a specialised 6G research initiative (Bharat 6G Alliance) for innovation in 6G technology.
Professors at IIT Indore claim that the system they are working on has features different from the ones currently in use. They state that the receiver system can recognise coding, interleaving (a technique used to enhance existing error-correcting codes), and modulation methods together in situations of difficult environments, which makes it useful for transmitting information efficiently and securely, and thus could not only be used for telecommunication but the army as well. They also mention that previously, different receivers were required for different scenarios, however, they aim to build a system that has a single receiver that can adapt to any situation.
Previously, in another move that addressed the issue of misinformation in the army, the Ministry of Defence designated the Additional Directorate General of Strategic Communication in the Indian Army as the authorised officer to issue take-down notices regarding instances of posts consisting of illegal content and misinformation concerning the Army.
Recommendations
Here are a few policy implications and deliberations one can explore with respect to innovations geared toward tackling misinformation within the army:
- Research and Development: In this context, investment and research in better communication through institutes have enabled a system that ensures encrypted and secure communication, which helps with ways to combat misinformation for the army.
- Strategic Deployment: Relevant innovations can focus on having separate pilot studies testing sensitive data in the military areas to assess their effectiveness.
- Standardisation: Once tested, a set parameter of standards regarding the intelligence communication systems used can be encouraged.
- Cybersecurity integration: As misinformation is largely spread online, innovation in such fields can encourage further exploration with regard to integration with Cybersecurity.
Conclusion
The spread of misinformation during modern warfare can have severe repercussions. Sensitive and clear data is crucial for safe and efficient communication as a lot is at stake. Innovations that are geared toward combating such issues must be encouraged, for they not only ensure efficiency and security with matters related to defence but also combat misinformation as a whole.
References
- https://timesofindia.indiatimes.com/city/indore/iit-indore-unveils-groundbreaking-intelligent-receivers-for-enhanced-6g-and-military-communication-security/articleshow/115265902.cms
- https://www.hindustantimes.com/technology/6g-technology-and-intelligent-receivers-will-ease-way-for-army-intelligence-operations-iit-official-101731574418660.html

Related Blogs
Introduction
The trajectory of India's digital economy is growing at an unprecedented rate, and so is India's cybercrime ecosystem. Parliamentary data tabled before the Rajya Sabha in May 2024 by the MHA suggests an overwhelming 900% growth in cybercrime complaints from 2021 to '25, while annual losses crossed 22,800 crore in 2024. The structural issues like the low victim restitution rate, the lack of forensic infrastructure, issues of jurisdiction related to offshore fraud factories targeting Indian citizens, and the huge disparity in awareness levels amongst India's youngest online citizens continue to exist. This brief brings out the clear trends in cybercrime, the role of institutional mechanisms in its prevention and response, failure points, and recommends appropriate policy interventions from the perspective of CyberPeace.
The Data Imperative
Since its operationalisation in 2019 by the Indian Cyber Crime Coordination Centre (I4C), the NCRP serves as India's most significant institutional apparatus for cybercrime reporting and response. Data placed before the Rajya Sabha by the Ministry of Home Affairs on 30 July 2025 show that, with almost no exception, complaints of cybercrime have increased far more quickly than most traditional indicators of public safety. Between 2021 and June 2025, the NCRP received 6.59 million complaints, evidence of both a sustained and escalating expansion of India's cyber threat profile. Complaints per year more than quadrupled from 4.52 lakh in 2021 to 19.18 lakh in 2024 (324% over the period); by 2025, the NCRP had received 28.15 lakh complaints, a 523 percent rise compared with the 2021 baseline:
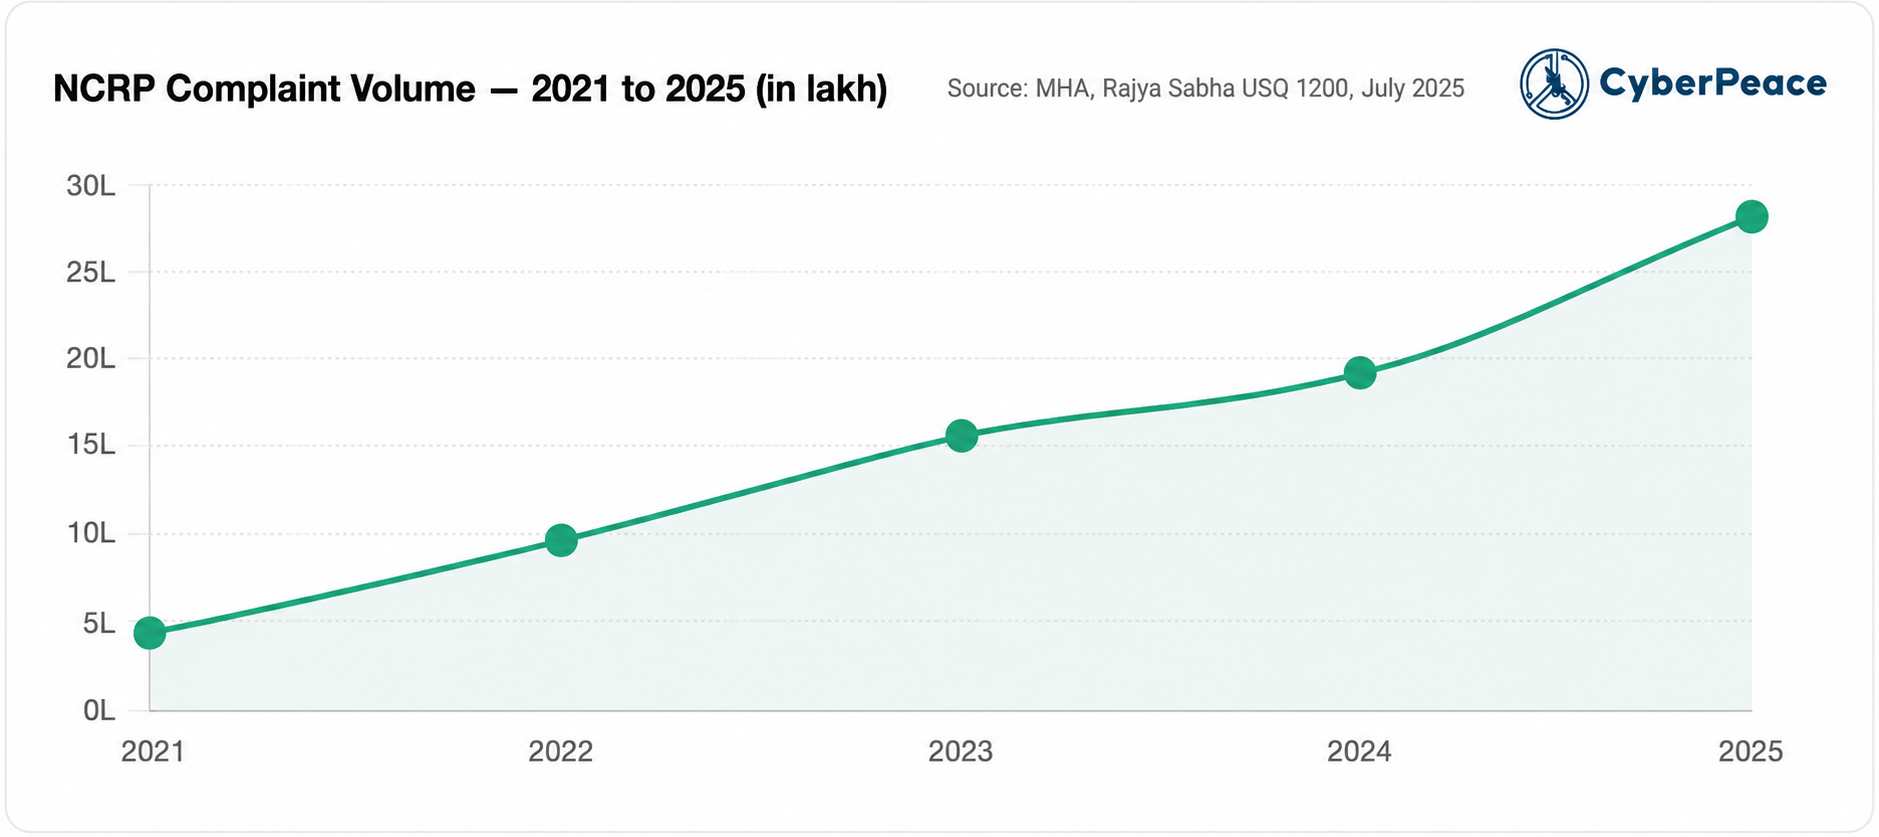
Clearly, cyber-enabled crime is no longer an occasional crisis but a systemic governance issue requiring consistent regulation and institution-building.
The financial fallout has also accelerated dramatically. Figures indicate that reported financial losses due to cybercrime jumped from 2,290 crore in 2022 to 22,812 crore in 2024 a 895% leap in two years:
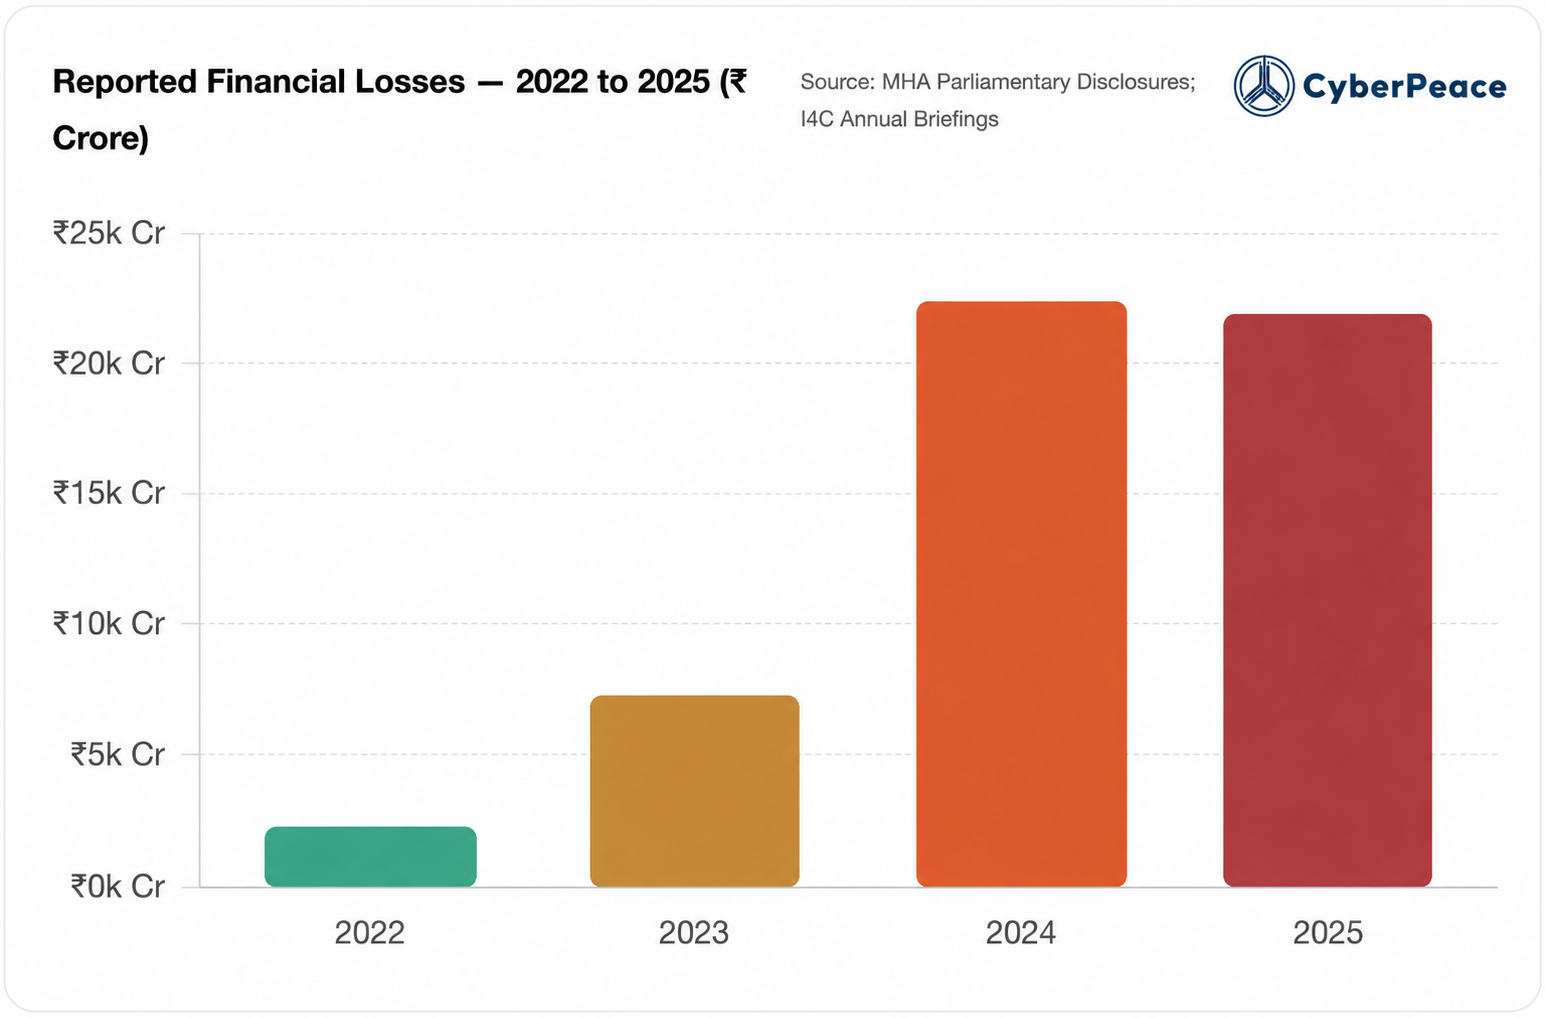
Though response mechanisms such as the Citizen Financial Cyber Fraud Reporting and Management System (CFCFRMS) successfully blocked or recovered close to 8,690 crore as of January 2026, victims appear to get back only about 2.18 percent of the losses they report.
In most areas, reporting and response have expanded greatly, but both the rate and scale of cyber-enabled financial fraud continue to outstrip India's remediation and law enforcement capacity.
Threat Typology of India’s Fraud Ecosystem
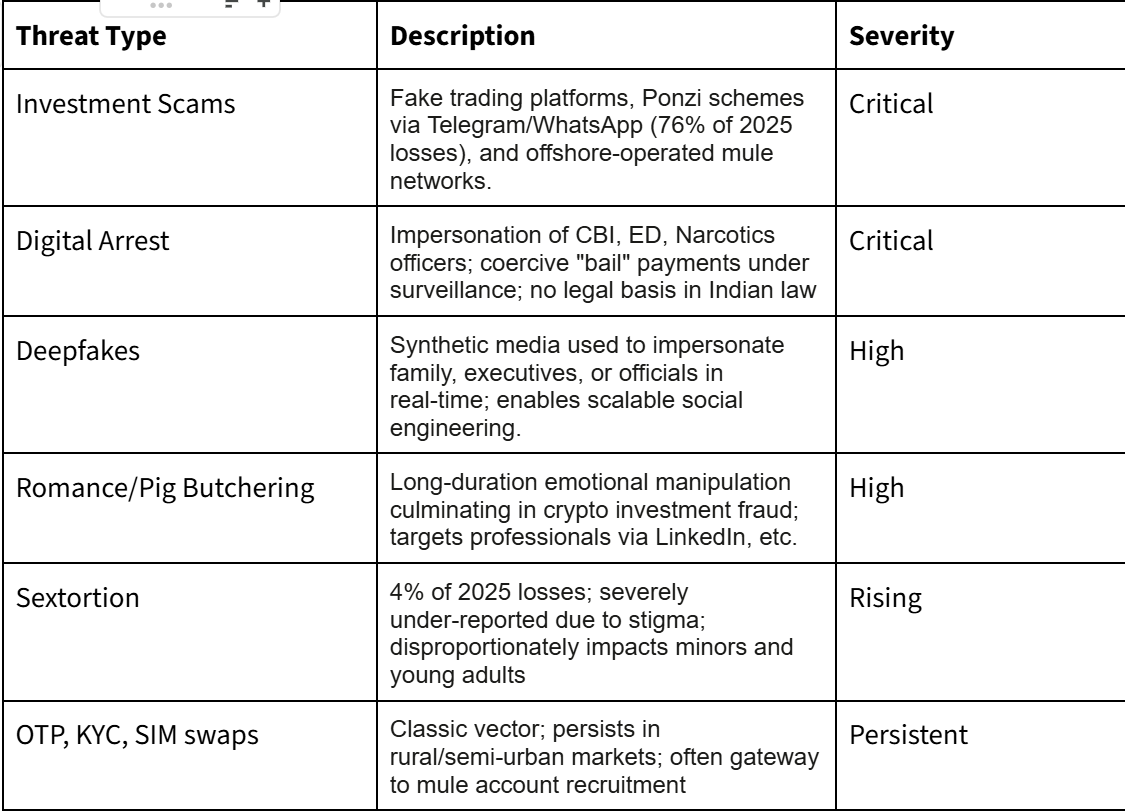
The nature of cyber crime in India has evolved from an opportunistic volume-based activity to a layered transnational criminal environment. I4C intelligence as tabled in Parliament reveals investment scams as the biggest threat: they accounted for 76% of the financial fraud lost in 2025 (although only 35% of complaints were filed, thus, a very high value per case was lost).
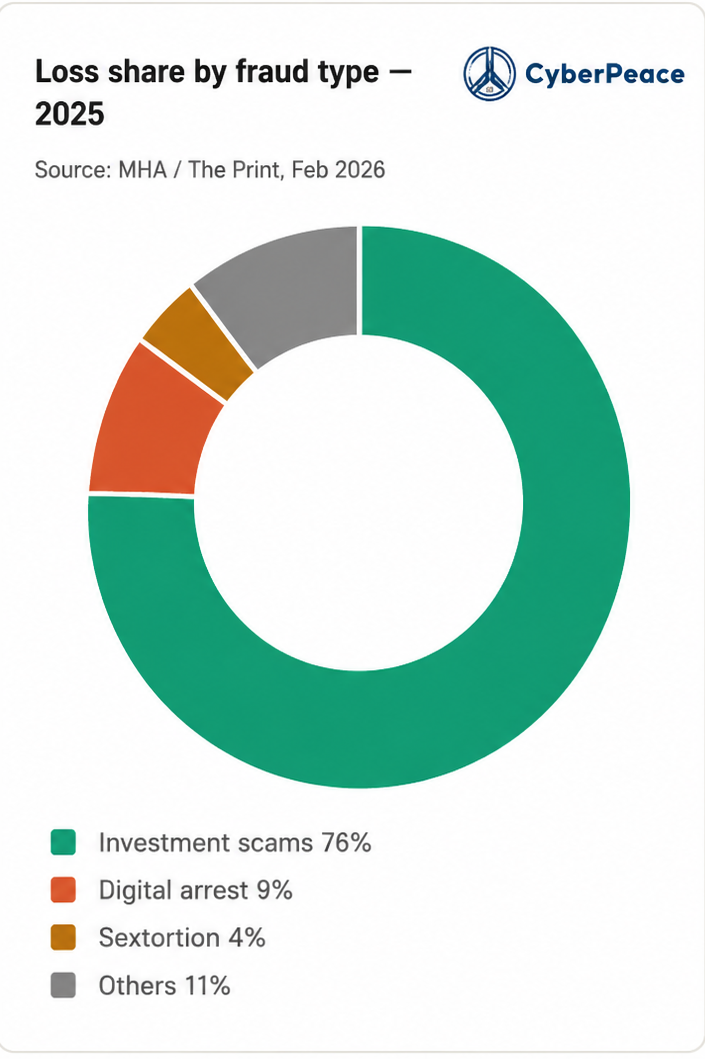
Digital arrest frauds, which tap on citizens' unawareness that "digital arrest" is not permissible under Indian law, rose from 39,925 cases (91 crore) in 2022 to 123,672 cases (1,935crore) in 2024.
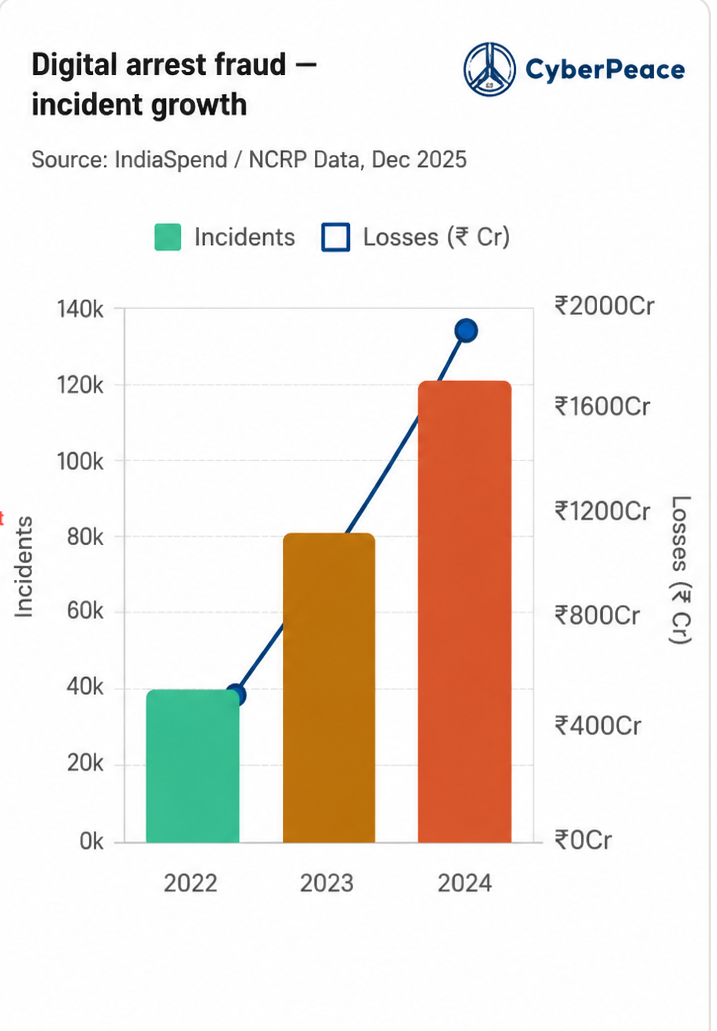
The fast rise in the number of incidents as well as in the volume of fraud clearly points out that digital arrest fraud has moved away from the phase of novel scam typology to a formidable cyber-extortion landscape. The main orchestrators of investment, trading, dating, and digital arrest scams targeting Indian citizens were recently identified by the I4C CEO Rajesh Kumar as transnational criminal scam networks in Cambodia, Myanmar, and Laos. Hence, this issue does not only fall within the domain of domestic law enforcement but constitutes a transnational cybercrime requiring parallel financial intelligence, diplomatic initiative, platform responsibility, and international investigative collaboration.
Geographic Concentration
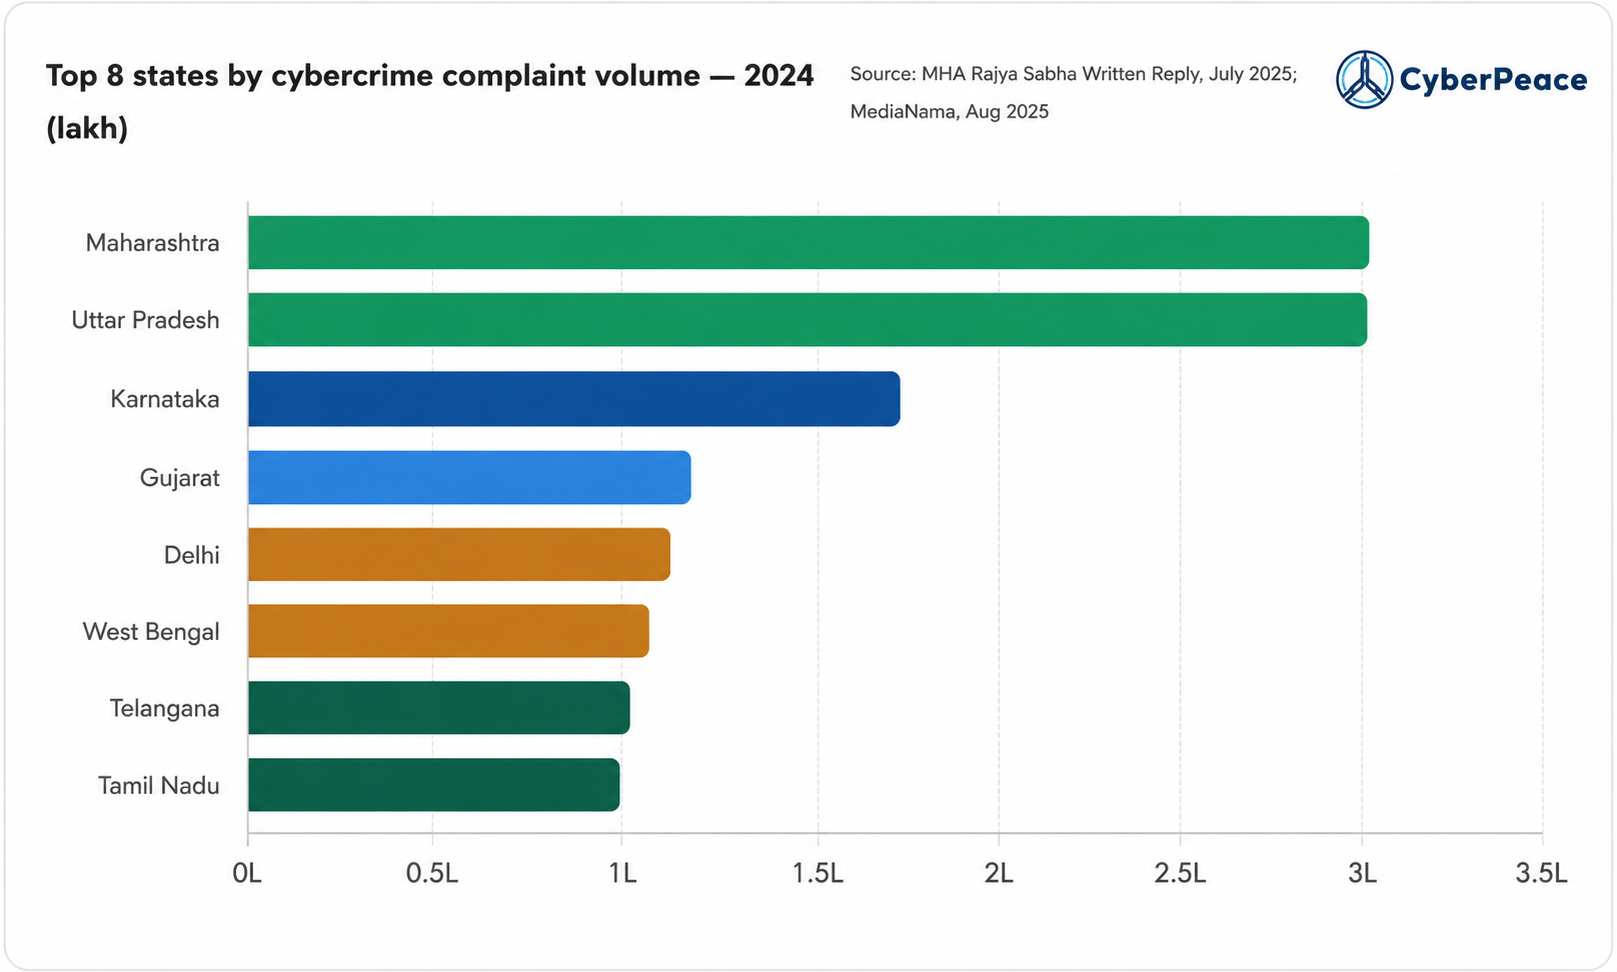
Maharashtra and UP register the highest volumes in total complaints at 3.03 lakh and 3.01 lakh, owing to them being the financial capital and most populous state, respectively. Karnataka, Gujarat, Delhi, WB, Telangana, TN, Rajasthan, and Haryana register above 1 lakh complaints each. However, the critical information that is being missed is that while complaint rate growth is the fastest in Tier 2 and 3 geographies (Haryana leads per-capita complaint rate with 381/100k people in 2023; Telangana (261); Uttarakhand (243)), this signifies rural digital growth as a risk multiplier.
Institutional Architecture: Mechanisms and Performances
India's institutional response to cybercrime, led by the Ministry of Home Affairs' Indian Cyber Crime Coordination Centre (I4C), is one of the world's largest real-time fraud detection and prevention ecosystems. The backbone of this is the Citizen Financial Cyber Fraud Reporting and Management System (CFCFRMS), which has onboarded over 700 banks, payment service providers, e-commerce portals, digital wallets, and, since the Standard Operating Procedure was issued on 2nd January 2026, virtual asset service providers and crypto exchanges. This interconnected network allows for prompt freezing of funds and timely fraud intervention during the 'golden hour' of a cybercrime report.
Institutional capacity is robust, with approximately 8,690 crore saved via the CFCFRMS since its inception for over 24.65 lakh complaints. The national cybercrime helpline (1930) receives close to 10,000 calls daily, while the Suspect Registry has enabled the rejection of 9,519 crore via the detection of 23.05 lakh suspect entities and 27.37 lakh mule accounts. In parallel, the CyTrain platform has expanded training by registering 151,081 police and judicial officers and issuing 142,025 certificates. Cyberforensic labs in all 33 States and Union Territories have received central assistance totalling 132.93 crore, and data-driven interstate crime analytics and offender linkages through the Samanvaya and Pratibimb platforms have led to 21,857 arrests.
Ecosystem Gaps
Through I4C, CFCFRMS, CyTrain, and the establishment of forensic infrastructure in states, India’s cybercrime ecosystem has greatly grown. But due to the rapid proliferation of cybercrime, systemic shortcomings are revealed regarding the restoration of victims, investigation, forensic capacity, cross-border enforcement, awareness, and stakeholder coordination:
- Victim Restitution Deficit: Although the total of ₹ 8,690 crore frozen has increased, the refund for victim compensation is limited to only ₹ 167 crore (2.18%) due to lengthy restoration processes relying on court orders.
- Forensic Capacity Limitations: 2 national, state-level, unevenly equipped cyber forensic labs can’t match the needs of over 10 million cybercrime complaints per year.
- Low conviction rate: The investigations of cybercrimes suffer from evidence collection and criminal proceedings, leading to limited conviction rates.
- Cross-border enforcement challenges: Many of the investment and digital arrest scams, in fact, are originating from Cambodia, Myanmar, and Laos, rendering the cybercrime response mechanisms of India helpless.
- Lack of Awareness: First-time digital users are quite prone to online scams and fraud, and many of the victims continue not reporting due to social stigma and lack of confidence.
- Partial Stakeholder Integration: Banks and small financial institutions, small companies, and emerging virtual asset providers not yet on board allow the money to slip through without being tracked.
CyberPeace Insights: Strategic Way Forward
India has already built a relatively mature response structure for cybercrime with I4C, CFCFRMS, and CyTrain and is coordinating the financial sector on it. The way ahead lies in outcome-oriented improvements and not just in the ability to report and intercept more. Here are the priority interventions that address the most important institutional shortcomings identified in the current ecosystem:
- Fast-track victim restoration: Introduce time-bound victim restoration mechanisms for low-value incidents through simplified processes and mandate national-level roll-out of successful Lok Adalat-based settlement mechanisms.
- District-level cyber forensics: Establish cyber forensic support units at the district level and enhance access to mobile, cloud, and blockchain forensic capabilities.
- AI-powered fraud prevention: Mandate deep-fake and voice-clone detection mechanisms across all financial institutions and telecom networks; embed predictive risk analytics into transaction screening frameworks.
- Cyber Suraksha Gram initiative: Increase digital fraud awareness across all common service centres, Jan Dhan enrollment schemes, and rural banking channels, and tackle the awareness asymmetry.
- Regional cybercrime coordination: Establish real-time, operational intelligence-sharing mechanisms with Southeast Asian economies, which have become home to large scam networks preying on Indian citizens.
- Specialised cyber prosecution ecosystem: Develop exclusive cyber courts, standardise digital evidence procedures, and broaden the scope of CyTrain to include the development of specialised cadres of investigators and prosecutors capable of handling increasingly complex cybercrime cases.
Conclusion
The 22,812 crore lost due to cybercrime in 2024 was more than a mere figure; it signifies a serious concern regarding citizen trust, economic security, and digital inclusion. Though India's institutional response to cybercrime is one of the largest, with an operational I4C and a CFCFRMS functioning in real time, the victim compensation and prosecution mechanism falls short. It's time for implementation: faster recovery of resources, increased enforcement, a larger scale of awareness, and finally, translating the institutional innovations into concrete justice for victims nationwide.
References
- https://sansad.in/getFile/annex/270/AU1341_tmaxdx.pdf?source=pqars
- https://www.mha.gov.in/MHA1/Par2017/pdfs/par2025-pdfs/LS02122025/452.pdf
- https://www.pib.gov.in/PressReleasePage.aspx?PRID=2244504®=3&lang=2
- https://static.pib.gov.in/WriteReadData/specificdocs/documents/2025/oct/doc2025107659501.pdf
- https://www.medianama.com/2025/08/223-india-cybercrime-500-percent-increase-2021-2024/
- https://theprint.in/india/cybercrime-saw-24-spike-in-2025-indians-lost-rs-22495-crore-mainly-in-investment-scams/2859930/

A few of us were sitting together, talking shop - which, for moms, inevitably circles back to children, their health and education. Mothers of teenagers were concerned that their children seemed to spend an excessive amount of time online and had significantly reduced verbal communication at home.
Reena shared that she was struggling to understand her two boys, who had suddenly transformed from talkative, lively children into quiet, withdrawn teenagers.
Naaz nodded. “My daughter is glued to her device. I just can’t get her off it! What do I do, girls? Any suggestions?”
Mou sighed, “And what about the rising scams? I keep warning my kids about online threats, but I’m not sure I’m doing enough.”
Not just scams, those come later. What worries me more are the videos and photos of unsuspecting children being edited and misused on digital platforms,” added Reena.
The Digital Parenting Dilemma
For parents, it’s a constant challenge—allowing children internet access means exposing them to potential risks while restricting it invites criticism for being overly strict.
‘What do I do?’ is a question that troubles many parents, as they know how addictive phones and gaming devices can be. (Fun fact: Even parents sometimes struggle to resist endlessly scrolling through social media!)
‘What should I tell them, and when?’ This becomes a pressing concern when parents hear about cyberbullying, online grooming, or even cyberabduction.
‘How do I ensure they stay cybersafe?’ This remains an ongoing worry, as children grow and their online activities evolve.
Whether it’s a single-child, dual-income household, a two-child, single-income family, or any other combination, parents have their hands full managing work, chores, and home life. Sometimes, children have to be left alone—with grandparents, caregivers, or even by themselves for a few hours—making it difficult to monitor their digital lives. While smartphones help parents stay connected and track their child’s location, they can also expose children to risks if not used responsibly.
Breaking It Down
Start cybersafety discussions early and tailor them to your child’s age.
For simplicity, let’s categorize learning into five key age groups:
- 0 – 2 years
- 3 – 7 years
- 8 – 12 years
- 13 – 16 years
- 16 – 19 years
Let’s explore the key safety messages for each stage.
Reminder:
Children will always test boundaries and may resist rules. The key is to lead by example—practice cybersafety as a family.
0 – 2 Years: Newborns & Infants
Pediatricians recommend avoiding screen exposure for children under two years old. If you occasionally allow screen time (for example, while changing them), keep it to a minimum. Children are easily distracted—use this to your advantage.
What can you do?
- Avoid watching TV or using mobile devices in front of them.
- Keep activity books, empty boxes, pots, and ladles handy to engage them.
3 – 7 Years: Toddlers & Preschoolers
Cybersafety education should ideally begin when a child starts engaging with screens. At this stage, parents have complete control over what their child watches and for how long.
What can you do?
- Keep screen time limited and fully supervised.
- Introduce basic cybersecurity concepts, such as stranger danger and good picture vs. bad picture.
- Encourage offline activities—educational toys, books, and games.
- Restrict your own screen time when your child is awake to set a good example.
- Set up parental controls and create child-specific accounts on devices.Secure all devices with comprehensive security software.
8 – 12 Years: Primary & Preteens
Cyber-discipline should start now. Strengthen rules, set clear boundaries, and establish consequences for rule violations.
What can you do?
- Increase screen time gradually to accommodate studies, communication, and entertainment.
- Teach them about privacy and the dangers of oversharing personal information.
- Continue stranger-danger education, including safe/unsafe websites and apps.
- Emphasize reviewing T&Cs before downloading apps.Introduce concepts like scams, phishing, deepfakes, and virus attacks using real-life examples.
- Keep banking and credit card credentials private—children may unintentionally share sensitive information.
Cyber Safety Mantras:
- STOP. THINK. ACT.
- Do Not Trust Blindly Online.
13 – 16 Years: The Teenage Phase
Teenagers are likely to resist rules and demand independence, but if cybersecurity has been a part of their upbringing, they will tolerate parental oversight.
What can you do?
- Continue parental controls but allow greater access to previously restricted content.
- Encourage open conversations about digital safety and online threats.
- Respect their need for privacy but remain involved as a silent observer.
- Discuss cyberbullying, harassment, and online reputation management.
- Keep phones out of bedrooms at night and maintain device-free zones during family time.
- Address online relationships and risks like dating scams, sextortion, and trafficking.
16 – 19 Years: The Transition to Adulthood
By this stage, children have developed a sense of responsibility and maturity. It’s time to gradually loosen control while reinforcing good digital habits.
What can you do?
- Monitor their online presence without being intrusive.Maintain open discussions—teens still value parental advice.
- Stay updated on digital trends so you can offer relevant guidance.
- Encourage digital balance by planning device-free family outings.
Final Thoughts
As a parent, your role is not just to set rules but to empower your child to navigate the digital world safely. Lead by example, encourage responsible usage, and create an environment where your child feels comfortable discussing online challenges with you.
Wishing you a safe and successful digital parenting journey!

Introduction
Since February 2020 the government has been taking keen steps to safeguard the Indian markets and the consumer, this could be seen in the forms of policies and exemptions for the market players and the consumers, however, due to the COVID-19 pandemic, the markets places became vulnerable to loss and various forms of new crimes and frauds. The Government recently tabled the Jan Vishwas bill which is an aftermath of the Vivad se Vishwas Bill, 2020 which was tabled in February 2020 for creating a safe and dynamic market, this bill is a clear example of how AtmaNirbhar Bharat plays a crucial role in nations development.
What is Jan Vishwas Bill, 2022
The Jan Vishwas (Amendment of Provisions) Bill, 2022 is a 108-page bill introduced in the Lok Sabha by the Union Minister of Commerce and Industry, Piyush Goyal. The statement of objects and reasons of the Bill states, “To amend certain enactments for decriminalizing and rationalizing minor offenses to further enhance trust-based governance for ease of living and doing business.” The bill aims to promote ease of doing business in India by decriminalizing minor offences and amending 183 provisions in 42 Acts administered by 19 ministries. The bill proposes to replace minor offences with monetary penalties and rationalize existing monetary penalties based on the gravity of the offences. The Acts to be amended by the bill include-
- Drugs and Cosmetics Act, 1940
- Public Debt Act, 1944
- Pharmacy Act, 1948
- Cinematograph Act, 1952
- Copyright Act, 1957
- Patents Act, 1970
- Environment (Protection) Act, 1986
- Motor Vehicles Act, 1988
- Trade Marks Act, 1999l Railways Act, 1989
- Information Technology Act, 2000
- Prevention of Money-laundering Act, 2002
- Food Safety and Standards Act, 2006
- Legal Metrology Act, 2009
- Factoring Regulation Act, 2011
The bill aims to decriminalize a large number of minor offences and replace them with monetary penalties. This step by the government is a clear indication of how important the market regulations are, in recent times Google was imposed with a penalty of 1300 crores and 900 crores for violating competitive market practices, these penalties, and criminalised actions will ensure proper compliance to laws of the land thus creating a blanket of safeguards for the Indian consumer and netizen.
What will the Ease of Business be?
The Government has been critical in pinpointing various parameters and factors to improve the ease of business in the country, this bill comes at the right time when we can see numerous start-ups and entrepreneurs emerging in our country. The parameters are as follows-
- Starting a Business of all
- Dealing with Construction Permits
- Getting Electricity
- Registering Property
- Getting Credit
- Protecting
- Minority Investors
- Paying Taxes
- Trading across Borders
- Enforcing Contracts and Resolving Insolvency
These parameters have been created with a sight on the future of the markets and how external factors like the Russia-Ukraine war can influence the markets. According to Minister Piyush Goyal, the fear of imprisonment for minor offences is a major factor hindering the growth of the business ecosystem and individual confidence in India. The Jan Vishwas Bill, 2022 aims to address this issue by replacing minor offences with monetary penalties. The bill also proposes an increase of 10% in the minimum amount of fine and penalty levied after every three years, once the bill becomes a law.
Conclusion
The bill will create a level playing field for the market players and the consumers with the backing of strong legislation and precedents thus maintaining transparency and accountability in the system. The amended provisions will allow various already existing legislation to come in tune with the current times and emerging technologies. The nation is at a critical juncture to fabricate policies and laws to address the issues and threats of the future and hence such a bill will be the strengthening pillar of the Indian markets and cyber-ecosystem. The Jan Vishwas Bill, 2022 has been referred to a 31-member joint parliamentary committee for scrutiny. The committee includes members from the Lok Sabha and the Rajya Sabha and will submit its report to parliament by the second part of the Budget session in 2023, The members from the Lok Sabha include PP Chaudhary, Sanjay Jaiswal, Queen Ojha, Rajendra Agrawal, Gaurav Gogoi, A Raja, Rajendra Agarwal, Poonam Pramod Mahajan, and Sougata Ray.
