
Delhi High Court Directs Centre to Nominate Members for Deepfake Committee
The Delhi High Court vide order dated 21st November 2024 directed the Centre to nominate members for a committee constituted to examine the issue of deepfakes. The court was informed by the Union Ministry of Electronics and Information Technology (MeitY) that a committee had been formed on 20 November 2024 on deepfake matters. The Delhi High Court passed an order while hearing two writ petitions against the non-regulation of deepfake technology in the country and the threat of its potential misuse. The Centre submitted that it was actively taking measures to address and mitigate the issues related to deepfake technology. The court directed the central government to nominate the members within a week.
The court further stated that the committee shall examine and take into consideration the suggestions filed by the petitioners and consider the regulations as well as statutory frameworks in foreign countries like the European Union. The court has directed the committee to invite the experiences and suggestions of stakeholders such as intermediary platforms, telecom service providers, victims of deepfakes, and websites which provide and deploy deepfakes. The counsel for the petitioners stated that delay in the creation, detection and removal of deepfakes is causing immense hardship to the public at large. Further, the court has directed the said committee to submit its report, as expeditiously as possible, preferably within three months. The matter is further listed on 24th March 2025.
CyberPeace Outlook
Through the issue of misuse of deepfakes by bad actors, it has become increasingly difficult for users to differentiate between genuine and altered content created by deepfakes. This increasing misuse has led to a rise in cyber crimes and poses dangers to users' privacy. Bad actors use any number of random pictures or images collected from the internet to create such non-consensual deepfake content. Such deepfake videos further pose risks of misinformation and fake news campaigns with the potential to sway elections, cause confusion and mistrust in authorities, and more.
The conceivable legislation governing the deepfake is the need of the hour. It is important to foster regulated, ethical and responsible consumption of technology. The comprehensive legislation governing the issue can help ensure technology can be used in a better manner. The dedicated deepfake regulation and deploying ethical practices through a coordinated approach by concerned stakeholders can effectively manage the problems presented by the misuse of deepfake technology. Legal frameworks in this regard need to be equipped to handle the challenges posed by deepfake and AI. Accountability in AI is also a complex issue that requires comprehensive legal reforms. The government should draft policies and regulations that balance innovation and regulation. Through a multifaceted approach and comprehensive regulatory landscape, we can mitigate the risks posed by deepfakes and safeguard privacy, trust, and security in the digital age.
References
- https://www.devdiscourse.com/article/law-order/3168452-delhi-high-court-calls-for-action-on-deepfake-regulation
- https://images.assettype.com/barandbench/2024-11-23/w63zribm/Chaitanya_Rohilla_vs_Union_of_India.pdf

Related Blogs

Introduction
Assisted Reproductive Technology (“ART”) refers to a diverse set of medical procedures designed to aid individuals or couples in achieving pregnancy when conventional methods are unsuccessful. This umbrella term encompasses various fertility treatments, including in vitro fertilization (IVF), intrauterine insemination (IUI), and gamete and embryo manipulation. ART procedures involve the manipulation of both male and female reproductive components to facilitate conception.
The dynamic landscape of data flows within the healthcare sector, notably in the realm of ART, demands a nuanced understanding of the complex interplay between privacy regulations and medical practices. In this context, the Information Technology (Reasonable Security Practices And Procedures And Sensitive Personal Data Or Information) Rules, 2011, play a pivotal role, designating health information as "sensitive personal data or information" and underscoring the importance of safeguarding individuals' privacy. This sensitivity is particularly pronounced in the ART sector, where an array of personal data, ranging from medical records to genetic information, is collected and processed. The recent Assisted Reproductive Technology (Regulation) Act, 2021, in conjunction with the Digital Personal Data Protection Act, 2023, establishes a framework for the regulation of ART clinics and banks, presenting a layered approach to data protection.
A note on data generated by ART
Data flows in any sector are scarcely uniform and often not easily classified under straight-jacket categories. Consequently, mapping and identifying data and its types become pivotal. It is believed that most data flows in the healthcare sector are highly sensitive and personal in nature, which may severely compromise the privacy and safety of an individual if breached. The Information Technology (Reasonable Security Practices And Procedures And Sensitive Personal Data Or Information) Rules, 2011 (“SPDI Rules”) categorizes any information pertaining to physical, physiological, mental conditions or medical records and history as “sensitive personal data or information”; this definition is broad enough to encompass any data collected by any ART facility or equipment. These include any information collected during the screening of patients, pertaining to ovulation and menstrual cycles, follicle and sperm count, ultrasound results, blood work etc. It also includes pre-implantation genetic testing on embryos to detect any genetic abnormality.
But data flows extend beyond mere medical procedures and technology. Health data also involves any medical procedures undertaken, the amount of medicine and drugs administered during any procedure, its resultant side effects, recovery etc. Any processing of the above-mentioned information, in turn, may generate more personal data points relating to an individual’s political affiliations, race, ethnicity, genetic data such as biometrics and DNA etc.; It is seen that different ethnicities and races react differently to the same/similar medication and have different propensities to genetic diseases. Further, it is to be noted that data is not only collected by professionals but also by intelligent equipment like AI which may be employed by any facility to render their service. Additionally, dissemination of information under exceptional circumstances (e.g. medical emergency) also affects how data may be classified. Considerations are further nuanced when the fundamental right to identity of a child conceived and born via ART may be in conflict with the fundamental right to privacy of a donor to remain anonymous.
Intersection of Privacy laws and ART laws:
In India, ART technology is regulated by the Assisted Reproductive Technology (Regulation) Act, 2021 (“ART Act”). With this, the Union aims to regulate and supervise assisted reproductive technology clinics and ART banks, prevent misuse and ensure safe and ethical practice of assisted reproductive technology services. When read with the Digital Personal Data Protection Act, 2023 (“DPDP Act”) and other ancillary guidelines, the two legislations provide some framework regulations for the digital privacy of health-based apps.
The ART Act establishes a National Assisted Reproductive Technology and Surrogacy Registry (“National Registry”) which acts as a central database for all clinics and banks and their nature of services. The Act also establishes a National Assisted Reproductive Technology and Surrogacy Board (“National Board”) under the Surrogacy Act to monitor the implementation of the act and advise the central government on policy matters. It also supervises the functioning of the National Registry, liaises with State Boards and curates a code of conduct for professionals working in ART clinics and banks. Under the DPDP Act, these bodies (i.e. National Board, State Board, ART clinics and banks) are most likely classified as data fiduciaries (primarily clinics and banks), data processors (these may include National Board and State boards) or an amalgamation of both (these include any appropriate authority established under the ART Act for investigation of complaints, suspend or cancellation of registration of clinics etc.) depending on the nature of work undertaken by them. If so classified, then the duties and liabilities of data fiduciaries and processors would necessarily apply to these bodies. As a result, all bodies would necessarily have to adopt Privacy Enhancing Technologies (PETs) and other organizational measures to ensure compliance with privacy laws in place. This may be considered one of the most critical considerations of any ART facility since any data collected by them would be sensitive personal data pertaining to health, regulated by the Information Technology (Reasonable Security Practices And Procedures And Sensitive Personal Data Or Information) Rules, 2011 (“SPDI Rules 2011”). These rules provide for how sensitive personal data or information are to be collected, handled and processed by anyone.
The ART Act independently also provides for the duties of ART clinics and banks in the country. ART clinics and banks are required to inform the commissioning couple/woman of all procedures undertaken and all costs, risks, advantages, and side effects of their selected procedure. It mandatorily ensures that all information collected by such clinics and banks to not informed to anyone except the database established by the National Registry or in cases of medical emergency or on order of court. Data collected by clinics and banks (these include details on donor oocytes, sperm or embryos used or unused) are required to be detailed and must be submitted to the National Registry online. ART banks are also required to collect personal information of donors including name, Aadhar number, address and any other details. By mandating online submission, the ART Act is harmonized with the DPDP Act, which regulates all digital personal data and emphasises free, informed consent.
Conclusion
With the increase in active opt-ins for ART, data privacy becomes a vital consideration for all healthcare facilities and professionals. Safeguard measures are not only required on a corporate level but also on a governmental level. It is to be noted that in the 262 Session of the Rajya Sabha, the Ministry of Electronics and Information Technology reported 165 data breach incidents involving citizen data from January 2018 to October 2023 from the Central Identities Data Repository despite publicly denying. This discovery puts into question the safety and integrity of data that may be submitted to the National Registry database, especially given the type of data (both personal and sensitive information) it aims to collate. At present the ART Act is well supported by the DPDP Act. However, further judicial and legislative deliberations are required to effectively regulate and balance the interests of all stakeholders.
References
- The Information Technology (Reasonable Security Practices And Procedures And Sensitive Personal Data Or Information) Rules, 2011
- Caring for Intimate Data in Fertility Technologies https://dl.acm.org/doi/pdf/10.1145/3411764.3445132
- Digital Personal Data Protection Act, 2023
- https://www.wolterskluwer.com/en/expert-insights/pharmacogenomics-and-race-can-heritage-affect-drug-disposition

Introduction
A zero-click cyber attack solely relies on software and hardware flaws, bypassing any human factor to infect a device and take control over its data. It is almost impossible to discover the attack and know that the device is hacked unless someone on your side is closely monitoring your network traffic data.
At Kaspersky, security analysts used their SIEM solution KUMA to monitor their corporate WiFi network traffic and discovered this mysterious attack. They took necessary actions to investigate it and even went a step further to dive right into the action and uncover the entire attack chain.
A few months ago, Kaspersky shared their findings about this attack on iOS devices. They shared how these zero-click vulnerabilities were being exploited by the attackers and called this attack ‘Operation Triangulation’.
A zero-click exploit in the network
Kaspersky detected a zero-click attack on the iPhones of their colleagues while monitoring their corporate WiFi network traffic. They managed to get detailed information on all the stages of the attack by simply identifying a pattern in the domain names flowing through their network. Although the attackers were quite experienced, their mistakes helped Kaspersky detect critical vulnerabilities in all iOS devices.
The name-pattern
These previously unsuspected domains had a similar name-style which consisted of two names and ended with ‘.com’, such as ‘backuprabbit.com’ and ‘cloudsponcer.com’. They were used in pairs, one for an exportation process and the other served as a command and control server. These domains showed high outbound traffic, they were registered with NameCheap and protected with Cloudflare.
The network pattern
Each time a connection to these suspicious domains was made, it was preceded by an iMessage connection which indicated these domains are being accessed by iOS devices. It was observed that the devices connected to these domains, downloaded attachments, performed a few requests to a first level domain which was an exploitation framework server, then made regular connections with the second level domain which was a command and control server controlled by the attackers.
Getting more information
To get more information about the attack all the infected devices were collected and backed up after carefully informing the device owners. Although the attackers had managed to clean their artefacts, the backed up data was used to perform digital forensic procedures and find traces of the attacks. This helped Kaspersky to figure out how the infection might be taking place.
The attacker’s mistakes
The attackers deleted all the attachment files and exploits but did not delete the modified SMS attachment folder. That folder had no files left inside it. The attackers removed evidence from other databases as well, like the ‘SMS.db’ database, however another database called ‘datausage.sqlite’ was not sanitised.
The ‘datausage.sqlite’ database is the most important database when it comes to iOS forensics as its contents can be used to track applications and network usage. Upon examination of this database, a process logged as ‘BackupAgent’ was found to be making network connections at the same time the device was making connections to the suspicious domains.
The indicator of compromise
‘BackupAgent’ stood out in this scenario because although it is a legitimate binary, it has been deprecated since iOS4 and it should not have been making any network connections. This identified the ‘BackupAgent’ process as the first solid indicator of compromise in Operation Triangulation. The indicator is termed as- ‘Data usage by process BackupAgent’, and was used to determine if any specific device was infected.
Taking it a step ahead
The team at Kaspersky successfully identified the indicator of compromise and determined which devices were infected, but as the attackers were experienced enough to delete their payloads, they decided to set a trap and perform a man-in-the-middle attack. When they did, the attackers were unable to detect it.
The man-in the-middle attack
Kaspersky prepared a server with ‘WireGuard’ and ‘mitmproxy’. They installed root certificates on devices that could be used as targets for the attackers and routed all the network traffic to that server. They also developed a ‘Telegram’ bot to notify them about new infections as they decrypted the network traffic.
Setting up a bot proved to be an effective way of real time monitoring while modifying all the network packets on-the-fly with ‘mitmproxy’, this gave them unlimited power! Their trap was successful in capturing a payload sent by the attackers and it was analysed in detail.
The name was in the payload
The payload was an HTML page with obfuscator javascript which performed various code checks and canvas footprinting. It rendered a yellow triangle and calculated its hash value. This is why the operation was named Operation Triangulation.
The team at Kaspersky started cracking various layers of asymmetric cryptography with regular expressions. They patched the stages one-by-one on the fly to move the logic from each stage to ‘mitmproxy’ and finally implemented a 400 line ‘mitmproxy’ add-on. This add-on decrypted all the validators, exploits, spyware and additional modules.
The mystery
It is remarkable how Kaspersky detected the attack and identified multiple vulnerabilities, set up a trap to capture a payload and decrypted it completely. They shared all their findings with the device manufacturer and Apple responded by sending out a security patch update addressing four zero-day vulnerabilities.
A zero-click vulnerability
Traditionally any spyware relies on the user to to click on a compromised link or file to initiate the infection. However a zero-click vulnerability is a specific flaw in the device software or hardware that the attacker can use to infect the device without the need for a click or tap from the user.
The vulnerabilities identified
- Tricky Font Flaw (CVE-2023-41990): A clandestine method involving the manipulation of font rendering on iPhones, akin to a secret code deciphered by the attackers.Apple swiftly addressed this vulnerability in versions iOS 15.7.8 and iOS 16.3.
- Kernel Trick (CVE-2023-32434): Exploiting a hidden language understood only by the iPhone's core, the attackers successfully compromised the kernel's integrity.Apple responded with fixes implemented in iOS 15.7.7, iOS 15.8, and iOS 16.5.1.
- Web Sneakiness (CVE-2023-32435): Leveraging a clever ploy in the interpretation of web content by iPhones, the attackers manipulated the device's behaviour.Apple addressed this vulnerability in iOS 15.7.7 and iOS 16.5.1.
- Kernel Key (CVE-2023-38606): The pinnacle of the operation, the attackers discovered a covert method to tamper with the iPhone's core, the kernel.Apple responded with a fix introduced in iOS 16.6, thwarting the intrusion into the most secure facets of the iPhone
Still, how these attackers were able to find this critical vulnerability in a device which stands out for it’s security features is still unknown.
CyberPeace Advisory
Zero-click attacks are a real threat, but you can defend yourself. Being aware of the risks and taking proactive steps can significantly reduce vulnerability. Regularly installing the latest updates for your operating system, apps, and firmware helps patch vulnerabilities before attackers can exploit them.
- Keep your software updated as they contain crucial security patches that plug vulnerabilities before attackers can exploit them.
- Use security software to actively scan for suspicious activity and malicious code, acting as a first line of defence against zero-click intrusions.
- Be cautious with unsolicited messages if the offer seems too good to be true or the link appears suspicious as it can contain malware that can infect your device.
- Disable automatic previews as it can potentially trigger malicious code hidden within the content.
- Be mindful of what you install and avoid unverified apps and pirated software, as they can be Trojan horses laden with malware.
- Stay informed about the latest threats and updates by following reliable news sources and security blogs to stay ahead of the curve, recognize potential zero-click scams and adjust your behaviour accordingly.
Check out our (advisory report)[add report link] to get in depth information.
Conclusion
Operation Triangulation stands as a testament to the continuous cat-and-mouse game between cybercriminals and tech giants. While the covert spy mission showcased the vulnerabilities present in earlier iPhone versions, Apple's prompt response underscores the commitment to user security. As the digital landscape evolves, vigilance, timely updates, and collaborative efforts remain essential in safeguarding against unforeseen cyber threats.
References:
- Operation Triangulation: iOS devices targeted with previously unknown malware | Securelist, 1 June, 2023
- Operation Triangulation: The last (hardware) mystery | Securelist, 27 December, 2023.
- 37C3 - Operation Triangulation: What You Get When Attack iPhones of Researchers (youtube.com), 29 December,2023
Executive Summary
A video is being widely shared on social media and linked to protests that allegedly took place in Lucknow after the reported killing of Iran’s Supreme Leader Ali Khamenei.Users claim that police in the capital of Uttar Pradesh baton-charged people who were protesting against the United States and Israel. The video is being widely circulated across social media platforms with this claim. However, research by CyberPeace found the claim to be false. Our verification revealed that the video is not from Lucknow but from Bareilly, and it is related to an incident that took place on September 26, 2025, when Uttar Pradesh Police baton-charged protesters during a rally held in support of the “I Love Mohammad” campaign.
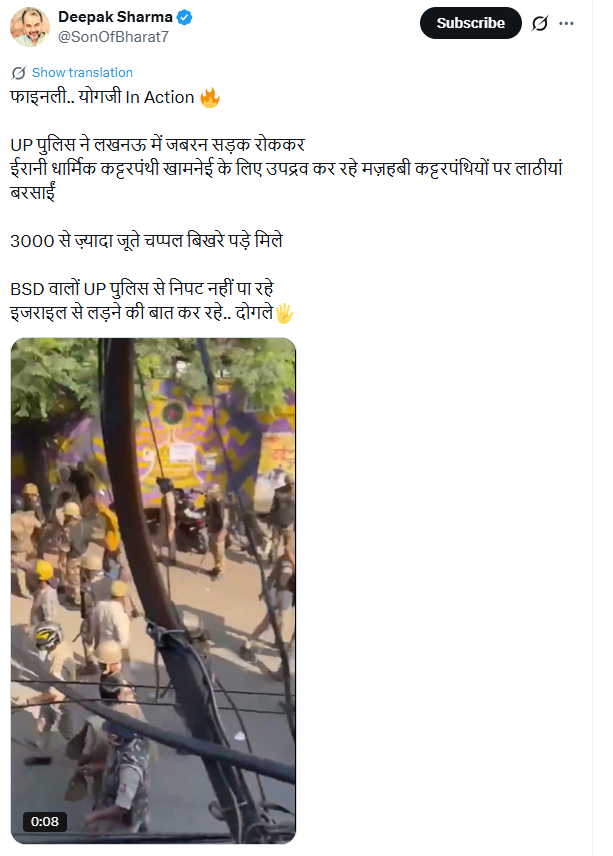
Claim Post:
On March 3, 2026, an X (formerly Twitter) user shared the viral video claiming that the Uttar Pradesh Police took action against people blocking roads in Lucknow and creating unrest in support of Ali Khamenei.
Fact Check
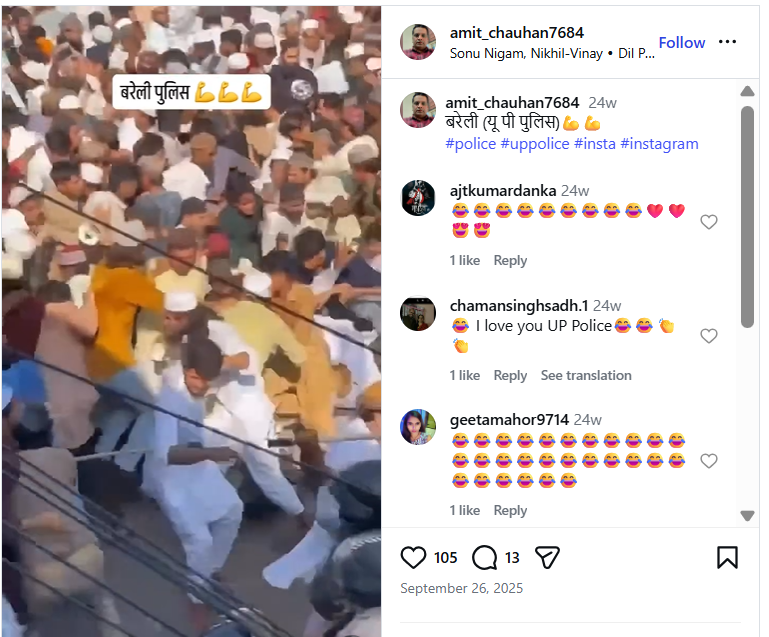
To verify the claim, we extracted key frames from the viral video and conducted a reverse image search using Google Lens. During the search, we found a similar video posted on Instagram on September 26, 2025, indicating that the footage predates the current claim.
Further research led us to the same video on the website of Aaj Tak, where it was published on September 26, 2025.
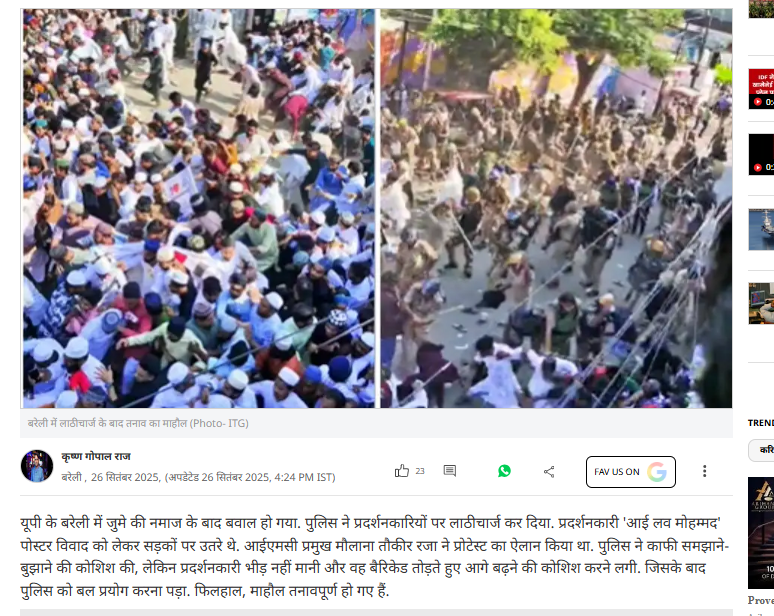
According to the report, protests erupted in Bareilly after Friday prayers over a controversy related to “I Love Mohammad” posters. Hundreds of people took to the streets carrying banners and posters. The report further stated that protesters, responding to a call by cleric Maulana Tauqeer Raza, attempted to break police barricades and move forward. Police initially tried to persuade the crowd to disperse, but when the situation escalated and the crowd refused to back down, officers resorted to baton-charging to control the situation. The incident reportedly led to tension in the area.
Conclusion:
Our research found that the viral video being shared as police action on protesters in Lucknow after the alleged killing of Ali Khamenei is misleading. The footage is actually from Bareilly and shows a police baton-charge during a protest rally held on September 26, 2025 in support of the “I Love Mohammad” campaign.
