
#FactCheck - Philadelphia Plane Crash Video Falsely Shared as INS Vikrant Attack on Karachi Port
Executive Summary:
A video currently circulating on social media falsely claims to show the aftermath of an Indian Navy attack on Karachi Port, allegedly involving the INS Vikrant. Upon verification, it has been confirmed that the video is unrelated to any naval activity and in fact depicts a plane crash that occurred in Philadelphia, USA. This misrepresentation underscores the importance of verifying information through credible sources before drawing conclusions or sharing content.
Claim:
Social media accounts shared a video claiming that the Indian Navy’s aircraft carrier, INS Vikrant, attacked Karachi Port amid rising India-Pakistan tensions. Captions such as “INDIAN NAVY HAS DESTROYED KARACHI PORT” accompanied the footage, which shows a crash site with debris and small fires.

Fact Check:
After reverse image search we found that the viral video to earlier uploads on Facebook and X (formerly Twitter) dated February 2, 2025. The footage is from a plane crash in Philadelphia, USA, involving a Mexican-registered Learjet 55 (tail number XA-UCI) that crashed near Roosevelt Mall.

Major American news outlets, including ABC7, reported the incident on February 1, 2025. According to NBC10 Philadelphia, the crash resulted in the deaths of seven individuals, including one child.

Conclusion:
The viral video claiming to show an Indian Navy strike on Karachi Port involving INS Vikrant is entirely misleading. The footage is from a civilian plane crash that occurred in Philadelphia, USA, and has no connection to any military activity or recent developments involving the Indian Navy. Verified news reports confirm the incident involved a Mexican-registered Learjet and resulted in civilian casualties. This case highlights the ongoing issue of misinformation on social media and emphasizes the need to rely on credible sources and verified facts before accepting or sharing sensitive content, especially on matters of national security or international relations.
- Claim: INS Vikrant, attacked Karachi Port amid rising India-Pakistan tensions
- Claimed On: Social Media
- Fact Check: False and Misleading

Related Blogs
Executive Summary
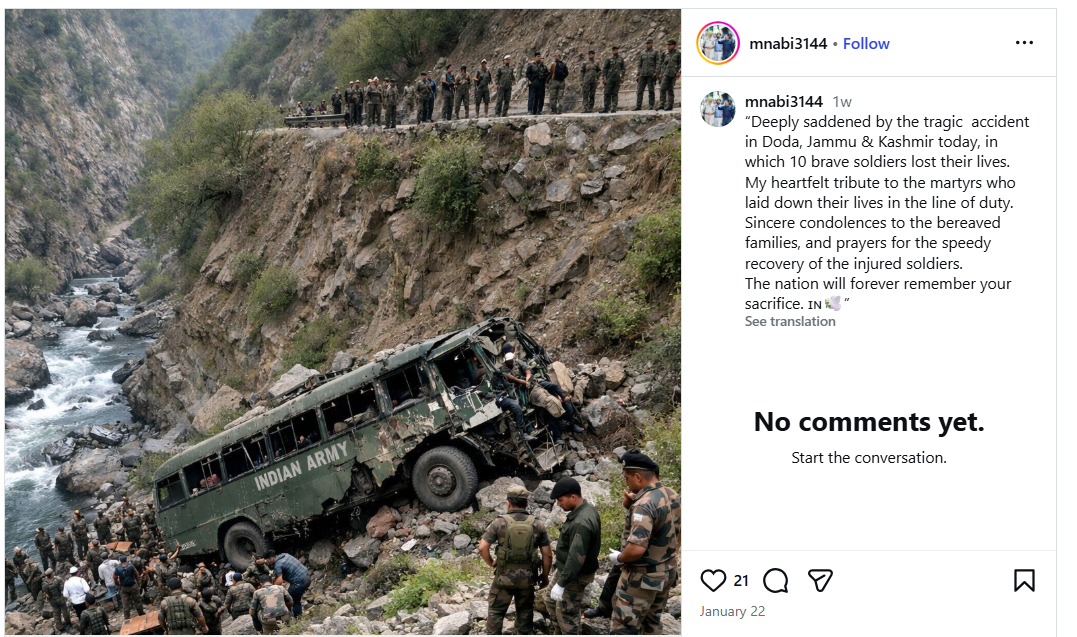
On January 22, an Indian Army vehicle met with an accident in Jammu and Kashmir’s Doda district, resulting in the death of 10 soldiers, while several others were injured. In connection with this tragic incident, a photograph is now going viral on social media. The viral image shows an Army vehicle that appears to have fallen into a deep gorge, with several soldiers visible around the site. Users sharing the image are claiming that it depicts the actual scene of the Doda accident.
However, an research by the CyberPeacehas found that the viral image is not genuine. The photograph has been generated using Artificial Intelligence (AI) and does not represent the real accident. Hence, the viral post is misleading.
Claim
An Instagram user shared the viral image on January 22, 2026, writing:“Deeply saddened by the tragic accident in Doda, Jammu & Kashmir today, in which 10 brave soldiers lost their lives. My heartfelt tribute to the martyrs who laid down their lives in the line of duty.Sincere condolences to the bereaved families, and prayers for the speedy recovery of the injured soldiers.The nation will forever remember your sacrifice.”
The link and screenshot of the post can be seen below.
- https://www.instagram.com/p/DT0UBIRk_3k/
- https://archive.ph/submit/?url=https%3A%2F%2Fwww.instagram.com%2Fp%2FDT0UBIRk_3k%2F+
Fact Check:
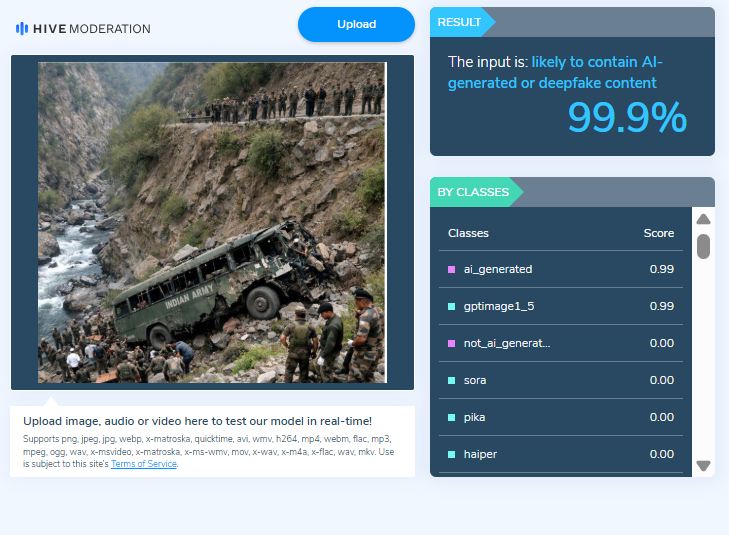
To verify the claim, we first closely examined the viral image. Several visual inconsistencies were observed. The structure of the soldier visible inside the damaged vehicle appears distorted, and the hands and limbs of people involved in the rescue operation look unnatural. These anomalies raised suspicion that the image might be AI-generated. Based on this, we ran the image through the AI detection tool Hive Moderation, which indicated that the image is over 99.9% likely to be AI-generated.
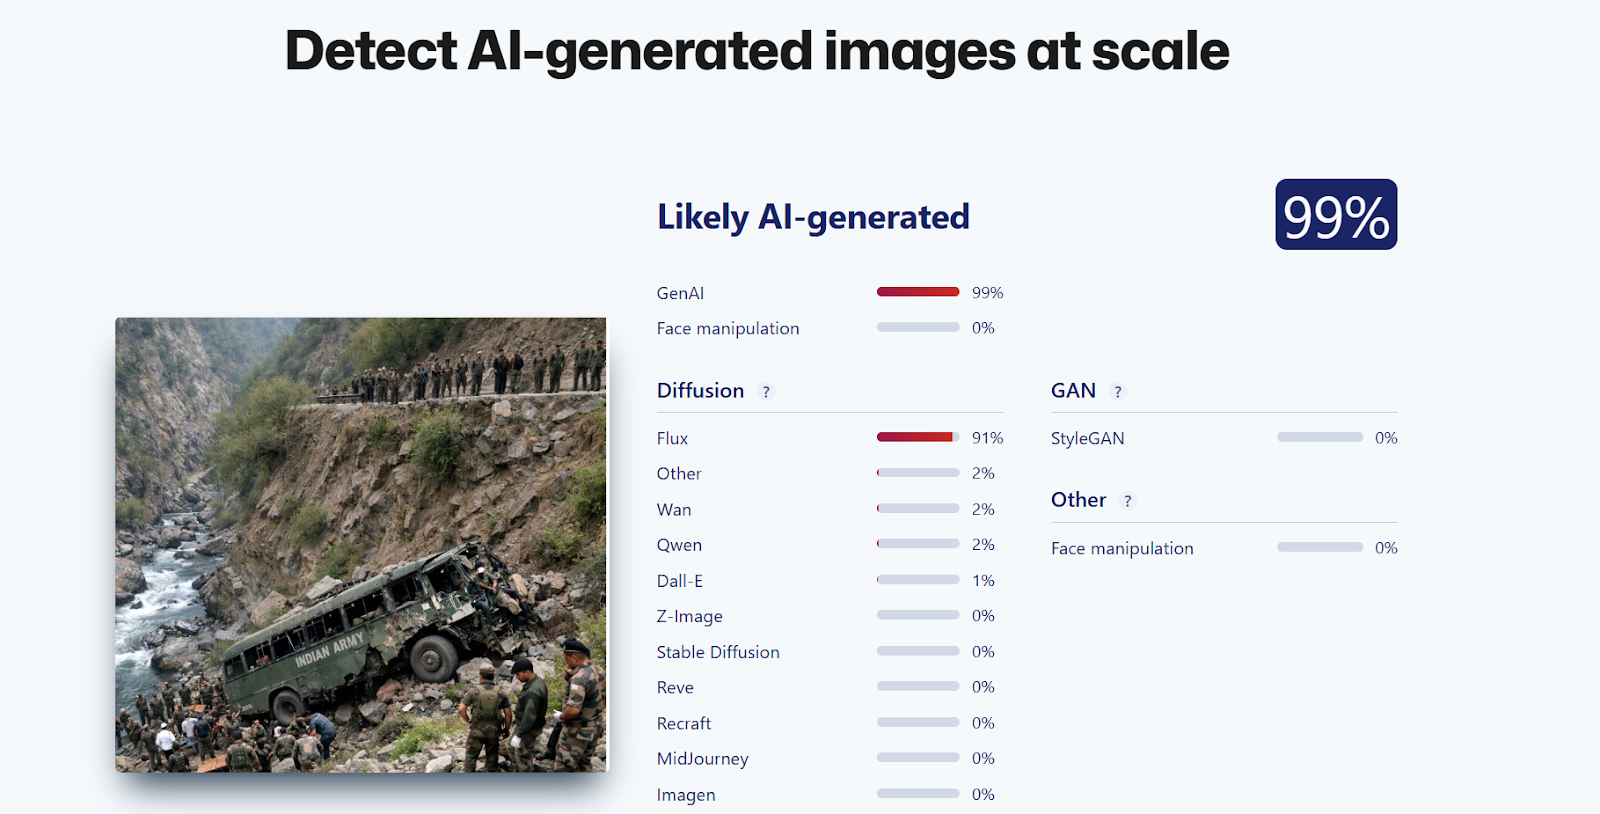
Another AI image detection tool, Sightengine, also flagged the image as 99% AI-generated.
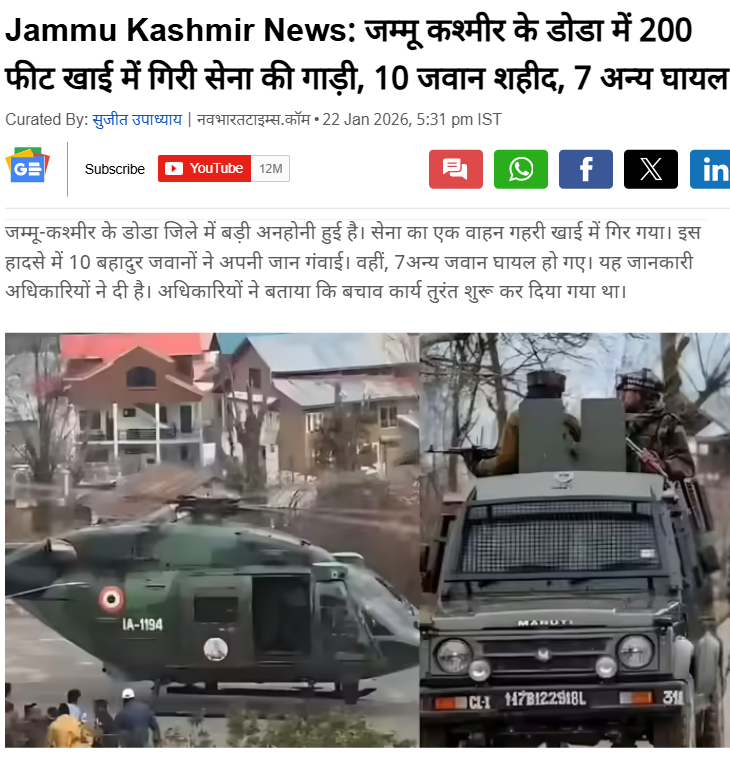
During further research , we found a report published by Navbharat Times on January 22, 2026, which confirmed that an Indian Army vehicle had indeed fallen into a deep gorge in Doda district. According to officials, 10 soldiers were killed and 7 others were injured, and rescue operations were immediately launched.
However, it is important to note that the image circulating on social media is not an actual photograph from the incident.
Conclusion
CyberPeace research confirms that the viral image linked to the Doda Army vehicle accident has been created using Artificial Intelligence. It is not a real photograph from the incident, and therefore, the viral post is misleading.

Executive Summary
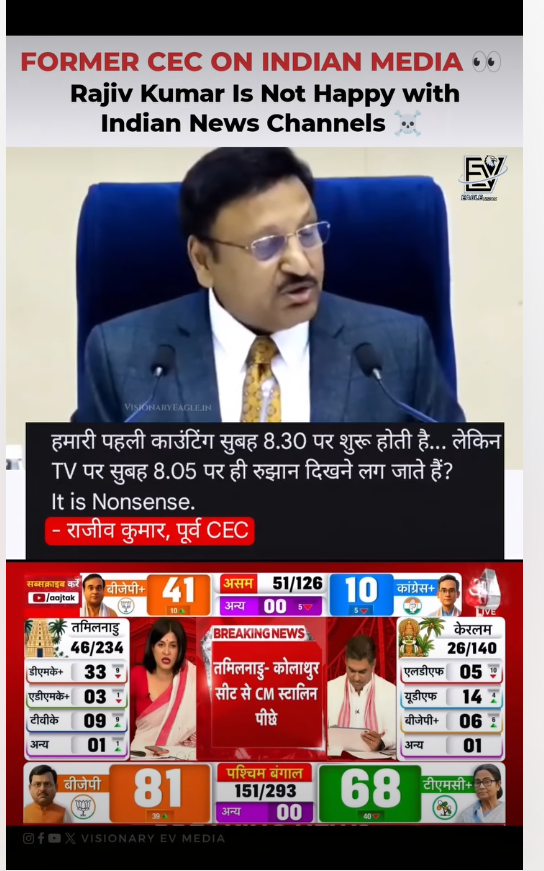
Following the results of the recent West Bengal elections, a video of former Chief Election Commissioner Rajiv Kumar has gone viral on social media. In the clip, Kumar is seen questioning television news channels over their election-result coverage and alleged early “trends” before the actual counting process begins. In the viral video, Rajiv Kumar can be heard saying, “When counting begins, channels start showing trends from 8:05 AM itself, which is nonsense. The first round of counting starts only at 8:30 AM. We have evidence that leads were being shown before that. Is it possible that these early trends are shown just to justify exit polls?”The video is being widely shared with the claim that Kumar made these remarks after the recently concluded West Bengal Assembly elections Research conducted by CyberPeace Research Wing found that a 2024 video of former Chief Election Commissioner Rajiv Kumar is being misleadingly shared as a recent statement made after the West Bengal election results.
Claim
An Instagram user shared the viral clip suggesting that the former Election Commissioner made these comments in the context of the latest West Bengal poll results.
Fact Check
Using relevant keyword searches, we traced the original source of the clip to an official post shared by the Election Commission of Indiaon Facebook on October 15, 2024. The video was part of a press conference announcing the Assembly election schedule for Maharashtra and Jharkhand.
We also found the complete live-streamed press conference on the official YouTube channel of the Election Commission.
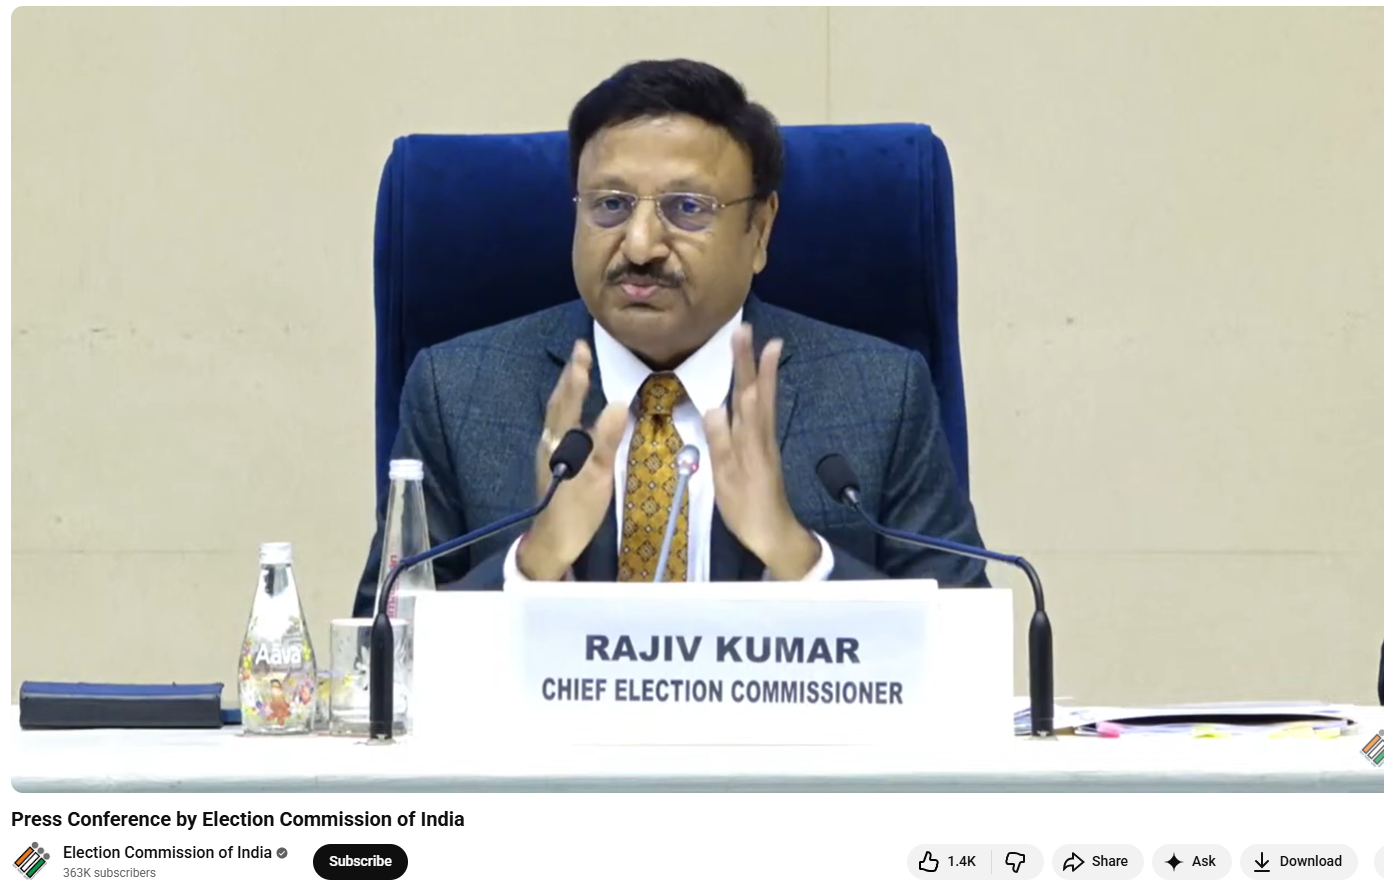
During the press conference, around the 26:45-minute mark, an ANI journalist referred to discrepancies between exit polls and actual Lok Sabha election results and asked whether such situations fuel doubts over EVMs among the public. Responding to the question at around 30:27 minutes, Rajiv Kumar spoke about the need for self-regulation in electronic media and concerns over premature “trends” shown during counting day. He said that exit polls often create public expectations despite lacking a clear scientific basis and questioned why TV channels begin displaying leads even before the first official counting round starts.
Conclusion
The viral claim is misleading. The video of former Chief Election Commissioner Rajiv Kumar is not related to the recent West Bengal election results. The clip is from an October 15, 2024 press conference held to announce the Maharashtra and Jharkhand Assembly election schedule and is now being falsely shared in a misleading context after the West Bengal polls.

Executive Summary:
Recently PAN-OS software of Palo Alto Networks was discovered with the critical vulnerability CVE-2024-3400. It is the software used to power all their networks in the next generation firewalls. This vulnerability is a common injection vulnerability which provides access to unauthenticated attackers to execute random code having root privileges on the attacked system. This has been exploited actively by threat actors, leaving many organizations at risk for severe cyberattacks. This report helps to understand the exploitation, detection, mitigations and recommendations for this vulnerability.

Understanding The CVE-2024-3400 Vulnerability:
CVE-2024-3400 impacts the particular version of PAN-OS and a certain configuration susceptible to this kind of a security issue. It is a command injection, which exists in the GlobalProtect module of the PAN-OS software. The vulnerability can be exploited by an unauthorized user to run any code on the firewall having root privileges. This targets Active Directory database (ntds.dit), important data (DPAPI), and Windows event logs (Microsoft-Windows-TerminalServices-LocalSessionManager%4Operational.evtx) and also login data, cookies, and local state data for Chrome and Microsoft Edge from specific targets leading attackers to capture the browser master key and steal sensitive information of the organization.
The CVE-2024-3400 has been provided with a critical severity rating of 10.0. The following two weaknesses make this CVE highly severe:
- CWE-77: Improper Neutralization of Special Elements used in a Command ('Command Injection')
- CWE-20: Improper Input Validation.
Impacted Products:
The affected version of PAN-OS by CVE-2024-3400 are-

Only the versions 10.2, 11.0, and 11.1, setup with GlobalProtect Gateway or GlobalProtect Portal are exploited by this vulnerability. Whereas the Cloud NGFW, Panorama appliances and Prisma Access are not affected.
Detecting Potential Exploitation:
Palo Alto Networks has confirmed that they are aware of the exploitation of this particular vulnerability by threat actors. In a recent publication they have given acknowledgement to Volexity for identifying the vulnerability. There is an increasing number of organizations that face severe and immediate risk by this exploitation. Third parties also have released the proof of concept for the vulnerability.
The suggestions were provided by Palo Alto Networks to detect this critical vulnerability. To detect this vulnerability, the following command shall be run on the command-line interface of PAN-OS device:
grep pattern "failed to unmarshal session(.\+.\/" mp-log gpsvc.log*
This command looks through device logs for specific entries related to vulnerability.
These log entries should contain a long, random-looking code called a GUID (Globally Unique Identifier) between the words "session(" and ")". If an attacker has tried to exploit the vulnerability, this section might contain a file path or malicious code instead of a GUID.
Presence of such entries in your logs, could be a sign of a potential attack to hack your device which may look like:
- failed to unmarshal session(../../some/path)
A normal, harmless log entry would look like this:
- failed to unmarshal session(01234567-89ab-cdef-1234-567890abcdef)
Further investigations and actions shall be needed to secure the system in case the GUID entries were not found and suspicious.
Mitigation and Recommendations:
Mitigation of the risks posed by the critical CVE-2024-3400 vulnerability, can be accomplished by the following recommended steps:
- Immediately update Software: This vulnerability is fixed in software releases namely PAN-OS 10.2.9-h1, PAN-OS 11.0.4-h1, PAN-OS 11.1.2-h3, and all higher versions. Updating software to these versions will protect your systems fully against potential exploitation.
- Leverage Hotfixes: Palo Alto Networks has released hotfixes for commonly deployed maintenance releases of PAN-OS 10.2, 11.0, and 11.1 for the users who cannot upgrade to the latest versions immediately. These hotfixes do provide a temporary solution while you prepare for the full upgrade.
- Enable Threat Prevention: Incase of available Threat Prevention subscription, enable Threat IDs 95187, 95189, and 95191 to block attacks targeting the CVE-2024-3400 vulnerability. These Threat IDs are available in Applications and Threats content version 8836-8695 and later.
- Apply Vulnerability Protection: Ensure that vulnerability protection has been applied in the GlobalProtect interface to prevent the exploitation on the device. It can be implemented using these instructions.
- Monitor Advisory Updates: Regularly checking for the updates to the official advisory of Palo Alto Networks. This helps to stay up to date of the new releases of the guidance and threat prevention IDs of CVE-2024-3400.
- Disable Device Telemetry – Optional: It is suggested to disable the device telemetry as an additional precautionary measure.
- Remediation: If there is an active exploitation observed, follow the steps mentioned in this Knowledge Base article by Palo Alto Networks.
Implementation of the above mitigation measures and recommendations would be in a position to greatly reduce the risk of exploitation you might face from a cyber attack targeting the CVE-2024-3400 vulnerability in Palo Alto Networks' PAN-OS software.
Conclusion:
The immediate response should be taken against the offensive use of the critical CVE-2024-3400 vulnerability found in the PAN-OS platform of Palo Alto Networks. Organizations should actively respond by implementing the suggested mitigation measures such as upgrading to the patched versions, enabling threat prevention and applying vulnerability protection to immediately protect from this vulnerability. Regular monitoring, implementing security defense mechanisms and security audits are the necessary measures that help to combat emerging threats and save critical resources.
