
#FactCheck - Debunking Viral Photo: Tears of Photographer Not Linked to Ram Mandir Opening
Executive Summary:
A photographer breaking down in tears in a viral photo is not connected to the Ram Mandir opening. Social media users are sharing a collage of images of the recently dedicated Lord Ram idol at the Ayodhya Ram Mandir, along with a claimed shot of the photographer crying at the sight of the deity. A Facebook post that posts this video says, "Even the cameraman couldn't stop his emotions." The CyberPeace Research team found that the event happened during the AFC Asian Cup football match in 2019. During a match between Iraq and Qatar, an Iraqi photographer started crying since Iraq had lost and was out of the competition.
Claims:
The photographer in the widely shared images broke down in tears at seeing the icon of Lord Ram during the Ayodhya Ram Mandir's consecration. The Collage was also shared by many users in other Social Media like X, Reddit, Facebook. An Facebook user shared and the Caption of the Post reads,


Fact Check:
CyberPeace Research team reverse image searched the Photographer, and it landed to several memes from where the picture was taken, from there we landed to a Pinterest Post where it reads, “An Iraqi photographer as his team is knocked out of the Asian Cup of Nations”

Taking an indication from this we did some keyword search and tried to find the actual news behind this Image. We landed at the official Asian Cup X (formerly Twitter) handle where the image was shared 5 years ago on 24 Jan, 2019. The Post reads, “Passionate. Emotional moment for an Iraqi photographer during the Round of 16 clash against ! #AsianCup2019”

We are now confirmed about the News and the origin of this image. To be noted that while we were investigating the Fact Check we also found several other Misinformation news with the Same photographer image and different Post Captions which was all a Misinformation like this one.
Conclusion:
The recent Viral Image of the Photographer claiming to be associated with Ram Mandir Opening is Misleading, the Image of the Photographer was a 5 years old image where the Iraqi Photographer was seen Crying during the Asian Cup Football Competition but not of recent Ram Mandir Opening. Netizens are advised not to believe and share such misinformation posts around Social Media.
- Claim: A person in the widely shared images broke down in tears at seeing the icon of Lord Ram during the Ayodhya Ram Mandir's consecration.
- Claimed on: Facebook, X, Reddit
- Fact Check: Fake

Related Blogs

Executive Summary
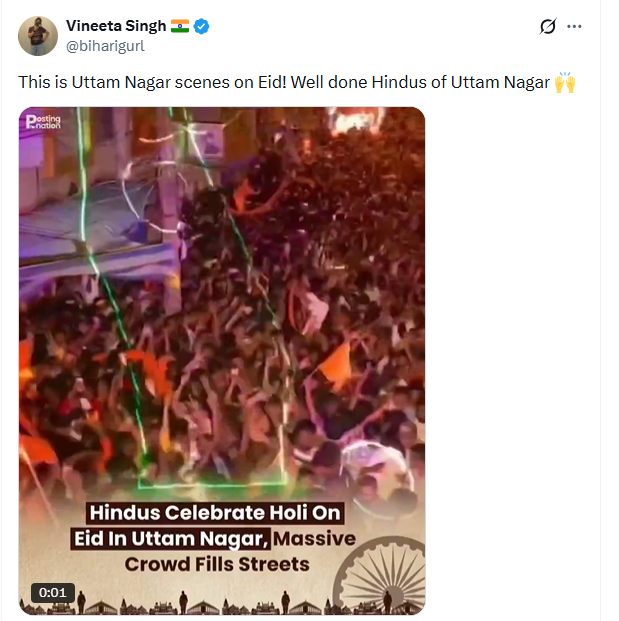
A video is being shared on social media showing a group of people dancing on a road while carrying saffron flags. A mosque can also be seen nearby in the video Sharing this clip, some users are claiming that it is from Uttam Nagar in Delhi, where members of the Hindu community celebrated Holi on the occasion of Eid on March 21. Research by the CyberPeace found the viral claim to be misleading. Our probe revealed that the video is not related to Holi celebrations on Eid in Uttam Nagar, Delhi. In fact, the video has been available on the internet since 2024 and is said to be from Raichur district in Karnataka. Several users have shared it claiming that it was recorded during Ganesh Chaturthi celebrations.
Claim:
A social media user shared the viral video on March 21, 2026, with a misleading claim. The link and archive link of the post are given below.
Fact Check:
To verify the viral claim, we first conducted a keyword search on Google. However, we did not find any credible media report supporting the claim. In the next step, we extracted keyframes from the video and performed a reverse search using Google Lens. During this process, we found the same video on an Instagram account, which was posted on September 23, 2024.
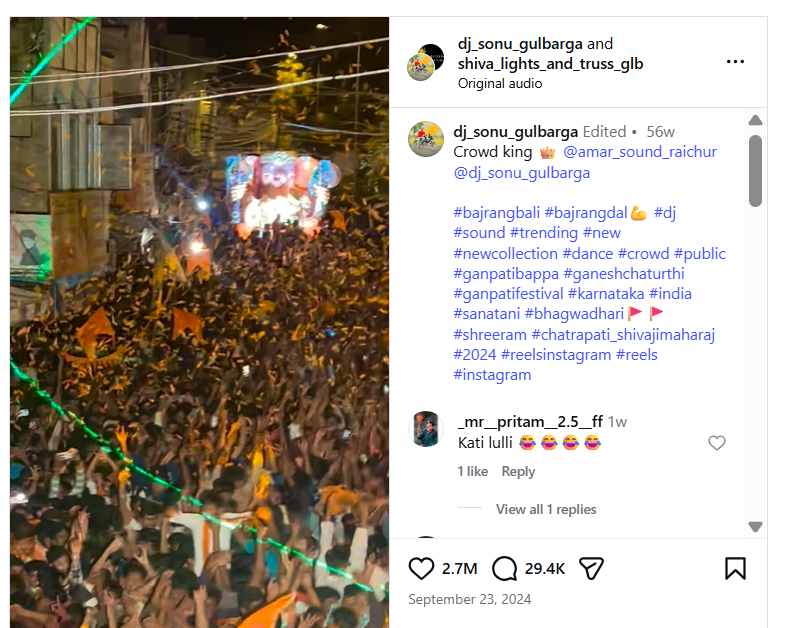
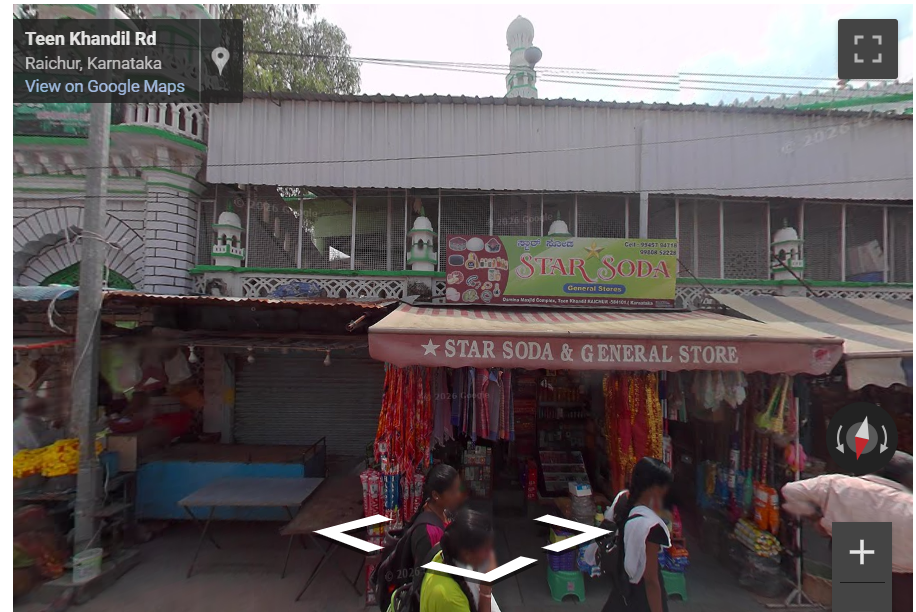
The user had captioned the video as “Ganesh Chaturthi 2024,” suggesting that the clip is related to the festival. Further, upon closely analyzing the video, we noticed that the mosque visible in the background had “Usmania Masjid” written on it. We then searched for this location on Google Maps and found that the mosque is located on Teen Khandil Road in Raichur, Karnataka, which matches the visuals seen in the viral clip.
Conclusion:
Our research found that the video is not from Uttam Nagar, Delhi, nor is it related to Holi celebrations on Eid. The clip has been available online since 2024 and is from Raichur, Karnataka. It has been shared with a misleading claim and is actually linked to Ganesh Chaturthi celebrations.
Introduction
For years, the story of terror recruitment in Jammu & Kashmir followed a familiar arc: physical infiltration across the Line of Control, local Over Ground Workers (OGWs) acting as couriers, and recruitment pitches on mainstream apps like WhatsApp and Facebook Messenger. Indian security agencies built entire surveillance architectures around that arc. Now, officials say, the architecture is being outflanked in a way few anticipated: through pornography and dating platforms.
The New Front: Chat Rooms Nobody Is Watching
According to officials cited in recent reporting, Pakistan-based terror handlers working in coordination with Pakistan's ISI have begun exploiting the real-time chat features built into pornography and dating websites to reach recruits in Jammu & Kashmir. These pornography platforms feature real-time chat tools that operate under the guise of helping users find dates nearby, and handlers are exploiting that feature to broadcast messages and coordinate activities. It's a strikingly mundane pivot for an organisation engaged in violent extremism, but that is precisely the point that nobody expects a counter-terror dragnet to be watching a dating chatbox.
Officials say the tactic is designed to evade the surveillance that has become standard on conventional social media platforms, allowing handlers to convey instructions to recruits while staying off the radar of established monitoring tools. WhatsApp, Signal and Facebook Messenger have all, in various ways, become known quantities to Indian intelligence subject to legal intercepts, metadata analysis and years of institutional familiarity. A chat window buried inside an adult content site is not.
Tor, Encrypted Nodes, and Apps Built to Disappear
Other than porn sites, investigators have also flagged a cluster of niche, privacy-first messaging apps that route traffic through Tor-based, encrypted nodes to mask user identity. Security agencies have placed a wide array of specialised digital tools under scrutiny, with terror handlers relying on Tor-based messaging applications like Coatex and Conion to route data through encrypted nodes and obscure user identities. Access to at least one of these apps' installation files is reportedly already restricted within India, though enforcement against sideloaded Android packages remains an uphill battle.
What makes these platforms attractive to handlers isn't unique code so much as the design philosophy behind privacy-first messaging generally. Some of these apps offer only basic encryption, while others go further with end-to-end encryption, self-destructing messages, and strong on-device encryption algorithms that keep data processing off any third-party server. Several reportedly allow account creation without a phone number or SIM verification, stripping away one of the most basic identity anchors that Indian telecom-linked surveillance depends on.
There's also an operational, almost logistical, reason for the shift: connectivity. Officials note that some of these applications provide end-to-end encryption, self-destructing messages and registration without a phone number or email, making it difficult for security agencies to trace users, even as terror networks also shift away from commonly used platforms. In the hilly, forested and often poorly connected terrain of Jammu's border districts, apps engineered to function on weak 2G or EDGE networks have an obvious tactical advantage over data-hungry mainstream platforms.
VPNs, Banned Apps, and a Cat-and-Mouse Game
Virtual Private Networks add another layer of obfuscation, letting operatives access apps banned in India and mask the geographic origin of their traffic. This isn't new tradecraft, but its pairing with adult-content chat infrastructure and Tor-routed messaging represents a genuinely novel combination in the Kashmir context, according to the officials describing the pattern to reporters.
The broader trend line, officials say, is a steady migration away from platforms Indian agencies have learned to monitor. Terror networks are increasingly moving away from mainstream, commonly used platforms in favour of more obscure alternatives, forcing intelligence agencies into a perpetual game of catch-up: each time a monitoring capability matures against one platform, handlers migrate to the next.
This is not the first time investigators have flagged this cat-and-mouse dynamic. Reporting on a recent case in Jammu's Bathindi area described a 19-year-old allegedly radicalised through the encrypted app. Session the same platform reportedly linked to suspects in a Delhi bomb plot investigation after months of contact with Pakistan-based handlers. Investigators in that case noted that terror organisations have increasingly turned to multi-layered encrypted messaging services specifically to evade monitoring by intelligence agencies.
The Virtual SIM Problem
Alongside app-layer evasion, foreign-issued virtual SIM cards remain a persistent headache for investigators. The most cited example remains the 2019 Pulwama attack investigation, in which agencies reportedly traced more than 40 virtual SIM cards to the Jaish-e-Mohammed suicide bomber and his network numbers that could be provisioned and abandoned without ever touching an Indian telecom's KYC system. That case became something of a template for how virtual and foreign-registered numbers can be used to build communication chains that are extremely difficult to map after the fact, since there is no physical SIM, no retail purchase record, and often no domestic carrier data trail at all.
More recent J&K cases echo the same pattern in a different form. Police investigating a cross-border radicalisation network noted that intelligence agencies now suspect unauthorised SIM card distribution is being used by terrorists to communicate with handlers across the border, part of a broader push to choke off the logistical and communication backbone that keeps sleeper modules alive even when direct physical contact with a local handler is minimal or non-existent.
How Agencies Are Responding
To their credit, security agencies aren't standing still. Officials say cyber-surveillance frameworks are actively being redesigned to map and intercept these "off-grid" communication channels, a phrase that itself signals how far outside traditional monitoring territory this recruitment method has moved. Agencies say they continue to adapt their cyber-surveillance frameworks specifically to map and intercept these off-grid communication channels. That has included moving to restrict access to specific APKs, tightening scrutiny of virtual number providers, and, as seen in recent CIK (Counter Intelligence Kashmir) operations, proactively disrupting online propaganda networks before recruitment pitches can mature into operational plots. One recent CIK operation, for instance, intercepted attempts to recruit two teenage boys who were allegedly being fed terror content in the direction of a Pakistan-based handler, underlining how young the target pool for these campaigns has become.
Conclusion
What this episode really illustrates isn't a single clever trick but a structural truth about counter-terror surveillance: it is inherently reactive. Every time agencies build competence around a platform, handlers find a low-attention, high-friction-to-monitor alternative: first fringe messaging apps, then Tor-routed clients, and now the sprawling, largely unregulated back-end of adult content platforms, which few people would ever think to associate with national security. It's a reminder that the fight against radicalisation online is no longer confined to obviously "extremist" corners of the internet; it can hide in plain sight, inside the most ordinary-looking corners of the web.
Sources
- New J-K terror tactic: Pornography apps, Tor network used for secret messaging — The Tribune
- New J&K terror tactic: Handlers turn to porn sites, encrypted apps to contact recruits — Deccan Herald
- Terrorists using porn website, encrypted apps for chats with recruits — Organiser
- New J&K Terror Tactic: Pornography Apps, Tor Network Used For Secret Messaging — Kashmir Dot Com
- From WhatsApp to Porn Sites: Terror Groups Adopt New Digital Tactic in J&K — Jammu Kashmir Now
- Jammu teenager's arrest exposes cross-border radicalisation network — The Tribune
- After OGW network, J&K cops target communication channel of terrorists — The Tribune
- CIK busts online radical network, foils recruitment of two minors — The Tribune

Overview:
A recent addition to the list of cybercrime is SharpRhino, a RAT (Remote Access Trojan) actively used by Hunters International ransomware group. SharpRhino is highly developed and penetrates into the network mask of IT specialists, primarily due to the belief in the tools’ legitimacy. Going under the genuine software installer, SharpRhino started functioning in mid-June 2024. However, Quorum Cyber discovered it in early August 2024 while investigating ransomware.
About Hunters International Group:
Hunters International emerged as one of the most notorious groups focused on ransomware attacks, having compromised over 134 targets worldwide in the first seven months of 2024. It is believed that the group is the rebranding of Hive ransomware group that was previously active, and there are considerable similarities in the code. Its focus on IT employees in particular demonstrates the fact that they move tactically in gaining access to the organizations’ networks.
Modus Operandi:
1. Typosquatting Technique
SharpRhino is mainly distributed by a domain that looks like the genuine Angry IP Scanner, which is a popular network discovery tool. The malware installer, labeled as ipscan-3.9.1-setup. It is a 32-bit Nullsoft installer which embeds a password protected 7z archive in it.
2. Installation Process
- Execution of Installer: When the victim downloads and executes the installer and changes the windows registry in order to attain persistence. This is done by generating a registry entry that starts a harmful file, Microsoft. AnyKey. exe, are fakes originating from fake versions of true legitimate Microsoft Visual Studio tools.
- Creation of Batch File: This drops a batch file qualified as LogUpdate at the installer.bat, that runs the PowerShell scripts on the device. These scripts are to compile C# code into memory to serve as a means of making the malware covert in its operation.
- Directory Creation: The installer establishes two directories that allow the C2 communication – C:\ProgramData\Microsoft: WindowsUpdater24 and LogUpdateWindows.
3. Execution and Functionality:
- Command Execution: The malware can execute PowerShell commands on the infected system, these actions may involve privilege escalation and other extended actions such as lateral movement.
- C2 Communication: SharpRhino interacts with command and control servers located on domains from platforms such as Cloudflare. This communication is necessary for receiving commands from the attackers and for returning any data of interest to the attackers.
- Data Exfiltration and Ransomware Deployment: Once SharpRhino has gained control, it can steal information and then proceed to encrypt it with a .locked extension. The procedure generally concludes with a ransom message, which informs users on how to purchase the decryption key.
4. Propagation Techniques:
Also, SharpRhino can spread through the self-copying method, this is the virus may copy itself to other computers using the network account of the victim and pretending to be trustworthy senders such as emails or network-shared files. Moreover, the victim’s machine may then proceed to propagate the malware to other systems like sharing in the company with other employees.
Indicators of Compromise (IOCs):
- LogUpdate.bat
- Wiaphoh7um.t
- ipscan-3.9.1-setup.exe
- kautix2aeX.t
- WindowsUpdate.bat
Command and Control Servers:
- cdn-server-1.xiren77418.workers.dev
- cdn-server-2.wesoc40288.workers.dev
- Angryipo.org
- Angryipsca.com
Analysis:

Graph:

Precautionary measures to be taken:
To mitigate the risks posed by SharpRhino and similar malware, organizations should implement the following measures:
- Implement Security Best Practices: It is important only to download software from official sites and avoid similar sites to confuse the user by changing a few letters.
- Enhance Detection Capabilities: Use technology in detection that can detect the IOCs linked to Sharp Rhino.
- Educate Employees: Educate IT people and employees on phishing scams and the requirement to check the origin of the application.
- Regular Backups: It is also important to back up important files from systems and networks in order to minimize the effects of ransomware attacks on a business.
Conclusion:
SharpRhino could be deemed as the evolution of the strategies used by organizations like Hunters International and others involved in the distribution of ransomware. SharpRhino primarily focuses on the audience of IT professionals and employs complex delivery and execution schemes, which makes it an extremely serious threat for corporate networks. To do so it is imperative that organizations have an understanding of its inner workings in order to fortify their security measures against this relatively new threat. Through the enforcement of proper security measures and constant enlightenment of organizations on the importance of cybersecurity, firms can prevent the various risks associated with SharpRhino and related malware. Be safe, be knowledgeable, and most importantly, be secure when it comes to cyber security for your investments.
Reference:
https://cybersecuritynews.com/sharprhino-ransomware-alert/
https://cybersecsentinel.com/sharprhino-explained-key-facts-and-how-to-protect-your-data/
https://www.dataprivacyandsecurityinsider.com/2024/08/sharprhino-malware-targeting-it-professionals/
