
#FactCheck - Bangladeshi Migrant’s Arrest Misrepresented as Indian in Viral Video!
Executive Summary:
An old video dated 2023 showing the arrest of a Bangladeshi migrant for murdering a Polish woman has been going viral massively on social media claiming that he is an Indian national. This viral video was fact checked and debunked.
Claim:
The video circulating on social media alleges that an Indian migrant was arrested in Greece for assaulting a young Christian girl. It has been shared with narratives maligning Indian migrants. The post was first shared on Facebook by an account known as “Voices of hope” and has been shared in the report as well.

Facts:
The CyberPeace Research team has utilized Google Image Search to find the original source of the claim. Upon searching we find the original news report published by Greek City Times in June 2023.


The person arrested in the video clip is a Bangladeshi migrant and not of Indian origin. CyberPeace Research Team assessed the available police reports and other verifiable sources to confirm that the arrested person is Bangladeshi.
The video has been dated 2023, relating to a case that occurred in Poland and relates to absolutely nothing about India migrants.
Neither the Polish government nor authorized news agency outlets reported Indian citizens for the controversy in question.

Conclusion:
The viral video falsely implicating an Indian migrant in a Polish woman’s murder is misleading. The accused is a Bangladeshi migrant, and the incident has been misrepresented to spread misinformation. This highlights the importance of verifying such claims to prevent the spread of xenophobia and false narratives.
- Claim: Video shows an Indian immigrant being arrested in Greece for allegedly assaulting a young Christian girl.
- Claimed On: X (Formerly Known As Twitter) and Facebook.
- Fact Check: Misleading.

Related Blogs

Executive Summary:
A viral social media message claims that the Indian government is offering a ₹5,000 gift to citizens in celebration of Prime Minister Narendra Modi’s birthday. However, this claim is false. The message is part of a deceptive scam that tricks users into transferring money via UPI, rather than receiving any benefit. Fact-checkers have confirmed that this is a fraud using misleading graphics and fake links to lure people into authorizing payments to scammers.

Claim:
The post circulating widely on platforms such as WhatsApp and Facebook states that every Indian citizen is eligible to receive ₹5,000 as a gift from the current Union Government on the Prime Minister’s birthday. The message post includes visuals of PM Modi, BJP party symbols, and UPI app interfaces such as PhonePe or Google Pay, and urges users to click on the BJP Election Symbol [Lotus] or on the provided link to receive the gift directly into their bank account.


Fact Check:
Our research indicates that there is no official announcement or credible article supporting the claim that the government is offering ₹5,000 under the Pradhan Mantri Jan Dhan Yojana (PMJDY). This claim does not appear on any official government websites or verified scheme listings.

While the message was crafted to appear legitimate, it was in fact misleading. The intent was to deceive users into initiating a UPI payment rather than receiving one, thereby putting them at financial risk.
A screen popped up showing a request to pay ₹686 to an unfamiliar UPI ID. When the ‘Pay ₹686’ button was tapped, the app asked for the UPI PIN—clearly indicating that this would have authorised a payment straight from the user’s bank account to the scammer’s.

We advise the public to verify such claims through official sources before taking any action.
Our research indicated that the claim in the viral post is false and part of a fraudulent UPI money scam.

Clicking the link that went with the viral Facebook post, it took us to a website
https://wh1449479[.]ispot[.]cc/with a somewhat odd domain name of 'ispot.cc', which is certainly not a government-related or commonly known domain name. On the website, we observed images that featured a number of unauthorized visuals, including a Prime Minister Narendra Modi image, a Union Minister and BJP President J.P. Nadda image, the national symbol, the BJP symbol, and the Pradhan Mantri Jan Dhan Yojana logo. It looked like they were using these visuals intentionally to convince users that the website was legitimate.
Conclusion:
The assertion that the Indian government is handing out ₹5,000 to all citizens is totally false and should be reported as a scam. The message uses the trust related to government schemes, tricking users into sending money through UPI to criminals. They recommend that individuals do not click on links or respond to any such message about obtaining a government gift prior to verification. If you or a friend has fallen victim to this fraud, they are urged to report it immediately to your bank, and report it through the National Cyber Crime Reporting Portal (https://cybercrime.gov.in) or contact the cyber helpline at 1930. They also recommend always checking messages like this through their official government website first.
- Claim: The Modi Government is distributing ₹5,000 to citizens through UPI apps
- Claimed On: Social Media
- Fact Check: False and Misleading
Introduction
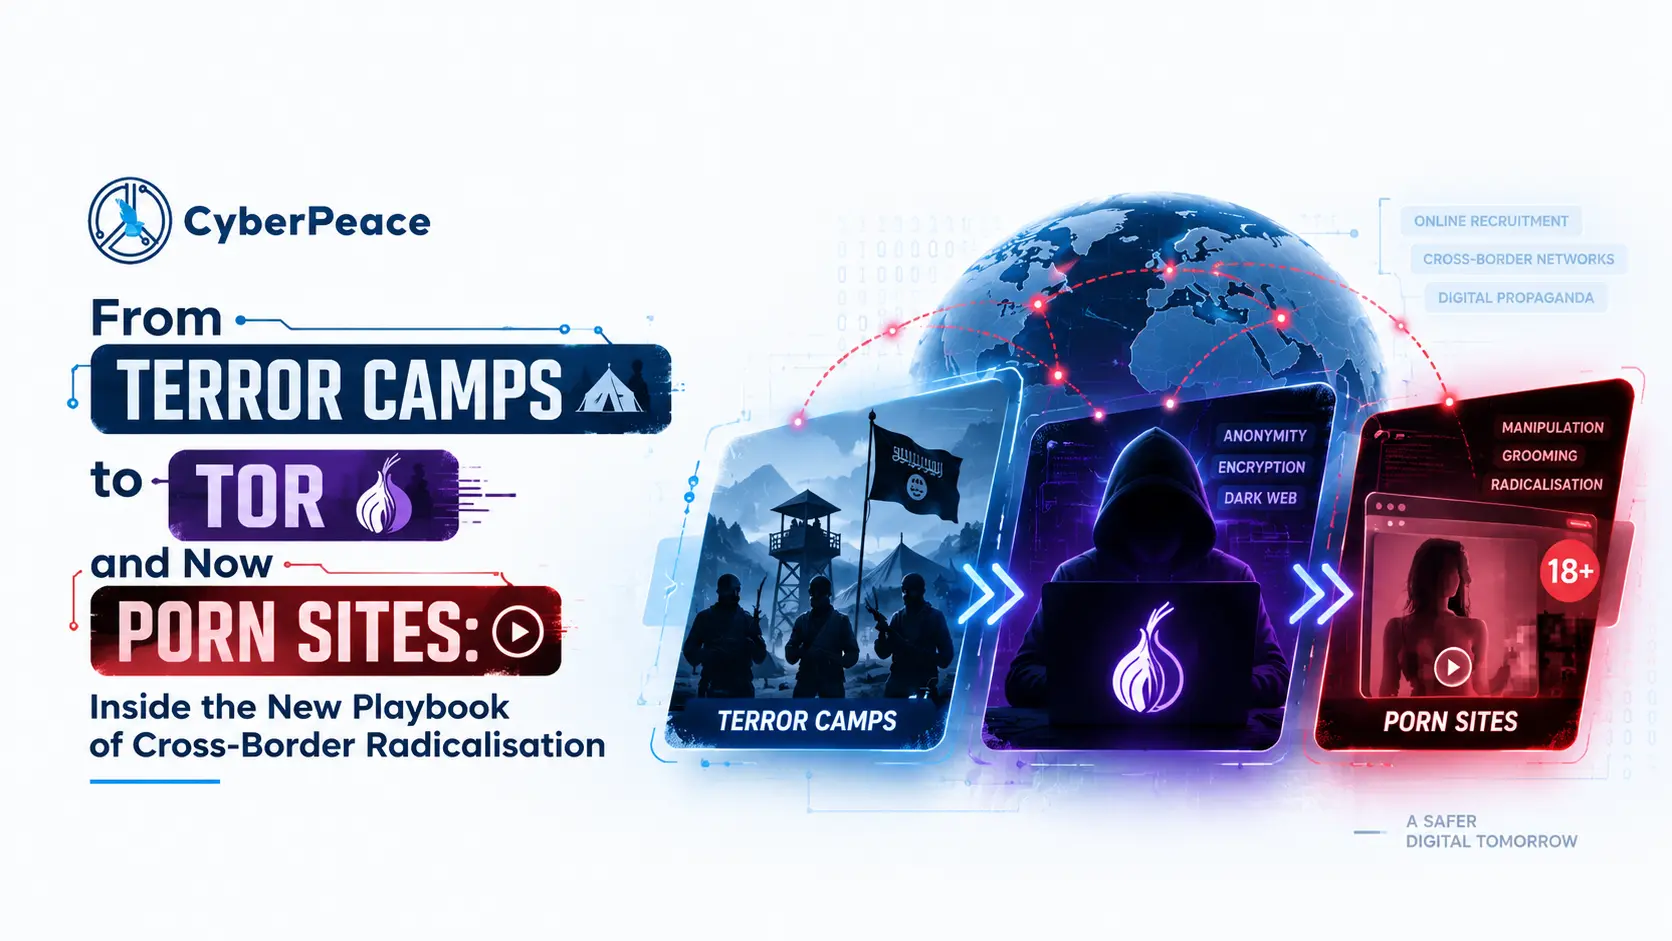
For years, the story of terror recruitment in Jammu & Kashmir followed a familiar arc: physical infiltration across the Line of Control, local Over Ground Workers (OGWs) acting as couriers, and recruitment pitches on mainstream apps like WhatsApp and Facebook Messenger. Indian security agencies built entire surveillance architectures around that arc. Now, officials say, the architecture is being outflanked in a way few anticipated: through pornography and dating platforms.
The New Front: Chat Rooms Nobody Is Watching
According to officials cited in recent reporting, Pakistan-based terror handlers working in coordination with Pakistan's ISI have begun exploiting the real-time chat features built into pornography and dating websites to reach recruits in Jammu & Kashmir. These pornography platforms feature real-time chat tools that operate under the guise of helping users find dates nearby, and handlers are exploiting that feature to broadcast messages and coordinate activities. It's a strikingly mundane pivot for an organisation engaged in violent extremism, but that is precisely the point that nobody expects a counter-terror dragnet to be watching a dating chatbox.
Officials say the tactic is designed to evade the surveillance that has become standard on conventional social media platforms, allowing handlers to convey instructions to recruits while staying off the radar of established monitoring tools. WhatsApp, Signal and Facebook Messenger have all, in various ways, become known quantities to Indian intelligence subject to legal intercepts, metadata analysis and years of institutional familiarity. A chat window buried inside an adult content site is not.
Tor, Encrypted Nodes, and Apps Built to Disappear
Other than porn sites, investigators have also flagged a cluster of niche, privacy-first messaging apps that route traffic through Tor-based, encrypted nodes to mask user identity. Security agencies have placed a wide array of specialised digital tools under scrutiny, with terror handlers relying on Tor-based messaging applications like Coatex and Conion to route data through encrypted nodes and obscure user identities. Access to at least one of these apps' installation files is reportedly already restricted within India, though enforcement against sideloaded Android packages remains an uphill battle.
What makes these platforms attractive to handlers isn't unique code so much as the design philosophy behind privacy-first messaging generally. Some of these apps offer only basic encryption, while others go further with end-to-end encryption, self-destructing messages, and strong on-device encryption algorithms that keep data processing off any third-party server. Several reportedly allow account creation without a phone number or SIM verification, stripping away one of the most basic identity anchors that Indian telecom-linked surveillance depends on.
There's also an operational, almost logistical, reason for the shift: connectivity. Officials note that some of these applications provide end-to-end encryption, self-destructing messages and registration without a phone number or email, making it difficult for security agencies to trace users, even as terror networks also shift away from commonly used platforms. In the hilly, forested and often poorly connected terrain of Jammu's border districts, apps engineered to function on weak 2G or EDGE networks have an obvious tactical advantage over data-hungry mainstream platforms.
VPNs, Banned Apps, and a Cat-and-Mouse Game
Virtual Private Networks add another layer of obfuscation, letting operatives access apps banned in India and mask the geographic origin of their traffic. This isn't new tradecraft, but its pairing with adult-content chat infrastructure and Tor-routed messaging represents a genuinely novel combination in the Kashmir context, according to the officials describing the pattern to reporters.
The broader trend line, officials say, is a steady migration away from platforms Indian agencies have learned to monitor. Terror networks are increasingly moving away from mainstream, commonly used platforms in favour of more obscure alternatives, forcing intelligence agencies into a perpetual game of catch-up: each time a monitoring capability matures against one platform, handlers migrate to the next.
This is not the first time investigators have flagged this cat-and-mouse dynamic. Reporting on a recent case in Jammu's Bathindi area described a 19-year-old allegedly radicalised through the encrypted app. Session the same platform reportedly linked to suspects in a Delhi bomb plot investigation after months of contact with Pakistan-based handlers. Investigators in that case noted that terror organisations have increasingly turned to multi-layered encrypted messaging services specifically to evade monitoring by intelligence agencies.
The Virtual SIM Problem
Alongside app-layer evasion, foreign-issued virtual SIM cards remain a persistent headache for investigators. The most cited example remains the 2019 Pulwama attack investigation, in which agencies reportedly traced more than 40 virtual SIM cards to the Jaish-e-Mohammed suicide bomber and his network numbers that could be provisioned and abandoned without ever touching an Indian telecom's KYC system. That case became something of a template for how virtual and foreign-registered numbers can be used to build communication chains that are extremely difficult to map after the fact, since there is no physical SIM, no retail purchase record, and often no domestic carrier data trail at all.
More recent J&K cases echo the same pattern in a different form. Police investigating a cross-border radicalisation network noted that intelligence agencies now suspect unauthorised SIM card distribution is being used by terrorists to communicate with handlers across the border, part of a broader push to choke off the logistical and communication backbone that keeps sleeper modules alive even when direct physical contact with a local handler is minimal or non-existent.
How Agencies Are Responding
To their credit, security agencies aren't standing still. Officials say cyber-surveillance frameworks are actively being redesigned to map and intercept these "off-grid" communication channels, a phrase that itself signals how far outside traditional monitoring territory this recruitment method has moved. Agencies say they continue to adapt their cyber-surveillance frameworks specifically to map and intercept these off-grid communication channels. That has included moving to restrict access to specific APKs, tightening scrutiny of virtual number providers, and, as seen in recent CIK (Counter Intelligence Kashmir) operations, proactively disrupting online propaganda networks before recruitment pitches can mature into operational plots. One recent CIK operation, for instance, intercepted attempts to recruit two teenage boys who were allegedly being fed terror content in the direction of a Pakistan-based handler, underlining how young the target pool for these campaigns has become.
Conclusion
What this episode really illustrates isn't a single clever trick but a structural truth about counter-terror surveillance: it is inherently reactive. Every time agencies build competence around a platform, handlers find a low-attention, high-friction-to-monitor alternative: first fringe messaging apps, then Tor-routed clients, and now the sprawling, largely unregulated back-end of adult content platforms, which few people would ever think to associate with national security. It's a reminder that the fight against radicalisation online is no longer confined to obviously "extremist" corners of the internet; it can hide in plain sight, inside the most ordinary-looking corners of the web.
Sources
- New J-K terror tactic: Pornography apps, Tor network used for secret messaging — The Tribune
- New J&K terror tactic: Handlers turn to porn sites, encrypted apps to contact recruits — Deccan Herald
- Terrorists using porn website, encrypted apps for chats with recruits — Organiser
- New J&K Terror Tactic: Pornography Apps, Tor Network Used For Secret Messaging — Kashmir Dot Com
- From WhatsApp to Porn Sites: Terror Groups Adopt New Digital Tactic in J&K — Jammu Kashmir Now
- Jammu teenager's arrest exposes cross-border radicalisation network — The Tribune
- After OGW network, J&K cops target communication channel of terrorists — The Tribune
- CIK busts online radical network, foils recruitment of two minors — The Tribune
Executive Summary
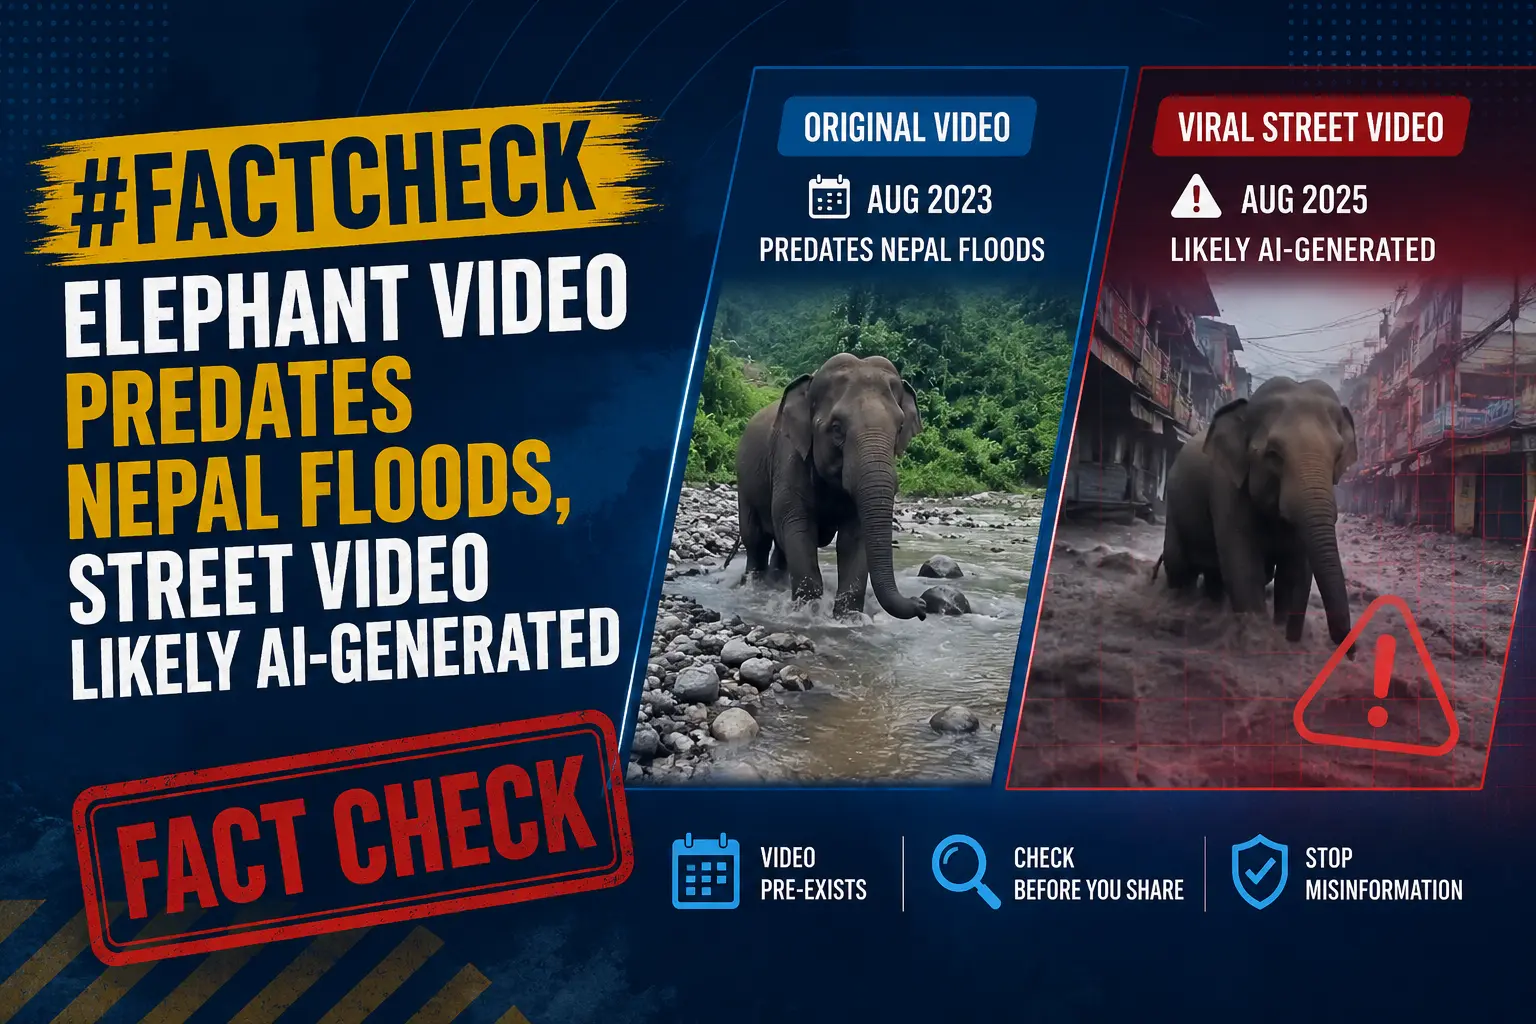
Amid the floods in Nepal, several videos are being shared on social media, claiming to show the current situation in the country. A research done by the Research Wing of the CyberPeace found that the video showing elephants is from an incident that occurred before the floods in Nepal, while the video showing the street is likely AI-generated.
Claim 1
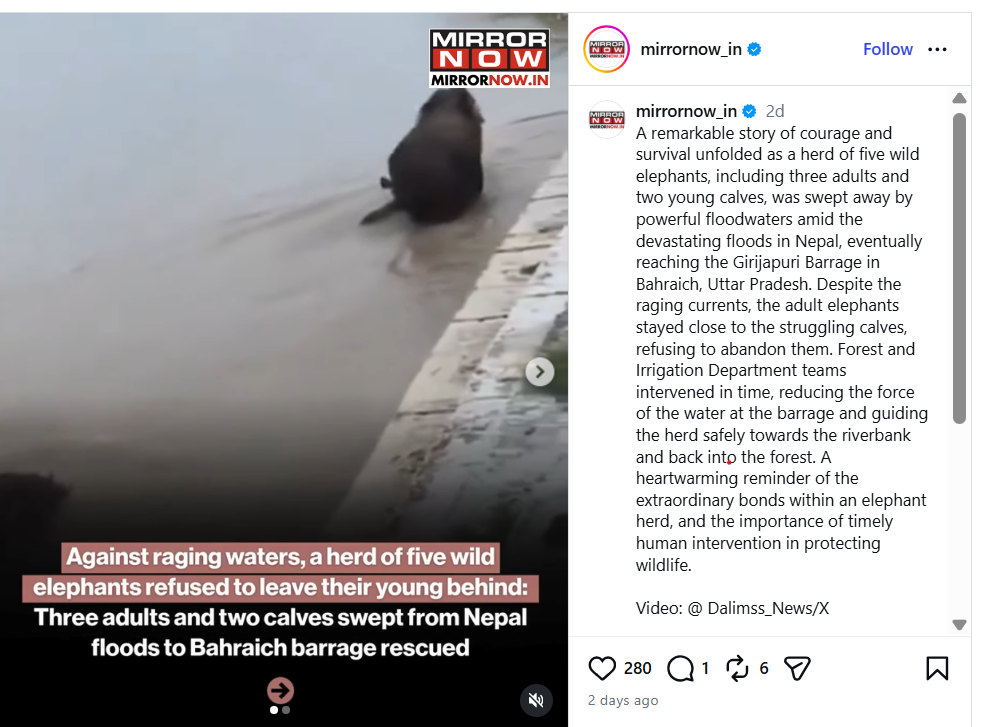
Videos claiming to show a street being swept away by flash floods in Nepal and a herd of elephants being carried away by the floods and reaching Uttar Pradesh are going viral on social media.
https://www.instagram.com/p/DcimGaiiCa7/
Claim 2
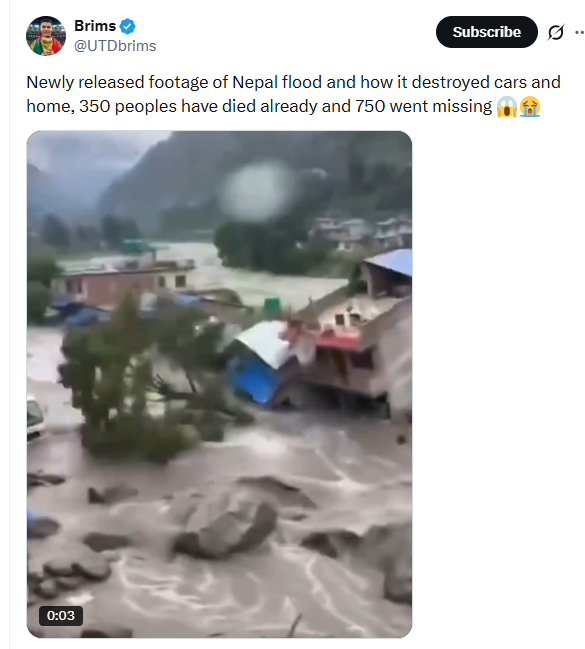
A newly surfaced video purportedly shows the devastation caused by floods in Nepal, with cars and homes being destroyed. It is being claimed that 350 people have died and 750 are missing so far
https://x.com/UTDbrims/status/2092829398462341484?s=48
Fact Check 1
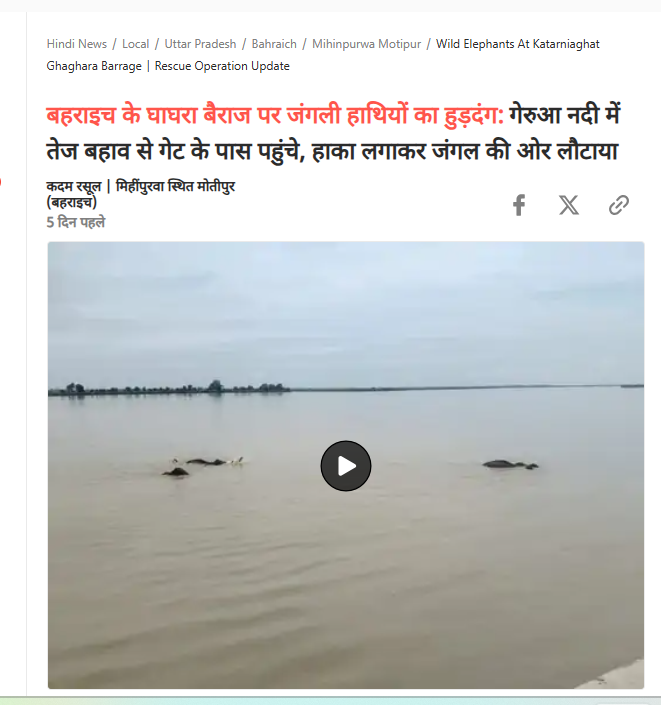
The first video claims to show a herd of wild elephants that was swept away by the floods in Nepal and reached Uttar Pradesh. We conducted a reverse image search of the first video using Google Lens and found a report by Hindi news publication Dainik Bhaskar, which shared a video featuring visuals similar to those in the viral clip. According to the report, a herd of wild elephants coming from the Gerua River reached the gates of the Chaudhary Charan Singh Ghaghra Barrage in Bahraich district, Uttar Pradesh, due to the strong current of the river. The report also quoted the Forest Range Officer as saying that the area is adjacent to an elephant corridor, which is why elephants frequently move through the region.
Fact Check 2
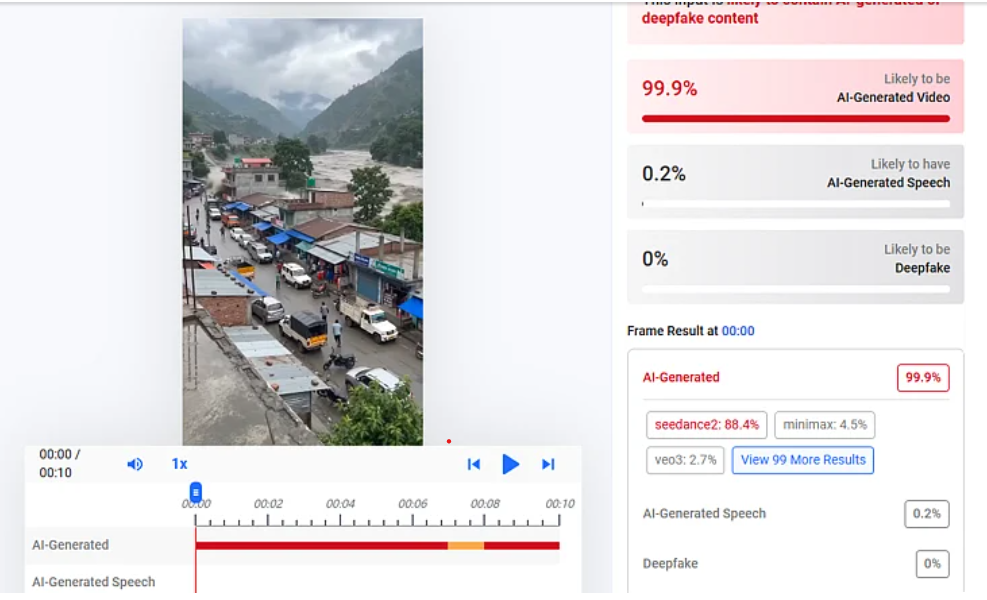
The second video shows a street being completely swept away by floodwaters. We conducted a reverse image search of the video using Google Lens but could not find any credible source that had shared the footage. Following this, we ran the video through the AI detection tool Hive Moderation, which flagged it as 99 percent likely to be AI-generated.
Conclusion
Our research found that the viral videos being shared as scenes of devastation caused by the recent floods in Nepal are misleading. The video showing a herd of elephants is from a separate incident in Bahraich, Uttar Pradesh, and predates the Nepal floods. Meanwhile, the video showing a street being swept away could not be traced to any credible source and was flagged as 99 percent likely to be AI-generated by Hive Moderation.
