
#Fact Check-Misleading Newspaper from Kerala stating ban on paper currency
Executive Summary:
Recently, our team came across a widely circulated post on X (formerly Twitter), claiming that the Indian government would abolish paper currency from February 1 and transition entirely to digital money. The post, designed to resemble an official government notice, cited the absence of advertisements in Kerala newspapers as supposed evidence—an assertion that lacked any substantive basis

Claim:
The Indian government will ban paper currency from February 1, 2025, and adopt digital money as the sole legal tender to fight black money.

Fact Check:
The claim that the Indian government will ban paper currency and transition entirely to digital money from February 1 is completely baseless and lacks any credible foundation. Neither the government nor the Reserve Bank of India (RBI) has made any official announcement supporting this assertion.
Furthermore, the supposed evidence—the absence of specific advertisements in Kerala newspapers—has been misinterpreted and holds no connection to any policy decisions regarding currency
During our research, we found that this was the prediction of what the newspaper from the year 2050 would look like and was not a statement that the notes will be banned and will be shifted to digital currency.
Such a massive change would necessitate clear communication to the public, major infrastructure improvements, and precise policy announcements which have not happened. This false rumor has widely spread on social media without even a shred of evidence from its source, which has been unreliable and is hence completely false.
We also found a clip from a news channel to support our research by asianetnews on Instagram.

We found that the event will be held in Jain Deemed-to-be University, Kochi from 25th January to 1st February. After this advertisement went viral and people began criticizing it, the director of "The Summit of Future 2025" apologized for this confusion. According to him, it was a fictional future news story with a disclaimer, which was misread by some of its readers.
The X handle of Summit of Future 2025 also posted a video of the official statement from Dr Tom.

Conclusion:
The claim that the Indian government will discontinue paper currency by February 1 and resort to full digital money is entirely false. There's no government announcement nor any evidence to support it. We would like to urge everyone to refer to standard sources for accurate information and be aware to avoid misinformation online.
- Claim: India to ban paper currency from February 1, switching to digital money.
- Claimed On: X (Formerly Known As Twitter)
- Fact Check: False and Misleading

Related Blogs
Executive Summary
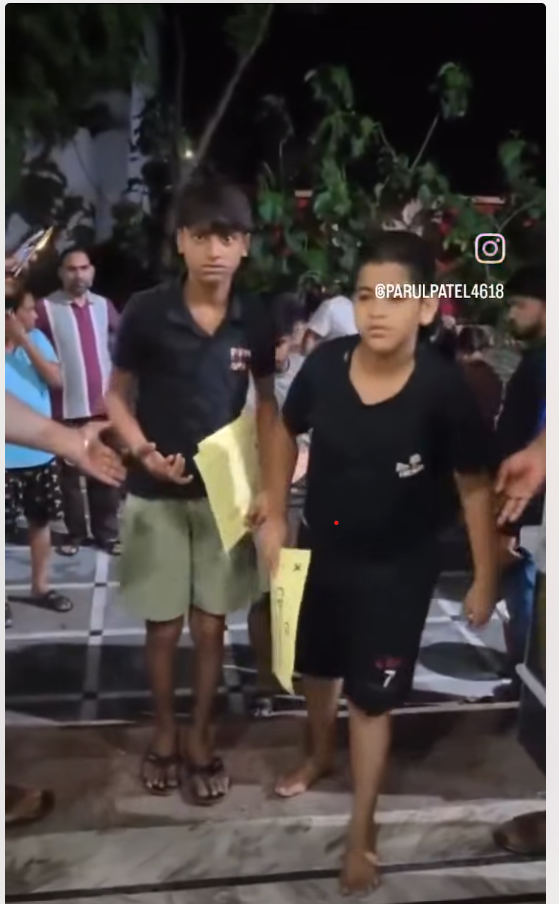
A video showing several children in an injured condition is being widely shared on social media with the claim that the footage is from the ‘Sansad March’ protest organised by the Cockroach Janata Party (CJP) on July 20, 2026. The video is being circulated with the allegation that Delhi Police lathi-charged children during the protest in Delhi. CyberPeace Research Wing’s research found the claim to be false. The viral video is not related to the CJP protest in Delhi. The footage is from an old incident at a private school hostel in Farrukhabad, Uttar Pradesh, where a warden was accused of assaulting students. The old video has been falsely linked to the recent protest with a misleading claim.
Claim:
A Facebook user named ‘The sociopolitics’ shared the video on July 23, 2026, claiming that children were beaten by Delhi Police during the protest.The post stated, “What had the children done wrong? Were they beaten with their eyes covered, or was the anger of their bosses taken out on the public?” The viral post was shared widely on social media by users who believed the claim to be true. The archived version of the post can be accessed here:
https://www.instagram.com/reels/DbKiqy8lOu5/
Fact Check:
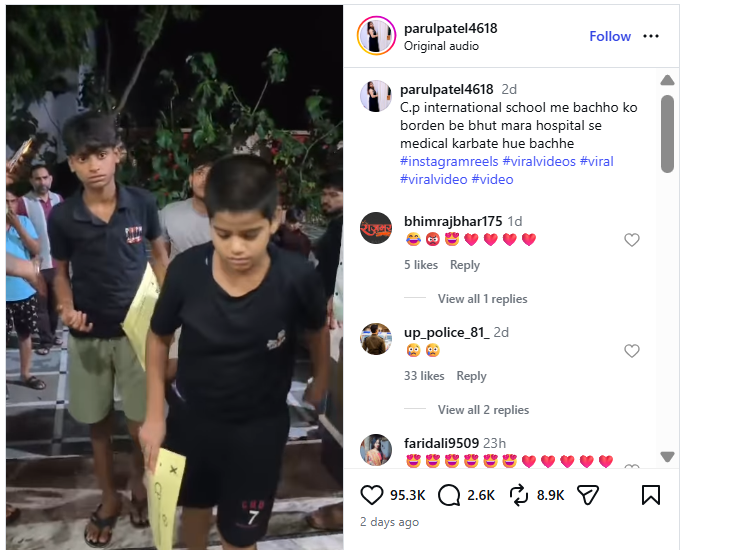
To verify the authenticity of the viral video, the Desk first analysed the footage carefully and examined its audio. The conversation of the children in the video made it clear that the visuals were not connected to the student protest at Delhi’s Jantar Mantar or any police lathi-charge. In the video, the children can be heard mentioning the name of their school and speaking about the warden who allegedly assaulted them. The video also displayed the Instagram username ‘parulpatel4618’, which provided a lead for further research.
https://www.instagram.com/p/DbFcdAjxvG5
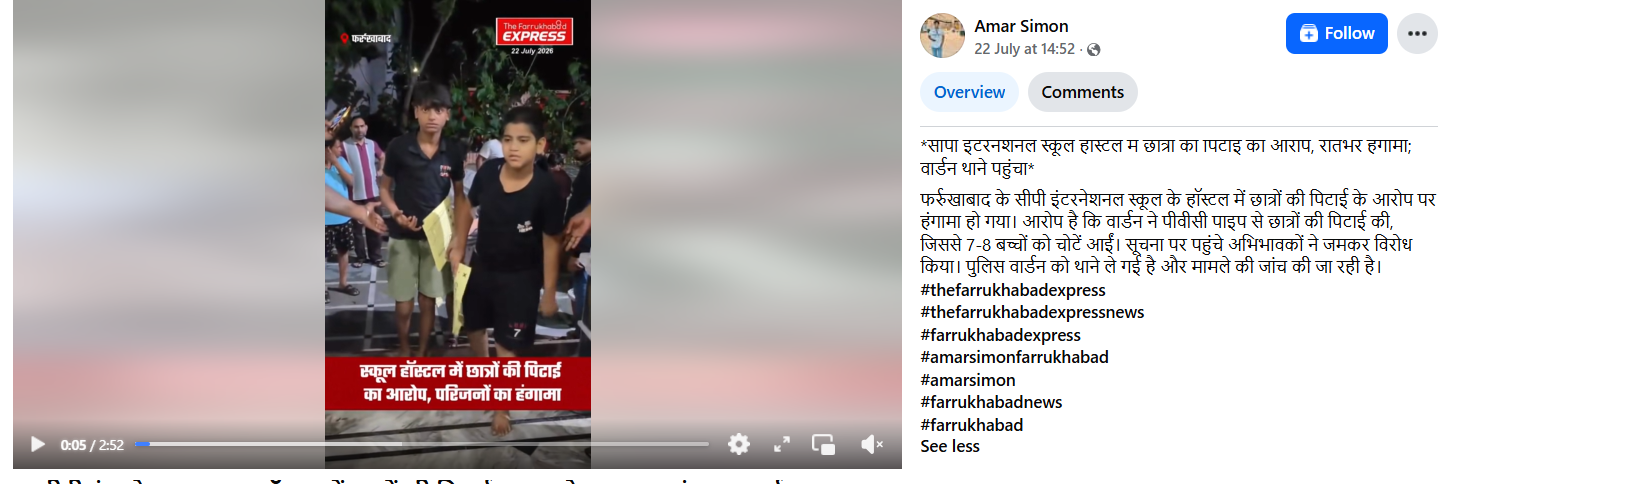
In the next stage of the research, the Desk found a Facebook post dated July 22, 2026, related to the incident. According to the post, students at CP International School hostel in Farrukhabad, Uttar Pradesh, were allegedly beaten, following which a protest was reported. The post stated that the hostel warden was accused of assaulting students with a PVC pipe, leaving several children injured. After receiving information about the incident, parents reached the spot and protested. Police took the warden to the police station and initiated an research.
https://www.facebook.com/watch/?v=992060370500487
Conclusion:
The research established that the viral video is not from the CJP ‘Sansad March’ protest in Delhi. The footage is from an old incident at a private school hostel in Farrukhabad, Uttar Pradesh, where a warden was accused of assaulting students. The video is being circulated with a false claim by linking it to a recent protest.

Introduction
India officially became part of the US-led Pax Silica project on February 20, 2026, at the India AI Impact Summit in New Delhi. This was a significant milestone in India’s involvement in global technology and supply chain cooperation. India joined a coalition of advanced economies by signing the Pax Silica Declaration in a move aimed at strengthening coordination over technology supply chains on which artificial intelligence, semiconductors, critical minerals and advanced manufacturing rely. The entry of India into the global technology landscape is indicative of India’s growing role in the global technology order and reflects broader shifts in how countries are responding to the geopolitics of silicon and AI infrastructure.
What Is Pax Silica and Why It Matters
The United States Department of State introduced Pax Silica as a strategic program launched in December 2025. It seeks to establish safe, resilient and innovation-driven supply chains for emerging technologies that are the foundations of the AI era. This encompasses activities ranging from mining and refining of rare earths, gallium and germanium to semiconductor manufacturing, the creation of advanced computing hardware and energy infrastructure. The project describes cooperation as a method of reducing what are termed as coercive dependencies on any one supplier or economy, thereby supporting sustained access to building blocks of state-of-the-art technology.
Pax Silica derives its name from the Latin terms for 'peace' and the substrate material of 'silicon', meaning that the coalition aims at achieving stability and prosperity by working together in supply chains of technology. Early signatories were the United States, Japan, South Korea, Australia, the United Kingdom, Israel, Singapore, the Netherlands, Greece, Qatar and the United Arab Emirates. India was the twelfth member to sign the declaration.
India’s Strategic Interests in Pax Silica
The move to join Pax Silica is both a diplomatic and economic decision. The incorporation of India into a network led ostensibly by the Western bloc and containing developed economy players in the technological supply chain creates the messaging that it wants to be more deeply integrated into the global high-tech ecosystems.
India currently relies on importing a large proportion of the chips for its electronics production sector, while its domestic manufacturing capacity remains limited. Pax Silica membership could provide Indian firms with advanced manufacturing equipment, process expertise and joint ventures with their partners, who have already developed the fabrication capabilities.
The signing of the declaration was done by the current Union Minister of Electronics and Information Technology (MeitY) , the Union Minister, who noted that India is expanding its technological capabilities and future ambitions. He observed that the Indian engineers already play a role in designing advanced semiconductor chips and that the increase in semiconductor capacity will demand a professional workforce. He also emphasised that the availability of international tools and alliances would help accelerate India’s growth in this sector.
Another strategic area is the critical minerals. India is estimated to have significant rare earth reserves, but the resources remain largely underdeveloped. The diversification strategy of Pax Silica in terms of supply and processing routes provides India with an opportunity to have joint ventures and infrastructure projects that could help unlock domestic mineral potential within the country.
Supply Chains, AI, and Geopolitical Context
Pax Silica has emerged within a broader geopolitical and supply chain context rather than as a purely economic initiative. The last few years have placed a strain on global technology supply chains with disruptions caused by pandemics, trade tensions, export controls, and the concentrated control of some components of the value chain. China currently dominates in the refinement of rare earths as well as in a variety of legacy semiconductor manufacturing. The concentration has raised concerns about resilience and strategic autonomy among the technology-producing democracies.
This initiative is based on the premise that a diversified and trusted supply chain will make the economic security of countries participating in Pax Silica more secure in case of a trade embargo or as a tool of political leverage. The voluntary and non-binding framework by the coalition only provides a guide to cooperation instead of a binding commitment, though it highlights an acknowledgement of risk and opportunity in global technology markets.
Such concerns as strategic autonomy and the extent of India’s involvement in the initiative have been expressed by those who criticise it, particularly because the coalition is perceived to be partially designed to respond to Chinese dominance in the most important technological sectors. Some analysts have also suggested that India will have to balance its participation in Pax Silica by taking special care of its own interests and alliances outside this coalition.
Economic and Industrial Implications for India
Joining Pax Silica offers India potential benefits on multiple fronts.
Strengthening Innovation and Manufacturing Ecosystems
India's membership will allow cooperation in semiconductor production, development of advanced computing infrastructure and implementation of AI. The government and industry players could attract investments through partnerships, technology transfer and joint R&D. India’s emerging design and fabrication projects could use a greater international integration in this venture.
Talent and Skills Development
A recurring theme among Indian policymakers is the issue of a skilled workforce. As the world semiconductor and AI sector is expected to need millions of specialists in the next 10 years, India’s large talent pool presents an opportunity to produce local talent that is capable of catering to local demands as well as international supply needs. Initiatives linked to Pax Silica have the potential to establish training pathways and institutional bridges that facilitate workforce preparedness.
Diversification of Supply Partnerships
In the case of India, the diversification of suppliers and partners goes beyond the availability of materials and technologies. It also implies reducing exposure to supply shocks and enhancing resilience in important industries such as consumer electronics, automotive manufacturing, defence systems and digital infrastructure, all of which rely on semiconductors and advanced computing hardware.
Broader Industrial Readiness and Domestic Challenges
India’s participation in Pax Silica highlights the domestic conditions required to support advanced technology manufacturing. A conducive environment will depend on reliable infrastructure, regulatory stability, specialised industrial clusters and sustained policy coordination across government and industry. Semiconductor and AI hardware production are resource-intensive, requiring significant energy, water and chemical management, making environmental safeguards and sustainable industrial planning essential to prevent long-term ecological strain.
At the same time, India faces gaps in its human resource development ecosystem. While engineering talent is abundant, specialised training in semiconductor fabrication, materials science and advanced manufacturing remains limited. Additionally, the relative lack of applied research and development initiatives aimed at reducing technological and financial risks may constrain large-scale industrial expansion, underscoring the need for stronger industry–academia collaboration and targeted innovation support.
Conclusion: A Strategic Step into the AI Era
India’s formal entry into the Pax Silica initiative at the 2026 India AI Impact Summit reflects a thoughtful recalibration of its global technology engagement. By aligning with a coalition aimed at securing the supply chains that make modern digital economies possible, India has signalled its intent to be more than just a consumer of technology. It seeks to help shape the infrastructure, partnerships and norms that will define the next generation of AI, semiconductors and critical technologies.
While questions around strategic autonomy and long-term dependencies remain important considerations, Pax Silica offers India access to networks, capabilities and collaborative frameworks that can accelerate its semiconductor ambitions and broaden its role in the global tech order. The move underscores how technology cooperation today increasingly interacts with geopolitics, economic strategy and national aspirations for growth and innovation.
Sources
- https://timesofindia.indiatimes.com/technology/tech-news/what-is-pax-silica-and-why-does-india-joining-the-ai-supply-chain-alliance-matter/articleshow/128594775.cms
- https://paxsilica.org/f/pax-silica-securing-the-foundations-of-the-ai-era
- https://www.businesstoday.in/india/story/ai-impact-summit-2026-india-set-to-join-us-led-pax-silica-today-517167-2026-02-20
- https://www.business-standard.com/india-news/pax-silica-india-joins-us-supply-chain-initiative-ai-impact-summit-2026-126022000339_1.html

Introduction
Since users are now constantly retrieving critical data on their mobile devices, fraudsters are now focusing on these devices. App-based, network-based, and device-based vulnerabilities are the three main ways of attacking that Mobile Endpoint Security names as mobile threats. Composed of the following features: program monitoring and risk, connection privacy and safety, psychological anomaly and reconfiguration recognition, and evaluation of vulnerabilities and management, this is how Gartner describes Mobile Threat Defense (MTD).
The widespread adoption and prevalence of cell phones among consumers worldwide have significantly increased in recent years. Users of these operating system-specific devices can install a wide range of software, or "apps," from online marketplaces like Google Play and the Apple App Store. The applications described above are the lifeblood of cell phones; they improve users' daily lives and augment the devices' performance. The app marketplaces let users quickly search for and install new programs, but certain malicious apps/links/websites can also be the origin of malware hidden among legitimate apps. These days, there are many different security issues and malevolent attacks that might affect mobile devices.
Unveiling Malware Landscape
The word "malware" refers to a comprehensive category of spyware intended to infiltrate networks, steal confidential data, cause disruptions, or grant illegal access. Malware can take many forms, such as Trojan horses, worms, ransomware, infections, spyware, and adware. Because each type has distinct goals and features, security specialists face a complex problem. Malware is a serious risk to both people and businesses. Security incidents, monetary losses, harm to one's credibility, and legal repercussions are possible outcomes. Understanding malware's inner workings is essential to defend against it effectively. Malware analysis is helpful in this situation. The practice of deconstructing and analysing dangerous software to comprehend its behaviour, operation, and consequences is known as malware analysis.Major threats targeting mobile phones
Viruses: Viruses are self-renewing programs that can steal data, launch denial of service assaults, or enact ransomware strikes. They spread by altering other software applications, adding malicious code, and running it on the target's device. Computer systems all over the world are still infected with viruses, which attack different operating systems like Mac and Microsoft Windows, even though there is a wealth of antiviral programs obtainable to mitigate their impacts.
Worms: Infections are independent apps that propagate quickly and carry out payloads—such as file deletion or the creation of botnets—to harm computers. Worms, in contrast to viruses, usually harm a computer system, even if it's just through bandwidth use. By taking advantage of holes in security or other vulnerabilities on the target computer, they spread throughout computer networks.
Ransomware: It causes serious commercial and organisational harm to people and businesses by encrypting data and demanding payment to unlock it. The daily operations of the victim organisation are somewhat disrupted, and they need to pay a ransom to get them back. It is not certain, though, that the financial transaction will be successful or that they will receive a working translation key.
Adware: It can be controlled via notification restrictions or ad-blockers, tracks user activities and delivers unsolicited advertisements. Adware poses concerns to users' privacy even though it's not always malevolent since the information it collects is frequently combined with information gathered from other places and used to build user profiles without their permission or knowledge.
Spyware: It can proliferate via malicious software or authentic software downloads, taking advantage of confidential data. This kind of spyware gathers data on users' actions without their authorisation or agreement, including:Internet activityBanking login credentialsPasswordsPersonally Identifiable Information (PII)
Navigating the Mobile Security Landscape
App-Centric Development: Regarding mobile security, app-centric protections are a crucial area of focus. Application authorisations should be regularly reviewed and adjusted to guarantee that applications only access the knowledge that is essential and to lower the probability of data misuse. Users can limit hazards and have greater oversight over their confidentiality by closely monitoring these settings. Installing trustworthy mobile security apps also adds another line of protection. With capabilities like app analysis, real-time protection, and antivirus scanning, these speciality apps strengthen your gadget's protection against malware and other harmful activity.
Network Security: Setting priorities for secure communication procedures is crucial for safeguarding confidential data and thwarting conceivable dangers in mobile security. Avoiding unprotected public Wi-Fi networks is essential since they may be vulnerable to cyberattacks. To lessen the chance of unwelcome entry and data surveillance, promote the usage of reliable, password-protected networks instead. Furthermore, by encrypting data transfer, Virtual Private Networks (VPNs) provide additional protection and make it more difficult for malevolent actors to corrupt information. To further improve security, avoid using public Wi-Fi for essential transactions and hold off until a secure network is available. Users can strengthen their handheld gadgets against possible privacy breaches by implementing these practices, which can dramatically lower the risk of data eavesdropping and illegal access.
Constant development: Maintaining a robust mobile security approach requires a dedication to constant development. Adopt a proactive stance by continuously improving and modifying your security protocols. By following up on recurring outreach and awareness campaigns, you can stay updated about new hazards. Because cybersecurity is a dynamic field, maintaining one step ahead and utilising emerging technologies is essential. Stay updated with security changes, implement the newest safeguards, and incorporate new industry standard procedures into your plan. This dedication to ongoing development creates a flexible barrier, strengthening your resistance to constantly evolving mobile security threats.
Threat emergency preparedness: To start, familiarise yourself with the ever-changing terrain associated with mobile dangers to security. Keep updated on new threats including malware, phishing, and illegal access.
Sturdy Device Management: Put in place a thorough approach to device management. This includes frequent upgrades, safe locking systems, and additional safeguarding capabilities like remote surveillance and erasing.
Customer Alertness: Emphasise proper online conduct and acquaint yourself and your team with potential hazards, such as phishing efforts.
Dynamic Measures for a Robust Wireless Safety Plan
In the dynamic field of mobile assurances, taking a proactive strategy is critical. To strengthen safeguards, thoroughly research common risks like malware, phishing, and illegal access. Establish a strong device management strategy that includes frequent upgrades, safe locking mechanisms, and remote monitoring and deletion capabilities for added security.
Promoting user awareness by educating people so they can identify and block any hazards, especially regarding phishing attempts. Reduce the dangers of data eavesdropping and illegal access by emphasising safe communication practices, using Virtual Private Networks (VPNs), and avoiding public Wi-Fi for essential transactions.
Pay close attention to app-centric integrity by periodically checking and modifying entitlements. Downloading trustworthy mobile security apps skilled at thwarting malware and other unwanted activity will enhance your smartphone's defenses. Lastly, create an atmosphere of continuous development by keeping up with new threats and utilising developing technology to make your handheld security plan more resilient overall.
Conclusion
Mobile privacy threats grow as portable electronics become increasingly integrated into daily activities. Effective defense requires knowledge of the various types of malware, such as worms, ransomware, adware, and spyware. Tools for Mobile Threat Defense, which prioritise vulnerability assessment, management, anomaly detection, connection privacy, and program monitoring, are essential. App-centric development, secure networking procedures, ongoing enhancement, threat readiness, strong device control, and user comprehension are all components of a complete mobile security strategy. People, as well as organisations, can strengthen their defenses against changing mobile security threats by implementing dynamic measures and maintaining vigilance, thereby guaranteeing safe and resilient mobile surrounding.
References
https://www.titanfile.com/blog/types-of-computer-malware/
https://www.simplilearn.com/what-is-a-trojan-malware-article
https://www.linkedin.com/pulse/latest-anti-analysis-tactics-guloader-malware-revealed-ukhxc/?trk=article-ssr-frontend-pulse_more-articles_related-content-card
