
Barbie malware
Introduction
The ‘Barbie’ fever is going high in India, and it’s hype to launch online scams in India. The cybercriminals attacking the ‘Barbie’ fans in India, as the popular malware and antivirus protection MacAfee has recently reported that India is in the top 3rd number among countries facing major malware attacks. After the release of ‘barbie’ in theatres, the Scams started spreading across India through the free download of the ‘Barbie’ movie from the link and other viruses. The scammers trick the victims by selling free ‘Barbie’ tickets and, after the movie’s hit, search for the free download links on websites which leads to the Scams.
What is the ‘Barbie’ malware?
After the release of the ‘Barbie’ movie, trying to keep up with the trend, Barbie fans started to search the links for free movie downloads from anonymous sources. And after downloading the movie, there was malware in the downloaded zip files. The online scam includes not genuine dubbed downloads of the movie that install malware, barbie-related viruses, and fake videos that point to free tickets, and also clicking on unverified links for the movie access resulted in Scam. It is important not to get stuck in these trends just because to keep up with them, as it could land you in trouble.
Case: As per the report of McAfee, several cases of malware trick victims into downloading the ‘ Barbie’ movie in different languages. By clicking the link, it prompts the user to download a Zip file, which is packed with malware
Countries-wise malware distribution
Cyber Scams witnessed a significant surge in just a few weeks, with hundreds of incidents of new malware cases. And The USA is on the top No. Among all the countries, In the USA there was 37 % of ‘Barbie’ malware attacks held per the, while Australia, the UK, and India suffered 6 % of malware attacks. And other countries like Japan, Ireland, and France faced 3% of Malware attacks.
What are the precautions?
Cyber scams are evolving everywhere, users must remain vigilant and take necessary precautions to protect their personal information. The user shall avoid clicking on suspicious links, also those which are related to unauthorised movie downloads or fake ticket offers. The people shall use legitimate and official platforms to access movie-related content. Keeping anti-malware and antivirus will add an extra layer of protection.
Here are some following precautions against Malware:
- Use security software.
- Use strong passwords and authentication.
- Enforce safe browsing and email.
- Data backup.
- Implement Anti-lateral Movement.
Conclusion
Cyberspace is evolving, and with that, Scams are also evolving. With the new trend of ‘Barbie’ Scams going on the rise everywhere, India is on top 3rd No. In India, McAfee reported several malicious attacks that attempted to trick the victims into downloading the free version of ‘Barbie’ movie in dubbed languages. This resulted in a Scam. People usually try to keep up with trends that land them in trouble. The users shall beware of these kinds of cyber-attacks. These scams result in huge losses. Technology should be used with proper precautions as per the incidents happening around.

Related Blogs
Introduction
A digital forensic investigation can start with a question: what really happened? The tricky part is that the answer might be hidden in thousands of files, system logs, browser records, messages, application artefacts and timestamps. Traditional forensic practice gives a method to find, collect, check and report such evidence yet the amount of digital data keeps growing. NIST’s forensic guidance says that evidence must be kept safe its integrity checked and investigative steps written down so that results can be examined and repeated.[4] This is where Large Language Models (LLMs) draw interest. LLMs can. Summarise large amounts of text, spot connections between pieces of information and help an examiner move through evidence faster. However, an important question remains: can an LLM truly become an investigator or should it stay an assistant to one?
Understanding the basic idea: What is an LLM?
A Large Language Model is an AI system trained on collections of text so that it can learn language patterns and produce answers. In terms an LLM does not think like a human investigator. An LLM creates language from patterns it learned during training and from the details it receives. This makes an LLM handy for summarisation, classification, question answering and pulling information from text.
Where LLMs can actually help a forensic examiner
Finding relevant evidence faster
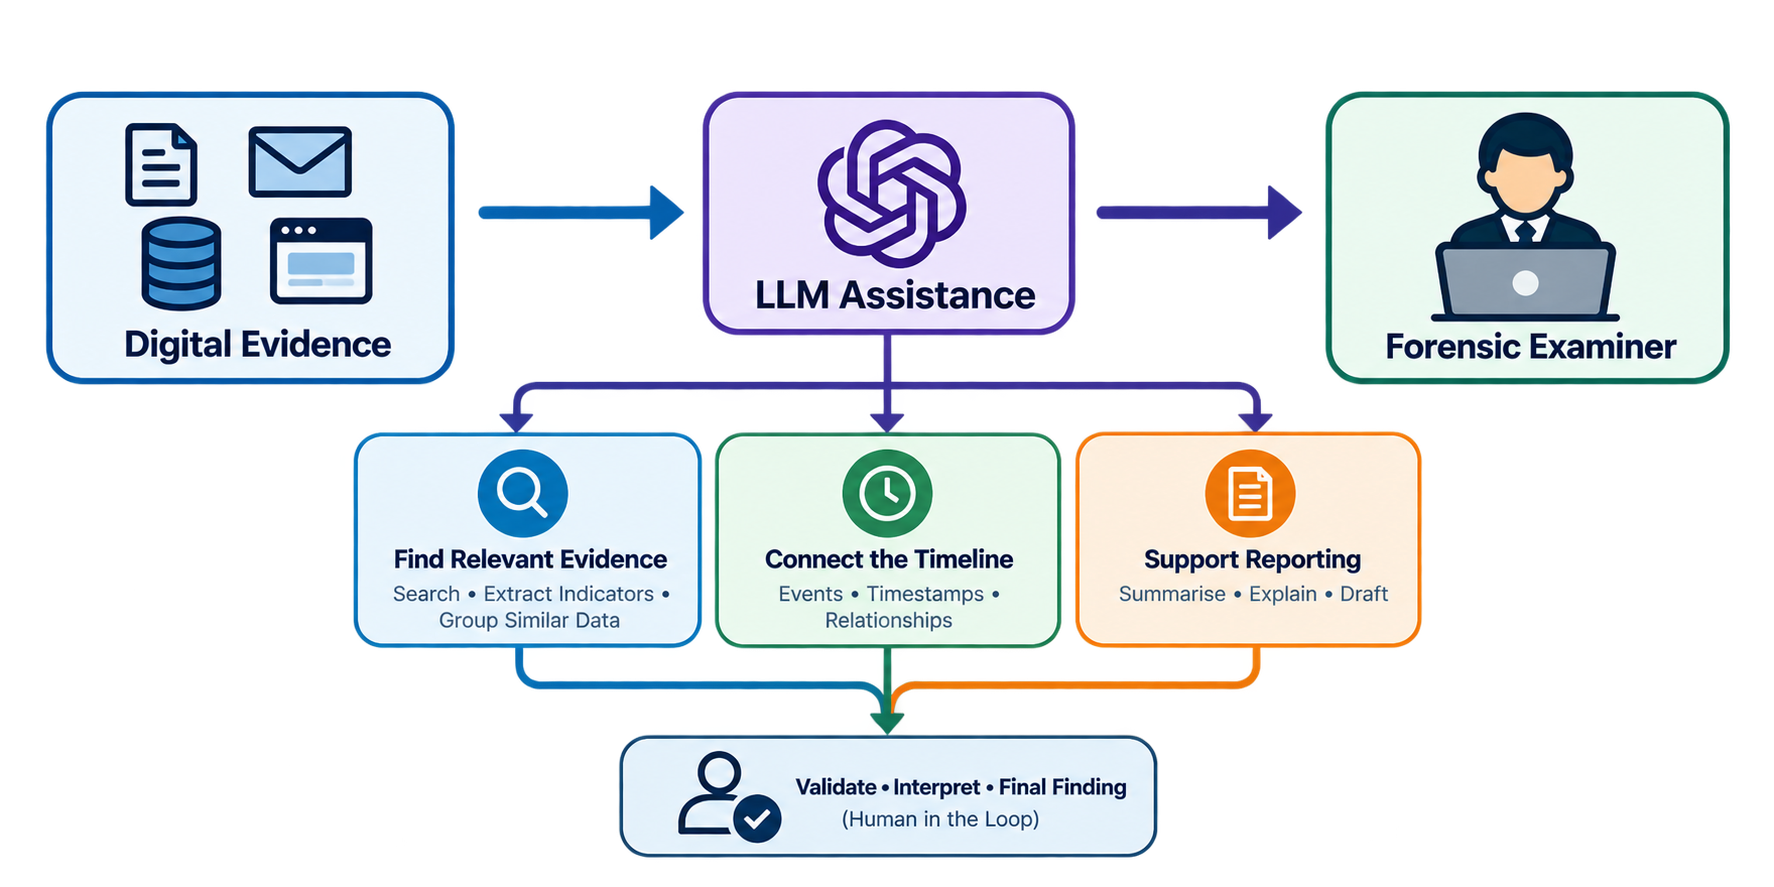
Consider a case involving a suspected phishing incident. A forensic examiner may have email headers, message bodies, attachments, browser history, DNS records and system logs. An LLM can help organize text-based evidence, spot repeated terms pull out indicators such as domains or IP addresses and cluster related events for review. Research on LLM-assisted forensics says that pattern recognition and early evidence analysis are promising use cases.[1][3]
Connecting the timeline
Investigations often rely on order: what happened first what followed and which artefacts back that order. An LLM can turn amounts of timestamped data into a clear timeline or point out records that seem related. The key point is that the LLM helps an examiner see relationships; it does not independently prove that one event caused another.
Making forensic reporting easier to understand
A good forensic report should be understandable to technical and non-technical readers. LLMs can help turn examiner notes or structured findings into clearer draft language, summaries or executive explanations. This is particularly useful when an investigation contains technical terms that need to be explained without losing their meaning. Research also identifies evidence presentation and reporting as a potential area for LLM assistance.[1]
A realistic example
Imagine an organisation reports that an employee account may have been compromised. The examiner collects the relevant disk image, authentication logs, browser history and email data using established procedures. After preservation and examination with validated tools, a controlled set of extracted text or structured artefacts could be given to an LLM. It might identify unusual login patterns, highlight a suspicious domain appearing in multiple sources, and draft questions for further examination.
The examiner then checks those observations against the original evidence and forensic tool outputs. If the model says a login occurred at 10:14, that timestamp must be verified in the source log. If it suggests that two events are linked, the relationship must be supported by evidence. The model can accelerate the search, but the evidence remains the foundation of the conclusion.
Why an LLM cannot simply replace the investigator
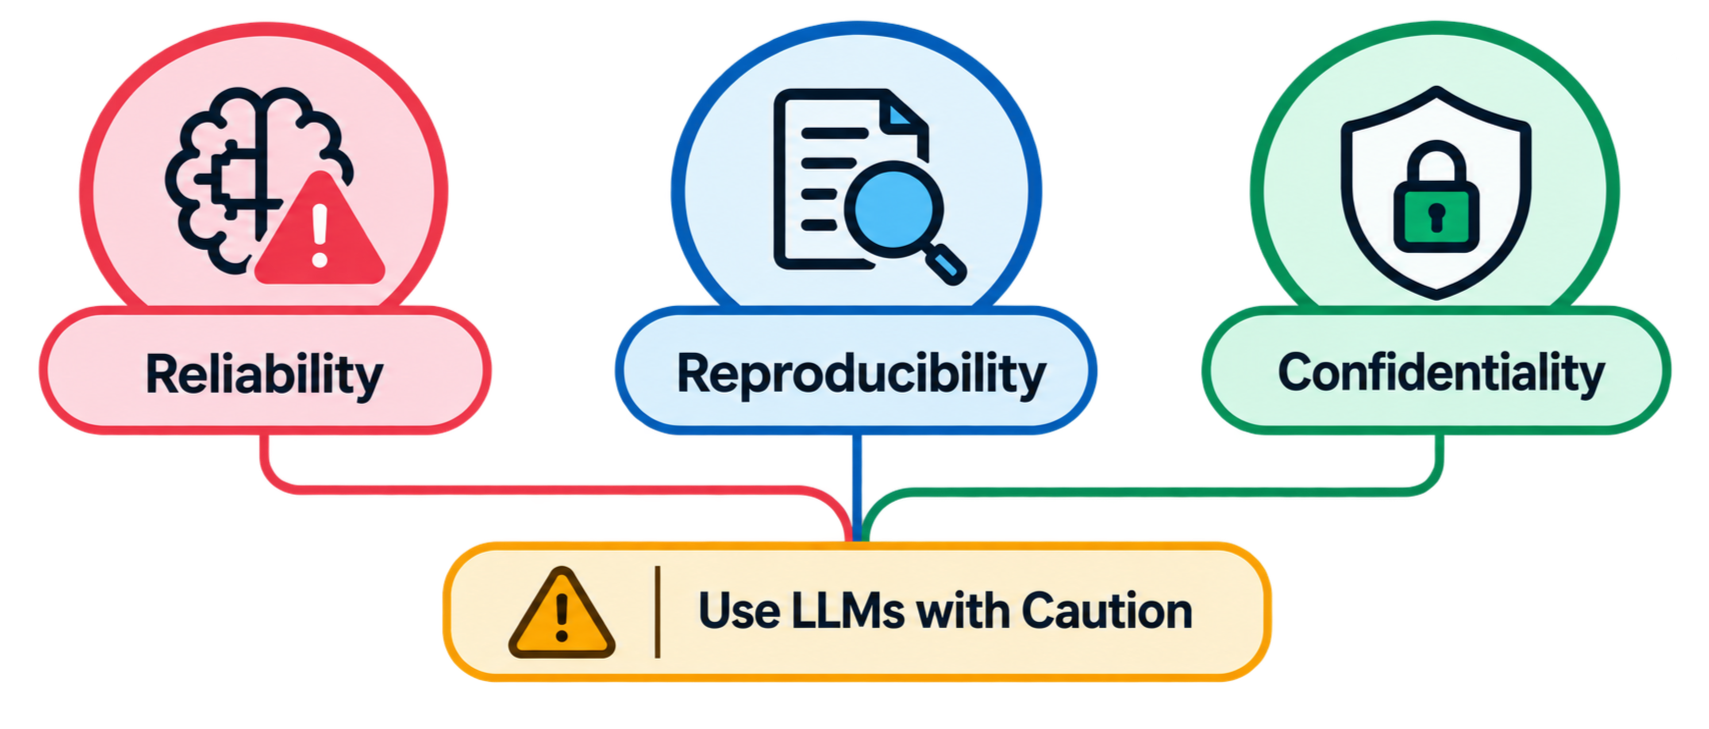
The biggest challenge is reliability. LLMs can produce fluent answers that sound convincing even when the answer is wrong. The 2026 systematic review of 33 peer-reviewed works on LLMs in digital forensics highlights hallucination, explainability, reproducibility and legal admissibility as major concerns.[1] In forensic work, an incorrect sentence is not just a minor inconvenience; it can change how a case is understood.
There is also a reproducibility problem. Traditional forensic practice depends on validated processes, integrity checks and documentation. NIST recommends verifying acquired data and recording actions and tools so work can be repeated.[4] LLM output can vary with the model, settings, context and system version. That makes raw model output unsuitable as forensic proof on its own.
Another concern is confidentiality. Evidence may contain personal information, credentials, private communications or sensitive organisational data. Sending it to an external AI service without proper controls can create a privacy and governance risk. NIST’s Generative AI Profile stresses managing risks across the AI lifecycle.[5]
What responsible LLM-assisted forensics could look like
A practical approach is to keep the examiner in control. The LLM should receive only the information needed for the task, preferably through a controlled environment with access restrictions and logging. Critical findings should always link back to the source artefact rather than being accepted because the model sounds confident.
A simple operational principle is: -
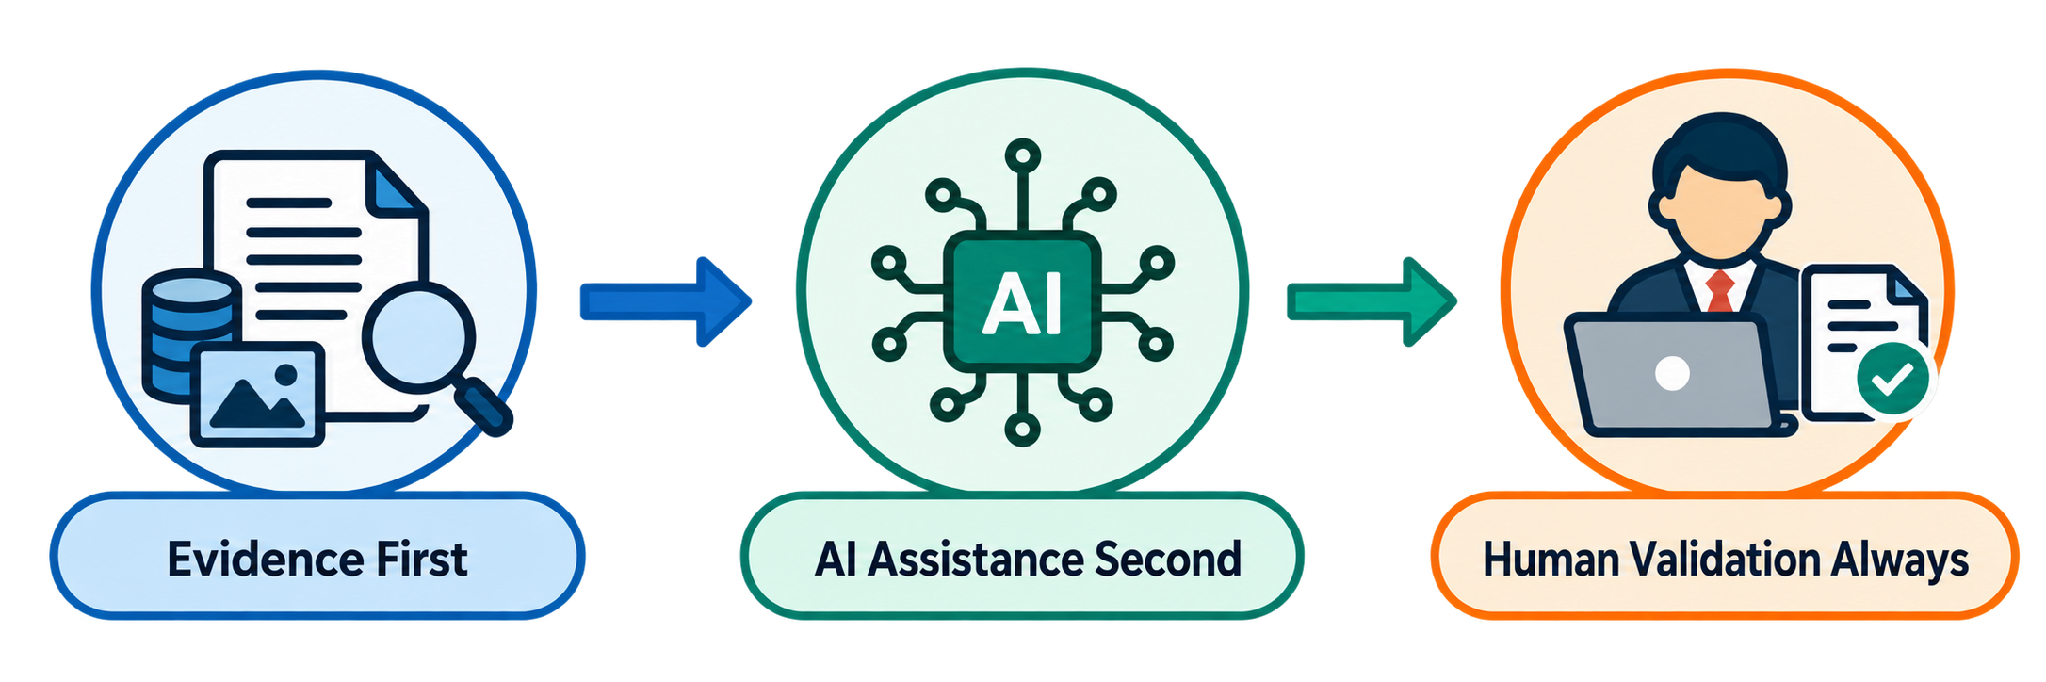
In practice, this means preserving and hashing evidence, using validated forensic tools for acquisition and examination, recording what data was supplied to the AI system, retaining relevant prompts and outputs in working notes, and independently verifying material claims. SWGDE guidance likewise emphasises protecting the integrity of evidence and documenting handling throughout the evidence lifecycle.[6]
A further possibility is a local or specialised forensic model. Research on “ForensicLLM” demonstrates this direction, including source attribution and retrieval-augmented approaches.[2] Such designs may provide a more controlled environment, but they still require testing and validation before operational use.
Conclusion
LLMs are unlikely to make the forensic examiner irrelevant. Their more realistic value is in helping the examiner deal with the scale and complexity of modern evidence. They can search, summarise, classify, correlate and help communicate findings, but these capabilities come with limitations that matter deeply in forensic work. A forensic conclusion must remain traceable to evidence, repeatable through a documented process and open to independent verification.[1][4]
The future of AI-assisted digital forensics is therefore less about replacing investigators and more about designing a disciplined partnership between human expertise and machine assistance. The strongest model is one in which AI speeds up the routine parts of an investigation while the examiner remains responsible for validation, interpretation and final conclusions. As research develops, the real question will not simply be whether an LLM is intelligent enough to analyse evidence, but whether the complete system around it is controlled, explainable and trustworthy enough for forensic use.
References / Endnotes
[1] Chernyshev, M., Baig, Z., Syed, N., Doss, R., & Shore, M. (2026). “Large language models in digital forensics: capabilities, challenges and future directions.” Forensic Science International: Digital Investigation, 56, 302043. https://doi.org/10.1016/j.fsidi.2025.302043
[2] “ForensicLLM: A local large language model for digital forensics.” Forensic Science International: Digital Investigation, 52, Supplement, 301872 (2025). https://doi.org/10.1016/j.fsidi.2025.301872
[3] Wickramasekara, A., Breitinger, F., & Scanlon, M. (2025). “Exploring the Potential of Large Language Models for Improving Digital Forensic Investigation Efficiency.” Forensic Science International: Digital Investigation, 52, 301859. https://doi.org/10.1016/j.fsidi.2024.301859
[4] Kent, K., Chevalier, S., Grance, T., & Dang, H. (2006). Guide to Integrating Forensic Techniques into Incident Response, NIST Special Publication 800-86. National Institute of Standards and Technology. https://doi.org/10.6028/NIST.SP.800-86
[5] Autio, C., Schwartz, R., Dunietz, J., Jain, S., Stanley, M., Tabassi, E., Hall, P., & Roberts, K. (2024). Artificial Intelligence Risk Management Framework: Generative Artificial Intelligence Profile, NIST AI 600-1. National Institute of Standards and Technology. https://doi.org/10.6028/NIST.AI.600-1
[6] Scientific Working Group on Digital Evidence (SWGDE). Best Practices for Digital Evidence Collection, 18-F-002-2.0. https://www.swgde.org/documents/published-complete-listing/18-f-002-2-0/
Executive Summary
A video of Foreign Secretary Vikram Misri speaking to a reporter is being circulated on social media with the claim that he said the Indian government was forced to publicly acknowledge the soldiers killed during Operation Sindoor due to political pressure from the families of the deceased. Research conducted by the CyberPeace Research Wing found that the viral video had been manipulated using artificial intelligence (AI). Vikram Misri's voice was artificially cloned, meaning the audio heard in the clip is not genuine but has been generated and altered using AI technology.
Claim
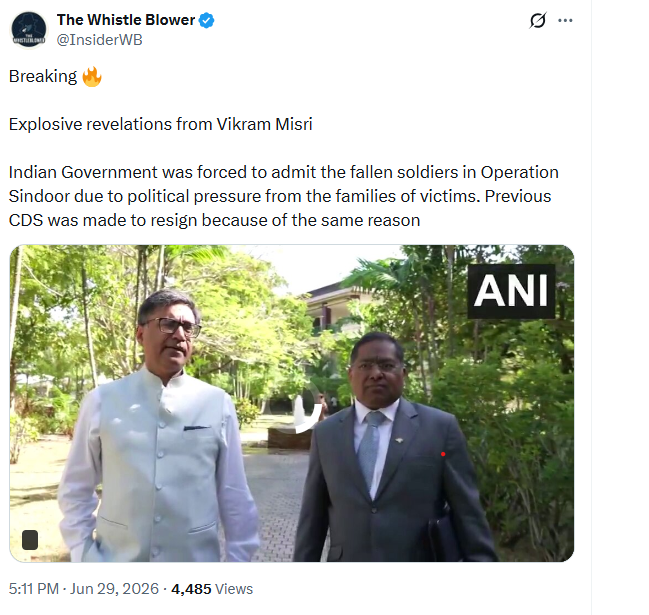
The video was shared on X (formerly Twitter) with the following caption: "Breaking. Explosive revelations from Vikram Misri. Indian Government was forced to admit the fallen soldiers in Operation Sindoor due to political pressure from the families of victims. Previous CDS was made to resign because of the same reason."
https://x.com/InsiderWB/status/2071642756125008031
Fact Check
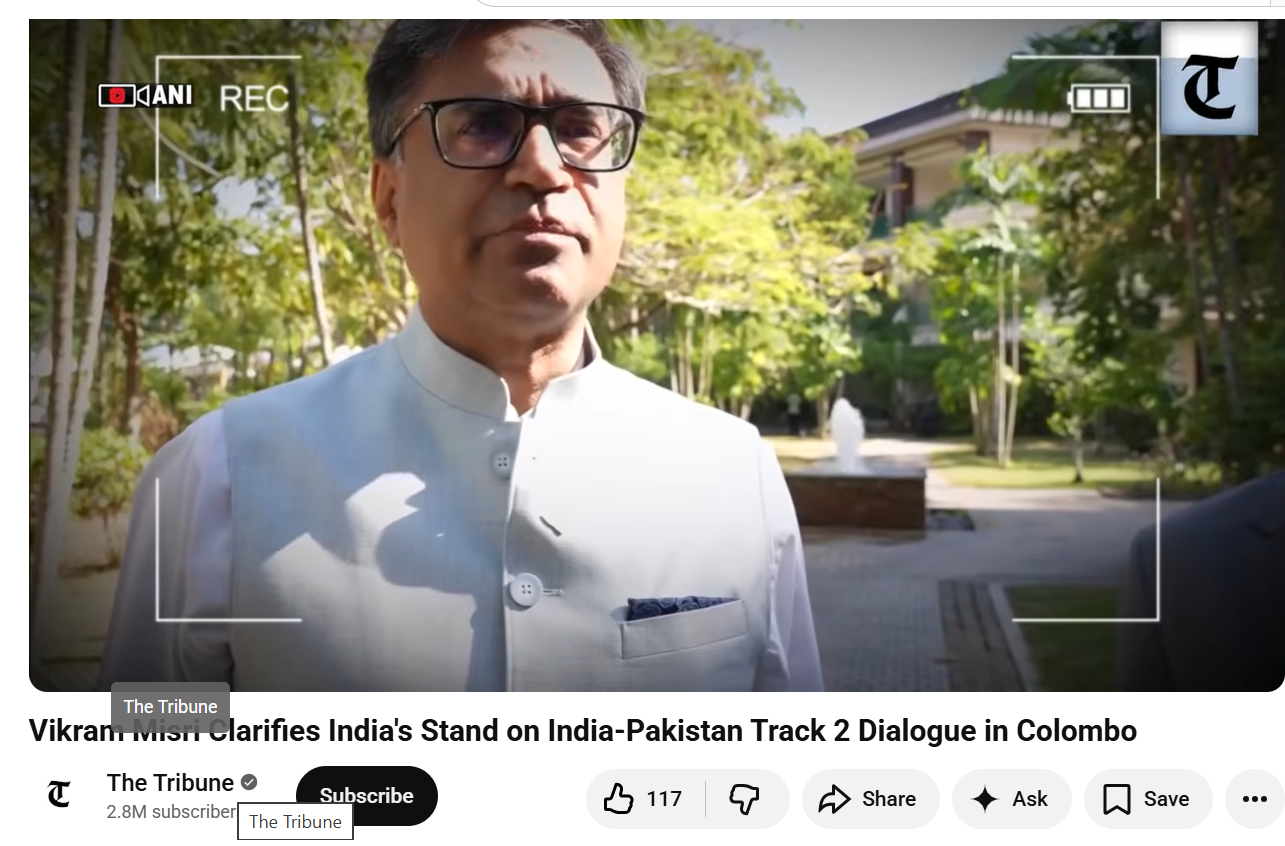
We conducted a reverse image search using Google Lens, which led us to a video uploaded on The Tribune's verified YouTube channel that matched the viral clip. In the original video, Vikram Misri clarified that the Government of India neither officially participated in, supported, nor was involved in any event related to India-Pakistan dialogue. He further stated that the government had taken no cognisance of such private events and that the retired dignitaries and diplomats present were expressing their personal views, not speaking on behalf of the Government of India.
https://www.youtube.com/watch?v=wCrv0Vcgp28
Since we found no evidence that Vikram Misri had ever made the statements attributed to him in the viral clip, we analysed the video using Hive Moderation's AI-generated content detection tool. The analysis indicated that the viral video is 96 per cent AI-generated.
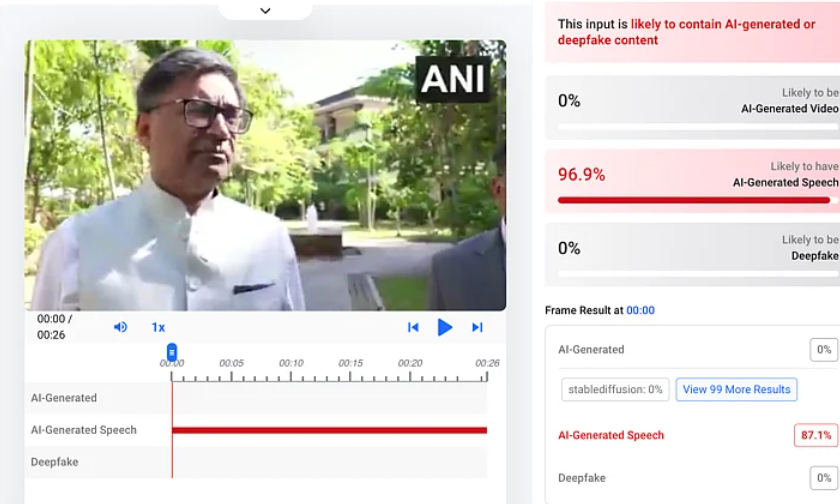
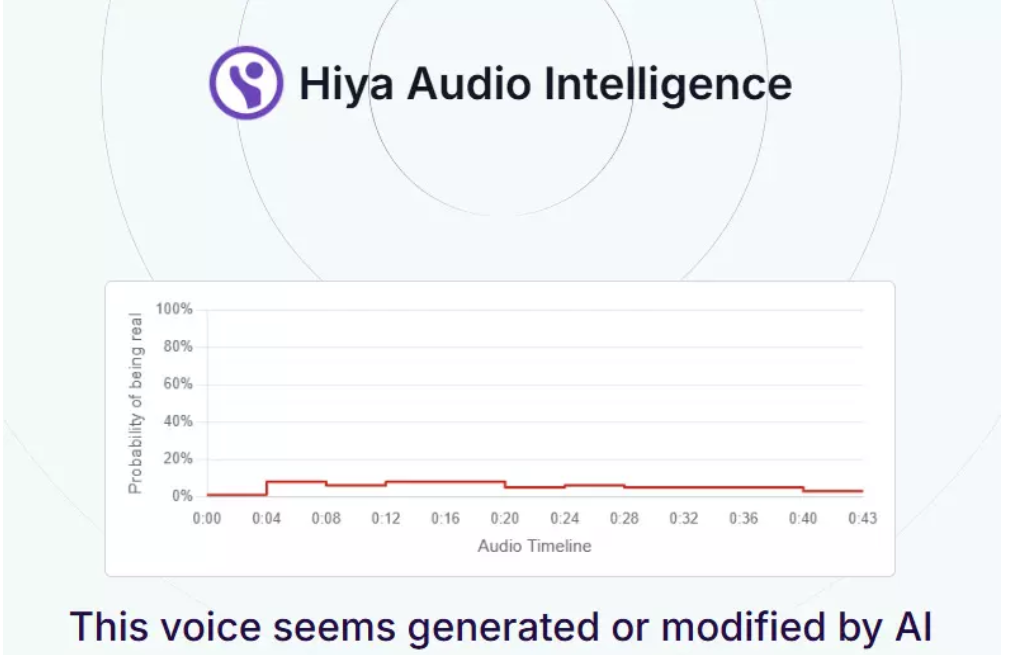
To further verify the claim, we analysed the audio using Hiya Audio Intelligence. The tool concluded that the voice in the viral video appears to have been generated or modified using artificial intelligence.
Conclusion
The viral video is misleading. Our research found that the video of Foreign Secretary Vikram Misri had been manipulated using artificial intelligence. He never made any statement claiming that the Indian government disclosed the names of soldiers killed during Operation Sindoor due to pressure from their families. Therefore, the viral claim is false.

Recent Incidents:
Recent reports are revealing a significant security threat linked to a new infostealer based malware campaign known to solely target gaming accounts. This attack has affected users of Activision and other gaming websites. The sophisticated software has captured millions of login credentials, notably from the cheats and players. The officials at Activision Blizzard, an American video game holding company, are still investigating the matter and collaborating with cheated developers to minimize the impact and inform the accounts’ residents of appropriate safety measures.
Overview:
Infostealer, also known as information stealer, is a type of malware designed in the form of a Trojan virus for stealing private data from the infected system. It can have a variety of incarnations and collect user data of various types such as browser history, passwords, credit card numbers, and login details and credentials to social media, gaming platforms, bank accounts, and other websites. Bad actors use the log obtained as a result of the collection of personal records to access the victim’s financial accounts, appropriate the victim’s online identity, and perform fraudulent actions on behalf of the victim.
Modus Operandi:
- Infostealer is a malicious program created to illegally obtain people's login details, like usernames and passwords. Its goal is to enable cyberattacks, sell on dark web markets, or pursue malicious aims.
- This malware targets both personal devices and corporate systems. It spreads through methods like phishing emails, harmful websites, and infected public sites.
- Once inside a device, Infostealer secretly gathers sensitive data like passwords, account details, and personal information. It's designed to infiltrate systems being undetected. The stolen credentials are compiled into datalogs. These logs are then sold illegally on dark web marketplaces for profit.
Analysis:


Basic properties:
- MD5: 06f53d457c530635b34aef0f04c59c7d
- SHA-1: 7e30c3aee2e4398ddd860d962e787e1261be38fb
- SHA-256: aeecc65ac8f0f6e10e95a898b60b43bf6ba9e2c0f92161956b1725d68482721d
- Vhash: 145076655d155515755az4e?z4
- Authentihash: 65b5ecd5bca01a9a4bf60ea4b88727e9e0c16b502221d5565ae8113f9ad2f878
- Imphash: f4a69846ab44cc1bedeea23e3b680256
- Rich PE header hash: ba3da6e3c461234831bf6d4a6d8c8bff
- SSDEEP: 6144:YcdXHqXTdlR/YXA6eV3E9MsnhMuO7ZStApGJiZcX8aVEKn3js7/FQAMyzSzdyBk8:YIKXd/UgGXS5U+SzdjTnE3V
- TLSH:T1E1B4CF8E679653EAC472823DCC232595E364FB009267875AC25702D3EFBB3D56C29F90
- File type: Win32 DLL executable windows win32 pepe dll
- Magic: PE32+ executable (DLL) (GUI) x86-64, for MS Windows
- File size: 483.50 KB (495104 bytes)
Additional Hash Files:
- 160389696ed7f37f164f1947eda00830
- 229a758e232aeb49196c862655797e12
- 23e4ac5e7db3d5a898ea32d27e8b7661
- 3440cced6ec7ab38c6892a17fd368cf8
- 36d7da7306241979b17ca14a6c060b92
- 38d2264ff74123f3113f8617fabc49f6
- 3c5c693ba9b161fa1c1c67390ff22c96
- 3e0fe537124e6154233aec156652a675
- 4571090142554923f9a248cb9716a1ae
- 4e63f63074eb85e722b7795ec78aeaa3
- 63dd2d927adce034879b114d209b23de
- 642aa70b188eb7e76273130246419f1d
- 6ab9c636fb721e00b00098b476c49d19
- 71b4de8b5a1c5a973d8c23a20469d4ec
- 736ce04f4c8f92bda327c69bb55ed2fc
- 7acfddc5dfd745cc310e6919513a4158
- 7d96d4b8548693077f79bc18b0f9ef21
- 8737c4dc92bd72805b8eaf9f0ddcc696
- 9b9ff0d65523923a70acc5b24de1921f
- 9f7c1fffd565cb475bbe963aafab77ff
Indicators of Compromise:
- Unusual Outbound Network Traffic: An increase in odd or questionable outbound network traffic may be a sign that infostealer malware has accessed more data.
- Anomalies in Privileged User Account Activity: Unusual behavior or illegal access are two examples of irregular actions that might indicate a breach in privileged user accounts.
- Suspicious Registry or System File Changes: Infostealer malware may be trying to alter system settings if there are any unexpected changes to system files, registry settings, or configurations.
- Unusual DNS queries: When communicating with command and control servers or rerouting traffic, infostealer malware may produce strange DNS queries.
- Unexpected System Patching: Unexpected or unauthorized system patching by unidentified parties may indicate that infostealer malware has compromised the system and is trying to hide its footprint or become persistent.
- Phishing emails and social engineering attempts: It is a popular strategy employed by cybercriminals to get confidential data or implant malicious software. To avoid compromise, it is crucial to be wary of dubious communications and attempts of social engineering.
Recommendations:
- Be Vigilant: In today's digital world, many cybercrimes threaten online safety, Phishing tricks, fake web pages, and bad links pose real dangers. Carefully check email sources. Examine websites closely. Use top security programs. Follow safe browsing rules. Update software often. Share safety tips. These steps reduce risks. They help keep your online presence secure.
- Regular use of Anti-Virus Software to detect the threats: Antivirus tools are vital for finding and stopping cyber threats. These programs use signature detection and behavior analysis to identify known malicious code and suspicious activities. Updating virus definitions and software-patches regularly, improves their ability to detect new threats. This helps maintain system security and data integrity.
- Provide security related training to the employees and common employees: One should learn Cybersecurity and the best practices in order to keep the office safe. Common workers will get lessons on spotting risks and responding well, creating an environment of caution.
- Keep changing passwords: Passwords should be changed frequently for better security. Rotating passwords often makes it harder for cyber criminals to compromise and make it happen or confidential data to be stolen. This practice keeps intruders out and shields sensitive intel.
Conclusion:
To conclude, to reduce the impact and including the safety measures, further investigations and collaboration are already in the pipeline regarding the recent malicious software that takes advantage of gamers and has stated that about millions of credentials users have been compromised. To protect sensitive data, continued usage of antivirus software, use of trusted materials and password changes are the key elements. The ways to decrease risks and safely protect sensitive information are to develop improved Cybersecurity methods such as multi-factor authentication and the conduct of security audits frequently. Be safe and be vigilant.
Reference:
- https://techcrunch.com/2024/03/28/activision-says-its-investigating-password-stealing-malware-targeting-game-players/
- https://www.bleepingcomputer.com/news/security/activision-enable-2fa-to-secure-accounts-recently-stolen-by-malware/
- https://cyber.vumetric.com/security-news/2024/03/29/activision-enable-2fa-to-secure-accounts-recently-stolen-by-malware/
- https://www.virustotal.com/
- https://otx.alienvault.com/
