
Using incognito mode and VPN may still not ensure total privacy, according to expert
SVIMS Director and Vice-Chancellor B. Vengamma lighting a lamp to formally launch the cybercrime awareness programme conducted by the police department for the medical students in Tirupati on Wednesday.
An awareness meet on safe Internet practices was held for the students of Sri Venkateswara University University (SVU) and Sri Venkateswara Institute of Medical Sciences (SVIMS) here on Wednesday.
“Cyber criminals on the prowl can easily track our digital footprint, steal our identity and resort to impersonation,” cyber expert I.L. Narasimha Rao cautioned the college students.
Addressing the students in two sessions, Mr. Narasimha Rao, who is a Senior Manager with CyberPeace Foundation, said seemingly common acts like browsing a website, and liking and commenting on posts on social media platforms could be used by impersonators to recreate an account in our name.
Turning to the youth, Mr. Narasimha Rao said the incognito mode and Virtual Private Network (VPN) used as a protected network connection do not ensure total privacy as third parties could still snoop over the websites being visited by the users. He also cautioned them tactics like ‘phishing’, ‘vishing’ and ‘smishing’ being used by cybercriminals to steal our passwords and gain access to our accounts.
“After cracking the whip on websites and apps that could potentially compromise our security, the Government of India has recently banned 232 more apps,” he noted.
Additional Superintendent of Police (Crime) B.H. Vimala Kumari appealed to cyber victims to call 1930 or the Cyber Mitra’s helpline 9121211100. SVIMS Director B. Vengamma stressed the need for caution with smartphones becoming an indispensable tool for students, be it for online education, seeking information, entertainment or for conducting digital transactions.

Related Blogs
Introduction
The Delhi Police on October 23, 2026, stated that six persons, five of them bankers, have been arrested as part of the international cyber fraud syndicate. As per ANI, the accused were said to have laundered the proceeds of crime via cryptocurrency and kept in touch with one Chinese national who was paid in cash. Police claimed that the network has been operational since 2013 with two regional banks in Kerala, but these banks have not been named publicly, and an investigation is on.
One interesting piece of information has come up – the police reportedly said that the group kept the mobile phones that they used in the offence at least five kilometres away from their physical location in order to dodge location tracking. Interestingly, the same report also mentioned the arrest of seven persons by the Ghaziabad Crime Branch in a separate case of a fake motor insurance call centre that accumulated more than Rs 60 lakh by using fake Google Ads, but there appears to be no link to the two cases. All accused persons are presumed innocent until proven guilty in a court of law.
Why Bankers Matter
"Fraud only benefits when the gains out of the operation can be withdrawn without the fraudster catching the eye of the bank. Evidence indicates that victims are often asked to transfer money into accounts operated by the fraudster, requiring bank accounts to receive a large amount of inflows to be withdrawn without raising suspicion. These accounts are known as mule accounts," reports the I4C.
Delhi Police has met the insider problem before. In October 2025 it arrested five people, including a bank relationship manager who allegedly helped open fake current accounts and leaked internal alerts about complaints and account freezes on the National Cybercrime Reporting Portal. The seized material was tied to 52 complaints across at least 12 states. In September 2026, the Special Cell's IFSO unit arrested five people over Rs 12.84 crore taken from the corporate account of Hero FinCorp, among them a relationship manager of a private bank, with part of the money converted into the USDT stablecoin and sent abroad.
Five bankers in a single case, if the allegations hold, would suggest that the compromise was not one rogue employee but a group, and a thirteen year timeline makes a standing arrangement more plausible than an opportunistic one. That is a harder problem for banks than an individual lapse, because the people who design and enforce controls are the ones accused of bypassing them.
From Rupees to Crypto
However, the easy part is that once money is transferred to the mule account, its recovery depends largely on time taken to process the transaction. As per the Delhi Police, which has recently cracked down on a serious syndicate involved in money laundering through bank accounts and hawala channels that converted money into crypto, investigators said an account in the case had reportedly processed over 10,000 transactions worth Rs 5.24 crore over the course of five days.
Another favoured asset could be Tether (USDT), a US dollar-pegged coin used in a similar case and considered popular for its purchase in cash from local agents at a premium and being able to leave the country outside the banking system. In the June 2025 case, police have indicated that the accused maintained a direct Telegram line with a Chinese individual, which would have sent money into China through USDT. The scheme explained that USDT outflows plus cash inflows might be the basis for the Chinese contact to be under investigation.
The Scale of the Problem
Government figures to Parliament show how quickly cyber crime has spiralled. The amount of money lost to cybercrime, which is reported on the National Cyber Crime Reporting Portal and the Citizen Financial Cyber Crime Reporting and Management System, rose to Rs 22,845.73 crore in 2024 from Rs 7,465.18 crore in 2023, up 206%. The number of instances went up to 363,728 from 2,442,978.
While the steps taken have resulted in the saved money, the exact amount saved is not enough to offset the losses. As per the Ministry of Home Affairs, by June 30, 2026, a total of Rs 11,158 crore was saved through more than 32.80 lakh complaints. Since the amount saved is less than half of the losses, which is Rs 6,596,418,870, the actual amount saved from the amount lost in 2024 is different; thus, these figures are not the statistics of how much money was recovered.
Mule accounts seem to be the key. The Indian Cyber Crime Coordination Centre (I4C) has informed the government that 4.5 lakh such accounts had been frozen in one year alone. State Bank of India, Punjab National Bank, Canara Bank, Kotak Mahindra Bank and Airtel Payments Bank were named as the most common banks in which such accounts were opened. Bank managers and officials who helped set up these accounts are also under investigation, something the recent arrests would also seem to suggest.
How Authorities Are Responding
The Reserve Bank Innovation Hub has designed a machine learning-based model called Mule Hunter.AI that looks for transactional patterns. to detect suspicious accounts more accurately and with far fewer false alarms than many static rules. The government has told the Lok Sabha that the model was currently active in 26 banks and its implementation is under way. This design also aims to offer lower-tier banks some detection ability they would not otherwise have been able to design for themselves, a critical factor as regional lenders face probes in this case.
The pact between I4C and the Innovation Hub was signed in May 2026 to include data from the I4C Suspect Registry in such models. As many as 10,599 arrests had been made till July 2025 in the registry, which was launched on September 10, 2024. Union Home Minister Amit Shah has said mule accounts are one of the biggest hurdles in addressing cybercrime. Shah added that the Centre was also planning to bring all banks, even cooperative banks, on to the I4C portal by December 2026.
What Remains Unanswered
The public record is thin. Police have not revealed how much money the syndicate might have deposited, how many victims could be involved, what banks might be caught up in this, or whether the accounts were opened with real customers' documents. The nature of the link to the Chinese national is also unclear.
Furthermore, there is a more fundamental problem. Detection models learn from patterns, but an insider can open accounts that look legitimate and pass along warnings, as alleged in the October 2025 case. Technology therefore has to be paired with ordinary governance: tighter audit of account openings, access logs that show who viewed complaint alerts, separation of duties, and prompt action when an account draws repeated complaints. Experts quoted in reporting on mule networks have urged stricter KYC checks and real-time monitoring for the same reason.
Conclusion
For ordinary account holders, the message is simple. Never let an unknown person use your bank account, whatever the payment offered, because the account may become a link in a laundering chain. Anyone who loses money should report it at once through the helpline 1930 or the National Cyber Crime Reporting Portal, since quick reporting improves the chance of freezing the funds before they are moved on.
Executive Summary:
The ongoing conflict between Iran and the US-Israel has entered its 19th day. Meanwhile, a video is being widely shared on social media claiming that Iran is carrying out continuous drone attacks at Dubai International Airport. The clip shows visuals of massive fire and explosion However, research by the CyberPeace has found the claim to be misleading. Our research revealed that the video has been available on the internet since 2020. In reality, the footage shows a fire at a market in Ajman, UAE, and not explosions at Dubai Airport in 2026. Although there were recent reports of a fire near DXB (Dubai Airport) following a drone attack, this video is not related to that incident.
Claim:
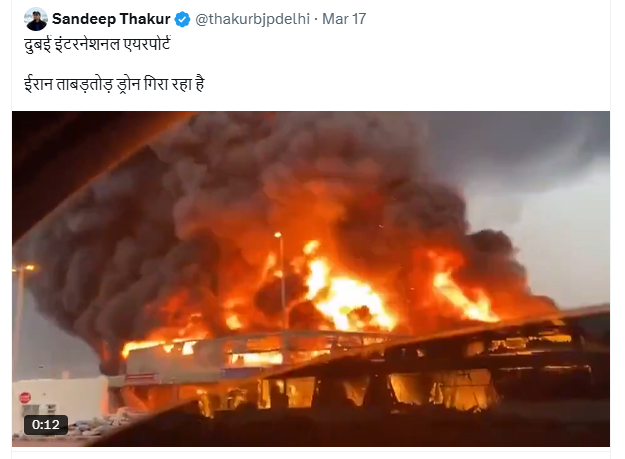
On social media platform X (formerly Twitter), a user shared the viral video on March 17, 2026, writing:
“Dubai International Airport – Iran is dropping drones continuously.”
Post link, archive link, and screenshot are given below:
Fact Check:
To verify the viral claim, we extracted keyframes from the video and conducted a reverse image search using Google Lens. During the research, we found the same video on a YouTube channel, where it was uploaded on August 6, 2020. The caption read: “Ajman fruits and vegetables market caught in fire.”
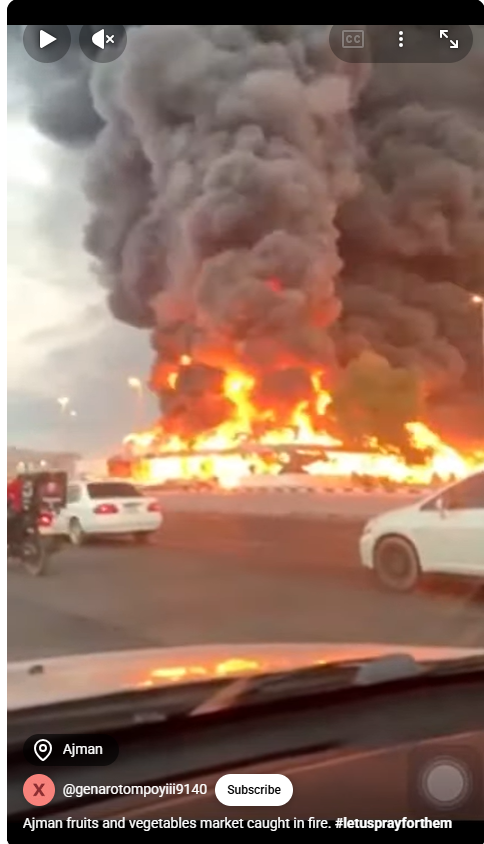
Based on this clue, it became clear that the viral video has no connection with the ongoing Iran-US-Israel conflict. In the next step, we searched using relevant keywords and found a report published on August 5, 2020, on the website of Gulf News, which contained visuals similar to the viral video.
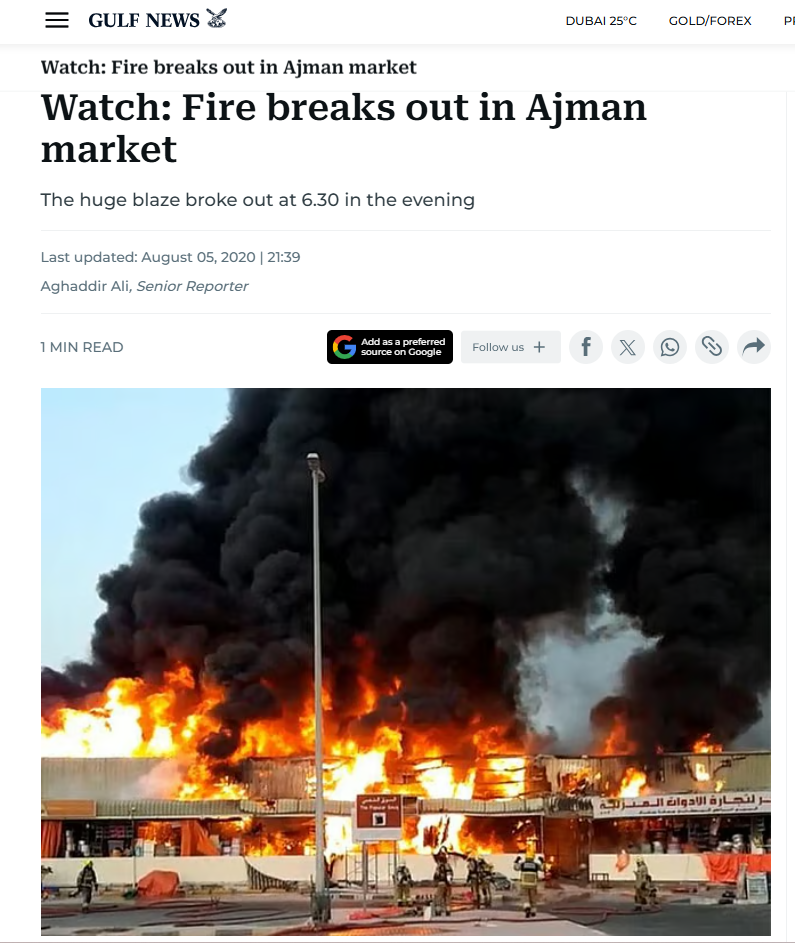
According to the Gulf News report, a major fire broke out at a public market in the new industrial area of Ajman at around 6:30 pm. The blaze was later brought under control by Ajman Civil Defence with assistance from teams in Dubai, Sharjah, and Umm Al Quwain.
Conclusion:
Our research found that the viral video has been online since 2020 and shows a fire at a market in Ajman, UAE. It is not related to any recent incident at Dubai Airport.

Introduction
The world has been riding the wave of technological advancements, and the fruits it has born have impacted our lives. Technology, by its virtue, cannot be quantified as safe or unsafe it is the application and use of technology which creates the threats. Its times like this, the importance and significance of policy framework are seen in cyberspace. Any technology can be governed by means of policies and laws only. In this blog, we explore the issues raised by the EU for the tech giants and why the Indian Govt is looking into probing Whatsapp.
EU on Big Techs
Eu has always been seen to be a strong policy maker for cyberspace, and the same can be seen from the scope, extent and compliance of GDPR. This data protection bill is the holy grail for worldwide data protection bills. Apart from the GDPR, the EU has always maintained strong compliance demographics for the big tech as most of them have originated outside of Europe, and the rights of EU citizens come into priority above anything else.
New Draft Notification
According to the draft of the new notification, Amazon, Google, Microsoft and other non-European Union cloud service providers looking to secure an EU cybersecurity label to handle sensitive data can only do so via a joint venture with an EU-based company. The document adds that the cloud service must be operated and maintained from the EU, all customer data must be stored and processed in the EU, and EU laws take precedence over non-EU laws regarding the cloud service provider. Certified cloud services are operated only by companies based in the EU, with no entity from outside the EU having effective control over the CSP (cloud service provider) to mitigate the risk of non-EU interfering powers undermining EU regulations, norms and values.
This move from the EU is still in the draft phase however, it is expected to come into action soon as issues related to data breaches of EU citizens have been reported on numerous occasions. The document said the tougher rules would apply to personal and non-personal data of particular sensitivity where a breach may have a negative impact on public order, public safety, human life or health, or the protection of intellectual property.
How will it secure the netizens?
Since the EU has been the leading policy maker in cyberspace, it is often seen that the rules and policies of the EU are often replicated around the world. Hence this move comes at a critical time as the EU is looking towards safeguarding the EU netizens and the Cyber security industry in the EU by allowing them to collaborate with big tech while maintaining compliance. Cloud services can be protected by this mechanism, thus ensuring fewer instances of data breaches, thus contributing to a dip in cyber crimes and attacks.
The Indian Govt on WhatsApp
The Indian Govt has decided to probe Whatsapp and its privacy settings. One of the Indian Whatsapp users tweeted a screenshot of WhatsApp accessing the phone’s mic even when the phone was not in use, and the app was not open even in the background. The meta-owned Social messaging platform enjoys nearly 487 million users in India, making it their biggest market. The 2018 judgement on Whatsapp and its privacy issues was a landmark judgement, but the platform is in violation of the same.
The MoS, Ministry of Electronics and Information Technology, Rajeev Chandrashekhar, has already tweeted that the issue will be looked into and that they will be punished if the platform is seen violating the guidelines. The Digital Personal Data Protection Bill is yet to be tabled at the parliament. Still, despite the draft bill being public, big platforms must maintain the code of conduct to maintain compliance when the bill turns into an Act.
Threats for Indian Users
The Indian Whatsapp user contributes to the biggest user base un the world, and still, they are vulnerable to attacks on WhatsApp and now WhatsApp itself. The netizens are under the following potential threats –
- Data breaches
- Identity theft
- Phishing scams
- Unconsented data utilisation
- Violation of Right to Privacy
- Unauthorised flow of data outside India
- Selling of data to a third party without consent
The Indian netizen needs to stay vary of such issues and many more by practising basic cyber safety and security protocols and keeping a check on the permissions granted to apps, to keep track of one’s digital footprint.
Conclusion
Whether it’s the EU or Indian Government, it is pertinent to understand that the world powers are all working towards creating a safe and secured cyberspace for its netizens. The move made by the EU will act as a catalyst for change at a global level, as once the EU enforces the policy, the world will soon replicate it to safeguard their cyber interests, assets and netizens. The proactive stance of the Indian Government is a crucial sign that the things will not remain the same in the Indian Cyber ecosystem, and its upon the platforms and companies to ensure compliance, even in the absence of a strong legislation for cyberspace. The government is taking all steps to safeguard the Indian netizen, as the same lies in the souls and spirit of the new Digital India Bill, which will govern cyberspace in the near future. Still, till then, in order to maintain the synergy and equilibrium, it is pertinent for the platforms to be in compliance with the laws of natural justice.
