
#FactCheck - Stunning 'Mount Kailash' Video Exposed as AI-Generated Illusion!
EXECUTIVE SUMMARY:
A viral video is surfacing claiming to capture an aerial view of Mount Kailash that has breathtaking scenery apparently providing a rare real-life shot of Tibet's sacred mountain. Its authenticity was investigated, and authenticity versus digitally manipulative features were analyzed.
CLAIMS:
The viral video claims to reveal the real aerial shot of Mount Kailash, as if exposing us to the natural beauty of such a hallowed mountain. The video was circulated widely in social media, with users crediting it to be the actual footage of Mount Kailash.


FACTS:
The viral video that was circulated through social media was not real footage of Mount Kailash. The reverse image search revealed that it is an AI-generated video created by Sonam and Namgyal, two Tibet based graphic artists on Midjourney. The advanced digital techniques used helped to provide a realistic lifelike scene in the video.
No media or geographical source has reported or published the video as authentic footage of Mount Kailash. Besides, several visual aspects, including lighting and environmental features, indicate that it is computer-generated.
For further verification, we used Hive Moderation, a deep fake detection tool to conclude whether the video is AI-Generated or Real. It was found to be AI generated.

CONCLUSION:
The viral video claiming to show an aerial view of Mount Kailash is an AI-manipulated creation, not authentic footage of the sacred mountain. This incident highlights the growing influence of AI and CGI in creating realistic but misleading content, emphasizing the need for viewers to verify such visuals through trusted sources before sharing.
- Claim: Digitally Morphed Video of Mt. Kailash, Showcasing Stunning White Clouds
- Claimed On: X (Formerly Known As Twitter), Instagram
- Fact Check: AI-Generated (Checked using Hive Moderation).

Related Blogs

Introduction
The Australian Parliament has passed the world’s first legislation regarding a ban on social media for children under 16. This was done citing risks to the mental and physical well-being of children and the need to contain misogynistic influence on them. The debate surrounding the legislation is raging strong, as it is the first proposal of its kind and would set precedence for how other countries can assess their laws regarding children and social media platforms and their priorities.
The Legislation
Currently trailing an age-verification system (such as biometrics or government identification), the legislation mandates a complete ban on underage children using social media, setting the age limit to 16 or above. Further, the law does not provide exemptions of any kind, be it for pre-existing accounts or parental consent. With federal elections approaching, the law seeks to address parental concerns regarding measures to protect their children from threats lurking on social media platforms. Every step in this regard is being observed with keen interest.
The Australian Prime Minister, Anthony Albanese, emphasised that the onus of taking responsible steps toward preventing access falls on the social media platforms, absolving parents and their children of the same. Social media platforms like TikTok, X, and Meta Platforms’ Facebook and Instagram all come under the purview of this legislation.
CyberPeace Overview
The issue of a complete age-based ban raises a few concerns:
- It is challenging to enforce digitally as children might find a way to circumnavigate such restrictions. An example would be the Cinderella Law, formally known as the Shutdown Law, which the Government of South Korea had implemented back in 2011 to reduce online gaming and promote healthy sleeping habits among children. The law mandated the prohibition of access to online gaming for children under the age of 16 between 12 A.M. to 6 A.M. However, a few drawbacks rendered it less effective over time. Children were able to use the login IDs of adults, switch to VPN, and even switch to offline gaming. In addition, parents also felt the government was infringing on the right to privacy and the restrictions were only for online PC games and did not extend to mobile phones. Consequently, the law lost relevance and was repealed in 2021.
- The concept of age verification inherently requires collecting more personal data and inadvertently opens up concerns regarding individual privacy.
- A ban is likely to reduce the pressure on tech and social media companies to develop and work on areas that would make their services a safe child-friendly environment.
Conclusion
Social media platforms can opt for an approach that focuses on how to create a safe environment online for children as they continue to deliberate on restrictions. An example of an impactful-yet-balanced step towards the protection of children on social media while respecting privacy is the U.K.'s Age-Appropriate Design Code (UK AADC). It is the U.K.’s implementation of the European Union’s General Data Protection Regulation (GDPR), prepared by the ICO (Information Commissioner's Office), the U.K. data protection regulator. It follows a safety-by-design approach for children. As we move towards a future that is predominantly online, we must continue to strive and create a safe space for children and address issues in innovative ways.
References
- https://indianexpress.com/article/technology/social/australia-proposes-ban-on-social-media-for-children-under-16-9657544/
- https://www.thehindu.com/opinion/op-ed/should-children-be-barred-from-social-media/article68661342.ece
- https://forumias.com/blog/debates-on-whether-children-should-be-banned-from-social-media/
- https://timesofindia.indiatimes.com/education/news/why-banning-kids-from-social-media-wont-solve-the-youth-mental-health-crisis/articleshow/113328111.cms
- https://iapp.org/news/a/childrens-privacy-laws-and-freedom-of-expression-lessons-from-the-uk-age-appropriate-design-code
- https://www.techinasia.com/s-koreas-cinderella-law-finally-growing-up-teens-may-soon-be-able-to-play-online-after-midnight-again
- https://wp.towson.edu/iajournal/2021/12/13/video-gaming-addiction-a-case-study-of-china-and-south-korea/
- https://www.dailysabah.com/world/asia-pacific/australia-passes-worlds-1st-total-social-media-ban-for-children
Executive Summary
A video of Prime Minister Narendra Modi is being shared on social media with the claim that he disrespected the national anthem by continuing to walk while it was being played. The CyberPeace Research Wing’s investigation found that the claim is false. The audio heard in the viral clip has been added separately to the original footage, creating a misleading impression about what was happening in the video.
Claim
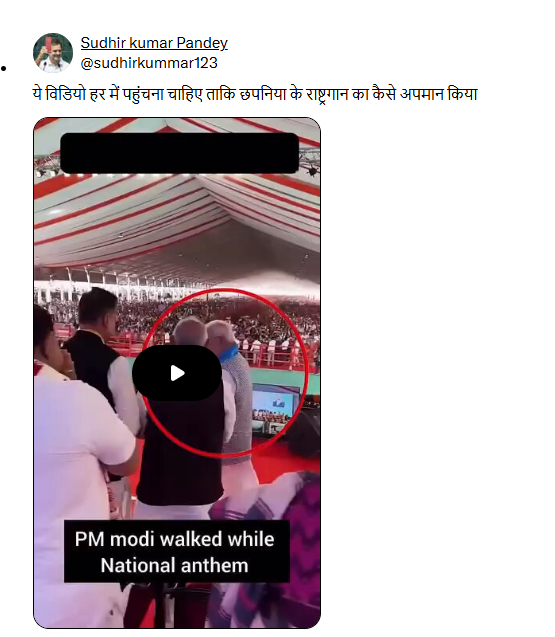
An X user shared the video claiming that Prime Minister Narendra Modi continued walking during the national anthem, thereby disrespecting it.
https://x.com/sudhirkummar123/status/2089044275665535414?s=20
Fact Check
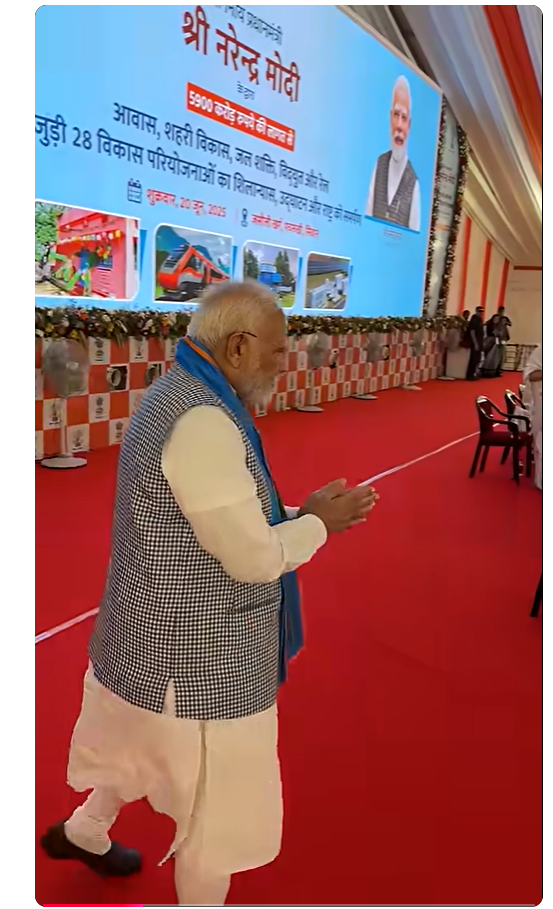
To verify the claim, the Desk conducted a reverse image search using keyframes from the viral video. The search led us to a longer version of the footage uploaded on Prime Minister Narendra Modi’s official YouTube channel on June 21, 2025. We reviewed the longer video and found that the audio in the viral clip does not match the original footage. The original video does not feature the national anthem being played. Instead, a female announcer on the stage can be heard asking the gathering to welcome Prime Minister Modi upon his arrival in Siwan, Bihar. The description accompanying the original video also states that people gave Prime Minister Modi a warm welcome upon his arrival in Siwan.
https://www.youtube.com/shorts/YhBryZZwlIk
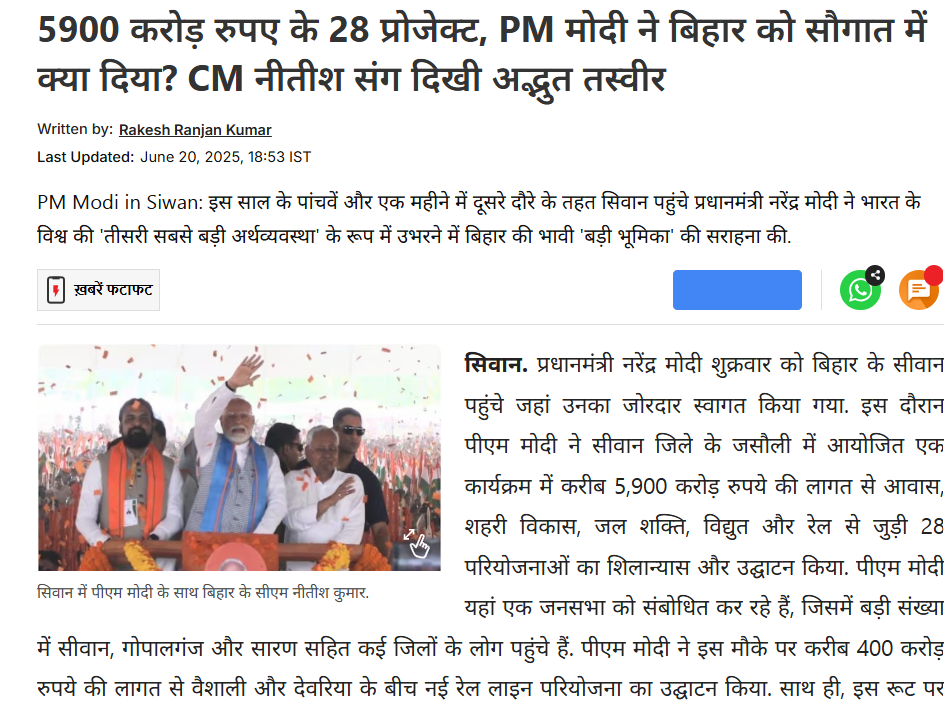
The investigation also found several media reports published on June 20, 2025, which reported that Modi had visited Siwan ahead of the Bihar Assembly elections and inaugurated or laid the foundation stones for development projects worth around Rs 5,900 crore. News18 report on PM Modi’s Siwan visit
The original footage therefore establishes that the scene was related to Modi’s welcome in Siwan and not to the playing of the national anthem.
Conclusion
The claim that Prime Minister Narendra Modi disrespected the national anthem by walking during its rendition is false. The original footage does not contain the national anthem. The audio heard in the viral clip has been added separately to the video, creating a false impression about the incident.
Introduction
Insurance companies hold a huge amount of sensitive data. Medical history, bank account numbers, identity proofs, years of claims records — all of it sits on insurer servers, waiting. That makes the sector an easy target. India saw close to 370 million malware attacks in a single recent year. Banking, financial services and insurance firms bore the brunt of it. That got the attention of the Insurance Regulatory and Development Authority of India (IRDAI). On 6 April 2026, it released a new set of Information and Cyber Security Guidelines. These replace the old 2023 rules and ask insurers to take much stronger responsibility for protecting their systems, and their customers' data.
Who Must Follow These New Rules
The updated guidelines are not limited to large insurance companies alone. They apply to life, general and health insurers. They also apply to foreign reinsurance branches operating in India, and to intermediaries such as brokers, corporate agents, web aggregators and third-party administrators. Insurance repositories and the Insurance Information Bureau of India fall within scope too. Individual insurance agents, point-of-sale persons and surveyors are not covered directly. But insurers must still make sure these people follow a basic security framework approved by their board. Foreign reinsurance branches get a little more room — they can depart from a specific rule, but only if they can justify it properly to the regulator. Why cast such a wide net in the first place? Because breaches rarely start at the big insurer with the well-staffed Information Technology (IT) team. They start with the small broker or corporate agent who never got around to updating a password policy.
A Stronger Role for the Boardroom
An Independent CISO (Chief Information Security Officer)
The clearest change sits right at the top. A Chief Information Security Officer (CISO) can no longer report to the Head of Information Technology (IT). Nor can the CISO (Chief Information Security Officer) be handed sales targets or any other business goal. Why does this matter so much? Picture a CISO (Chief Information Security Officer) who answers to the same person pushing hard for a product launch next week. Flagging a serious vulnerability suddenly becomes an awkward, career-risking conversation. The IRDAI (Insurance Regulatory and Development Authority of India) has simply removed that awkwardness by rule.
More Frequent Oversight
The Information Security Risk Management Committee used to meet only twice a year. Now it must meet at least once every quarter. A new Information Technology (IT) Steering Committee has also been set up to handle day-to-day technology decisions. This frees the risk committee to focus purely on oversight. There's also a new seat at the table: at least one outside cybersecurity expert must now join the Risk Management Committee. Someone with no stake in internal politics, no department to protect, just technical judgement.
Faster Action When Something Goes Wrong
A Six-Hour Reporting Deadline
No system is completely safe from attack. So the guidelines also focus heavily on how insurers respond once something goes wrong. Every cybersecurity incident now has to reach the Indian Computer Emergency Response Team within six hours of being spotted, with the IRDAI (Insurance Regulatory and Development Authority of India) and other regulators looped in at the same time. Six hours is a tight deadline. It means insurers need detection and escalation systems that work round the clock, not just during office hours.
Testing and Exceptions
Business continuity and disaster recovery plans must be tested at least once a year, and not through some comfortable, pre-planned shutdown either — the test has to feel like a real disaster. Exceptions to security policy are also handled with far more discipline now. A short exception of up to three months can be approved by the CISO (Chief Information Security Officer) alone. One lasting between three months and a year needs sign-off from the risk committee. Anything longer needs approval from the board itself. Gaps found during audits must be closed within twelve months, with the board tracking progress at every stage.
Looking Ahead to Tomorrow's Risks
The guidelines do not stop at today's threats. More insurers are moving their operations to the cloud. So the rules now demand stronger contracts with cloud vendors, and a clear plan for what happens to customer data once a vendor relationship ends. Third-party risk gets close attention too. Many security breaches in the financial sector start with a vendor, not with the insurer's own systems. Before hiring any vendor, insurers must now check their security properly. Every contract must include audit rights and a clause requiring the vendor to report incidents. One of the most forward-looking additions is early preparation for a post-quantum world. Insurers must keep a clear list of their cryptographic assets. In simple terms, this is a map of where and how encryption is used across their systems. It helps them get ready once stronger encryption standards become necessary. Quantum computers capable of breaking today's encryption are still some years away, by most estimates. Mapping out those cryptographic assets now is a lot cheaper than scrambling to do it after the threat has already landed.
Conclusion
Where does all this leave things? Cybersecurity in Indian insurance isn't a server-room problem anymore — it sits squarely in the boardroom now. Directors now own this risk, not just Information Technology (IT) managers tucked away in a basement office. Policyholders benefit too, since their data now sits behind stronger locks, watched more closely and reported on far more often than before. Insurers who treat this as a paperwork exercise will struggle to keep up. Those who actually build these habits into daily operations will likely spend less time firefighting breaches five years from now, and more time competing on service and price instead.
References
3. Medianama, 'IRDAI Updates Cybersecurity Rules, Mandates DPDP Compliance', April 2026.
4. DSCI, brief on IRDAI's Information and Cyber Security Guidelines, 2026, April 2026.
7. Deloitte India, 'IRDAI Tightens Cyber Net: Wake-up Call for Insurers'.
