
#FactCheck - "Deep fake Falsely Claimed as a photo of Arvind Kejriwal welcoming Elon Musk when he visited India to discuss Delhi’s administrative policies.”
Executive Summary:
A viral online image claims to show Arvind Kejriwal, Chief Minister of Delhi, welcoming Elon Musk during his visit to India to discuss Delhi’s administrative policies. However, the CyberPeace Research Team has confirmed that the image is a deep fake, created using AI technology. The assertion that Elon Musk visited India to discuss Delhi’s administrative policies is false and misleading.


Claim
A viral image claims that Arvind Kejriwal welcomed Elon Musk during his visit to India to discuss Delhi’s administrative policies.


Fact Check:
Upon receiving the viral posts, we conducted a reverse image search using InVid Reverse Image searching tool. The search traced the image back to different unrelated sources featuring both Arvind Kejriwal and Elon Musk, but none of the sources depicted them together or involved any such event. The viral image displayed visible inconsistencies, such as lighting disparities and unnatural blending, which prompted further investigation.
Using advanced AI detection tools like TrueMedia.org and Hive AI Detection tool, we analyzed the image. The analysis confirmed with 97.5% confidence that the image was a deepfake. The tools identified “substantial evidence of manipulation,” particularly in the merging of facial features and the alignment of clothes and background, which were artificially generated.


Moreover, a review of official statements and credible reports revealed no record of Elon Musk visiting India to discuss Delhi’s administrative policies. Neither Arvind Kejriwal’s office nor Tesla or SpaceX made any announcement regarding such an event, further debunking the viral claim.
Conclusion:
The viral image claiming that Arvind Kejriwal welcomed Elon Musk during his visit to India to discuss Delhi’s administrative policies is a deep fake. Tools like Reverse Image search and AI detection confirm the image’s manipulation through AI technology. Additionally, there is no supporting evidence from any credible sources. The CyberPeace Research Team confirms the claim is false and misleading.
- Claim: Arvind Kejriwal welcomed Elon Musk to India to discuss Delhi’s administrative policies, viral on social media.
- Claimed on: Facebook and X(Formerly Twitter)
- Fact Check: False & Misleading

Related Blogs

Overview:
A recent addition to the list of cybercrime is SharpRhino, a RAT (Remote Access Trojan) actively used by Hunters International ransomware group. SharpRhino is highly developed and penetrates into the network mask of IT specialists, primarily due to the belief in the tools’ legitimacy. Going under the genuine software installer, SharpRhino started functioning in mid-June 2024. However, Quorum Cyber discovered it in early August 2024 while investigating ransomware.
About Hunters International Group:
Hunters International emerged as one of the most notorious groups focused on ransomware attacks, having compromised over 134 targets worldwide in the first seven months of 2024. It is believed that the group is the rebranding of Hive ransomware group that was previously active, and there are considerable similarities in the code. Its focus on IT employees in particular demonstrates the fact that they move tactically in gaining access to the organizations’ networks.
Modus Operandi:
1. Typosquatting Technique
SharpRhino is mainly distributed by a domain that looks like the genuine Angry IP Scanner, which is a popular network discovery tool. The malware installer, labeled as ipscan-3.9.1-setup. It is a 32-bit Nullsoft installer which embeds a password protected 7z archive in it.
2. Installation Process
- Execution of Installer: When the victim downloads and executes the installer and changes the windows registry in order to attain persistence. This is done by generating a registry entry that starts a harmful file, Microsoft. AnyKey. exe, are fakes originating from fake versions of true legitimate Microsoft Visual Studio tools.
- Creation of Batch File: This drops a batch file qualified as LogUpdate at the installer.bat, that runs the PowerShell scripts on the device. These scripts are to compile C# code into memory to serve as a means of making the malware covert in its operation.
- Directory Creation: The installer establishes two directories that allow the C2 communication – C:\ProgramData\Microsoft: WindowsUpdater24 and LogUpdateWindows.
3. Execution and Functionality:
- Command Execution: The malware can execute PowerShell commands on the infected system, these actions may involve privilege escalation and other extended actions such as lateral movement.
- C2 Communication: SharpRhino interacts with command and control servers located on domains from platforms such as Cloudflare. This communication is necessary for receiving commands from the attackers and for returning any data of interest to the attackers.
- Data Exfiltration and Ransomware Deployment: Once SharpRhino has gained control, it can steal information and then proceed to encrypt it with a .locked extension. The procedure generally concludes with a ransom message, which informs users on how to purchase the decryption key.
4. Propagation Techniques:
Also, SharpRhino can spread through the self-copying method, this is the virus may copy itself to other computers using the network account of the victim and pretending to be trustworthy senders such as emails or network-shared files. Moreover, the victim’s machine may then proceed to propagate the malware to other systems like sharing in the company with other employees.
Indicators of Compromise (IOCs):
- LogUpdate.bat
- Wiaphoh7um.t
- ipscan-3.9.1-setup.exe
- kautix2aeX.t
- WindowsUpdate.bat
Command and Control Servers:
- cdn-server-1.xiren77418.workers.dev
- cdn-server-2.wesoc40288.workers.dev
- Angryipo.org
- Angryipsca.com
Analysis:

Graph:

Precautionary measures to be taken:
To mitigate the risks posed by SharpRhino and similar malware, organizations should implement the following measures:
- Implement Security Best Practices: It is important only to download software from official sites and avoid similar sites to confuse the user by changing a few letters.
- Enhance Detection Capabilities: Use technology in detection that can detect the IOCs linked to Sharp Rhino.
- Educate Employees: Educate IT people and employees on phishing scams and the requirement to check the origin of the application.
- Regular Backups: It is also important to back up important files from systems and networks in order to minimize the effects of ransomware attacks on a business.
Conclusion:
SharpRhino could be deemed as the evolution of the strategies used by organizations like Hunters International and others involved in the distribution of ransomware. SharpRhino primarily focuses on the audience of IT professionals and employs complex delivery and execution schemes, which makes it an extremely serious threat for corporate networks. To do so it is imperative that organizations have an understanding of its inner workings in order to fortify their security measures against this relatively new threat. Through the enforcement of proper security measures and constant enlightenment of organizations on the importance of cybersecurity, firms can prevent the various risks associated with SharpRhino and related malware. Be safe, be knowledgeable, and most importantly, be secure when it comes to cyber security for your investments.
Reference:
https://cybersecuritynews.com/sharprhino-ransomware-alert/
https://cybersecsentinel.com/sharprhino-explained-key-facts-and-how-to-protect-your-data/
https://www.dataprivacyandsecurityinsider.com/2024/08/sharprhino-malware-targeting-it-professionals/
Executive Summary
A video of Indian Army Chief General Dhiraj Seth is being shared on social media, allegedly showing him referring to an incident in which Major Rajendra Pratap Singh survived for 40 days by drinking cow urine during the 1965 India-Pakistan war and saying that Indian Army personnel should keep such a practice alive. The video is being shared with the claim that General Dhiraj Seth said that Major Rajendra Pratap Singh had consumed cow urine for 40 days to quench his thirst during the 1965 war and that serving Army personnel should also continue the practice. However, CyberPeace Research Wing found the claim to be false. The viral video has been digitally manipulated, with fabricated audio/remarks added to it. In the original video, General Dhiraj Seth did not make any such statement.
Claim:
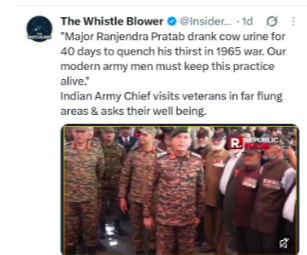
Indian Army Chief General Dhiraj Seth allegedly referred to an incident in which Major Rajendra Pratap Singh survived for 40 days by drinking cow urine during the 1965 India-Pakistan war and urged serving Army personnel to keep the practice alive.
https://x.com/InsiderWB/status/2104242428647727428
Fact Check
To verify the truth behind the viral claim, we conducted a Google search using relevant keywords. During the search, we did not find any credible media reports supporting the claim. As part of the next step in our research, we extracted keyframes from the video and conducted a reverse image search. During the research, we found the original video on Gulistan News, which was published on September 25, 2026.
https://x.com/GulistanNewsTV/status/2103461004374061389
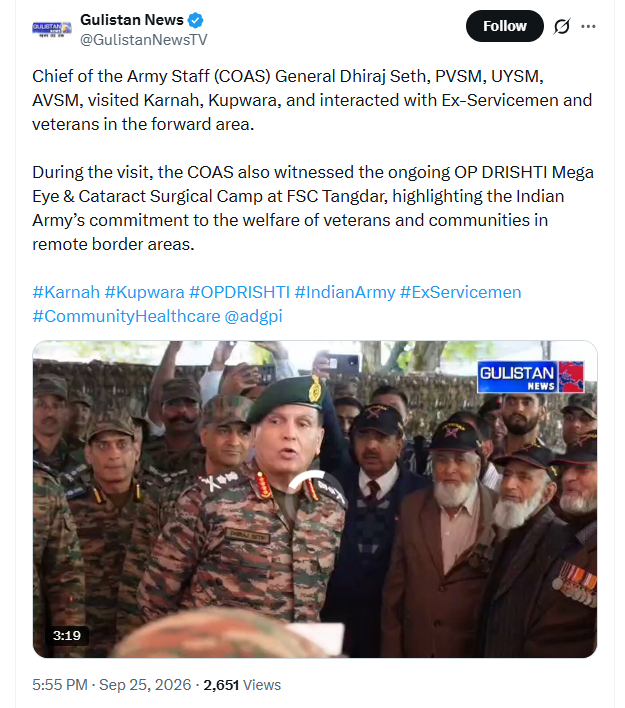
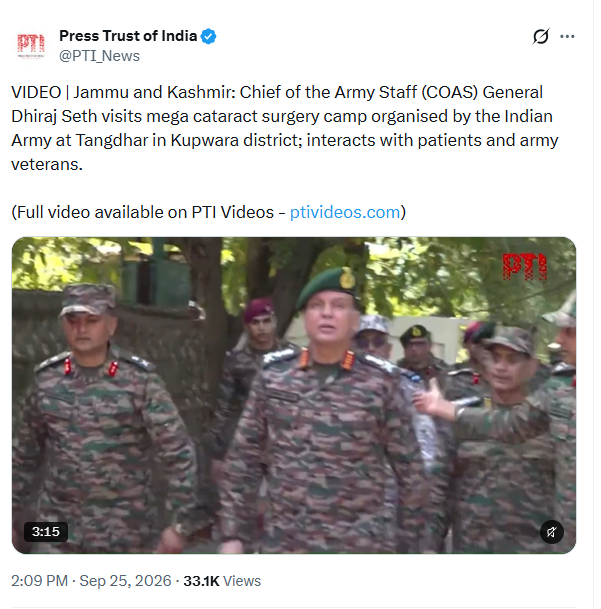
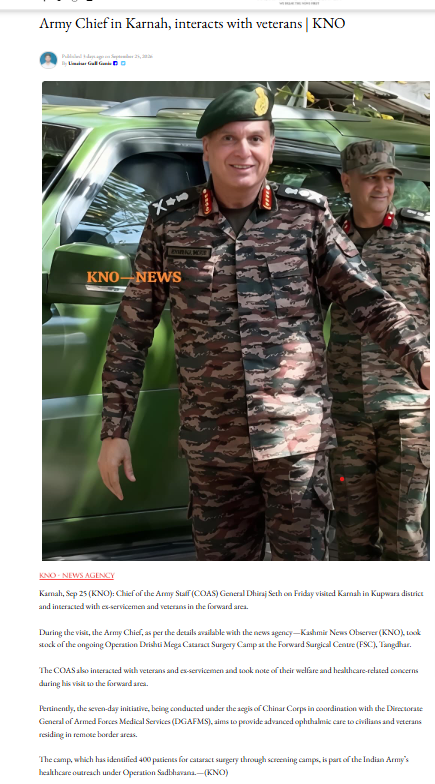
According to Gulistan News, Chief of the Army Staff (COAS) General Dhiraj Seth, PVSM, UYSM, AVSM, visited Karnah in Kupwara and interacted with ex-servicemen and veterans in the forward area. During the visit, the Army Chief also took stock of the ongoing ‘Operation Drishti’ Mega Eye and Cataract Surgical Camp at FSC Tangdhar. The initiative highlights the Indian Army’s commitment to the welfare of veterans and local communities in remote border areas. Further research led us to a video posted by the Press Trust of India (PTI) on X. According to its caption, Army Chief (COAS) General Dhiraj Seth visited the mega cataract surgery camp organised by the Indian Army at Tangdhar in Kupwara district and interacted with patients and army veterans.
https://x.com/PTI_News/status/2103404022279598579?s=20
After verifying the viral video, we conducted a Google search using relevant keywords. During the search, we found a report by the news agency Kashmir News Observer (KNO). According to the report, Chief of the Army Staff (COAS) General Dhiraj Seth visited Karnah in Kupwara district on Friday and interacted with ex-servicemen and veterans in the forward area. During the visit, the Army Chief took stock of the ongoing ‘Operation Drishti’ Mega Cataract Surgery Camp at the Forward Surgical Centre (FSC), Tangdhar.The COAS also interacted with veterans and ex-servicemen and took note of their welfare and healthcare-related concerns.The seven-day initiative, being conducted under the aegis of Chinar Corps in coordination with the Directorate General of Armed Forces Medical Services (DGAFMS), aims to provide advanced ophthalmic care to civilians and veterans residing in remote border areas.
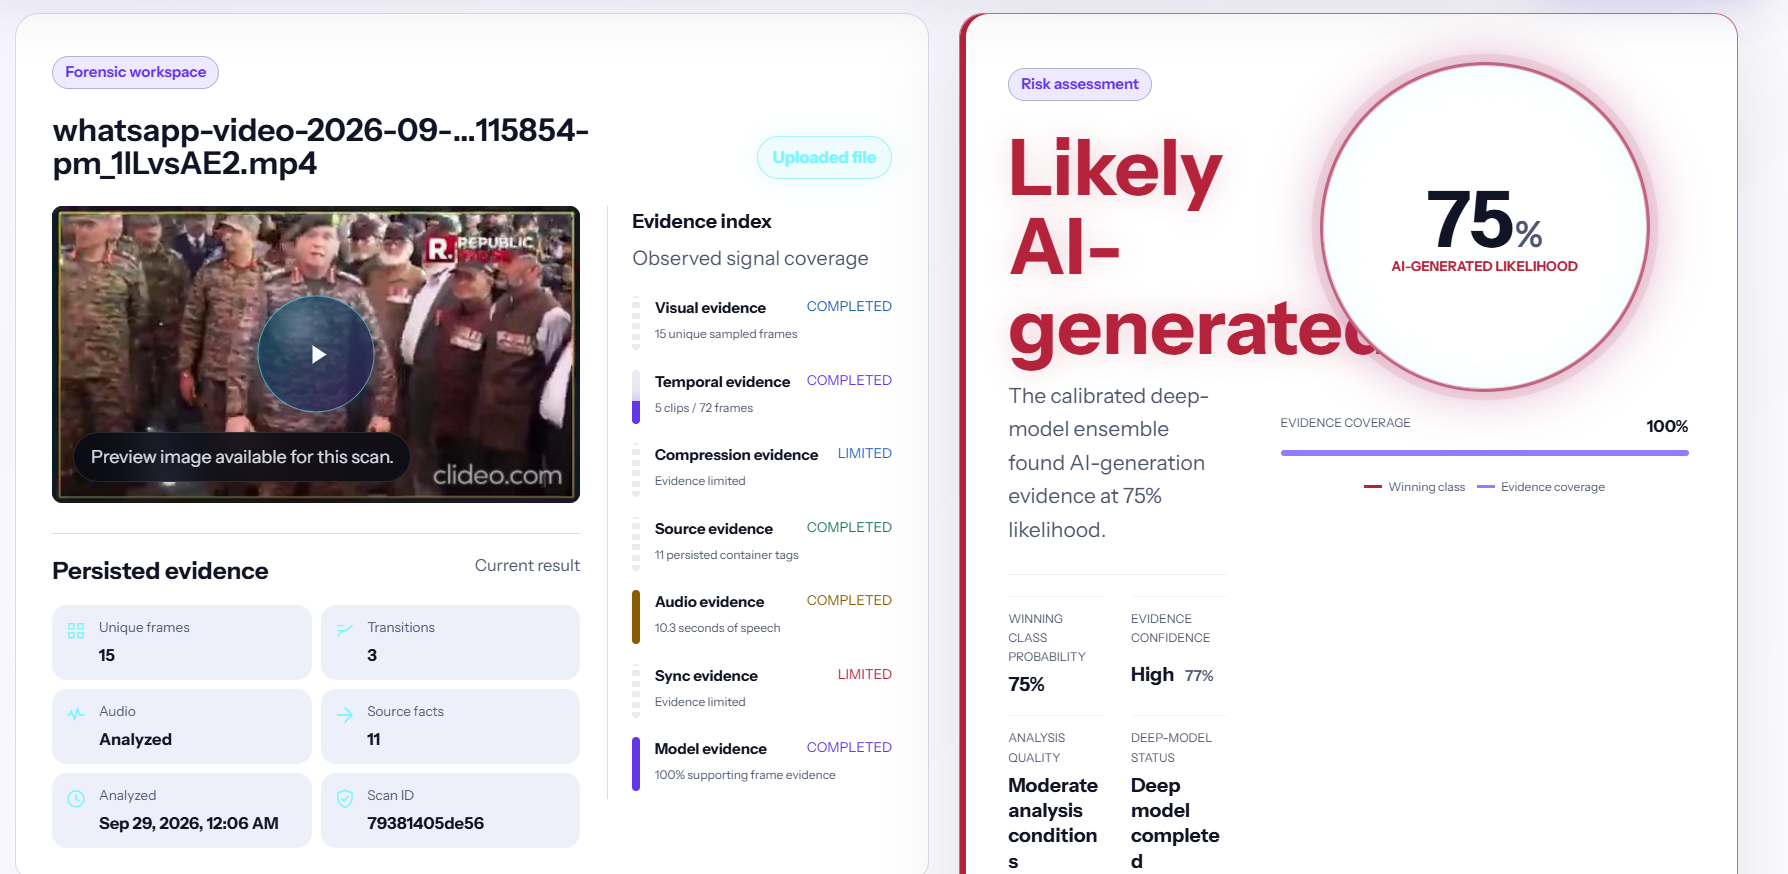
We scanned the video using the AI detection tool Detect Video AI. According to the results, the viral video is 75 per cent AI-generated.
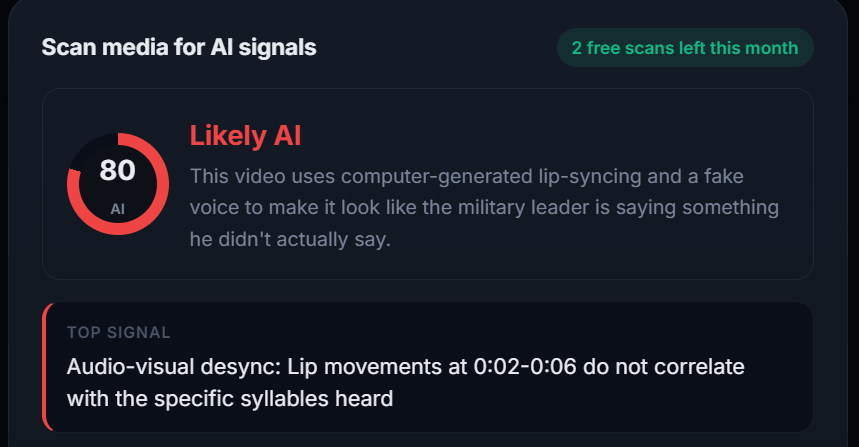
At the end of our research, we also scanned the video using HumanMeter. According to the results, the viral video is 80 per cent AI-generated.
Conclusion:
The video being circulated on social media in the name of Indian Army Chief General Dhiraj Seth is misleading. The viral video purportedly shows him referring to an incident in which Major Rajendra Pratap Singh allegedly survived for 40 days by drinking cow urine during the 1965 India-Pakistan war and saying that Army personnel should keep the practice alive. However, the original video available does not contain any such statement by General Dhiraj Seth. The viral video has been digitally manipulated, with fabricated remarks attributed to him.

Introduction:
This Op-ed sheds light on the perspectives of the US and China regarding cyber espionage. Additionally, it seeks to analyze China's response to the US accusation regarding cyber espionage.
What is Cyber espionage?
Cyber espionage or cyber spying is the act of obtaining personal, sensitive, or proprietary information from individuals without their knowledge or consent. In an increasingly transparent and technological society, the ability to control the private information an individual reveals on the Internet and the ability of others to access that information are a growing concern. This includes storage and retrieval of e-mail by third parties, social media, search engines, data mining, GPS tracking, the explosion of smartphone usage, and many other technology considerations. In the age of big data, there is a growing concern for privacy issues surrounding the storage and misuse of personal data and non-consensual mining of private information by companies, criminals, and governments.
Cyber espionage aims for economic, political, and technological gain. Fox example Stuxnet (2010) cyber-attack by the US and its allies Israel against Iran’s Nuclear facilities. Three espionage tools were discovered connected to Stuxnet, such as Gauss, FLAME and DuQu, for stealing data such as passwords, screenshots, Bluetooth, Skype functions, etc.
Cyber espionage is one of the most significant and intriguing international challenges globally. Many nations and international bodies, such as the US and China, have created their definitions and have always struggled over cyber espionage norms.
The US Perspective
In 2009, US officials (along with other allied countries) mentioned that cyber espionage was acceptable if it safeguarded national security, although they condemned economically motivated cyber espionage. Even the Director of National Intelligence said in 2013 that foreign intelligence capabilities cannot steal foreign companies' trade secrets to benefit their firms. This stance is consistent with the Economic Espionage Act (EEA) of 1996, particularly Section 1831, which prohibits economic espionage. This includes the theft of a trade secret that "will benefit any foreign government, foreign agent or foreign instrumentality.
Second, the US advocates for cybersecurity market standards and strongly opposes transferring personal data extracted from the US Office of Personnel Management (OPM) to cybercrime markets. Furthermore, China has been reported to sell OPM data on illicit markets. It became a grave concern for the US government when the Chinese government managed to acquire sensitive details of 22.1 million US government workers through cyber intrusions in 2014.
Third, Cyber-espionage is acceptable unless it’s utilized for Doxing, which involves disclosing personal information about someone online without their consent and using it as a tool for political influence operations. However, Western academics and scholars have endeavoured to distinguish between doxing and whistleblowing. They argue that whistleblowing, exemplified by events like the Snowden Leaks and Vault 7 disclosures, serves the interests of US citizens. In the US, being regarded as an open society, certain disclosures are not promoted but rather required by mandate.
Fourth, the US argues that there is no cyber espionage against critical infrastructure during peacetime. According to the US, there are 16 critical infrastructure sectors, including chemical, nuclear, energy, defence, food, water, and so on. These sectors are considered essential to the US, and any disruption or harm would impact security, national public health and national economic security.
The US concern regarding China’s cyber espionage
According to James Lewis (a senior vice president at the Center for US-China Economic and Security Review Commission), the US faces losses between $ 20 billion and $30 billion annually due to China’s cyberespionage. The 2018 U.S. Trade Representative (USTR) Section 301 report highlighted instances, where the Chinese government and executives from Chinese companies engaged in clandestine cyber intrusions to obtaining commercially valuable information from the U.S. businesses, such as in 2018 where officials from China’s Ministry of State Security, stole trade from General Electric aviation and other aerospace companies.
China's response to the US accusations of cyber espionage
China's perspective on cyber espionage is outlined by its 2014 anti-espionage law, which was revised in 2023. Article 1 of this legislation is formulated to prevent, halt, and punish espionage actions to maintain national security. Article 4 addresses the act of espionage and does not differentiate between state-sponsored cyber espionage for economic purposes and state-sponsored cyber espionage for national security purposes. However, China doesn't make a clear difference between government-to-government hacking (spying) and government-to-corporate sector hacking, unlike the US. This distinction is less apparent in China due to its strong state-owned enterprise (SOE) sector. However, military spying is considered part of the national interest in the US, while corporate spying is considered a crime.
China asserts that the US has established cyber norms concerning cyber espionage to normalize public attribution as acceptable conduct. This is achieved by targeting China for cyber operations, imposing sanctions on accused Chinese individuals, and making political accusations, such as blaming China and Russia for meddling in US elections. Despite all this, Washington D.C has never taken responsibility for the infamous Flame and Stuxnet cyber operations, which were widely recognized as part of a broader collaborative initiative known as Operation Olympic Games between the US and Israel. Additionally, the US takes the lead in surveillance activities conducted against China, Russia, German Chancellor Angela Merkel, the United Nations (UN) Secretary-General, and several French presidents. Surveillance programs such as Irritant Horn, Stellar Wind, Bvp47, the Hive, and PRISM are recognized as tools used by the US to monitor both allies and adversaries to maintain global hegemony.
China urges the US to cease its smear campaign associated with Volt Typhoon’s cyberattack for cyber espionage, citing the publication of a report titled “Volt Typhoon: A Conspiratorial Swindling Campaign Targets with U.S. Congress and Taxpayers Conducted by U.S. Intelligence Community” by China's National Computer Virus Emergency Response Centre and the 360 Digital Security Group on 15 April. According to the report, 'Volt Typhoon' is a ransomware cyber criminal group self-identified as the 'Dark Power' and is not affiliated with any state or region. Multiple cybersecurity authorities in the US collaborated to fabricate this story just for more budgets from Congress. In the meantime, Microsoft and other U.S. cybersecurity firms are seeking more big contracts from US cybersecurity authorities. The reality behind “Volt Typhoon '' is a conspiratorial swindling campaign to achieve two objectives by amplifying the "China threat theory" and cheating money from the U.S. Congress and taxpayers.
Beijing condemned the US claims of cyber espionage without any solid evidence. China also blames the US for economic espionage by citing the European Parliament report that the National Security Agency (NSA) was also involved in assisting Boeing in beating Airbus for a multi-billion dollar contract. Furthermore, Brazilian President Dilma Rousseff also accused the US authorities of spying against the state-owned oil company “Petrobras” for economic reasons.
Conclusion
In 2015, the US and China marked a milestone as both President Xi Jinping and Barack Obama signed an agreement, committing that neither country's government would conduct or knowingly support cyber-enabled theft of trade secrets, intellectual property, or other confidential business information to grant competitive advantages to firms or commercial sectors. However, the China Cybersecurity Industry Alliance (CCIA) published a report titled 'US Threats and Sabotage to the Security and Development of Global Cyberspace' in 2024, highlighting the US escalating cyber-attack and espionage activities against China and other nations. Additionally, there has been a considerable increase in the volume and sophistication of Chinese hacking since 2016. According to a survey by the Center for International and Strategic Studies, out of 224 cyber espionage incidents reported since 2000, 69% occurred after Xi assumed office. Therefore, China and the US must address cybersecurity issues through dialogue and cooperation, utilizing bilateral and multilateral agreements.

