
DPDP Bill 2023 A Comparative Analysis
Introduction
THE DIGITAL PERSONAL DATA PROTECTION BILL, 2022 Released for Public Consultation on November 18, 2022THE DIGITAL PERSONAL DATA PROTECTION BILL, 2023Tabled at LokSabha on August 03. 2023Personal data may be processed only for a lawful purpose for which an individual has given consent. Consent may be deemed in certain cases.The 2023 bill imposes reasonable obligations on data fiduciaries and data processors to safeguard digital personal data.There is a Data Protection Board under the 2022 bill to deal with the non-compliance of the Act.Under the 2023 bill, there is the Establishment of a new Data Protection Board which will ensure compliance, remedies and penalties.
Under the new bill, the Board has been entrusted with the power of a civil court, such as the power to take cognisance in response to personal data breaches, investigate complaints, imposing penalties. Additionally, the Board can issue directions to ensure compliance with the act.The 2022 Bill grants certain rights to individuals, such as the right to obtain information, seek correction and erasure, and grievance redressal.The 2023 bill also grants More Rights to Individuals and establishes a balance between user protection and growing innovations. The bill creates a transparent and accountable data governance framework by giving more rights to individuals. In the 2023 bill, there is an Incorporation of Business-friendly provisions by removing criminal penalties for non-compliance and facilitating international data transfers.
The new 2023 bill balances out fundamental privacy rights and puts reasonable limitations on those rights.Under the 2022 bill, Personal data can be processed for a lawful purpose for which an individual has given his consent. And there was a concept of deemed consent.The new data protection board will carefully examine the instance of non-compliance by imposing penalties on non-compiler.The bill does not provide any express clarity in regards to compensation to be granted to the Data Principal in case of a Data Breach.Under 2023 Deemed consent is there in its new form as ‘Legitimate Users’.The 2022 bill allowed the transfer of personal data to locations notified by the government.There is an introduction of the negative list, which restricts cross-data transfer.

Related Blogs
Executive Summary
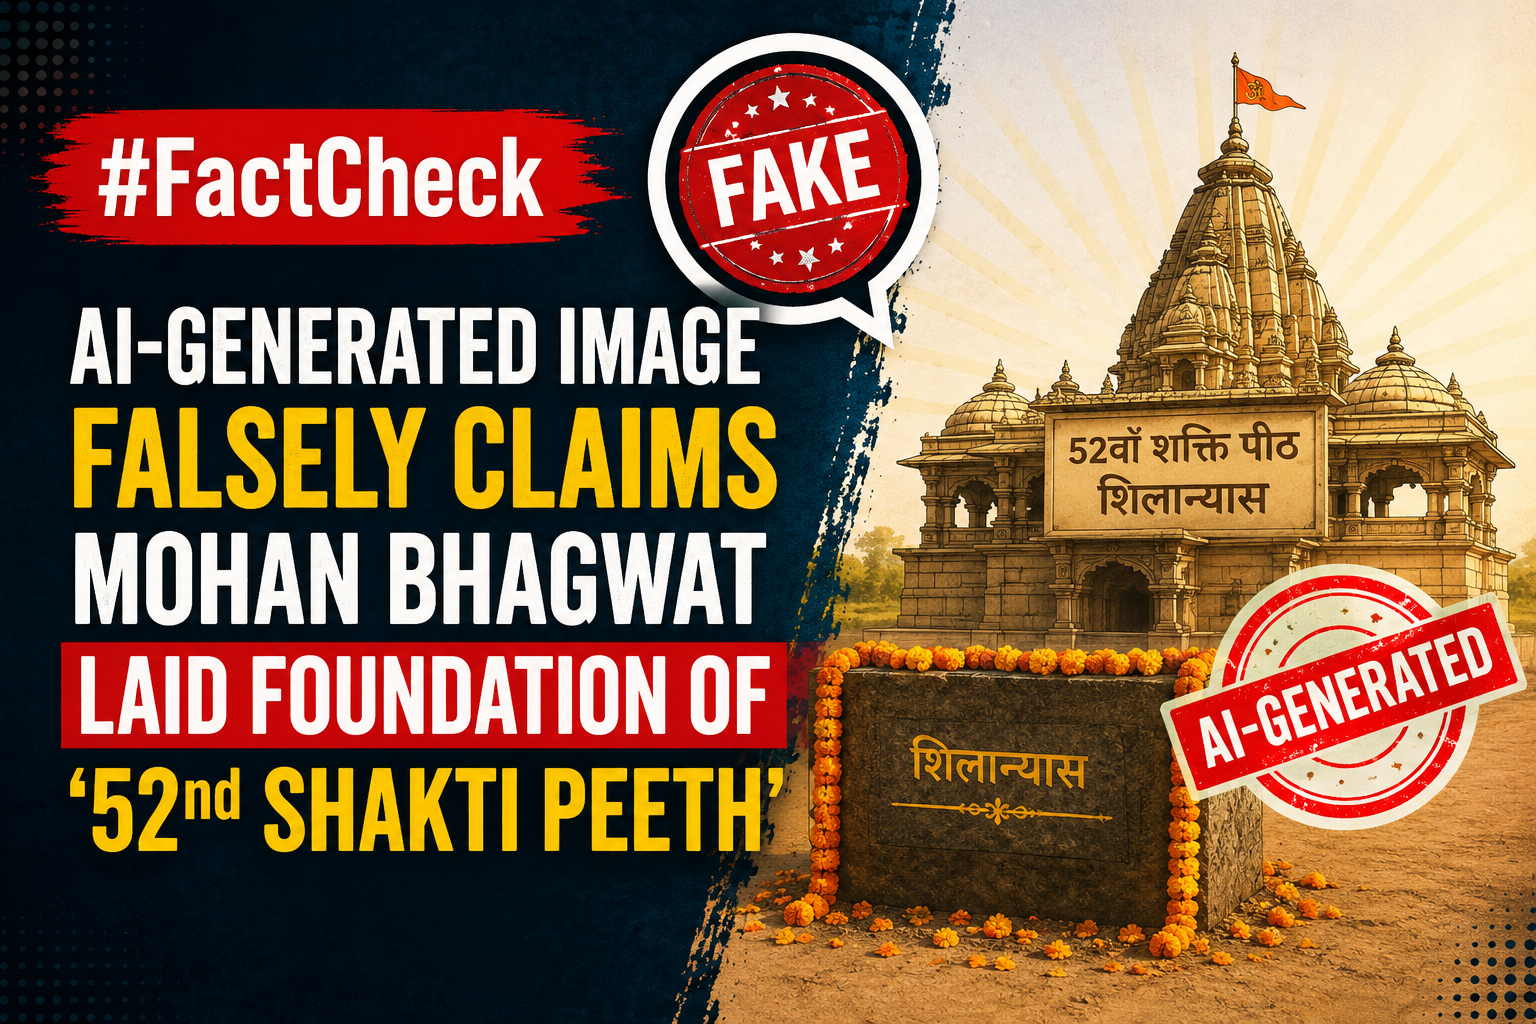
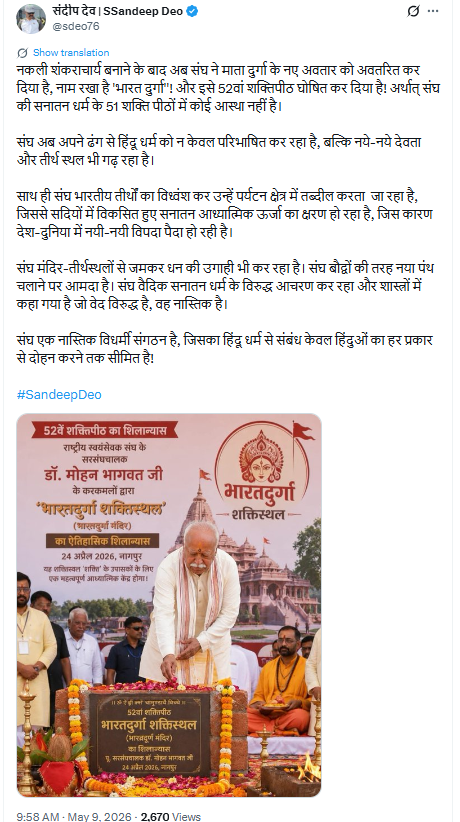
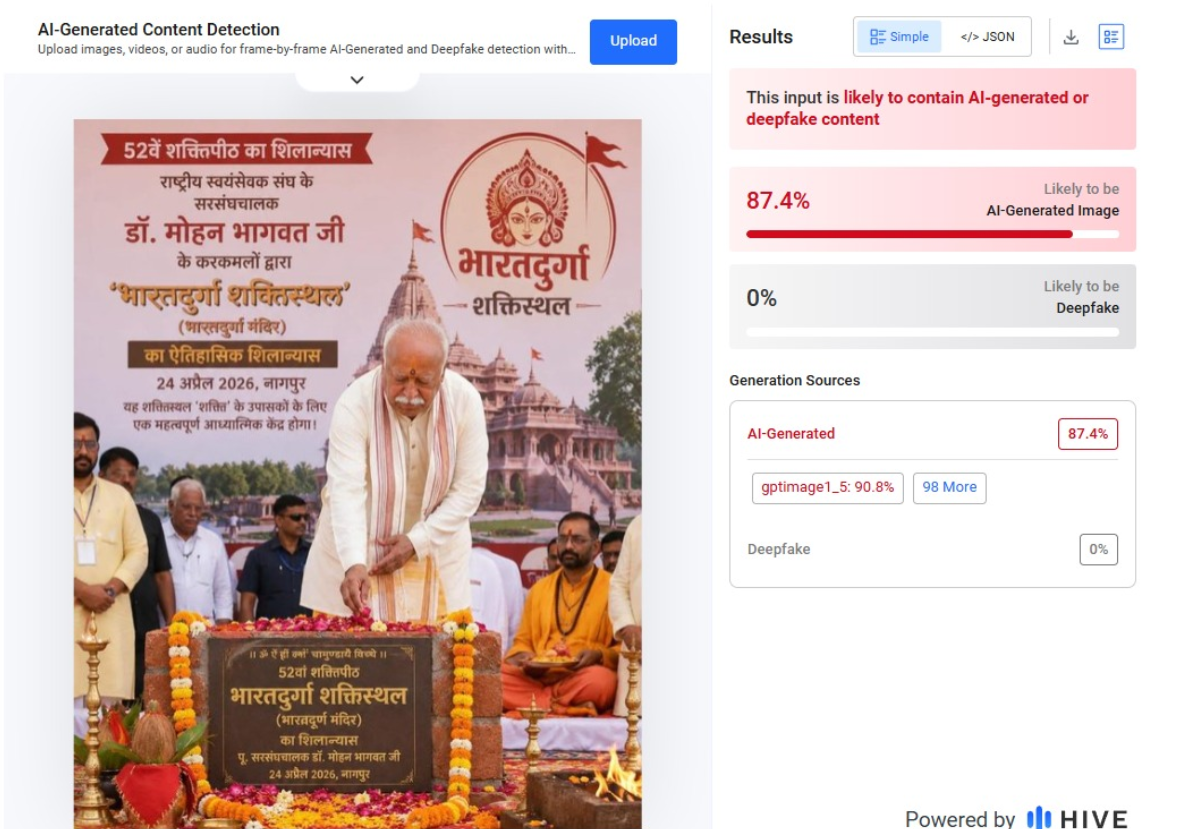
A picture of Mohan Bhagwat is going viral on social media, showing him allegedly laying the foundation stone of a so-called “52nd Shakti Peeth” named Bharatdurga. Users are claiming that the RSS chief insulted Sanatan Dharma by creating a new Shakti Peeth in Nagpur. Research by CyberPeace Research Wing found that the claim is false. The viral image is AI-generated, and Mohan Bhagwat did not inaugurate any “52nd Shakti Peeth.” In reality, he laid the foundation stone of the Bharatdurga Temple.
Claim
An X user named Sandeep Dev shared the viral image and alleged that after creating “fake Shankaracharyas,” the RSS had now introduced a new form of Goddess Durga called “Bharat Durga” and declared it the 52nd Shakti Peeth. The post further claimed that the RSS was redefining Hinduism and creating new religious sites.
Fact Check
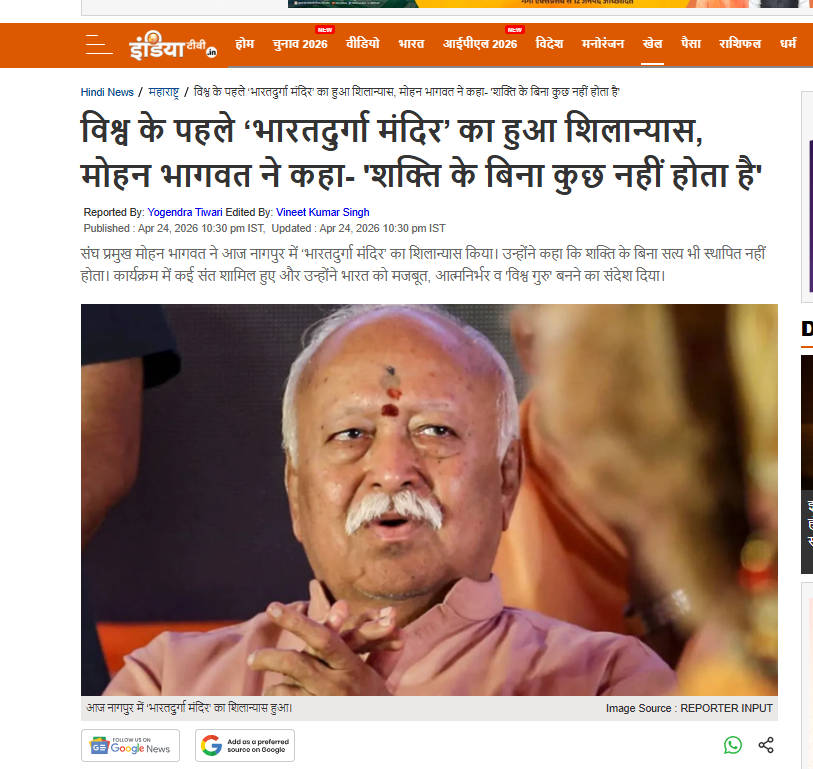
To verify the claim, we searched relevant keywords and found reports published on April 24, 2026, by India TV and Navbharat Times. According to these reports, Mohan Bhagwat laid the foundation stone of the world’s first Bharatdurga Temple in Nagpur during a ceremony organized at the Jamtha campus of Dr. Abaji Thatte Seva and Research Institute. Several prominent saints and religious leaders attended the event. Importantly, none of the reports described the temple as the “52nd Shakti Peeth.”
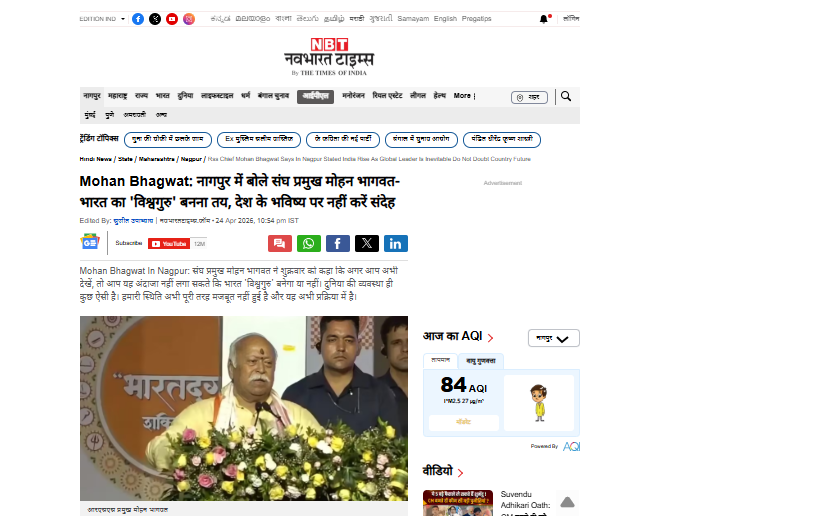
Further research led us to the full video of the foundation ceremony uploaded on the YouTube channel of Devendra Fadnavis. The stage backdrop and video thumbnail clearly mention “Bharatdurga Temple Foundation Ceremony.” However, the viral image frame was not visible anywhere in the authentic footage.

We also analyzed the viral image using AI detection tools, which indicated that the image was AI-generated.
Conclusion
Our research confirms that the claim about Mohan Bhagwat laying the foundation of a “52nd Shakti Peeth” is false. The viral image is AI-generated. In reality, he participated in the foundation ceremony of the Bharatdurga Temple in Nagpur.
Introduction
How Generative Artificial Intelligence, or GenAI, is changing the employee workday is no longer limited to writing emails or debugging code, but now also includes analysing contracts, generating reports, and much more. The use of AI tools in everyday work has become commonplace, but the speed at which companies have adopted these technologies has created a new kind of risk. Unlike threats that come from an outside attacker, Shadow AI is created inside an organisation by a legitimate employee who uses unapproved AI tools to make their work more efficient and productive. In many cases, the employee is unaware of the potential security, data privacy, and compliance risks involved in using such tools to perform their job duties.
What Is Shadow AI?
Shadow AI is when individuals use AI tools at work that aren’t provided by the company, like tools or other software programs, without the knowledge or permission of the employer. Examples of shadow AI include:
- Using personal ChatGPT or other chatbot accounts to complete tasks at the office
- Uploading business-related documents to online AI technologies for analysis or summarisation.
- Copying proprietary source code into an online AI model for debugging
- Installing browser extensions and add-ons that are not approved by IT or Security personnel.
How Shadow AI Is Harmful
1. Uncontrolled Data Exposure
When employees access or input information into their user-created AI, it becomes outside the controls of the company, such as both employee personal information and any third-party personal information, private company information (such as source code or contracts), and company internal strategies. After a user enters data into their user-created AIs, the company loses all ability to monitor how that data is stored, processed, or maintained. A data leak situation exists without a malicious cyberattack. The biggest risk of a data leak is not maliciousness but rather the loss of control and governance over sensitive data.
2. Regulatory and Legal Non-Compliance
Data protection laws like GDPR, India’s Digital Personal Data Protection (DPDP) Act, HIPAA, and other relevant sectoral laws require businesses to process data in accordance with the law, to minimise the amount of data they use, and to be accountable for their actions. Shadow AI often results in the unlawful use of personal data due to a lack of a legal basis for the processing, unauthorised cross-border data transfers, and not having appropriate contractual protections in place with their AI service providers. Regulators do not see the convenience of employees as an excuse for not complying with the law, and therefore, the organisation is ultimately responsible for any violations that occur.
3. Loss of Intellectual Property
Employees frequently use AI tools to speed up tasks involving proprietary information—debugging code, reviewing contracts, or summarising internal research. When done using unapproved AI platforms, this can expose trade secrets and intellectual property, eroding competitive advantage and creating long-term business risk.
Real-Life Example: Samsung’s ChatGPT Data Leak
In 2023, a case study exemplifying the Shadow AI risk occurred when Samsung Electronics placed a temporary ban on employee access to ChatGPT and other AI tools after reports from engineers revealed they were using ChatGPT to create debugging processes for internal source code and to summarise meeting notes. Consequently, confidential source code related to semiconductors was inadvertently uploaded onto a public AI platform. While there were no known incursions into the company’s system due to this incident, Samsung faced a significant challenge: once sensitive information is input into a public AI tool, it exists on external servers that are outside of the company’s purview or control.
As a result of this incident, Samsung restricted employee use of ChatGPT on corporate devices, issued a series of internal communications prohibiting the sharing of corporate data with public AI tools, and increased the urgency of their discussions regarding the adoption of secure, enterprise-level AI (artificial intelligence) solutions.
What Organisations Are Doing Today
Many organisations respond to Shadow AI risk by:
- Blocking access at the network level
- Circulating warning emails or policies
While these actions may reduce immediate exposure, they fail to address the root cause: employees still need AI to perform their jobs efficiently. As a result, bans often push AI usage underground, increasing Shadow AI rather than eliminating it.
Why Blocking AI Does Not Work—Governance Does
History has demonstrated that prohibition does not work - we see this when trying to block access to cloud storage, instant messaging and collaboration tools. Employees are forced to use personal devices and/or accounts when their employers block AI, which means employers do not have real-time visibility into how their employees are using these technologies, and creates friction with the security and compliance team as they try to enforce the types of tools their employees can use. Prohibiting AI adoption will not stop it from being adopted; it will just create a challenge for employers regarding how safe and responsible it is. The challenge for effective organisations is therefore to shift from denial and develop governance-first AI strategies aimed at controlling data usage, protection and security, rather than merely restricting access to a list of specific tools.
Shadow AI: A Silent Legal Liability Under the GDPR
Shadow AI isn't a problem for the Information Technology Department; it is a failure of Governance, Compliance and Law. By using AI tools that have not been approved as a result, the organisation processes personal data without a lawful basis (Article 6 of the General Data Protection Regulation (GDPR)), repurposes data for use beyond its original intent and in breach of the Purpose Limitation (Article 5(1)(b)), and routinely exceeds necessity and in breach of Data Minimisation (Article 5(1)(c)). The outcome of these actions is the use of tools that involve International Data Transfers Without Authorisation and are therefore in breach of Chapter V, and violate Article 32 because there are no enforceable safeguards in place. Most significantly, the failure to demonstrate Oversight, Logging and Control under Articles 5(2) and 24 constitutes a failure in Accountability. Therefore, from a Regulatory perspective, Shadow AI is not accidental and is not defensible.
The Right Solution: Secure and Governed AI Adoption
1. Provide Approved AI Tools
Employers have an obligation to supply business-approved AI technology for helping workers to be productive while maintaining maximum protections, like storing data separately and not using employees' data for training a model; defining how long data is kept, and the rules around deleting that data. When employees are provided with verified and secure AI options that align with their work processes, they will rely significantly less on Shadow AI.
2. Enforce Zero-Trust Data Access
The governance of AI systems must follow the principles of "zero trust," granting access to data only through the principle of "least privilege," which means that data access will only be allowed by the system user, and providing continuous verification of user-identity and context; this supports and helps establish context-aware controls to monitor and track all user activities, which will be especially important as agent-like AI systems become increasingly autonomous and are capable of operating at machine-speed where even small errors in configuration, will result in rapid and large expose to data.
3. Apply DLP and Audit Logging
It is important to have robust data loss prevention measures in place to protect sensitive data that is sent outside an organisation. The first end user or machine that accesses the data should be detailed in a comprehensive audit log that indicates when and how the data is accessed. In combination with other controls, these measures create accountability, comply with regulations, and assist with appropriately detecting and responding to incidents.
4. Maintain Visibility Across AI, Cloud, and SaaS
Security teams need unified visibility across AI tools, personal cloud applications, and SaaS platforms. Risks move across systems, and controls must follow the data wherever it flows.
Conclusion
This new threat exposes an organisation to the risk of data loss through leaks, regulatory fines, liability for the loss of intellectual property, and reputational damage, all of which can occur without any intent to cause harm. The way forward is not to block AI, but to adopt a clear framework built on governance, visibility, and secure enablement. This approach allows organisations to use AI with confidence, while ensuring trust, accountability, and effective oversight to protect data and support AI in reaching its full transformative potential. AI use is encouraged, but it must be done responsibly, ethically, and securely.
References
- https://bronson.ai/resources/shadow-ai/
- https://www.varonis.com/blog/shadow-ai
- https://www.waymakeros.com/learn/gdpr-hipaa-shadow-ai-compliance-nightmare
- https://www.forbes.com/sites/siladityaray/2023/05/02/samsung-bans-chatgpt-and-other-chatbots-for-employees-after-sensitive-code-leak/
- https://www.usatoday.com/story/special/contributor-content/2025/05/23/shadow-ai-the-hidden-risk-in-todays-workplace/83822081007
Executive Summary
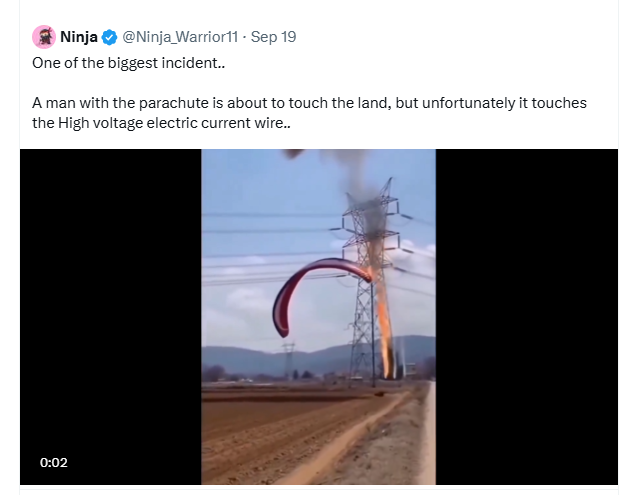
A video is being shared on social media claiming that a person who was paragliding came into contact with high-voltage electric wires during a recent incident. The video shows a paraglider coming into contact with electric wires while descending towards the ground, following which a fire can be seen breaking out. Social media users are sharing the post claiming that the incident is recent and linking it to the ongoing developments. CyberPeace Research found the viral claim to be misleading. Our research found that the viral video is not recent but dates back to a paragliding accident that took place in South Korea in June 2023. According to available media reports, on June 16, 2023, a 60-year-old man who was paragliding near Seopjikoji Beach on Jeju Island, South Korea, came into contact with high-voltage electric wires. He died in the accident.
Claim:
A video being shared on social media claims that a person descending towards the ground with a parachute unfortunately came into contact with high-voltage electric wires. The video shows the area around the person catching fire after he came into contact with the electric wires. The post is being shared on social media claiming that the incident is recent.
https://x.com/i/birdwatch/t/2101315570067189899?source=6
Fact Check
To verify the viral claim, we conducted a Google search using relevant keywords. During the search, we did not find any credible media reports related to the claim. To further verify the authenticity of the viral claim, we conducted another search on Google using relevant keywords. During the search, we found a similar video on a YouTube channel. This made it clear that the video is not recent. As part of our research, we also found the video on the South Korean website Bobaedream. According to the website, on June 16, 2023, a tourist aged around 60 came into contact with a high-voltage electric wire while paragliding near Seopjikoji Beach in Seongsan-eup, Seogwipo-si, Jeju-do Province, South Korea.
https://www.bobaedream.co.kr/bike2/board/view.php?code=strange&No=5785730
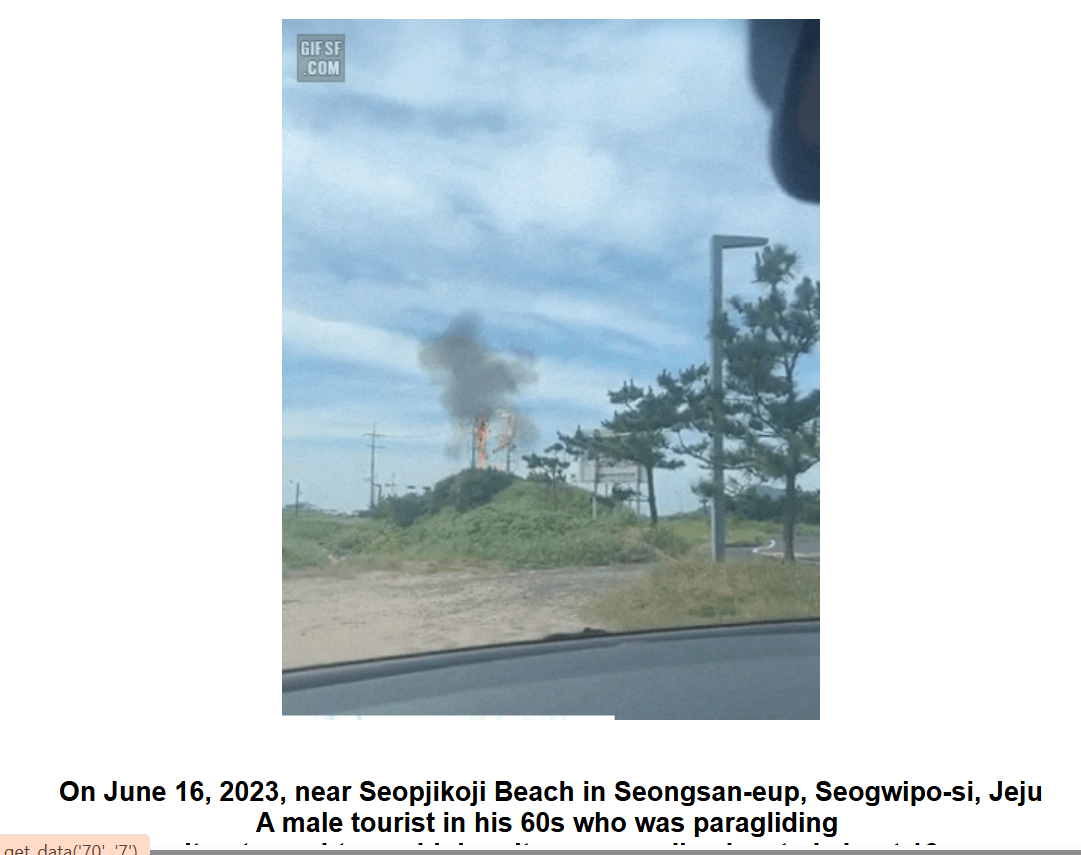
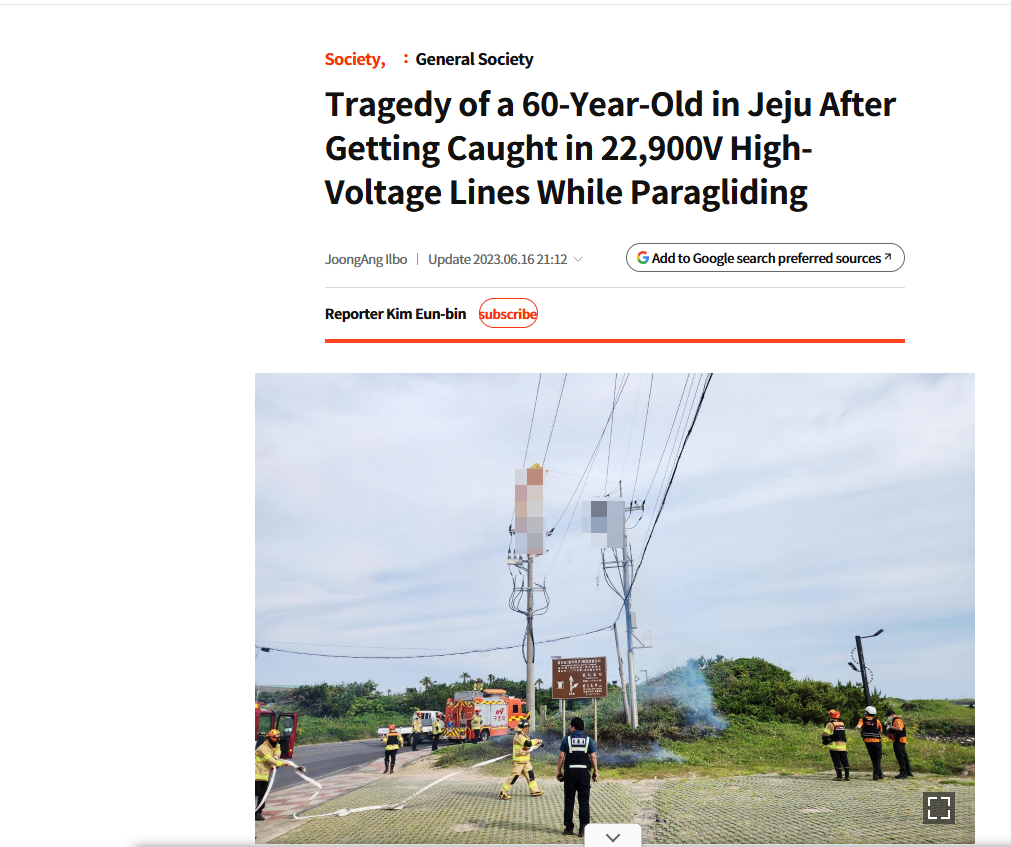
At the end of our research, we found a report published by South Korean news outlet The JoongAng on June 16, 2023. Citing the Jeju Eastern Fire Department, the report stated that at around 4:35 p.m. that day, a person flying a motorized paraglider near Seopjikoji Beach was reported to have become entangled in a high-voltage electric wire. According to the report, the person died after coming into contact with the high-voltage current.
https://www.joongang.co.kr/article/25170445#home
Conclusion
Our research found that the video being shared on social media does not show a recent incident. Available media reports and other sources confirm that the video is from a paragliding accident that took place on Jeju Island, South Korea, in June 2023. According to reports, on June 16, 2023, a man aged around 60 who was paragliding near Seopjikoji Beach became entangled in a high-voltage electric wire. He died after coming into contact with the electric current. Therefore, the claim that the video shows a recent incident is misleading.
