
#FactCheck: Fake video falsely claims FM Sitharaman endorsed investment scheme
Executive Summary:
A video gone viral on Facebook claims Union Finance Minister Nirmala Sitharaman endorsed the government’s new investment project. The video has been widely shared. However, our research indicates that the video has been AI altered and is being used to spread misinformation.

Claim:
The claim in this video suggests that Finance Minister Nirmala Sitharaman is endorsing an automotive system that promises daily earnings of ₹15,00,000 with an initial investment of ₹21,000.
Fact Check:
To check the genuineness of the claim, we used the keyword search for “Nirmala Sitharaman investment program” but we haven’t found any investment related scheme. We observed that the lip movements appeared unnatural and did not align perfectly with the speech, leading us to suspect that the video may have been AI-manipulated.
When we reverse searched the video which led us to this DD News live-stream of Sitharaman’s press conference after presenting the Union Budget on February 1, 2025. Sitharaman never mentioned any investment or trading platform during the press conference, showing that the viral video was digitally altered. Technical analysis using Hive moderator further found that the viral clip is Manipulated by voice cloning.

Conclusion:
The viral video on social media shows Union Finance Minister Nirmala Sitharaman endorsing the government’s new investment project as completely voice cloned, manipulated and false. This highlights the risk of online manipulation, making it crucial to verify news with credible sources before sharing it. With the growing risk of AI-generated misinformation, promoting media literacy is essential in the fight against false information.
- Claim: Fake video falsely claims FM Nirmala Sitharaman endorsed an investment scheme.
- Claimed On: Social Media
- Fact Check: False and Misleading

Related Blogs
Introduction
On June 11, 2026, the Ministry of Home Affairs (MHA) India released one of the most critical Indian government advisories concerning cybersecurity by the Indian Cyber Crime Coordination Centre (I4C) under the National Cybercrime Threat Analytics Unit (NCTAU) concerning the immediate and escalating threat posed by the weaponization of generative artificial intelligence to forge synthetic biometric identities capable of bypassing the existing facial verification mechanisms in India. This advisory is arguably one of the most explicit Indian government recognitions of the deep-seated threats associated with AI-generated deepfakes in the country’s digital financial infrastructure. As many Indian financial service providers embrace facial recognition and biometric verification systems for customer onboarding and authentications, the myth that biometric traits are in themselves secure is slowly unraveling.
The advisory states that cybercriminals are deploying sophisticated AI tools to forge such credible digital simulacrums that exhibit such a precise similarity of facial expressions, eye movements, eye blinks, head movements, and voice patterns that they are virtually indistinguishable from the originals for identity verification mechanisms. Such a confluence of easy AI technology, mass onboarding of digital identities, and underdeveloped infrastructure to detect these synthetics requires urgent regulatory, institutional, and technological intervention.
The I4C Advisory: Core Findings and Threat Architecture
In its advisory, NCTAU describes a complex, multi-step attack chain used by scammers to capture biometric information and perpetrate fraud using everyday social interactions. The attackers typically use social media accounts, chat messengers, online job applications, dating applications, or direct phone calls to reach their targets. These interactions are presented as innocuous, such as for video calls, job interviews, identity checks, or just normal conversation with the intention of recording facial and vocal data.
During these interactions, victims may be asked to perform gestures commonly seen in legitimate video calls, such as look directly at the camera, blink, turn their head, or say specific phrases. However, the perpetrators record this video feed without the victim's knowledge and then use deep learning generative AI technologies to process it. Through methods such as Generative Adversarial Networks (GANs) and diffusion models, the scammers create photorealistic synthetic duplicates of the target, capable of mirroring all physical and vocal attributes, such as facial expressions, blinking patterns, head movements, and even voice tones.
The advisory explicitly states that these synthetic identities can be used for a variety of fraudulent activities, such as spoofing face authentication systems, circumventing liveness detection checks, successfully completing video KYC, enabling fraudulent account recovery processes, and illegally accessing bank and financial services. NCTAU also cautions that these voice deepfakes may be paired with facial deepfakes in an attempt to undermine multi-modal authentication methods, and the occurrence of related SIM-swap attacks can eliminate the last layer of security in OTP verification and facilitate a complete account compromise.
The scale of India's Digital Financial Ecosystem
The scale of I4C's detected threat can be better understood by considering India's entire digital financial landscape. In 2025 India has witnessed over 228 billion UPI transactions, with 21.63 billion in December alone, an annual growth rate of 29% from 2024, and an active user base of over 500 million by the beginning of 2026. Furthermore, total e-KYC transactions by April 2025 have exceeded 2,393 crore, and thus, it can be seen the extent to which these aspects of finance (banking, insurance, and credit) are now conducted via remote digital verification. The transformation, although instrumental in increasing financial inclusion, has, according to some analysts, created an attack surface of historic scale. As hundreds of millions more become financially integrated via the very same channels that now form the country's infrastructure and systems of identity, the threat from identity-based fraud becomes astronomically large.
Indian government data further illustrates the extent to which such frauds are a growing concern. Cybercrime cases jumped 42% year-on-year to 2.27 million in 2024, resulting in losses amounting to nearly 228.45 billion. Within that, 1.34 million UPI cases, worth 1,087 crore, occurred in FY2024 alone, while cybercrimes in general soared from 260,000 cases in 2021 to nearly 2.8 million by 2025, totaling cybercrime losses of 22,931 crore.
How Do Deepfakes Defeat Biometric Systems?
Deepfake fraud, in particular, is extremely difficult to counteract due to the direct attack it poses on the assumptions underlying traditional verification systems. Passive techniques for verifying a live person from a static photo or video existed that primarily looked for similarities in textures, lighting, and geometrical properties or challenged subjects to perform an action in real-time. But the generation of real-time face swapping that contains blinks, head motion, and speaking can now be produced on even cheap machines. Cybercriminals can exploit these by using virtual camera drivers to "inject" the false image feed into the live verification session, nullifying any passive liveness checks. Data from the industry clearly shows the extent of this problem: iProov, a leading authenticator, documented a 7.8-fold rise in injection attacks in 2024; Jumio noted an 88% increase in deepfake-induced fraud in 2025; and voice-deepfake attacks on financial call centres saw a 6.8-fold increase in 2024.
Gartner had also predicted that 30% of organizations would have lost trust in facial verification alone by 2026, and work by Kubam (2024) confirmed a lack of multi-factor authentication such as cross-validation of biometric, document, and device integrity signals used within KYC platforms. Such fears have been corroborated by FATF's 2025 Horizon Scan, which classified deepfakes as an emerging threat to the AML/CDD framework and digital identity verification.
Recommendations by I4C
I4C's advisory goes beyond merely warning about threats and lists actionable recommendations to both institutions and citizens. Banks, NBFCs, fintech companies, and onboarding platforms have been advised to incorporate advanced deepfake and synthetic content detection techniques into their verification flows, given that first-generation liveness checks are not enough. They should employ a multi-modal strategy that considers face features along with the device, network signals, behavioral biometrics, and alignment of face and voice. They also have been advised to make a more robust upgrade of their onboarding and verification platforms, as much of the current remote verification architecture was built in a less sophisticated threat context. This aligns with the KYC Master Direction of the RBI that specifies end-to-end encryption, IP-based access controls, geotagging, and technology platforms and systems are to be upgraded frequently. Citizens are advised by I4C to keep their biometric information secure; be careful of unsolicited video calls and online interviews; keep an eye on transaction-related SMS and emails; and report suspicious instances through the National Cybercrime Reporting Portal and through the telephone number 1930. It is clarified that this advisory aims to create awareness of developing AI-based identity fraud schemes, and it is not a declaration that any specific organization, platform, or service is vulnerable.
The Legislative Dimension: India's Evolving Response to Synthetic Media
The problem highlighted by I4C is evolving in a heavily legislated environment, not a legal void. The first-ever legal definition of "synthetic media" in India came into force in the Information Technology Amendment Rules 2026 on February 20, 2026. These rules oblige significant platforms to remove deepfakes and non-consensual intimate media within three hours and two hours, respectively, or lose their safe harbor protection under Section 79 of the IT Act. While the provision focuses on harm stemming from content, this creates a new legal and normative precedent on dealing with AI-induced deception. However, financial frauds facilitated through deepfakes are not content but involve the use of remote identity verification and customer onboarding systems, which require specific technical standards. The overall policy environment when viewed in light of the FATF Horizon Scan, RBI KYC rules, and recent I4C advisory already offers significant scope to define and introduce mandatory deepfake detection and identity assurance standards even before these are explicitly legislated.
Institutional and Technical Recommendations
- For Financial Institutions and Fintech platforms: The existing verification systems (liveness detection) must be replaced with multi-layered deep-fake detection processes, including injection attack detection, behavioral biometrics, cross-modal facial and voice verification, device integrity check, and hardware attestation during onboarding itself.
- For Regulators: The RBI and Ministry of Home Affairs should work together to release technical standards that specify minimum deepfake-detection requirements for video-KYC and remote onboarding systems in line with FATF digital identity guidance and the upcoming EU AI Act.
- For researchers and academia: Dedicated studies on deepfake detection performance across varied demographic, linguistic, and regional populations of India should be prioritized. Current models are mostly trained on Western data.
- For citizens: Face recordings and other biometric information should be treated with the same caution as sensitive financial details. Be wary of unsolicited video calls, remote interviews, or verification requests from unknown people, and report suspicious activities on any account immediately via the National Cybercrime Helpline (1930) or cybercrime.gov.in.
Conclusion
The I4C advisory of June 2026 marks a critical recognition that advances in generative AI have fundamentally challenged the reliability of facial biometric authentication. For a country whose digital financial ecosystem relies heavily on remote identity verification, the implications are significant. The integrity of India's financial inclusion framework now depends on rapidly strengthening identity assurance mechanisms. Addressing this threat will require coordinated action by regulators, financial institutions, technology developers, researchers, and citizens to develop robust technical standards, enhance detection capabilities, and build public awareness at a pace matching the evolution of AI-enabled fraud.
References and Sources
- I4C / NCTAU Advisory, June 2026 — National Cybercrime Threat Analytics Unit, Indian Cyber Crime Coordination Centre, Ministry of Home Affairs, Government of India. Advisory on AI-Enabled Deepfake Identity Fraud. Issued 11 June 2026.
- shuftipro.com/blog/key-takeaways-from-fatf-horizon-scan-report-on-deepfakes
- https://timesofindia.indiatimes.com/india/fraudsters-creating-deepfakes-to-bypass-facial-authentication-i4c/articleshow/131668958.cms
- hyperverge.co/blog/what-is-a-deepfake
- iproov.com/reports/threat-intelligence-report-2026
- arxiv.org/pdf/2601.06241
Executive Summary
A video showing flames and thick smoke rising over a densely populated city at night is being widely circulated on social media. The video is being shared with the claim that it shows the actual visuals of explosions and destruction caused by an attack on Iran. CyberPeace Research Wing ’s research found the viral claim to be false. Our research revealed that the video is not real footage but an AI-generated video, which is being circulated with a false claim.
Claim
A user on social media platform Instagram shared the viral video on July 17, 2026, claiming that it shows the real visuals of an attack on Iran and the massive explosions caused by it.
https://www.instagram.com/reel/Da1_gaXyyoP/?utm_source=ig_web_copy_link&igsh=NTc4MTIwNjQ2YQ==

Fact Check
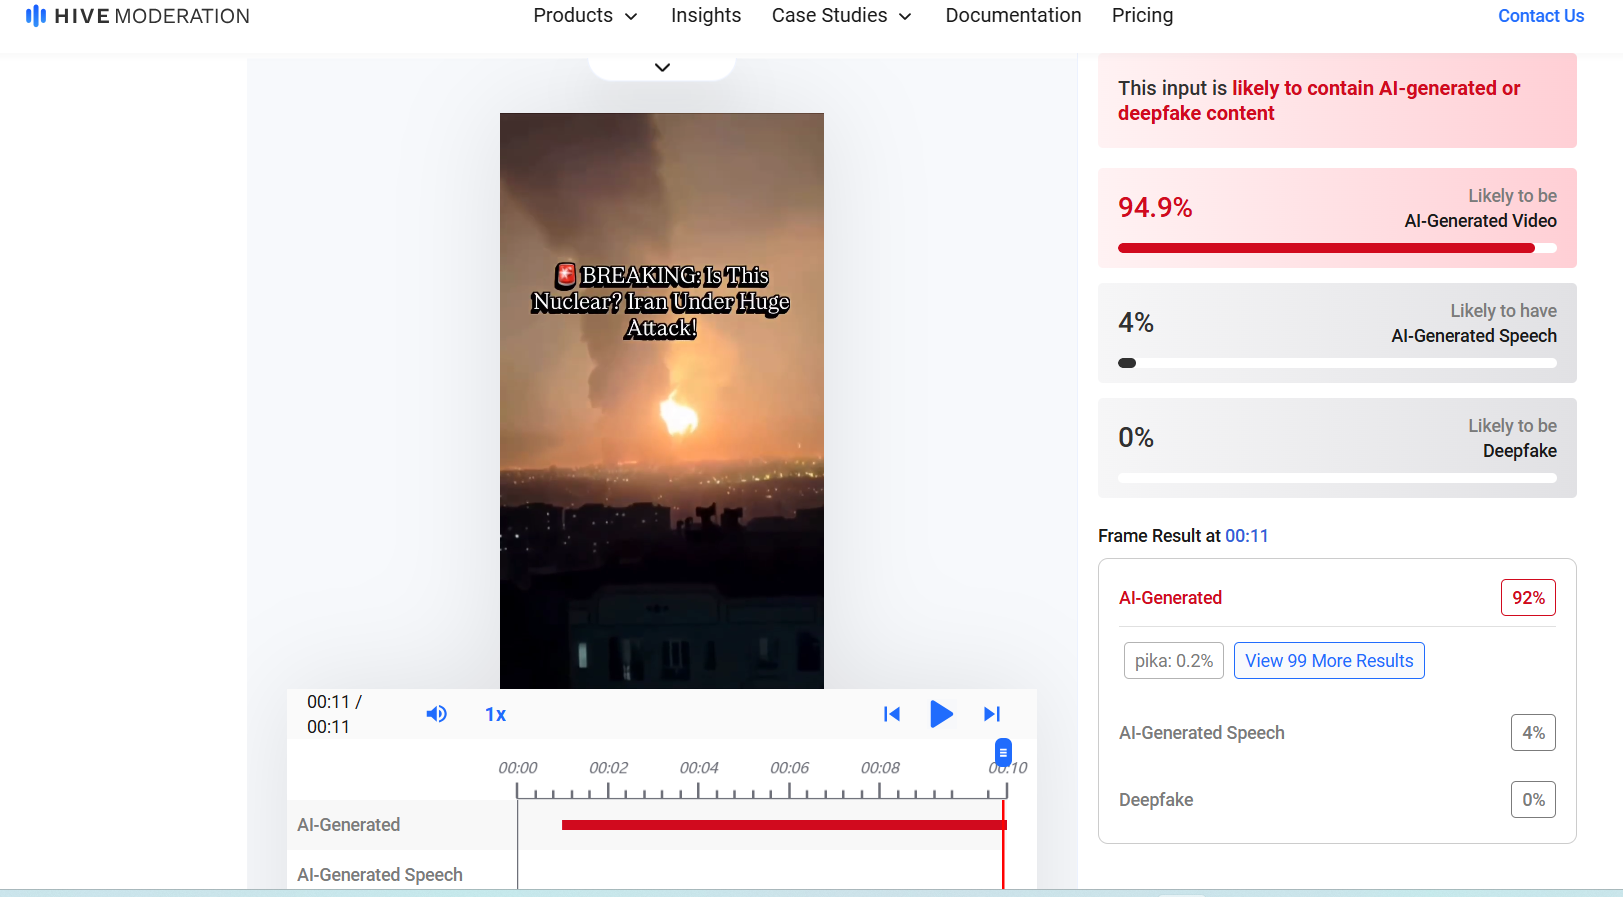
To verify the authenticity of the viral claim, we extracted multiple keyframes from the video and conducted a reverse image search using Google Lens. During the research, we did not find any credible news report, verified video, or authentic source confirming that the footage was related to any attack on Iran. To further examine the authenticity of the video, we analysed it using multiple AI detection tools. First, we scanned the video using Hive Moderation. The tool’s analysis indicated that the video had a 94.9% probability of being AI-generated, suggesting that the footage may have been created using Artificial Intelligence.
For additional verification, we analysed the video using DetectVideo AI. The tool also indicated that the video was likely AI-generated, with an estimated 80% probability.

We further checked the video using another AI detection tool, AI or Not, which suggested that the footage had a 64% probability of being AI-generated.

At the final stage of verification, we used WasIt.AI, which also indicated that the video was likely AI-generated, with an 88% probability.

Conclusion
CyberPeace Research Wing ’s research found that the viral video does not show real footage of an attack on Iran.The video was created using Artificial Intelligence (AI) and is being falsely shared as authentic visuals of explosions and destruction caused by an attack on Iran. Users are advised to verify such sensational claims before sharing them online.
Executive Summary
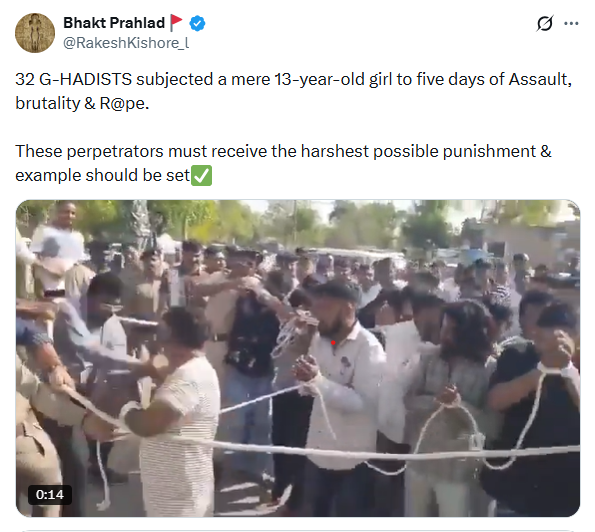
Amid nationwide outrage over the gang-rape of a 13-year-old minor in Sriganganagar, Rajasthan, a video is circulating on social media. The clip shows police officers tying the hands of several accused individuals and parading them publicly on the streets. Users sharing the video claim that these are the culprits from the Sriganganagar case being beaten by the police.
A fact-check by the CyberPeace Research Wing found this claim to be misleading. The viral video has no connection to the Rajasthan incident; it actually depicts a separate event from Patan, Gujarat, dating back to March 2026.
The Claim
On July 7, 2026, a user on X (formerly Twitter) shared the video with the caption: "32 jihadis assaulted, brutalized, and raped a 13-year-old girl for five days. These criminals must get the harshest punishment to set an example."
https://x.com/RakeshKishore_l/status/2074400280352084129
Fact Check
To verify the viral claim, keyframes from the video were extracted and analysed using Google Lens for reverse image search. During the research, we found a report published by NDTV on March 19, 2026, which carried visuals matching the viral video. The report link and screenshot are provided below:
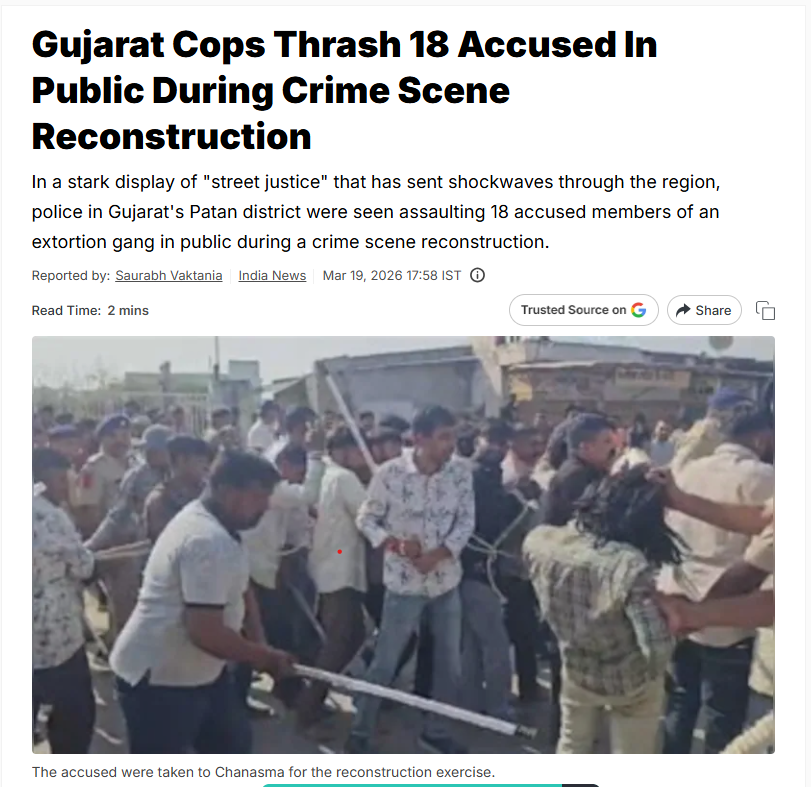
According to the NDTV report, a video showing police personnel publicly assaulting 18 alleged accused persons in Gujarat’s Patan district had surfaced. The incident was reported to have taken place during a crime scene reconstruction exercise.
The report stated that the accused, allegedly linked to an extortion gang, were taken to Chanasma for the reconstruction process. During the exercise, police personnel were seen assaulting them. Witnesses claimed that the accused were paraded through areas where they had allegedly created fear among locals.
The accused were reportedly linked to the alleged Jhiliya gang. The incident occurred days after a violent clash in which members of the same group allegedly attacked a police team, forcing officers to retreat from the spot.
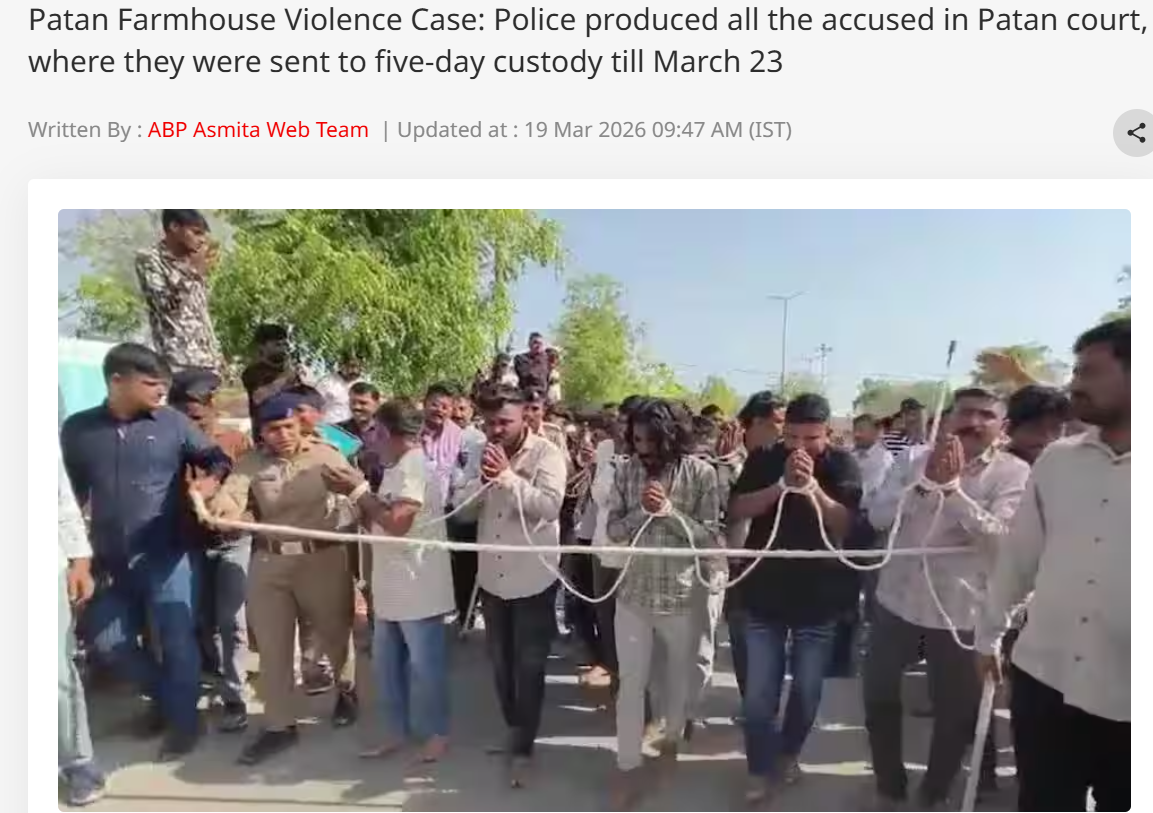
During further research, we found a report published by ABP Asmita on March 19, 2026. According to the report, the incident was linked to an old dispute over temple donations.
The report stated that the accused were produced before a court, which sent them to five days of police custody until March 23, 2026. The report link and screenshot are provided below:
Conclusion
The research found that the viral video is not related to the alleged gang rape case in Sri Ganganagar, Rajasthan. The video is being shared with a false context. The footage actually belongs to a separate incident from Gujarat’s Patan district reported in March 2026.
