
Domestic UPI Frauds: Finance Ministry Presented Data in LokSabha
Introduction
According to the Finance Ministry's data, the incidence of domestic Unified Payment Interface (UPI) fraud rose by 85% in FY 2023-24 compared to FY 2022-23. Further, as of September of FY 2024-25, 6.32 lakh fraud cases had been already reported, amounting to Rs 485 crore. The data was shared on 25th November 2024, by the Finance Ministry in response to a question in Lok Sabha’s winter session about the fraud in UPI transactions during the past three fiscal years.
Statistics

UPI Frauds and Government's Countermeasures
On the query as to measures taken by the government for safe and secure UPI transactions and prevention of fraud in the transactions, the ministry has highlighted the measures as follows:
- The Reserve Bank of India (RBI) has launched the Central Payment Fraud Information Registry (CPFIR), a web-based tool for reporting payment-related frauds, operational since March 2020, and it requires requiring all Regulated Entities (RE) to report payment-related frauds to the said CPFIR.
- The Government, RBI, and National Payments Corporation of India (NPCI) have implemented various measures to prevent payment-related frauds, including UPI transaction frauds. These include device binding, two-factor authentication through PIN, daily transaction limits, and limits on use cases.
- Further, NPCI offers a fraud monitoring solution for banks, enabling them to alert and decline transactions using AI/ML models. RBI and banks are also promoting awareness through SMS, radio, and publicity on 'cyber-crime prevention'.
- The Ministry of Home Affairs has launched a National Cybercrime Reporting Portal (NCRP) (www.cybercrime.gov.in) and a National Cybercrime Helpline Number 1930 to help citizens report cyber incidents, including financial fraud. Customers can also report fraud on the official websites of their bank or bank branches.
- The Department of Telecommunications has introduced the Digital Intelligence Platform (DIP) and 'Chakshu' facility on the Sanchar Saathi portal, enabling citizens to report suspected fraud messages via call, SMS, or WhatsApp.
Conclusion
UPI is India's most popular digital payment method. As of June 2024, there are around 350 million active users of the UPI in India. The Indian Cyber Crime Coordination Centre (I4C) report indicates that ‘Online Financial Fraud’, a cyber crime category under NCRP, is the most prevalent among others. The rise of financial fraud, particularly UPI fraud is cause for alarm, the scammers use sophisticated strategies to deceive victims. It is high time for netizens to exercise caution and care with their personal and financial information, stay aware of common tactics used by fraudsters, and adhere to best security practices for secure transactions and the safe use of UPI services.
References

Related Blogs

Introduction
When a tragedy strikes, moments are fragile, people are vulnerable, emotions run high, and every second is important. In such critical situations, information becomes as crucial as food, water, shelter, and medication. As soon as any information is received, it often leads to stampedes and chaos. Alongside the tragedy, whether natural or man-made, emerges another threat: misinformation. People, desperate for answers, cling to whatever they can find.
Tragedies can take many forms. These may include natural disasters, mass accidents, terrorist activities, or other emergencies. During the 2023 earthquakes in Turkey, misinformation spread on social media claiming that the Yarseli Dam had cracked and was about to burst. People believed it and began migrating from the area. Panic followed, and search and rescue teams stopped operations in that zone. Precious hours were lost. Later, it was confirmed to be a rumour. By then, the damage was already done.
Similarly, after the recent plane crash in Ahmedabad, India, numerous rumours and WhatsApp messages spread rapidly. One message claimed to contain the investigation report on the crash of Air India flight AI-171. It was later called out by PIB and declared fake.
These examples show how misinformation can take control of already painful moments. During emergencies, when emotions are intense and fear is widespread, false information spreads faster and hits harder. Some people share it unknowingly, while others do so to gain attention or push a certain agenda. But for those already in distress, the effect is often the same. It brings ore confusion, heightens anxiety, and adds to their suffering.
Understanding Disasters and the Role of Media in Crisis
Disaster can be defined as a natural or human-caused situation that causes a transformation from a usual life of society into a crisis that is far beyond its existing response capacity. It can have minimal or maximum effects, from mere disruption in daily life practices to as adverse as inability to meet basic requirements of life like food, water and shelter. Hence, the disaster is not just a sudden event. It becomes a disaster when it overwhelms a community’s ability to cope with it.
To cope with such situations, there is an organised approach called Disaster Management. It includes preventive measures, minimising damages and helping communities recover. Earlier, public institutions like governments used to be the main actors in disaster management, but today, with every small entity having a role, academic institutions, media outlets and even ordinary people are involved.
Communication is an important element in disaster management. It saves lives when done correctly. People who are vulnerable need to know what’s happening, what they should do and where to seek help. It involves risk in today’s instantaneous communication.
Research shows that the media often fails to focus on disaster preparedness. For example, studies found that during the 2019 Istanbul earthquake, the media focused more on dramatic scenes than on educating people. Similar trends were seen during the 2023 Turkey earthquakes. Rather than helping people prepare or stay calm, much of the media coverage amplified fear and sensationalised suffering. This shows a shift from preventive, helpful reporting to reactive, emotional storytelling. In doing so, the media sometimes fails in its duty to support resilience and worse, can become a channel for spreading misinformation during already traumatic events. However, fighting misinformation is not just someone’s liability. It is penalised in the official disaster management strategy. Section 54 of the Disaster Management Act, 2005 mentions that "Whoever makes or circulates a false alarm or warning as to disaster or its severity or magnitude, leading to panic, shall, on conviction, be punishable with imprisonment which may extend to one year or with a fine."
AI as a Tool in Countering Misinformation
AI has emerged as a powerful mechanism to fight against misinformation. AI technologies like Natural Language Processing (NLP) and Machine Learning (ML) are effective in spotting and classifying misinformation with up to 97% accuracy. AI flags unverified content, leading to a 24% decrease in shares and 7% drop in likes on platforms like TikTok. Up to 95% fewer people view content on Facebook when fact-checking labels are used. Facebook AI also eliminates 86% of graphic violence, 96% of adult nudity, 98.5% of fake accounts and 99.5% of content related to terrorism. These tools help rebuild public trust in addition to limiting the dissemination of harmful content. In 2023, support for tech companies acting to combat misinformation rose to 65%, indicating a positive change in public expectations and awareness.
How to Counter Misinformation
Experts should step up in such situations. Social media has allowed many so-called experts to spread fake information without any real knowledge, research, or qualification. In such conditions, real experts such as authorities, doctors, scientists, public health officials, researchers, etc., need to take charge. They can directly address the myths and false claims and stop misinformation before it spreads further and reduce confusion.
Responsible journalism is crucial during crises. In times of panic, people look at the media for guidance. Hence, it is important to fact-check every detail before publishing. Reporting that is based on unclear tips, social media posts, or rumours can cause major harm by inciting mistrust, fear, or even dangerous behaviour. Cross-checking information, depending on reliable sources and promptly fixing errors are all components of responsible journalism. Protecting the public is more important than merely disseminating the news.
Focus on accuracy rather than speed. News spreads in a blink in today's world. Media outlets and influencers often come under pressure to publish it first. But in tragic situations like natural disasters and disease outbreaks, rushing to come first is not as important as accuracy is, as a single piece of misinformation can spark mass-scale panic and can slow down emergency efforts and lead people to make rash decisions. Taking a little more time to check the facts ensures that the information being shared is helpful, not harmful. Accuracy may save numerous lives during tragedies.
Misinformation spreads quickly it can only be prevented if people learn to critically evaluate what they hear and see. This entails being able to spot biased or deceptive headlines, cross-check claims and identify reliable sources. Digital literacy is of utmost importance; it makes people less susceptible to fear-based rumours, conspiracy theories and hoaxes.
Disaster preparedness programs should include awareness about the risks of spreading unverified information. Communities, schools and media platforms must educate people on how to respond responsibly during emergencies by staying calm, checking facts and sharing only credible updates. Spreading fake alerts or panic-inducing messages during a crisis is not only dangerous, but it can also have legal consequences. Public communication must focus on promoting trust, calm and clarity. When people understand the weight their words can carry during a crisis, they become part of the solution, not the problem.
References:
- https://dergipark.org.tr/en/download/article-file/3556152
- https://www.dhs.gov/sites/default/files/publications/SMWG_Countering-False-Info-Social-Media-Disasters-Emergencies_Mar2018-508.pdf
- https://english.mathrubhumi.com/news/india/fake-whatsapp-message-air-india-crash-pib-fact-check-fcwmvuyc
- https://www.dhs.gov/sites/default/files/publications/SMWG_Countering-False-Info-Social-Media-Disasters-Emergencies_Mar2018-508.pdf
Executive Summary
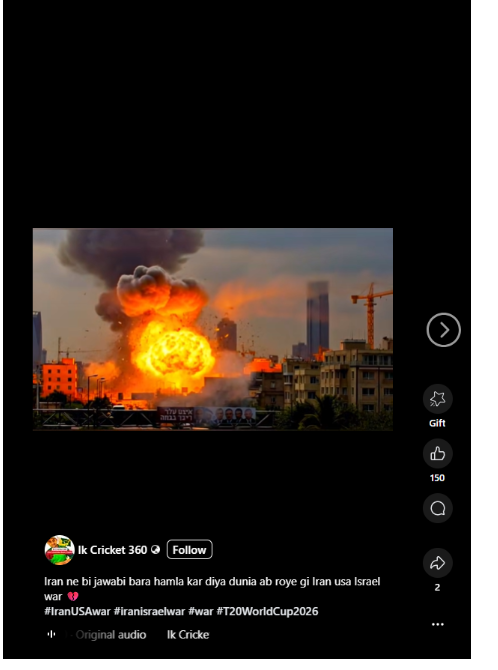
A video is being widely shared on social media linking it to the ongoing tensions between Israel and Iran. The clip shows multiple fighter jets flying across the sky, while massive flames appear to be rising from tall buildings below. The visuals are dramatic and alarming, creating the impression of a large-scale military strike. Users sharing the video claim that after Israel carried out an attack, Iran launched a retaliatory strike on Israel, and that the viral footage captures the aftermath of this counterattack. However, research conducted by the CyberPeace found the claim to be misleading. Our research revealed that the viral video is not authentic but AI-generated.
Claim
On the social media platform Facebook, a user shared the viral video with the caption: “Iran has also carried out a retaliatory attack on Israel.”
(Post link and archive link provided above.)
Factcheck
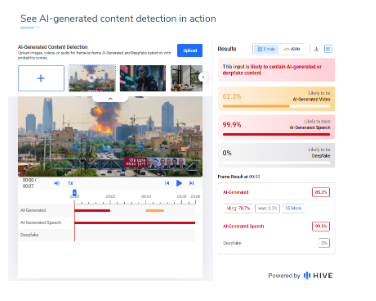
Upon closely examining the video, we noticed several irregularities in the visuals and motion patterns, which raised suspicion that the footage may have been generated using artificial intelligence. To verify this, we analyzed the video using the AI detection tool developed by Hive Moderation. According to the analysis report, there is a 62 percent likelihood that the viral video is AI-generated.
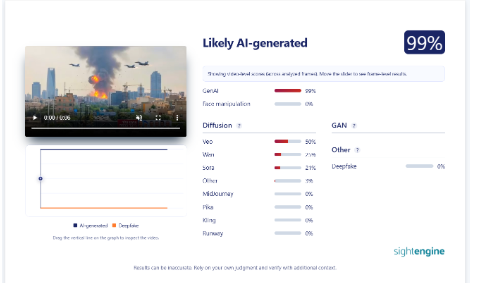
As part of further verification, we also scanned the video using Sightengine. The results indicated an even stronger probability, suggesting that the video is 99 percent AI-generated.
Conclusion
Our research confirms that the viral video does not depict a real military attack. It is AI-generated content being falsely shared in the context of Israel-Iran tensions.
Introduction
On 14 October 2026, ANI reported that the Sashastra Seema Bal (SSB), the force responsible for guarding India’s borders with Nepal and Bhutan, had directed its personnel not to fall for online honey traps, open suspicious APK files, or become victims of cyber scams. The warning was issued a day after the force’s annual cybersecurity awareness week and is relevant to every smartphone user in India. The three threats highlighted in the advisory, emotional exploitation, malware disguised as APK files, and financial scams, are often interconnected in a cyberattack chain that can compromise a person’s device or finances. This blog examines the advisory, the methods used by cybercriminals, and the everyday precautions users can take to stay safe.
What the Advisory Says
As per the ANI report, the SSB has cautioned its personnel about talking to strangers on the internet, where they have been instructed not to share photos or videos with anyone in the public eye, accept suspicious calls or video calls, or entertain requests for money, and not to install APKs or applications from any untrusted sources or websites, only use an authorised Android market to install applications, not to share your OTP, PIN, password, or banking details, and to be cautious while receiving an unknown call, suspicious SMS, or click on unknown links and scan QR codes. Personnel have been told not to tell something that does not seem right, and any fraud should be reported through cybercrime helpline number 1930 or cybercrime.gov.in. "Always verify before any transaction" & "Stop, think, check, then act." The SSB caution has been read.
How Online Honey Traps Operate
A honey trap, by definition, is a trap set through the manipulation of a fictitious romantic or social identity designed to gain trust, which is then used against it. There are certain elements that almost always constitute the honey trap.
- Contact: A fake profile, typically an attractive picture, reaches out to the targeted person on social media or a messaging platform.
- Rapport: Created via a mix of small talk, flattery, and "shares" or "interests."
- Escalation: The chatting advances to private messaging, involving sharing of photos or video.
- Extortion: The victim is subsequently threatened with blackmail through recordings, forced to make payments, or extorted for personal information.
This is not an isolated case. Earlier, the Delhi Police had revealed that fake Facebook female profiles were used to lure and befriend defence personnel and extract confidential information (The Quint). Even more recently, a case was reported of an IAF wing commander being lured on social media while undergoing troubled times and, thereafter, made to reveal sensitive defence-related information (Outlook India). While the matter is sub judice, it draws our attention towards an important point of analytical significance – most probably it is emotional trauma, which an attacker would rely upon, rather than technical and security flaws.
The Risk of Malicious APK Files
APK – Android Package Kit, is the package file format used by the Android operating system for the distribution and installation of mobile applications. Downloaded from Play Store, the application goes through a rigorous screening. However, those downloaded from WhatsApp, Telegram or SMS have not been screened. This is the modus operandi of the cybercriminals. They hide malware behind seemingly harmless files like a challan, a gas bill update, a KYC or a wedding invite. Proof from Moneylife pointing to an alert issued by CERT-In as well as file names like RTO Challan.apk and Gas Bill Update.apk establishes that government departments would not send an APK file over any messaging platform.
According to the CERT-In research of India's cybersecurity agency, the way this malware works: The malware Drinik posed as a download application from the Income Tax Department and asked for a long list of admin permissions, including SMS, call history, and contacts. It then presented a fake banking app to steal credentials, as Madhyamam reports. The Tribune reported that the SOVA trojan was hidden in fake apps with famous brands' logos. The report also states that the Black Rock malware variant was targeting 337 applications, including social, communication, and dating applications.
A security advisory by the bank, dated 24 November 2023, mentions what happens if a virus-infected app is installed. Once installed, the attackers would be able to access the messages with the one-time passwords (OTPs) and personal identification numbers (PINs). They could take over the device and make money transactions from the bank account of the owner of the device, says the advisory.
Social Engineering: The Common Thread
Although honey traps and APK frauds may appear on the surface to be very different, there is one aspect they have in common: both are social engineering tricks. The attacker does not rely solely on technological control or access control but also on human vulnerabilities – the fear, intimidation, lust, or love – to persuade the target to behave in a certain manner. The "opposite" sex may ask you to install some "video call app", or a "bank officer" may advise you to update KYC via a file that you may or may not be having. In any of these instances, it is the final step that you will likely carry out without hesitation. The SSB's four steps (stop, think, check, then act) provide a mechanism to break this cycle.
Implications for Personal, Financial and National Security
A phone on the compromised list reveals contacts, snaps, messages and location. Honey trap nudity can take a toll on a person's mental health and reputation via sextortion.
Financial security- Since malware can read SMS, OTP-based protection works quietly. The fraudster can authorise the transaction without the victim providing a code.
National security – For service members, it's not just their personal information at risk. A compromised device can disclose information about their location and their colleagues or how they operate. Border forces operate in a high-risk environment, and no information is too small; even duty rosters or images taken against a landmark background could be of interest to a hostile person, and honey trap recruitment for spy work is one of the oldest.
Practical Precautions
- Avoid sideloading APKs at all costs. Sideloading APKs is highly discouraged. It is best to keep the "Install from unknown sources" option turned off and install apps only from the Google Play Store or the Apple App Store.
- Whenever you have an unsolicited contact, it is not worth believing. It is believed that reversing the search of profile images and being very careful with new acquaintances who quickly begin chatting in private is protective. Never comply with any requests for money.
- Sharing intimate images or receiving surprise video calls from unknown people should be avoided.
- Storing credentials is especially sensitive. Research has shown that a legitimate bank or government body would not typically ask for details like OTPs, PINs or passwords.
- Scrutinise app permissions. Beware of a seemingly simple app requesting permission to access SMS, call logs or contacts.
- It should be verified from an official source. Challans, KYC or taxes are to be submitted using the official website or app and not the link provided in the message.
- It is important to keep professional and personal lives separate. Do not discuss comments, movements or chores or post location-tagged updates.
- Keeping your devices updated and turning on Google Play Protect are crucial.
- In case you are a victim, do take quick actions. Remove the suspicious app, disconnect from the web, and inform your bank. You can report to 1930 or cybercrime.gov.in. Do not pass the suspicious file as it is going to pass on the same.
Conclusion
The SSB advisory today is a reminder that cyberattacks are less about technology and more about exploiting human vulnerabilities. Studies indicate that fake ID cards, realistic files and misinformation are easy to implement and hard to detect. It appears that cultivating verification routines, instilling a "careful hygiene of use", and quick reporting on 1930 or cybercrime.gov.in are the best initiatives that border forces and citizens can take. Creating awareness about pausing, analysing, verifying and acting if in doubt could be an even better way of building resilience. It is crucial for everyone to remain cognisant and alert and keep cyber safety at the top of the mind.
