
Cybersecurity in the Power Sector; The Central Electricity Authority released draft regulations for public comments
Introduction
The Central Electricity Authority (CEA) has released the Draft Central Electricity Authority (Cyber Security in Power Sector) Regulations, 2024, inviting ‘comments’ from stakeholders, including the general public, which are to be submitted by 10 September 2024. The new regulation is intended to make India’s power sector more cyber-resilient and responsive to counter emerging cyber threats and safeguard the nation's power infrastructure.
Key Highlights of the CEA’s New (Cyber Security in Power Sector) Regulations, 2024
- Central Electricity Authority has framed the ‘Cyber Security in Power Sector Regulations, 2024’ in the exercise of the powers conferred by sub-section (1) of 177 of the Electricity Act, 2003 in order to make regulations for measures relating to Cyber Security in the power sector.
- The scope of the regulation entails that these regulations will be applicable to all Responsible Entities, Regional Power Committees, Appropriate Commission, Appropriate Government and Associated Power Sector Government Organizations, and Training Institutes recognized by the Authority, Authority and Vendors.
- One key aspect of the proposed regulation is the establishment of a dedicated Computer Security Incident Response Team (CSIRT) for the power sector. This team will coordinate a unified cyber defense strategy throughout the sector, establishing security frameworks, and serving as the main agency for handling incident response and recovery. The CSIRT will also be responsible for creating/developing Standard Operating Procedures (SOPs), security policies, and best practices for incident response activities in consultation with CERT-In and NCIIPC. The detailed roles and responsibilities of CSIRT are outlined under Chapter 2 of the said regulations.
- All responsible entities in the power sector as mentioned under the scope of the regulation, are mandated to appoint a Chief Information Security Officer (CISO) and an alternate CISO, who need to be Indian nationals and who are senior management employees. The regulations specify that these officers must directly report to the CEO/Head of the Responsible Entity. Thus emphasizing the critical nature of CISO’s roles in safeguarding the nation’s power grid sector assets.
- All Responsible Entities shall establish an Information Security Division (ISD) dedicated to ensuring Cyber Security, headed by the CISO and remain operational around the clock. The schedule under regulation entails that the minimum workforce required for setting up an ISD is 04 (Four) officers including CISO and 04 officers/officials for shift operations. Sufficient workforce and infrastructure support shall be ensured for ISD. The detailed functions and responsibilities of ISD are outlined under Chapter 5 regulation 10. Furthermore, the ISD shall be manned by sufficient numbers of officers, having valid certificates of successful completion of domain-specific Cyber Security courses.
- The regulation obliged the entities to have a defined, documented and maintained Cyber Security Policy which is approved by the Board or Head of the entity. The regulation also obliged the entities to have a Cyber Crisis Management Plan (CCMP) approved by the higher management.
- As regards upskilling and empowerment the regulation advocates for organising or conducting periodic Cyber Security awareness programs and Cyber Security exercises including mock drills and tabletop exercises.
CyberPeace Policy Outlook
CyberPeace Policy & Advocacy Vertical has submitted its detailed recommendations on the proposed ‘Cyber Security in Power Sector Regulations, 2024’ to the Central Electricity Authority, Government of India. We have advised on various aspects within the regulation including harmonisation of these regulations with other rules as issued by CERT-In and NCIIPC, at present. As this needs to be clarified which set of guidelines will supersede in case of any discrepancy that may arise. Additionally, we advised on incorporating or making modifications to specific provisions under the regulation for a more robust framework. We have also emphasized legal mandates and penalties for non-compliance with cybersecurity, so as to make sure that these regulations do not only act as guiding principles but also provide stringent measures in case of non-compliance.
References:

Related Blogs
Introduction
Fundamentally, artificial intelligence (AI) is the greatest extension of human intelligence. It is the culmination of centuries of logic, reasoning, math, and creativity, machines trained to reflect cognition. However, such intelligence no longer resembles intelligence at all when it is put in the hands of the irresponsible, the one with malice, or the perverse, unleashed into the wild with minimal safeguards. Instead, distortion seems as a tool of debasement rather than enlightenment.
Recent incidents involving sexually explicit photographs created by AI on social media sites reveal an extremely unsettling reality. When intelligence is detached from accountability, morality, and governance, it corrodes society rather than elevates it. We are seeing a failure of stewardship rather than just a failure of technology.
The Cost of Unchecked Intelligence
The AI chatbot Grok, which operates under Elon Musk’s X (formerly Twitter), is the subject of a debate that goes beyond a single platform or product. The romanticisation of “unfiltered” knowledge and the perilous notion that innovation should come before accountability are signs of a bigger lapse in the digital ecosystem. We have allowed mechanisms that can be used as weapons against human dignity, especially the dignity of women and children, in the name of freedom.
We are no longer discussing artistic expression or experimental AI when a machine can digitally undress women, morph photos, or produce sexualised portrayals of kids with a few keystrokes. We stand in the face of algorithmic violence. Even if the physical touch is absent, the harm caused by it is genuine, long-lasting, and extremely personal.
The Regulatory Red Line
A major inflexion was reached when the Indian government responded by ordering a thorough technical, procedural, and governance-level audit. It acknowledges that AI systems are not isolated entities. Platforms that use them are not neutral pipes, but rather intermediaries with responsibilities. The Bhartiya Nyay Sanhita, the IT Act, the IT Rules 2021, and the possible removal of Section 79 safe-harbour safeguards all make it quite evident that innovation is not automatic immunity.
However, the fundamental dilemma cannot be resolved by legislation alone. AI is hailed as a force multiplier for innovation, productivity, and advancement, but when incentives are biased towards engagement, virality, and shock value, its misuse shows how easily intelligence can turn into ugliness. The output receives greater attention the more provocative it is. Profit increases with attention. Restraint turns into a business disadvantage in this ecology.
The Aftermath
Grok’s own acknowledgement that “safeguard lapses” enabled the creation of pictures showing children wearing skimpy attire underscores a troubling reality, safety was not absent due to impossibility, but due to insufficiency. It was always possible to implement sophisticated filtering, more robust monitoring, and stricter oversight. They were simply not prioritised. When a system asserts that “no system is 100% foolproof,” it must also acknowledge that there is no acceptable margin of error when it comes to child protection.
The casual normalisation of such lapses is what is most troubling. By characterising these instances as “isolated cases,” systemic design decisions run the risk of being trivialised. In addition to intelligence, AI systems that have been taught on enormous amounts of human data also inherit bias, misogyny, and power imbalances.
Conclusion
What is required today is recalibration. Platforms need to shift from reactive compliance to proactive accountability. Safeguards must be incorporated at the architectural level; they cannot be cosmetic or post-facto. Governance must encompass enforced ethical boundaries in addition to terms of service. The idea that “edgy” AI is a sign of advancement must also be rejected by society.
Artificial Intelligence has never promised freedom under the guise of vulgarity. It was improvement, support, and augmentation. The fundamental core of intelligence is lost when it is used as a tool for degradation.So what’s left is a decision between principled innovation and unbridled novelty. Between responsibility and spectacle, between intelligence as purpose and intellect as power.
References
https://www.rediff.com/news/report/govt-orders-x-review-of-grok-over-explicit-content/20260103.htm
In recent months, conversations around the possible shortage of liquefied petroleum gas (LPG), a basic cooking fuel in Indian households, have quietly resurfaced across the country. From whispers in local markets to viral messages circulating on social media, concerns about LPG availability began to take hold in the public imagination. Though the immediacy of the situation has since faded, its echoes remain, reminding us how quickly uncertainty can spread. Like a ripple across still water, a single rumour can travel far, gathering force as it moves and blurring the line between perception and reality.
Against this backdrop, in April 2026, reports began circulating about a potential LPG shortage. The Union Government moved quickly to counter what it identified as misinformation, emphasising that supply remained stable and urging citizens not to engage in panic buying. A noticeable disconnect emerged between official communication and public perception. Across different regions, signs of anxiety-driven behaviour became evident. Instances of panic buying and hoarding increased, law enforcement agencies conducted raids to address such actions, and opportunistic thefts were reported, often exploiting widespread concern. These incidents highlight how misinformation, even when addressed promptly, can continue to shape public behaviour.
It is worth noting that rising prices also played a role in shaping public response, as increases in LPG rates contributed to a sense of urgency among consumers. Therefore, the surge in panic buying cannot be attributed solely to misinformation, but rather to a combination of economic pressures and perceived scarcity.
Misinformation Ecosystem - From Rumours to Behaviour
The spread of misinformation is occurring at an unprecedented pace and is, in large part, driven by the viral nature of social media. Digital platforms not only enable the rapid dissemination of information but also allow it to be amplified in ways that would not be possible through traditional media outlets. Often, the drive for virality outweighs any concern for accuracy, meaning that many individuals who spread misinformation are motivated more by the pursuit of attention than by any ideological agenda. Recent arrests of individuals involved in spreading misinformation about LPG and petrol shortages, much of which went viral, suggest that misinformation today is frequently driven by the desire for visibility rather than ideological motives. The information being circulated has largely followed a similar pattern, focusing on fears of an LPG shortage, expectations of price increases, and concerns about supply disruptions. Even though this information has not been verified, it has triggered behavioural responses among individuals. In several areas, including parts of Uttar Pradesh and Goa, the spread of misinformation through social media has led to panic buying, despite official assurances that there would be sufficient LPG supply to meet demand.
The impact of panic buying, and its associated misinformation, has already been seen in multiple sectors; these increased demands have placed pressure on the distribution network, leading to disruptions in access, as well as being out of stock of certain products. In many cases, commercial users of products (especially restaurants) have experienced significant disruption, threatening their continued operations, and industry representatives have alerted others about the inconsistent supply of commercial cylinders; likewise, consumers (households) are beginning to switch to alternative products (e.g., induction cooking) as a reflection of the anticipatory mindset to address the uncertainty created through perceptions of Product Scarcity.
State Response: Managing Misinformation or Behaviour?

The government has taken a variety of approaches, from advisories and enforcement actions to communicating with citizens indirectly. For example, State Governments have been directed to combat misinformation, monitor supply chains and take action against hoarding and black market activity. There has been a significant increase in the level of large- scale enforcement activity, with over 3,700 raids carried out to crack down on hoarding and black marketing related to LPG, in addition to confiscating cylinders and issuing penalties to those who break the law. In addition, the authorities have also focused on maintaining regular communication with the public in order to reassure them about the supply of LPG and fuel stability.
Geopolitical Context: Why Rumours Are Believable
Understanding today’s panic requires an understanding of the global environment: i.e., due to the ongoing conflict in West Asia, the energy markets are unstable, and energy supply is uncertain not only in West Asia but across a large part of the world. Even if domestic supply remains stable, public perception is affected by global instability. A clear example of this can be seen in neighbouring countries to India; Pakistan has seen significant increases in the cost of fuel, implemented measures such as reducing the number of days individuals work each week, and has created public support mechanisms; Bangladesh has imposed restrictions on the use of energy, has shortened the number of hours individuals can operate businesses each day, and has restricted the total amount of energy used; Sri Lanka has begun to ration fuel, and to increase the price of petrol; and Nepal has reduced the numbers of days individuals may work each week, and has adjusted supply.
All of these examples are not isolated instances, but are markers of a common regional environment. As we live in a global community that is connected in many ways, these developments will quickly affect public expectations everywhere. Therefore, for consumers in India, seeing evidence of rationing of fuel and shortages of fuel in neighbouring countries increases their belief that these types of problems could occur in their country.
Critical Perspective: Between Panic and Precaution
The LPG incident has brought about questions surrounding the nature of misinformation in terms of its definition & regulation. One of the main concerns is whether or not "misinformation" is being cast too widely. To be sure, false claims need to be addressed; however, not everything that is responded to publicly is based on untrue facts, as many times public responses are based on perceived risk via global and/or local incidents that occur. Perhaps the greatest challenge is the difficulty in differentiating precaution and panic. People’s memories of the COVID-19 pandemic are fresh in their minds and will serve to influence their behaviours moving onward, in that many people are stockpiling or preparing for uncertainty not out of irrational fear, but as an anticipatory response to their prior experiences.
Conclusion
The Indian LPG "crisis" is not so much a problem with actual supply chain breakdown as it is a result of how information and behaviour are connected through perception. This cohabitating environment of panic buying, law enforcement, and government assurance demonstrates an evident disconnect and gap between how governments present a narrative and how the public responds. While there is some role of misinformation within this discourse, the misinformation itself extends beyond any or all false claims about LPG supply and operates within a greater ecosystem of global uncertainty and personal experience. As such, and because of this, perception becomes an incredibly strong force in itself that produces true economic consequences.
Reference
- https://www.pib.gov.in/PressReleasePage.aspx?PRID=2248640&utm_source®=3&lang=2
- https://www.pmindia.gov.in/en/news_updates/pm-addresses-the-lok-sabha-on-the-ongoing-conflict-in-west-asia/
- https://www.ndtv.com/delhi-news/iran-war-middle-east-conflict-why-the-lpg-crisis-is-forcing-migrants-to-quietly-leave-delhi-11313629
- https://timesofindia.indiatimes.com/city/bareilly/thieves-steal-108-lpg-cylinders-from-godown-in-up/articleshow/130035518.cms
- https://indianexpress.com/article/india/arrested-rumours-lpg-petrol-shortage-police-chasing-views-10614193/
- https://www.hindustantimes.com/cities/lucknow-news/social-media-rumours-fuel-panic-buying-in-some-up-districts-situation-normal-in-lucknow-101774465353107.html
- https://timesofindia.indiatimes.com/city/goa/fear-of-shortage-price-rise-fuels-panic-buying-across-goa/articleshow/129810144.cms
- https://www.news18.com/cities/new-delhi-news/online-rumours-offline-rush-panic-buying-sweeps-petrol-pumps-across-cities-whats-the-truth-ws-ln-9995684.html
- https://m.economictimes.com/news/india/3700-raids-conducted-across-country-to-wipe-out-lpg-black-marketing-says-centre/articleshow/130025232.cms
- https://www.reuters.com/business/energy/induction-stoves-fly-off-shelves-india-gas-shortage-fears-spark-panic-buying-2026-03-12/
- https://www.ndtv.com/india-news/restaurant-body-warns-of-closures-over-commercial-lpg-supply-concerns-writes-to-minister-11194418
- https://www.freepressjournal.in/mumbai/fpj-dialogue-we-are-getting-only-1-cylinder-instead-of-10-says-ahar-president-vijay-shetty-on-mumbai-lpg-crisis
- https://www.hindustantimes.com/world-news/fuel-cuts-wfh-and-more-how-indias-neighbours-are-dealing-with-global-energy-crisis-triggered-by-us-iran-war-101775397199941.html
- https://www.abc.net.au/news/2026-03-30/four-step-fuel-supply-plan-national-cabinet-fuel-crisis/106512706
- https://tribune.net.ph/2026/04/07/philippines-scrambles-as-regional-oil-crisis-hits
Introduction
Agentic AI systems are autonomous systems that can plan, make decisions, and take actions by interacting with external tools and environments. But they shift the nature of risk by blurring the lines among input, decision, and execution. A conventional model generates an output and stops. An agent takes input, makes plans, invokes tools, updates its state and repeats the cycle. This creates a system where decisions are continuously revised through interaction with external tools and environments, rather than being fixed at the point of input.
This means the attack surface expands in size and becomes more dynamic. Instead of remaining confined to components as in traditional computational systems, they spread in layers and can continue to grow through time. To understand this shift, the system can be analysed through functional layers such as inputs, memory, reasoning, and execution, while recognising that risk does not remain isolated within these layers but emerges through their interaction.
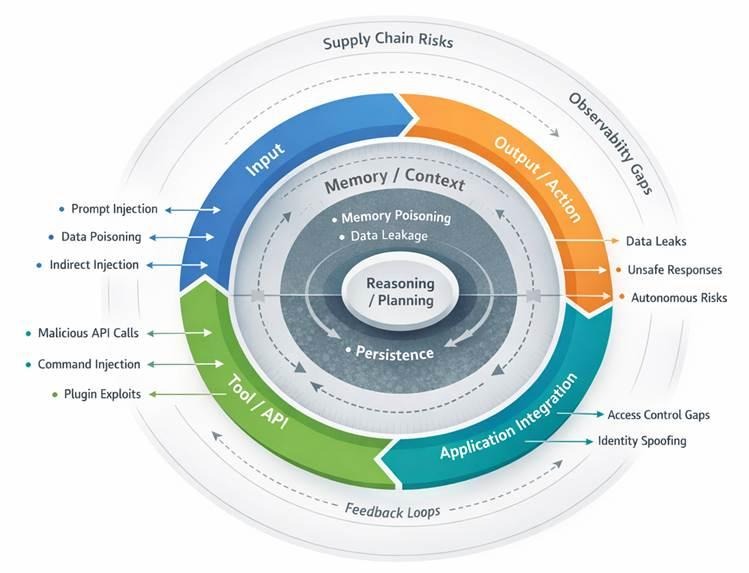
Agentic AI Attack Surface
A layered view of how risks emerge across input, memory, reasoning, execution, and system integration, including feedback loops and cross-system dependencies that amplify vulnerabilities.
Input Layer: Where Untrusted Data Becomes Control
The entry point of an agent is no longer one prompt. The documents, APIs, files, system logs and the outputs of other agents can now be considered input. This diversity is significant due to the fact that every source of input carries its own trust assumptions, and in the majority of cases, they are weak.
The most obvious threat is prompt injection, where inputs are treated as instructions rather than data. Since inputs are treated as instructions, a virus, a malicious webpage, or a document can contain instructions that override system goals without necessarily being detected as something harmful.
Indirect prompt injection extends this risk beyond direct user interaction. Instead of targeting the interface, attackers compromise the retrieval process by embedding malicious instructions within external data sources. When the agent retrieves and processes the data, it treats the embedded content as legitimate input. As a result, the attack is executed through normal reasoning processes, allowing the system to act on untrusted data without recognising the manipulation.
Data poisoning also occurs at runtime. In contrast to classical poisoning (where training data is manipulated), runtime poisoning distorts the agent’s perception of its environment as it runs. This can change decisions without causing apparent failures.
Obfuscation introduces another indirect attacker vector. Encoded instructions or complicated forms may bypass human review but remain readable to the model. This creates asymmetry whereby the system knows more about the attack than those operating it. Once compromised at this layer, the agent implements compromised instructions which affect downstream operations.
Context and Memory: Persistence of Influence
Agentic systems depend on memory to operate efficiently. They often retain context across sessions and frequently store information between sessions.
This introduces a different type of risk: persistence. Through memory poisoning, attackers can insert false or adversarial information into sorted context, which then influences future decisions. Unlike prompt injection, which is often limited to a single interaction, this effect carries forward. Over time, the agent begins to operate on a distorted internal state, shaping decisions in ways that may not be immediately visible.
Another issue is cross-session leakage. Information in a particular context may be replayed in a different context when memory is being shared or there is insufficient memory separation. This is specifically dangerous in those systems that combine retrieval and long-term storage. The context management in itself becomes a weakness. Agents are required to make decisions on what to retain and what to discard. This is susceptible to attackers who can flood the context or manipulate what is still visible and indirectly affect reasoning.
The underlying problem is structural. Memory turns data into a state. Once state is corrupted, the system cannot easily distinguish valid knowledge from adversarial influence.
The issue is structural. Memory converts temporary data into a persistent state. Once this state is weakened, the system cannot reliably separate valid information from adversarial influence, making recovery significantly more difficult.
Reasoning and Planning: Manipulating Intent Without Breaking Logic
The reasoning layer is where agentic AI stands apart from traditional systems. The model no longer reacts to inputs alone. It actively breaks down objectives, analyses alternatives, and ranks actions.
At the reasoning stage, the nature of risk shifts. The concern is no longer limited to injecting instructions, but to influencing how decisions are made. One example is goal manipulation, where the agent subtly reinterprets its objective and produces outcomes that are technically correct but strategically harmful. Reasoning hijacking operates within intermediate steps, altering how constraints are evaluated or how trade-offs are prioritised. The system may remain internally consistent, which makes such deviations difficult to detect.
Tool selection becomes a critical control point. Agents decide which tools to use and when, so influencing these choices can redirect execution without directly accessing the tools themselves. Hallucinations also take on a different role here. In static systems, they remain errors. In agentic systems, they can trigger actions. A perceived need or incorrect judgement can translate into real-world consequences.
This layer introduces probabilistic failure. The system is not fully weakened, but it is nudged towards decisions that appear reasonable yet are incorrect. The risk lies in how those decisions are justified.
Tool and Execution: When Decisions Gain Reach
Once an agent begins interacting with tools, its behaviour extends beyond the model into external systems. APIs, databases, and services become part of the execution path.
One key risk is the use of unauthorised tools. When agents operate with broad permissions, any manipulation of the upstream can be converted into real-world actions. This makes access control a central security concern. Command injection also takes a different form here. The agent generates commands based on its reasoning, so if that reasoning is compromised, the resulting actions may still appear valid despite being harmful.
External tool outputs introduce another risk. If these systems return corrupted or misleading data, the agent may accept it without verification and incorporate it into its decisions. It is also becoming increasingly reliant on third-part tools and plugins adds to this exposure. If these components are compromised, they can affect behaviour without directly attacking the core system, creating a supply-side risk.
At this stage, the agent effectively operates as an insider. It holds legitimate credentials and interacts with systems in expected ways, making misuse harder to identify.
Application and Integration: System-Level Exposure
Agentic systems rarely operate in isolation. They are embedded in larger environments, interacting with identity systems, business logic, and operational workflows.
Access control becomes a major vulnerability. Agents tend to operate across multiple systems with various permission models, creating irregularities that can be exploited. Risks also arise from identity and delegation. In case an agent is operating on behalf of a user, then any vulnerabilities in authentication or session management can allow attackers to assume that authority.
Workflow execution amplifies these risks. Agents can initiate multi-step processes such as transactions, updates, or approvals. Manipulating a single step can change the result of the entire workflow. As integrations increase, so do the number of interaction points, making cumulative risk harder to track.
At this layer, failures are not isolated. They propagate into business operations, making consequences harder to contain.
Output and Action: Where Failures Become Visible
The output layer is where failures become visible, though they rarely originate there.
Data leakage has been a key concern. Agents may disclose information they are allowed to access, especially when tasks boundaries are not clearly defined. Misinformation and unsafe outputs are also important, particularly when outputs directly influence actions or decisions.
Generated code and commands introduce execution risk. If outputs are used without validation, errors or manipulations can have system-level effects. The shift towards autonomous action increases this risk, as small upstream deviations can lead to significant consequences without human intervention. This layer reflects symptoms rather than root causes. Addressing it alone does not reduce the underlying risk.
Beyond Layers: The Missing Dimension
A layered view helps, but it does not capture the full picture. Agentic systems are defined by continuous interaction across layers.
The key missing dimension is the runtime loop. Inputs shape reasoning, reasoning drives action, and actions feed back into both reasoning and memory. These cycles create feedback loops, where small manipulations may escalate over time. This also reduces observability. With multiple interacting components, it becomes difficult to trace cause and effect or identify where failures originate.
Supply chain dependencies add another layer of risk. Models, datasets, APIs, and plugins each introduce their own points of failure. A compromise at any of these points can propagate across the system. The attack surface also includes governance. Weak supervision, unclear responsibility, or excessive autonomy increase overall risk. Human control is not external to the system; it is part of its security.
Conclusion: Structuring the Attack Surface
Agentic AI expands the attack surface beyond traditional systems. It is both recursive and stateful. Risk does not just accumulate across layers; it moves and changes as the system operates.
Any useful representation must go beyond a linear stack. It should capture feedback loops, persistent state, and cross-layer dependencies that characterise the way these systems actually behave. The system is not a pipeline but a cycle. That is where both its capability and its risk emerge.
