
Centre Proposes New Bills for Criminal Law
Introduction
Criminal justice in India is majorly governed by three laws which are – Indian Penal Code, Criminal Procedure Code and Indian Evidence Act. The centre, on 11th August 2023’ Friday, proposes a new bill in parliament Friday, which is replacing the country’s major criminal laws, i.e. Indian Penal Code, Criminal Procedure Code and Indian Evidence Act.
The following three bills are being proposed to replace major criminal laws in the country:
- The Bharatiya Nyaya Sanhita Bill, 2023 to replace Indian Penal Code 1860.
- The Bharatiya Nagrik Suraksha Sanhita Bill, 2023, to replace The Code Of Criminal Procedure, 1973.
- The Bharatiya Sakshya Bill, 2023, to replace The Indian Evidence Act 1872.
Cyber law-oriented view of the new shift in criminal lawNotable changes:Bharatiya Nyaya Sanhita Bill, 2023 Indian Penal Code 1860.
Way ahead for digitalisation
The new laws aim to enhance the utilisation of digital services in court systems, it facilitates online registration of FIR, Online filing of the charge sheet, serving summons in electronic mode, trial and proceedings in electronic mode etc. The new bills also allow the virtual appearance of witnesses, accused, experts, and victims in some instances. This shift will lead to the adoption of technology in courts and all courts to be computerised in the upcoming time.
Enhanced recognition of electronic records
With the change in lifestyle in terms of the digital sphere, significance is given to recognising electronic records as equal to paper records.
Conclusion
The criminal laws of the country play a significant role in establishing law & order and providing justice. The criminal laws of India were the old laws existing under British rule. There have been several amendments to criminal laws to deal with the growing crimes and new aspects. However, there was a need for well-established criminal laws which are in accordance with the present era. The step of the legislature by centralising all criminal laws in their new form and introducing three bills is a good approach which will ultimately strengthen the criminal justice system in India, and it will also facilitate the use of technology in the court system.

Related Blogs

Overview:
After the blackout on July 19, 2024, which affected CrowdStrike’s services worldwide, cybercriminals began to launch many phishing attacks and distribute malware. These activities mainly affect CrowdStrike customers, using the confusion as a way to extort information through fake support sites. The analysis carried out by the Research Wing of CyberPeace and Autobot Infosec has identified several phishing links and malicious campaigns.
The Exploitation:
Cyber adversaries have registered domains that are similar to CrowdStrike’s brand and have opened fake accounts on social media platforms. These are fake platforms that are employed to defraud users into surrendering their personal and sensitive details for use in other fraudulent activities.
Phishing Campaign Links:
- crowdstrike-helpdesk[.]com
- crowdstrikebluescreen[.]com
- crowdstrike-bsod[.]com
- crowdstrikedown[.]site
- crowdstrike0day[.]com
- crowdstrikedoomsday[.]com
- crowdstrikefix[.]com
- crashstrike[.]com
- crowdstriketoken[.]com
- fix-crowdstrike-bsod[.]com
- bsodsm8r[.]xamzgjedu[.]com
- crowdstrikebsodfix[.]blob[.]core[.]windows[.]net
- crowdstrikecommuication[.]app
- fix-crowdstrike-apocalypse[.]com
- supportportal-crowdstrike-com[.]translate[.]goog
- crowdstrike-cloudtrail-storage-bb-126d5e[.]s3[.]us-west-1[.]amazonaws[.]com
- crowdstrikeoutage[.]info
- clownstrike[.]co[.]uk
- crowdstrikebsod[.]com
- whatiscrowdstrike[.]com
- clownstrike[.]co
- microsoftcrowdstrike[.]com
- crowdfalcon-immed-update[.]com
- crowdstuck[.]org
- failstrike[.]com
- winsstrike[.]com
- crowdpass[.]com
In one case, a PDF file is being circulated with CrowdStrike branding, saying ‘Download The Updater,’ which is a link to a ZIP file. The ZIP file is a compressed file that has an executable file with a virus. This is a clear sign that the hackers are out to take advantage of the current situation by releasing the malware as an update.


In another case, there is a malicious Microsoft Word document that is currently being shared, which claims to offer a solution on how to deal with this CrowdStrike BSOD bug. But there is a hidden risk in the document. When users follow the instructions and enable the embedded macro, it triggers the download of an information-stealing malware from a remote host. This is a form of malware that is used to steal information and is not well recognized by most security software. Also it sends the stolen data to the samesame remote host but with different port number, which likey works as the CnC server for the campaign.
- Name New_Recovery_Tool_to_help_with_CrowdStrike_issue_impacting_Windows[.]docm
- MD5 dd2100dfa067caae416b885637adc4ef
- SHA-1 499f8881f4927e7b4a1a0448f62c60741ea6d44b
- SHA-256 803727ccdf441e49096f3fd48107a5fe55c56c080f46773cd649c9e55ec1be61
- URLS http://172.104.160[.]126:8099/payload2.txt, http://172.104.160[.]126:5000/Uploadss


Recent Outage Impact:
On July 19, 2024, CrowdStrike faced a global outage that originated from an update of its Falcon Sensor security software. This outage affected many government organizations and companies in different industries, such as finance, media, and telecommunications. The event led to numerous complaints from the users who experienced problems like blue screen of death and system failure. Although, CrowdStrike has admitted to the problem and is in the process of fixing it.
Preventive Measures:
- Organize regular awareness sessions to educate the employees about the phishing techniques and how they can avoid the phishing scams, emails, links, and websites.
- MFA should be used for login to the sensitive accounts and systems for an improvement on the security levels.
- Make sure all security applications including the antivirus and anti-malware are up to date to help in the detection of phishing scams.
- This includes putting in place of measures such as alert on account activity or login patterns to facilitate early detection of phishing attempts.
- Encourage employees and users to inform the IT department as soon as they have any suspicions regarding phishing attempts.
Conclusion:
The recent CrowdStrike outage is a perfect example of how cybercriminals take advantage of the situation and user’s confusion and anxiety. Thus, people and organizations can keep themselves from these threats and maintain the confidentiality of their information by being cautious and adhering to the proper standards. To get the current information on the BSOD problem and the detailed instructions on its solution, visit CrowdStrike’s support center. Reported problems should be handled with caution and regular backup should be made to minimize the effects.
References:
- https://app.any.run/tasks/2c0ffc87-4059-4d6f-8306-1258cf33aa54/
- https://app.any.run/tasks/48e18e33-2007-49a8-aa60-d04c21e8fa11
- https://www.virustotal.com/gui/file/19001dd441e50233d7f0addb4fcd405a70ac3d5e310ff20b331d6f1a29c634f0/relations
- https://www.virustotal.com/gui/file/803727ccdf441e49096f3fd48107a5fe55c56c080f46773cd649c9e55ec1be61/detection
- https://www.joesandbox.com/analysis/1478411#iocs

Introduction
Advanced deepfake technology blurs the line between authentic and fake. To ascertain the credibility of the content it has become important to differentiate between genuine and manipulated or curated online content highly shared on social media platforms. AI-generated fake voice clone, videos are proliferating on the Internet and social media. There is the use of sophisticated AI algorithms that help manipulate or generate synthetic multimedia content such as audio, video and images. As a result, it has become increasingly difficult to differentiate between genuine, altered, or fake multimedia content. McAfee Corp., a well-known or popular global leader in online protection, has recently launched an AI-powered deepfake audio detection technology under Project “Mockingbird” intending to safeguard consumers against the surging threat of fabricated or AI-generated audio or voice clones to dupe people for money or unauthorisly obtaining their personal information. McAfee Corp. announced its AI-powered deepfake audio detection technology, known as Project Mockingbird, at the Consumer Electronics Show, 2024.
What is voice cloning?
To create a voice clone of anyone's, audio can be deeplyfaked, too, which closely resembles a real voice but, in actuality, is a fake voice created through deepfake technology.
Emerging Threats: Cybercriminal Exploitation of Artificial Intelligence in Identity Fraud, Voice Cloning, and Hacking Acceleration
AI is used for all kinds of things from smart tech to robotics and gaming. Cybercriminals are misusing artificial intelligence for rather nefarious reasons including voice cloning to commit cyber fraud activities. Artificial intelligence can be used to manipulate the lips of an individual so it looks like they're saying something different, it could also be used for identity fraud to make it possible to impersonate someone for a remote verification for your bank and it also makes traditional hacking more convenient. Cybercriminals have been misusing advanced technologies such as artificial intelligence, which has led to an increase in the speed and volume of cyber attacks, and that's been the theme in recent times.
Technical Analysis
To combat Audio cloning fraudulent activities, McAfee Labs has developed a robust AI model that precisely detects artificially generated audio used in videos or otherwise.
- Context-Based Recognition: Contextual assessment is used by technological devices to examine audio components in the overall setting of an audio. It improves the model's capacity to recognise discrepancies suggestive of artificial intelligence-generated audio by evaluating its surroundings information.
- Conductual Examination: Psychological detection techniques examine linguistic habits and subtleties, concentrating on departures from typical individual behaviour. Examining speech patterns, tempo, and pronunciation enables the model to identify artificially or synthetically produced material.
- Classification Models: Auditory components are categorised by categorisation algorithms for detection according to established traits of human communication. The technology differentiates between real and artificial intelligence-synthesized voices by comparing them against an extensive library of legitimate human speech features.
- Accuracy Outcomes: McAfee Labs' deepfake voice recognition solution, which boasts an impressive ninety per cent success rate, is based on a combined approach incorporating psychological, context-specific, and categorised identification models. Through examining audio components in the larger video context and examining speech characteristics, such as intonation, rhythm, and pronunciation, the system can identify discrepancies that could be signs of artificial intelligence-produced audio. Categorical models make an additional contribution by classifying audio information according to characteristics of known human speech. This all-encompassing strategy is essential for precisely recognising and reducing the risks connected to AI-generated audio data, offering a strong barrier against the growing danger of deepfake situations.
- Application Instances: The technique protects against various harmful programs, such as celebrity voice-cloning fraud and misleading content about important subjects.
Conclusion
It is important to foster ethical and responsible consumption of technology. Awareness of common uses of artificial intelligence is a first step toward broader public engagement with debates about the appropriate role and boundaries for AI. Project Mockingbird by Macafee employs AI-driven deepfake audio detection to safeguard against cyber criminals who are using fabricated AI-generated audio for scams and manipulating the public image of notable figures, protecting consumers from financial and personal information risks.
References:
- https://www.cnbctv18.com/technology/mcafee-deepfake-audio-detection-technology-against-rise-in-ai-generated-misinformation-18740471.htm
- https://www.thehindubusinessline.com/info-tech/mcafee-unveils-advanced-deepfake-audio-detection-technology/article67718951.ece
- https://lifestyle.livemint.com/smart-living/innovation/ces-2024-mcafee-ai-technology-audio-project-mockingbird-111704714835601.html
- https://news.abplive.com/fact-check/audio-deepfakes-adding-to-cacophony-of-online-misinformation-abpp-1654724
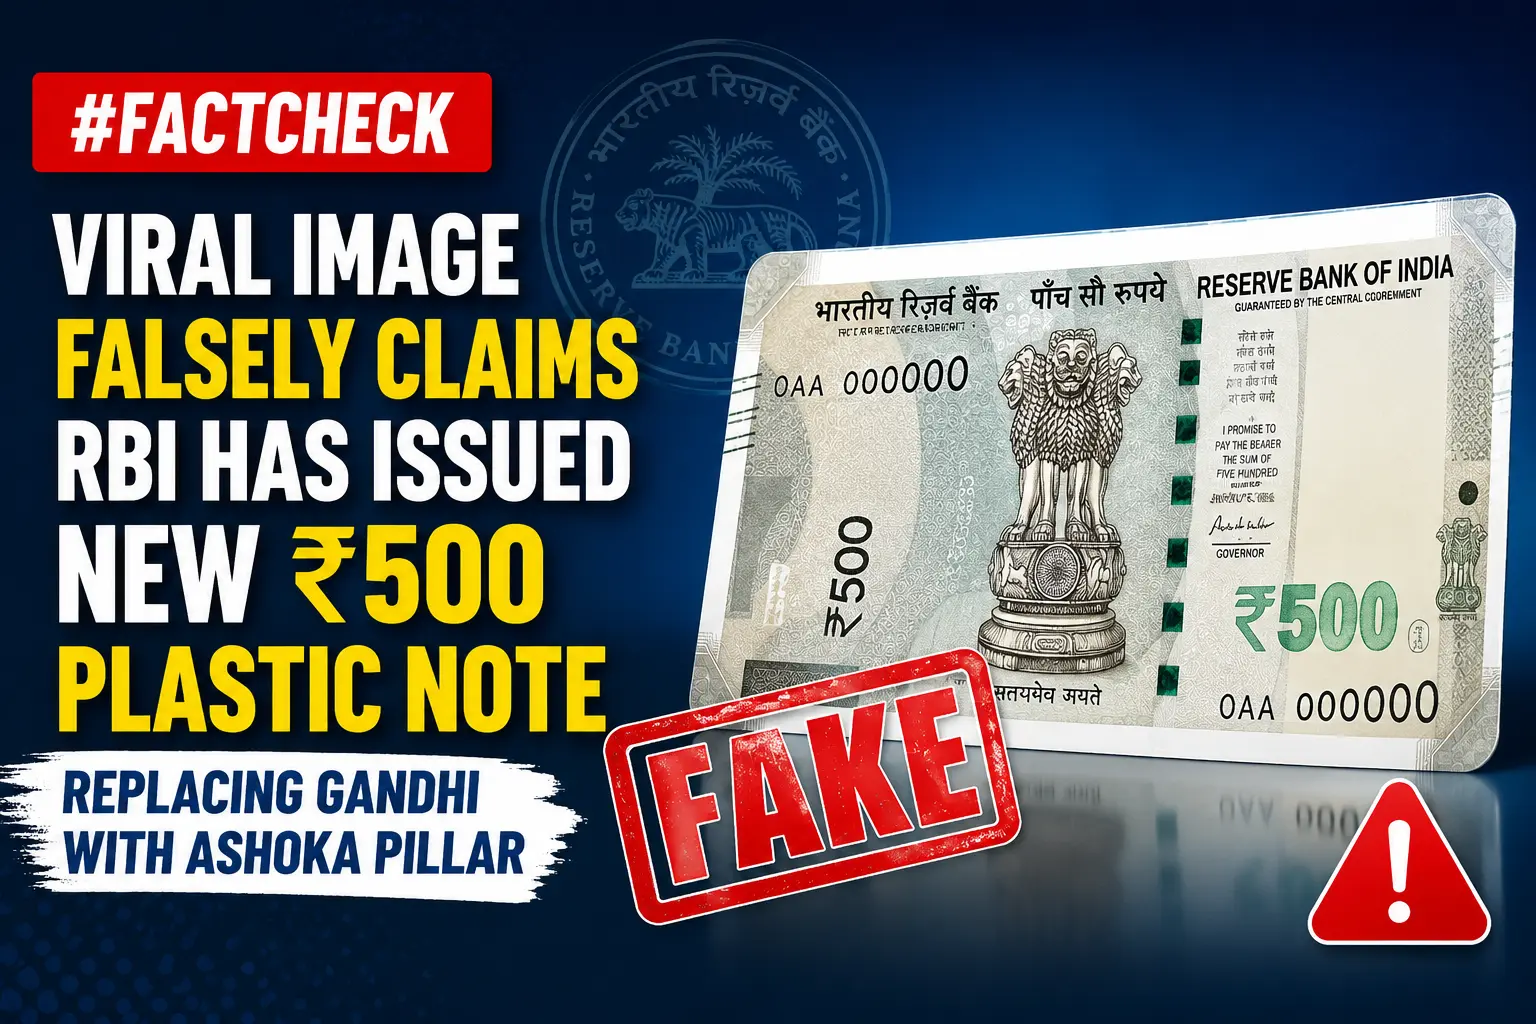
Executive Summary
An image of a purported new ₹500 plastic banknote is being widely shared on social media. Users claim that the Reserve Bank of India (RBI) has issued the new note and replaced Mahatma Gandhi’s portrait with the Ashoka Pillar.The CyberPeace Research Wing research found the claim to be misleading. The probe revealed that RBI has not issued any new ₹500 plastic banknote. Furthermore, no official announcement or decision has been made regarding the removal of Mahatma Gandhi’s portrait from Indian currency and its replacement with the Ashoka Pillar.
Claim
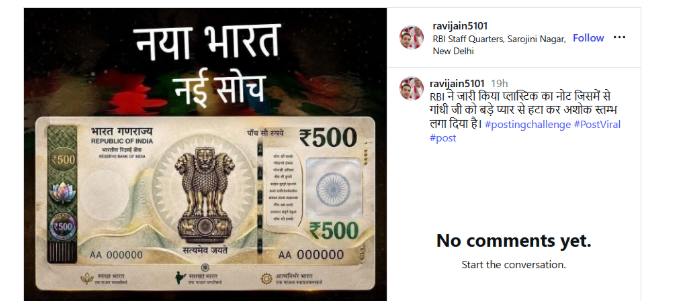
An Instagram user shared the viral image with the claim: “RBI has issued a ₹500 plastic note in which Mahatma Gandhi’s image has been removed and replaced with the Ashoka Pillar.” The claim has been widely circulated on social media, with many users sharing the image as genuine. The post link, archived version, and screenshot can be seen below.
Fact Check
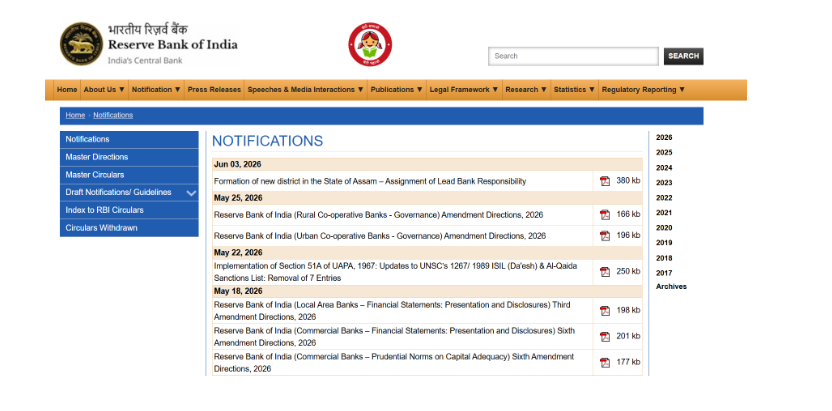
To verify the claim, we conducted a keyword search on Google. However, we found no credible media reports suggesting that RBI had issued a new ₹500 plastic note featuring the Ashoka Pillar in place of Mahatma Gandhi. We then searched the official RBI website for any notification or announcement related to the claim. Our search yielded no official communication supporting the viral claim.
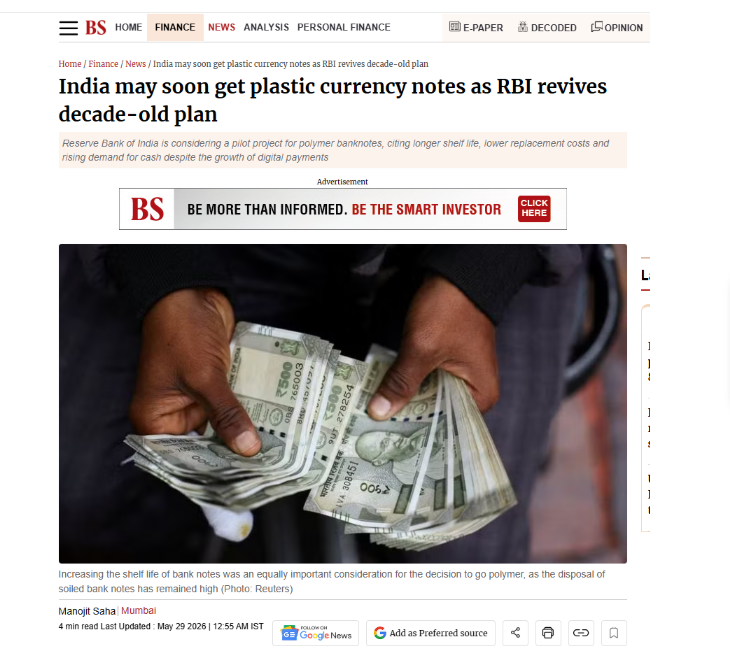
During the research, we also came across a report published by Business Standard. According to the report, the Reserve Bank of India is exploring the possibility of introducing polymer (plastic) currency notes in the future. The report states that RBI is studying and discussing the proposal in view of the growing global adoption of polymer notes and their greater durability. However, the report does not state that RBI has already issued a new ₹500 plastic note. Nor does it mention any decision to remove Mahatma Gandhi’s portrait from existing currency notes and replace it with the Ashoka Pillar.
- https://www.business-standard.com/finance/news/rbi-set-to-unveil-polymer-rupee-notes-amid-rising-currency-demand-126052801725_1.html
Conclusion
The research found that the viral claim is misleading. RBI has not issued any new ₹500 plastic banknote, and there has been no official announcement or decision to replace Mahatma Gandhi’s portrait on Indian currency with the Ashoka Pillar.
